dumpstool logo
You need to recommend a solution to secure the MedicalHistory data in the ClaimsDetail table. The solution must meet the Contoso developer requirements.
What should you include in the recommendation?
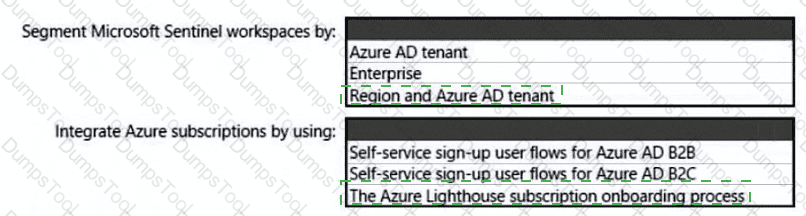
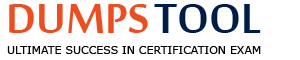
You need to recommend a SIEM and SOAR strategy that meets the hybrid requirements, the Microsoft Sentinel requirements, and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to recommend a solution for securing the landing zones. The solution must meet the landing zone requirements and the business requirements.
What should you configure for each landing zone?
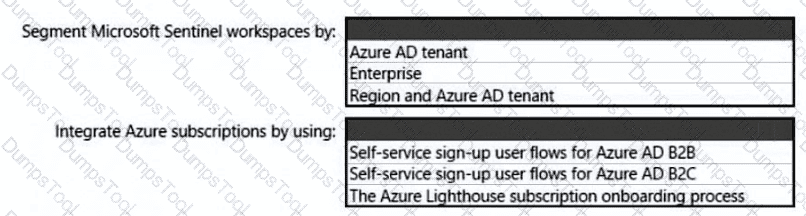
You need to recommend a strategy for securing the litware.com forest. The solution must meet the identity requirements. What should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE; Each correct selection is worth one point.
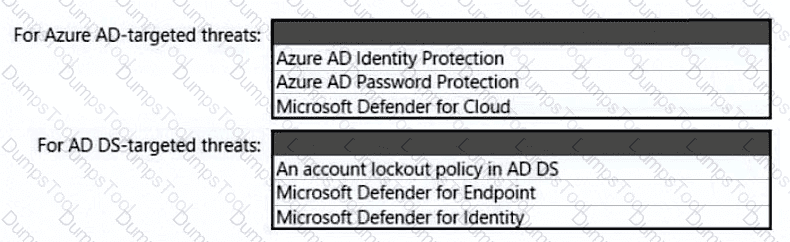
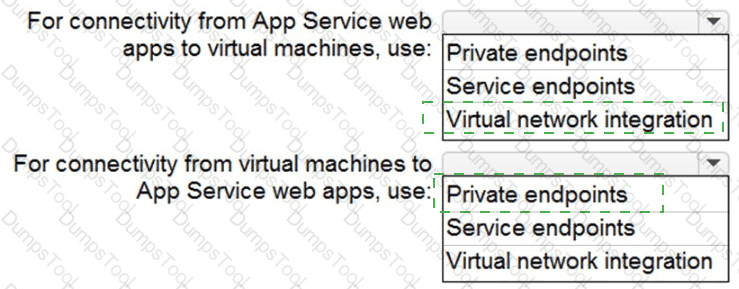
You need to recommend a strategy for App Service web app connectivity. The solution must meet the landing zone requirements. What should you recommend? To answer, select the appropriate options in the answer area. NOTE Each correct selection is worth one point.
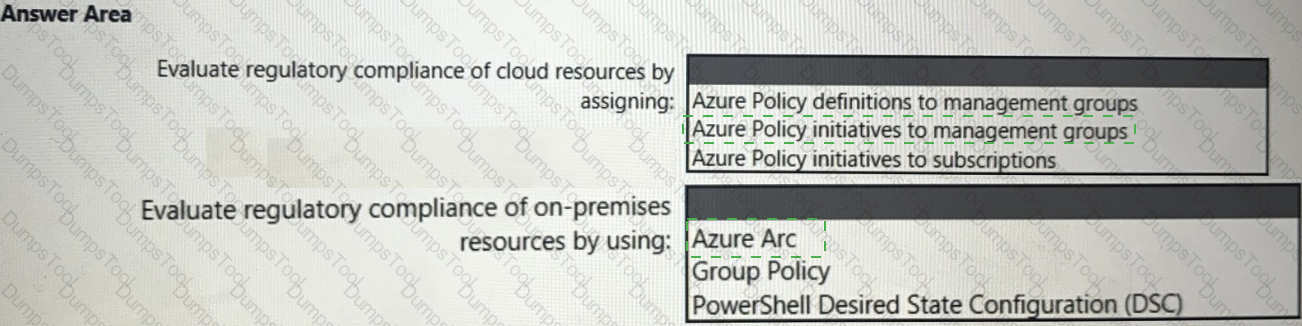
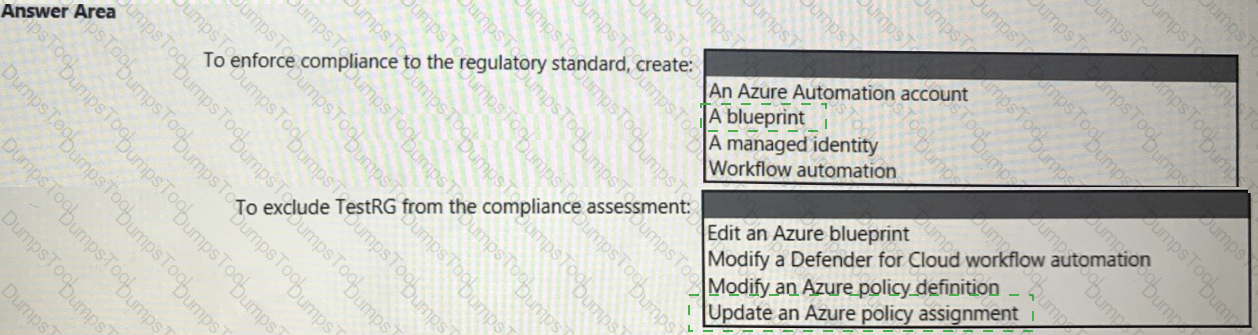
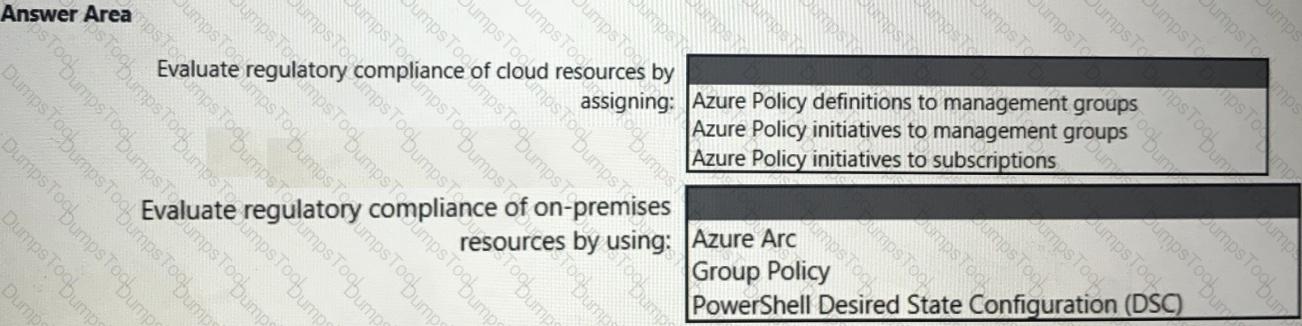
You need to recommend a solution to evaluate regulatory compliance across the entire managed environment. The solution must meet the regulatory compliance requirements and the business requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
To meet the application security requirements, which two authentication methods must the applications support? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
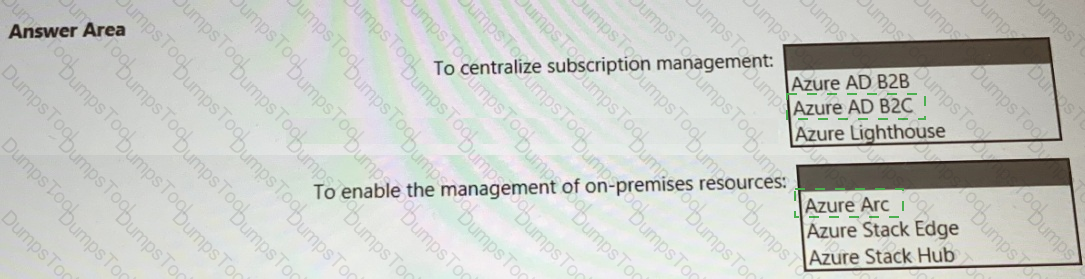
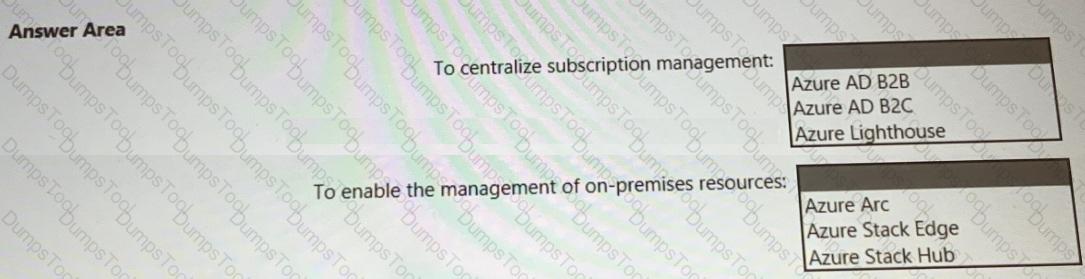
You need to recommend a multi-tenant and hybrid security solution that meets to the business requirements and the hybrid requirements. What should you recommend? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You need to design a strategy for securing the SharePoint Online and Exchange Online data. The solution must meet the application security requirements.
Which two services should you leverage in the strategy? Each correct answer presents part of the solution. NOTE; Each correct selection is worth one point.
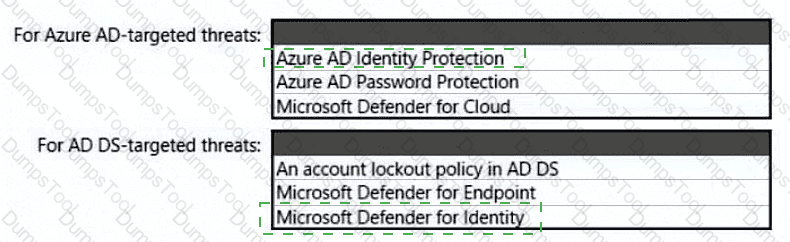
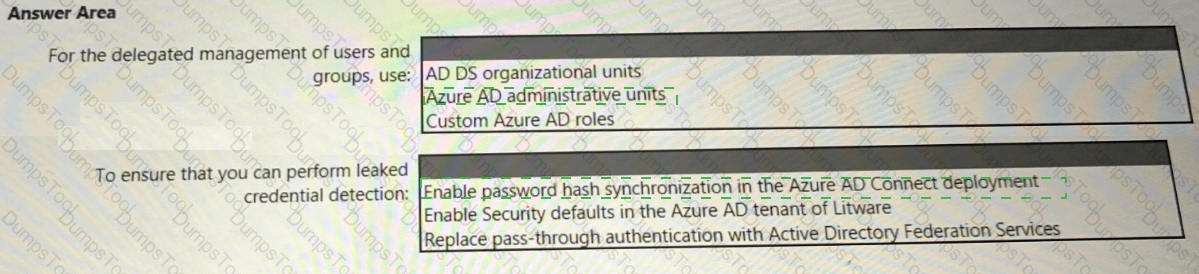
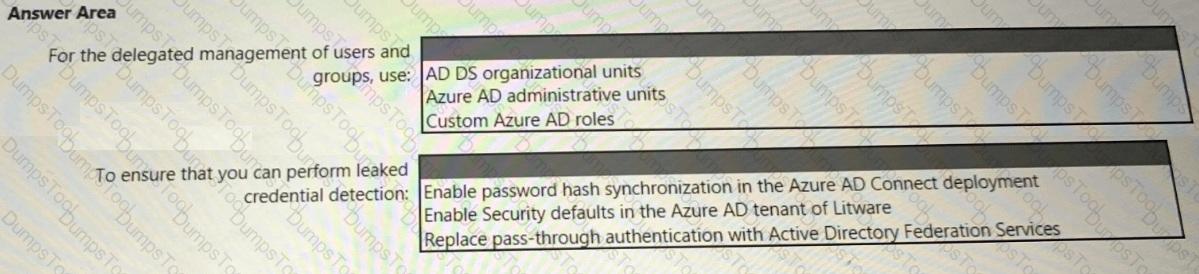
You need to recommend an identity security solution for the Azure AD tenant of Litware. The solution must meet the identity requirements and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
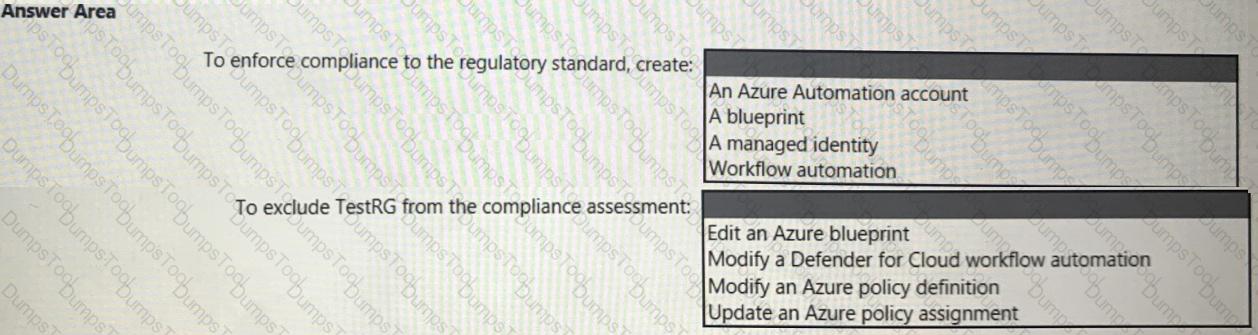
You need to recommend a solution to meet the compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
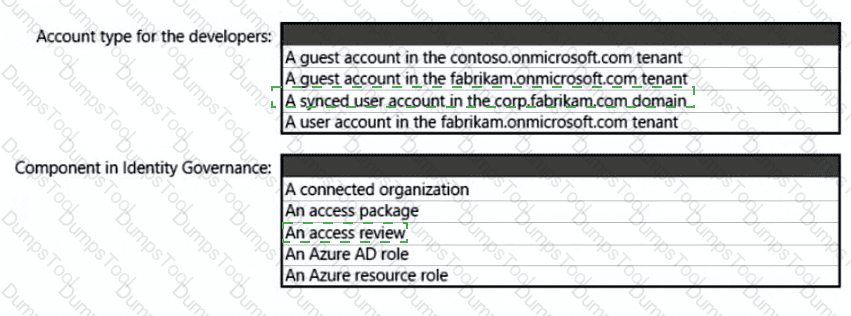
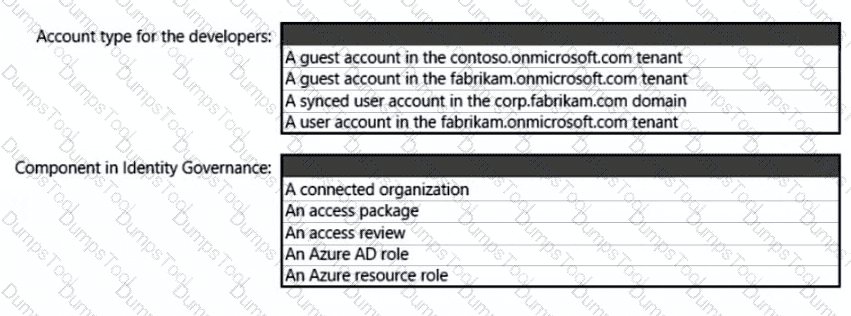
What should you create in Azure AD to meet the Contoso developer requirements?
You need to recommend a solution to scan the application code. The solution must meet the application development requirements. What should you include in the recommendation?
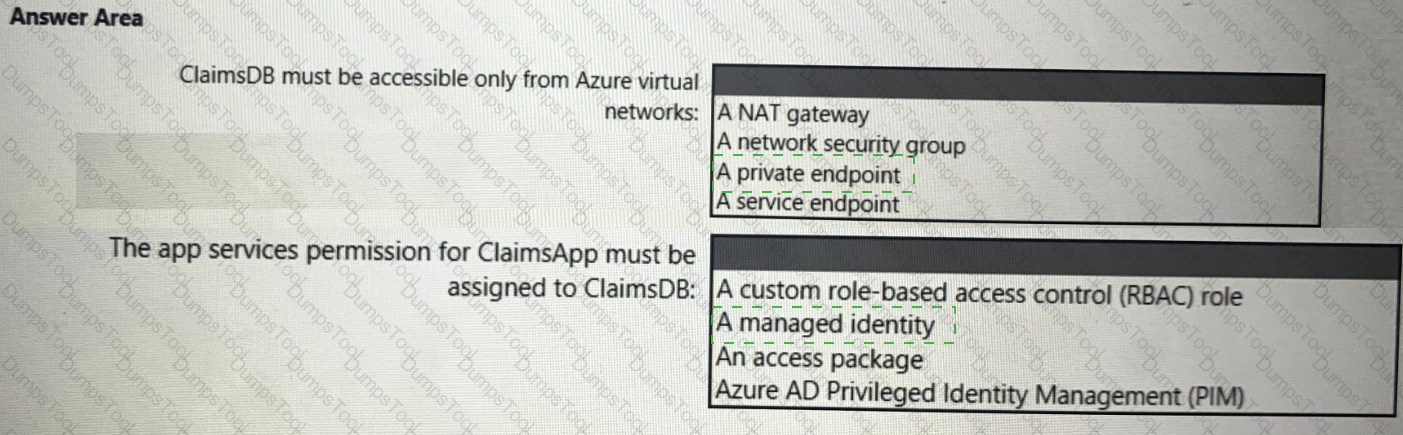
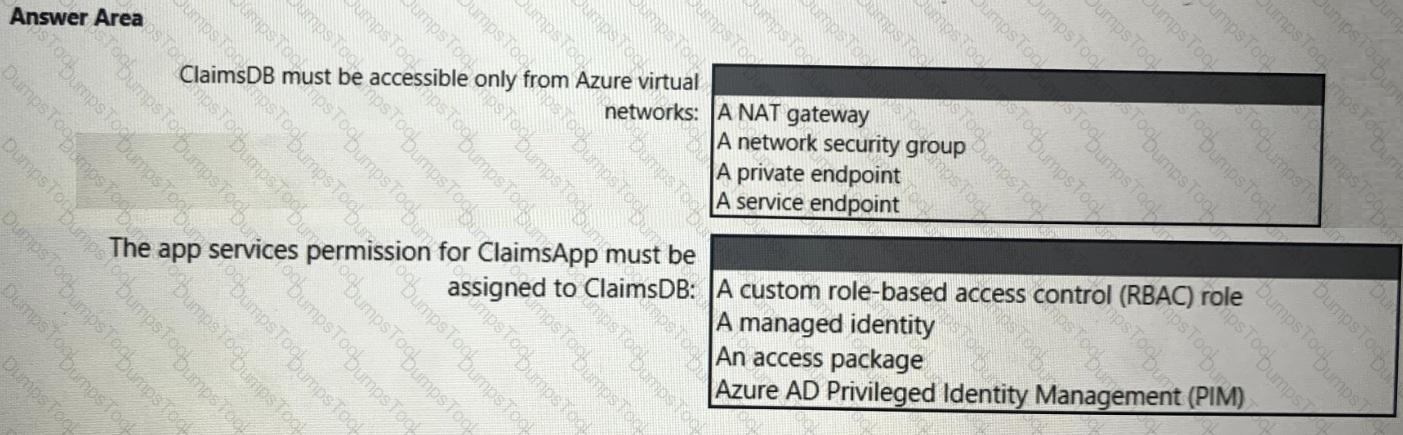
You need to recommend a solution to meet the requirements for connections to ClaimsDB.
What should you recommend using for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
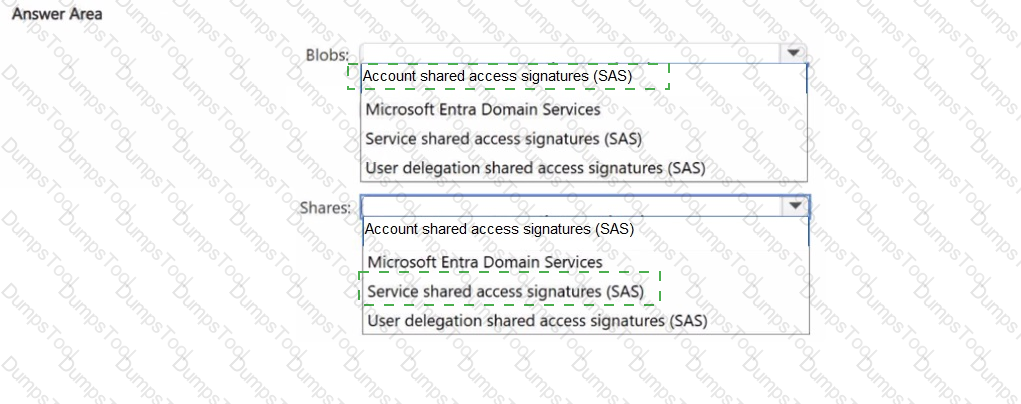
You have an Azure subscription that contains multiple Azure Storage blobs and Azure Files shares.
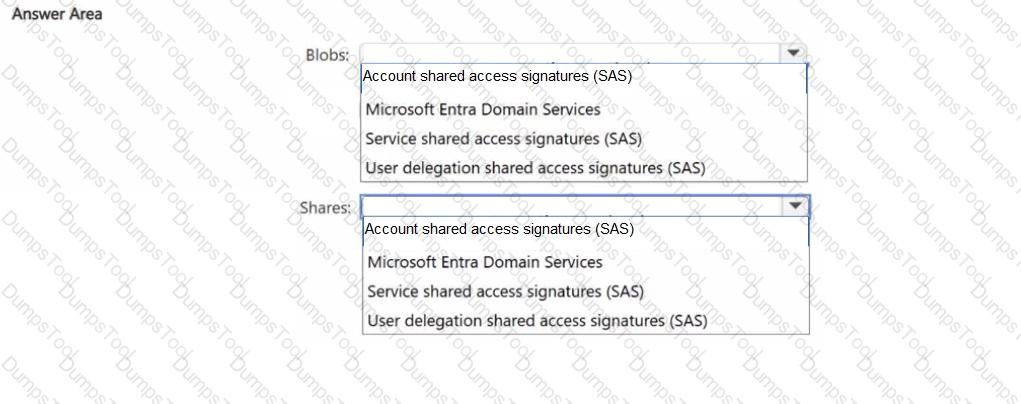
You need to recommend a security solution for authorizing access to the blobs and shares. The solution must meet the following requirements:
• Support access to the shares by using the SMB protocol.
• Limit access to the blobs to specific periods of time.
• Include authentication support when possible.
What should you recommend for each resource? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.
You need to recommend a solution to resolve the virtual machine issue. What should you include in the recommendation? (Choose Two)
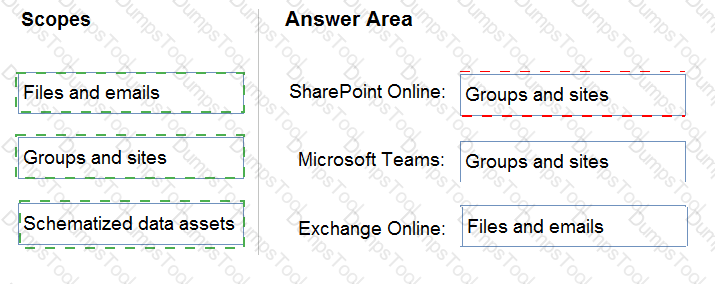
Your company has Microsoft 365 E5 licenses and Azure subscriptions.
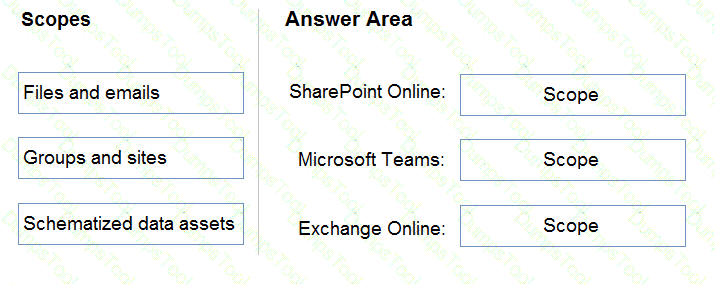
The company plans to automatically label sensitive data stored in the following locations:
• Microsoft SharePoint Online
• Microsoft Exchange Online
• Microsoft Teams
You need to recommend a strategy to identify and protect sensitive data.
Which scope should you recommend for the sensitivity label policies? To answer, drag the appropriate scopes to the correct locations. Each scope may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You have an Azure subscription.
You have a subscription to a third-party cloud provider. The subscription contains 100 virtual machines.
You manage cloud security for both subscriptions from the Azure subscription.
You need to recommend a solution to validate the security posture of the virtual machines.
Which two services should you include in the recommendation? Each correct answer presents part of the solution.
Your network contains an Active Directory Domain Services (AD DS) domain.
You need to ensure that the built-in administrator account for the domain can be used only for interactive sign-ins to domain controllers.
What should you configure?
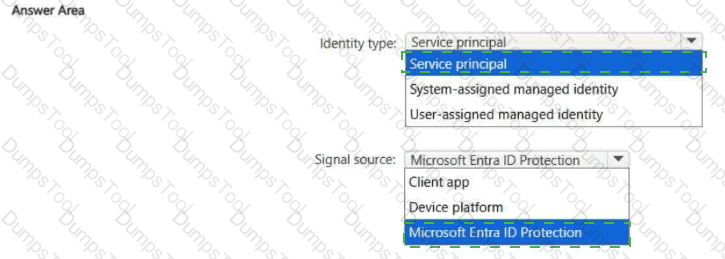
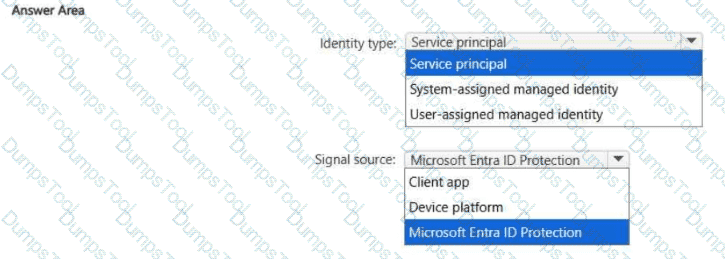
You have a Microsoft Entra tenant and an Azure subscription.
You are evaluating the use of a risk-based Conditional Access policy to control the access of workload identities to resources.
To which type of identity should you apply the policy, and which signal source can you use as part of the policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have an on-premises datacenter and an Azure Kubernetes Service (AKS) cluster named AKS1.
You need to restrict internet access to the public endpoint of AKS 1. The solution must ensure that AKS1 can be accessed only from the public IP addresses associated with the on-premises datacenter.
What should you use?
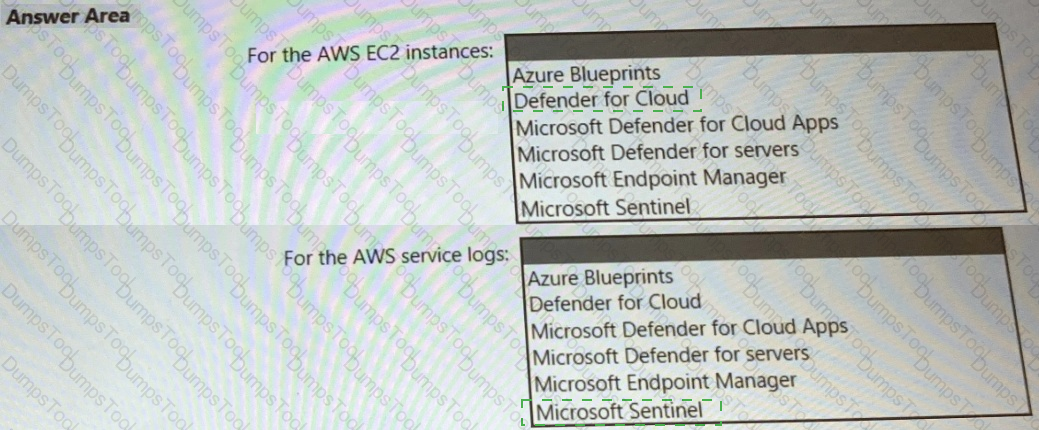
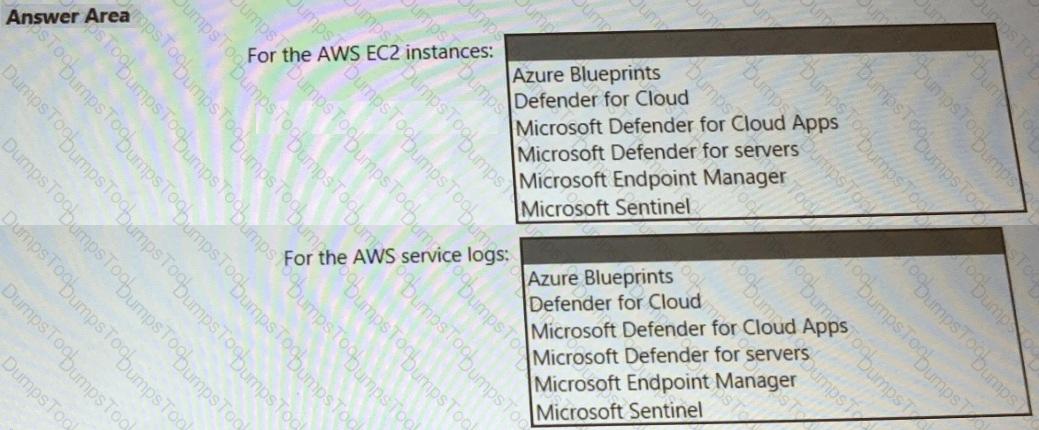
You need to recommend a solution to meet the AWS requirements.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
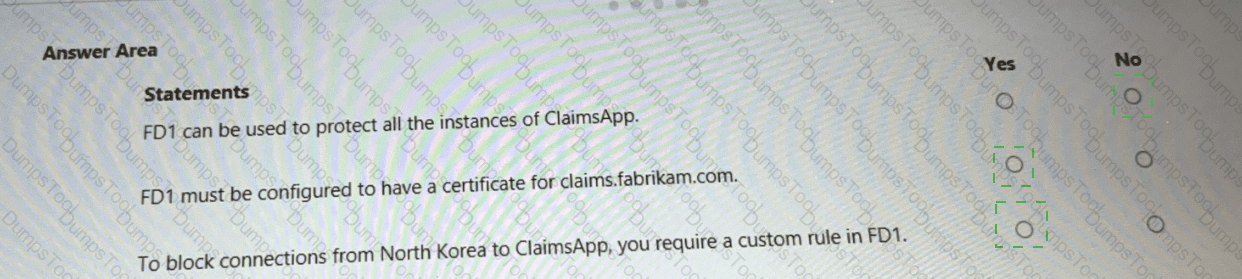
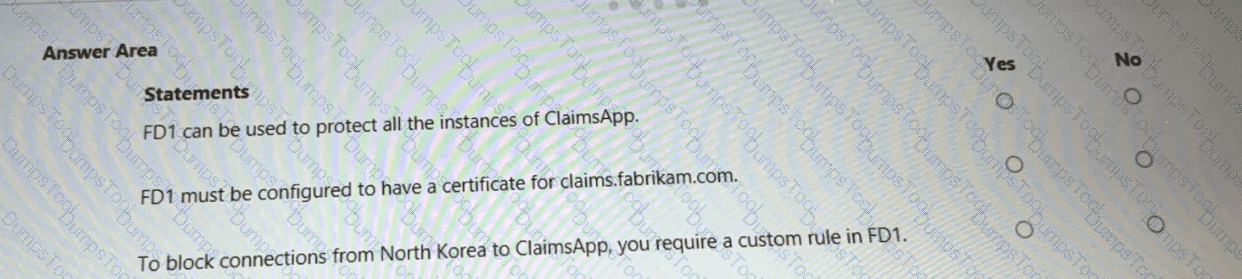
You are evaluating the security of ClaimsApp.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE; Each correct selection is worth one point.
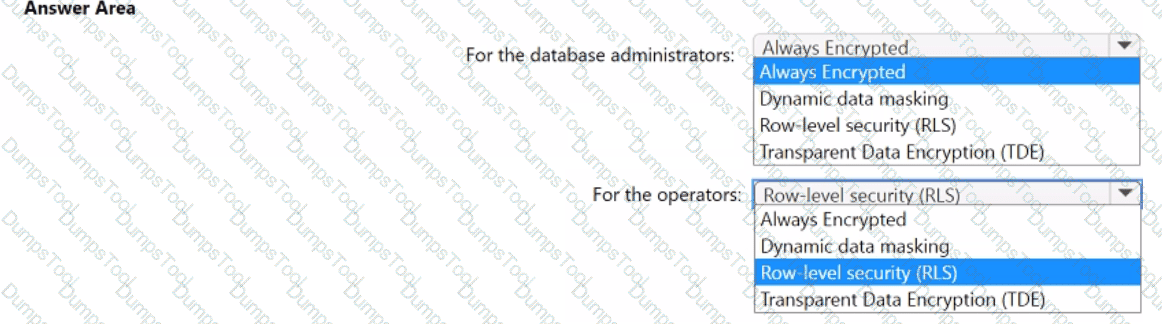
You have an Azure SQL database named DB1 that contains customer information.
A team of database administrators has full access to DB1.
To address customer inquiries, operators in the customer service department use a custom web app named App1 to view the customer information.
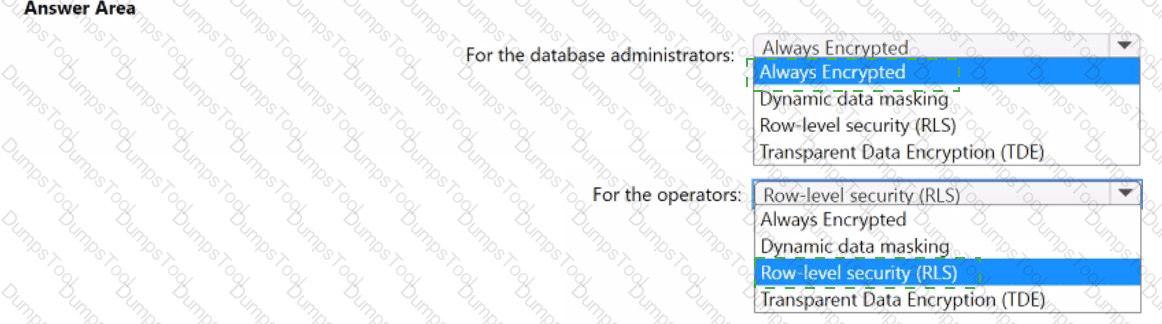
You need to design a security strategy for D81. The solution must meet the following requirements:
• When the database administrators access DB1 by using SQL management tools, they must be prevented from viewing the content of the Credit Card attribute of each customer record.
• When the operators view customer records in App1, they must view only the last four digits of the Credit Card attribute.
What should you include in the design? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
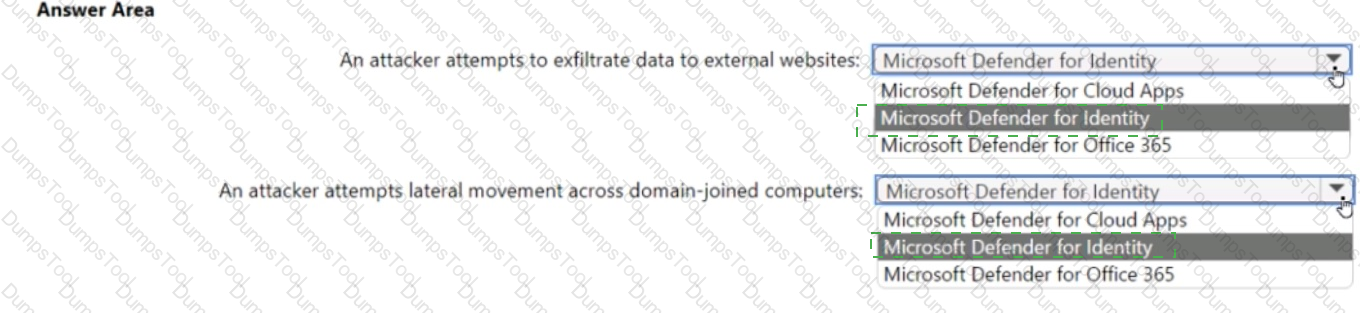
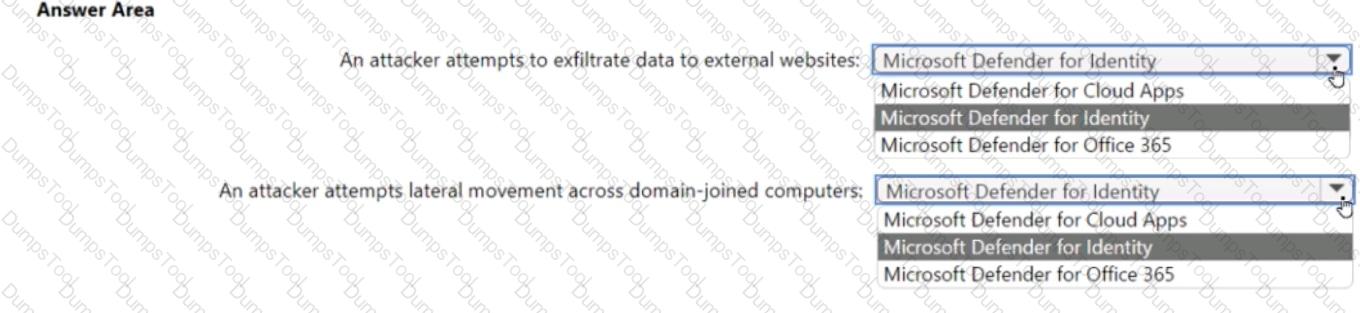
For a Microsoft cloud environment, you are designing a security architecture based on the Microsoft Cybersecurity Reference Architectures (MCRA). You need to protect against the following external threats of an attack chain:
• An attacker attempts to exfiltrate data to external websites.
• An attacker attempts lateral movement across domain-joined computers.
What should you include in the recommendation for each threat? To answer, select the appropriate options in the answer area.
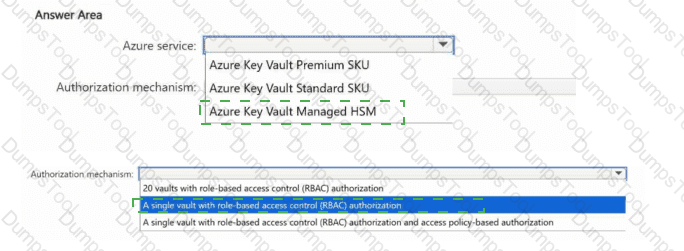
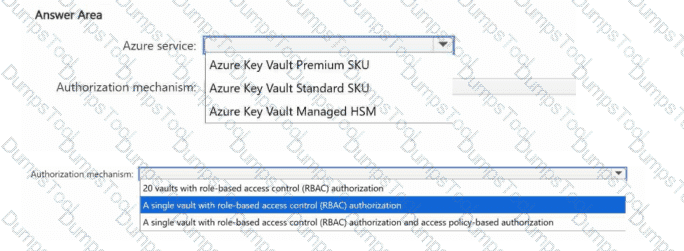
You have an Azure subscription. The subscription contains 20 App Service web apps that provide services to external customers.
Each web app has a unique certificate and key.
You need to recommend a solution to manage the keys and certificates of the web apps. The solution must meet the follow requirements:
Provide a single tenancy to store the keys and certificates.
Maintain FIPS 140-2 Level 3 compliance.
Follow the principle of least privilege.
You have an Azure AD tenant that contains 10 Windows 11 devices and two groups named Group1 and Group2. The Windows 11 devices are joined to the Azure AD tenant and are managed by using Microsoft Intune.
You are designing a privileged access strategy based on the rapid modernization plan (RaMP). The strategy will include the following configurations:
• Each user in Group1 will be assigned a Windows 11 device that will be configured as a privileged access device.
• The Security Administrator role will be mapped to the privileged access security level.
• The users in Group1 will be assigned the Security Administrator role.
• The users in Group2 will manage the privileged access devices.
You need to configure the local Administrators group for each privileged access device. The solution must follow the principle of least privilege.
What should you include in the solution?
Your company has 10 branch offices. Each office has a local internet connection that uses a static IP address.
You have an Azure subscription. The subscription contains a storage account named storage1 that stores blobs.
Users in the branch offices access the blobs via the internet.
You need to recommend a solution to ensure that the data in storage1 is accessible only from the branch office static IP addresses.
The solution must minimize costs.
What should include in the recommendation?
Your network contains an on-premises Active Directory Domain Services (AD DS) domain.
You have a Microsoft 365 subscription.
You need to recommend a solution to evaluate the security and governance of the domains. The solution must meet the following requirements:
• identify configuration issues and administrative vulnerabilities.
• Minimize effort.
What should you include in the recommendation?
You have an Azure subscription that is used as an Azure landing zone for an application. You need to evaluate the security posture of all the workloads in the landing zone. What should you do first?
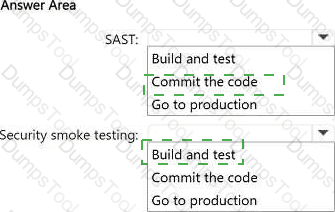
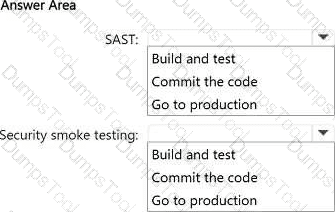
You have an Azure subscription that contains multiple apps. The apps are deployed by using continuous integration and continuous delivery (CI/CD) pipelines in Azure DevOps.
You need to integrate static application security testing (SAST) and security smoke testing into the pipelines based on Microsoft Cloud Adoption Framework for Azure principles.
At which stage of the CI/CID process should each type of test be integrated? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
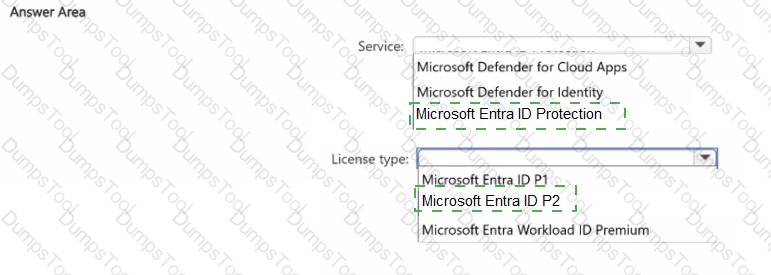
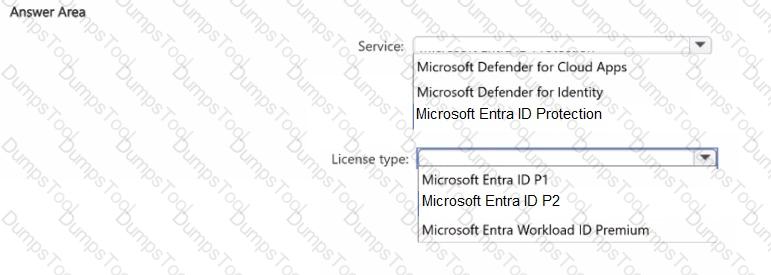
You have a Microsoft Entra tenant that is linked to a Microsoft 365 subscription and an Azure subscription. The tenant contains service principals that are used to access applications in the Azure subscription.
You need to recommend a solution to detect risky sign-ins and other risky activities performed by the service principals in the tenant. The solution must minimize costs.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have a Microsoft 365 tenant.
You have an Azure subscription that contains Azure App Service web apps. The apps have the following characteristics:
• The apps use third-party and open-source components.
• The apps were developed by using C#, Python, and Java.
• The app deployment process is managed by using Azure DevOps.
• The source code for the apps is stored in GitHub Enterprise Cloud repositories and protected by using GitHub Advanced Security.
You need to reduce the risk of supply chain attacks during the application lifecycle.
What should you implement?
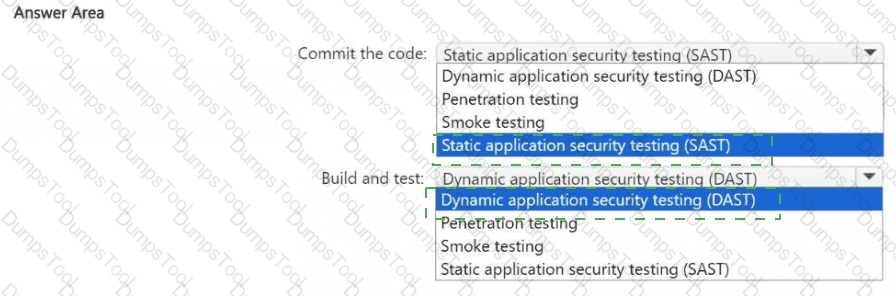
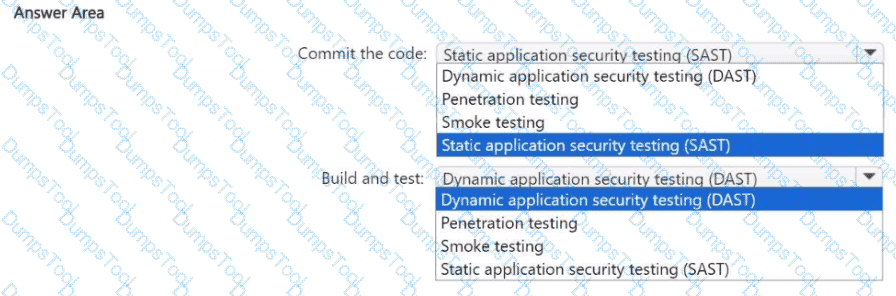
You have an Azure subscription that contains multiple apps. The apps are managed by using continuous integration and continuous deployment (CI/CD) pipelines in Azure DevOps.
You need to recommend DevSecOps controls for the Commit the code and the Build and test CI/CD process stages based on the Microsoft Cloud Adoption Framework for Azure.
Which testing method should you recommend for each stage? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
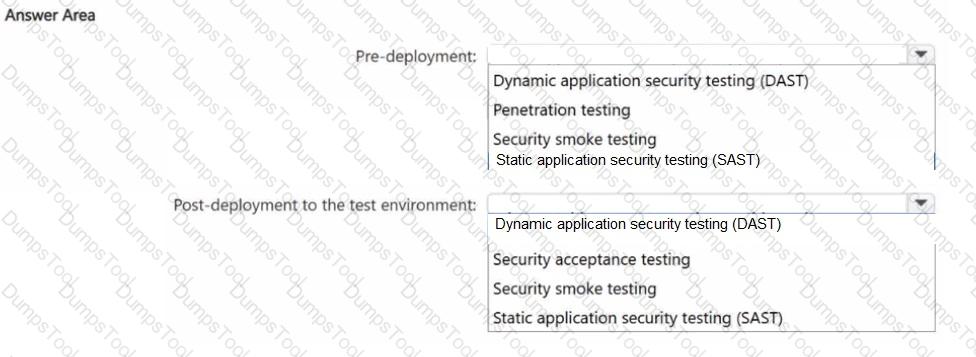
You have an Azure subscription that contains Azure App Service web apps. The apps have the following characteristics:
• The apps are deployed by using continuous integration and continuous deployment (CI/CD) pipelines in Azure DevOps.
• The apps are deployed to a test environment first, and then to a production environment.
• The source code for the apps is stored in Azure Repos.
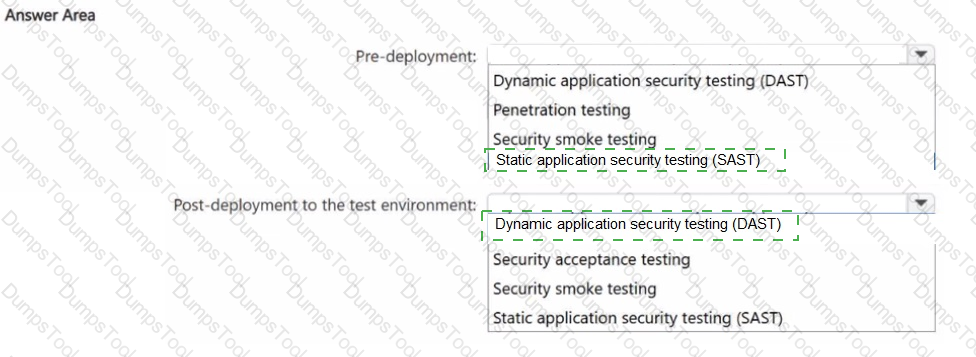
You plan to implement DevSecOps controls based on the Microsoft Cloud Adoption Framework for Azure. You need to recommend testing controls to meet the following requirements:
• All the source code must be tested for security vulnerabilities in Azure Repos before deploying the apps.
• Once the apps are deployed to the test environment they must be tested for security vulnerabilities.
Which testing method should you recommend for each stage? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.
A customer has a hybrid cloud infrastructure that contains a Microsoft 365 E5 subscription and an Azure subscription.
All on-premises Windows servers in the perimeter network are prevented from connecting directly to the internet.
The customer recently recovered from a tansomware attack.
The customer plans to deploy Microsoft Sentinel.
You need to recommend solutions to meet the following requirements:
• Ensure that the security operations team can access the security logs and the operation logs.
• Ensure that the IT operations team can access only the operations logs, including the event logs of the servers in the perimeter network.
Which two solutions should you include in the recommendation? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
You have an operational model based on the Microsoft Cloud Adoption framework for Azure.
You need to recommend a solution that focuses on cloud-centric control areas to protect resources such as endpoints, database, files, and storage accounts.
What should you include in the recommendation?
You have a Microsoft 365 tenant. Your company uses a third-party software as a service (SaaS) app named App1. App1 supports authenticating users by using Azure AO credentials. You need to recommend a solution to enable users to authenticate to App1 by using their Azure AD credentials. What should you include in the recommendation?
Your company has on-premises Microsoft SQL Server databases.
The company plans to move the databases to Azure.
You need to recommend a secure architecture for the databases that will minimize operational requirements for patching and protect sensitive data by using dynamic data masking. The solution must minimize costs.
What should you include in the recommendation?
You are designing a security strategy for providing access to Azure App Service web apps through an Azure Front Door instance. You need to recommend a solution to ensure that the web apps only allow access through the Front Door instance.
Solution: You recommend access restrictions based on HTTP headers that have the Front Door ID.
Does this meet the goal?
Your company has a Microsoft 365 E5 subscription.
The Chief Compliance Officer plans to enhance privacy management in the working environment. You need to recommend a solution to enhance the privacy management. The solution must meet the following requirements:
• Identify unused personal data and empower users to make smart data handling decisions.
• Provide users with notifications and guidance when a user sends personal data in Microsoft Teams.
• Provide users with recommendations to mitigate privacy risks.
What should you include in the recommendation?
You have an Azure subscription that contains 15 custom apps. The source files for the apps are stored in Git repositories. The apps are deployed by using Azure DevOps.
You need to recommend a DevSecOps solution to implement static application security testing (SAST) of the app code to identify hard-coded secrets.
What should you include in the recommendation?
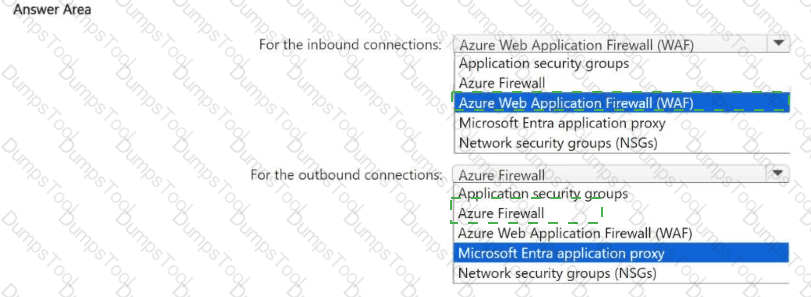
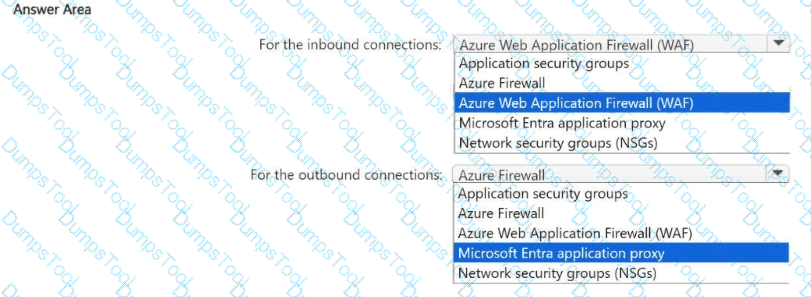
You have an Azure subscription that contains a virtual network named VNet1. VNet1 contains a 10-node virtual machine scale set that hosts a web search app named App1. Customers access App1 from the internet. The nodes establish outbound HTTP and HTTPS connections to the internet.
You need to recommend a network security solution for App1. The solution must meet the following requirements:
• Inbound connections to App1 that contain security threats specified in the Core Rule. Set (CRS) from the Open Web Application Security Project (OWASP) must be blocked.
• Outbound HTTP and HTTPS connections from the virtual machine scale set that contain security threats identified by the Microsoft Defender Threat Intelligence (Defender Tl) feed must be blocked.
What should you include in the recommendation? To answer, select the options in the answer area,
NOTE: Each correct answer is worth one point.
You have an Azure subscription.
Your company has a governance requirement that resources must be created in the West Europe or North Europe Azure regions.
What should you recommend using to enforce the governance requirement?
A customer follows the Zero Trust model and explicitly verifies each attempt to access its corporate applications.
The customer discovers that several endpoints are infected with malware.
The customer suspends access attempts from the infected endpoints.
The malware is removed from the end point.
Which two conditions must be met before endpoint users can access the corporate applications again? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft 365 subscription that uses Microsoft Defender XDR. The subscription contains 500 devices that are enrolled in Microsoft Intune. The subscription contains 500 users that connect to external software as a service (SaaS) apps by using the devices.
You need to implement a solution that meets the following requirements:
• Allows user access to SaaS apps that Microsoft has identified as low risk.
• Blocks user access to Saas apps that Microsoft has identified as high risk.
Solution: You configure app protection policies in Intune, and you create a Conditional Access policy.
Does this meet the goal?
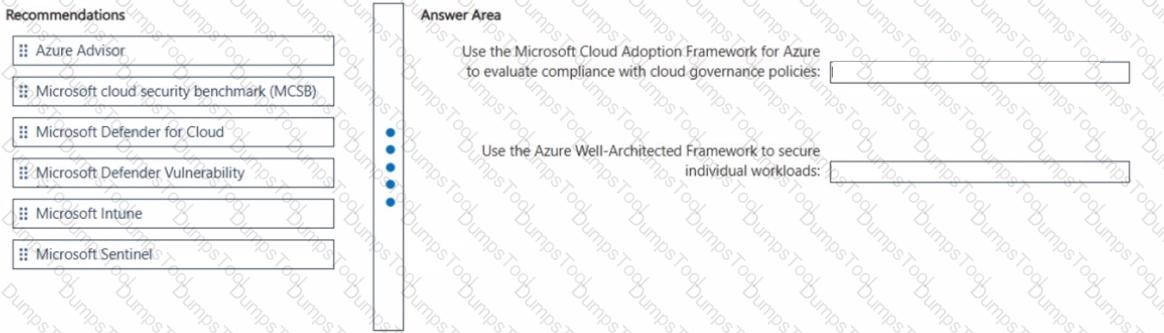
You have an Azure environment that contains multiple workloads deployed across multiple subscriptions.
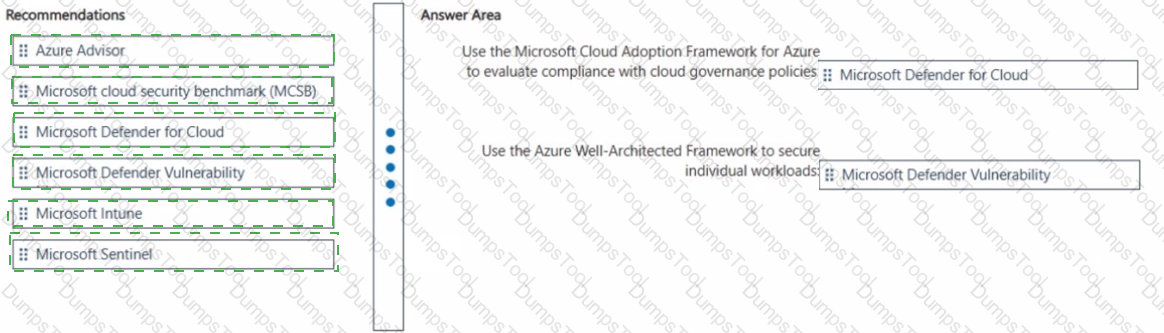
You need to recommend a solution to assess and improve the security posture of the workloads. The solution must meet the following requirements:
• Use the Microsoft Cloud Adoption Framework for Azure to evaluate compliance with cloud governance policies.
• Use the Azure Well-Architected Framework to secure individual workloads.
What should you include in the recommendation for each requirement? To answer, drag the appropriate recommendations to the correct requirements. Each recommendation may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content
NOTE: Each correct selection is worth one point.
Your company is designing an application architecture for Azure App Service Environment (ASE) web apps as shown in the exhibit. (Click the Exhibit tab.)
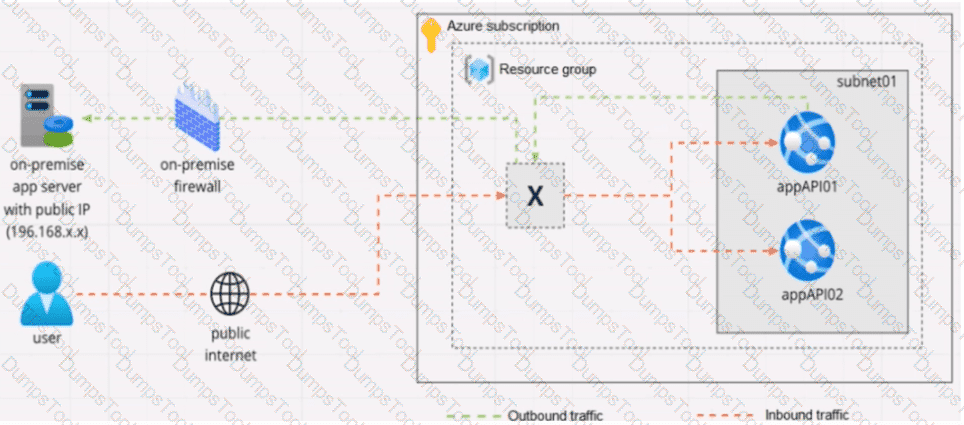
Communication between the on-premises network and Azure uses an ExpressRoute connection.
You need to recommend a solution to ensure that the web apps can communicate with the on-premises application server. The solution must minimize the number of public IP addresses that are allowed to access the on-premises network.
What should you include in the recommendation?
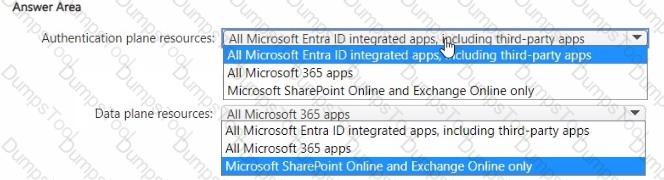
You have a Microsoft 365 E5 subscription.
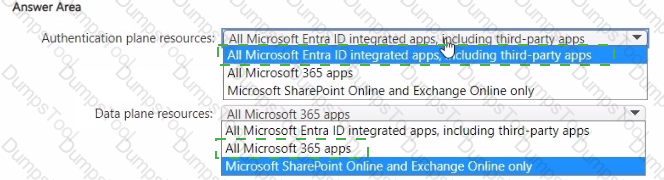
You plan to deploy Global Secure Access universal tenant restrictions v2.
Which authentication plane resources and which data plane resources will be protected? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
TESTED 26 Oct 2026