dumpstool logo
An organization is measuring the effectiveness of its change management program to reduce the number of unplanned production changes. Which of the following would be the BEST metric to determine if the program is performing as expected?
Decrease in the time to move changes to production
Ratio of emergency fixes to total changes
Ratio of system changes to total changes
Decrease in number of changes without a fallback plan
The ratio of emergency fixes to total changes is the best metric to determine if the change management program is performing as expected, because it reflects the quality and stability of the changes that are implemented in the production environment. A high ratio of emergency fixes to total changes indicates that the change management program is not effective, as it means that many changes are causing problems or failures that require urgent correction. A low ratio of emergency fixes to total changes indicates that the change management program is effective, as it means that most changes are well-planned, tested, and approved, and do not cause significant disruptions or defects. The ratio of emergency fixes to total changes can also help identify the root causes of the problems, the gaps in the change management process, and the areas for improvement. For example, if the ratio of emergency fixes to total changes is high, it may indicate that the change management program has issues with the following aspects: - Change request and approval: The change management program may not have a clear and consistent process for requesting, reviewing, and approving changes, or the process may not be followed by all stakeholders. - Change impact analysis: The change management program may not have acomprehensive and systematic method for assessing the potential impact of the changes on thebusiness processes, the IT systems, the users, and the customers. - Change testing and validation: The change management program may not have adequate testing and validation procedures to ensure that the changes meet the requirements and specifications, and do not introduce errors or vulnerabilities. - Change communication and training: The change management program may not have effective communication and training strategies to inform and educate the affected parties about the changes and their implications. - Change implementation and monitoring: The change management program may not have proper implementation and monitoring plans or tools to ensure that the changes are executed smoothly and successfully, and that any issues or incidents are detected and resolved promptly. Therefore, the ratio of emergency fixes to total changes is the best metric to determine if the change management program is performing as expected, as it can provide valuable feedback and insights for the change management program and its improvement. References = How to Measure Change Management Effectiveness: Metrics, Tools & Processes1, Metrics for Measuring Change Management2, Driving Value with Change Management Metrics3, Must-Know Organizational Change Management Metrics
Which of the following is the PRIMARY benefit of using a risk map with stakeholders?
Consolidates risk response options by severity
Aligns risk appetite with business objectives
Correlates risk scenarios to risk appetite
Defines an organizational risk taxonomy
Arisk maphelps stakeholders understand how risk scenarios align with the organization’srisk appetite. This visualization facilitates informed decision-making and ensures risk responses are consistent with organizational priorities.
===========
The BEST way for management to validate whether risk response activities have been completed is to review:
the risk register change log.
evidence of risk acceptance.
control effectiveness test results.
control design documentation.
Reviewing the risk register change log is the best way for management to validate whether risk response activities have been completed, because it helps to track and monitor the changes and updates that have been made to the risk register, and to verify that the risk response activities have been implemented and closed. A risk register is a document that captures, identifies, assesses and tracks risk as part of the risk management process4. A risk register change log is a record that documents the date, description, and reason for each change or update that is made to the risk register. A risk response activity is an action or task that is performed to implement the chosen risk response strategy for a specific risk, such as avoid, transfer, mitigate, or accept. Reviewing the risk register change log is the best way, as it helps to ensure that the risk register is accurate and current, and that the risk response activities have been completed and reported. Reviewing evidence of risk acceptance, control effectiveness test results, and control design documentation are all possible ways to validate whether risk response activities have been completed, but they are not the best way, as they may not cover all the risk response activities, and they may not reflect the changes or updates in the risk register. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.4.1, page 101
A risk practitioner has discovered a deficiency in a critical system that cannot be patched. Which of the following should be the risk practitioner ' s FIRST course of action?
Report the issue to internal audit.
Submit a request to change management.
Conduct a risk assessment.
Review the business impact assessment.
The first course of action for a risk practitioner when discovering a deficiency in a critical system that cannot be patched is to conduct a risk assessment. A risk assessment is a process of identifying, analyzing, and evaluating the risks that could affect the achievement of the objectives of the system or the organization. A risk assessment helps to determine the level and nature of the risk exposure, and to prioritize and respond to the risks. Conducting a risk assessment is the first course of action, as it helps to understand the source, cause, and impact of the deficiency, and to estimate the likelihood and consequences of the risk events that could exploit the deficiency. Conducting a risk assessment also helps to identify and evaluate the existing or potential controls or mitigations that could address the deficiency, and to recommend the appropriate risk treatment options. Reporting the issue to internal audit, submitting a request to change management, and reviewing the business impact assessment are not the first courses ofaction, as they are either the outputs or the inputs of the risk assessment process, and they do not address the primary need of assessing the risk situation and status. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 49.
A risk practitioner has identified that the agreed recovery time objective (RTO) with a Software as a Service (SaaS) provider is longer than the business expectation. Which ot the following is the risk practitioner ' s BEST course of action?
Collaborate with the risk owner to determine the risk response plan.
Document the gap in the risk register and report to senior management.
Include a right to audit clause in the service provider contract.
Advise the risk owner to accept the risk.
The best course of action for the risk practitioner who has identified that the agreed RTO with a SaaS provider is longer than the business expectation is to collaborate with the risk owner to determine the risk response plan. The risk owner is the person who has the authority and accountability to manage the risk within their scope of responsibility. The risk response plan is the document that describes the actions and resources needed to address the risk. By collaborating with the risk owner, the risk practitioner can help toanalyze the gap between the agreed RTO and the business expectation, evaluate the potential impact and consequences, and select the most appropriate risk response option, such as avoiding, reducing, transferring, or accepting the risk. Documenting the gap in the risk register, including a right to audit clause in the service provider contract, or advising the risk owner to accept the risk are not the best courses of action, because they do not address the root cause of the problem, or provide a solution to reduce the risk to an acceptable level. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-23.
Which of the following would BEST provide early warning of a high-risk condition?
Risk register
Risk assessment
Key risk indicator (KRI)
Key performance indicator (KPI)
A key risk indicator (KRI) is a metric that provides information on the level of exposure to a given risk or the potential impact of a risk. KRIs are used to monitor changes in risk levels and alert management when a risk exceeds a predefined threshold or tolerance. KRIs can help provide early warning of a high-risk condition and enable timely response and mitigation actions. A risk register is a tool that records and tracks the identified risks, their likelihood, impact, and status. A risk assessment is a process that identifies, analyzes, andevaluates risks. A key performance indicator (KPI) is a metric that measures the achievement of a specific goal or objective. References = Risk IT Framework, pages 22-231; CRISC Review Manual, pages 44-452
An organization has initiated a project to implement an IT risk management program for the first time. The BEST time for the risk practitioner to start populating the risk register is when:
identifying risk scenarios.
determining the risk strategy.
calculating impact and likelihood.
completing the controls catalog.
According to the CRISC Review Manual1, the risk register is a tool that records the results of risk identification, analysis, evaluation, and treatment. The risk register should be populated as soon as possible in the risk management process, to capture and document the risks and their attributes. The best time for the risk practitioner to start populating the risk register is when identifying risk scenarios, as this is the first step in the risk identification process. Risk scenarios are hypothetical situations that describe the potential causes, impacts, and responses of a risk event. Identifying risk scenarios helps to generate a comprehensive and relevant list of risks that can be recorded in the risk register. References = CRISC Review Manual1, page 191, 206.
Which of the following BEST facilitates the process of documenting risk tolerance?
Creating a risk register
Interviewing management
Conducting a risk assessment
Researching industry standards
Interviewing managementis key because risk tolerance reflects leadership’s perspective on acceptable risk levels. ISACA stresses that understanding risk tolerance requires direct input from those responsible for risk decisions and strategic direction.
A MAJOR advantage of using key risk indicators (KRIs) is that they:
Identify scenarios that exceed defined risk appetite.
Help with internal control assessments concerning risk appetite.
Assess risk scenarios that exceed defined thresholds.
Identify when risk exceeds defined thresholds.
KRIs provide measurable indicators that flag when risks exceed predefined thresholds, enabling swift and effective risk response. This supports theMonitoring and Reportingfunction in risk management, ensuring risks are managed proactively.
To help ensure the success of a major IT project, it is MOST important to:
obtain the appropriate stakeholders ' commitment.
align the project with the IT risk framework.
obtain approval from business process owners.
update the risk register on a regular basis.
Which of the following is the GREATEST risk associated with the misclassification of data?
inadequate resource allocation
Data disruption
Unauthorized access
Inadequate retention schedules
According to the CRISC Review Manual, the greatest risk associated with the misclassification of data is unauthorized access, because it can result in the loss of confidentiality, integrity, and availability of the data. Data classification is the process of assigning categories to data based on its sensitivity and value to the organization. Data classification helps to determine the appropriate level of protection and handling for the data. If the data is misclassified, it may not receive the adequate level of security controls, and it may be accessed by unauthorized or inappropriate users. The other options are not the greatest risks associated with the misclassification of data, as they are less likely or less severe than unauthorized access. Inadequate resource allocation is the risk of not allocating sufficient resources to protect the data, which may affect its availability and performance. Data disruption is the risk of losing or corrupting the data, which may affect its integrity and availability. Inadequate retention schedules is the risk of not retaining the data forthe required period of time, which may affect its compliance and usability. References = CRISC Review Manual, 7th Edition, Chapter 4, Section 4.1.1, page 161.
What is the PRIMARY reason an organization should include background checks on roles with elevated access to production as part of its hiring process?
To eliminate risk associated with personnel
To reduce internal threats
To ensure new hires have the required skills
To reduce exposure to vulnerabilities
The correct answer is B because the primary reason for conducting background checks on individuals who will have elevated access to production systems is to reduce internal threats . Personnel with privileged access can significantly affect confidentiality, integrity, and availability. Background screening is a preventive governance and personnel security control intended to lower the likelihood of insider misuse, fraud, abuse of privilege, or other harmful actions.
The other options are less appropriate:
A. To eliminate risk associated with personnel is incorrect because risk cannot be fully eliminated.
C. To ensure new hires have the required skills is handled more directly through recruitment, vetting, and qualification review, not primarily through background checks.
D. To reduce exposure to vulnerabilities is too indirect; vulnerabilities are weaknesses in systems or controls, while this question is about personnel risk.
Exact Extracts supporting the answer:
“The MOST effective measure against insider threats to confidential information is role-based access control.”
“The PRIMARY reason that an enterprise would establish segregation of duties controls is to prevent errors or fraudulent activity on high-risk transactions.”
“The control that focuses directly on preventing the risk of collusion is mandatory job rotation.”
“The MOST concern to the risk practitioner regarding applications running in production is backdoors.”
These extracts support that elevated access roles create significant internal threat exposure and require preventive controls focused on reducing insider risk. Therefore, the primary reason for background checks is to reduce internal threats .
===========
QUESTION NO: 91 [Risk Assessment]
Which of the following would be MOST helpful to review when prioritizing the implementation of multiple IT-related initiatives?
A. Risk awareness program objectives
B. Risk assessment results
C. Risk profile
D. Risk policy
Answer: C
The correct answer is C because the risk profile provides the most useful enterprise-level view when prioritizing multiple IT-related initiatives. It reflects the aggregated level of risk facing the organization, helps identify which exposures are most significant, and supports comparison across initiatives based on business impact, likelihood, and current exposure.
The other options are less useful for prioritization at this level:
A. Risk awareness program objectives relate to culture and communication, not implementation prioritization.
B. Risk assessment results are important, but the risk profile is more useful when consolidating and prioritizing across multiple initiatives.
D. Risk policy sets direction and expectations, but it does not provide the comparative view needed for prioritization.
Exact Extracts supporting the answer:
“The most important aspect to consider in relation to a risk profile is the aggregated risk to the enterprise.”
“The main purpose of risk monitoring is to provide timely information on the actual status of the enterprise with regard to risk with the risk profile offering an overall risk status.”
“When reporting the status of the IT control environment to management the most important component is the risk profile of the enterprise.”
“The PRIMARY result of a risk assessment process is input for risk-aware decisions.”
These extracts show that the risk profile is the best consolidated basis for prioritizing multiple IT-related initiatives.
===========
QUESTION NO: 92 [Risk and Control Monitoring and Reporting]
Which of the following attributes of data provided to an automated log analysis tool is MOST important for effective risk monitoring?
A. Confidentiality
B. Scalability
C. Retention
D. Relevancy
Answer: D
The correct answer is D because the most important attribute of data fed into an automated log analysis tool is relevancy . For effective risk monitoring, the tool must receive data that is meaningful, useful, and directly related to the risks, events, controls, and activities being monitored. Irrelevant data reduces signal quality, obscures important indicators, and weakens timely detection.
The other options are less important for monitoring effectiveness itself:
A. Confidentiality is important for protecting the data, but it does not by itself make the monitoring effective.
B. Scalability is a system capability, not a core attribute of the data itself.
C. Retention is important for historical review and forensics, but not the most important factor for effective real-time or ongoing monitoring.
Exact Extracts supporting the answer:
“If the correct information was not received by the necessary recipients in time to allow proper action this can be categorized as relevance risk.”
“The most important consideration when implementing key risk indicators is linking the metric to a specific risk.”
“The MOST essential criterion for the effectiveness of operational metrics is relevance to the recipient.”
“The main purpose of continuous monitoring is detecting changes to the enterprise’s risk environment.”
These extracts directly support that relevant information is essential for useful monitoring and effective action. Therefore, relevancy is the most important attribute.
===========
QUESTION NO: 93 [Risk Assessment]
In the context of a business impact analysis (BIA) which of the following activities would be MOST complex and time-consuming for a risk practitioner in a large global organization?
A. Calculating recovery time objectives (RTOs)
B. Analyzing the financial impact of a disruption
C. Analyzing the interdependences between business departments
D. Identifying critical IT business processes and procedures
Answer: C
The correct answer is C because in a large global organization, the most complex and time-consuming BIA activity is analyzing the interdependencies between business departments . Large enterprises have numerous cross-functional, regional, operational, legal, and technical dependencies. Understanding how disruption in one area affects another is often the most difficult and resource-intensive part of a business impact analysis.
The other options are important, but generally less complex in a large global environment:
A. Calculating recovery time objectives (RTOs) is important, but it is usually derived after understanding process criticality and dependencies.
B. Analyzing the financial impact of a disruption can be difficult, but interdependency mapping is often broader and more complicated.
D. Identifying critical IT business processes and procedures is foundational, but in a global organization the network of dependencies is typically the harder task.
Exact Extracts supporting the answer:
“The objective of a business impact analysis is best described as the identification of time-sensitive critical business functions and interdependencies.”
“The most useful process in developing a series of recovery time objectives is business impact analysis.”
“A business impact analysis is primarily used to evaluate the impact of disruption on an enterprise’s ability to operate over time.”
“The main outcome of a business impact analysis (BIA) is the criticality of business processes.”
These extracts show that identifying interdependencies is central to BIA. In a large global organization, that makes it the most complex and time-consuming activity.
===========
QUESTION NO: 94 [Risk and Control Monitoring and Reporting]
Which of the following criteria is MOST important to include in an agreement with a penetration testing vendor?
A. Details of testing methods to be used
B. Expectations of code escrow safeguards
C. Scope of the systems to be assessed
D. Steps to remediate identified vulnerabilities
Answer: C
The correct answer is C because the most important criterion to include in an agreement with a penetration testing vendor is the scope of the systems to be assessed . Clear scope is essential to define what is authorized, what assets may be tested, what environments are in scope, and what boundaries apply. Without a clearly defined scope, testing could miss key assets or unintentionally affect systems that were not authorized for assessment.
The other options are less important as the primary agreement requirement:
A. Details of testing methods to be used are useful, but they come after scope is clearly established.
B. Expectations of code escrow safeguards are unrelated to most penetration testing agreements.
D. Steps to remediate identified vulnerabilities may follow from the test results, but they are not the most important initial contractual criterion.
Exact Extracts supporting the answer:
“Prior to conducting a penetration test the most important step is obtaining senior management approval of exercise parameters.”
“Before beginning a black box penetration test it ' s crucial to have a clearly stated definition of scope in place.”
“To best preserve service availability during a penetration test it ' s essential to schedule testing of critical systems during maintenance windows.”
“For an Internet-facing application penetration testing is the most effective control assessment type.”
These extracts directly support that clear scope is the most important criterion in an agreement with a penetration testing vendor.
Which of the following provides the MOST reliable evidence to support conclusions after completing an information systems controls assessment?
Risk and control self-assessment (CSA) reports
Information generated by the systems
Control environment narratives
Confirmation from industry peers
The source that provides the most reliable evidence to support conclusions after completing an information systems controls assessment is the information generated by the systems, as it reflects the actual and objective data and results of the system operations and performance, and can be verified and tested against the control objectives and criteria. The other options are not the most reliable sources, as they may be subjective, biased, or incomplete, and may not reflect theactual or current state of the system controls, respectively. References = CRISC Review Manual, 7th Edition, page 154.
Senior management has requested more information regarding the risk associated with introducing a new application into the environment. Which of the following should be done FIRST?
Perform an audit.
Conduct a risk analysis.
Develop risk scenarios.
Perform a cost-benefit analysis.
Understanding Risk Analysis:
Risk analysis involves identifying potential risks associated with a new application and assessing their likelihood and impact on the organization.
It provides a detailed understanding of the potential threats, vulnerabilities, and consequences, enabling informed decision-making.
Steps in Conducting a Risk Analysis:
Identify Risks:Determine what risks could arise from the new application, including security vulnerabilities, compliance issues, and operational disruptions.
Assess Risks:Evaluate the likelihood and impact of each identified risk. This includes both qualitative and quantitative assessments.
Prioritize Risks:Rank the risks based on their assessed impact and likelihood to focus on the most significant threats first.
Importance of Risk Analysis:
Provides senior management with a comprehensive view of the risks involved, enabling them to make informed decisions about proceeding with the application.
Helps in developing mitigation strategies to address the identified risks.
Comparing Other Options:
Perform an Audit:Audits are useful for evaluating existing controls but are not the first step in assessing risks for a new application.
Develop Risk Scenarios:This is part of the risk analysis process but comes after identifying and assessing risks.
Perform a Cost-Benefit Analysis:Important for decision-making but follows the initial risk analysis to understand potential impacts.
References:
The CRISC Review Manual emphasizes the importance of conducting a risk analysis to understand and manage risks associated with new applications (CRISC Review Manual, Chapter 2: IT Risk Assessment, Section 2.2.1 Conducting Risk Analysis).
Which of the following provides the MOST useful information to determine risk exposure following control implementations?
Strategic plan and risk management integration
Risk escalation and process for communication
Risk limits, thresholds, and indicators
Policies, standards, and procedures
Risk limits, thresholds, and indicators provide the most useful information to determine risk exposure following control implementations, as they help to measure and monitor the current and residual risk levels and compare them with the desired and acceptable risk levels. Risk limits, thresholds, and indicators are defined as follows:
Risk limits are the maximum amount of risk that an organization is willing to accept for a given activity, process, or objective. Risk limits are derived from the organizational risk appetite and tolerance, and they help to guide the risk response and control selection.
Risk thresholds are the points or levels at which the risk or performance is acceptable or unacceptable. Risk thresholds are used to trigger alerts, actions, or escalation when the risk or performance deviates from the expected or planned range.
Risk indicators are metrics or measures that provide information on the current or potential risk exposure or performance. Risk indicators can be classified into key risk indicators (KRIs), whichmeasure the likelihood and impact of risk events, and key performance indicators (KPIs), which measure the effectiveness and efficiency of controls and processes.
Risk limits, thresholds, and indicators help to determine risk exposure following control implementations by providing quantitative and qualitative data and feedback on the risk and control environment. They also help to identify and prioritize the areas for improvement and enhancement of the risk and control environment. Risk limits, thresholds, and indicators also facilitate the communication, collaboration, and accountability among the stakeholders involved in the risk management and control processes.
The other options are not the most useful information to determine risk exposure following control implementations. Strategic plan and risk management integration is the process of aligning the organizational strategy and objectives with the risk management framework and activities, but it does not provide specific information on the risk exposure or control effectiveness. Risk escalation and process for communication is the process of reporting and escalating the risk issues and incidents to the appropriate authority and stakeholders, but it doesnot provide comprehensive information on the risk exposure or control performance. Policies, standards, and procedures are the documents that define the principles, rules, and guidelines for the risk management and control processes, but they do not provide actual information on the risk exposure or control implementation. References = Risk Limits, Thresholds and Indicators - ISACA, IT Risk Resources | ISACA, Risk Management: Risk Indicators and Risk Appetite
Which of the following provides the MOST useful information for developing key risk indicators (KRIs)?
Business impact analysis (BIA) results
Risk scenario ownership
Risk thresholds
Possible causes of materialized risk
Key risk indicators (KRIs) are metrics that provide an early warning of increasing risk exposure in various areas of the organization. They help to monitor changes in the level of risk and enable timely actions to mitigate the risk. The most useful information for developing KRIs is the possible causes of materialized risk, which are the factors or events that trigger or contribute to the occurrence of a risk. By identifying the possible causes of materialized risk, an organization can design KRIs that measure the likelihood and impact of the risk, and alert the management when the risk exceeds the acceptable level. References = CRISC Review Manual, 7th Edition, page 101.
A compensating control is MOST appropriate when:
Management wants to increase the number of controls.
A vulnerability is identified.
Existing controls are inadequate.
A key control is already in place and operating effectively.
A compensating control addresses risk when the primary control cannot meet the required objectives due to practical constraints.
Within the three lines of defense model, the responsibility for managing risk and controls resides with:
operational management.
the risk practitioner.
the internal auditor.
executive management.
According to the three lines of defense model, the responsibility for managing risk and controls resides with the operational management, which forms the first line of defense. The operational management is the function that owns and manages risk as part of their accountability for achieving objectives. They are responsible for identifying, assessing, mitigating, and reportingon risks and controls within their areas ofoperation. They are also responsible for implementing and maintaining effective internal controls and ensuring compliance with policies, standards, and regulations.
Which stakeholders are PRIMARILY responsible for determining enterprise IT risk appetite?
Audit and compliance management
The chief information officer (CIO) and the chief financial officer (CFO)
Enterprise risk management and business process owners
Executive management and the board of directors
The stakeholders who are PRIMARILY responsible for determining enterprise IT risk appetite are the executive management and the board of directors, because they are the ones who set thestrategic direction and objectives of the enterprise, and who define the acceptable level of risk exposure and tolerance for achieving those objectives. The other options are not the primary stakeholders, because:
Option A: Audit and compliance management are responsible for providing assurance and oversight on the effectiveness of the risk management process and the compliance with internal and external requirements, but they do not determine the enterprise IT risk appetite.
Option B: The CIO and the CFO are responsible for managing the IT resources and the financial resources of the enterprise, respectively, but they do not determine the enterprise IT risk appetite.
Option C: Enterprise risk management and business process owners are responsible for identifying, assessing, and responding to the risks that affect their domains, but they do not determine the enterprise IT risk appetite. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 83.
An organization has outsourced its customer management database to an external service provider. Of the following, who should be accountable for ensuring customer data privacy?
The organization ' s business process owner
The organization ' s information security manager
The organization ' s vendor management officer
The vendor ' s risk manager
Which of the following is the MOST effective way to incorporate stakeholder concerns when developing risk scenarios?
Evaluating risk impact
Establishing key performance indicators (KPIs)
Conducting internal audits
Creating quarterly risk reports
The most effective way to incorporate stakeholder concerns when developing risk scenarios is to evaluate the risk impact. Risk impact is the extent of the potential consequences or losses that may result from arisk event. Evaluating the risk impact involves considering the stakeholder concerns, expectations, and perspectives, as they may have different views on the value of the assets, the severity of the threats, and the acceptability of the outcomes. Evaluating the risk impact can help to ensure that the risk scenarios reflect the stakeholder interests and priorities, and that the risk responses are aligned with the stakeholder objectives. Establishing key performance indicators (KPIs), conducting internal audits, and creating quarterly risk reports are not as effective as evaluating the risk impact, as they are not directly related to the development of risk scenarios, and may not capture the stakeholder concerns adequately. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 50.
An organization ' s finance team is proposing the adoption of a blockchain technology to provide a secure method for moving funds. Which of the following should the risk practitioner do FIRST?
Recommend permissionless blockchain.
Perform a risk assessment.
Perform a business impact analysis (BIA).
Recommend permissioned blockchain.
Before selecting technologies or deployment models, a risk assessment should be conducted to evaluate potential threats, vulnerabilities, and controls. This ensures the technology aligns with the risk appetite and regulatory requirements of the organization.
After several security incidents resulting in significant financial losses, IT management has decided to outsource the security function to a third party that provides 24/7 security operation services. Which risk response option has management implemented?
Risk mitigation
Risk avoidance
Risk acceptance
Risk transfer
Risk transferinvolves shifting the responsibility for managing specific risks to a third party. By outsourcing the security function, the organization transfers the associated risk to a vendor specializing in security management.
Which of the following is the STRONGEST indication an organization has ethics management issues?
Employees do not report IT risk issues for fear of consequences.
Internal IT auditors report to the chief information security officer (CISO).
Employees face sanctions for not signing the organization ' s acceptable use policy.
The organization has only two lines of defense.
According to the CRISC Review Manual, ethics management is the process of ensuring that the enterprise’s values and principles are embedded in its culture and practices. Ethics management helps to promote trust, integrity, accountability, and transparency among the stakeholders. One of the key elements of ethics management is to encourage the reporting of IT risk issues and incidents, and to protect the whistleblowers from any retaliation or negative consequences. Therefore, if employees do not report IT risk issues for fear of consequences, it is the strongest indication that the organization has ethics management issues, as it implies that there is a lack of trust, openness, and support in the organization. The other options are not the strongest indications of ethics management issues, as they are related to other aspects of IT governance,such as audit independence, policy compliance, and risk management framework. References = CRISC Review Manual, 7th Edition, Chapter 1, Section 1.3.2, page 34.
When is the BEST to identify risk associated with major project to determine a mitigation plan?
Project execution phase
Project initiation phase
Project closing phase
Project planning phase
The best time to identify the risk associated with a major project to determine a mitigation plan is the project initiation phase. The project initiation phase is the first phase of the project management process, where the project is defined, authorized, and planned. The project initiation phase includes the activities of developing the project charter, identifying the stakeholders, and defining the scope and objectives of the project. The project initiation phase is the best time to identify the risk associated with the project, as it provides the opportunity to understand the project context, requirements, and expectations, and to establish the risk management framework, process, and plan. By identifying the risk early in the project, the mitigation plan can be integrated with the project plan, and the resources, budget, and schedule can be allocated accordingly. The other options are not as optimal as the project initiation phase, as they are related to the execution, closing, or planning of the project, not the definition or authorization of the project. References = Risk and Information Systems Control Study Manual, Chapter 1: IT Risk Identification, Section 1.1: IT Risk Management Process, page 15.
Which of the following is the PRIMARY responsibility of the first line of defense related to computer-enabled fraud?
Providing oversight of risk management processes
Implementing processes to detect and deter fraud
Ensuring that risk and control assessments consider fraud
Monitoring the results of actions taken to mitigate fraud
Computer-enabled fraud is the use of information technology (IT) to commit or conceal fraudulent activities, such as theft, manipulation, or unauthorized access of data, systems, or networks. Computer-enabled fraud can pose significant risks to an organization, such as financial loss, reputational damage, legal liability, or regulatory sanctions. Therefore, an organization should establish a comprehensive and effective framework to prevent, detect, and respond to computer-enabled fraud. The framework should involve three lines of defense, which are theroles and responsibilities of different functions within theorganization to manage and control risks. The first line of defense consists of the business owners, whose role is to identify, assess, and manage risks, including computer-enabled fraud risks. The primary responsibility of the first line of defense related to computer-enabled fraud is to implement processes to detect and deter fraud. This means designing and executing controls that can prevent or reduce the occurrence of computer-enabled fraud, such as authentication, authorization, encryption, logging, orsegregation of duties. This also means monitoring and reporting any suspicious or anomalous activities or transactions that may indicate computer-enabled fraud, such as unusual patterns, volumes, or frequencies of data or system access or usage. Implementing processes to detect and deter fraud can help the first line of defense to protect the organization’s assets, data, and reputation from computer-enabled fraud, and to comply with the organization’s policies and regulations. References = Three Lines of Defence, Roles of Three Lines of Defense for Information Security and Governance, THE THREE LINES OF DEFENSE IN EFFECTIVE RISK MANAGEMENT AND CONTROL, The Three Lines of Defense.
When a risk practitioner is building a key risk indicator (KRI) from aggregated data, it is CRITICAL that the data is derived from:
business process owners.
representative data sets.
industry benchmark data.
data automation systems.
Building Key Risk Indicators (KRIs):
KRIs are metrics used to provide an early signal of increasing risk exposure in various areas of an organization.
Importance of Representative Data Sets:
To ensure KRIs are accurate and meaningful, it is critical that the data used is representative of the entire population or relevant subset of activities being monitored.
Representative data ensures that the KRIs reflect the true state of risk and are not biased or incomplete.
Impact on KRIs:
Using representative data sets improves the reliability and validity of KRIs, enabling better risk detection and management.
It ensures that the KRIs provide a realistic view of potential risk trends and patterns.
Comparing Other Data Sources:
Business Process Owners:While they provide valuable insights, data from them alone may not be representative.
Industry Benchmark Data:Useful for comparisons but not specific to the organization’s unique context.
Data Automation Systems:Helpful for efficiency but must ensure the data is representative.
References:
The CRISC Review Manual emphasizes the importance of using representative data to build effective KRIs (CRISC Review Manual, Chapter 3: Risk Response and Mitigation, Section 3.11 Data Collection Aggregation Analysis and Validation) .
Whether the results of risk analyses should be presented in quantitative or qualitative terms should be based PRIMARILY on the:
requirements of management.
specific risk analysis framework being used.
organizational risk tolerance
results of the risk assessment.
The results of risk analyses should be presented in quantitative or qualitative terms based primarily on the requirements of management, because they are the intended audience and users of the risk information, and they have the authority and responsibility to make risk-based decisions. The requirements of management may vary depending on the purpose, scope, and context of the risk analysis, and the level of detail, accuracy, and reliability that they need. Quantitative risk analysis uses numerical data and mathematical models to estimate theprobability and impact of risks, and to express the risk exposure and value in monetary or other measurable units. Qualitative risk analysis uses descriptive data and subjective judgmentsto assess the likelihood and severity of risks, and to rank the risks according to their relative importance or priority. Both methods have their advantages and disadvantages, and they can be used separately or together, depending on the situation and the availability of data and resources. However, the primary factor that determines the choice of the method is the requirements of management, as they are the ones who will use the risk information to support their objectives, strategies, and actions. References = Risk IT Framework, ISACA, 2022, p. 141
Which of the following would be MOST helpful in assessing the risk associated with data loss due to human vulnerabilities?
Reviewing password change history
Performing periodic access recertification
Conducting social engineering exercises
Reviewing the results of security awareness surveys
Social engineering exercises are simulations of real-world attacks that exploit human vulnerabilities, such as phishing, baiting, pretexting, or quid pro quo. Conducting social engineering exercises can help assess the risk associated with data loss due to human vulnerabilities by measuring the employees’ susceptibility to such attacks, their awareness of security policies and procedures, and their response to incidents. Reviewing password change history, performing periodic access recertifications, and reviewing the results of security awareness surveys are also useful, but they do not directly test the employees’ behavior and resilience in the face of social engineering attacks.
When establishing an enterprise IT risk management program, it is MOST important to:
review alignment with the organizations strategy.
understand the organization ' s information security policy.
validate the organization ' s data classification scheme.
report identified IT risk scenarios to senior management.
The most important thing to do when establishing an enterprise IT risk management program is to review the alignment with the organization’s strategy. The organization’s strategy is the plan or direction that the organization follows to achieve its vision, mission, and goals. The IT risk management program should be aligned with the organization’s strategy, so that it supports and enables the organization’s strategic objectives, and addresses the IT risks that could affect the organization’s performance and value. Reviewing the alignment with the organization’s strategy helps to ensure that the IT risk management program is relevant, effective, and consistent with the organization’s expectations and needs. The other options are not as important as reviewing the alignment with the organization’s strategy, although they may be useful or necessary steps or components of the IT risk management program. Understanding the organization’s information security policy, validating the organization’s data classification scheme, and reporting identified IT risk scenarios to senior management are all activities that can help to implement and improvethe IT risk management program, but they are not the initial or primary thing todo. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.2.1, page 2-12.
Which of the following aspects of an IT risk and control self-assessment would be MOST important to include in a report to senior management?
Changes in control design
A decrease in the number of key controls
Changes in control ownership
An increase in residual risk
An IT risk and control self-assessment (RCSA) is a process that helps organizations identify and evaluate operational risks and assess the effectiveness of their control measures12. It is a structured approach that involves identifying, assessing, mitigating, and monitoring risks across all levels of an organization12.
A report to senior management is a document that summarizes and communicates the results and findings of the RCSA, and provides recommendations and action plans for improving the risk management and control processes34.
The most important aspect of an IT risk and control self-assessment to include in a report to senior management is an increase in residual risk, which is the risk remaining after risk treatment, and represents the exposure or potential impact of the risk on the organization’s objectives56.
An increase in residual risk is the most important aspect because it indicates the level of risk that the organization is willing to accept or tolerate, and the gap between the current and desired risk profile56.
An increase in residual risk is also the most important aspect because it requires the attention and decision of the senior management, who are responsible for defining the organization’s risk appetite, strategy, and criteria, and for ensuring that the residual risk is within the acceptable range56.
The other options are not the most important aspects, but rather possible components or outcomes of an IT risk and control self-assessment that may support or complement the report to senior management. For example:
Changes in control design are components of an IT risk and control self-assessment that involve modifying or updating the control measures to address the changes in the risk environment or the organization’s objectives56. However, changes in control design are not the most importantaspect because they do not measure or reflect the residual risk, which is the ultimate goal of the risk treatment56.
A decrease in the number of key controls is an outcome of an IT risk and control self-assessment that indicates the improvement or optimization of the control processes, and the reduction of the complexity or redundancy of the control measures56. However, a decrease in the number of key controls is not the most important aspect because it does not indicate or imply the residual risk, which may depend on other factors such as the effectiveness or efficiency of the controls56.
Changes in control ownership are components of an IT risk and control self-assessment that involve assigning or reassigning the responsibility and accountability for the control processes to the appropriate individuals or groups within the organization56. However,changes in control ownership are not the most important aspect because they do not affect or determine the residual risk, which is independent of the control owners56. References =
1: Risk and control self-assessment - KPMG Global1
2: Control Self Assessments - PwC2
3: How-To Guide: Implementing Risk Control Self-Assessment Steps4
4: RISK MANAGEMENT SELF-ASSESSMENT TEMPLATE - Smartsheet5
5: Risk IT Framework, ISACA, 2009
6: IT Risk Management Framework, University of Toronto, 2017
Which of the following is MOST important to consider before determining a response to a vulnerability?
The likelihood and impact of threat events
The cost to implement the risk response
Lack of data to measure threat events
Monetary value of the asset
A vulnerability is a weakness or flaw in the IT system or environment that could be exploited by a threat. A threat event is an occurrence or action that exploits a vulnerability and causes harm or damage to the IT system or environment. The lack of data to measure threat events is the most important factor, because it may affect the accuracy and reliability of the risk assessment and evaluation, and consequently, the risk response and strategy. The lack of data to measure threat events may also create challenges or risks for the organization, such as compliance, legal, reputational, or operational risks, or conflicts or inconsistencies with the organization’s risk appetite, risk objectives, or risk policies. The other options are not as important as the lack of data to measure threat events, although they may also influence the risk response and strategy. The likelihood and impact of threat events, the cost to implement the risk response, and the monetary value of the asset are all factors that could affect the feasibility and sustainability of the risk response and strategy, but they do not necessarily affect the validity and quality of the risk assessment and evaluation
Which of the following indicators measures the performance of IT configuration management?
Number of devices reviewed for compliance
Number of devices adhering to baseline settings
Number of devices exceeding minimum configuration
Number of devices not reporting configuration data
The correct answer isBbecause the most meaningful indicator ofIT configuration management performanceis thenumber of devices adhering to baseline settings. Configuration management performance is best measured by how many devices are actually in compliance with established baseline configurations.
The other options are less effective indicators:
A. Number of devices reviewed for compliancemeasures activity, not actual performance or outcome.
C. Number of devices exceeding minimum configurationdoes not necessarily reflect compliance with approved baselines.
D. Number of devices not reporting configuration datamay indicate a monitoring issue, but it does not directly measure configuration management performance.
Exact Extracts supporting the answer:
“The control practice related to information systems architecture that includes establishing and maintaining baselines for internally developed systems is Configuration management.”
“The MOST appropriate metric to measure how well the information security function is managing the administration of user access is percent of accounts with configurations in compliance.”
“Including thresholds that identify when controls no longer provide the intended value is essential when developing metrics to monitor the control life cycle.”
“The use of key performance indicators for management of technology controls is BEST related to the measurement of control effectiveness to determine that business requirements are being met.”
These extracts support that configuration management should be measured againstbaseline compliance, makingdevices adhering to baseline settingsthe best indicator.
===========
Which of the following is the BEST success criterion for control implementation?
Adequate resources are allocated to perform the control.
Responsibilities for control execution are properly defined.
Risk is at an acceptable level after the control is in place.
Key risk indicators (KRIs) for the control are properly defined.
An organization has engaged a third party to provide an Internet gateway encryption service that protects sensitive data uploaded to a cloud service. This is an example of risk:
mitigation.
avoidance.
transfer.
acceptance.
Risk transfer is a risk response strategy that involves shifting the responsibility or burden of a risk to another party, such as a third party, an insurance company, or a joint venture. Risk transfer does not eliminate the risk, but it reduces the exposure or impact of the risk to the enterprise. An example of risk transfer is engaging a third party to provide an Internet gateway encryption service that protects sensitive data uploaded to a cloud service. By doing so, the organization transfers the risk of data breach or loss to the third party, who is responsible for ensuring the security and availability of the data. The other options are not examples of risk transfer, as they involve different risk response strategies:
Risk mitigation is a risk response strategy that involves reducing the likelihood or impact of a risk to an acceptable level, such as by implementing controls, policies, or procedures.
Risk avoidance is a risk response strategy that involves eliminating the risk by not performing the activity that generates the risk, such as by discontinuing a product or service, or not entering a market.
Risk acceptance is a risk response strategy that involves acknowledging the risk and taking no action to address it, such as by tolerating the risk, exploiting the risk, or sharing the risk. References =Risk and Information Systems Control Study Manual, 7th Edition, Chapter 3, Section 3.3.1.1, pp. 107-108.
One of an organization ' s key IT systems cannot be patched because the patches interfere with critical business application functionalities. Which of the following would be the risk practitioner ' s BEST recommendation?
Additional mitigating controls should be identified.
The system should not be used until the application is changed
The organization ' s IT risk appetite should be adjusted.
The associated IT risk should be accepted by management.
The risk practitioner’s best recommendation when one of an organization’s key IT systems cannot be patched because the patches interfere with critical business application functionalities is to identify additional mitigating controls, as they may reduce the likelihood or impact of the vulnerabilities being exploited, and align the residual risk with the risk tolerance and appetite of the organization. The other options are not the best recommendations, as they may not address the risk adequately, or may introduce unacceptable consequences, such as disrupting the businessoperations, changing the risk strategy, or accepting excessive risk. References = CRISC Review Manual, 7th Edition, page 111.
Which of the following is the PRIMARY purpose for ensuring senior management understands the organization’s risk universe in relation to the IT risk management program?
To define effective enterprise IT risk appetite and tolerance levels
To execute the IT risk management strategy in support of business objectives
To establish business-aligned IT risk management organizational structures
To assess the capabilities and maturity of the organization’s IT risk management efforts
Ensuring senior management understands the organization’s risk universe in relation to the IT risk management program is primarily to define effective enterprise IT risk appetite andtolerance levels. This understanding is essential for setting the boundaries within which the organization is willing to operate regarding IT risks.
Defining Effective IT Risk Appetite and Tolerance Levels (Answer A):
Purpose: Senior management needs to understand the range and nature of IT risks to set appropriate risk appetite and tolerance levels.
Impact: This enables the organization to make informed decisions about which risks to accept, mitigate, transfer, or avoid.
Alignment: It ensures that the IT risk management strategy is aligned with the overall business objectives and risk posture of the organization.
Comparison with Other Options:
B. To execute the IT risk management strategy in support of business objectives:
Purpose: While important, it follows the definition of risk appetite and tolerance.
Limitation: Without understanding the risk universe, execution may be misaligned.
C. To establish business-aligned IT risk management organizational structures:
Purpose: Structural alignment is crucial but secondary to setting risk appetite and tolerance.
D. To assess the capabilities and maturity of the organization’s IT risk management efforts:
Purpose: This is part of the ongoing process but not the primary purpose of understanding the risk universe.
After the review of a risk record, internal audit questioned why the risk was lowered from medium to low. Which of the following is the BEST course of action in responding to this inquiry?
Obtain industry benchmarks related to the specific risk.
Provide justification for the lower risk rating.
Notify the business at the next risk briefing.
Reopen the risk issue and complete a full assessment.
The best course of action in responding to the internal audit inquiry is to provide justification for the lower risk rating. This would demonstrate that the risk record was updated based on a valid and documented rationale, such as changes in the risk environment, risk drivers, risk indicators, or risk responses. Providing justification would also help to maintain the transparency and accountability of the risk management process, and ensure that the internal audit is satisfied with the risk assessment outcome. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.2.3, page 184.
A risk practitioner is MOST likely to use a SWOT analysis to assist with which risk process?
Risk assessment
Risk reporting
Risk mitigation
Risk identification
SWOT analysis (Strengths, Weaknesses, Opportunities, Threats) is used in the riskidentification phase to comprehensively analyze the organization ' s internal and externalenvironments. By understanding strengths and weaknesses, internal risks can be identified, while opportunities and threats help to identify external risks. This method provides a foundation for proactive risk management.
An organization is planning to move its application infrastructure from on-premises to the cloud. Which of the following is the BEST course of the actin to address the risk associated with data transfer if the relationship is terminated with the vendor?
Meet with the business leaders to ensure the classification of their transferred data is in place
Ensure the language in the contract explicitly states who is accountable for each step of the data transfer process
Collect requirements for the environment to ensure the infrastructure as a service (IaaS) is configured appropriately.
Work closely with the information security officer to ensure the company has the proper security controls in place.
The best course of action to address the risk associated with data transfer if the relationship is terminated with the vendor is to ensure the language in the contract explicitly states who is accountable for each step of the data transfer process. This can help to avoid ambiguity, confusion, or disputes over the ownership, responsibility, and liability of the data and the data transfer process. Meeting with the business leaders, collecting requirements, and working with the information security officer are important activities, but they are not as effective as ensuring the contractual agreement is clear and enforceable. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 4; CRISC Review Manual, 6th Edition, page 153.
Which of the following provides the MOST important information to facilitate a risk response decision?
Audit findings
Risk appetite
Key risk indicators
Industry best practices
Risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Risk appetite provides the most important information to facilitate a risk response decision, because it reflects the organization’s risk tolerance, preferences, and expectations, which guide the selection and implementation of the risk response strategies. Risk appetite helps the organization to balance the potential benefits and costs of taking risks, and to align the risk management process with the organizational strategy and culture. The other options are not as important as risk appetite, because they do not indicate the organization’s desired level of risk exposure, but rather provide supplementary or partial information for the risk response decision, as explained below:
A. Audit findings are the results and recommendations of the internal or external audit activities that evaluate the effectiveness and efficiency of the organization’s governance, risk management, and control processes. Audit findings provide useful information to facilitate a risk response decision, because they can identify the gaps or weaknesses in the current risk response strategies, and suggest corrective actions or improvements. However, audit findings do not indicate the organization’s risk appetite, which is the basis for determining the optimal risk response strategies.
C. Key risk indicators (KRIs) are metrics that measure the impact and likelihood of the risks, and provide early warning signs of changes in the risk exposure. KRIs provide useful information to facilitate a risk response decision, because they can monitor and report the performance and effectiveness of the current risk response strategies, and trigger corrective actions or adjustments.However, KRIs do not indicate the organization’s risk appetite, which is the basis for determining the acceptable level of risk exposure and performance.
D. Industry best practices are the standards, norms, and expectations for risk management that are established and followed by the peers or competitors in the same industry or sector. Industry best practices provide useful information to facilitate a risk response decision, because they can benchmark and compare the organization’s risk response strategies with those of the leading or successful organizations, and identify areas for improvement or innovation. However, industry best practices do not indicate the organization’s risk appetite, which is the basis for determining the unique and customized risk response strategies that suit the organization’s needs and goals. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.2.2, page 40. Risk Appetite: What It Is and How to Use It, Risk Appetite: How Hungry Are You?, Risk Appetite: The Strategic Balancing Act
Which of the following trends would cause the GREATEST concern regarding the effectiveness of an organization ' s user access control processes? An increase in the:
ratio of disabled to active user accounts.
percentage of users with multiple user accounts.
average number of access entitlements per user account.
average time between user transfers and access updates.
The average time between user transfers and access updates is a trend that would cause the greatest concern regarding the effectiveness of an organization’s user access control processes, as it indicates thedelay or inefficiency in updating the user access rights and privileges according to the user’s current role and responsibilities. This can result in unauthorized or excessive access to the organization’s information assets, and increase the risk of data leakage, fraud, or misuse. The user access control processes should ensure that the user access rights and privileges are reviewed and modified regularly, and especially when the user’s role or status changes, such as transfer, promotion, demotion, or termination. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question241. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 241. CRISC Sample Questions 2024, Question 241.
Which of the following provides the BEST evidence that risk mitigation plans have been implemented effectively?
Self-assessments by process owners
Mitigation plan progress reports
Risk owner attestation
Change in the level of residual risk
Residual risk is the risk that remains after the risk mitigation plans have been implemented. Residual risk reflects the effectiveness of the risk response in reducing the likelihood or impact of the risk. The best evidence that risk mitigation plans have been implemented effectively is the change in the level of residual risk. A change in the level of residual risk can be measured by comparing the risk level before and after the risk mitigation plans have been executed. A change in the level of residual risk can also be evaluated by comparing the actual residual risk with the target or acceptable residual risk. A change in the level of residual risk can demonstrate how well the risk mitigation plans have achieved the risk objectives and met the risk criteria. A change in the level of residual risk can also provide feedback and lessons learned for future risk management activities. References = Residual Risk: Definition, Formula & Management, Residual Risk: What It Is and How to Manage It, Residual Risk: How to Calculate and Manage It.
Which of the following is the BEST way to mitigate the risk to IT infrastructure availability?
Establishing a disaster recovery plan (DRP)
Establishing recovery time objectives (RTOs)
Maintaining a current list of staff contact delays
Maintaining a risk register
The best way to mitigate the risk to IT infrastructure availability is to establish a disaster recovery plan (DRP), because a DRP is a document that defines the procedures and resources needed to restore the IT infrastructure and resume the critical business functions in the event of a disaster or disruption. A DRP helps to minimize the downtime, data loss, and financial impact of a disaster, and ensures the continuity of operations and services. The other options are not the best ways to mitigate the risk to IT infrastructure availability, although they may also be helpful in supporting the DRP. Establishing recovery time objectives (RTOs), maintaining a current list of staff contact details, and maintaining a risk register are examples of planning or monitoring activities that aim to define the requirements, roles, and responsibilities for the disaster recovery process, but they do not address the actual implementation or execution of the DRP. References = CRISC: Certified in Risk & Information Systems Control Sample Questions
When presenting risk, the BEST method to ensure that the risk is measurable against the organization ' s risk appetite is through the use of a:
risk map
cause-and-effect diagram
maturity model
technology strategy plan.
A risk map is the best method to ensure that the risk is measurable against the organization’s risk appetite, as it is a graphical tool that displays the level and priority of risks based on their likelihood and impact, as well as other factors such as velocity, persistence, and urgency. A risk map can help to compare and communicate the risk levels across different business units, processes, and projects, and to align them with the organization’s risk appetite and tolerance. A risk map can also help to identify the gaps and overlaps in risk management, and to support the decision making and resource allocation for risk response. A cause-and-effect diagram is a tool that helps to identify and analyze the root causes and consequences of a risk or a problem, but it does not measure the risk against the organization’s risk appetite. A maturity model is a tool that helps to assess and improve the capability and performance of a process or a function, but it does not measure the risk against the organization’s risk appetite. A technology strategy plan is a document that outlines the vision, goals, and objectives of the organization’s use of information and technology, but it does not measure the risk against the organization’s risk appetite. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Assessment, page 97.
Which of the following BEST indicates how well a web infrastructure protects critical information from an attacker?
Failed login attempts
Simulating a denial of service attack
Absence of IT audit findings
Penetration test
A penetration test is a simulated cyberattack on a web infrastructure to evaluate its security posture and identify any vulnerabilities or weaknesses that could be exploited by an attacker. A penetration test is the best indicator of how well a web infrastructure protects critical information from an attacker, as it mimics the real-world scenarios and techniques that an attacker would use, and measures the effectiveness of the existing security controls and countermeasures. A penetration test can also provide recommendations for improving the security of the web infrastructure and reducing the risk exposure. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question 236. CRISC by Isaca Actual Free Exam Q & As, Question 9. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 236. Most Asked CRISC Exam Questions and Answers, Question 10.
Which of the following is the MOST important outcome of a business impact analysis (BIA)?
Understanding and prioritization of critical processes
Completion of the business continuity plan (BCP)
Identification of regulatory consequences
Reduction of security and business continuity threats
The most important outcome of a business impact analysis (BIA) is understanding and prioritization of critical processes. A BIA is a process that identifies and evaluates the potential effects of disruptions or disasters on the organization’s business functions and processes. A BIA helps to understand the dependencies, interrelationships, and impacts of the business processes, and to prioritize them based on their importance and urgency. A BIA also helps to determine the recovery objectives, strategies, and resources for the business processes, such as the recovery time objective (RTO), the recovery point objective (RPO), and the minimum operating requirements (MOR). The other options are not as important as understanding and prioritization of critical processes, although they may be part of or derived from the BIA. Completion of thebusiness continuity plan (BCP), identification of regulatory consequences, and reduction of security and business continuity threats are all activities or outcomes that can be supported or facilitated by the BIA, but they are not the primary purpose or result of the BIA. References = CISA Review Manual, 27th Edition, Chapter 5, Section 5.2.1, page 5-9.
Which of the following is MOST important to ensure when reviewing an organization ' s risk register?
Risk ownership is recorded.
Vulnerabilities have separate entries.
Control ownership is recorded.
Residual risk is less than inherent risk.
The most important factor to ensure when reviewing an organization’s risk register is that the risk ownership is recorded, as it indicates the authority and responsibility for managing the risk and its associated controls, and facilitates the communication and accountability of the risk management process and activities. The other options are not the most important factors, as they are more related to theidentification, classification, or measurement of the risk, respectively, rather than the management of the risk. References = CRISC Review Manual, 7th Edition, page 101.
Which of the following is the BEST way to mitigate the risk associated with fraudulent use of an enterprise ' s brand on Internet sites?
Utilizing data loss prevention (DLP) technology
Monitoring the enterprise ' s use of the Internet
Scanning the Internet to search for unauthorized usage
Developing training and awareness campaigns
Scanning the Internet for unauthorized usage of the enterprise ' s brand proactively identifies fraudulent activities and enables timely response. This aligns withBrand Protection and Risk Mitigationstrategies.
While reviewing the risk register, a risk practitioner notices that different business units have significant variances in inherent risk for the same risk scenario. Which of the following is the BEST course of action?
Update the risk register with the average of residual risk for both business units.
Review the assumptions of both risk scenarios to determine whether the variance is reasonable.
Update the risk register to ensure both risk scenarios have the highest residual risk.
Request that both business units conduct another review of the risk.
The risk register is a document that records the identified risks, their analysis, and their responses. It is a useful tool for monitoring and controlling the risks throughout the project lifecycle. However, the risk register is not a static document and it should be updated regularly to reflect the changes in the risk environment and the project status. Therefore, when reviewing therisk register, a risk practitioner should not only look at the risk ratings, but also the assumptions and the rationale behind them. Different business units may have different perspectives, contexts, and data sources for the same risk scenario, which can result in significant variances in inherent risk. Inherent risk is the risk level before considering the existing controls or responses. Therefore, the best course of action is to review the assumptions of both risk scenarios to determine whether the variance is reasonable or not. This can help to identify any errors, inconsistencies, or biases in the risk assessment process, and to ensure that the risk register reflects the current and accurate state of the risks. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.1, p. 106-107
Which of the following is the FIRST step in managing the security risk associated with wearable technology in the workplace?
Identify the potential risk.
Monitor employee usage.
Assess the potential risk.
Develop risk awareness training.
The security risk associated with wearable technology in the workplace is the possibility and impact of unauthorized access, disclosure, or use of the data or information that are collected, stored, or transmitted by the wearable devices, such as smartwatches, fitness trackers, or glasses, that are worn or used by the employees12.
The first step in managing the security risk associated with wearable technology in the workplace is to identify the potential risk, which is the process of recognizing and describing the sources,causes, and consequences of the risk, and the potential impacts on the organization’s objectives, performance, and value creation34.
Identifying the potential risk is the first step because it provides the basis and input for the subsequent steps of the risk management process, such as assessing, treating, monitoring, and communicating the risk34.
Identifying the potential risk is also the first step because it enables the organization to understand and prioritize the risk, and to allocate the appropriate resources and controls for the risk management process34.
The other options are not the first step, but rather possible subsequent steps that may depend on or follow the identification of the potential risk. For example:
Monitoring employee usage is a step that involves collecting and analyzing data and information on the frequency, duration, and purpose of the wearable devices that are used by the employees, and detecting and reporting any deviations, anomalies, or issues that may indicate a security risk5 . However, this step is not the first step because it requires theidentification of the potential risk to provide the guidance and standards for the monitoring process5 .
Assessing the potential risk is a step that involves estimating and evaluating the likelihood and impact of the risk, and the level of risk exposure or tolerance for the organization34. However, this step is not the first step because it requires the identification of the potential risk to provide the information and data for the assessment process34.
Developing risk awareness training is a step that involves educating and training the employees and other stakeholders on the security risks and best practices associated with the wearable technology, and informing them of their roles, obligations, and responsibilities for the risk management process . However, this step is not the first step because it requires the identification of the potential risk to provide the content and objectives for the training process . References =
1: Wearable Devices in the Workplace: Security Threats and Protection1
2: 10 security risks of wearables | CSO Online2
3: Risk IT Framework, ISACA, 2009
4: IT Risk Management Framework, University of Toronto, 2017
5: Continuous Monitoring - ISACA3
Continuous Monitoring: A New Approach to Risk Management - ISACA Journal4
What Is Security Awareness Training and Why Is It Important? - Kaspersky5
Security Awareness Training - Cybersecurity Education Online | Proofpoint US
Who should be responsible for implementing and maintaining data security controls?
Data architect.
Data scientist.
Data analyst.
Data custodian.
The correct answer is D . The data owner is accountable for classification and access decisions, but the data custodian implements and maintains the security controls that protect the data. The uploaded CRISC notes state that the data owner is responsible for information classification and for approving access. This supports the CRISC role distinction: owners decide and approve; custodians operate, implement, and maintain controls.
A data architect designs data structures, a data scientist analyzes data, and a data analyst uses data. None of these roles is primarily responsible for maintaining security controls.
===========
Senior management has requested a risk practitioner ' s guidance on whether
a new technical control requested by a business unit is worth the investment.
Which of the following should be the MOST important consideration before
providing input?
The cost of the control relative to the value of risk mitigation
The effectiveness of the control at reducing residual risk levels
The likelihood of a successful attack based on current risk
assessments
The availabilitv of budgeted funds for risk mitigationMitination
Which of the following is MOST important to ensure before using risk reports in decision making?
Root cause analysis is included.
Risk analysis results are validated.
Real-time risk information is provided.
Quantitative risk data is provided.
Validation of risk analysis results ensures the data is accurate, reliable, and can be trusted for making informed decisions. It minimizes the risk of acting on flawed insights.
Which of the following is MOST important to identify when developing top-down risk scenarios?
Key procedure control gaps
Business objectives
Senior management ' s risk appetite
Hypothetical scenarios
The most important factor to identify when developing top-down risk scenarios is B. Business objectives12
Top-down risk scenarios are based on the organization’s strategic goals, objectives, and key performance indicators (KPIs), and they aim to identify the potential events or situations that could prevent or hinder the achievement of those goals and objectives12
By identifying the business objectives, the risk practitioner can align the risk scenarios with the organization’s mission, vision, and values, and ensure that the risk scenarios are relevant, realistic, and meaningful for the senior management and other stakeholders12
The other factors are not as important as the business objectives when developing top-down risk scenarios, because they are either more relevant for bottom-up risk scenarios (A and D), or they are derived from the business objectives and the risk scenarios ©12
The PRIMARY reason a risk practitioner would be interested in an internal audit report is to:
plan awareness programs for business managers.
evaluate maturity of the risk management process.
assist in the development of a risk profile.
maintain a risk register based on noncompliance.
According to the CRISC Review Manual (Digital Version), the primary reason a risk practitioner would be interested in an internal audit report is to evaluate the maturity of the risk management process, as it provides an independent and objective assessment of the effectiveness and efficiency of the risk management activities and controls. An internal audit report helps to:
Identify and evaluate the strengths and weaknesses of the risk management process and its alignment with the organization’s objectives and strategy
Detect and report any gaps, errors, or deficiencies in the risk identification, assessment, response, and monitoring processes and controls
Recommend and implement corrective actions or improvement measures to address the issues or findings in the risk management process
Communicate and coordinate the audit results and recommendations with the relevant stakeholders, such as the risk owners, the senior management, and the board
Enhance the accountability and transparency of the risk management process and its outcomes
References = CRISC Review Manual (Digital Version), Chapter 4: IT Risk Monitoring and Reporting, Section 4.2: IT Risk Reporting, pp. 223-2241
Which of the following shortcomings of perimeter security does Zero Trust aim to resolve?
Lack of access verification for systems on the internal network
Identification and authentication failures for users
Poorly configured firewall rules introducing security breaches
Ineffective load balancing on network devices
Zero Trustassumes that no system or user is inherently trustworthy—even within the internal network. It addresses theinadequacy of perimeter securityby enforcing continuous verification for every access request.
An organization wants to develop a strategy to mitigate the risk associated with unethical actions by stakeholders. Which of the following should be done FIRST?
Provide incentives for whistleblowers to report unethical actions
Communicate sanctions and penalties for unethical actions
Develop company-wide training on business ethics
Create a policy regarding ethical behavior
The first step in establishing an ethical governance culture is tocreate a clear and formal policyoutlining acceptable behavior and consequences for violations.
ISACA guidance:
“Developing and approving an enterprise code of ethics or ethical policy establishes the foundation for enforcing ethical conduct and guiding all subsequent training and enforcement activities.”
Training and enforcement follow policy creation.
Therefore,D. Create a policy regarding ethical behavioris correct.
CRISC Reference:Domain 1 – IT Risk Governance, Topic: Ethics and Governance Policies.
Which of the following conditions presents the GREATEST risk to an application?
Application controls are manual.
Application development is outsourced.
Source code is escrowed.
Developers have access to production environment.
The production environment is the environment where the application is deployed and used by the end users. The production environment should be protected from unauthorized or unintended changes that could compromise the availability, integrity, or confidentiality of the application and its data. Developers have access to the production environment presents the greatest risk to an application, as it could allow them tobypass the change management process, introduce errors or vulnerabilities, or manipulate the application or its data for malicious purposes. The other options are not as risky as developers having access to the production environment, as they involve different aspects of the application lifecycle:
Application controls are manual means that the application relies on human intervention to perform some functions or validations, such as data entry, reconciliation, or authorization. This could increase the risk of human error, fraud, or inefficiency, but it does not directly affect the production environment.
Application development is outsourced means that the application is developed by a third party, such as a vendor or a contractor. This could increase the risk of quality issues, contractual disputes, or intellectual property rights, but it does not directly affect the production environment.
Source code is escrowed means that the source code of the application is deposited with a trusted third party, such as a lawyer or a bank. This could provide assurance and continuity in case the original developer is unable or unwilling to maintain or support the application, but it does not directly affect the production environment. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.1.1.1, pp. 144-145.
Which of the following BEST enables an organization to determine whether risk management is aligned with its goals and objectives?
The organization has approved policies that provide operational boundaries.
Organizational controls are in place to effectively manage risk appetite.
Environmental changes that impact risk are continually evaluated.
The organization has an approved enterprise architecture (EA) program.
According to the CRISC Review Manual, enterprise architecture (EA) is a comprehensive framework that defines the structure and operation of an organization, including its business processes, information systems, technology infrastructure, organizational structure, and strategic objectives2. An EA program is a set of principles, policies, standards, and guidelines that govern the development and implementation of the EA3. By having an approved EA program, an organization can ensure that its risk management is aligned with its goals and objectives, as the EA provides a clear and consistent vision of the desired state and direction of the organization, as well as the means to achieve and measure it4. The EA also helps to identify and prioritize the risks and opportunities that may affect the organization’s performance and resilience. The other options are not as effective or relevant as option D, as they do not directly relate to the alignment of risk management with organizational goals and objectives. Option A, having approved policies that provide operational boundaries, is more related to the governance and compliance of risk management, not its alignment. Option B, having organizational controls to manage risk appetite, is more related to the implementation and monitoring of risk management, not its alignment. Option C, continually evaluating environmental changes that impact risk, is more related to the identification and assessment of risk management, not its alignment.
Which of the following is an IT business owner ' s BEST course of action following an unexpected increase in emergency changes?
Evaluating the impact to control objectives
Conducting a root cause analysis
Validating the adequacy of current processes
Reconfiguring the IT infrastructure
Conducting a root cause analysis is the best course of action for an IT business owner following an unexpected increase in emergency changes, as it helps to identify and address the underlying cause(s) of the problem and prevent it from recurring in the future. A root cause analysis is a systematic process of finding and resolving the fundamental factors that contribute to a specific issue or event. A root cause analysis can help to improve the quality and reliability of the IT services and processes, reduce the costs and risks associated with emergency changes, and enhance the customer satisfaction and trust.
The other options are not the best courses of action for an IT business owner following an unexpected increase in emergency changes. Evaluating the impact to control objectives is an important step to assess the potential consequences of the emergency changes on the IT governance and risk management, but it does not provide a solution or mitigation strategy for the problem. Validating the adequacy of current processes is a good practice to ensure that the IT processes are aligned with the business needs and objectives, but it does not address the specific cause(s) of the emergency changes. Reconfiguring the IT infrastructure is a possible action to implement the emergency changes, but it does not prevent the occurrence or recurrence of the problem. References = IT Business Owner’s Best Course of Action Following Unexpected Increase …, ITIL Change Types: Standard vs Normal vs Emergency - Freshworks, Emergency Change Management: Please Stop The Drama
Which of the following should be of GREATEST concern to a risk practitioner when determining the effectiveness of IT controls?
Configuration updates do not follow formal change control.
Operational staff perform control self-assessments.
Controls are selected without a formal cost-benefit
analysis-Management reviews security policies once every two years.
Configuration updates are changes made to the settings, parameters, or components of an IT system or network. Configuration updates can affect the functionality, performance, security, and reliability of the system or network. Therefore, configuration updates should follow formal change control, which is a process that ensures that changes are authorized, documented, tested, and implemented in a controlled manner. Formal change control can help prevent errors, conflicts, disruptions, and vulnerabilities that may arise from configuration updates. Configuration updates that do not follow formal change control should be of greatest concern to a risk practitioner when determining the effectiveness of IT controls, as they can introduce newrisks or compromise existing controls. References = Risk and Information Systems Control Study Manual, Chapter 3: Risk Response and Mitigation, Section 3.5: Control Monitoring and Reporting, p. 161-162.
Reviewing which of the following would provide the MOST useful information when preparing to evaluate the effectiveness of existing controls?
Previous audit reports
Control objectives
Risk responses in the risk register
Changes in risk profiles
Understanding the Question:
The question seeks to identify which source provides the most useful information for evaluating the effectiveness of existing controls.
Analyzing the Options:
A. Previous audit reports:Provide historical data but might not reflect current risks.
B. Control objectives:These are standards to be achieved, not current evaluations.
C. Risk responses in the risk register:Useful but focused on specific responses rather than overall effectiveness.
D. Changes in risk profiles:Reflect current and emerging risks, providing a dynamic view of control effectiveness.
Risk Profiles:Evaluating changes in risk profiles helps understand how effective existing controls are against current threats. If risk levels are increasing, it may indicate that controls are insufficient or need updating.
Proactive Adjustment:By monitoring changes in risk profiles, organizations can proactively adjust their controls to address new or evolving risks.
Who is PRIMARILY accountable for risk treatment decisions?
Risk owner
Business manager
Data owner
Risk manager
The risk owner is primarily accountable for risk treatment decisions, as they are the person or entity with the authority and responsibility to manage a particular risk. The risk owner shouldevaluate the available risk response options, select the most appropriate one, implement the chosen response, and monitor its effectiveness. The risk owner should also communicate and report on the risk status and any issues or changes. The business manager, data owner, and risk manager are not primarily accountable for risk treatment decisions, although they may be involved in the risk management process. The business manager is responsible for the overall performance and objectives of a business unit or function. The data owner is responsible for the security and quality of a specific data asset. The risk manager is responsible for facilitating and coordinating the risk management activities across the organization. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Identification, page 47.
When reviewing a report on the performance of control processes, it is MOST important to verify whether the:
business process objectives have been met.
control adheres to regulatory standards.
residual risk objectives have been achieved.
control process is designed effectively.
When reviewing a report on the performance of control processes, it is most important to verify whether the residual risk objectives have been achieved, as this indicates the extent to which the control processes have reduced the risk to an acceptable level. Residual risk is the risk that remains after the implementation of controls, and it should be aligned with the risk appetite and tolerance of the enterprise. Business process objectives, regulatory standards, and control process design are not the most important factors to verify,as they do not directly measure the effectiveness and efficiency of the control processes in managing the risk. References = CRISCPractice Quiz and Exam Prep; CRISC: Certified in Risk & Information Systems Control Sample Questions, question 209.
What is the PRIMARY benefit of risk monitoring?
It reduces the number of audit findings.
It provides statistical evidence of control efficiency.
It facilitates risk-aware decision making.
It facilitates communication of threat levels.
Risk monitoring is the process of tracking and evaluating the performance and effectiveness of the risk management process and controls, and identifying any changes or emerging risks that may affect theenterprise’s objectives and strategy. The primary benefit of risk monitoring is that it facilitates risk-aware decision making, as it provides timely and relevant information and feedback to the decision-makers and stakeholders, and enables them to adjust the risk strategy and response actions accordingly. Risk monitoring also helps to ensure that the risk management process is aligned with the enterprise’s risk appetite and tolerance, and supports the achievement of the enterprise’s goals and value creation. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question 239. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 239. CRISC Sample Questions 2024, Question 239.
Which of the following is the PRIMARY concern for a risk practitioner regarding an organization ' s adoption of innovative big data analytics capabilities?
It may be expensive to maintain a data lake.
It may be difficult to find experts who can develop analytical queries.
There may be a lack of documented processes for big data analysis.
Analytics methods may identify someone who was previously de-identified.
The primary concern for a risk practitioner in adopting innovative big data analytics is the potential re-identification of individuals from previously anonymized data. Advanced analytics techniques can inadvertently combine datasets in ways that reveal personal identities, leading to privacy breaches and regulatory non-compliance. This risk is heightened when data from multiple sources are aggregated, increasing the chance of re-identification.
Which of the following BEST facilitates the mitigation of identified gaps between current and desired risk environment states?
Develop a risk treatment plan.
Validate organizational risk appetite.
Review results of prior risk assessments.
Include the current and desired states in the risk register.
Developing a risk treatment plan is the best way to facilitate the mitigation of identified gaps between current and desired risk environment states. A risk treatment plan is a document that outlines the actions and resources needed to implement the chosen risk response strategy for each risk scenario. A risk treatment plan should include the following elements:
Risk scenario description and risk ID
Risk owner and other stakeholders
Risk response strategy and objectives
Risk response actions and tasks
Resources, costs, and benefits
Roles and responsibilities
Timeline and milestones
Performance indicators and monitoring mechanisms
Contingency plans and triggers
A risk treatment plan helps to close the gaps between the current and desired risk environment states by providing a clear and comprehensive roadmap for risk mitigation. It also helps to ensure that the risk response actions are aligned with the organizational risk appetite, objectives, and priorities. A risk treatment plan also facilitates the communication, coordination, and collaboration among the risk owners and other stakeholders involved in the risk mitigation process.
The other options are not the best ways to facilitate the mitigation of identified gaps between current and desired risk environment states. Validating organizational risk appetite is an important step in establishing the risk criteria and thresholds for the risk assessment process, but it does not directly address the gaps between the current and desired risk environment states. Reviewing results of prior risk assessments can provide useful insights and lessons learned for the current risk assessment process, but it does not necessarily lead to the development and implementation of effective risk response actions. Including the current and desired states in the risk register can help to document and monitor the risk scenarios and their status, but it does not provide the details and guidance for risk mitigation. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4: Risk Response, Section 4.2: Risk Treatment, p. 189-191.
Which of the following would be the GREATEST concern related to data privacy when implementing an Internet of Things (loT) solution that collects personally identifiable information (Pll)?
A privacy impact assessment has not been completed.
Data encryption methods apply to a subset of Pll obtained.
The data privacy officer was not consulted.
Insufficient access controls are used on the loT devices.
According to the CRISC Review Manual1, access controls are the policies, procedures, practices, and technologies that are designed and implemented to prevent unauthorized or inappropriate access to IT resources and data. Access controls are essential for ensuring the confidentiality, integrity, and availability of data, especially personally identifiable information (Pll), which is any information that can be used to identify, locate, or contact an individual. Insufficient access controls are the greatest concern related to data privacy when implementing an Internet of Things (loT) solution that collects Pll, as they can expose the data to various risks and threats, such asdata leakage, theft, loss, corruption, manipulation, or misuse. Insufficient access controls can also cause legal, regulatory, ethical, or reputational issues for the organization, if the data privacy rights and expectations of the individuals are violated or compromised. References = CRISC Review Manual1, page 240, 253.
Which of the following is a PRIMARY benefit of creating an organizational code of conduct?
Clear expectations for employee behavior
Identification of ethical risk facing the organization
Improvement in workforce productivity
Enhanced integrity of management
The correct answer isAbecause the primary benefit of an organizationalcode of conductis to establishclear expectations for employee behavior. A code of conduct communicates the standards of ethical and professional behavior expected within the organization and provides a common basis for decision-making, accountability, and awareness.
The other options are less appropriate:
B. Identification of ethical risk facing the organizationmay result indirectly, but this is not the primary purpose of a code of conduct.
C. Improvement in workforce productivitycould occur as a secondary effect, but it is not the main benefit.
D. Enhanced integrity of managementmay be supported, but the code of conduct applies across the organization and primarily clarifies expected behavior.
Exact Extracts supporting the answer:
“The most effective way to support adherence to an enterprise ' s code of ethics is by ensuring periodic training evaluation and attestation of employees.”
“The most significant benefit when stakeholders promote and follow professional ethics is that it increases risk management effectiveness within an enterprise.”
“The best proactive approach for practicing professional ethics within an enterprise is to provide ethics awareness training.”
“Developing and practicing ethical behavior within an enterprise contributes the most to building the risk culture.”
These extracts support that ethics-related governance mechanisms such as a code of conduct are intended to guide and reinforce expected behavior throughout the enterprise. Therefore, the primary benefit isclear expectations for employee behavior.
===========
Which element of an organization ' s risk register is MOST important to update following the commissioning of a new financial reporting system?
Key risk indicators (KRIs)
The owner of the financial reporting process
The risk rating of affected financial processes
The list of relevant financial controls
The most important element of an organization’s risk register to update following the commissioning of a new financial reporting system is the risk rating of affected financial processes. A risk rating is a measure of the level and nature of the risk exposure, based on the impact and likelihood of the risk events. A risk rating can help to prioritize and respond to the risks, and to monitor and report the risk status. A new financial reporting system may introduce new or different risks, or change the existing risks, that could affect the financial processes of the organization, such as data quality, accuracy, timeliness, compliance, or security. Therefore, the risk rating of affected financial processes should be updated to reflect the current risk situation and to ensure that the risk register is accurate and complete. Key risk indicators (KRIs), the owner of the financial reporting process, and the list of relevant financial controls are not asimportant as the risk rating of affected financial processes, as they are not directly affected by the commissioning of a new financial reporting system, and they do not measure the risk exposure and impact of the financial processes. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 48.
Which of the following is the GREATEST concern associated with the transmission of healthcare data across the internet?
Unencrypted data
Lack of redundant circuits
Low bandwidth connections
Data integrity
The greatest concern associated with the transmission of healthcare data across the internet is unencrypted data, as this exposes the data to unauthorized access, interception, modification, or disclosure, which may compromise the confidentiality, integrity, and availability of the data. Healthcare data is sensitive and personal information that may include medical records, diagnoses, treatments, prescriptions, insurance claims, and biometric data. Healthcare data is subject to various legal and regulatory requirements, such as the Health Insurance Portability and Accountability Act (HIPAA) in the United States, that mandate the protection and privacy of the data. Encryption is a method of transforming the data into an unreadable format that can only be accessed or restored by authorized parties who have the decryption key. Encryption helps to prevent or reduce the risk of data breaches, identity theft, fraud, or other malicious attacks. The other options are not the greatest concerns associated with the transmission of healthcare dataacross the internet, although they may pose some challenges or issues. Lack of redundant circuits is a concern for the reliability and continuity of the data transmission, but it does notaffect the security or privacy of the data. Low bandwidth connections is a concern for the speed andefficiency of the data transmission, but it does not affect the security or privacy of the data. Data integrity is a concern for the accuracy and completeness of the data, but it does not necessarily depend on the encryption of the data. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk Response, page 156.
Which of the following is the BEST way to estimate the impact of an inherent risk over the next year?
Obtain input from organizational risk stakeholders.
Leverage industry threat intelligence reports.
Model and simulate historical impact.
Review industry and emerging risk trends.
The BEST answer is A because impact is business-context dependent. Inherent risk impact should be estimated based on how the risk could affect the organization’s objectives, operations, processes, assets, and stakeholders before considering controls. ISACA’s CRISC exam outline places inherent and residual risk under Risk Analysis and states that CRISC candidates must understand likelihood and impact of threats, vulnerabilities, and risk scenarios. ISACA’s risk analysis discussion explains that risk analysis evaluates both the possibility of occurrence and “the determination of the impact on business objectives”; for impact assessment, business impact information is often prepared by business function managers/risk owners. The uploaded CRISC notes also state that risk scenarios estimate frequency and impact, assessors determine magnitude of impact after likelihood, and top-down/business-objective context is important.
B and D are useful for understanding the threat landscape and future trends, but they do not by themselves estimate the organization-specific impact. C can help when reliable historical data exists, but historical modeling alone may not reflect current business context, changed operations, or stakeholder impact. For CRISC-style “BEST” questions, organizational stakeholders/risk owners provide the most relevant impact input.
===========
Which of the following BEST indicates that an organization ' s risk management processes are mature?
Risk policy is approved and communicated by the risk manager
Annual risk awareness training is conducted by risk owners
Risk principles are embedded within business operations and decisions
The board regularly follows up on risk status and action plans
CRISC maturity models describe high-maturity organizations as those whererisk management is integrated into everyday operations and decision-making.
Supporting extract:
“An organization achieves mature risk management when risk principles are embedded within business operations, culture, and decision-making processes.”
AandBdescribe compliance-level practices.
Dshows oversight but not integration.
Creflects operational embedding, which defines maturity.
CRISC Reference:Domain 1 – IT Risk Governance, Topic: Risk Management Maturity Model.
Which of the following is the BEST indication of an improved risk-aware culture following the implementation of a security awareness training program for all employees?
A reduction in the number of help desk calls
An increase in the number of identified system flaws
A reduction in the number of user access resets
An increase in the number of incidents reported
A security awareness training program is an educational program that aims to equip the organization’s employees with the knowledge and skills they need to protect the organization’s data and sensitive information from cyber threats, such as hacking, phishing, or other breaches12.
A risk-aware culture is a culture that values and promotes the understanding and management of risks, and encourages the behaviors and actions that support the organization’s risk objectives and strategy34.
The best indication of an improved risk-aware culture following the implementation of a security awareness training program for all employees is an increase in the number of incidents reported, which is the frequency or rate of security incidents that are detected and communicated by the employees to the appropriate authorities or channels56.
An increase in the number of incidents reported is the best indication because it shows that the employees have gained the awareness and confidence to recognize and report the security incidents that may affect the organization, and that they have the responsibility and accountability to contribute to the organization’s risk management and security posture56.
An increase in the number of incidents reported is also the best indication because it enables the organization to respond and recover from the security incidents more quickly and effectively, and to prevent or reduce the recurrence or escalation of similar incidents in the future56.
The other options are not the best indication, but rather possible outcomes or consequences of an improved risk-aware culture or a security awareness training program. For example:
A reduction in the number of help desk calls is an outcome of an improved risk-aware culture or a security awareness training program that indicates the employees have become more self-reliant and proficient in solving or preventing the common or minor IT issues or problems . However, this outcome does not measure the employees’ awareness or reporting of security incidents, which may be more serious or complex .
An increase in the number of identified system flaws is a consequence of an improved risk-aware culture or a security awareness training program that indicates the employees have become more vigilant and proactive in finding and reporting the vulnerabilities or weaknesses in the IT systems or processes . However, this consequence does not measure the employees’ awareness or reporting of security incidents, which may exploit or leverage the system flaws .
A reduction in the number of user access resets is an outcome of an improved risk-aware culture or a security awareness training program that indicates the employees have become more careful and responsible in managing and protecting their user credentials or accounts . However, this outcome does not measure the employees’ awareness or reporting of security incidents, which may compromise or misuse the user access . References =
1: Security Awareness Training - Cybersecurity Education Online | Proofpoint US5
2: What Is Security Awareness Training and Why Is It Important? - Kaspersky6
3: Risk IT Framework, ISACA, 2009
4: IT Risk Management Framework, University of Toronto, 2017
5: Security Incident Reporting and Response, University of Toronto, 2017
6: Security Incident Reporting and Response, ISACA, 2019
IT Help Desk Best Practices, ISACA Journal, Volume 2, 2018
IT Help Desk Best Practices, ISACA Now Blog, February 12, 2018
System Flaw Reporting and Remediation, University of Toronto, 2017
System Flaw Reporting and Remediation, ISACA, 2019
User Access Management and Control, University of Toronto, 2017
User Access Management and Control, ISACA, 2019
Which of the following would MOST effectively enable a business operations manager to identify events exceeding risk thresholds?
Continuous monitoring
A control self-assessment
Transaction logging
Benchmarking against peers
Events exceeding risk thresholds are situations or occurrences that result in the actual level of risk exceeding the acceptable or tolerable level of risk, as defined by the organization’s risk appetite, criteria, and objectives12.
The most effective way to enable a business operations manager to identify events exceeding risk thresholds is to implement continuous monitoring, which is a process that involves collecting and analyzing data and information on the performance and status of the business processes, systems, and controls, and detecting and reporting any deviations, anomalies, or issues that may indicate a risk event34.
Continuous monitoring is the most effective way because it provides timely and accurate visibility and insight into the risk landscape, and enables the business operations manager to identify and respond to the events exceeding risk thresholds before they escalate or cause significant harm or damage to the organization34.
Continuous monitoring is also the most effective way because it supports the risk management process and objectives, which are to identify and address the risks that may affect the achievement of the organization’s goals and the delivery of value to the stakeholders34.
The other options are not the most effective ways, but rather possible tools or techniques that may complement or enhance the continuous monitoring. For example:
A control self-assessment is a technique that involves engaging and empowering the business process owners and operators to evaluate and report on the effectiveness and efficiency of the controls that are designed and implemented to mitigate the risks56. However, this technique is not the most effective way because it is periodic rather than continuous, and it may not capture or communicate the events exceeding risk thresholds in a timely or consistent manner56.
Transaction logging is a tool that involves recording and storing the details and history of the transactions or activities that are performed by the business processes or systems, and providing an audit trail for verification or investigation purposes78. However, this tool is not the most effective way because it is passive rather than active, and it may not detect or report the events exceeding risk thresholds unless they are analyzed or queried78.
Benchmarking against peers is a technique that involves comparing and contrasting the performance and practices of the business processes or systems with those of the similar or leading organizations in the same or related industry, and identifying the gaps or opportunities for improvement . However, this technique is not the most effective way because it is external rather than internal, and it may not reflect or align with the organization’s specific risk appetite, criteria, and objectives . References =
1: Risk IT Framework, ISACA, 2009
2: IT Risk Management Framework, University of Toronto, 2017
3: Continuous Monitoring - ISACA1
4: Continuous Monitoring: A New Approach to Risk Management - ISACA Journal2
5: Risk and control self-assessment - KPMG Global3
6: Control Self Assessments - PwC4
7: Transaction Log - Wikipedia5
8: Transaction Logging - IBM6
Benchmarking - Wikipedia7
Benchmarking: Definition, Types, Process, Advantages & Examples
Which of the following is the BEST key performance indicator (KPI) to measure the effectiveness of an anti-virus program?
Frequency of anti-virus software updates
Number of alerts generated by the anti-virus software
Number of false positives detected over a period of time
Percentage of IT assets with current malware definitions
An anti-virus program is a software that detects and removes malicious software, such as viruses, worms, or ransomware, from the IT assets, such as computers, servers, or networks. The effectiveness of an anti-virus program can be measured by the key performance indicators (KPIs) that reflect the achievement of the program objectives and the alignment with the enterprise’s risk appetite and tolerance. The best KPI to measure the effectiveness of an anti-virus program is the percentage of IT assets with current malware definitions. Malware definitions are the files or databases that contain the signatures or patterns of the known malicious software, and they are used by the anti-virus program to scan and identify the malware. The percentage of IT assets with current malware definitions indicates how well the anti-virus program is able to protect the IT assets from the latest or emerging threats, and reduce the exposure and impact of the risks associated with the malware. The other options are not as good as the percentage of IT assets with current malware definitions, as they may not reflect the quality or timeliness of the protection, or the alignment with the enterprise’s risk appetite and tolerance. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.3.2.1, pp. 171-172.
Which of the following resources is MOST helpful to a risk practitioner when updating the likelihood rating in the risk register?
Risk control assessment
Audit reports with risk ratings
Penetration test results
Business impact analysis (BIA)
Penetration test results are the most helpful resource to a risk practitioner when updating the likelihood rating in the risk register. Penetration testing is a method of simulating real-world attacks on an IT system or network to identify and exploit vulnerabilities and measure the potential impact. Penetration test results provide empirical evidence of the existence and severity of vulnerabilities, as well as the ease and probability of exploitation. These results can help the risk practitioner to update the likelihood rating of the risks associated with the vulnerabilities, and to prioritize the risk response actions. Risk control assessment, audit reports with risk ratings, and business impact analysis (BIA) are also useful resources for risk management, but they are not as directly related to the likelihood rating as penetration test results. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.3.3, page 2-28.
Which of the following will BEST help to improve an organization ' s risk culture?
Maintaining a documented risk register
Establishing a risk awareness program
Rewarding employees for reporting security incidents
Allocating resources for risk remediation
A risk awareness program is a set of activities that aim to educate and inform employees about the organization’s risk culture, policies, and procedures. A risk awareness program can help improve an organization’s risk culture by enhancing the employees’ understanding of risk, their roles and responsibilities in risk management, and the benefits of risk mitigation. A risk awareness program can also foster a culture of openness, trust, and collaboration among employees, managers, and stakeholders, which can improve the organization’s risk performance and resilience.
Maintaining a documented risk register, rewarding employees for reporting security incidents, and allocating resources for risk remediation are also important aspects of risk management, but they do not directly address the organization’s risk culture, which is the shared values, beliefs, and attitudes that influence how risk is perceived and handled within the organization.
Which of the following could BEST detect an in-house developer inserting malicious functions into a web-based application?
Segregation of duties
Code review
Change management
Audit modules
Code review could BEST detect an in-house developer inserting malicious functions into a web-based application, because it is a process that involves examining and verifying the source code of the application for any errors, vulnerabilities, or malicious functions. Code review can help toidentify and remove any unauthorized or harmful code that the developer may have inserted, either intentionally or unintentionally, and to ensure that the application meets the quality andsecurity standards and requirements. The other options are not as effective as code review, because:
Option A: Segregation of duties is a control that involves separating the roles and responsibilities of the developer from those of the tester, the approver, and the deployer, to prevent any conflict of interest or misuse of authority. Segregation of duties can help to reduce the risk of the developer inserting malicious functions into the web-based application, but it does not detect them.
Option C: Change management is a process that involves controlling and documenting any changes to the web-based application, such as new features, enhancements, or bug fixes, to ensure that they are authorized, tested, and approved. Change management can help to track and monitor the changes that the developer may have made to the web-based application, but it does not detect the malicious functions.
Option D: Audit modules are components that are embedded in the web-based application to record and report the activities and transactions that occur within the application, such as user login, data input, or data output. Audit modules can help to audit and review the performance and functionality of the web-based application, but they do not detect the malicious functions. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 214.
A risk practitioner has just learned about new done FIRST?
Notify executive management.
Analyze the impact to the organization.
Update the IT risk register.
Design IT risk mitigation plans.
According to the CRISC Review Manual1, impact analysis is the process of estimating and evaluating the potential effects of a risk event on the organization’s objectives, processes, resources, and risks. Impact analysis helps to quantify and qualify the severity and likelihood of the risk, and to identify the possible consequences and implications for the organization. Impact analysis is the first step that should be done when a risk practitioner learns about a new threat, as it helps to assess the current level of risk exposure and the urgency of the risk response. Impact analysis also helps to communicate and report the risk to the relevant stakeholders, and to facilitate risk-based decision making and action planning. References = CRISC Review Manual1, page 208.
Which of the following will BEST help to ensure that information system controls are effective?
Responding promptly to control exceptions
Implementing compensating controls
Testing controls periodically
Automating manual controls
The best way to ensure that information system controls are effective is to test them periodically. Testing controls periodically helps to verify that the controls are operating as intended, and that they are aligned with the enterprise’s objectives, policies, and standards. Testing controls periodically also helps to identify any gaps, weaknesses, or deficiencies in the controls, and to implement corrective actions or improvements. Responding promptly to control exceptions, implementing compensating controls, and automating manual controls are good practices, but they are not the best way to ensure control effectiveness. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 3, Section 3.1.1.2, page 1071
1: ISACA Certified in Risk and Information Systems Control (CRISC®) Exam Guide, Answer to Question 641.
A chief risk officer (CRO) has asked to have the IT risk register integrated into the enterprise risk management (ERM) process. Which of the following will BEST facilitate the reporting of IT risk at the enterprise level?
Aggregating the IT risk scenarios into a maturity benchmark value
Using an IT risk heat map to depict likelihood and impact
Using the same risk taxonomy across the organization
Providing a summary of open IT risk-related audit findings
Using aconsistent risk taxonomyensures that IT risks can be aggregated and compared with enterprise-level risks in a meaningful way. ISACA emphasizes that standardized risk language and categories are critical to integrating IT risk with ERM processes.
===========
Which of the following is MOST important for a risk practitioner to confirm when reviewing an organization’s information security policies?
Aligned with information security procedures.
Written at a high level to communicate the organization’s intentions.
Frequently updated to address minor technology changes.
Drafted at a technical level to focus on common security industry practices.
The correct answer is B . Policies should communicate management’s direction, intent, and governing principles at a high level. Procedures provide detailed implementation steps; standards provide mandatory specific requirements. The uploaded study material states that policies state management direction and governing principles, while standards define required criteria and procedures describe steps. It also defines policies as high-level statements outlining the organization’s stance on information security.
A is useful, but procedures should align to policy rather than define the policy’s primary quality. C is incorrect because minor technology changes usually belong in standards/procedures. D is incorrect because technical detail belongs in standards or procedures, not high-level policy.
===========
Which of the following would BEST help to address the risk associated with malicious outsiders modifying application data?
Multi-factor authentication
Role-based access controls
Activation of control audits
Acceptable use policies
Role-based access controls (RBAC) are a type of preventive control that limit the access and actions of users based on their roles and responsibilities within the organization. RBAC can help to address the risk of malicious outsiders modifying application data by restricting their access to the data and the functions they can perform on it. RBAC can also enforce the principle of least privilege, which means that users only have the minimum level of access required to perform their tasks. RBAC can be implemented through policies, procedures, and technical mechanisms such as access control lists, encryption, and authentication. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1.1, p. 178-179
When outsourcing a business process to a cloud service provider, it is MOST important to understand that:
insurance could be acquired for the risk associated with the outsourced process.
service accountability remains with the cloud service provider.
a risk owner must be designated within the cloud service provider.
accountability for the risk will remain with the organization.
According to the FIC Article by FSCA, accountable institutions remain fully accountable, responsible and liable for any compliance failures that may result from or be associated with an outsourcing arrangement and as such, liability and/or culpability for non-compliance with the FIC Act obligations cannot be transferred to a third-party service provider2. Therefore, even if a business process is outsourced to a cloud service provider, the organization still has the ultimate responsibility and accountability for the risk associated with the outsourced process. The other options are not correct, as they imply that the cloud service provider can take over the accountability or responsibility for the risk, or that the organization can mitigate the risk by acquiring insurance, which is not the case.
Which of the following is the BEST key performance indicator (KPI) for determining how well an IT policy is aligned to business requirements?
Total cost to support the policy
Number of exceptions to the policy
Total cost of policy breaches
Number of inquiries regarding the policy
An IT policy is a document that defines the rules, standards, and procedures for the use, management, and security of IT resources within an organization. An IT policy should be aligned to the business requirements, which are the needs, expectations, and objectives of the business stakeholders, such as customers, employees, managers, partners, regulators, etc. An IT policy that is aligned to the business requirements can help support the business strategy, improve the business performance, and enhance the business value. A key performance indicator (KPI) is a metric that measures the achievement of a specific goal or objective. A KPI should be relevant, measurable, achievable, realistic, and time-bound. The best KPI for determining how well an IT policy is aligned to the business requirements is the number of exceptions to the policy. An exception to the policy is a deviation or violation of the policy rules, standards, or procedures, which may be intentional or unintentional, authorized or unauthorized, justified or unjustified. The number of exceptions to the policy can indicate how well the policy is understood, communicated, implemented, and enforced within the organization. The number of exceptions to the policy can also indicate how well the policy reflects the current and future business needs and expectations, and how flexible and adaptable the policy is to the changing business environment. A low number of exceptions to the policy can suggest that the policy is well aligned to the business requirements, while a high number of exceptions to the policy can suggest that the policy is misaligned or outdated, and may need to be reviewed or revised. References = Key Performance Indicator (KPI): Definition, Types, andExamples, Business KPIs: 5 important characteristics to be effective, What is a KPI? How To Choose the Best KPIs for Your Business - HubSpot Blog.
Which of the following is the GREATEST concern associated with business end users developing their own applications on end user spreadsheets and database programs?
An IT project manager is not assigned to oversee development.
Controls are not applied to the applications.
There is a lack of technology recovery options.
The applications are not captured in the risk profile.
The GREATEST concern associated with business end users developing their own applications on end user spreadsheets and database programs is:
B. Controls are not applied to the applications.
When end users create their own applications, there is often a lack of formal controls that would typically be applied in a structured development environment. This can lead to issues with data integrity, security vulnerabilities, and non-compliance with organizational policies and standards.
Which of the following is MOST important for an organization that wants to reduce IT operational risk?
Increasing senior management ' s understanding of IT operations
Increasing the frequency of data backups
Minimizing complexity of IT infrastructure
Decentralizing IT infrastructure
According to the Operational Risk: Overview, Importance, and Examples article, operational risk is the risk of loss resulting from inadequate or failed internal processes, people, and systems. One of the factors that can increase operational risk is the complexity of IT infrastructure, which refers to the number, variety, and interdependence of IT components, such as hardware, software, networks, and data. A complex IT infrastructure can pose challenges for IT management, such as increased costs, reduced performance, lower reliability, highervulnerability, and more difficulty in troubleshooting and maintenance. Therefore, minimizing the complexity of IT infrastructure can help reduce IT operational risk, as it can simplify IT operations, improve IT efficiency and effectiveness, enhance IT security and resilience, and facilitate IT innovation and adaptation. References = Operational Risk: Overview, Importance, and Examples
An organization ' s risk register contains a large volume of risk scenarios that senior management considers overwhelming. Which of the following would BEST help to improve the risk register?
Analyzing the residual risk components
Performing risk prioritization
Validating the risk appetite level
Conducting a risk assessment
Performing risk prioritization would best help to improve the risk register, which is a document that records and summarizes the key information and data about the identified risks and the risk responses1. Risk prioritization is the process of ranking the risks according to their significance and urgency, based on their probability and impact2. By performing risk prioritization, the organization can:
Reduce the complexity and volume of the risk register, and focus on the most important and relevant risks that require immediate attention and action3.
Enhance the communication and understanding of the risks among the senior management and other stakeholders, and facilitate the decision-making and resource allocation for the risk responses4.
Improve the efficiency and effectiveness of the risk management process, and ensure that the risk register is aligned with the organization’s risk strategy, objectives, and appetite5.
The other options are not the best ways to improve the risk register, because:
Analyzing the residual risk components is not the best way, as it may not address the issue of the large volume of risk scenarios. Residual risk is the level of risk that remains after the implementation of risk responses6. Analyzing the residual risk components can help to measure the exposure or uncertainty of the assets, and to determine the need and extent of the risk responses. However, it may not reduce the complexity or volume of the risk register, as it may add more information or data to the risk register.
Validating the risk appetite level is not the best way, as it may not address the issue of the overwhelming risk scenarios. Risk appetite is the amount and type of risk that the organization is willing to accept or pursue in order to achieve its objectives7. Validating the risk appetite levelcan help to ensure that the risk register is consistent and proportional to the risk level, and that the risk responses are suitable and feasible. However, it may not reduce the complexity or volume of the risk register, as it may require more information or data to validate the risk appetite level.
Conducting a risk assessment is not the best way, as it may not address the issue of the existing risk scenarios. Risk assessment is the process of estimating the probability and impact of the risks, and prioritizing the risks based on their significance and urgency. Conducting a risk assessment can help to identify and analyze new or emerging risks, and to update or revise the risk register accordingly. However, it may not reduce the complexity or volume of the risk register, as it may introduce more information or data to the risk register.
References =
Risk Register - CIO Wiki
Risk Prioritization - CIO Wiki
Risk Prioritization: A Guide for Project Managers - ProjectManager.com
Risk Prioritization: How to Prioritize Risks in Project Management - Clarizen
Risk Prioritization: A Key Step in Risk Management - ISACA
Residual Risk - CIO Wiki
Risk Appetite - CIO Wiki
[Risk Assessment - CIO Wiki]
A company has located its computer center on a moderate earthquake fault. Which of the following is the MOST important consideration when establishing a contingency plan and an alternate processing site?
The contingency plan provides for backup media to be taken to the alternative site.
The contingency plan for high priority applications does not involve a shared cold site.
The alternative site is a hot site with equipment ready to resume processing immediately.
The alternative site does not reside on the same fault no matter how far the distance apart.
The most important consideration when establishing a contingency plan and an alternate processing site for a company that has located its computer center on a moderate earthquake fault is that the alternative site does not reside on the same fault no matter how far the distance apart, as it ensures that the alternative site is not affected by the same earthquake event that may disrupt the primary site, and that the business continuity and recovery objectives can be met. The other options are not the most important considerations, as they are more related to the backup, priority, or readiness of the alternative site, respectively, rather than the location of the alternative site. References = CRISC Review Manual, 7th Edition, page 111.
An organization mandates the escalation of a service ticket when a key application is offline for 5 minutes or more due to potential risk exposure. The risk practitioner has been asked by management to prepare a report of application offline times using both 3- and 5-minute thresholds. What does the 3-minute threshold represent?
Recovery Time Objective (RTO)
Key Risk Indicator (KRI)
Recovery Point Objective (RPO)
Key Performance Indicator (KPI)
The 3-minute threshold is a KRI designed to act as an early warning before a more critical limit (5 minutes) is breached, helping prevent risk realization.
Which of the following should be the HIGHEST priority when developing a risk response?
The risk response addresses the risk with a holistic view.
The risk response is based on a cost-benefit analysis.
The risk response is accounted for in the budget.
The risk response aligns with the organization ' s risk appetite.
A risk response is the action or plan that is taken to address a specific risk that has been identified, analyzed, and evaluated. It can be one of the following types: mitigate, transfer, avoid, or accept.
The highest priority when developing a risk response is to ensure that it aligns with the organization’s risk appetite, which is the amount and type of risk that the organization is willing to accept in pursuit of its goals. The risk appetite is usually expressed as a range or a threshold, and it is aligned with the organization’s strategy and culture.
Aligning the risk response with the organization’s risk appetite ensures that the risk response is consistent, appropriate, and proportional to the level and nature of the risk, and that it supports the organization’s objectives and values. It also helps to optimize the balance between risk and return, and to create and protect value for the organization and its stakeholders.
The other options are not the highest priority when developing a risk response, because they do not address the fundamental question of whether the risk response is suitable and acceptable for the organization.
The risk response addresses the risk with a holistic view means that the risk response considers the interrelationships and dependencies among the risk sources, events, impacts, and responses, and the potential secondary and residual effects of the risk response. This is important to ensure that the risk response is comprehensive and effective, and that it does not create new or unintended risks, but it is not the highest priority when developing a risk response, because it does not indicate whether the risk response is aligned with the organization’s risk appetite.
The risk response is based on a cost-benefit analysis means that the risk response compares the expected costs and benefits of implementing the risk response, and selects the risk response that provides the most favorable net outcome. This is important to ensure that the risk response is efficient and economical, and that it maximizes the return on investment, but it is not the highest priority when developing a risk response, because it does not indicate whether the risk response is aligned with the organization’s risk appetite.
The risk response is accounted for in the budget means that the risk response is included in the financial plan and allocation of resources for the organization or the project. This is important toensure that the risk response is feasible and realistic, and that it has the necessary funding and support, but it is not the highest priority when developing a risk response, because it does not indicate whether the risk response is aligned with the organization’s risk appetite. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 29-30, 34-35, 38-39, 44-45, 50-51, 54-55
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 147
Numerous media reports indicate a recently discovered technical vulnerability is being actively exploited. Which of the following would be the BEST response to this scenario?
Assess the vulnerability management process.
Conduct a control serf-assessment.
Conduct a vulnerability assessment.
Reassess the inherent risk of the target.
A technical vulnerability is a weakness or flaw in the design or implementation of an information system or resource that can be exploited or compromised by a threat or source of harm that may affect the organization’s objectives or operations. A technical vulnerability may be caused byvarious factors, such as human error, system failure, process inefficiency, resource limitation, etc.
A vulnerability assessment is a process of identifying and evaluating the technical vulnerabilities that exist or may arise in the organization’s information systems or resources, and determining their severity and impact. A vulnerability assessment can help the organization to assess and prioritize the risks, and to design and implement appropriate controls or countermeasures to mitigate or prevent the risks.
The best response to the scenario of a recently discovered technical vulnerability being actively exploited is to conduct a vulnerability assessment, because it can help the organization to address the following questions:
What is the nature and extent of the technical vulnerability, and how does it affect the functionality or security of the information system or resource?
How is the technical vulnerability being exploited or compromised, and by whom or what?
What are the potential consequences or impacts of the exploitation or compromise of the technical vulnerability for the organization and its stakeholders?
How can the technical vulnerability be detected and reported, and what are the available or feasible options or solutions to address or correct it?
Conducting a vulnerability assessment can help the organization to improve and optimize the information system or resource quality and performance, and to reduce or eliminate the technicalvulnerability. It can also help the organization to align the information system or resource with the organization’s objectives and requirements, and to comply with the organization’s policies and standards.
The other options are not the best responses to the scenario of a recently discovered technical vulnerability being actively exploited, because they do not address the main purpose and benefit of conducting a vulnerability assessment, which is to identify and evaluate the technical vulnerability, and to determine its severity and impact.
Assessing the vulnerability management process is a process of evaluating and verifying the adequacy and effectiveness of the process that is used to identify, analyze, evaluate, and communicate the technical vulnerabilities, and to align them with the organization’s objectives and requirements. Assessing the vulnerability management process can help the organization to improve and optimize the process, and to reduce or eliminate the gaps or weaknesses in the process, but it is not the best response to the scenario, because it does not indicate the nature and extent of the technical vulnerability, and how it affects the organization and its stakeholders.
Conducting a control self-assessment is a process of evaluating and verifying the adequacy and effectiveness of the controls that are intended to ensure the confidentiality, integrity, availability, and reliability of the information systems and resources, using the input and feedback from the individuals or groups that are involved or responsible for the information systems activities or functions. Conducting a control self-assessment can help the organization to identify and document the control deficiencies, and to align them with the organization’s objectives and requirements, but it is not the best response to the scenario, because it does not indicate thenature and extent of the technical vulnerability, and how it affects the organization and its stakeholders.
Reassessing the inherent risk of the target is a process of reevaluating and recalculating the amount and type of risk that exists in the absence of any controls, and that is inherent to the nature or characteristics of the target, which is the information system or resource that is affected by the technical vulnerability. Reassessing the inherent risk of the target can help the organization to understand and document the risk exposure or level, and to align it with the organization’s risk appetite and tolerance, but it is not the best response to the scenario, because it does not indicate the nature and extent of the technical vulnerability, and how it affects the organization and its stakeholders. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 195
CRISC Practice Quiz and Exam Prep
Which of the following aspects of risk can be transferred to a third party?
Reputation impact
Ownership
Financial impact
Accountability
While responsibility and accountability generally remain with the enterprise, financial impact (e.g., via insurance or outsourcing) can be transferred to a third party.
Which of the following is MOST useful when communicating risk to management?
Risk policy
Audit report
Risk map
Maturity model
A risk map is a visual tool that helps to communicate risk to management by showing the likelihood and impact of different risks on a matrix1. A risk map can help to:
Identify the most critical risks that need immediate attention or action
Compare and prioritize risks based on their severity and probability
Align risk management strategies with the organization’s risk appetite and tolerance
Communicate risk information in a clear and concise way that is easy to understand and interpret2
References = Risk and Information Systems Control Study Manual, Chapter 5: Risk Assessment Process3
Which of the following is the BEST way to support communication of emerging risk?
Update residual risk levels to reflect the expected risk impact.
Adjust inherent risk levels upward.
Include it on the next enterprise risk committee agenda.
Include it in the risk register for ongoing monitoring.
Emerging risk is a risk that is new or evolving, and has the potential to significantly affect the enterprise’s objectives, performance, or reputation. Emerging risk can arise from changes in the internal or external environment, such as technological innovations, regulatory developments, or social trends. The best way to support communication of emerging risk is to include it on the next enterprise risk committee agenda. The enterprise risk committee is a group of senior executives who oversee the enterprise-wide risk management program, and provide guidance and direction to the risk owners and practitioners. By including the emerging risk on the agenda, the risk practitioner can ensure that the enterprise risk committee is aware of the risk, its causes, impacts, and likelihood, and can decide on the appropriate risk response strategy and actions. The other options are not the best way to support communication of emerging risk, as they involve different aspects of the risk management process:
Update residual risk levels to reflect the expected risk impact means that the risk practitioner adjusts the risk levels after considering the existing or planned risk responses. This may not befeasible or accurate for emerging risk, as the risk responses may not be defined or implemented yet, or may not be effective for the new or evolving risk.
Adjust inherent risk levels upward means that the risk practitioner increases the risk levels before considering any risk responses. This may not reflect the true nature or magnitude of the emerging risk, as the inherent risk levels are based on the assumptions and estimates of the risk practitioner, and may not account for the uncertainties or complexities of the emerging risk.
Include it in the risk register for ongoing monitoring means that the risk practitioner records and tracks the emerging risk, its causes, impacts, likelihood, responses, and owners. This is an important step in the risk management process, but it does not necessarily support communication ofthe emerging risk, as the risk register may not be accessible or visible to all the relevant stakeholders, or may not be updated or reviewed frequently enough to capture the changes in the emerging risk. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.2.2.2, pp. 21-22.
Which of the following MUST be assessed before considering risk treatment options for a scenario with significant impact?
Risk magnitude
Incident probability
Risk appetite
Cost-benefit analysis
According to the Risk Assessment and Management: A Complete Guide, risk magnitude is the product of the likelihood and impact of a risk scenario. Risk magnitude is an important factor to consider before choosing risk treatment options, as it indicates the level of exposure andpotential harm that the organization faces from the risk scenario. Risk treatment options should be selected based on the risk magnitude, as well as the risk appetite and tolerance of the organization. For a scenario with significant impact, the risk magnitude is likely to be high, and therefore the risk treatment options should aim to reduce the likelihood and/or impact of the risk scenario as much as possible, or to transfer or avoid the risk altogether. References = Risk Assessment and Management: A Complete Guide, ISO 27001 Risk Assessment & Risk Treatment: The Complete Guide
Which of the following is the MOST appropriate risk owner for a payroll application that has recently been outsourced to a cloud software provider?
IT executive.
HR executive.
Vendor management executive.
Cloud service provider’s information security executive.
The correct answer is B . Payroll is a business process owned by HR, so the HR executive is the most appropriate risk owner. Outsourcing the application to a cloud software provider does not transfer business accountability for payroll risk. The uploaded CRISC notes state that ownership is best established by mapping identified risk to a specific business process. They also emphasize assignment of risk owners and accountability as critical to risk management.
The IT executive may manage technology controls, vendor management may oversee the contract, and the cloud provider may operate provider-side controls, but the business risk owner remains the HR executive.
===========
An organization recently received an independent security audit report of its cloud service provider that indicates significant control weaknesses. What should be done NEXT in response to this report?
Migrate all data to another compliant service provider.
Analyze the impact of the provider ' s control weaknesses to the business.
Conduct a follow-up audit to verify the provider ' s control weaknesses.
Review the contract to determine if penalties should be levied against the provider.
An independent security audit report is a document that provides an objective and comprehensive assessment of the security posture and practices of a cloud service provider (CSP), based on a set of standards, criteria, or frameworks1. An independent security audit report can help an organization to evaluate the risks and benefits of using a CSP, and to ensure that the CSP meets the organization’s security and compliance requirements2.
If an organization receives an independent security audit report of its CSP that indicates significant control weaknesses, the next step that should be done in response to this report is to analyze the impact of the provider’s control weaknesses to the business. This means that the organization should:
Identify and prioritize the business processes, functions, or objectives that depend on or are affected by the CSP’s services
Assess the potential consequences and likelihood of the control weaknesses leading to security incidents, breaches, or losses
Estimate the financial, operational, reputational, or legal impacts of the security incidents, breaches, or losses
Compare the impacts with the organization’s risk appetite and tolerance, and determine the level of risk exposure and acceptance
Communicate the results of the analysis to the relevant stakeholders and decision-makers3
References = What is a Security Audit?, Cloud Security Audit: A 10-Step Checklist, Independent security audits are essential for cloud service providers. Here’s why
A risk practitioner has just learned about new malware that has severely impacted industry peers worldwide data loss?
Customer database manager
Customer data custodian
Data privacy officer
Audit committee
The data privacy officer is the best person to notify in case of a new malware that has severely impacted industry peers with data loss. The data privacy officer is responsible for ensuring that the enterprise complies with the applicable privacy laws and regulations, and that the personal data of the customers, employees, and other stakeholders are protected from unauthorized access, use, disclosure, or destruction. The data privacy officer can assess the potential impact of the malware on the enterprise’s data privacy obligations and risks, and coordinate the appropriate response and remediation actions. The customer database manager, the customer data custodian, and the audit committee are not the best persons to notify, as they do not have the same level of authority, responsibility, and expertise as the data privacy officer in dealing with data privacy issues. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 191.
Which of the following is the PRIMARY reason for monitoring activities performed in a production database environment?
Ensuring that database changes are correctly applied
Enforcing that changes are authorized
Deterring illicit actions of database administrators
Preventing system developers from accessing production data
Ensuring that database changes are correctly applied is the primary reason for monitoring activities performed in a production database environment, as it helps to maintain the integrity, availability, and performance of the database and the applications that depend on it. Database changes are any modifications made to the database structure, configuration, data, or code, such as adding or deleting tables, columns, indexes, or triggers, updating or inserting data, or altering stored procedures or functions. Database changes can have significant impacts on the database functionality and behavior, and may introduce errors, inconsistencies, or vulnerabilities if not applied correctly. Therefore, monitoring database changes is essential to verify that the changes are implemented as intended, comply with the design specifications and standards, and do not cause any adverse effects or conflicts with the existing database or application components.
The other options are not the primary reasons for monitoring activities performed in a production database environment. Enforcing that changes are authorized is an important aspect of database change management, but it is not the main purpose of database monitoring. Database change management is the process of planning, reviewing, approving, and implementing database changes in a controlled and consistent manner. Database change management helps to ensure that the changes are authorized by the appropriate stakeholders, aligned with the business requirements and objectives, and documented and communicated to the relevant parties. Database monitoring can support database change management by providing information and feedback on the change implementation and performance, but it does not enforce the change authorization. Deterring illicit actions of database administrators is a possible benefit of database monitoring, but it is not the primary reason for it. Database administrators are the users who have the highest level of access and privilege to the database, and they are responsible for managingand maintaining the database operations and security. Database monitoring can help to deter illicit actions of database administrators by tracking and auditing their activities and actions on the database, and alerting or escalating any suspicious or malicious behavior. However, database monitoring is not the only or the most effective way to prevent or detect illicit actions of database administrators. Other measures, such as implementing the principle of least privilege, segregating duties, enforcing password policies, and encrypting data, are also necessary to protect the database from unauthorized or improper access or manipulation by database administrators or other users. Preventing system developers from accessing production data is apossible benefit of database monitoring, but it is not the primary reason for it. System developers are the users who design, develop, and test the applications that interact with the database. System developers should not have access to the production data, as it may contain sensitive or confidential information that could be compromised or misused by the developers. System developers should only use test or dummy data for their development and testing purposes. Database monitoring can help to prevent system developers from accessing production data by controlling and restricting their access and privilege to the database, and logging and reporting any unauthorized or inappropriate access attempts. However, database monitoring is not the only or the most effective way to prevent system developers from accessing production data. Other measures, such as implementing access control policies, masking or anonymizing data, and isolating development and production environments, are also necessary to safeguard the production data from system developers or other users. References = Database Monitoring: Basics & Introduction | Splunk, IT Risk Resources | ISACA, Best Practices for Database Performance Monitoring
Which of the following methods would BEST contribute to identifying obscure risk scenarios?
Brainstorming sessions
Control self-assessments
Vulnerability analysis
Monte Carlo analysis
Brainstorming sessions would best contribute to identifying obscure risk scenarios, as they allow participants to generate and share ideas without being constrained by conventional thinking or assumptions. Brainstorming sessions can help to identify risks that are not obvious, not well understood, or not covered by existing controls. Control self-assessments, vulnerability analysis, and Monte Carlo analysis are useful methods for evaluating and quantifying risks, but they are not designed to identify obscure risk scenarios. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Identification, page 59.
When developing risk scenario using a list of generic scenarios based on industry best practices, it is MOST imported to:
Assess generic risk scenarios with business users.
Validate the generic risk scenarios for relevance.
Select the maximum possible risk scenarios from the list.
Identify common threats causing generic risk scenarios
The most important step when developing risk scenarios using a list of generic scenarios based on industry best practices is to validate the generic risk scenarios for relevance. The generic risk scenarios may not be applicable or suitable for the specific context, objectives, and environment of the organization. Therefore, the risk practitioner should validate the relevance of the generic risk scenarios by comparing them with the organization’s risk profile, risk appetite, and risk criteria. Assessing generic risk scenarios with business users, selecting the maximum possible risk scenarios from the list, and identifying common threats causing generic risk scenarios are other steps that may be useful, but they are not as important as validating the relevance of the generic risk scenarios. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 12; CRISC Review Manual, 6th Edition, page 215.
A data privacy regulation has been revised to incorporate more stringent requirements for personal data protection. Which of the following provides the MOST important input to help ensure compliance with the revised regulation?
Gap analysis
Current control attestation
Risk profile update
Business impact analysis (BIA)
Gap analysisidentifies differences between existing controls and the new regulatory requirements.
CRISC guidance explains:
“When a regulatory or compliance requirement changes, the first step is to conduct a gap analysis comparing current controls to the new requirements.”
This allows the practitioner to identify areas requiring remediation or policy enhancement.
Hence,A. Gap analysisis correct.
CRISC Reference:Domain 3 – Risk Response and Mitigation, Topic: Compliance and Regulatory Alignment.
Which of the following is the GREATEST concern when using a generic set of IT risk scenarios for risk analysis?
Quantitative analysis might not be possible.
Risk factors might not be relevant to the organization
Implementation costs might increase.
Inherent risk might not be considered.
According to the CRISC 351-400 topic3 Flashcards, the greatest concern when using a generic set of IT risk scenarios for risk analysis is that the risk factors might not be relevant to the organization. This is because generic risk scenarios are not tailored to the specific context, objectives, and environment of the organization, and they may not capture the unique threats, vulnerabilities, and impacts that the organization faces. Therefore, using generic risk scenarios may result in inaccurate or incomplete risk assessment and analysis, and may lead to ineffective or inappropriate risk responses. To avoid this, the organization should customize the risk scenarios to reflect its own situation and needs, and involve the relevant stakeholders and experts in the process. References = CRISC 351-400 topic3 Flashcards, Generic IT Risk Scenarios for Risk Analysis: The Greatest Concern
A recent big data project has resulted in the creation of an application used to support important investment decisions. Which of the following should be of GREATEST concern to the risk practitioner?
Data quality
Maintenance costs
Data redundancy
System integration
The greatest concern for the risk practitioner when a big data project has resulted in the creation of an application used to support important investment decisions is the data quality. Data quality is the degree to which the data is accurate, complete, consistent, reliable, relevant, and timely. Data quality is essential for the success of any big data project, as it affects the validity and reliability of the analysis and the outcomes. Poor data quality could lead to erroneous or misleading results, which could have negative consequences for the investment decisions and the organization’s performance and reputation. The other options are not as concerning as the data quality, although they may also pose some challenges or risks for the big data project. Maintenance costs, data redundancy, and system integration are all factors that could affect the efficiency and effectiveness of the big data project, but they do not directly affect the accuracy and reliability of the analysis and the outcomes. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.1, page 3-20.
Accept the residual risk due to the low likelihood of occurrence.
Implement additional mitigation measures.
Determine whether residual risk is within risk appetite.
Adopt a new risk assessment method to avoid the residual risk.
When a risk treatment plan does not reduce residual risk as expected, the immediate next step is to evaluate whether the current level of residual risk remains within the organization ' s defined risk appetite. If the residual risk is acceptable per the risk appetite, it may be tolerable without further mitigation. If it exceeds risk appetite, additional measures should be considered. Changing the risk assessment method is not a direct response to residual risk management. Acceptance should only occur if the risk is within tolerance levels【5:230, 5:231†CRISC_SentenceinNOTE30.pptx】.
Which of the following should be the risk practitioner ' s FIRST course of action when an organization plans to adopt a cloud computing strategy?
Request a budget for implementation
Conduct a threat analysis.
Create a cloud computing policy.
Perform a controls assessment.
Which of the following would BEST indicate to senior management that IT processes are improving?
Changes in the number of intrusions detected
Changes in the number of security exceptions
Changes in the position in the maturity model
Changes to the structure of the risk register
The best indicator to senior management that IT processes are improving is the changes in the position in the maturity model. A maturity model is a framework that defines the levels of capability and performance of a process, such as IT processes, based on the criteria such as governance, management, control, measurement, and improvement. A maturity model can help to assess the current state and the desired state of the IT processes, and to identify the gaps, strengths, and opportunities for improvement. A maturity model can also help to communicate the progress and the value of the IT processes to the senior management, and to support the strategic alignment and integration of the IT processes with the business objectives. Changes in the position in the maturity model indicate that the IT processes are improving, as they show that the IT processes are moving from a lower level to a higher level of maturity, and that they are achieving higher standards of quality, efficiency, and effectiveness. Changes in the number of intrusions detected, changes in the number of security exceptions, and changes to the structure of the risk register are not as good as changes in the position in the maturity model, as they do not provide a comprehensive and consistent measure of the IT processes improvement, and they may not reflect the actual impact and performance of the IT processes. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 36.
The MOST significant benefit of using a consistent risk ranking methodology across an organization is that it enables:
allocation of available resources
clear understanding of risk levels
assignment of risk to the appropriate owners
risk to be expressed in quantifiable terms
The most significant benefit of using a consistent risk ranking methodology across an organization is that it enables a clear understanding of risk levels, as this facilitates the comparison and prioritization of risks, the communication and reporting of risks, and the alignment of risk management with the enterprise’s objectives and strategy. A consistent risk ranking methodology is a set of criteria and scales that are used to measure and rate the likelihood and impact of risks, as well as other factors such as urgency, velocity, and persistence. A consistent risk ranking methodology ensures that the risk assessment results are objective, reliable, and comparable across different business units, processes, and projects. The other options are not the most significant benefits of using a consistent risk ranking methodology,although they may be secondary benefits or outcomes of doing so. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Assessment, page 97.
Which of the following is MOST important for an organization to have in place to identify unauthorized devices on the network?
A technology review and approval process
An acceptable use policy
An automated network scanning solution
A bring your own device (BYOD) policy
Automated scanning tools continuously monitor the network, detecting unauthorized devices quickly and reliably.
An organization recently invested in an identity and access management (IAM) solution to manage user activities across corporate mobile devices. Which of the following is MOST important to update in the risk register?
Inherent risk
Risk appetite
Risk tolerance
Residual risk
Residual risk is the remaining risk after implementing risk responses, such as controls or mitigation strategies. With the deployment of an IAM solution, the organization has addressed certain access-related risks. Updating the risk register to reflect the new residual risk levels ensures accurate tracking and informs future risk management decisions.
Who is the BEST person to an application system used to process employee personal data?
Compliance manager
Data privacy manager
System administrator
Human resources (HR) manager
The data privacy manager is the best person to an application system used to process employee personal data, because they are responsible for ensuring that the organization complies with the applicable data protection laws and regulations, and that the personal data of employees are collected, stored, processed, and disposed of in a secure and ethical manner. The data privacy manager is also responsible for establishing and maintaining the data privacy policies, procedures, and controls, and for conducting data privacy impact assessments and audits. The compliance manager, the system administrator, and the human resources (HR) manager are all involved in the of the application system, but they are not the best person to it, as they do not have the primary accountability and expertise for data privacy. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.2, page 158
A risk practitioner recently discovered that sensitive data from the production environment is required for testing purposes in non-production environments. Which of the following i the BEST recommendation to address this situation?
Enable data encryption in the test environment
Implement equivalent security in the test environment.
Prevent the use of production data for test purposes
Mask data before being transferred to the test environment.
Masking data before being transferred to the test environment is the best recommendation to address the situation where sensitive data from the production environment is required for testing purposes in non-production environments. Data masking is a technique that replaces sensitive data elements with realistic but fictitious data, preserving the format, structure, and meaning of the original data. Data masking ensures that the test data is sufficiently anonymized and de-identified, while still maintaining its functionality and validity for testing purposes. Data masking also reduces the risk of data leakage, exposure, or breach in the test environment, which may have lower security controls than the production environment. The other options are not the best recommendations, as they do not adequately protect the sensitive data or meet the testingrequirements. Enabling data encryption in the test environment may protect the data from unauthorized access, but it does not prevent the data from being decrypted by authorized users who may misuse or mishandle it. Implementing equivalent security in the test environment may be costly, complex, or impractical, and it may not be feasible to replicate the same level of security controls as in the production environment. Preventing the use of production data for test purposes may not be possible or desirable, as production data may be required to ensure the accuracy, reliability, and quality of the testing results. References = P = NP: Cloud dataprotection in vulnerable non-production environments …; Data masking secures sensitive data in non-production environments …; CRISC EXAM TOPIC 2 LONG Flashcards | Quizlet
After undertaking a risk assessment of a production system, the MOST appropriate action is fcr the risk manager to
recommend a program that minimizes the concerns of that production system.
inform the process owner of the concerns and propose measures to reduce them.
inform the IT manager of the concerns and propose measures to reduce them.
inform the development team of the concerns and together formulate risk reduction measures.
The most appropriate action for the risk manager to take after undertaking a risk assessment of a production system is to inform the process owner of the concerns and propose measures to reduce them, as the process owner has the authority and responsibility to manage the production system and its associated risks and controls, and to decide on the optimal risk response. Recommending a program that minimizes the concerns of that production system, informing the IT manager of the concerns and proposing measures to reduce them, and informing the development team of the concerns and together formulating risk reduction measures are not the most appropriate actions, as they may not involve the process owner, who is the key stakeholder and decision maker for the production system and its risks. References = CRISC Review Manual, 7th Edition, page 101.
An IT department has organized training sessions to improve user awareness of organizational information security policies. Which of the following is the BEST key performance indicator (KPI) to reflect effectiveness of the training?
Number of training sessions completed
Percentage of staff members who complete the training with a passing score
Percentage of attendees versus total staff
Percentage of staff members who attend the training with positive feedback
A key performance indicator (KPI) is a metric that reflects how well an organization is achieving its goals and objectives. A KPI should be specific, measurable, achievable, relevant, and time-bound. For an IT department that has organized training sessions to improve user awareness of organizational information security policies, the best KPI to reflect the effectiveness of the training is the percentage of staff members who complete the training with a passing score. This KPI measures the level of knowledge and understanding of the security policies among the staff members, as well as the quality and impact of the training sessions. It also indicates whether the training sessions have met the predefined criteria and standards for success. A high percentage of staff members who complete the training with a passing score implies that the training sessions have been effective in improving user awareness of organizational information security policies. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.2, p. 117-118
An organization has provided legal text explaining the rights and expected behavior of users accessing a system from geographic locations that have strong privacy regulations. Which of the following control types has been applied?
Detective
Directive
Preventive
Compensating
The type of control that has been applied when an organization provides legal text explaining the rights and expected behavior of users accessing a system from geographic locations that have strong privacy regulations is directive. A directive control is a control that guides or instructs the users or the staff on the policies, procedures, or standards that they need to follow or comply with when performing their tasks or activities. A directive control can help to prevent or reduce the risk of non-compliance, errors, or violations, by ensuring that the users or the staff are aware and informed of the expectations and requirements of the organization or the system. A directive control can also help to enforce the accountability and responsibility of the users or the staff, and to support the audit and monitoring of their actions and behaviors. Providing legal text explaining the rights and expected behavior of users accessing a system from geographic locations that have strong privacy regulations is an example of a directive control, as it informs the users of the legal obligations and consequences of using the system, and instructs them on how to protect their privacy and the privacy of others. Detective, preventive, and compensating are not the correct types of control, as they do not match the definition or the purpose of the control that has been applied. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 217.
Which of the following BEST supports the communication of risk assessment results to stakeholders?
Monitoring of high-risk areas
Classification of risk profiles
Periodic review of the risk register
Assignment of risk ownership
A risk profile is a summary of the key risks that affect an organization, a business unit, a process, or a project. A risk profile can help stakeholders understand the current and potential exposure to various sources of uncertainty, and prioritize the risk response accordingly. Classification of risk profiles is the process of grouping and categorizing risks based on common characteristics, such as source, impact, likelihood, or response strategy. Classification of risk profiles can help communicate risk assessment results to stakeholders by providing a clear and consistent way of presenting and comparing risks across different domains, levels, or perspectives. Classification of risk profiles can also help identify patterns, trends, and interrelationships among risks, and facilitate the allocation of resources and responsibilities for risk management. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.1: Risk Profile, p. 193-195.
Which of the following findings of a security awareness program assessment would cause the GREATEST concern to a risk practitioner?
The program has not decreased threat counts.
The program has not considered business impact.
The program has been significantly revised
The program uses non-customized training modules.
The greatest concern for a risk practitioner when reviewing the findings of a security awareness program assessment is that the program uses non-customized training modules. Non-customizedtraining modules are generic and may not address the specific security needs, issues, and challenges of the organization. They may also fail to engage and motivate the employees to follow the security policies and procedures, and to enhance their security knowledge and skills. The program not decreasing threat counts, not considering business impact, or being significantly revised are other possible findings, but they are not as concerning as the program using non-customized training modules. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 7; CRISC Review Manual, 6th Edition, page 202.
Which of the following is a business asset for an organization that runs only in a Software as a Service (SaaS) cloud computing environment?
Hosted data
Platforms
Containers
Security logs
In a SaaS environment, the provider manages infrastructure and platforms. The primary asset that remains under the organization’s control is its hosted data. Hence, data is the key business asset.
Key performance indicators (KPIs) are BEST utilized to provide a high-level overview of:
control efficiency
cost effectiveness
return on investment (ROI)
changes in risk tolerance
KPIs provide metrics that show whether processes and controls are meeting performance targets. CRISC explains that KPIs help identifyhow efficiently controls or processes are operating. They provide a leading view of performance, enabling early identification of inefficiencies that may lead to increased risk. KPIs do not measure cost effectiveness, ROI, or changes in risk tolerance—those belong to financial or strategic measurement systems. Control efficiency aligns directly with KPI use because KPIs measure operational results against objectives.
The risk associated with an asset after controls are applied can be expressed as:
a function of the cost and effectiveness of controls.
the likelihood of a given threat.
a function of the likelihood and impact.
the magnitude of an impact.
The risk associated with an asset after controls are applied can be expressed as a function of the likelihood and impact, as it helps to measure and quantify the residual risk level and exposure. Residual risk is the risk that remains after the implementation of controls or risk treatments. Residual risk can be calculated by multiplying the likelihood and impact of a risk event, where likelihood is the probability or frequency of the risk event occurring, and impact is the consequence or severity of the risk event on the asset or objective. Residual risk can be expressed as:
ResidualRisk=Likelihood×Impact
Expressing the risk associated with an asset after controls are applied as a function of the likelihood and impact helps to provide the following benefits:
It enables a data-driven and evidence-based approach to risk assessment and reporting, rather than relying on subjective or qualitative judgments.
It facilitates a consistent and standardized way of measuring and communicating risk levels and exposure across the organization and to the external stakeholders.
It supports the alignment of risk management and control activities with the organizational strategy and objectives, and helps to evaluate the achievement of the desired outcomes.
It helps to identify and prioritize the areas for improvement and enhancement of the risk management and control processes, and guide the development and implementation of corrective or preventive actions.
It provides feedback and learning opportunities for the risk management and control processes, and helps to foster a culture of continuous improvement and innovation.
The other options are not the best ways to express the risk associated with an asset after controls are applied. A function of the cost and effectiveness of controls is a measure of the inputs or outputs of therisk management and control processes, but it does not indicate the risk level or exposure. The likelihood of a given threat is a component of the risk calculation, but it does not reflect the impact or consequence of the threat. The magnitude of an impact is a component of the risk calculation, but it does not reflect the likelihood or probability of the risk event.References=Risk Assessment and Analysis Methods: Qualitative and Quantitative,IT Risk Resources | ISACA,Residual Risk: Definition, Formula & Management - Video & Lesson …
A robotic process automation (RPA) project has implemented new robots to enhance the efficiency of a sales business process. Which of the following provides the BEST evidence that the new controls have been implemented successfully?
A post-implementation review has been conducted by key personnel.
A qualified independent party assessed the new controls as effective.
Senior management has signed off on the design of the controls.
Robots have operated without human interference on a daily basis.
Independent Assessment:
Objective Evaluation: An assessment by a qualified independent party ensures that the evaluation of the new controls is unbiased and thorough. It provides a credible verification of the control ' s effectiveness.
Expertise and Standards: Independent assessors bring specialized expertise and follow established standards and best practices, ensuring a comprehensive review of the control implementation.
Validation and Assurance: This assessment provides assurance to stakeholders that the controls are functioning as intended and meet the required security and operational standards.
Comparison with Other Options:
Post-Implementation Review by Key Personnel: While valuable, this review may lack the objectivity and thoroughness of an independent assessment.
Senior Management Sign-Off: Sign-off from senior management is important but does not provide the detailed validation of control effectiveness that an independent assessment offers.
Daily Operation of Robots without Human Interference: This indicates operational stability but does not verify that all controls are functioning as intended.
Best Practices:
Regular Independent Assessments: Schedule regular independent assessments to continuously validate the effectiveness of controls.
Comprehensive Reporting: Ensure that the independent assessment includes comprehensive reporting on findings and recommendations for improvement.
Follow-Up Actions: Implement any recommended actions from the assessment to address identified gaps or weaknesses in the controls.
An organization is preparing to transfer a large number of customer service representatives to the sales department. Of the following, who is responsible for mitigating the risk associated with residual system access?
IT service desk manager
Sales manager
Customer service manager
Access control manager
Residual system access is the risk that the customer service representatives who are transferred to the sales department may still have access to the systems or applications that they used in their previous role, which may not be relevant or authorized for their new role.
The access control manager is the person or function who is responsible for defining, implementing, and maintaining the policies and procedures for granting, modifying, reviewing, and revoking access rights to the systems or applications, based on the principle of least privilege and the segregation of duties.
The access control manager is responsible for mitigating the risk associated with residual system access, by ensuring that the access rights of the customer service representatives are updated or removed according to their new role and responsibilities, and that the access changes are documented and approved by the appropriate authorities.
The other options are not responsible for mitigating the risk associated with residual system access. They are either irrelevant or less effective than the access control manager.
The references for this answer are:
Risk IT Framework, page 26
Information Technology & Security, page 20
Risk Scenarios Starter Pack, page 18
A newly enacted information privacy law significantly increases financial penalties for breaches of personally identifiable information (Pll). Which of the following will MOST likely outcome for an organization affected by the new law?
Increase in compliance breaches
Increase in loss event impact
Increase in residual risk
Increase in customer complaints
A loss event is an occurrence that results in a negative consequence or damage for an organization, such as a data breach, a cyberattack, or a natural disaster. The impact of a loss event is the extent or magnitude of the harm or loss caused by the event, such as financial losses, reputational damage, operational disruptions, or legal liabilities. A newly enacted information privacy law that significantly increases financial penalties for breaches of personally identifiable information (PII) will most likely increase the impact of a loss event for an organization affected by the new law, because it will increase the potential cost and severity of a data breach involving PII. The other options are not as likely as an increase in loss event impact, because they do not directly result from the new law, but rather depend on other factors, such as the organization’s risk management capabilities, as explained below:
A. Increase in compliance breaches is not a likely outcome, because it assumes that the organization will not comply with the new law, which would expose it to more risks and penalties. A rational organization would try to comply with the new law by implementing appropriate controls and measures to protect PII and prevent data breaches.
C. Increase in residual risk is not a likely outcome, because it assumes that the organization will not adjust its risk response strategies to account for the new law, which would leave it with more risk exposure than desired. A prudent organization would try to reduce its residual risk by enhancing its risk mitigation controls or transferring its risk to a third party, such as an insurance company.
D. Increase in customer complaints is not a likely outcome, because it assumes that the organization will experience more data breaches involving PII, which would affect its customersatisfaction and loyalty. A responsible organization would try to avoid data breaches by improving its security posture and practices, and by communicating transparently and effectively with its customers about the new law and its implications. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.1.1, page 32.
Within the system development life cycle (SDLC), controls should be specified during:
project initiation
business case development.
system integration testing.
requirements definition.
The correct answer isDbecause controls should be specified during therequirements definitionstage of the SDLC. At this point, business, security, and control requirements are identified and documented so they can be designed into the system from the beginning rather than added later.
The other options are less appropriate:
A. project initiationbegins the project, but detailed control specification occurs later when requirements are defined.
B. business case developmentjustifies the project but does not specify controls in sufficient detail.
C. system integration testingis used to test implemented controls, not to specify them.
Exact Extracts supporting the answer:
“The system development life cycle stage MOST suitable for incorporating internal controls is design.”
“In the system development life cycle the risk practitioner should first become involved during the planning phase.”
“Initiation is the phase in the system development life cycle where risk related to system requirements should be determined.”
“Before moving on to the system design phase it MUST be accomplished that the risk associated with the proposed system and controls is accepted by management.”
These extracts show that controls must be identified before design and implementation, and among the answer choices,requirements definitionis the correct stage for specifying them.
===========
An organization recently implemented new technologies that enable the use of robotic process automation. Which of the following is MOST important to reassess?
Risk profile
Risk tolerance
Risk capacity
Risk appetite
The risk profile is the most important thing to reassess when an organization implements new technologies that enable the use of robotic process automation (RPA). The risk profile is a comprehensive and dynamic view of the organization’s risks, their ratings, responses, and status. RPA can introduce new risks or change the existing risks related to the organization’s objectives, operations, and performance. For example, RPA can create risks such as system failures, databreaches, compliance violations, human errors, or ethical dilemmas. Therefore, the organization should reassess its risk profile to identify, assess, treat, monitor, and review the risks associated with RPA, and to ensure that the risk management strategy is aligned with the business needs and expectations.
Which of the following is a risk practitioner ' s MOST appropriate course of action upon learning that an organization is not compliant with its patch management policy?
Document the concern in an issue tracker.
Strengthen data loss prevention (DLP) controls.
Apply the most recent available patches.
Escalate the issue to the ethics committee.
In order to efficiently execute a risk response action plan, it is MOST important for the emergency response team members to understand:
system architecture in target areas.
IT management policies and procedures.
business objectives of the organization.
defined roles and responsibilities.
In order to efficiently execute a risk response action plan, it is most important for the emergency response team members to understand their defined roles and responsibilities. This can help to ensure that the team members know what they are expected to do, how they should coordinate and communicate with each other, and how they should report the progress and outcome of therisk response. The system architecture in target areas, IT management policies and procedures, and business objectives of the organization are other important factors, but they arenot as important as the defined roles and responsibilities. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 12; CRISC Review Manual, 6th Edition, page 215.
What should a risk practitioner do FIRST when an assessment reveals a control is not operating as intended?
Recommend updates to the control procedures
Determine the root cause of the control issue.
Discuss the status with the control owner.
Recommend compensating controls.
A new international data privacy regulation requires personal data to be
disposed after the specified retention period, which is different from the local
regulatory requirement. Which of the following is the risk practitioner ' s
BEST course of action?
The application code has not been version controlled.
Knowledge of the applications is limited to few employees.
An IT project manager is not assigned to oversee development.
Controls are not applied to the applications.
Which of the following will BEST help to ensure the continued effectiveness of the IT risk management function within an organization experiencing high employee turnover?
Well documented policies and procedures
Risk and issue tracking
An IT strategy committee
Change and release management
The best way to ensure the continued effectiveness of the IT risk management function within an organization experiencing high employee turnover is to have well documented policies and procedures. Policies and procedures are the formal documents that define the roles, responsibilities, processes, and standards for the IT risk management function. They provide guidance, consistency, and continuity for the IT risk management activities and outcomes. They also facilitate the knowledge transfer, training, and performance evaluation of the IT risk management staff. The other options are not as helpful as well documented policies and procedures, as they are related to the tools, mechanisms, or structures that support the IT risk management function, not the foundation and direction of the IT risk managementfunction. References = Risk and Information Systems Control Study Manual, Chapter 1: IT Risk Identification, Section 1.1: IT Risk Management Process, page 15.
Which of the following is the MOST important reason for a risk practitioner to continuously monitor a critical security transformation program?
To validate the quality of defined deliverables for the program
To detect increases in program costs
To ensure program risk events are mitigated in a timely manner
To provide timely reporting to the governance steering committee
Continuously monitoring a critical security transformation program is crucial for a risk practitioner primarily to ensure that any risk events are identified and mitigated promptly. This ensures that the security transformation remains on track and that potential risks do not escalate to a level that could compromise the program’s success.
Identifying and Mitigating Risks:
Risk Identification:Continuously monitoring the program helps in the early identification of risks. This is essential because unidentified risks can lead to unexpected issues that might derail the program.
Timely Mitigation:Once risks are identified, it is crucial to mitigate them as quickly as possible. Delays in mitigation can allow risks to grow in impact, making them harder and more expensive to address.
Ensuring Program Continuity:
Maintaining Momentum:Security transformation programs often involve significant changes and can be disruptive. By ensuring that risks are mitigated in a timely manner, the risk practitioner helps maintain the program’s momentum and keeps it on schedule.
Preventing Escalation:Timely risk mitigation prevents minor issues from escalating into major problems that could halt the program.
Aligning with Strategic Goals:
Strategic Alignment:Ensuring timely mitigation of risks helps in keeping the program aligned with the strategic goals of the organization. It ensures that the security objectives are met without significant delays or cost overruns.
Which of the following is MOST helpful to ensure effective security controls for a cloud service provider?
A control self-assessment
A third-party security assessment report
Internal audit reports from the vendor
Service level agreement monitoring
A third-party security assessment report is the most helpful to ensure effective security controls for a cloud service provider, because it provides an independent and objective evaluation of the cloud provider’s security posture, policies, and practices. A third-party security assessment report can help to verify and validate the cloud provider’s compliance with the relevant standards, regulations, and best practices, such as ISO 27001, PCI DSS, NIST, or CSA. A third-party security assessment report can also help to identify and address any gaps, weaknesses, or vulnerabilities in the cloud provider’s security controls, and to provide recommendations and guidance for improvement. A third-party security assessment report can also help to increase the trust and confidence of the cloud customers, and to facilitate the due diligence and risk management processes. The other options are less helpful to ensure effective security controls for a cloud service provider. A control self-assessment is a process that enables the cloud provider to assess its own security controls, using a predefined framework or questionnaire. However, a control self-assessment may not be as reliable or comprehensive as a third-party security assessment report, as it may be biased, incomplete, or inaccurate, and it may not cover all the aspects or dimensions of security. Internal audit reports from the vendor are documents that provide the results and findings of the internal audits conducted by the cloud provider’s ownauditors, to verify and validate the effectiveness and efficiency of the securitycontrols. However, internal audit reports from the vendor may not be as credible or trustworthy as a third-party security assessment report, as they may be influenced by the cloud provider’s interests, objectives, or agenda, and they may not follow the same standards or criteria as the external auditors. Service level agreement monitoring is a process that measures and evaluates the performance and availability of the cloud services, based on the predefined metrics and targets agreed between the cloud provider and the cloud customer. However, service level agreement monitoring may not be sufficient or relevant to ensure effective security controls for a cloud service provider, as it may not address the security aspects or requirements of the cloud services, such as confidentiality, integrity, or accountability, and it may not reflect the actual security risks or incidents that may occur in the cloud environment. References = Cloud Security Controls: Key Elements and 4 Control Frameworks 1
As part of its risk strategy, an organization decided to transition its financial system from a cloud-based provider to an internally managed system. Which of the following should the risk practitioner do FIRST?
Reassess whether the risk responses properly address known risks and vulnerabilities
Analyze the risk register to identify potential updates and changes
Evaluate existing control test plans of the system for potential changes
Update the processes within impacted financial control assessments
Whenever there is achange in sourcing strategy, such as moving from cloud to internal hosting, thefirst stepis to reassess theeffectiveness and completeness of existing risk responsesand confirm that they still mitigate the risks appropriately.
CRISC emphasizes:
“When transitioning services or changing control environments, practitioners should reassess risk responses and validate that previously identified risks and vulnerabilities remain properly addressed.”
Only after reassessment should the practitioner proceed to update registers, controls, and audit plans.
Hence,Ais the correct answer.
CRISC Reference:Domain 3 – Risk Response and Mitigation, Topic: Managing Control Changes.
Which of the following is the MOST significant risk associated with using cloud computing for disaster recovery?
Cloud vendor lock-in and dependency
Lack of adequate incident management capabilities
Use of multiple cloud access service brokers (CASBs)
Availability issues with cloud storage solutions
In cloud-based disaster recovery, CRISC emphasizes that the most impactful strategic risk isvendor lock-in and dependency. When disaster recovery capabilities rely on a single cloud provider, organizations become fully dependent on that provider’s technology, APIs, and platform architecture. This dependency makes it difficult and costly to migrate to another provider, limits flexibility in recovery options, and increases exposure if the provider experiences outages or changes service terms. While availability issues, CASB usage, and incident management gaps are important, they do not present the same level of strategic long-term operational and resilience impact as vendor lock-in.
Which of the following is the BEST evidence that risk management is driving business decisions in an organization?
Compliance breaches are addressed in a timely manner.
Risk ownership is identified and assigned.
Risk treatment options receive adequate funding.
Residual risk is within risk tolerance.
Risk treatment options are the actions or plans that are implemented to modify or reduce the risk exposure of the organization. Risk treatment options receive adequate funding when the organization allocatessufficient resources and budget to support the risk response actions, and to ensure that the risk controls are effective and efficient. This is the best evidence that risk management is driving business decisions in the organization, as it shows that the organizationprioritizes and values the risk management process, and that it aligns its risk strategy and objectives with its business goals and value creation. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question 245. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 245. CRISC Sample Questions 2024, Question 245.
An unauthorized individual has socially engineered entry into an organization ' s secured physical premises. Which of the following is the BEST way to prevent future occurrences?
Employ security guards.
Conduct security awareness training.
Install security cameras.
Require security access badges.
Social engineering is a technique that involves manipulating or deceiving people into performing actions or divulging information that may compromise the security of an organization or its data12.
Entry into an organization’s secured physical premises is a form of physical access that allows an unauthorized individual to access, steal, or damage the organization’s assets, such as equipment, documents, or systems34.
The best way to prevent future occurrences of social engineering entry into an organization’s secured physical premises is to conduct security awareness training, which is an educational program that aims to equip the organization’s employees with the knowledge and skills they need to protect the organization’s data and sensitive information from cyber threats, such as hacking, phishing, or other breaches56.
Security awareness training is the best way because it helps the employees to recognize and resist the common and emerging social engineering techniques, such as tailgating,impersonation, or pretexting, that may be used by the attackers to gain physical access to the organization’s premises56.
Security awareness training is also the best way because it fosters a culture of security and responsibility among the employees, and encourages them to follow the best practices andpolicies for physical security, such as locking the doors, verifying the identity of visitors, or reporting any suspicious activities or incidents56.
The other options are not the best way, but rather possible measures or controls that may supplement or enhance the security awareness training. For example:
Employing security guards is a measure that involves hiring or contracting professional personnel who are trained and authorized to monitor, patrol, and protect the organization’s premises from unauthorized access or intrusion78. However, this measure is not the best way because it may not be sufficient or effective to prevent or deter all types of social engineering attacks, especially if the attackers are able to bypass, deceive, or coerce the security guards78.
Installing security cameras is a control that involves using electronic devices that capture and record the visual images of the organization’s premises, and provide evidence or alerts of any unauthorized access or activity . However, this control is not the best way because it is reactive rather than proactive, and may not prevent or stop the social engineering attacks before they cause any harm or damage to the organization .
Requiring security access badges is a control that involves using physical or electronic cards that identify and authenticate the employees or authorized visitors who are allowed to enter the organization’s premises, and restrict or deny the access to anyone else . However, this control is not the best way because it may not be foolproof or reliable to prevent or detect the social engineering attacks, especially if the attackers are able to steal, forge, or clone the security access badges . References =
1: What is Social Engineering? | Types & Examples of Social Engineering Attacks1
2: Social Engineering: What It Is and How to Prevent It | Digital Guardian2
3: What is physical Social Engineering and why is it important? - Integrity3603
4: What Is Tailgating (Piggybacking) In Cyber Security? - Wlan Labs4
5: What Is Security Awareness Training and Why Is It Important? - Kaspersky5
6: Security Awareness Training - Cybersecurity Education Online | Proofpoint US6
7: Security Guard - Wikipedia7
8: Security Guard Services - Allied Universal8
Security Camera - Wikipedia
Security Camera Systems - The Home Depot
Access Badge - Wikipedia
Access Control Systems - HID Global
Which of the following is the MOST important characteristic when designing a key risk indicator (KRI)?
It is linked to a key performance indicator (KPI)
It is linked to a key control indicator (KCI)
It contains an objective alert threshold
It aligns with industry benchmarks
For a KRI to be actionable and effective, it must haveobjective thresholds. These thresholds act as triggers for decision-making and allow for timely response before risk materializes.
An organization is planning to implement a Zero Trust model. From a cybersecunty perspective, which of the following is MOST important to ensure successful alignment with the overall inten Zero Trust?
Access policies
Industry benchmarks
Network compatibility
Encryption algorithms
Which of the following is a risk practitioner ' s MOST important action to reduce the likelihood of internal fraud?
Recommend fraud awareness training for staff
Communicate legal consequences for internal fraud.
Update the internal fraud risk likelihood in the risk register.
Verify the effectiveness of separation of duties.
The correct answer isDbecause the most important action to reduce the likelihood of internal fraud is toverify the effectiveness of separation of duties. Separation of duties is a core preventive control that reduces the opportunity for fraudulent activity by ensuring no single individual has end-to-end control over critical transactions or processes.
The other options are less effective:
A. Recommend fraud awareness training for staffis useful, but it is not as strong a preventive control as segregation of duties.
B. Communicate legal consequences for internal fraudmay deter misconduct, but it does not directly reduce control weakness.
C. Update the internal fraud risk likelihood in the risk registeris documentation, not risk reduction.
Exact Extracts supporting the answer:
“The PRIMARY reason that an enterprise would establish segregation of duties controls is to prevent errors or fraudulent activity on high-risk transactions.”
“The MOST effective control to prevent segregation of duties violations is implementing role-based access.”
“The control that focuses directly on preventing the risk of collusion is mandatory job rotation.”
“An independent review of audit logs is the best compensating control when a segregation of duties conflict exists in a small IT department.”
These extracts show that preventive control effectiveness, especially segregation of duties, is the strongest way to reduce the likelihood of internal fraud.
Which of the following is a risk practitioner ' s BEST recommendation to help reduce IT risk associated with scheduling overruns when starting a new application development project?
Implement a tool to track the development team ' s deliverables.
Review the software development life cycle.
Involve the development team in planning.
Assign more developers to the project team.
Involve the development team in planning is the best recommendation to help reduce IT risk associated with scheduling overruns when starting a new application development project. This is because involving the development team in planning can help ensure that the project scope, requirements, resources, and timeline are realistic, feasible, and agreed upon by all stakeholders. It can also help improve the communication, collaboration, and commitment of the development team, as well as identify and mitigate potential risks and issues early in the project life cycle. According to the CRISC Review Manual 2022, one of the key risk identification techniques for IT projects is to involve the project team and other relevant parties in the risk assessment process1. According to the CRISC Review Questions, Answers & Explanations Manual 2022, involving the development team in planning is the correct answer to this question2.
Implementing a tool to track the development team’s deliverables, reviewing the software development life cycle, and assigning more developers to the project team are not the best recommendations to help reduce IT risk associated with scheduling overruns. These are possible actions that can be taken during or after the planning phase, but they do not address the root cause of the risk, which is the lack of involvement of the development team in planning. Implementing a tool to track the development team’s deliverables can help monitor the project progress and performance, but it does not guarantee that the deliverables are aligned with the project objectives and expectations. Reviewing the software development life cycle can help ensure that the project follows a structured and standardized process, but it does not account for the specific needs and challenges of the project. Assigning more developers to the project team can help increase the project capacity and productivity, but it can also introduce new risks such as coordination, communication, and quality issues.
Which of the following is the PRIMARY reason to adopt key control indicators (KCIs) in the risk monitoring and reporting process?
To provide data for establishing the risk profile
To provide assurance of adherence to risk management policies
To provide measurements on the potential for risk to occur
To provide assessments of mitigation effectiveness
Key control indicators (KCIs) are metrics that measure the performance and effectiveness of the controls that are implemented to mitigate the risks. KCIs can help to monitor the status and health of the controls, as well as to identify any issues or gaps that need to be addressed. The primary reason to adopt KCIs in the risk monitoring and reporting process is to provideassessments of mitigation effectiveness, meaning that they can help to evaluate how well the controls are reducing the risk exposure and achieving the desired outcomes. KCIs can also help to support the risk management decision making and improvement actions, as well as to demonstrate the value and benefits of the controls. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.1.2, p. 115-116
Who is MOST appropriate to be assigned ownership of a control
The individual responsible for control operation
The individual informed of the control effectiveness
The individual responsible for resting the control
The individual accountable for monitoring control effectiveness
A control is a measure or action that is implemented to reduce the likelihood or impact of a risk event, or to enhance the benefits or opportunities of a risk event. A control owner is a person who is assigned the responsibility and authority for the design, implementation, operation, and maintenance of a control. The most appropriate person to be assigned ownership of a control is the individual accountable for monitoring control effectiveness, which is the process of measuring and evaluating the performance and compliance of the control. By assigning the control ownership to the individual accountable for monitoring control effectiveness, the organization can ensure that the control is aligned with the risk objectives, operates as intended, and delivers the expected results. References = 4
Which of the following would present the MOST significant risk to an organization when updating the incident response plan?
Obsolete response documentation
Increased stakeholder turnover
Failure to audit third-party providers
Undefined assignment of responsibility
The most significant risk to an organization when updating the incident response plan is the undefined assignment of responsibility. An incident response plan is a document that defines the roles, responsibilities, procedures, and resources for responding to an incident that could disrupt the normal operations of the organization, or compromise its assets, reputation, or compliance. An incident response plan should clearly assign the responsibility for each task and activity involved in the incident response process, such as detection, containment, analysis, eradication, recovery, and reporting. Undefined assignment of responsibility could lead to confusion, duplication, conflict, or omission among the stakeholders, and impair the effectiveness and efficiency of the incident response process. Undefined assignment of responsibility could also increase the risk of escalation, recurrence, or impact of the incident, and affect the accountability and performance of the organization. Obsolete response documentation, increased stakeholder turnover, and failure to audit third-party providers are also risks, but they are not as significant as undefined assignment of responsibility, as they do not directly affect the execution and outcome of the incident response process. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 130.
An organization with a large number of applications wants to establish a security risk assessment program. Which of the following would provide the MOST useful information when determining the frequency of risk assessments?
Feedback from end users
Results of a benchmark analysis
Recommendations from internal audit
Prioritization from business owners
A benchmark analysis is a process of comparing the organization’s performance, practices, and processes with those of other organizations in the same industry or sector. A benchmark analysis can provide the most useful information when determining the frequency of risk assessments, because it can help the organization to identify the best practices, standards, and expectations for security risk management in its industry. A benchmark analysis can also help the organization to assess its current level of maturity, capability, and compliance in relation to security risk management, and to determine the gaps and areas for improvement. By conducting a benchmark analysis, the organization can establish a realistic and appropriate frequency of risk assessments that aligns with its industry norms and its own risk profile. The other options are not as useful as a benchmark analysis, because they do not provide a comprehensive and relevant view of the security risk management landscape, but rather focus on specific or partial aspects of the organization’s situation. References = Risk and Information Systems Control Study Manual, Chapter 1, Section 1.3.2, page 18.
Which of the following is MOST important for a risk practitioner to consider when evaluating plans for changes to IT services?
Change testing schedule
Impact assessment of the change
Change communication plan
User acceptance testing (UAT)
According to the CRISC Review Manual1, impact assessment is the process of identifying and evaluating the potential effects of changes to IT services on the organization’s business objectives, processes, resources, and risks. Impact assessment is essential for ensuring that the changes are aligned with the organization’s strategy, goals, and risk appetite, and that the benefits of the changes outweigh the costs and risks. Impact assessment also helps to prioritize, plan, and implement the changes effectively and efficiently, and to monitor and measure the outcomes of the changes. Therefore, the most important factor for a risk practitioner to consider when evaluating plans for changes to IT services is the impact assessment of the change. References = CRISC Review Manual1, page 224.
Which of the following is a risk practitioner ' s MOST important course of action when the level of risk has exceeded risk tolerance?
Facilitate a review of risk tolerance levels
Adjust the risk impact and likelihood scale
Revise key risk indicator (KRI) thresholds
Introduce the risk treatment process
When risk exceeds tolerance, the appropriate action is to engage the risk treatment process. This involves evaluating and implementing appropriate responses such as mitigation, transfer, or acceptance.
Which of the following observations would be the GREATEST concern to a risk practitioner evaluating an organization ' s risk management practices?
Senior management has approved numerous requests for risk acceptance.
Business leaders provide final approval for information security policies.
Several risk scenarios have action plans spanning multiple years.
Senior management does not set risk tolerance.
A penetration test reveals several vulnerabilities in a web-facing application. Which of the following should be the FIRST step in selecting a risk response?
Correct the vulnerabilities to mitigate potential risk exposure.
Develop a risk response action plan with key stakeholders.
Assess the level of risk associated with the vulnerabilities.
Communicate the vulnerabilities to the risk owner.
The first step in selecting a risk response after a penetration test reveals several vulnerabilities in a web-facing application is to assess the level of risk associated with the vulnerabilities, as it involves evaluating the likelihood and impact of the vulnerabilities being exploited, and comparing them with the risk tolerance and appetite of the organization. Correcting the vulnerabilities, developing a risk response action plan, and communicating the vulnerabilities are possible steps in selecting a risk response, but they are not the first step, as they require the prior knowledge of the risk level and the optimal risk response. References = CRISC Review Manual, 7th Edition, page 108.
Which of the following should be the PRIMARY input to determine risk tolerance?
Regulatory requirements
Organizational objectives
Annual loss expectancy (ALE)
Risk management costs
Organizational objectives should be the primary input to determine risk tolerance, as they define the desired outcomes and performance of the organization, and guide the selection of the acceptable level of risk that the organization is willing to take to achieve those objectives. Regulatory requirements, annual loss expectancy (ALE), and risk management costs are not the primary inputs, as they are more related to the external or internal constraints or factors that affect the risk tolerance, rather than the drivers or determinants of the risk tolerance. References = CRISC Review Manual, 7th Edition, page 109.
Periodically reviewing and updating a risk register with details on identified risk factors PRIMARILY helps to:
minimize the number of risk scenarios for risk assessment.
aggregate risk scenarios identified across different business units.
build a threat profile of the organization for management review.
provide a current reference to stakeholders for risk-based decisions.
A risk register is a document that records and tracks the information and status of the identified risks and their responses. It includes the risk description, category, source, cause, impact, probability, priority, response, owner, action plan, status, etc.
Periodically reviewing and updating a risk register with details on identified risk factors primarily helps to provide a current reference to stakeholders for risk-based decisions, which are the decisions that are made based on the consideration and evaluation of the risks and their responses. Providing a current reference to stakeholders for risk-based decisions helps to ensure that the decisions are consistent, appropriate, and proportional to the level and nature of the risks, and that they support the organization’s objectives and values. It also helps to optimize the balance between risk and return, and to create and protect value for the organization and its stakeholders.
The other options are not the primary benefits of periodically reviewing and updating a risk register with details on identified risk factors, because they do not address the main purpose and benefit of a risk register, which is to provide a current reference to stakeholders for risk-based decisions.
Minimizing the number of risk scenarios for risk assessment means reducing the scope and depth of risk analysis and reporting, and impairing the organization’s ability to identify and respond to emerging or changing risks. Periodically reviewing and updating a risk register with details onidentified risk factors does not necessarily minimize the number of risk scenarios for risk assessment, and it may not be a desirable or beneficial outcome for the organization.
Aggregating risk scenarios identified across different business units means combining or consolidating the risks that are identified by different parts or functions of the organization, and creating a holistic or integrated view of the organization’s risk profile. Periodically reviewing and updating a risk register with details on identified risk factors does not necessarily aggregate risk scenarios identified across different business units, and it may not be a sufficient or effective way to achieve a holistic or integrated view of the organization’s risk profile.
Building a threat profile of the organization for management review means creating or developing a summary or representation of the potential threats or sources of harm that may affect the organization’s objectives and operations, and presenting or reporting it to the senior management for their awareness and approval. Periodically reviewing and updating a risk register with details on identified risk factors does not necessarily build a threat profile of the organization for management review, and it may not be a comprehensive or reliable way to create or develop a summary or representation of the potential threats or sources of harm that may affect the organization. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 172
CRISC Practice Quiz and Exam Prep
What should be the PRIMARY consideration related to data privacy protection when there are plans for a business initiative to make use of personal information?
Do not collect or retain data that is not needed.
Redact data where possible.
Limit access to the personal data.
Ensure all data is encrypted at rest and during transit.
Which of the following is the PRIMARY reason for a risk practitioner to report changes and trends in the IT risk profile to senior management?
To ensure risk owners understand their responsibilities
To ensure IT risk is managed within acceptable limits
To ensure the organization complies with legal requirements
To ensure the IT risk awareness program is effective
The primary reason for a risk practitioner to report changes and trends in the IT risk profile to senior management is to ensure that IT risk is managed within acceptable limits, because it helps to inform and advise the senior management on the current state and direction of IT risk, and to support the risk-based decision making and prioritization. An IT risk profile is a summary of the key IT risks that an organization faces, and their implications for the organization’s objectives and strategy. An IT risk profile may change or evolve over time, due to factors such as newtechnologies, business initiatives, or external events. Reporting changes and trends in the IT risk profile to senior management is the primary reason, as it helps to ensure that the senior management is aware of and prepared for the IT risk challenges and opportunities, and that the IT risk is managed within the acceptable limits defined by the organization’s risk appetite and tolerance. To ensure risk owners understand their responsibilities, to ensure the organization complies with legal requirements, and to ensure the IT risk awareness program is effective are all possible reasons for reporting changes and trends in the IT risk profile, but they are not the primary reason, as they are not directly related to the management of IT risk within acceptable limits. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.3, page 91
IT stakeholders have asked a risk practitioner for IT risk profile reports associated with specific departments to allocate resources for risk mitigation. The BEST way to address this request would be to use:
the cost associated with each control.
historical risk assessments.
key risk indicators (KRls).
information from the risk register.
The best way to address the request for IT risk profile reports associated with specific departments would be to use key risk indicators (KRIs), which are metrics that provide information on the level of exposure to a given operational risk1. KRIs can help to monitor the changes in risk levels over time, identify emerging risks, and trigger risk response actions when the risk exceeds the acceptable thresholds2. KRIs can also help to allocate resources for risk mitigation by prioritizing the risks that pose the greatest threat to the business objectives and performance of each department. The other options are not the best ways to address the request, as they do not provide the same level of insight and guidance as KRIs. The cost associated with each control may indicate the efficiency of the risk mitigation, but not the effectiveness or the necessity. Historical risk assessments may provide some baseline data, but not the current or future risk trends. Information from the risk register may include too much detail or irrelevant information, and not the key risk factors that need to be monitored and reported. References = Key Risk Indicators; Key Risk Indicators: A Practical Guide
Which of the following is MOST important for the organization to consider before implementing a new in-house developed artificial intelligence (Al) solution?
Industry trends in Al
Expected algorithm outputs
Data feeds
Alert functionality
The most important factor for the organization to consider before implementing a new in-house developed artificial intelligence (AI) solution is the expected algorithm outputs, as they define the desired outcomes and objectives of the AI solution, and guide the design, testing, and validation of the AI algorithm. The other options are not the most important factors, as they are more related to the research, input, or monitoring of the AI solution, respectively, rather than the output of the AI solution. References = CRISC Review Manual, 7th Edition, page 153.
Which of the following is the PRIMARY role of the first line within the three lines model?
Maintaining effective internal controls
Providing oversight and governance
Conducting independent audits
Establishing the organization’s risk appetite
In theThree Lines Model, thefirst line(operational management) owns and manages risk through daily operations.
Per ISACA:
“Operational management, as the first line of defense, is responsible for maintaining effective internal controls and executing risk management processes.”
Oversight is the second line’s role; audits belong to the third line.
Hence,Ais correct.
CRISC Reference:Domain 1 – IT Risk Governance, Topic: Three Lines of Defense Model.
Which of the following should be determined FIRST when a new security vulnerability is made public?
How severe the vulnerability is across the industry
Whether the affected technology is internet-facing
Whether the affected technology is used within the organization
What mitigating controls are currently in place
The very first action in vulnerability management is confirmingwhether the affected technology exists in the organization’s environment.
CRISC notes:
“Before prioritizing or mitigating, it is critical to determine whether the enterprise uses the affected asset or service.”
If the organization isnot usingthe affected technology, no further response is required.
After that, severity and mitigating controls are reviewed.
Hence,Cis correct.
CRISC Reference:Domain 2 – IT Risk Assessment, Topic: Vulnerability and Asset Validation.
After an annual risk assessment is completed, which of the following would be MOST important to communicate to stakeholders?
A decrease in threats
A change in the risk profile
An increase in reported vulnerabilities
An increase in identified risk scenarios
A change in the risk profile would be the most important information to communicate to stakeholders after an annual risk assessment is completed, as it indicates how the risk landscape of the organization has changed over time, and how it affects the achievement of the business goals and objectives. A decrease in threats, an increase in reported vulnerabilities, and an increase in identified risk scenarios are also important information, but they are not the most important, as they are specific aspects of the risk profile, and do not provide a holistic view of the risk exposure and appetite of the organization. References = CRISC Review Manual, 7th Edition, page 109.
Which risk response strategy could management apply to both positive and negative risk that has been identified?
Transfer
Accept
Exploit
Mitigate
Accepting risk is the only risk response strategy that could be applied to both positive and negative risk that has been identified. Accepting risk means taking no action to change the likelihood or impact of the risk, but being prepared to deal with the consequences if the risk occurs. Accepting risk is usually chosen when the risk is low, unavoidable, or outweighed by the benefits. For positive risks, accepting risk means taking advantage of the opportunities if they arise. For negative risks, accepting risk means setting aside contingency reserves or plans to copewith the threats. The other risk response strategies are specific to either positive or negative risks. Transfer, exploit, and mitigate are strategies for negative risks, while share, enhance, and avoid are strategies for positive risks. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-23.
An organization has established a single enterprise-wide risk register that records high-level risk scenarios. The IT risk department has created its own register to record more granular scenarios applicable to IT. Which of the following is the BEST way to ensure alignment between these two registers?
Map the granular risk scenarios to the high-level risk register items.
List application and server vulnerabilities in the IT risk register.
Identify overlapping risk scenarios between the two registers.
Maintain both high-level and granular risk scenarios in a single register.
Mapping granular scenarios to high-level register items ensures consistency and alignment across different levels of risk management. This approach supportsIntegrated Risk Management Frameworks.
Which of the following is the BEST approach to use when creating a comprehensive set of IT risk scenarios?
Derive scenarios from IT risk policies and standards.
Map scenarios to a recognized risk management framework.
Gather scenarios from senior management.
Benchmark scenarios against industry peers.
IT risk scenarios are the descriptions or representations of the possible or hypothetical situations or events that may cause or result in an IT risk for the organization. IT risk scenarios usually consist of three elements: a threat or source of harm, a vulnerability or weakness, and an impact or consequence.
The best approach to use when creating a comprehensive set of IT risk scenarios is to map scenarios to a recognized risk management framework, which is an established or recognized model or standard that provides the principles, guidelines, and best practices for the organization’s IT risk management function. Mapping scenarios to a recognized risk management framework can help the organization to create a comprehensive set of IT risk scenarios by providing the following benefits:
It can ensure that the IT risk scenarios are relevant, appropriate, and proportional to the organization’s IT objectives and needs, and that they support the organization’s IT strategy and culture.
It can ensure that the IT risk scenarios are consistent and compatible with the organization’s IT governance, risk management, and control functions, and that they reflect the organization’s IT risk appetite and tolerance.
It can provide useful references and benchmarks for the identification, analysis, evaluation, and communication of the IT risk scenarios, and for the alignment and integration of the IT risk scenarios with the organization’s IT risk policies and standards.
The other options are not the best approaches to use when creating a comprehensive set of IT risk scenarios, because they do not provide the same level of detail and insight that mapping scenarios to a recognized risk management framework provides, and they may not be specific or applicable to the organization’s IT objectives and needs.
Deriving scenarios from IT risk policies and standards means creating or generating the IT risk scenarios based on the rules or guidelines that define and describe the organization’s IT risk management function, and that specify the expectations and requirements for the organization’s IT risk management function. Deriving scenarios from IT risk policies and standards can help the organization to create a consistent and compliant set of IT risk scenarios, but it is not the best approach, because it may not cover all the relevant or significant IT risks that may affect the organization, and it may not support the organization’s IT strategy and culture.
Gathering scenarios from senior management means collecting or obtaining the IT risk scenarios from the senior management or executives that oversee or direct the organization’s IT activities or functions. Gathering scenarios from senior management can help the organization to create a high-level and strategic set of IT risk scenarios, but it is not the best approach, because it may not reflect the operational or technical aspects of the IT risks, and it may not involve the input or feedback from the other stakeholders or parties that are involved or responsible for the IT activities or functions.
Benchmarking scenarios against industry peers means comparing and contrasting the IT risk scenarios with those of other organizations or industry standards, and identifying the strengths, weaknesses, opportunities, or threats that may affect the organization’s IT objectives oroperations. Benchmarking scenarios against industry peers can help the organization to create a competitive and innovative set of IT risk scenarios, but it is not the best approach, because it may not be relevant or appropriate for the organization’s IT objectives and needs, and it may not comply with the organization’s IT policies and standards. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 199
CRISC Practice Quiz and Exam Prep
To effectively address ethical risk within an organization, who MUST ensure the ethics policy is enforced and equally applied to all levels of authority ' ?
Local authorities and regulators
Ethics and compliance team
Senior management
Internal audit team
Which of the following is the BEST way for a risk practitioner to consolidate the results of risk assessments across multiple operating units?
Implement a governance, risk, and compliance (GRC) system.
Update departmental risk registers with items from the central risk register.
Aggregate operating unit risk registers to a central risk register.
Perform additional risk assessments and create an enterprise risk matrix.
The BEST answer is C because consolidation should roll up operating-unit risk assessment results into a central enterprise view. Operating units own and identify their local risks, but the enterprise needs an aggregated risk profile for decision-making. The uploaded CRISC notes state that the risk register is the best tool for identifying changes in the enterprise risk profile and that aggregated risk to the enterprise is the most important aspect of a risk profile. They also state that a centrally published risk register with workflow features is the best way to maintain accuracy over time.
ISACA explains that a risk register is a collection of identified risk scenarios incorporated into the enterprisewide risk profile, and that risk registers document risk areas and rank them by likelihood and impact. ISACA’s CRISC outline also includes maintaining or establishing the information system risk register and incorporating it into the enterprisewide risk profile.
A is incorrect because a GRC system is only a tool; it does not define the consolidation approach. B is reversed because enterprise consolidation should aggregate from departmental/unit registers into the central view, not push central items down first. D is unnecessary if operating-unit assessments already exist; creating an enterprise matrix may help reporting, but the best consolidation method is a central risk register.
As pan of business continuity planning, which of the following is MOST important to include m a business impact analysis (BlA)?
An assessment of threats to the organization
An assessment of recovery scenarios
industry standard framework
Documentation of testing procedures
As part of business continuity planning, the most important thing to include in a business impact analysis (BIA) is an industry standard framework. A BIA is a process of identifying and analyzing the potential effects of disruptions to the critical business functions and processes. An industry standard framework is a set of best practices, guidelines, and methodologies that provide a consistent and comprehensive approach to conducting a BIA. An industry standard framework can help to ensure that the BIA is complete, accurate, and reliable, and that it covers all the relevant aspects, such as the scope, objectives, criteria, methods, data sources, and reporting. An industry standard framework can also help to benchmark the BIA results against the industry norms and expectations, and to align the BIA with the business continuity strategy and plan. The other options are not as important as an industry standard framework, as they are related to the specific steps, activities, or outputs of the BIA, not the overall structure and quality of the BIA. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.4: Key Control Indicators, page 211.
A control owner identifies that the organization ' s shared drive contains personally identifiable information (Pll) that can be accessed by all personnel. Which of the following is the MOST effective risk response?
Protect sensitive information with access controls.
Implement a data loss prevention (DLP) solution.
Re-communicate the data protection policy.
Implement a data encryption solution.
Personally identifiable information (PII) is any information that can be used to identify, contact, or locate an individual, such as name, address, phone number, email, social security number, etc1. PII is subject to various laws and regulations that aim to protect the privacy and security of individuals’data1. Organizations that collect, store, process, or transmit PII have a responsibility to safeguard it from unauthorized access, use, disclosure, modification, or destruction1.
One of the best practices for protecting PII is to implement access controls, which are mechanisms that restrict access to PII based on the principle of least privilege2. Access controls ensure that only authorized personnel who have a legitimate need to access PII can do so, and that they can only perform the actions that are necessary for their roles and responsibilities2. Access controls can be implemented at different levels, such as network, system, application, or data level, and can use various methods, such as passwords, tokens, biometrics, encryption, etc2.
If an organization’s shared drive contains PII that can be accessed by all personnel, this poses a high risk of data breach, theft, loss, or misuse, which could result in legal, financial, reputational, or operational consequences for the organization and the individuals whose data is compromised3. Therefore, the most effective risk response is to protect the sensitive information with access controls, such as:
Classify the PII according to its sensitivity and impact level, and assign appropriate labels and permissions to the data files and folders2.
Restrict access to the shared drive to only those personnel who have a valid business reason to access the PII, and grant them the minimum level of access required to perform their tasks2.
Implement strong authentication and authorization mechanisms, such as multifactor authentication, role-based access control, or attribute-based access control, to verify the identity and privileges of the users who access the shared drive2.
Encrypt the PII stored on the shared drive, and use secure protocols and channels to transmit the data over the network2.
Monitor and audit the access and activities on the shared drive, and generate logs and reports to detect and respond to any unauthorized or anomalous events2.
The other options are not as effective as access controls, because they do not directly address the root cause of the risk, which is the lack of access restrictions on the shared drive. Implementing a data loss prevention (DLP) solution, which is a tool that monitors and prevents the leakage of sensitive data, may help to detect and block some unauthorized data transfers, but it does not prevent unauthorized access or viewing of the PII on the shared drive4. Re-communicating the data protection policy, which is a document that defines the rules and responsibilities for handling PII, may help to raise awareness and compliance among the personnel, but it does not enforce or verify the actual implementation of the policy. Implementing a data encryption solution, which is a technique that transforms the PII into an unreadable format, may helpto protect the confidentiality of the data, but it does not prevent unauthorized access or modification of the data, and it may introduce additional complexity and overhead to the data management process.
References = Guide to Protecting the Confidentiality of Personally Identifiable Information (PII), Best Practices for Protecting PII, How to Secure Personally Identifiable Information against Loss or Compromise, Data Loss Prevention (DLP) | Microsoft 365 security, [Protecting Personal Information: A Guide for Business], [Encryption - Wikipedia]
Which of the following presents the GREATEST security risk to an organization with a large number of Internet of Things (IoT) devices within its network?
Inadequate network bandwidth
Lack of interoperability between IoT devices
Insufficient IoT policies and procedures
Increased maintenance costs for IoT devices
The correct answer isCbecauseinsufficient IoT policies and procedurescreate the greatest security risk. In an environment with many IoT devices, governance and control are essential. Without clear policies and procedures, the organization may fail to define security requirements, ownership, configuration standards, patching responsibilities, access restrictions, monitoring expectations, and acceptable use requirements. This creates widespread unmanaged exposure across the network.
The other choices are less significant from a security-risk perspective:
A. Inadequate network bandwidthis mainly a performance issue.
B. Lack of interoperability between IoT devicesis primarily an operational or compatibility issue.
D. Increased maintenance costs for IoT devicesis a financial concern, not the greatest direct security risk.
Exact Extracts supporting the answer:
“When evaluating risks related to Internet of Things (IoT) devices used on enterprise networks the first recommendation should address IoT devices with hard-coded passwords.”
“Enterprise policies are the most influential factor in determining an enterprise’s approach to risk management.”
“The BEST way to identify IS control deficiencies is through defined control objectives.”
“The MOST important criterion when reviewing information security controls is ensuring that the controls are effectively addressing risk.”
These extracts show that IoT risk must be addressed through governance, defined requirements, and effective controls. Since policies and procedures establish how IoT devices are secured and managed, insufficient IoT policies and procedures present the greatest security risk.
===========
Which of the following is PRIMARILY responsible for providing assurance to the board of directors and senior management during the evaluation of a risk management program implementation?
Risk management
Business units
External audit
Internal audit
Internal audit provides independent assurance to the board and senior management regarding the effectiveness of risk management program implementation, consistent withGovernance and Assurance Principles.
Which of the following is the PRIMARY responsibility of a control owner?
To make risk-based decisions and own losses
To ensure implemented controls mitigate risk
To approve deviations from controls
To design controls that will eliminate risk
A control owner ' s primary responsibility is to ensure that the controls under their purview are effectively implemented and functioning as intended to mitigate associated risks. This involves regular monitoring, evaluation, and reporting on the performance of controls to maintain the organization ' s risk posture within acceptable limits.
Which of the following statements in an organization ' s current risk profile report is cause for further action by senior management?
Key performance indicator (KPI) trend data is incomplete.
New key risk indicators (KRIs) have been established.
Key performance indicators (KPIs) are outside of targets.
Key risk indicators (KRIs) are lagging.
A risk profile report is a document that summarizes the current status and trends of the risks that an organization faces, as well as the actions taken or planned to manage them1. A risk profile report is a useful tool for senior management to monitor and oversee the organization’s risk management performance and to make informed decisions and adjustments as needed2. One of the key components ofa risk profile report is the key performance indicators (KPIs), which are metrics used to measure andevaluate the achievement of the organization’s objectives and strategies3. KPIs are aligned with the organization’s risk appetite and tolerance, and they have specific targets or benchmarks that indicate the desired level of performance4. Therefore, if the KPIs are outside of targets, it means that the organization is not meeting its objectives and strategies, and that there may be gaps or issues in the risk management process or the risk response actions. This is a cause for further action by senior management, as they need to investigate the root causes of the deviation, assess the impact and implications of the underperformance, and take corrective or preventive measures to improve the situation and bringthe KPIs back to the targets. Incomplete KPI trend data, new KRIs, and lagging KRIs are not the most critical statements in a risk profile report that require further action by senior management, as they do not directly indicate a failure or a problem in the risk management performance or the achievement of the objectives and strategies. Incomplete KPI trend data means that there is missing or insufficient information on the historical or projected changes in the KPIs over time. This may affect the accuracy and reliability of the risk profile report, but it does not necessarily mean that the KPIs are outside of targets or that the objectives and strategies are not met. Senior management may need to request or obtain the complete KPI trend data, but this is not as urgent or important as addressing the KPIs that are outside of targets. New KRIs means that there are additional or revised metrics used to measure and monitor the level of risk associated with a particular process, activity, or system within the organization. This may reflect the changes or updates in the risk environment, the risk appetite and tolerance, or the risk assessment methodology. However, new KRIs do not directly indicate a failure or a problem inthe risk management performance or the achievement of the objectives and strategies. Senior management may need to review and approve the new KRIs, but this is not as urgent or important as addressing the KPIs that are outside of targets. Lagging KRIs means that there are metrics that measure and monitor the level of risk after a risk event has occurred or a risk response has been implemented. This may provide useful feedback and lessons learned for the risk management process, but it does not directly indicate a failure or a problem in the risk management performance or the achievement of the objectives and strategies. Senior management may need to analyze and evaluate the lagging KRIs, but this is not as urgent or important as addressing the KPIs that are outside of targets. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.3: Risk Reporting, pp. 201-205.
Risk mitigation procedures should include:
buying an insurance policy.
acceptance of exposures
deployment of counter measures.
enterprise architecture implementation.
Risk mitigation procedures are the actions and plans that an organization implements to reduce the likelihood and impact of identified risks. Risk mitigation procedures should include the deployment of counter measures, which are the specific controls or solutions that address the root causes or sources of the risks, and prevent or minimize the potential losses or damages. For example, a counter measure for therisk of data breach could be encrypting the data or implementing a firewall. The deployment of counter measures should be based on a cost-benefit analysis, a risk assessment, and a risk response strategy. The other options are not necessarily part of risk mitigation procedures. Buying an insurance policy is an example of risk transfer,which is a risk response strategy that shifts the responsibility or burden of the risk to another party, such as an insurer or a vendor. However, risk transfer does not eliminate or reduce the risk itself, and it may involve additional costs or conditions. Acceptance of exposures is an example of risk acceptance, which is a risk response strategy that acknowledges the existence and consequences of the risk, and decides not to take any action to change the risk situation. However, risk acceptance does not mitigate the risk, and it may require contingency plans or reserves to deal with the potential outcomes. Enterprise architecture implementation is an example of a business process or project that may involve or create risks, but it is not a risk mitigation procedure itself. Enterprise architecture is the design and structure of an organization’s IT systems, networks, and resources, and how they align with the organization’s goals and strategies. Enterprise architecture implementation may require risk management activities, such as risk identification, assessment, and response, but it is not a risk mitigation procedure itself. References = Risk IT Framework, ISACA, 2022, p. 151
Which of the following approaches would BEST help to identify relevant risk scenarios?
Engage line management in risk assessment workshops.
Escalate the situation to risk leadership.
Engage internal audit for risk assessment workshops.
Review system and process documentation.
The best approach to identify relevant risk scenarios is to engage line management in risk assessment workshops. Risk scenarios are hypothetical situations that describe how a risk event could occur and what the consequences could be1. Identifying risk scenarios can help to understand and communicate the nature and impact of the risks, and to design and evaluate the risk responses2. To identify relevant risk scenarios, it is important to involve the people who are responsible for or affected by the risks, such as the line managers. Line managers are the managers who oversee the operational activities and processes of the organization, and whoreport to the senior or executive management3. By engaging line managers in risk assessment workshops, the organization can:
Leverage the line managers’ knowledge and experience of the operational environment, the business objectives, the stakeholder expectations, and the potential threats and opportunities4.
Encourage the line managers’ participation and collaboration in the risk identification and analysis process, and foster a risk-aware culture and mindset5.
Enhance the line managers’ ownership and accountability of the risks and the risk responses, and ensure their alignment and commitment to the risk management strategy and objectives6.
The other options are not the best approaches to identify relevant risk scenarios, because:
Escalating the situation to risk leadership is not an effective or efficient way to identify risk scenarios, as it may bypass or undermine the line managers’ role and responsibility in the risk management process. Risk leadership is the function or role that provides the vision, direction, andguidance for the risk management activities and initiatives of the organization7. Escalating the situation to risk leadership may imply that the line managers are not capable or willing to identify and manage the risks, or that the risk leadership is not aware or involved in the riskmanagement process. This may create confusion, conflict, or distrust among the risk management stakeholders, and reduce the quality and credibility of the risk scenarios.
Engaging internal audit for risk assessment workshops is not a suitable or appropriate way to identify risk scenarios, as it may violate the independence and objectivity of the internal audit function. Internal audit is an independent and objective assurance and consulting activity that evaluates and improves the effectiveness of the organization’s governance, risk management, and control processes8. Engaging internal audit for risk assessment workshops may compromise the internal audit’s role and mandate, as it may create a conflict of interest or a self-review threat. Internal auditshould not be involved in the risk identification and analysis process, but rather provide assurance or advice on the adequacy and reliability of the process.
Reviewing system and process documentation is not a sufficient or comprehensive way to identify risk scenarios, as it may overlook or miss some important or emerging risks. System and process documentation are the records or artifacts that describe the structure, functions, features, and requirements of the organization’s systems and processes. Reviewing system and process documentation can help to identify some risks that are related to the design, implementation, or operation of the systems and processes, but it cannot capture all the risks that may affect the organization. Some risks may arise from external or internal factors that are not reflected or updated in the system and process documentation, such as changes in the market, technology, regulation, or stakeholder expectations.
References =
Risk Scenarios Toolkit - ISACA
Risk Scenarios Starter Pack - ISACA
Line Manager - CIO Wiki
Engaging Line Managers in Risk Management - IRM
Risk Culture - CIO Wiki
Risk Ownership - CIO Wiki
Risk Leadership - CIO Wiki
Internal Audit - CIO Wiki
[System Documentation - CIO Wiki]
Which of the following is the BEST way to ensure data is properly sanitized while in cloud storage?
Deleting the data from the file system
Cryptographically scrambling the data
Formatting the cloud storage at the block level
Degaussing the cloud storage media
The best way to ensure data is properly sanitized while in cloud storage is to cryptographically scramble the data. Cryptographic scrambling is the process of transforming data into an unreadable form using a secret key or algorithm. Cryptographic scrambling protects the data from unauthorized access, modification, or deletion, even if the cloud storage provider or a third party gains access to the data. Cryptographic scrambling also ensures that the data can be restored to its original form using the same key or algorithm, if needed. The other options are not as effective as cryptographic scrambling, because they either do not completely remove the data,or they make it impossible to recover the data. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.1, page 3-21.
An organization becomes aware that IT security failed to detect a coordinated
cyber attack on its data center. Which of the following is the BEST course of
action?
Perform a business impact analysis (BIA).
Identify compensating controls
Conduct a root cause analysis.
Revise key risk indicator (KRI) thresholds.
Risk aggregation in a complex organization will be MOST successful when:
using the same scales in assessing risk
utilizing industry benchmarks
using reliable qualitative data for risk Hems
including primarily low-level risk factors
Risk aggregation in a complex organization will be MOST successful when using the same scales in assessing risk, because it can help to ensure the consistency and comparability of the risk assessment results across different units, levels, and domains of the organization. Using the same scales in assessing risk can also help to avoid the potential errors or biases that may arise from using different scales, such as overestimating or underestimating the risk exposure, or misaligning the risk appetite and tolerance. The other options are not as important as using the same scales in assessing risk, because:
Option B: Utilizing industry benchmarks is a good way to improve the quality and validity of the risk assessment results, but it does not ensure the success of the risk aggregation, which is the process of combining and consolidating the risk assessment results into a holistic and comprehensive view of the risk profile and exposure of the organization.
Option C: Using reliable qualitative data for risk items is a useful way to capture and describe the risk items, which are the sources and causes of the risks, but it does not ensure the success of the risk aggregation, which is the process of quantifying and measuring the risk items, and their likelihood and impact on the business objectives and processes.
Option D: Including primarily low-level risk factors is a necessary way to identify and assess the risk factors, which are the characteristics and attributes of the risks, but it does not ensure the success of the risk aggregation, which is the process of prioritizing and ranking the risk factors, and their significance and relevance to the organization’s strategy and goals. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 105.
A recent audit identified high-risk issues in a business unit though a previous control self-assessment (CSA) had good results. Which of the following is the MOST likely reason for the difference?
The audit had a broader scope than the CSA.
The CSA was not sample-based.
The CSA did not test control effectiveness.
The CSA was compliance-based, while the audit was risk-based.
A compliance-based CSA focuses on ensuring that the business unit follows the policies and procedures established by the enterprise, regardless of the actual risk level or impact of the controls.
A risk-based CSA focuses on identifying and evaluating the risks that may affect the business unit’s objectives, and designing and implementing controls that are appropriate to mitigate those risks.
A compliance-based CSA may not capture all the high-risk issues that exist in a business unit, especially if they are not aligned with the enterprise’s standards or expectations.
A risk-based CSA may identify more high-risk issues than a compliance-based CSA, because it considers both internal and external factors that may affect the business unit’s performance or security.
Therefore, a difference in results between a previous control self-assessment (CSA) and an audit indicates that either one of them was not risk-based, but rather compliance-based.
The references for this answer are:
Risk IT Framework, page 9
Information Technology & Security, page 3
Risk Scenarios Starter Pack, page 1
An organization is implementing data warehousing infrastructure. Senior management is concerned about safeguarding client data security in this new environment. Which of the following should the risk practitioner recommend be done NEXT?
Ensure a role-based access control (RBAC) model is implemented.
Perform a gap analysis regarding the organization ' s client data access model.
Ensure an attribute-based access control model is implemented.
Establish new controls addressing a consistently applied data access model.
It is MOST important to the effectiveness of an IT risk management function that the associated processes are:
aligned to an industry-accepted framework.
reviewed and approved by senior management.
periodically assessed against regulatory requirements.
updated and monitored on a continuous basis.
The effectiveness of an IT risk management function depends on how well it can identify, analyze, evaluate, and treat the IT-related risks that may affect the organization’s objectives and performance. To achieve this, the IT risk management function needs to have processes that are updated and monitored on a continuous basis, so that they can capture the changes in the IT environment, the business context, the risk appetite and tolerance, and the regulatory requirements. Updating and monitoring the IT risk management processes also helps to ensure that they are consistent, reliable, and efficient, and that they provide timely and accurate information for decision making and reporting12. Aligning the IT risk management processes to an industry-accepted framework is important, but not the most important factor for the effectiveness of the function. A framework provides a common language, structure, and methodology for IT risk management, but it does not guarantee that the processes are updated and monitored on a continuous basis. A framework also needs to be customized and adapted to the specific needs and context of theorganization3. Reviewing and approving the IT risk management processes by senior management is important, but not the most important factor for the effectiveness of the function. Senior management support and endorsement are essential for establishing the tone and culture of IT risk management, as well as for allocating the necessary resources and authority for the function. However, senior management review and approval alone do not ensure that the processes are updated and monitored on a continuous basis. Senior management also need to oversee and evaluate the performance and outcomes of the IT riskmanagement function4. Periodically assessing the IT risk management processes against regulatory requirements is important, but not the most important factor for the effectiveness of the function. Regulatory compliance is one of the objectives and drivers of IT risk management, and it requires the function to adhere to the applicable laws, rules, and standards. However, regulatory requirements are not the only source of IT risk, and they may not cover all the aspects and dimensions of IT risk management.Moreover, periodic assessment may not be sufficient to capture the dynamic and evolving nature of IT risk. Therefore, the IT risk management processes need to be updated and monitored on a continuous basis, not only to meet the regulatoryrequirements, but also to address the other sources and impacts of IT risk5. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.1: Risk Response Process, pp. 121-123.
Which of the following BEST mitigates the risk of sensitive personal data leakage from a software development environment?
Tokenized personal data only in test environments
Data loss prevention tools (DLP) installed in passive mode
Anonymized personal data in non-production environments
Multi-factor authentication for access to non-production environments
Anonymizing personal data in non-production environments means replacing the real data with fictitious but realistic data that does not allow identification of the individuals. This is a good way to mitigate the risk of sensitive personal data leakage from a software development environment, as it reduces the exposure of the data to unauthorized access or misuse. Tokenizing personal data only in test environments is not sufficient, as the data may still be exposed in other non-production environments, such as development or staging. Data loss prevention tools (DLP) installed in passive mode may detect and report data leakage incidents, but they do not prevent them from happening. Multi-factor authentication for access to non-production environments may enhance the security of the access, but it does not protect the data from being leaked by authorized users or compromised by other means. References = CRISC Review Manual (Digital Version), page 226; CRISC Review Questions, Answers & Explanations Database, question 195.
Which of the following is MOST likely to cause a key risk indicator (KRI) to exceed thresholds?
Occurrences of specific events
A performance measurement
The risk tolerance level
Risk scenarios
Occurrences of specific events are the most likely to cause a key risk indicator (KRI) to exceed thresholds, as they represent the actual or potential realization of the risk. A KRI is a metric that measures the level of risk exposure and the effectiveness of risk response strategies, and it has predefined thresholds that indicate the acceptable or unacceptable risk status. When a specific event occurs that affects the risk, such as a security breach, a system failure, or a compliance violation, the KRI value may change and exceed the thresholds, triggering an alert or an action. A performance measurement, the risk tolerance level, and risk scenarios are not the most likely to cause a KRI to exceed thresholds, as they do not reflect the actual or potential occurrence of the risk, but rather the expected or desired outcome, limit, or simulation of the risk. References = [CRISC Review Manual (Digital Version)] , page 121; CRISC by Isaca Actual Free Exam Q & As, question 217.
Which of the following would MOST effectively reduce risk associated with an increase of online transactions on a retailer website?
Scalable infrastructure
A hot backup site
Transaction limits
Website activity monitoring
The most effective way to reduce risk associated with an increase of online transactions on a retailer website is to implement website activity monitoring. Website activity monitoring can help to detect and prevent fraudulent transactions, unauthorized access, data breaches, and other cyber threats that may compromise the security and integrity of the website and its data. Scalable infrastructure, a hot backup site, and transaction limits are other possible ways to reduce risk, but they are not as effective as website activity monitoring. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 7; CRISC Review Manual, 6th Edition, page 202.
Which of the following is MOST important for managing ethical risk?
Involving senior management in resolving ethical disputes
Developing metrics to trend reported ethics violations
Identifying the ethical concerns of each stakeholder
Establishing a code of conduct for employee behavior
Establishing a code of conduct for employee behavior is the most important factor for managing ethical risk, because it defines the standards and expectations for ethical conduct and decision making within the organization, and provides guidance and direction for employees to act in a responsible and ethical manner. Ethical risk is the risk of violating the moral principles or values that govern the behavior and actions of individuals or organizations, such as honesty, integrity, fairness, or respect. A code of conduct is a document that outlines the ethical principles, values, and rules that the organization and its employees must follow, and the consequences of non-compliance. A code of conduct helps to promote a positive and ethical culture within the organization, and to prevent or mitigate the ethical risks that may arise from conflicts of interest, fraud, corruption, discrimination, or other misconduct. Involving senior management in resolving ethical disputes, developing metrics to trend reported ethics violations, and identifying the ethical concerns of each stakeholder are all useful factors for managing ethical risk, but they are not the most important factor, as they do not directly address the ethical conduct and decision making of employees. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.5.1, page 67
An organization requires data owners to perform a quarterly review of all privileged users on key financial systems. What type of control does this represent?
Preventive.
Directive.
Corrective.
Detective.
The correct answer is D . A quarterly privileged-user review is a detective control because it identifies inappropriate, excessive, or unauthorized privileged access after access has been granted. The uploaded CRISC notes state that a supervisor’s review of firewall logs is an administrative control and that regularly testing information system controls helps identify design flaws, failures, and redundancies. The same principle applies here: periodic review detects whether access remains appropriate.
A preventive control stops an event before it occurs. B directs behavior through policy or guidance. C restores or fixes after an issue. The quarterly access review is primarily detective.
===========
A risk practitioner is organizing a training session lo communicate risk assessment methodologies to ensure a consistent risk view within the organization Which of the following i < the MOST important topic to cover in this training?
Applying risk appetite
Applying risk factors
Referencing risk event data
Understanding risk culture
Applying risk appetite is the most important topic to cover in a training session to communicate risk assessment methodologies. Risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. It is a key element of the risk management framework and influences the risk assessment process. Applying risk appetite helps to ensure a consistent risk view within the organization by providing a common basis for evaluating and prioritizing risks, aligning risk responses with business goals, and communicating risk information to stakeholders. The other options are not the most important topics to cover in a training session to communicate risk assessment methodologies, although they may be relevant and useful. Applying risk factors is a technique to quantify or qualify the likelihood and impact of risks based on predefined criteria or scales. Referencing risk event data is a source of information to identify and analyze risks based on historical or current incidents. Understanding risk culture is a factor that affectsthe risk behavior and attitude of the organization and its people. References = CRISC Review Manual, pages 40-411; CRISC Review Questions, Answers & Explanations Manual, page 612
A risk practitioner has determined that a key control does not meet design expectations. Which of the following should be done NEXT?
Document the finding in the risk register.
Invoke the incident response plan.
Re-evaluate key risk indicators.
Modify the design of the control.
The next step after determining that a key control does not meet design expectations is to document the finding in the risk register, because this helps to record and track the information about the identified risk, such as its description, likelihood, impact, response, and status. A key control is a control that addresses a significant risk or supports a critical business process or objective. A control design expectation is a criterion or requirement that defines how the control should operate or perform to achieve its objective. If a key control does not meet its design expectation, it means that there is a gap, weakness, or deficiency in the control that may compromise its effectiveness or efficiency, and increase the risk exposure or impact. By documenting the finding in the risk register, the risk practitioner can communicate and report the risk issue to the relevant stakeholders, such as the risk owner, the management, or the auditor, and initiate the appropriate risk response actions, such as modifying the design of the control, implementing a compensating control, or accepting the risk. The other options are not the best next steps after determining that a key control does not meet design expectations. Invoking the incident response plan is a reactive measure that is triggered when a risk event occurs or is imminent, and requires immediate action to contain, mitigate, or recover from the incident. However, in this case, the risk event has not occurred yet, and there may be time to prevent or reduce it by improving the control design. Re-evaluating key risk indicators is a monitoring activity that measures and evaluates the level and impact of risks, and provides timely signals that something may be going wrong or needs urgent attention. However, in this case, the risk practitioner has already identified the risk issue, and needs to document and address it, rather than re-evaluate it. Modifying the design of the control is a possible risk response action that may be taken to improve the control and reduce the risk, but it is not the next step after determining that the key control does not meet design expectations. The next step is to document the finding in the risk register, and then decide on the best risk response action, which may or may not be modifying the design of the control, depending on the cost-benefit analysis, the risk assessment, and the risk response strategy. References = Risk IT Framework, ISACA, 2022, p. 13
A business unit is unable to fully implement the security policy on a critical business application. Which type of process should be in place to BEST manage the related risk?
Change management
Exception management
Configuration management
Incident management
The correct answer isBbecause when a business unit cannot fully implement a required security policy, the best way to manage the related risk is through anexception managementprocess. This allows the deviation to be formally reviewed, justified, approved by the appropriate authority, documented, and monitored with awareness of the resulting residual risk.
The other options are less appropriate:
A. Change managementcontrols how changes are introduced, but it does not formally manage policy deviations.
C. Configuration managementhelps maintain technical baselines, but it does not address acceptance of noncompliance with policy.
D. Incident managementis used after an event occurs, not for governing approved deviations from policy.
Exact Extracts supporting the answer:
“In the absence of a formal policy on personal devices in the workplace the risk practitioner should recommend implementing an exception process based on appropriate approvals.”
“The primary reason for initiating a policy-exception process is the risk being justified by the benefit.”
“When an enterprise wants to quickly implement a technical solution that deviates from the company’s policies the risk practitioner should recommend a risk assessment and subsequent implementation only if residual risk is accepted.”
“The BEST way to ensure appropriate mitigation occurs on identified information systems vulnerabilities is by assigning action plans with deadlines to responsible personnel.”
These extracts directly support that a formalexception managementprocess is the best mechanism for managing risk when policy cannot be fully implemented.
===========
Which of the following would be- MOST helpful to understand the impact of a new technology system on an organization ' s current risk profile?
Hire consultants specializing m the new technology.
Review existing risk mitigation controls.
Conduct a gap analysis.
Perform a risk assessment.
A risk assessment is a process of measuring and comparing the likelihood and impact of various risk scenarios, and prioritizing them based on their significance and urgency. A risk assessmentcan help the organization to understand and document the risks that may affect its objectives and operations, and to support the decision making and planning for the risk management.
Performing a risk assessment would be the most helpful to understand the impact of a new technology system on an organization’s current risk profile, because it can help the organization to address the following questions:
What are the potential benefits and challenges of implementing the new technology system, and how do they align with the organization’s objectives and needs?
What are the existing or emerging risks that may affect the new technology system, and how do they relate to the organization’s current risk profile?
How likely and severe are the risks that may affect the new technology system, and what are the possible consequences or impacts for the organization and its stakeholders?
How can the risks that may affect the new technology system be mitigated or prevented, and what are the available or feasible options or solutions?
Performing a risk assessment can help the organization to understand the impact of the new technology system on its current risk profile by providing the following benefits:
It can enable the comparison and evaluation of the current and desired state and performance of the organization’s risk management function, and to identify and quantify the gaps or opportunities for improvement.
It can provide useful references and benchmarks for the alignment and integration of the new technology system with the organization’s risk management function, and for the compliance with the organization’s risk policies and standards.
It can support the implementation and monitoring of the new technology system, and for the allocation and optimization of the resources, time, and budget for the new technology system.
The other options are not the most helpful to understand the impact of a new technology system on an organization’s current risk profile, because they do not provide the same level of detail and insight that performing a risk assessment provides, and they may not be specific or applicable to the organization’s objectives and needs.
Hiring consultants specializing in the new technology means engaging or contracting external experts or professionals that have the skills and knowledge on the new technology system, and that can provide advice or guidance on the implementation and management of the new technology system. Hiring consultants specializing in the new technology can help the organization to enhance its competence and performance on the new technology system, but it is not the most helpful, because it does not measure and compare the likelihood and impact of the risks that may affect the new technology system, and it may not be relevant or appropriate for the organization’s current risk profile.
Reviewing existing risk mitigation controls means examining and evaluating the adequacy and effectiveness of the controls or countermeasures that are intended to reduce or eliminate the risksthat may affect the organization’s objectives and operations. Reviewing existing risk mitigation controls can help the organization to improve and optimize its risk management function, but it is not the most helpful, because it does not identify and prioritize the risks that may affect the newtechnology system, and it may not cover all the relevant or significant risks that may affect the new technology system.
Conducting a gap analysis means comparing and contrasting the current and desired state and performance of the organization’s objectives and operations, and identifying and quantifying the gaps or differences that need to be addressed or corrected. Conducting a gap analysis can help the organization to identify and document its improvement needs and opportunities, but it is not the most helpful, because it does not measure and compare the likelihood and impact of the risks that may affect the new technology system, and it may not be aligned or integrated with the organization’s current risk profile. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 208
CRISC Practice Quiz and Exam Prep
Which of the following scenarios presents the GREATEST risk of noncompliance with data privacy best practices?
Making data available to a larger audience of customers
Data not being disposed according to the retention policy
Personal data not being de-identified properly
Data being used for purposes the data subjects have not opted into
Data Privacy Principles:
Consent and Purpose Limitation: According to data privacy regulations like GDPR, data subjects must provide explicit consent for specific purposes. Using data for purposes beyond what was consented to violates these principles, posing significant compliance risks.
Transparency and Accountability: Organizations must be transparent about how they use personal data and ensure accountability in data processing. Using data without consent undermines this transparency and accountability.
Greatest Risk of Noncompliance:
Legal and Regulatory Risks: Using personal data without consent can lead to severe penalties under laws like GDPR and CPRA. These laws impose heavy fines for noncompliance, making this scenario the highest risk.
Reputational Damage: Unauthorized use of personal data can severely damage an organization’s reputation, leading to loss of customer trust and potential financial losses.
Operational Impact: Ensuring compliance with consent requirements is fundamental to an organization ' s data processing activities. Failure to do so can disrupt business operations and necessitate significant remediation efforts.
Comparison with Other Options:
Making Data Available to a Larger Audience of Customers: While potentially risky, this does not inherently violate data privacy principles if done within consented uses.
Data Not Being Disposed According to the Retention Policy: This poses risks related to data minimization and retention principles but is less severe than unauthorized data use.
Personal Data Not Being De-identified Properly: This is a significant risk but typically involves fewer direct legal and regulatory implications compared to using data without consent.
Which of the following is the PRIMARY objective of maintaining an information asset inventory?
To provide input to business impact analyses (BIAs)
To protect information assets
To facilitate risk assessments
To manage information asset licensing
An information asset inventory is a list of all the information assets that an organization owns or uses. It includes information such as the asset name, description, owner, location, classification,value, and dependencies. The primary objective of maintaining an information asset inventory is to provide input to business impact analyses (BIAs), which are used to identify the criticality and recovery priorities of information assets in the event of a disruption. By having an updated and accurate information asset inventory, an organization can ensure that the BIAs reflect the current state and needs of the business processes that rely on the information assets. References = CRISC Review Manual, 7th Edition, page 74.
Which of the following is the BEST recommendation of a risk practitioner for an organization that recently changed its organizational structure?
Communicate the new risk profile.
Implement a new risk assessment process.
Revalidate the corporate risk appetite.
Review and adjust key risk indicators (KRIs).
Communicating the new risk profile is the best recommendation for a risk practitioner for an organization that recently changed its organizational structure, because it helps to inform and align the stakeholders on the current state of risks and their implications for the organization’s objectives and strategy. A risk profile is a summary of the key risks that an organization faces, along with their likelihood, impact, and response strategies. An organizational structure is the way that an organization arranges its people, roles, and responsibilities to achieve its goals and deliver its value proposition. A change in the organizational structure may affect the risk profile, as it may introduce new sources or types of risk, or alter the existing risk levels orresponses. Therefore, communicating the new risk profile is the best recommendation, as it helps to ensure that the stakeholders are aware of and prepared for the changes and challenges that the new organizational structure may bring. Implementing a new risk assessment process, revalidating the corporate risk appetite, and reviewing and adjusting key risk indicators (KRIs) are all important tasks to perform after communicating the new risk profile, but they are not the best recommendation, as they depend on the communication and understanding of the new risk profile. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.3, page 91
Which of the following is the MOST appropriate action when a tolerance threshold is exceeded?
Communicate potential impact to decision makers.
Research the root cause of similar incidents.
Verify the response plan is adequate.
Increase human resources to respond in the interim.
The most appropriate action when a tolerance threshold is exceeded is to communicate the potential impact to the decision makers. A tolerance threshold is the acceptable level of variation or deviation from the expected or planned performance or outcome of a risk response. When a tolerance threshold is exceeded, it means that the risk response is not effective or efficient enough to reduce the risk to an acceptable level, and that the enterprise is exposed to unacceptable levels of risk that could impair its ability to achieve its objectives. Therefore, the potential impact of the risk should be communicated to the decision makers, such as senior management, risk owners, or risk committee, who have the authority and responsibility to decide on the appropriate actions to address the risk situation. Communicating the potential impact can help to raise the awareness and urgency of the risk issue, and to facilitate the risk-based decision making process. Researching the root cause of similar incidents, verifying the response plan isadequate, and increasing human resources to respond in the interim are not as appropriate as communicating the potential impact, as they do not address the primary need of informing and involving the decision makers, and may not be feasible or effective in resolving the risk issue. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 41.
The risk associated with a high-risk vulnerability in an application is owned by the:
security department.
business unit
vendor.
IT department.
A high-risk vulnerability in an application is a system flaw or weakness in the application’s code that can be exploited by a malicious actor, potentially leading to a security breach. The risk associated with a high-risk vulnerability in an application is the possibility and impact of such a breach occurring. The risk owner of a high-risk vulnerability in an application is the person or entity who has the authority and responsibility for managing the risk. The risk owner should be able to define the risk appetite, assess the risk level, select and implement the risk response, monitor and report the risk status, and ensure the risk alignment with the business objectives and strategy. The risk owner of a high-risk vulnerability in an application is the business unit, which is the organizational unit that operates the application and derives value from it. The businessunit understands the business needs and expectations of the application, and the potential consequences of a security breach. The business unit also has the resources and incentives to address the risk effectively and efficiently. Therefore, the business unit is the most appropriate risk owner of a high-risk vulnerability in an application. References = Why Assigning a Risk Owner is Important and How to Do It Right, CRISC 351-400 topic3, Foundations of Project Management : Week 2.
Which of the following would BEST mitigate an identified risk scenario?
Conducting awareness training
Executing a risk response plan
Establishing an organization ' s risk tolerance
Performing periodic audits
The best way to mitigate an identified risk scenario is to execute a risk response plan. A risk response plan is a document that describes the actions and resources that are needed to address the risk scenario. A risk response plan can include one or more of the following strategies: avoid, transfer, mitigate, accept, or exploit. By executing a risk response plan, the organization can reduce the likelihood and/or impact of the risk scenario, or take advantage of the opportunities that the risk scenario may present. The other options are not as effective as executing a riskresponse plan, as they are related to the awareness, assessment, or monitoring of the risk scenario, not the actual treatment of the risk scenario. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.2: IT Risk Response Options, page 133.
Sensitive data has been lost after an employee inadvertently removed a file from the premises, in violation of organizational policy. Which of the following controls MOST likely failed?
Background checks
Awareness training
User access
Policy management
Awareness training is the most likely control that failed in this scenario, as it is designed to educate employees on the proper handling and protection of sensitive data, and the consequences of violating the organizational policy. Awareness training can help to prevent or reduce the occurrence of human errors, such as inadvertently removing a file from the premises, that may result in data loss or breach. The other options are not the most likely controls that failed, as they are either not directly related to the scenario or not sufficient to prevent the incident. Background checks are used to verify the identity, qualifications, and trustworthiness of potential or current employees, but they do not ensure that employees will always follow the policy or avoidmistakes. User access is used to restrict the access to information systems or resources based on the identity, role, or credentials of the user, but it does not prevent the user from copying or removing the data once they have access. Policy management is used to create, communicate, and enforce the organizational policy, but it does not ensure that employees will understand orcomply with the policy. References = Sensitive Data Essentials – The Lifecycle Of A Sensitive File; Personal data breach examples | ICO; How do I prevent staff accidentally sending personal information … - GCIT; 10 Ways to Protect Sensitive Employee Information; My personal data has been lost after a breach, what are my rights …
Which of the following is the PRIMARY reason for sharing risk assessment reports with senior stakeholders?
To support decision-making for risk response
To hold risk owners accountable for risk action plans
To secure resourcing for risk treatment efforts
To enable senior management to compile a risk profile
The primary reason for sharing risk assessment reports with senior stakeholders is to support decision-making for risk response. Risk assessment reports are documents that summarize the results of the risk assessment process, such as the risk sources, causes, impacts, likelihood, and levels. Risk assessment reports also provide recommendations for risk response options, such as avoiding, reducing, transferring, or accepting the risk. Sharing risk assessment reports with senior stakeholders helps to inform them of the current risk situation, and to solicit their input, feedback, or approval for the risk response actions. The other options are not the primary reason for sharing risk assessment reports, although they may be secondary reasons or outcomes. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 4-13.
Which of the following BEST indicates the condition of a risk management program?
Number of risk register entries
Number of controls
Level of financial support
Amount of residual risk
The best indicator of the condition of a risk management program is the amount of residual risk. Residual risk is the risk that remains after the implementation of risk responses. Residual risk reflects the effectiveness and efficiency of the risk management program in reducing the risk exposure to an acceptable level, and in aligning the risk profile with the risk appetite and tolerance of the enterprise. A low amount of residual risk indicates that the risk managementprogram is performing well, and that the controls are adequate and appropriate. A high amount of residual risk indicates that the risk management program is not functioning properly, and that the controls are insufficient or ineffective. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.2.2, page 191
An organization ' s stakeholders are unable to agree on appropriate risk responses. Which of the following would be the BEST course of action?
Escalate to senior management.
Identify a risk transfer option.
Reassess risk scenarios.
Benchmark with similar industries.
Escalating to senior management is the best course of action when an organization’s stakeholders are unable to agree on appropriate risk responses. This is because senior management has the authority and responsibility to make strategic decisions and resolve conflicts regarding risk management. Senior management can also provide guidance and direction on the risk appetite, tolerance, and criteria for the organization, as well as allocate resources and assign roles and responsibilities for risk response. According to the CRISC Review Manual 2022, one of the key risk response techniques is to escalate the risk to senior management when the risk exceeds the acceptable level or when there is a disagreement on the risk response1. According to the CRISC Review Questions, Answers & Explanations Manual 2022, escalating to senior management is the correct answer to this question2.
Identifying a risk transfer option, reassessing risk scenarios, and benchmarking with similar industries are not the best courses of action when an organization’s stakeholders are unable to agree on appropriate risk responses. These are possible actions that can be taken as part of the risk response process, but they do not address the underlying issue of stakeholder disagreement. Identifying a risk transfer option can help reduce or share the risk with a third party, such as an insurance company or a vendor, but it may not be suitable or acceptable for all types of risks or stakeholders. Reassessing risk scenarios can help update the risk analysis and evaluation, but it may not change the risk level or the risk response options. Benchmarking with similar industries can help compare the risk performance and practices of the organization with its peers, but it may not reflect the organization’s specific needs or risks.
Which of the following is MOST important to understand when determining an appropriate risk assessment approach?
Complexity of the IT infrastructure
Value of information assets
Management culture
Threats and vulnerabilities
When determining an appropriate risk assessment approach, the most important factor to understand is the value of information assets. This is because the value of information assets determines the potential impact of risks and the level of protection required. The value of information assets can be assessed based on their confidentiality, integrity, availability, and relevance to the business objectives and processes. A risk assessment approach should be aligned with the value of information assets and the risk appetite of the organization. The other options are not the most important factors to understand when determining a risk assessment approach, although they may influence the choice of methods and tools. The complexity of the IT infrastructure may affect the scope and depth of the risk assessment, but it does not indicate the level of risk or the priority of risk management. The management culture may affect the risk tolerance and the risk communication, but it does not reflect the value of information assets or the risk exposure. The threats and vulnerabilities may affect the likelihood and severity of risks, but they do not measure the value of information assets or the risk acceptance. References = CRISC Review Manual, pages 38-391; CRISC Review Questions, Answers & Explanations Manual, page 582
Who is PRIMARILY accountable for identifying risk on a daily basis and ensuring adherence to the organization ' s policies?
Third line of defense
Line of defense subject matter experts
Second line of defense
First line of defense
Which of the following is MOST important when defining controls?
Identifying monitoring mechanisms
Including them in the risk register
Aligning them with business objectives
Prototyping compensating controls
According to the CRISC Review Manual1, controls are the policies, procedures, practices, and organizational structures that are designed and implemented to manage risk. The most important factor when defining controls is to align them with the business objectives, as this helps to ensure that the controls support the achievement of the organization’s strategy, goals, and values. Aligning controls with business objectives also helps to optimize the benefits and costs of controls, and to prioritize and allocate resources for control implementation and maintenance. References = CRISC Review Manual1, page 202.
From a risk management perspective, which of the following is the PRIMARY benefit of using automated system configuration validation tools?
Residual risk is reduced.
Staff costs are reduced.
Operational costs are reduced.
Inherent risk is reduced.
From a risk management perspective, the primary benefit of using automated system configuration validation tools is that they reduce the inherent risk, which is the risk that exists before any controls are applied. Automated system configuration validation tools can help to ensure that the system settings are consistent, compliant, and secure, and that they match the predefined standards and policies. This can reduce the likelihood and impact of errors, misconfigurations, vulnerabilities, or deviations that may compromise the system’s functionality, performance, or integrity. The other options are not the primary benefits of using automated system configuration validation tools, although they may be secondary benefits or outcomes of doing so. Residual risk is the risk that remains after the controls are applied, and it may not be directly affected by the automated system configuration validation tools. Staff costs and operational costs are related to the efficiency and economy of the system configuration process, but they are not the main risk management objectives. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk Response, page 150.
Which of the following should be the MAIN consideration when validating an organization ' s risk appetite?
Comparison against regulations
Maturity of the risk culture
Capacity to withstand loss
Cost of risk mitigation options
According to the Gaining the competitive edge – measuring and assessing an organization’s risk culture article, risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Risk appetite should be aligned with the organization’s strategy, goals, and values, and should reflect the organization’s risk culture and capabilities. One of the main considerations when validating an organization’s risk appetite is the capacity to withstand loss, which is the ability of the organization to absorb the impact of adverse events without jeopardizing its viability or reputation. The capacity to withstand loss depends on various factors, such as the financial strength, the operational resilience, the governance structure, and the stakeholder expectations of the organization. By assessing the capacity to withstand loss, the organization can determine if its risk appetite is realistic and appropriate, or if it needs to be adjusted to match its risk profile and environment. References = Gaining the competitive edge – measuring and assessing an organization’s risk culture
Mitigating technology risk to acceptable levels should be based PRIMARILY upon:
organizational risk appetite.
business sector best practices.
business process requirements.
availability of automated solutions
Mitigating technology risk to acceptable levels means that the organization implements and maintains appropriate controls to reduce the likelihood and impact of potential threats or losses that may arise from the use of technology, such as IT systems, applications, networks, devices, etc.
The primary factor that should guide the mitigation of technology risk is the organizational risk appetite. This means that the organization defines and communicates the amount and type of risk that it is willing to accept or pursue in order to achieve its objectives and strategy.
The organizational risk appetite helps to determine the risk tolerance and thresholds for different risk categories and scenarios, prioritize the risks, select the most suitable risk responses, allocate the resources and budget for risk management, and monitor and report the risk performance and outcomes.
The other options are not the primary factors that should guide the mitigation of technology risk. They are either secondary or not essential for risk management.
The references for this answer are:
Risk IT Framework, page 25
Information Technology & Security, page 19
Risk Scenarios Starter Pack, page 17
Effective risk communication BEST benefits an organization by:
helping personnel make better-informed decisions
assisting the development of a risk register.
improving the effectiveness of IT controls.
increasing participation in the risk assessment process.
Effective risk communication best benefits an organization by helping personnel make better-informed decisions. Risk communication is the process of exchanging information and opinions among stakeholders about the nature, magnitude, significance, or control of a risk. By communicating risk information clearly and consistently, the organization can enhance the understanding and awareness of the risk, and enable the personnel to make decisions that are aligned with the risk appetite and objectives of the organization. Assisting the development of a risk register, improving the effectiveness of IT controls, and increasing participation in the risk assessment process are other possible benefits, but they are not as important as helping personnel make better-informed decisions. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 12; CRISC Review Manual, 6th Edition, page 215.
Of the following, who is responsible for approval when a change in an application system is ready for release to production?
Information security officer
IT risk manager
Business owner
Chief risk officer (CRO)
The business owner is the person who is responsible for approval when a change in an application system is ready for release to production. The business owner is the person who has the authority and accountability for the business process or function that is supported by the application system. The business owner should approve the change to ensure that it meets the business requirements, objectives, and expectations, and that it does not introduce any adverse impacts or risks to the business operations. The information security officer, the IT risk manager, and the chief risk officer (CRO) are not responsible for the approval of the change, although they may provide input, feedback, or oversight. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.4.1, page 3-32.
Which of the following BEST indicates that additional or improved controls ate needed m the environment?
Management, has decreased organisational risk appetite
The risk register and portfolio do not include all risk scenarios
merging risk scenarios have been identified
Risk events and losses exceed risk tolerance
The best indicator that additional or improved controls are needed in the environment is when risk events and losses exceed risk tolerance. Risk tolerance is the acceptable level of variation in performance or outcomes relative to the achievement of objectives. Risk events and losses are the negative consequences of risk that have occurred or are expected to occur. When risk events and losses exceed risk tolerance, it means that the existing controls are not sufficient or effective to prevent or mitigate the risk, and that the organization is exposed to unacceptable levels of risk that could impair its ability to achieve its objectives. Therefore, additional or improved controls are needed to reduce the risk to an acceptable level. Management decreasing organizational risk appetite, the risk register and portfolio not including all risk scenarios, and emerging risk scenarios being identified are not as clear and direct indicators that additional or improved controls are needed in the environment, as they do not necessarily reflect the actual performance or outcomes of the risk management process. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 41.
Which of the following should be of GREATEST concern when reviewing the results of an independent control assessment to determine the effectiveness of a vendor ' s control environment?
The report was provided directly from the vendor.
The risk associated with multiple control gaps was accepted.
The control owners disagreed with the auditor ' s recommendations.
The controls had recurring noncompliance.
The most concerning issue when reviewing the results of an independent control assessment to determine the effectiveness of a vendor’s control environment is that the controls had recurring noncompliance. This indicates that the vendor’s controls are not operating as intended or designed, and that the vendor is not taking corrective actions to address the control deficiencies. This can increase the risk exposure and liability for the organization that outsources the service or function to the vendor. The report being provideddirectly from the vendor, the risk associated with multiple control gaps being accepted, and the control owners disagreeing with the auditor’s recommendations are other possible issues, but they are not as critical as the recurring noncompliance. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 11; CRISC Review Manual, 6th Edition, page 144.
To communicate the risk associated with IT in business terms, which of the following MUST be defined?
Compliance objectives
Risk appetite of the organization
Organizational objectives
Inherent and residual risk
According to the CRISC Review Manual, risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Risk appetite is a key factor in communicating the risk associated with IT in business terms, because it helps to align the IT risk management with the business strategy and goals. Risk appetite also helps to define the risk tolerance and thresholds, which are the acceptable levels of variation around the objectives. The other options are not the correct answers, because they are not essential for communicating the risk associated with IT in business terms. Compliance objectives are the objectives that an organization must achieve to comply with the applicable laws, regulations, standards, andcontracts. Organizational objectives are the objectives that an organization sets to achieve its mission, vision, and values. Inherent and residual risk are the risk levels before and after applying the risk responses, respectively. References = CRISC Review Manual, 7th Edition, Chapter 2, Section 2.1.1, page 66.
Which of the following is the PRIMARY reason to ensure policies and standards are properly documented within the risk management process?
It facilitates the use of a framework for risk management.
It establishes a means for senior management to formally approve risk practices.
It encourages risk-based decision making for stakeholders.
It provides a basis for benchmarking against industry standards.
Policies and standards are important components of the risk management process, as they define the objectives, expectations, and requirements for managing risk within the organization. Policies and standards are also the means by which senior management formally approves and communicates the risk practices to the stakeholders, ensuring that the risk management process is aligned with the organizational strategy, culture, and values. Policies and standards also provide the authority and accountability for the risk management roles and responsibilities, as well as the criteria and metrics for measuring and reporting risk performance.
Which of the following would provide the MOST helpful input to develop risk scenarios associated with hosting an organization ' s key IT applications in a cloud environment?
Reviewing the results of independent audits
Performing a site visit to the cloud provider ' s data center
Performing a due diligence review
Conducting a risk workshop with key stakeholders
The most helpful input to develop risk scenarios associated with hosting an organization’s key IT applications in a cloud environment is conducting a risk workshop with key stakeholders. A risk workshop is a facilitated session that involves brainstorming, discussing, and analyzing the potential risks and opportunities related to a specific topic or project. A risk workshop helps to identify and prioritize the most relevant and significant risk scenarios, as well as to explore the possible causes, impacts, and responses. A risk workshop also helps to engage and align the key stakeholders, such as the business owners, IT managers, cloud providers, and risk experts, and to leverage their knowledge, experience, and perspectives. The other options are not as helpful as conducting a risk workshop, although they may provide some inputor information for the risk scenario development. Reviewing the results of independent audits, performing a site visit to the cloud provider’s data center, and performing a due diligence review are all activities that can help to assess the current state and performance of the cloud environment, but they do not necessarily generate or evaluate the risk scenarios. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 4-13.
Which of the following is the PRIMARY risk management responsibility of the second line in the three lines model?
Applying risk treatments
Implementing internal controls
Monitoring risk responses
Providing assurance of control effectiveness
Thesecond line of defensein the Three Lines Model plays arisk oversightandmonitoringrole rather than operational execution.
According to ISACA’s CRISC framework:
Thefirst line(operational management) owns and manages risk and implements controls.
Thesecond line(risk and compliance functions) providesrisk oversight, guidance, and monitoringof risk responses and ensures adherence to policies and frameworks.
Thethird line(internal audit) providesindependent assuranceregarding the overall effectiveness of controls.
Therefore, theprimary responsibilityof the second line is tomonitor and evaluate risk responsesimplemented by the first line to ensure they are effective and aligned with enterprise risk appetite.
Supporting Extract:
CRISC study notes (Slides 127–134) state:
“The most significant benefit of using the three lines of defense model is that it clarifies essential roles of key stakeholders. The second line of defense provides oversight and monitoring of risk and control activities.”
Hence, the correct answer isC. Monitoring risk responses.
Which of the following BEST mitigates reputational risk associated with disinformation campaigns against an organization?
Monitoring digital platforms that disseminate inaccurate or misleading news stories
Engaging public relations personnel to debunk false stories and publications
Restricting the use of social media on corporate networks during specific hours
Providing awareness training to understand and manage these types of attacks
Understanding Reputational Risk:
Reputational risk arises from negative public perception, which can be fueled by disinformation campaigns. These campaigns spread false or misleading information about an organization, potentially damaging its reputation.
Mitigating Reputational Risk:
The best way to mitigate this risk is to actively counteract false information and restore public trust. This involves debunking false stories and correcting misinformation promptly and effectively.
Role of Public Relations:
Engaging public relations (PR) personnel is crucial in managing the organization ' s reputation. PR professionals are skilled in crafting messages, dealing with media, and using communication strategies to address and correct false narratives.
PR personnel can issue press releases, organize press conferences, and leverage social media to reach a wide audience, ensuring the correct information is disseminated.
Monitoring and Awareness Training:
While monitoring digital platforms and providing awareness training are important, they are more preventive measures. Monitoring helps in early detection, and training aids in internalmanagement of such risks. However, they do not actively counteract the false information once it is in the public domain.
Restricting Social Media:
Restricting social media usage on corporate networks does not address the core issue of disinformation campaigns. It may reduce internal risks but does not mitigate external reputational damage.
References:
The CRISC Review Manual discusses strategies for managing reputational risk and highlights the importance of proactive communication and public relations efforts (CRISC Review Manual, Chapter 1: Governance, Section 1.3.4 The Value of Risk Communication).
The BEST way to obtain senior management support for investment in a control implementation would be to articulate the reduction in:
detected incidents.
residual risk.
vulnerabilities.
inherent risk.
Residual risk is the risk that remains after applying risk responses, such as avoidance, mitigation, transfer, or acceptance. It represents the level of exposure that the organisation is willing to tolerate or assume. Residual risk should be aligned with the organisation’s risk appetite and risk tolerance, which are determined by senior management. Therefore, the best way to obtain senior management support for investment in a control implementation would be to articulate the reduction in residual risk that the control would achieve. This would demonstrate how the control would help the organisation meet its riskobjectives and reduce the likelihood or impact of adverse events. References = ISACA CRISC Review Manual, 7th Edition, Chapter 1, Section 1.3.2, page 25.
An organization has initiated a project to launch an IT-based service to customers and take advantage of being the first to market. Which of the following should be of GREATEST concern to senior management?
More time has been allotted for testing.
The project is likely to deliver the product late.
A new project manager is handling the project.
The cost of the project will exceed the allotted budget.
Being the first to market is a competitive advantage that can help an organization gain market share, customer loyalty, and brand recognition. However, this advantage can be lost if the projectis delayed and the competitors catch up or surpass the organization. Therefore, the project delivery time is of greatest concern to senior management, as it directly affects the strategic objective of the project. The other options are less critical, as they can be managed or mitigated by the project team. More time for testing can improve the quality and reliability of the product, a new project manager can bring fresh ideas and perspectives, and the cost overrun can be justified by the expected benefits and revenues of the product. References = Project Initiation: The First Step to Project Management [2023] • Asana, 12 Steps to Initiate and Plan a Successful Project
Which of the following is a KEY consideration for a risk practitioner to communicate to senior management evaluating the introduction of artificial intelligence (Al) solutions into the organization?
Al requires entirely new risk management processes.
Al potentially introduces new types of risk.
Al will result in changes to business processes.
Third-party Al solutions increase regulatory obligations.
Artificial intelligence (AI) solutions can offer significant benefits to an organization, such as improved efficiency, accuracy, and innovation. However, AI also poses new challenges and risks that need to be considered and addressed by senior management. Some of these risks include:
Ethical and social risks: AI solutions may have unintended or undesirable impacts on human values, rights, and behaviors, such as privacy, fairness, accountability, and transparency. For example, AI systems may exhibit bias, discrimination, or manipulation, or may infringe on personal data or autonomy.
Technical and operational risks: AI solutions may have vulnerabilities, errors, or failures that affect their performance, reliability, or security. For example, AI systems may be subject to hacking, tampering, or misuse, or may malfunction or produce inaccurate or harmful outcomes.
Legal and regulatory risks: AI solutions may have unclear or conflicting legal or regulatory implications or obligations, such as liability, compliance, or governance. For example, AI systems may raise questions about ownership, responsibility, or accountability, or may violate existing laws or regulations, or create new ones.
Therefore, a risk practitioner should communicate to senior management that AI potentially introduces new types of risk that need to be identified, assessed, and managed in alignment with the organization’s objectives, values, and risk appetite. References = ISACA CRISC Review Manual, 7th Edition, Chapter 3, Section 3.2.2, page 113.
How should an organization approach the retention of data that is no longer needed for business operations?
Data should be retained for a reasonable period of time in case of system rollback.
Data should be destroyed or retained on the basis of a cost-benefit analysis.
Data should be retained based on regulatory requirements.
Data should be destroyed to avoid any risk exposure.
Regulatory and legal compliance dictate data retention requirements, making them the primary basis for retention decisions.
The MAIN purpose of selecting a risk response is to.
ensure compliance with local regulatory requirements
demonstrate the effectiveness of risk management practices.
ensure organizational awareness of the risk level
mitigate the residual risk to be within tolerance
The main purpose of selecting a risk response is to mitigate the residual risk to be within tolerance. Residual risk is the risk that remains after applying a risk response. Risk tolerance is the amount and type of risk that an organization is willing to accept in order to achieve its objectives. Risk response is the process of selecting and implementing actions to address risk. The goal of risk response is to reduce the residual risk to a level that is acceptable to the organization and its stakeholders. The other options are not the main purpose of selecting a risk response, although they may be secondary benefits or outcomes. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-23.
Which of the following provides the MOST up-to-date information about the effectiveness of an organization ' s overall IT control environment?
Key performance indicators (KPIs)
Risk heat maps
Internal audit findings
Periodic penetration testing
The IT control environment is the set of standards, processes, and structures that provide the basis for carrying out IT internal control across the organization1. The IT control environment comprises the IT governance, IT policies and procedures, IT organizational structure, IT roles and responsibilities, IT competencies and training, and IT culture and ethics2. The effectiveness of the IT control environment can be measured by how well it supports the achievement of the organization’s IT objectives, such as IT reliability, security, compliance, and performance3.
One of the best ways to provide the most up-to-date information about the effectiveness of the organization’s overall IT control environment is to perform periodic penetrationtesting. Penetration testing is the process of simulating real-world cyberattacks on the organization’s IT systems, networks, and applications, to identify and exploit any vulnerabilities, weaknesses, or gaps in the IT control environment4. Penetration testing can help to:
Evaluate the current state and maturity of the IT control environment and its alignment with the organization’s risk appetite and tolerance
Detect and prioritize the most critical and urgent IT risks and threats that may compromise the organization’s IT objectives or assets
Test and validate the effectiveness and efficiency of the existing IT controls and their ability to prevent, detect, or respond to cyberattacks
Provide recommendations and feedback for improving the IT control environment and enhancing the IT security posture and resilience of the organization
References = COSO – Control Environment - Deloitte, How to use COSO to assess IT controls - Journal of Accountancy, What is Penetration Testing?, [Penetration Testing: A Guide for Business Leaders]
As part of an overall IT risk management plan, an IT risk register BEST helps management:
align IT processes with business objectives.
communicate the enterprise risk management policy.
stay current with existing control status.
understand the organizational risk profile.
An IT risk register is a document that is used as a risk management tool to identify, analyze, and track the potential risks related to the use of information technology within an organization. An IT risk register helps management to understand the organizational risk profile, which is a comprehensive and structured representation of the risks that the organization faces. The risk profile helps the organization to understand its risk exposure, appetite, and tolerance, and to align its risk management strategy with its business objectives and context. The risk register is an essential input for creating and updating the risk profile, as it provides the data and analysis ofthe risks that need to be prioritized and addressed12. The other options are not the best answers, as they are either not directly shown or derived from the IT risk register. Aligning IT processes with business objectives is a goal of IT governance, which may be influenced by the IT risk register, but not solely determined by it. Communicating the enterprise risk management policy is a responsibility of the senior management and the board of directors, which may use the IT risk register as a reference, but not as the main source. Staying current with existing control status is a function of IT audit and assurance, which may rely on the IT risk register as a basis, but not as the only evidence. References = Risk Register: A Project Manager’s Guide with Examples [2023] • Asana; Complete Guide to IT Risk Management | CompTIA
Which of the following is MOST important for an organization to continuously manage after implementing a Zero Trust security model?
Privileged user access reviews
Integration with existing security protocols
Policy enforcement inconsistencies
Network segmentation errors
In aZero Trustmodel, access is never implicitly trusted and must be continuously verified — makingprivileged access reviewcritical.
ISACA CRISC guidance:
“Under the Zero Trust model, continuous validation and review of privileged user access is essential to prevent privilege escalation and insider threats.”
Integration and segmentation are design concerns;privileged access managementis the ongoing control requirement.
Thus,Ais correct.
CRISC Reference:Domain 4 – Risk and Control Monitoring and Reporting, Topic: Zero Trust and Continuous Authorization.
Senior leadership has set guidelines for the integration of a new acquisition. The guidelines allow for a variation in the level of risk-taking. The variation indicates which of the following risk management concepts?
Risk tolerance
Risk appetite
Risk sensitivity
Risk velocity
Risk tolerance refers to the acceptable level of variation in outcomes related to specific risks that an organization is willing to withstand. It defines the boundaries within which the organization can operate safely and is often set by senior leadership to guide decision-making processes. In the context of integrating a new acquisition, allowing for variation in the level of risk-taking directly pertains to the organization ' s risk tolerance.
Which of the following is the MOST important requirement when implementing a data loss prevention (DLP) system?
Identifying users who have access
Selecting an encryption solution
Defining the data retention period
Determining the value of data
Determining the value of data is essential when implementing a DLP system. Understanding data value helps prioritize protection efforts, allocate resources effectively, and ensure that critical information assets are adequately safeguarded against loss or unauthorized access.
An organization wants to develop a strategy to mitigate the risk associated with unethical actions by stakeholders. Which of the following should be done FIRST?
Provide incentives for whistleblowers to report unethical actions.
Create a policy regarding ethical behavior.
Communicate sanctions and penalties for unethical actions.
Develop company-wide training on business ethics.
The correct answer is B because the first step is to define expected ethical behavior. A policy establishes the standard, responsibilities, required conduct, and prohibited conduct. After the policy exists, the organization can train employees, communicate sanctions, and establish reporting or incentive mechanisms. ISACA describes policies as documents that formally communicate required and prohibited activities and behaviors to guide enterprise operations and compliance requirements.
This is also consistent with ISACA’s Code of Professional Ethics, which guides professional and personal conduct, requires high standards of conduct and character, and states that failure to comply can lead to investigation and disciplinary measures. The uploaded CRISC notes further support that developing and practicing ethical behavior contributes most to building risk culture and that ethics awareness training supports professional ethics after expectations are established.
A, C, and D are useful supporting activities, but they should follow the policy. Training cannot be effective until the expected ethical behavior is defined, and sanctions or incentives should be based on the established ethics policy.
To reduce the risk introduced when conducting penetration tests, the BEST mitigating control would be to:
require the vendor to sign a nondisclosure agreement
clearly define the project scope.
perform background checks on the vendor.
notify network administrators before testing
According to the CRISC Review Manual, notifying network administrators before testing is the best mitigating control to reduce the risk introduced when conducting penetration tests, because it helps to avoid any disruption or damage to the network services and systems. Penetration testing is a technique that simulates an attack on the network to identify and exploit the vulnerabilities and weaknesses. Notifying network administrators before testing allows them to prepare for the test, monitor the test activities, and respond to any incidents or issues that may arise during the test. The other options are not the best mitigating controls, because they do not address the risk of network disruption or damage. Requiring the vendor to sign a nondisclosure agreement is a legal measure that protects the confidentiality of the network information, but it does not prevent the vendor from causing any harm to the network. Clearly defining the project scope is a planning activity that sets the boundaries and objectives of the test, but it does not ensure the safety and availability of the network. Performing background checks on the vendor is a due diligence activity that verifies the vendor’s credentials and reputation, but it does not guarantee the vendor’s performance or behavior. References = CRISC Review Manual, 7th Edition, Chapter 4, Section 4.2.2, page 181.
Within risk management, simulations are MOST useful during risk:
Monitoring.
Answer:Profiling.
Answer:Reporting.
Answer:Analysis.
Answer:D
The correct answer is D . Simulations are used during risk analysis to estimate possible outcomes, likelihood, impact, and uncertainty. The uploaded CRISC notes state that deriving likelihood and impact of risk scenarios through statistical methods is quantitative risk analysis. They also state that quantitative analysis is the best approach when financial impact of specific risk scenarios is needed.
Monitoring tracks risk over time, profiling summarizes the organization’s risk status, and reporting communicates risk information. Simulation is primarily an analytical technique, so it belongs in risk analysis.
===========
An online retailer has decided to store its customer database with a cloud provider in an Infrastructure as a Service (laaS) configuration. During an initial review of preliminary risk scenarios, a risk practitioner identifies instances where sensitive customer information is stored unencrypted. Who is accountable for ensuring this encryption?
The cloud provider
The retailer ' s IT department
The chief information officer (CIO)
The data owner
An audit reveals that there are changes in the environment that are not reflected in the risk profile. Which of the following is the BEST course of action?
Review the risk identification process.
Inform the risk scenario owners.
Create a risk awareness communication plan.
Update the risk register.
The best course of action when an audit reveals that there are changes in the environment that are not reflected in the risk profile is to review the risk identification process. This is because the risk identification process is the first step in the risk management process and it is responsible for identifying and assessing the potential risks that may affect the organization’s objectives. If the risk identification process is not effective, it may result in incomplete, inaccurate, or outdated risk profiles that do not reflect the current environment and the associated risks. Therefore, reviewing the risk identification process will help to ensure that the risk profile is updated and aligned with the changes in the environment and the organization’s strategy. References = Responding to Audit Findings
Which of the following controls would BEST reduce the likelihood of a successful network attack through social engineering?
Automated controls
Security awareness training
Multifactor authentication
Employee sanctions
The best control to reduce the likelihood of a successful network attack through social engineering is security awareness training. Security awareness training is a program that educates and trains employees on the common types, techniques, and indicators of social engineering attacks, such as phishing, baiting, pretexting, and quid pro quo12. Security awareness training also teaches employees how to protect themselves and the organization from social engineering attacks, such as by verifying the identity and legitimacy of the sender or caller, avoiding clicking on suspicious links or attachments, reporting any suspicious or unusual activity, and following the organization’s security policies and procedures. Security awareness training can help to reduce the likelihood of a successful network attack through social engineering, because it can increase the employees’ knowledge, skills, and confidence in recognizing and responding to social engineering attempts, and it can also foster a culture of security and responsibility among the employees. The other options are not the best control, although they may be useful or complementary to security awareness training. Automated controls are technical or procedural controls that are performed by a system or a device without human intervention, such as firewalls, antivirus software, encryption, and backups. Automated controls can help to protect the network from external or internal threats, but they may not be effective against social engineering attacks, which rely on humaninteraction and manipulation.Multifactor authentication is a security mechanism that requires users to provide two or more pieces of evidence to verify their identity and access a system or a service, such as a password, a token, a fingerprint, or a facial recognition. Multifactor authentication can help to prevent unauthorized access to the network, but it may not prevent social engineering attacks, which may persuade users to share or compromise their authentication factors. Employee sanctions are disciplinary actions that are taken against employees who violate the organization’s security policies and procedures, such as warnings, fines, suspensions, or terminations. Employee sanctions can help to deter and punish employees who fall victim to or facilitate social engineering attacks, but they may not prevent or reduce the likelihood of social engineering attacks, and they may also create a negative or fearful work environment. References = Avoiding Social Engineering and Phishing Attacks | CISA, What is Social Engineering | Attack Techniques & Prevention Methods …, 10 Types of Social Engineering Attacks - CrowdStrike
Which of the following stakeholders define risk tolerance for an enterprise?
IT compliance and IT audit
Regulators and shareholders
The board and executive management
Enterprise risk management (ERM)
Role of the Board and Executive Management:
The board of directors and executive management are responsible for setting the overall strategic direction of the organization, including its risk tolerance.
They have the authority and oversight necessary to define the levels of risk that the organization is willing to accept in pursuit of its objectives.
Defining Risk Tolerance:
Risk tolerance refers to the acceptable level of variation in performance relative to the achievement of objectives. It is essentially the degree of risk the organization is willing to endure.
The board and executive management establish risk tolerance based on the organization ' s strategic goals, capacity to absorb losses, and regulatory requirements.
Importance of Senior Leadership:
Senior leadership ' s involvement ensures that risk tolerance is aligned with the organization ' s overall strategy and risk appetite.
It provides a top-down approach to risk management, ensuring consistency and alignment across the organization.
Comparing Other Stakeholders:
IT Compliance and IT Audit:These functions are responsible for monitoring and ensuring adherence to policies but do not set risk tolerance.
Regulators and Shareholders:They influence risk management practices through external pressures but do not define risk tolerance directly.
Enterprise Risk Management (ERM):ERM frameworks support the implementation of risk management but the actual definition of risk tolerance comes from the board and executive management.
References:
The CRISC Review Manual discusses how senior management, including the board, is responsible for defining risk tolerance and ensuring it aligns with the organization ' s risk appetite (CRISC Review Manual, Chapter 1: Governance, Section 1.10 Risk Appetite, Tolerance, and Capacity) .
An organization has asked an IT risk practitioner to conduct an operational risk assessment on an initiative to outsource the organization ' s customer service operations overseas. Which of the following would MOST significantly impact management ' s decision?
Time zone difference of the outsourcing location
Ongoing financial viability of the outsourcing company
Cross-border information transfer restrictions in the outsourcing country
Historical network latency between the organization and outsourcing location
The most significant factor that would impact management’s decision when conducting an operational risk assessment on an initiative to outsource the organization’s customer service operations overseas is the cross-border information transfer restrictions in the outsourcing country. Cross-border information transfer restrictions are the laws, regulations, standards, or contracts that govern the collection, processing, storage, or transmission of information across national or regional boundaries. Cross-border information transfer restrictions may affect the organization’s outsourcing initiative, because they may impose limitations, obligations, or penalties on the organization or the outsourcing company, such as requiring consent, notification, or authorization, or prohibiting or restricting certain types or categories of information. Cross-border information transfer restrictions may also create challenges or risks for the organization’s outsourcing initiative, such as compliance, legal, reputational, or operational risks, or conflicts orinconsistencies with the organization’s own policies, regulations, standards, or contracts. The other options are not as significant as the cross-border information transfer restrictions, although they may also pose some difficulties or limitations for the organization’s outsourcing initiative. Time zone difference of the outsourcing location, ongoing financial viability of the outsourcing company, and historical network latency between the organization and outsourcing location are all factors that could affect the efficiency and effectiveness of the outsourcing initiative, but they do not directly affect the legality or security of the outsourcing initiative. References = 3
Which of the following would BEST enable a risk-based decision when considering the use of an emerging technology for data processing?
Gap analysis
Threat assessment
Resource skills matrix
Data quality assurance plan
The best way to enable a risk-based decision when considering the use of an emerging technology for data processing is to perform a gap analysis. A gap analysis is a technique that compares the current state and the desired state of a process, system, or capability, and identifies the gaps or differences between them. A gap analysis can help to evaluate the benefits, costs, risks, and opportunities of using an emerging technology for data processing, and to determine the feasibility, suitability, and readiness of adopting the emerging technology. The other options are not as helpful as a gap analysis, as they are related to the specific aspects or components ofthe data processing, not the overall assessment and comparison of the current and desired state of the data processing. References = Risk and Information Systems Control Study Manual, Chapter 1: IT Risk Identification, Section 1.2: IT Risk Identification Methods, page 19.
Which of the following risk activities is BEST facilitated by enterprise architecture (EA)?
Aligning business unit risk responses to organizational priorities
Determining attack likelihood per business unit
Adjusting business unit risk tolerances
Customizing incident response plans for each business unit
Which of the following activities should only be performed by the third line of defense?
Operating controls for risk mitigation
Testing the effectiveness and efficiency of internal controls
Providing assurance on risk management processes
Recommending risk treatment options
Providing assurance on risk management processes is the activity that should only be performed by the third line of defense, because it is the role and responsibility of the independent andobjective assurance function, such as internal audit or external audit, to evaluate and report on the effectiveness and efficiency of the risk management processes and controls. The third line of defense is the last layer of the three lines of defense model, which is a framework that defines the roles and responsibilities of different functions and levels within the organization for risk management and control. The first line of defense is the operational management and staff, who are responsible for identifying, assessing, and managing the risks and controls within their areas of responsibility. The second line of defense is the oversight and support functions, such as risk management, compliance, or legal, who are responsible for establishing and monitoring the risk policies, standards, and frameworks, and providing guidance and advice to the first line of defense. The third line of defense is the assurance function, who are responsible for providing independent and objective assurance on the adequacy and effectiveness of the risk management processes and controls, and reporting to the senior management and the board of directors. Operating controls for risk mitigation, testing the effectiveness and efficiency of internal controls, and recommending risk treatment options are all activities that can be performed by the first or second line of defense, but not by the third line of defense, as they are not part of the assurance function. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.4.1, page 59
Warning banners on login screens for laptops provided by an organization to its employees are an example of which type of control?
Corrective
Preventive
Detective
Deterrent
Warning banners on login screens serve as deterrent controls. Deterrent controls are designed to discourage individuals from attempting unauthorized actions by warning them of potential consequences.
Purpose of Warning Banners
Warning banners provide clear notice to users, both authorized and unauthorized, that their activities may be monitored and that unauthorized access is prohibited.
They serve as a legal disclaimer, which can be crucial in prosecuting unauthorized access attempts.
Effectiveness as a Deterrent Control
The primary function of a warning banner is to deter potential intruders by making them aware of the surveillance and legal implications of unauthorized access.
For authorized users, it reinforces awareness of the organization ' s security policies and acceptable use agreements.
Comparison with Other Control Types
A. Corrective: These controls are used to correct or restore systems after an incident.
B. Preventive: These controls are designed to prevent security incidents from occurring.
C. Detective: These controls are used to detect and alert about security incidents.
D. Deterrent: These controls are intended to discourage individuals from performing unauthorized activities.
References
Sybex-CISSP-Official-Study-Guide-9-Edition.pdf, p. 829, detailing the role of warning banners as deterrent controls.
An organization is considering allowing users to access company data from their personal devices. Which of the following is the MOST important factor when assessing the risk?
Classification of the data
Type of device
Remote management capabilities
Volume of data
The most important factor when assessing the risk of allowing users to access company data from their personal devices is the classification of the data, as it indicates the level of sensitivity, confidentiality, and criticality of the data. Data classification helps to determine the appropriate level of protection and controls that are needed to prevent unauthorized access, disclosure, modification, or loss of the data. Data classification also helps to define the roles and responsibilities of the data owners, custodians, and users, and the acceptable use of the data. The other options are not the most important factors, although they may be relevant or influential in the risk assessment. The type of device may affect the security features and vulnerabilities of the device, but it does not determine the value or impact of the data. The remote management capabilities may affect the ability to monitor, control, or wipe the device in case of theft or loss, but they do not reflect the nature or purpose of the data. The volume of data may affect the storage capacity or performance of the device, but it does not indicate the importance or significance of the data. References = What is BYOD (Bring-Your-Own-Device) - CrowdStrike; Understanding BYOD Policy - Get Certified Get Ahead; Addressing cyber security concerns on employees’ personal devices; Personal Devices at Work – Nonprofit Risk Management Center; 10 Keys to an Effective BYOD and Remote Access Policy
Which of the following is the PRIMARY role of a data custodian in the risk management process?
Performing periodic data reviews according to policy
Reporting and escalating data breaches to senior management
Being accountable for control design
Ensuring data is protected according to the classification
Which of the following tools is MOST effective in identifying trends in the IT risk profile?
Risk self-assessment
Risk register
Risk dashboard
Risk map
A risk dashboard is a graphical tool that displays the key indicators and metrics of the organization’s IT risk profile, such as the risk level, status, trend, performance, etc., using charts, graphs, tables, etc. A risk dashboard can help the organization to monitor and communicate the IT risk profile, and to support the decision making and planning for the IT risk management.
A risk dashboard is the most effective tool in identifying trends in the IT risk profile, because it provides a visual and intuitive representation of the changes and variations in the IT risk profile over time, and highlights the most significant and relevant IT risks that need to be addressed or monitored. A risk dashboard can also help to compare and contrast the IT risk profile with the organization’s IT objectives and risk appetite, and to identify the gaps or opportunities for improvement.
The other options are not the most effective tools in identifying trends in the IT risk profile, because they do not provide the same level of visibility and clarity that a risk dashboard provides, and they may not be updated or aligned with the organization’s IT objectives and risk appetite.
A risk self-assessment is a process of identifying, analyzing, and evaluating the IT risks that may affect the organization’s objectives and operations, using the input and feedback from the individuals or groups that are involved or responsible for the IT activities or functions. A risk self-assessment can help the organization to understand and document the IT risk profile, and to align it with the organization’s IT strategy and culture, but it is not the most effective tool in identifying trends in the IT risk profile, because it may not reflect the current or accurate state and performance of the IT risk profile, and it may not cover all the relevant or emerging IT risks that may exist or arise.
A risk register is a document that records and tracks the information and status of the identified IT risks and their responses. It includes the IT risk description, category, source, cause, impact, probability, priority, response, owner, action plan, status, etc. A risk register can help the organization to identify, analyze, evaluate, and communicate the IT risks and their responses, and to align them with the organization’s IT strategy and culture, but it is not the most effective tool in identifying trends in the IT risk profile, because it may not provide a visual and intuitive representation of the changes and variations in the IT risk profile over time, and it may not highlight the most significant and relevant IT risks that need to be addressed or monitored.
A risk map is a graphical tool that displays the results of the IT risk analysis in a matrix format, using colors and symbols to indicate the level and priority of the IT risks. A risk map can show the distribution and comparison of the IT risks based on various criteria, such as likelihood, impact, category, source, etc. A risk map can help the organization to assess and prioritize the IT risks, and to design and implement appropriate controls or countermeasures to mitigate or prevent the IT risks, but it is not the most effective tool in identifying trends in the IT risk profile, because it may not provide a visual and intuitive representation of the changes and variations in the IT risk profile over time, and it may not reflect the organization’s IT objectives and risk appetite. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 180
CRISC Practice Quiz and Exam Prep
A risk practitioner has been asked to evaluate the adoption of a third-party blockchain integration platform based on the value added by the platform and the organization ' s risk appetite. Which of the following is the risk practitioner ' s BEST course of action?
Conduct a risk assessment with stakeholders.
Conduct third-party resilience tests.
Update the risk register with the process changes.
Review risk related to standards and regulations.
Conducting a risk assessment with stakeholders is the best course of action for the risk practitioner to evaluate the adoption of a third-party blockchain integration platform, because it helps to identify, analyze, and evaluate the risks and opportunities associated with the platform, and to compare them with the organization’s risk appetite and value proposition. A risk assessment is a process of systematically identifying and assessing the sources and types of risk that an organization faces, and estimating their likelihood and impact. A risk assessment also involves identifying and evaluating the existing or proposed controls or mitigating factors that can reduce or eliminate the risk. A stakeholder is a person or group that has an interest or influence in the organization or its activities, such as customers, employees, shareholders,suppliers, regulators, or partners. A blockchain integration platform is a software solution that enables the organization to connect and interact with blockchain networks or applications, such as cryptocurrencies, smart contracts, or distributed ledgers. A blockchain integration platform can offer benefits such as transparency, security, efficiency, and innovation, but it can also pose risks such as technical complexity, interoperability issues, regulatory uncertainty, or cyberattacks. Therefore, conducting a risk assessment with stakeholders is the best way to evaluate the adoption of a third-party blockchain integration platform, as it helps to understand the benefits and risks of the platform, and to align them with the organization’s objectives and risk appetite. Conducting third-party resilience tests, updating the risk register with the process changes, and reviewing risk related to standards and regulations are all important tasks to perform after conducting a risk assessment, but they are not the best course of action, as they depend on the results of the risk assessment. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.2, page 87
An IT risk practitioner ' s report includes a treatment plan and projected risk ratings if recommendations are implemented. Once corrective actions are taken by the system owner, which of the following types of risk will the projected risk become?
Control
Inherent
Residual
Compliance
The correct answer isCbecause once corrective actions are implemented, the remaining projected risk becomesresidual risk. Residual risk is the exposure that remains after controls or treatment actions have been applied.
The other options are incorrect:
A. Controlis not a type of risk in this context.
B. Inherentrisk exists before controls are implemented.
D. Compliancerisk is a category of risk, not the remaining level after treatment.
Exact Extracts supporting the answer:
“Residual risk is best reflected as risk remaining after the implementation of new or enhanced controls.”
“The primary objective of a risk management program is to maintain residual risk at an acceptable level.”
“Acceptable risk for an enterprise is achieved when residual risk is within tolerance levels.”
“The risk most likely to be reduced to achieve acceptable risk is residual risk.”
These extracts directly show that once corrective actions are taken, the projected remaining risk isresidual risk.
===========
Which of the following is the MOST important objective from a cost perspective for considering aggregated risk responses in an organization?
Prioritize risk response options
Reduce likelihood.
Address more than one risk response
Reduce impact
The most important objective from a cost perspective for considering aggregated risk responses in an organization is to address more than one risk response. Aggregated risk responses are risk responses that can affect multiple risks or objectives simultaneously. By addressing more than one risk response, the organization can achieve cost efficiency and effectiveness in risk management. Prioritizing risk response options, reducing likelihood, and reducing impact are other possible objectives, but they are not as important from a cost perspective as addressing more than one risk response. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 10; CRISC Review Manual, 6th Edition, page 140.
Which of the following is the BEST approach for selecting controls to minimize risk?
Industry best practice review
Risk assessment
Cost-benefit analysis
Control-effectiveness evaluation
The best approach for selecting controls to minimize risk is to perform a risk assessment. A risk assessment is a process that identifies, analyzes, and evaluates the risks that could affect the organization’s objectives or operations. A risk assessment helps to determine the likelihood and impact of the risks, and to prioritize them based on their severity and relevance. A risk assessment also helps to select the most appropriate and effective controls to minimize the risks, such as avoiding, reducing, transferring, or accepting the risks. A risk assessment is the best approach for selecting controls, because it helps to align the controls with the organization’s risk profile, risk appetite, and risk objectives, and to ensure that the controls are adequate, suitable, and cost-effective. The other options are not the best approach for selecting controls, although they may be part of or derived from the risk assessment. Industry best practice review, cost-benefit analysis, and control-effectiveness evaluation are all activities that can help to support or improve the control selection, but they are not the best approach for selecting controls. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 4-13.
Which of the following functions independently reviews and provides feedback regarding the achievement of organizational objectives?
Risk management
Internal audit
IT governance
Senior leadership
Internal auditis thethird line of defense, providingindependent assuranceregarding risk management, controls, and governance effectiveness.
According to CRISC and the Three Lines Model:
“Internal audit independently reviews risk management processes and provides feedback on the achievement of objectives.”
Risk management (second line) monitors, not audits. Senior leadership (first line) executes strategy. Thus,Bis correct.
CRISC Reference:Domain 1 – IT Risk Governance, Topic: Three Lines Model Roles.
Which of the following is the PRIMARY reason for a risk practitioner to review an organization ' s IT asset inventory?
To plan for the replacement of assets at the end of their life cycles
To assess requirements for reducing duplicate assets
To understand vulnerabilities associated with the use of the assets
To calculate mean time between failures (MTBF) for the assets
Understanding vulnerabilities associated with the use of the assets is the primary reason for a risk practitioner to review an organization’s IT asset inventory, as it helps to identify and assess the potential threats and risks to the assets. The other options are not the primary reasons for a risk practitioner to review an organization’s IT asset inventory, although they may be related to the process.
Before selecting a final risk response option for a given risk scenario, management should FIRST:
determine control ownership.
evaluate the risk response of similar sized organizations.
evaluate the organization ' s ability to implement the solution.
determine the remediation timeline.
When evaluating a number of potential controls for treating risk, it is MOST important to consider:
risk appetite and control efficiency.
inherent risk and control effectiveness.
residual risk and cost of control.
risk tolerance and control complexity.
The most important factors to consider when evaluating a number of potential controls for treating risk are the residual risk and the cost of control. Residual risk is the risk that remains after the implementation of the controls. Cost of control is the amount of resources and efforts required to implement and maintain the controls. By considering the residual risk and the cost of control, the organization can optimize the balance between the risk exposure and the control investment, and choose the most effective and efficient controls. Risk appetite and control efficiency, inherent risk and control effectiveness, and risk tolerance and control complexity are other possible factors, but they are not as important as residual risk and cost of control. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 8; CRISC Review Manual, 6th Edition, page 97.
Which of the following BEST indicates that an organizations risk management program is effective?
Fewer security incidents have been reported.
The number of audit findings has decreased.
Residual risk is reduced.
inherent risk Is unchanged.
Residual risk is the risk that remains after the implementation of risk responses. An effective risk management program should aim to reduce the residual risk to a level that is acceptable by the enterprise, in alignment with its risk appetite and tolerance. The reduction of residual risk indicates that the risk responses are appropriate and effective, and that the enterprise is achieving its objectives while managing its risks. The other options are not necessarily indicative of an effective risk management program, as they may depend on other factors, such as the reporting culture, the audit scope and methodology, and the nature and source of the inherent risk. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.2.3.1, pp. 24-25.
A risk practitioner is performing a risk assessment of recent external advancements in quantum computing. Which of the following would pose the GREATEST concern for the risk practitioner?
The organization has incorporated blockchain technology in its operations.
The organization has not reviewed its encryption standards.
The organization has implemented heuristics on its network firewall.
The organization has not adopted Infrastructure as a Service (laaS) for its operations.
Which of the following is the BEST indication that an organization ' s risk management program has not reached the desired maturity level?
Significant increases in risk mitigation budgets
Large fluctuations in risk ratings between assessments
A steady increase in the time to recover from incidents
A large number of control exceptions
A risk management program is a set of processes, policies, and tools that enable an enterprise to identify, analyze, evaluate, treat, monitor, and communicate its risks. The maturity level of a risk management program indicates how well the program is integrated, standardized, and aligned with the enterprise’s objectives, culture, and values. The best indication that an organization’s risk management program has not reached the desired maturity level is large fluctuations in risk ratings between assessments. Risk ratings are the measures of the impact and likelihood of the risks, and they should be consistent and comparable across the enterprise and over time. Large fluctuations in risk ratings between assessments suggest that the risk management program is not stable, reliable, or effective, and that the risk identification and analysis methods are not robust, accurate, or transparent. The other options are not as indicative of the maturity level of the riskmanagement program, as they involve different aspects or outcomes of the risk management program:
Significant increases in risk mitigation budgets means that the enterprise is spending more resources on implementing risk responses, such as controls, policies, or procedures. This may indicate that the enterprise is facing more or higher risks, or that the risk responses are more costly or complex, but it does not necessarily reflect the maturity level of the risk management program, as it may also depend on the enterprise’s risk appetite, tolerance, and strategy.
A steady increase in the time to recover from incidents means that the enterprise is taking longer to restore its normal operations after a disruption or a loss. This may indicate that the enterprise is not prepared or resilient enough to deal with the incidents, or that the incidents are more frequent or severe, but it does not necessarily reflect the maturity level of the risk management program, as it may also depend on the nature and source of the incidents, or the availability and effectiveness of the recovery plans.
A large number of control exceptions means that the enterprise is deviating from the established controls, policies, or procedures, either intentionally or unintentionally. This may indicate that the enterprise is not complying with the risk management program, or that the controls are not adequate or appropriate for the enterprise’s needs, but it does not necessarily reflect the maturity level of the risk management program, as it may also depend on the reasons and justifications for the exceptions, or the approval and monitoring processes for the exceptions. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.1.3.1, pp. 14-15.
A risk practitioner is conducting a risk assessment after discovering the use of unauthorized cloud software on personal devices to accomplish work-related tasks. Which of the following is the risk practitioner ' s BEST course of action?
Evaluate the effectiveness of controls to prevent data loss.
Develop a policy standard for conducting business using personal devices.
Recommend blocking downloads of unauthorized software.
Identify the business need for the unauthorized software.
The correct answer isDbecause the risk practitioner should firstidentify the business need for the unauthorized software. If employees are using unauthorized cloud software on personal devices for work-related tasks, this indicates there is likely an unmet business requirement. Before recommending controls or restrictions, the best course of action is to understand why the software is being used, what business process it supports, and what gap in approved solutions exists. This aligns with CRISC principles that risk assessment must consider business objectives and operational needs before selecting risk responses.
The other options are not the best first step:
A. Evaluate the effectiveness of controls to prevent data lossmay be necessary later, but first the practitioner must understand the business driver behind the behavior.
B. Develop a policy standard for conducting business using personal devicesmay eventually be appropriate, but not before the underlying need is identified.
C. Recommend blocking downloads of unauthorized softwareis a control response, but it may disrupt business activities if the root business need is not understood.
Exact Extracts supporting the answer:
“During the initial stages of developing a risk management program it ' s crucial that the context and purpose of the program are defined.”
“Strategic planning and business requirements should be the driving forces behind the IT plan.”
“When selecting a risk response technique the foremost consideration should be the enterprise goals and objectives.”
“To best support IT in fulfilling business requirements an internal control system or framework is essential.”
“An approach that best helps an enterprise achieve risk-based organizational objectives is to embed risk management activities into business processes.”
These extracts support that the practitioner should first understand the business context and requirements behind the unauthorized use. Only after identifying that business need can the organization choose the most appropriate policy, control, or risk response.
Which of the following is the BEST way to determine the potential organizational impact of emerging privacy regulations?
Evaluate the security architecture maturity.
Map the new requirements to the existing control framework.
Charter a privacy steering committee.
Conduct a privacy impact assessment (PIA).
The best way to determine the potential organizational impact of emerging privacy regulations is to conduct a privacy impact assessment (PIA). A PIA is a systematic process of identifying, analyzing, and evaluating the privacy risks and impacts of a new or existing system, process, program, or initiative that involves the collection, use, storage, or disclosure of personal information. A PIA can help to ensure that the enterprise complies with the emerging privacyregulations, and that the privacy rights and expectations of the individuals are respected and protected. A PIA can also help to identify the gaps, weaknesses, and opportunities for improvement in the enterprise’s privacy policies, procedures, and controls. Evaluating the security architecture maturity, mapping the new requirements to the existing control framework, and chartering a privacy steering committee are not as comprehensive and effective as conducting a PIA, as they do not address the specific privacy risks and impacts of the enterprise’s activities. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 192.
After the implementation of a blockchain solution, a risk practitioner discovers noncompliance with new industry regulations. Which of the following is the MOST important course of actionpriorto informing senior management?
Evaluate the design effectiveness of existing controls.
Implement compensating controls.
Evaluate the industry response to the new regulations.
Evaluate the potential impact.
Before escalating to senior management, a risk practitioner must understandhow seriousthe issue is for the enterprise. That means first assessing thebusiness impactof the noncompliance (financial, regulatory, reputational, operational) so that management is givencontextualizedinformation rather than just “we are noncompliant.”
In ISACA’s CRISC framework, risk assessment always requires understandinglikelihood and impactbefore risk response and escalation decisions. Evaluating the potential impact allows:
Identification of which processes, customers, or jurisdictions are affected.
Estimation of the magnitude of legal/regulatory exposure.
Understanding whether immediate containment actions are needed.
Preparation of meaningful options and recommendations for senior management.
Options A and B (evaluating controls and implementing compensating controls) are importantlater, as part of risk response / treatment. However, without first knowing theimpact, you cannot determine how urgent or extensive the remedial actions must be.
Option C (evaluating industry response) may be useful for benchmarking, but it doesnothelp the enterprise understand its own specific exposure and obligations and therefore is secondary to an internal impact assessment.
This aligns with CRISC guidance thatthe primary result of a risk assessment is input for risk-aware decisionsand that risk professionals mustassess likelihood and impact to determine risk significance before escalation and treatment(see the risk assessment and risk profile–related guidance in your CRISC notes).
Which of the following BEST helps to mitigate risk associated with excessive access by authorized users?
Monitoring user activity using security logs
Revoking access for users changing roles
Granting access based on least privilege
Conducting periodic reviews of authorizations granted
The principle of least privilege is a key concept in information security that aims to provide users with the minimum level of access—or permissions—necessary to perform their job functions. Byensuring that users only have the access they need, organizations can significantly reduce the risk associated with excessive access by authorized users.
Understanding Least Privilege
The principle of least privilege restricts access rights for users to the bare minimum permissions they need to perform their work. This minimizes the potential damage from accidents or malicious activities.
Least privilege should be applied to all user accounts, including administrative and service accounts.
Implementation
Implementing least privilege involves a detailed analysis of job functions and the necessary access required for each role.
Regularly review and update access permissions to ensure they remain aligned with current job responsibilities and organizational needs.
Mitigating Risk
By limiting access to only what is necessary, organizations can prevent users from having permissions that could be exploited, intentionally or unintentionally, to cause harm.
This also includes revoking unnecessary privileges when users change roles or no longer need access.
Comparison with Other Options
A. Monitoring user activity using security logs: While monitoring can detect inappropriate activity, it does not prevent it.
B. Revoking access for users changing roles: This is a necessary practice but does not address the initial allocation of excessive privileges.
D. Conducting periodic reviews of authorizations granted: Periodic reviews are important but are reactive rather than proactive.
References
Sybex-CISSP-Official-Study-Guide-9-Edition.pdf, p. 641, discussing the principle of least privilege and its implementation.
Which of the following would BEST enable mitigation of newly identified risk factors related to internet of Things (loT)?
Introducing control procedures early in the life cycle
Implementing loT device software monitoring
Performing periodic risk assessments of loT
Performing secure code reviews
The BEST way to enable mitigation of newly identified risk factors related to internet of Things (loT) is to introduce control procedures early in the life cycle, because it can help to prevent or reduce the occurrence or impact of the risk factors, and to ensure that the loT devices and systems are designed and developed with security and quality in mind. The control procedures should include requirements analysis, design review, testing, validation, and verification of the loT devices and systems. The other options are not as effective as introducing control procedures early in the life cycle, because:
Option B: Implementing loT device software monitoring is a good way to detect and respond to the risk factors related to loT, but it does not enable mitigation of the risk factors, which is the proactive and preventive approach. Software monitoring is a reactive and corrective measure that may not be able to prevent or reduce the occurrence or impact of the risk factors, especially if they are embedded in the hardware or firmware of the loT devices.
Option C: Performing periodic risk assessments of loT is a necessary way to identify and evaluate the risk factors related to loT, but it does not enable mitigation of the risk factors, which is the action-oriented and solution-focused approach. Risk assessment is an analytical and descriptive process that may not provide the specific and effective measures to address or mitigate the risk factors, especially if they are complex or dynamic.
Option D: Performing secure code reviews is a useful way to verify and improve the security and quality of the software of the loT devices and systems, but it does not enable mitigation of the risk factors related to loT, which may involve more than just the software aspect. The risk factors related to loT may also include the hardware, firmware, network, communication, data, andintegration aspects, which may not be covered or resolved by the code reviews. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 214.
During a control review, the control owner states that an existing control has deteriorated over time. What is the BEST recommendation to the control owner?
Implement compensating controls to reduce residual risk
Escalate the issue to senior management
Discuss risk mitigation options with the risk owner.
Certify the control after documenting the concern.
The best recommendation to the control owner when an existing control has deteriorated over time is to discuss risk mitigation options with the risk owner. This is because the risk owner is the person or entity who has the authority and accountability to make decisions and take actions regarding the risk, including the selection and implementation of the risk response strategies. The control owner is the person or entity who is responsible for the design, operation, and maintenance of the control, but not for the overall risk management. By discussing risk mitigation options with the risk owner, the control owner can communicate the current status and performance of the control, and collaborate on finding the most appropriate and effective solution to address the risk and the control deterioration. The other options are not the best recommendation to the control owner, because they do not involve the risk owner, who is the key stakeholder in the risk management process, as explained below:
A. Implement compensating controls to reduce residual risk is not the best recommendation, because it may not be feasible, efficient, or sufficient to address the risk and the control deterioration. Compensating controls are additional or alternative controls that are implemented to mitigate the risk when the primary control is not available, adequate, or effective. However, implementing compensating controls without discussing with the risk owner may result in wasting resources, duplicating efforts, or conflicting objectives, and may not align with the risk appetite or strategy of the organization.
B. Escalate the issue to senior management is not the best recommendation, because it may not be necessary, timely, or appropriate to involve senior management in the risk and control deterioration issue. Senior management is the highest level of authority and oversight in the organization, and may not have the detailed or operational knowledge or involvement in the risk and control management. Escalating the issue to senior management without discussing with the risk owner may create confusion, delay, or misunderstanding, and may not result in the optimal risk mitigation solution.
D. Certify the control after documenting the concern is not the best recommendation, because it may not be accurate, honest, or compliant to certify the control when it has deteriorated over time. Certifying the control is the process of attesting that the control is designed and operating effectively and efficiently, and meets the established criteria and standards. Certifying the control after documenting the concern may not reflect the true status and performance of the control, and may not comply with the internal or external audit or regulatory requirements. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 115. Roles and Responsibilities in Risk Management, Risk Owner vs. Control Owner: What’s the Difference?, Control Deterioration: How to Avoid It and What to Do About It
Which of the following is a KEY responsibility of the second line of defense?
Implementing control activities
Monitoring control effectiveness
Conducting control self-assessments
Owning risk scenarios
The second line of defense is a group of functions that provide oversight, guidance, and monitoring of the risk management activities of the first line of defense. The second line of defense includes risk management, compliance, and internal control departments. Their key responsibility is to monitor the effectiveness of the control activities implemented by the first line of defense, and to report any issues or gaps to senior management and the board. The second line of defense also supports the first line of defense by providing frameworks, policies, tools,and techniques to identify, measure, and manage risks. The other options are not the key responsibility of the second line of defense, as explained below:
A. Implementing control activities is the responsibility of the first line of defense, which consists of the business units and process owners that own and manage the risks associated with their daily operations.
C. Conducting control self-assessments is a technique used by the first line of defense to evaluate the design and operation of their own controls, and to identify and report any deficiencies or improvement opportunities.
D. Owning risk scenarios is the responsibility of the first line of defense, which is accountable for the risks inherent in their business activities, and for developing and executing risk response strategies. References = Modernizing The Three Lines of Defense Model | Deloitte US, The second line of defence: fit for purpose, not an uncomfortable fit | Knowledge | Linklaters, COSO’s Take on the Three Lines of Defense | ERM - Enterprise Risk Management, Three Lines of Defense | Risk Management - Schneider Downs CPAs, What is the Three Lines of Defense Approach to Risk Management?
When developing a response plan to address security incidents regarding sensitive data loss, it is MOST important
revalidate current key risk indicators (KRIs).
revise risk management procedures.
review the data classification policy.
revalidate existing risk scenarios.
When developing a response plan to address security incidents regarding sensitive data loss, it is most important to review the data classification policy. A data classification policy is a document that defines the categories and levels of data based on their sensitivity, value, and criticality, and specifies the appropriate security measures and handling procedures for each data type. A data classification policy helps to identify and protect the sensitive data that could be exposed or compromised in a security incident, and to comply with the relevant laws, regulations, standards, and contracts. Reviewing the data classification policy is important when developing a response plan, because it helps to determine the scope, impact, and priority of the security incident, and to select the most appropriate and effective response actions and strategies. Reviewing the data classification policy also helps to communicate and coordinate the response plan with the internal and external stakeholders, such as the data owners, users, custodians, and regulators, and to report and disclose the security incident as required. The other options are not as important as reviewing the data classification policy, although they may be part of or derived from the response plan. Revalidating current key risk indicators (KRIs), revising risk management procedures, and revalidating existing risk scenarios are all activities that can help to improve or update the risk management process, but they are not the most important when developing aresponse plan. References = Risk and Information Systems Control Study Manual, Chapter 5, Section 5.3.1, page 5-25.
Which of the following would BEST help to ensure that identified risk is efficiently managed?
Reviewing the maturity of the control environment
Regularly monitoring the project plan
Maintaining a key risk indicator for each asset in the risk register
Periodically reviewing controls per the risk treatment plan
According to the CRISC Review Manual (Digital Version), periodically reviewing controls per the risk treatment plan would best help to ensure that identified risk is efficiently managed, as it involves verifying the effectiveness and efficiency of the implemented risk response actions and identifying any gaps or changes in the risk profile. Periodically reviewing controls per the risk treatment plan helps to:
Confirm that the controls are operating as intended and producing the desired outcomes
Detect any deviations, errors, or weaknesses in the controls and their performance
Evaluate the adequacy and appropriateness of the controls in relation to the current risk environment and the organization’s risk appetite and risk tolerance
Recommend and implement corrective actions or improvement measures to address any issues or deficiencies in the controls
Update the risk register and the risk treatment plan to reflect the current risk status and the residual risk levels
References = CRISC Review Manual (Digital Version), Chapter 4: IT Risk Monitoring and Reporting, Section 4.1: IT Risk Monitoring, pp. 215-2161
Which of the following is MOST critical to the design of relevant risk scenarios?
The scenarios are based on past incidents.
The scenarios are linked to probable organizational situations.
The scenarios are mapped to incident management capabilities.
The scenarios are aligned with risk management capabilities.
Risk scenarios are hypothetical situations that describe potential events or actions that could affect the achievement of enterprise objectives. The design of relevant risk scenarios should consider the following factors: the risk appetite and tolerance of the enterprise, the key risk indicators and risk drivers, the potential impact and likelihood of the scenarios, and the alignment with the risk management capabilities of the enterprise. The scenarios should be realistic, plausible, and consistent with the enterprise’s context and objectives. The scenarios should also be reviewed and updated periodically to reflect changes in the internal and external environment. The alignment with the risk management capabilities is the most critical factor, as it ensures that the scenarios are relevant for the decision making and risk response processes of the enterprise. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.3.3.2, pp. 67-69.
After the implementation of a remediation plan, an assessment of associated control design and operating effectiveness can determine the level of:
residual risk.
aggregated risk.
audit risk.
inherent risk.
Once remediation actions have been implemented, the risk practitioner evaluates whether the new or enhanced controls are designed appropriately and operating effectively. In the CRISC framework, this post-implementation evaluation is used to determine how much risk remains after controls are in place—this isresidual risk. Inherent risk is the risk level before considering any controls; therefore it is assessed earlier in the process. Audit risk relates to assurance work, not specifically to the outcome of a remediation plan. Aggregated risk refers to a combined view of multiple risks and is not the direct output of evaluating one specific remediation initiative. By assessing control design (fit for purpose) and operating effectiveness (working as intended), the practitioner can compare the new residual risk level to risk appetite and tolerance, and determine whether additional treatment is needed.
If preventive controls cannot be Implemented due to technology limitations, which of the following should be done FIRST to reduce risk7
Evaluate alternative controls.
Redefine the business process to reduce the risk.
Develop a plan to upgrade technology.
Define a process for monitoring risk.
If preventive controls cannot be implemented due to technology limitations, the first step to reduce risk is to evaluate alternative controls. Alternative controls are those that can achieve thesame or similar objectives as the original preventive controls, but using different methods or technologies. For example, if a firewall cannot be installed due to hardware compatibility issues, an alternative control could be a network segmentation or a proxy server. Evaluating alternative controls requires assessing their feasibility, effectiveness, efficiency, and cost-benefit. Redefining the business process, developing a plan to upgrade technology, and defining a process for monitoring risk are also possible actions to reduce risk, but they are not the first step, and they may not be feasible or desirable in some situations. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-23.
Which of the following IT key risk indicators (KRIs) provides management with the BEST feedback on IT capacity?
Trends in IT resource usage
Trends in IT maintenance costs
Increased resource availability
Increased number of incidents
IT capacity is the ability of an IT system or network to handle the current and future workload and performance demands. IT capacity can be affected by various factors, such as the numberand type of users, applications, devices, data, transactions, etc. IT capacity management is the process of planning, monitoring, and optimizing the IT resources to ensure that they meet the business needs and objectives. IT capacity management can help prevent issues such as system slowdowns, outages, errors, or failures, and improve the efficiency, reliability, and security of the IT system or network. One of the IT key risk indicators (KRIs) that provides managementwith the best feedback on IT capacity is the trends in IT resource usage. IT resource usage is the measure of how much of the IT resources, such as CPU, memory, disk, bandwidth, etc., are being consumed by the IT system or network. Trends in IT resource usage can help monitor and analyze the changes in the IT capacity over time, and identify the patterns, peaks, and bottlenecks in the IT resource consumption. Trends in IT resource usage can also help forecast the future IT capacity requirements, and plan for the appropriate IT resource allocation, optimization, or expansion. Trends in IT resource usage can provide management with valuable information on the current and potential IT capacity risks, and support the decision making and risk response for IT capacity management. References = Integrating KRIs and KPIs for Effective Technology Risk Management, p. 3-4.
Which of the following should be a risk practitioner’s MOST important consideration when developing IT risk scenarios?
The impact of controls on the efficiency of the business in delivering services
Linkage of identified risk scenarios with enterprise risk management
Potential threats and vulnerabilities that may have an impact on the business
Results of network vulnerability scanning and penetration testing
The MOST important consideration when developing IT risk scenarios is the potential threats and vulnerabilities that may have an impact on the business, because they are the key elements of a risk scenario that describe the sources and causes of the risk, and the potential consequences and impacts of the risk on the business objectives and processes. The other options are not as important as the potential threats and vulnerabilities, because:
Option A: The impact of controls on the efficiency of the business in delivering services is a secondary consideration that may affect the cost-benefit analysis of the risk response, but it does not directly affect the identification and assessment of the risk scenario.
Option B: Linkage of identified risk scenarios with enterprise risk management is a good practice that ensures the alignment and integration of the IT risk management with the overall enterprise risk management, but it does not directly affect the identification and assessment of the risk scenario.
Option D: Results of network vulnerability scanning and penetration testing are useful sources of information that may reveal some of the threats and vulnerabilities in the IT environment, but they are not the only or the most important consideration when developing IT risk scenarios, as they may not cover all the aspects and dimensions of the risk. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 104.
Recovery the objectives (RTOs) should be based on
minimum tolerable downtime
minimum tolerable loss of data.
maximum tolerable downtime.
maximum tolerable loss of data
Recovery time objectives (RTOs) are the acceptable timeframes within which business processes must be restored after a disruption. RTOs should be based on the maximum tolerable downtime (MTD), which is the longest time that a business process can be inoperable without causing irreparable harm to the organization. The other options are not directly related to RTOs, as they refer to the amount of data loss or corruption that can be tolerated, not the time to restore the business processes. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.3: Key Risk Indicators, page 197.
Which of the following BEST enforces access control for an organization that uses multiple cloud technologies?
Senior management support of cloud adoption strategies
Creation of a cloud access risk management policy
Adoption of a cloud access security broker (CASB) solution
Expansion of security information and event management (SIEM) to cloud services
A cloud access security broker (CASB) solution is the best way to enforce access control for an organization that uses multiple cloud technologies, as it provides a centralized and consistent platform to manage and monitor the access to various cloud services and applications. A CASB solution can help to implement and enforce the enterprise’s access policies and standards, as well as to detect and prevent unauthorized or malicious access attempts. Senior management support of cloud adoption strategies, creation of a cloud access risk management policy, and expansion of security information and event management (SIEM) to cloud services are not the best ways to enforce access control for an organization that uses multiple cloud technologies, as they do not provide the technical capabilities or tools to manage and monitor the access to various cloud services and applications. References = CRISC by Isaca Actual Free Exam Q & As, question 210; CRISC: Certified in Risk & Information Systems Control Sample Questions, question 210.
Which of the following would MOST effectively reduce the potential for inappropriate exposure of vulnerabilities documented in an organization ' s risk register?
Limit access to senior management only.
Encrypt the risk register.
Implement role-based access.
Require users to sign a confidentiality agreement.
A risk register is a document that contains information about potential cybersecurity risks that could threaten a project’s success, or even the business itself2. Therefore, it is important to protect the confidentiality and integrity of the risk register from unauthorized or inappropriate access, modification, or disclosure. One way to do this is to implement role-based access, which is a method of restricting access to the risk register based on the roles or responsibilities of the users1. This way, only authorized users who need to view or edit the risk register for legitimate purposes can do so, and the access rights can be revoked or modified as needed. This would most effectively reduce the potential for inappropriate exposure of vulnerabilities documented in the risk register. The other options are not as effective or feasible as option C, as they do not address the need to balance the security and availability of the risk register. Option A, limiting access to senior management only, would compromise the availability and usefulness of the risk register, as other stakeholders such as project managers, risk owners, or auditors may need to access therisk register for risk identification, analysis, response, or monitoring purposes3. Option B, encrypting the risk register, would enhance the security of the risk register, but it would not prevent authorized users from exposing the vulnerabilities to unauthorized parties, either intentionally or unintentionally. Encryption also adds complexity and cost to the risk register management process, and may affect the performance or usability of the risk register4. Option D, requiring users to sign a confidentiality agreement, would rely on the compliance and ethics of the users, but it would not prevent or detect any breaches of the agreement. A confidentiality agreement also does not specify the access rights or roles of the users, and may not be legally enforceable in some cases5.
During an organization ' s simulated phishing email campaign, which of the following is the BEST indicator of a mature security awareness program?
A high number of participants reporting the email
A high number of participants deleting the email
A low number of participants with questions for the help desk
A low number of participants opening the email
A mature program is indicated by employees recognizing phishing and actively reporting it—not just deleting it. ISACA guidance states that awareness programs should foster “threat identification and escalation actions,” not just passive compliance.
Which of the following is the BEST course of action when an organization wants to reduce likelihood in order to reduce a risk level?
Monitor risk controls.
Implement preventive measures.
Implement detective controls.
Transfer the risk.
The best course of action when an organization wants to reduce likelihood in order to reduce a risk level is to implement preventive measures. Likelihood is the probability or chance of a risk occurring, and risk level is the combination of likelihood and impact of a risk. Preventive measures are controls that are designed to prevent or deter the occurrence of a risk, such as policies, standards, procedures, guidelines, etc. Implementing preventive measures is the best course of action, because it helps to reduce the likelihood of a risk, and consequently, the risk level. Implementing preventive measures also helps to protect and enhance the organization’s objectives, performance, and improvement. The other options are not the best course of action, although they may be related to the risk management process. Monitoring risk controls, implementing detective controls, and transferring the risk are all activities that can help to manage or mitigate the risks, but they do not necessarily reduce the likelihood or the risk level. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-21.
Which of the following is the BEST way for a risk practitioner to help management prioritize risk response?
Align business objectives to the risk profile.
Assess risk against business objectives
Implement an organization-specific risk taxonomy.
Explain risk details to management.
The best way for a risk practitioner to help management prioritize risk response is to assess risk against business objectives. This means comparing the level and nature of the risks with the goals and strategies of the organization, and determining which risks pose the most significant threat or opportunity to the achievement of those objectives. By assessing risk against business objectives, the risk practitioner can help management identify the most critical and relevant risks, and prioritize the risk response actions accordingly. The risk response actions should be aligned with the organization’s risk appetite, which is the amount and type of risk that the organization is willing to take in order to meet its strategic goals1. The other options are not the best ways for a risk practitioner to help management prioritize risk response, as they are either less effective orless specific than assessing risk against business objectives. Aligning business objectives to the risk profile is a way of ensuring that the organization’s objectives are realistic and achievable, given the current and potential risks that the organization faces. However, this is not the same as prioritizing risk response, as it does not indicate which risks should be addressed first or howtheyshould be managed. Implementing an organization-specific risk taxonomy is a way of creating a common language and classification system for describing and categorizing risks. This can help improve the consistency and clarity of risk communication and reporting across the organization. However, this is not the same as prioritizing risk response, as it does not measure the likelihood and impact of the risks, or their relation to the organization’s objectives. Explaining risk details to management is a way of providing information and insight on the sources, drivers, consequences, and responses of the risks. This can help increase the awareness and understanding of the risks among the decision makers and stakeholders. However, this is not the same as prioritizing risk response, as it does not suggest or recommend the best course of action for managing the risks. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.6, Page 57.
To ensure key risk indicators (KRIs) are effective and meaningful, the KRIs should be aligned to:
A control framework
Industry standards
Capability maturity targets
Business processes
KRIs must be aligned to business processes to ensure they reflect actual risk conditions affecting critical operations. Misalignment can lead to inaccurate monitoring and ineffective response.
An organization has recently updated its disaster recovery plan (DRP). Which of the following would be the GREATEST risk if the new plan is not tested?
External resources may need to be involved.
Data privacy regulations may be violated.
Recovery costs may increase significantly.
Service interruptions may be longer than anticipated.
Testing a disaster recovery plan is essential to ensure its effectiveness and identify any gaps or weaknesses that might hinder the recovery process. Without testing, the organization may face longer service interruptions than anticipated, which could result in loss of revenue, customer dissatisfaction, reputational damage, and regulatory penalties. Some of the best practices for disaster recovery testing are1:
Test many scenarios
Test regularly
Document everything
Keep everyone updated
Define metrics
Evaluate the results
Test your disaster recovery plan
References = Best Practices For Disaster Recovery Testing | Snyk
Reviewing results from which of the following is the BEST way to identify information systems control deficiencies?
Vulnerability and threat analysis
Control remediation planning
User acceptance testing (UAT)
Control self-assessment (CSA)
Information systems control deficiencies are the weaknesses or flaws in the design or implementation of the controls that are intended to ensure the confidentiality, integrity, availability, and reliability of the information systems and resources. Information systems control deficiencies may reduce the effectiveness or efficiency of the controls, and expose the organization to various risks, such as unauthorized access, data loss, system failure, etc.
Reviewing results from control self-assessment (CSA) is the best way to identify information systems control deficiencies, because CSA is a process of evaluating and verifying the adequacy and effectiveness of the information systems controls, using the input and feedback from the individuals or groups that are involved or responsible for the information systems activities or functions. CSA can help the organization to identify and document the information systems control deficiencies, and to align them with the organization’s information systems objectives and requirements.
CSA can be performed using various techniques, such as questionnaires, surveys, interviews, workshops, etc. CSA can also be integrated with the organization’s governance, risk management, and compliance functions, and aligned with the organization’s policies and standards.
The other options are not the best ways to identify information systems control deficiencies, because they do not provide the same level of detail and insight that CSA provides, and they may not be relevant or actionable for the organization.
Vulnerability and threat analysis is a process of identifying and evaluating the weaknesses or flaws in the organization’s assets, processes, or systems that can be exploited or compromised by the potential threats or sources of harm that may affect the organization’s objectives or operations. Vulnerability and threat analysis can help the organization to assess and prioritize the risks, and to design and implement appropriate controls or countermeasures to mitigate or prevent the risks, but it is not the best way to identify information systems control deficiencies, because it does not indicate whether the existing information systems controls are adequate and effective, and whether they comply with the organization’s policies and standards.
Control remediation planning is a process of selecting and implementing the actions or plans to address or correct the information systems control deficiencies that have been identified,analyzed, and evaluated. Control remediation planning involves choosing one ofthe following types of control responses: mitigate, transfer, avoid, or accept. Control remediation planning can help the organization to improve and optimize the information systems controls, and to reduce or eliminate the information systems control deficiencies, but it is not the best way to identify information systems control deficiencies, because it is a subsequent or follow-up process that depends on the prior identification of the information systems control deficiencies.
User acceptance testing (UAT) is a process of verifying and validating the functionality and usability of the information systems and resources, using the input and feedback from the endusers or customers that interact with the information systems and resources. UAT can help the organization to ensure that the information systems and resources meet the user or customer expectations and requirements, and to identify and resolve any issues or defects that may affect the user or customer satisfaction, but it is not the best way to identify information systems control deficiencies, because it does not focus on the information systems controls, and it may not cover all the relevant or significant information systems control deficiencies that may exist or arise. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 186
CRISC Practice Quiz and Exam Prep
The BEST way to justify the risk mitigation actions recommended in a risk assessment would be to:
align with audit results.
benchmark with competitor s actions.
reference best practice.
focus on the business drivers
The best way to justify the risk mitigation actions recommended in a risk assessment would be to focus on the business drivers, which are the factors that influence the organization’s objectives, performance, and value creation12.
Focusing on the business drivers means aligning the risk mitigation actions with the organization’s strategic goals, priorities, and values, and demonstrating how the actions will support or enhance the organization’s capabilities, opportunities, and competitive advantage12.
Focusing on the business drivers also means communicating the benefits, costs, and trade-offs of the risk mitigation actions to the relevant stakeholders, and showing how the actions will address the organization’s risk appetite, tolerance, and exposure12.
The other options are not the best way to justify the risk mitigation actions, but rather possible sources of information or guidance that may support the justification. For example:
Aligning with audit results is a way to validate the effectiveness and efficiency of the risk mitigation actions, and to identify any gaps or weaknesses that need improvement34. However, audit results may not reflect the organization’s current or future business drivers, and may not capture the full scope or impact of the risk mitigation actions34.
Benchmarking with competitor’s actions is a way to compare the organization’s risk mitigation actions with the best practices or standards of the industry or market, and to identify any areas of improvement or differentiation56. However, competitor’s actions may not be suitable or applicable for the organization’s specific context, needs, or challenges, and may not align with the organization’s business drivers56.
Referencing best practice is a way to adopt the proven or accepted methods or techniques for risk mitigation, and to ensure the quality and consistency of the risk mitigation actions78. However, best practice may not be the most optimal or innovative solution for the organization’s unique situation, and may not address the organization’s business drivers78. References =
1: Risk IT Framework, ISACA, 2009
2: IT Risk Management Framework, University of Toronto, 2017
3: IT Audit and Assurance Standards, ISACA, 2014
4: IT Audit and Assurance Guidelines, ISACA, 2014
5: Benchmarking IT Risk Management Practices, ISACA Journal, Volume 4, 2017
6: Benchmarking: A Tool for Improving IT Risk Management, ISACA Now Blog, March 27, 2017
7: IT Risk Management Best Practices, ISACA Journal, Volume 1, 2018
8: IT Risk Management Best Practices, ISACA Now Blog, January 9, 2018
When assigning control ownership, it is MOST important to verify that the owner has accountability for:
Control effectiveness.
The budget for control implementation.
Assessment of control risk.
Internal control audits.
Control owners must be accountable for ensuring the effectiveness of the controls they manage. This accountability ensures the alignment of controls with risk objectives, as outlined inControl Governance and Ownership.
Which of the following is the BEST method of creating risk awareness in an organization?
Marking the risk register available to project stakeholders
Ensuring senior management commitment to risk training
Providing regular communication to risk managers
Appointing the risk manager from the business units
The best method of creating risk awareness in an organization is to ensure senior management commitment to risk training. Senior management plays a vital role in setting the tone and direction of the risk culture and governance in the organization. By demonstrating their support and participation in risk training, they can influence and motivate the employees to follow the risk policies and procedures, and to enhance their risk knowledge and skills. Marking the risk register available to project stakeholders, providing regular communication to risk managers, and appointing the risk manager from the business units are other methods of creating risk awareness, but they are not as effective as ensuring senior management commitment to risk training. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 12; CRISC Review Manual, 6th Edition, page 215.
Which of the following is the BEST metric to demonstrate the effectiveness of an organization ' s patch management process?
Average time to implement patches after vendor release
Number of patches tested prior to deployment
Increase in the frequency of patches deployed into production
Percent of patches implemented within established timeframe
The percent of patches implemented within established timeframe is the best metric to demonstrate the effectiveness of an organization’s patch management process, as it measures how well the organization meets its patching objectives and reduces its exposure to vulnerabilities. This metric reflects the timeliness, completeness, and quality of the patching process, and can be compared against the organization’s patch management policy and standards. A high percent of patches implemented within established timeframe indicates that the organization has a mature and efficient patch management process that minimizes the risk of security breaches or operational disruptions due to unpatched systems.
Which of the following should be the PRIMARY driver for an organization on a multi-year cloud implementation to publish a cloud security policy?
Evaluating gaps in the on-premise and cloud security profiles
Establishing minimum cloud security requirements
Enforcing compliance with cloud security parameters
Educating IT staff on variances between on premise and cloud security
The primary driver for an organization on a multi-year cloud implementation to publish a cloud security policy is to establish minimum cloud security requirements, as they specify the standards and expectations for the protection of the data and systems in the cloud environment, and ensure the alignment and compliance of the cloud security strategy with the organizational objectives and regulations. The other options are not the primary drivers, as they are more related to the evaluation, enforcement, or education of the cloud securitypolicy, respectively, rather than the establishment of the cloud security policy. References = CRISC Review Manual, 7th Edition, page 155.
Which of the following will BEST help mitigate the risk associated with malicious functionality in outsourced application development?
Perform an in-depth code review with an expert
Validate functionality by running in a test environment
Implement a service level agreement.
Utilize the change management process.
The risk associated with malicious functionality in outsourced application development is that the vendor may introduce unauthorized or harmful code into the enterprise’s system, which could compromise its security, integrity, or performance.
To mitigate this risk, the enterprise should perform an in-depth code review with an expert who can verify that the code meets the specifications, standards, and quality requirements, and that it does not contain any malicious or unwanted functionality.
A code review is a systematic examination of the source code of a software program, which can identify errors, vulnerabilities, inefficiencies, or deviations from best practices. A code review can also ensure that the code is consistent, readable, maintainable, and well-documented.
An expert is someone who has the knowledge, skills, and experience to perform the code review effectively and efficiently. An expert may be an internal or external resource, depending on the availability, cost, and independence of the reviewer.
A code review should be performed before the code is deployed to the production environment, and preferably at multiple stages of the development life cycle, such as design, testing, and integration.
A code review can also be complemented by other techniques, such as automated code analysis, testing, and scanning tools, which can detect common or known issues in the code. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, p. 143
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 143
Which of the following is the BEST way to validate privileged access to database accounts?
Regular reviews of privileged access
Confirmation from users with privileged access
Management approval of access requests
Confirmation from the database administrator (DBA)
Regular reviewshelp detect inappropriate, outdated, or excessive access rights. This is a fundamental part of access control governance and supports the principle of least privilege.
Which of the following BEST enables a proactive approach to minimizing the potential impact of unauthorized data disclosure?
Cyber insurance
Data backups
Incident response plan
Key risk indicators (KRIs)
Key Risk Indicators (KRIs) are metrics used by organizations to provide early warning signs of potential risks, including unauthorized data disclosure. By monitoring KRIs, organizations can proactively identify vulnerabilities and take corrective actions before a risk materializes. This proactive approach is essential in minimizing the potential impact of data breaches.
According to ISACA ' s CRISC Review Manual, KRIs are defined as " metrics capable of showing that the enterprise is, or has a high probability of being, subject to a risk that exceeds the defined risk appetite. " They are critical to the measurement and monitoring of risk and performance optimization. ISACA
While data backups (Option B) are vital for data recovery post-incident, they do not prevent unauthorized disclosures. An incident response plan (Option C) is reactive, focusing on responding after an incident has occurred. Cyber insurance (Option D) provides financial compensation post-incident but does not prevent the occurrence of data breaches.
Therefore, implementing and monitoring KRIs is the most proactive approach to minimizing the potential impact of unauthorized data disclosure.
Which of the following approaches will BEST help to ensure the effectiveness of risk awareness training?
Piloting courses with focus groups
Using reputable third-party training programs
Reviewing content with senior management
Creating modules for targeted audiences
The best approach to ensure the effectiveness of risk awareness training is to create modules for targeted audiences. This means that the risk awareness training should be customized and tailored to the specific needs, roles, and responsibilities of different groups of staff, such as business owners, process owners, IT staff, or external parties. Creating modules for targeted audiences helps to ensure that the risk awareness training is relevant, engaging, and applicable to the participants, and that it covers the appropriate level of detail and complexity. It also helps to enhance the learning outcomes and retention of the risk awareness training, and to foster aculture of risk awareness and responsibility within the enterprise. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 5, Section 5.4.1, page 2491
A risk manager has determined there is excessive risk with a particular technology. Who is the BEST person to own the unmitigated risk of the technology?
IT system owner
Chief financial officer
Chief risk officer
Business process owner
The best person to own the unmitigated risk of the technology is the IT system owner. The IT system owner is the person or entity that has the authority and responsibility for the acquisition, development, maintenance, and operation of the IT system. The IT system owner is also responsible for ensuring that the IT system meets the business requirements, security standards, and compliance obligations of the enterprise. The IT system owner should own the unmitigated risk of the technology, as they are in the best position to understand the nature and impact of the risk, and to implement the appropriate risk responses to reduce the risk exposure to an acceptable level. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.3.1, page 251234
Which of the following is MOST important to consider when developing an organization ' s risk management strategy?
Complexity of technology architecture
Disaster recovery strategy
Business operational requirements
Criteria for assessing risk
Thebusiness operational requirementsshould be the central consideration when crafting a risk management strategy. This ensures that risk management aligns with and supports business objectives, a core principle in ISACA’s risk management framework.
===========
An organization is considering the adoption of an aggressive business strategy to achieve desired growth From a risk management perspective what should the risk practitioner do NEXT?
Identify new threats resorting from the new business strategy
Update risk awareness training to reflect current levels of risk appetite and tolerance
Inform the board of potential risk scenarios associated with aggressive business strategies
Increase the scale for measuring impact due to threat materialization
The next thing that the risk practitioner should do from a risk management perspective when the organization is considering the adoption of an aggressive business strategy to achieve desired growth is to identify new threats resulting from the new business strategy. A threat is a potentialcause of an unwanted incident that may affect the achievement of the objectives. An aggressive business strategy is a strategy that involves pursuing high-risk, high-reward opportunities or initiatives to gain a competitive advantage or a significant market share. An aggressive business strategy may introduce new threats or increase thelikelihood or impact of existing threats, such as market volatility, regulatory changes, customer dissatisfaction, or competitor retaliation. Therefore, the risk practitioner should identify the new threats resulting from the new business strategy, and assess their potential consequences and implications for the organization. The other options are not as immediate as identifying new threats resulting from the new business strategy, as they are related to the update, information, or measurement of the risk management process, not the identification or analysis of the risk. References = Risk and Information Systems Control Study Manual, Chapter 1: IT Risk Identification, Section 1.3: IT Risk Scenarios, page 23.
Which of the following is the MOST important characteristic of a key risk indicator (KRI) to enable decision-making?
Monitoring the risk until the exposure is reduced
Setting minimum sample sizes to ensure accuracy
Listing alternative causes for risk events
Illustrating changes in risk trends
The most important characteristic of a key risk indicator (KRI) to enable decision-making is illustrating changes in risk trends, as it provides a clear and timely indication of the direction and magnitude of the risk level and exposure, and enables the stakeholders to take proactive andappropriate actions to address the risk. The other options are not the most important characteristics, as they are more related to the monitoring, measurement, or identification of the risk, respectively, rather than the illustration of the risk trends. References = CRISC Review Manual, 7th Edition, page 110.
During the control evaluation phase of a risk assessment, it is noted that multiple controls are ineffective. Which of the following should be the risk practitioner ' s FIRST course of action?
Compare the residual risk to the current risk appetite.
Recommend risk remediation of the ineffective controls.
Implement key control indicators (KCIs).
Escalate the control failures to senior management.
The first step is to assess whether the ineffective controls result in residual risk exceeding the risk appetite. This establishes the urgency and priority of remediation efforts and ensures alignment with enterprise risk thresholds, reflecting principles ofRisk Assessment and Prioritization.
After a high-profile systems breach at an organization s key vendor, the vendor has implemented additional mitigating controls. The vendor has voluntarily shared the following set of assessments:
Which of the assessments provides the MOST reliable input to evaluate residual risk in the vendor ' s control environment?
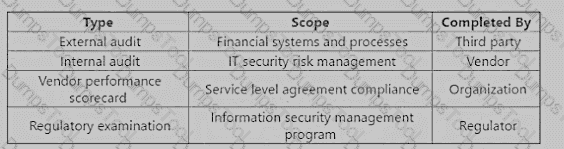
External audit
Internal audit
Vendor performance scorecard
Regulatory examination
An external audit is the most reliable input to evaluate residual risk in the vendor’s control environment, as it provides an independent and objective assessment of the vendor’s financial systems and processes. An external audit is conducted by a third party, such as a certified public accountant (CPA) or a professional auditing firm, that follows the generally accepted auditing standards (GAAS) and the generally accepted accounting principles (GAAP). An external audit can help to verify the accuracy and completeness of the vendor’s financial statements, identify any material misstatements or errors, and evaluate the effectiveness and efficiency of the vendor’s internal controls. An external audit can also provide assurance and confidence to the organization and other stakeholders that the vendor is complying with the relevant laws, regulations, and contractual obligations.
The other options are not the most reliable inputs to evaluate residual risk in the vendor’s control environment. An internal audit is conducted by the vendor itself, which may introduce bias or conflict of interest. An internal audit may also have a different scope, methodology, or quality than an external audit. A vendor performance scorecard is completed by the organization, which may not have the sufficient access, expertise, or authority to assess the vendor’s control environment. A vendor performance scorecard may also focus more on the service level agreement (SLA) compliance, rather than the financial systems and processes. A regulatory examination is conducted by a regulator, such as a government agency or a standard-settingbody, which may have a different purpose, criteria, or perspective than the organization. A regulatory examination may also have a limited scope, frequency, or transparency. References = Guide to VendorRisk Assessment | Smartsheet, Understanding Inherent Vs. Residual Risk Assessments - Resolver, Assessing Internal Controls over Compliance - HCCA Official Site
Which of the following is the MOST important consideration when determining the appropriate data retention period throughout the data management life cycle?
Data storage and collection methods
Data owner preferences
Legal and regulatory requirements
Choice of encryption algorithms
Legal and regulatory requirements are paramount when determining data retention periods. Compliance with laws such as GDPR, HIPAA, or industry-specific regulations ensures that data is retained appropriately and disposed of when no longer necessary, thereby mitigating legal risks.
Which of the following is accountable for the management of IT risk within an organization?
Senior management
Business process owners
Second line
Internal audit
The correct answer isBbecausebusiness process ownersare accountable for the management of IT risk within the organization. In CRISC, risk accountability rests with those who own the business activities and processes affected by the risk. They are responsible for ensuring that risk is identified, assessed, treated, and monitored in a way that supports business objectives.
The other options are not the best answer:
A. Senior managementapproves risk appetite, provides oversight, and signs off on plans, but accountability for specific business risk resides with the owners of the business processes and services.
C. Second lineprovides oversight, guidance, framework support, and monitoring, but does not own the risk.
D. Internal auditis independent and provides assurance; it does not manage or own IT risk.
Exact Extracts supporting the answer:
“Accountability for business risk related to IT primarily lies with users of IT services.”
“For an IT system supporting a critical business process senior managers should be accountable for the risk.”
“For an organizational business unit the most accurate description of risk-related roles and responsibilities is that the management team owns the risk and is responsible for identifying assessing and mitigating risk and reporting to the appropriate support functions and the board of directors.”
“Risk owner is a risk management role that is part of the first line of defense.”
“Operational management is the function that manages risk according to the three lines of defense model.”
Taken together, these extracts show that accountability for IT risk is assigned to the first line, meaning business and operational owners, not assurance or oversight functions. Therefore,business process ownersare accountable for management of IT risk within the organization.
===========
Which of the following would BEST enable a risk practitioner to embed risk management within the organization?
Provide risk management feedback to key stakeholders.
Collect and analyze risk data for report generation.
Monitor and prioritize risk data according to the heat map.
Engage key stakeholders in risk management practices.
Engaging key stakeholders in risk management practices is the best way to embed risk management within the organization. This means that the risk practitioner involves andcommunicates with the people who have an interest or influence in the organization’s objectives, activities, and risks, such as senior management, business unit managers, employees, customers, suppliers, regulators, etc.
Engaging key stakeholders in risk management practices helps to create a risk-aware culture, align risk management with the organization’s strategy and vision, ensure the ownership and accountability of risks and controls, obtain the support and commitment for risk management initiatives, and improve the risk management performance and outcomes.
The other options are not the best ways to embed risk management within the organization. They are either secondary or not essential for risk management.
The references for this answer are:
Risk IT Framework, page 17
Information Technology & Security, page 11
Risk Scenarios Starter Pack, page 9
What is the MOST important consideration when selecting key performance indicators (KPIs) for control monitoring?
Source information is acquired at stable cost.
Source information is tailored by removing outliers.
Source information is readily quantifiable.
Source information is consistently available.
The most important consideration when selecting KPIs for control monitoring is that the source information is consistently available, meaning that it can be obtained regularly, reliably, and timely from the same or equivalent data sources. This ensures that the KPIs can measure the performance of the controls over time and across different units or functions, and provide meaningful and comparable results. Source information that is acquired at stable cost, tailored by removing outliers, or readily quantifiable are also desirable, but not as essential as consistency.
During implementation of an intrusion detection system (IDS) to monitor network traffic, a high number of alerts is reported. The risk practitioner should recommend to:
reset the alert threshold based on peak traffic
analyze the traffic to minimize the false negatives
analyze the alerts to minimize the false positives
sniff the traffic using a network analyzer
An intrusion detection system (IDS) is a network security tool that monitors network traffic and devices for known malicious activity, suspicious activity or security policy violations1. An IDS can generate alerts when it detects any potential threats, but not all alerts are accurate or relevant. There are two types of errors that can affect the performance and reliability of an IDS: false positives and false negatives2.
A false positive is when an IDS incorrectly flags a benign or normal activity as malicious or suspicious. For example, an IDS may alert on a legitimate network scan or a harmless software update. False positives can reduce the credibility and efficiency of an IDS, as they can overwhelm the security team with unnecessary alerts, distract them from the real threats, and cause them to ignore or disable the IDS3.
A false negative is when an IDS fails to flag a malicious or suspicious activity as such. For example, an IDS may miss a stealthy or novel attack that does not match any known signatures or patterns. False negatives can compromise the security and integrity of the network, as they can allow attackers to bypass the IDS and cause damage or steal data without being detected4.
The risk practitioner should recommend to analyze the alerts to minimize the false positives, because this is the best way to improve the accuracy and usefulness of the IDS. By analyzing the alerts, the risk practitioner can:
Identify the sources and causes of the false positives, such as misconfigured or outdated IDS rules, network anomalies, or legitimate traffic that resembles malicious traffic5.
Adjust or fine-tune the IDS settings, such as the alert threshold, the sensitivity level, the detection method, or the rule base, to reduce the number of false positives without increasing the risk of false negatives.
Validate or verify the alerts with other sources of information, such as logs, network traffic analysis, or threat intelligence, to confirm or dismiss the alerts as true or false positives.
Prioritize or classify the alerts based on their severity, impact, or likelihood, to focus on the most critical or relevant alerts and avoid alert fatigue.
The other options are not the best course of action, because:
Resetting the alert threshold based on peak traffic is not a reliable or effective way to minimize the false positives, as it may also increase the risk of false negatives. The alert threshold is the level of activity or deviation that triggers an alert from the IDS. If the threshold is set too high, the IDS may miss some malicious or suspicious activity that occurs below the threshold. If the threshold is set too low, the IDS may generate too many alerts for normal or benign activity that exceeds the threshold. The optimal threshold depends on various factors, such as the network size, topology, traffic volume, and baseline. Peak traffic is not a good indicator of the optimal threshold, as it may vary depending on the time, day, or season, and it may not reflect the normal or expected network behavior.
Analyzing the traffic to minimize the false negatives is not the main issue or goal in this scenario, as the problem is the high number of alerts, not the low number of alerts. Analyzing thetraffic can help to identify the malicious or suspicious activity that the IDS may have missed, but it does not address the root cause of the false positives or improve the IDS performance. Moreover, analyzing the traffic can be time-consuming and resource-intensive, especially for large or complex networks, and it may require specialized tools or skills that the risk practitioner may not have.
Sniffing the traffic using a network analyzer is not a suitable or feasible option in this scenario, as it may violate the privacy or security policies of the network or the organization. Sniffing the traffic means capturing and inspecting the network packets that are transmitted or received by the devices on the network. A network analyzer is a tool that can perform this function and display the packet data in a readable format. However, sniffing the traffic can also expose sensitive or confidential information, such as passwords, usernames, or credit card numbers, that may be contained in the packets. Therefore, sniffing the traffic may require authorization or consent from the network owners or users, and it may be restricted or prohibited by law or regulation.
References =
What is an intrusion detection system (IDS)? - IBM
Intrusion detection system - Wikipedia
What Are Intrusion Detection Systems? - MUO
12 Best Intrusion Detection System (IDS) Software 2024 - Comparitech
What is an Intrusion Detection System (IDS)? - Fortinet
[False Positive and False Negative in Intrusion Detection System]
[False Positives and False Negatives in Intrusion Detection Systems]
[How to Reduce False Positives for Your IDS/IPS]
[How to Set the Right Alert Thresholds for Your IDS/IPS]
[Network Traffic Analysis: What It Is and How It Works]
[What is a Network Analyzer? - Definition from Techopedia]
Which of the following is the PRIMARY consideration when establishing an organization ' s risk management methodology?
Business context
Risk tolerance level
Resource requirements
Benchmarking information
The primary consideration when establishing an organization’s risk management methodology is the business context, which includes the internal and external factors that influence the organization’s objectives, strategies, scope, and boundaries. The business context helps to define the risk criteria, the risk appetite, the risk identification, the risk analysis, and the risk treatment. The other options are not the primary consideration, but rather the outcomes or inputs of the risk management methodology. References = ISO 31000 Risk Management – Principles andGuidelines; ISO 31000 Principles of Risk Management; The risk management process: What is the best structure and administration?
Which of the following introduces the GREATEST amount of risk during the software development life cycle (SDLC)?
Use of debugging tools
Incorrect firewall configuration
Inability to pass user acceptance tests (UATs)
Untested changes to production
CRISC emphasizes thatuntested changes in productionrepresent high operational risk due to potential downtime, integrity issues, or security failures.
Supporting extract:
“Untested changes to production systems introduce the greatest amount of risk because they may disrupt operations or introduce security vulnerabilities.”
UAT failureordebuggingpose limited impact confined to pre-production stages.
Hence,Dis the correct and verified answer.
CRISC Reference:Domain 2 – IT Risk Assessment, Topic: Risk in the System Development Life Cycle.
In the context of the three lines model, which of the following is responsible for providing assurance to senior management and the governing body through independent and objective reviews?
Internal auditors
Risk owners
Regulators
Risk management functions
The correct answer isAbecause in thethree lines model,internal auditorsprovide independent and objective assurance to senior management and the governing body. Their role is separate from operational risk ownership and from second-line oversight functions.
The other options are not correct:
B. Risk ownersare part of the first line and manage risk, but do not provide independent assurance.
C. Regulatorsmay perform external reviews, but they are not part of the organization’s three lines model.
D. Risk management functionsare typically part of the second line and provide oversight, not independent assurance.
Exact Extracts supporting the answer:
“The MOST significant benefit of using the three lines of defense model in a risk management framework of an enterprise is that it clarifies essential roles of the key stakeholders.”
“One of the MAIN purposes of the first line of defense in the three lines of defense model is to ensure control deficiencies are addressed.”
“Establishing a risk management framework is a direct responsibility of the second line of defense.”
“An internal audit function is best positioned to leverage the work performed in monitoring evaluating examining and reporting on controls as part of an ERM program.”
“Evaluating the effectiveness of existing internal information security controls within an enterprise is the responsibility of the system auditor.”
These extracts support that independent and objective assurance in the three lines model is provided byinternal auditors.
Which of the following is a PRIMARY objective of privacy impact assessments (PIAs)?
To identify threats introduced by business processes
To identify risk when personal information is collected
To ensure senior management has approved the use of personal information
To ensure compliance with data privacy laws and regulations
Which of the following observations should be of GREATEST concern to a risk practitioner assessing a third-party service provider for privacy risk?
Appropriate privacy training and awareness campaigns are not conducted for employees
The provider subcontracts part of the service to a fourth party
Contractual language for handling personally identifiable information (PII) is not defined.
The roles and responsibilities associated with data governance are not well defined
The correct answer is C because undefined contractual language for handling personally identifiable information (PII) is the greatest concern in a third-party privacy risk assessment. Contract terms establish the provider’s legal and operational obligations for collection, use, protection, sharing, retention, breach notification, and disposal of personal data. If these obligations are not clearly defined, the organization may be unable to enforce privacy requirements or demonstrate adequate governance over outsourced processing.
The other options are important, but not as critical as missing contractual obligations:
A. Appropriate privacy training and awareness campaigns are not conducted for employees is a control weakness, but contractual requirements come first.
B. The provider subcontracts part of the service to a fourth party is a significant concern, but it can be governed through contract language and oversight.
D. The roles and responsibilities associated with data governance are not well defined is also important, but contractual clarity over PII handling is more fundamental.
Exact Extracts supporting the answer:
“To safeguard an enterprise from issues like unbacked-up emails the best approach would be validating the company policies to the provider’s contract.”
“The most important part of any outsourcing contract is provisions to assess the compliance of the provider.”
“The most important consideration for an enterprise structuring a contract with a third party is the inclusion of a confidentiality clause.”
“The first step for a risk practitioner when an enterprise has decided to outsource all IT services and support to a third party is to ensure that security requirements are addressed in all contracts and agreements.”
“The MOST important consideration when transmitting personal information across networks is ensuring the privacy of the personal information.”
These extracts support that privacy and security obligations must be clearly established in contracts. Therefore, the greatest concern is that contractual language for handling PII is not defined .
===========
QUESTION NO: 96 [Risk Assessment]
Which of the following groups would provide the MOST relevant perspective when reporting loss exposure based on a risk analysis exercise?
A. Internal auditors
B. Senior management
C. Process owners
D. Independent risk consultants
Answer: C
The correct answer is C because process owners provide the most relevant perspective when reporting loss exposure . They understand the business process, operational dependencies, impact of disruptions, and real consequences if the risk materializes. Since loss exposure is closely tied to business impact, the people accountable for and closest to the process provide the most meaningful input.
The other options are less appropriate:
A. Internal auditors provide independent assurance, but they are not the primary source of business-impact perspective.
B. Senior management provides strategic oversight, but process owners offer more detailed and direct exposure insight.
D. Independent risk consultants may add external expertise, but not the same operational understanding of the specific process.
Exact Extracts supporting the answer:
“For an organizational business unit the most accurate description of risk-related roles and responsibilities is that the management team owns the risk and is responsible for identifying assessing and mitigating risk and reporting to the appropriate support functions and the board of directors.”
“For an IT system supporting a critical business process senior managers should be accountable for the risk.”
“The main outcome of a business impact analysis (BIA) is the criticality of business processes.”
“IT risk is measured by its impact on business operations.”
“The primary reason risk professionals conduct risk assessments is to identify risk with the highest business impact.”
These extracts support that loss exposure is best understood through the business process context, making process owners the most relevant group.
===========
QUESTION NO: 97 [Risk Response and Mitigation]
Which of the following processes is MOST helpful in proactively identifying non-compliant baseline images prior to implementing IT systems?
A. Patch management
B. Configuration management
C. Vulnerability management
D. Change management
Answer: B
The correct answer is B because configuration management is the process most directly concerned with establishing, maintaining, and validating system baselines. If the goal is to identify non-compliant baseline images before implementation, configuration management is the most helpful process because it governs approved configurations and compares actual builds to required baselines.
The other options are less appropriate:
A. Patch management focuses on updates and fixes, not full baseline compliance.
C. Vulnerability management identifies known weaknesses, but not baseline-image compliance as directly as configuration management.
D. Change management governs approval of changes, but it does not primarily validate baseline images.
Exact Extracts supporting the answer:
“The control practice related to information systems architecture that includes establishing and maintaining baselines for internally developed systems is Configuration management.”
“The MOST appropriate metric to measure how well the information security function is managing the administration of user access is percent of accounts with configurations in compliance.”
“Including thresholds that identify when controls no longer provide the intended value is essential when developing metrics to monitor the control life cycle.”
“The BEST way to identify IS control deficiencies is through defined control objectives.”
These extracts support that baseline definition and compliance checking are core configuration management activities. Therefore, the best answer is configuration management .
===========
QUESTION NO: 98 [Governance]
A risk practitioner notes that the number of unauthorized disclosures of confidential data has been increasing. Which of the following is MOST important to examine for determining the root cause?
A. Completeness of data classification schema
B. Updated regulations related to data protection
C. The volume of data loss prevention (DLP) alerts
D. Scope of security awareness training
Answer: A
The correct answer is A because the completeness of the data classification schema is the most important area to examine when determining the root cause of increasing unauthorized disclosures of confidential data. If data is not classified correctly or completely, the organization may fail to apply the right handling requirements, access restrictions, monitoring, retention, and protection controls. Classification is the foundation for protecting confidential information.
The other options are less important for root cause determination:
B. Updated regulations related to data protection may change compliance obligations, but they are not the most likely direct root cause of increased disclosures.
C. The volume of DLP alerts may reflect symptoms or detection levels, but it does not explain the underlying cause.
D. Scope of security awareness training may contribute, but it is secondary to correctly identifying and labeling sensitive data.
Exact Extracts supporting the answer:
“The PRIMARY responsibility for data classification rests with the data owner.”
“The FIRST policy that governs how information is to be protected from within the enterprise especially for a breakthrough technology is the data classification policy.”
“The MAIN benefit of information classification is that it helps select security measures proportional to risk.”
“To determine the level of protection required for securing personally identifiable information a risk practitioner should PRIMARILY consider the sensitivity property of the information.”
“The person responsible for ensuring that information is classified is the data owner.”
These extracts directly support that classification drives protection requirements. Therefore, the most important area to examine is the completeness of the data classification schema .
===========
QUESTION NO: 99 [Governance]
Which of the following BEST enables the classification of controls in a risk taxonomy?
A. Hiring external consultants
B. Adopting standards and frameworks
C. Reviewing security policies periodically
D. Performing internal and external audits
Answer: B
The correct answer is B because adopting standards and frameworks best enables the classification of controls in a risk taxonomy. Standards and frameworks provide structured categories, common terminology, and organized control domains that make it possible to classify controls consistently across the enterprise.
The other options are less appropriate:
A. Hiring external consultants may help with implementation, but does not itself provide the classification structure.
C. Reviewing security policies periodically supports maintenance, but not the foundational taxonomy.
D. Performing internal and external audits evaluates controls, but does not define their classification model.
Exact Extracts supporting the answer:
“To best support IT in fulfilling business requirements an internal control system or framework is essential.”
“An enterprise-wide risk management framework is adopted to enable a consistent approach to risk response throughout the enterprise.”
“When many corporate IT standards are outdated the best course of action is to review the standards against current requirements and determine their adequacy.”
“The BEST way to identify IS control deficiencies is through defined control objectives.”
These extracts support that frameworks and standards provide the necessary structure and consistency for organizing and classifying controls. Therefore, the best answer is adopting standards and frameworks .
An organization plans to provide specific cloud security training for the IT team to help manage risks associated with cloud technology. This response is considered risk:
Transfer
Mitigation
Acceptance
Deferral
Risk mitigationinvolves implementing measures to reduce either the likelihood or impact of a risk.
By providingtargeted training, the organization increases staff capability, thereby reducing thelikelihoodof misconfigurations or compliance errors in cloud usage.
ISACA defines mitigation as:
“Implementing controls or training to reduce exposure to risk within acceptable levels.”
ATransfer = insurance or outsourcing.
CAcceptance = no action.
DDeferral = postponing response.
Hence,B. Mitigationis correct.
CRISC Reference:Domain 3 – Risk Response and Mitigation, Topic: Risk Response Options.
Which of the following activities should be performed FIRST when establishing IT risk management processes?
Collect data of past incidents and lessons learned.
Conduct a high-level risk assessment based on the nature of business.
Identify the risk appetite of the organization.
Assess the goals and culture of the organization.
According to the Guide to Implementing an IT Risk Management Framework, the first activity that should be performed when establishing IT risk management processes is to assess the goals and culture of the organization. This is because the goals and culture of the organization define the context and scope of the IT risk management process, and influence the risk appetite and tolerance of the organization. By assessing the goals and culture of the organization, the IT risk manager can align the IT risk management process with the organization’s strategy, vision, mission, values, and objectives. The IT risk manager can also identify the key stakeholders, roles, and responsibilities involved in the IT risk management process, and ensure that they have the necessary skills, knowledge, and resources to perform their tasks effectively. Additionally, the IT risk manager can establish the communication and reporting mechanisms for the IT risk management process, and ensure that they are consistent with the organization’s culture and expectations. References = Guide to Implementing an IT Risk Management Framework, An Overview of the Risk Management Process
An organization has just recovered from an incident involving a new zero-day exploit that utilizes a unique entry point into its systems. Which of the following should the risk team do NEXT as a result of a post-mortem review?
Revise the risk appetite to account for this zero-day exploit
File a claim against the organization ' s cyber insurance policy
Update the risk events to ensure they cover this new exploit.
Notify customers affected by the attack
The correct answer is C because after a post-mortem review of a new zero-day exploit, the risk team should update the risk events / risk scenarios so future assessments and monitoring reflect this newly observed threat pattern and attack path. A post-incident review should strengthen the organization’s risk knowledge base and ensure similar events are represented in scenario development, assessment, and monitoring.
The other options are less appropriate as the next risk-team action:
A. Revise the risk appetite is too high-level and would not normally change because of one exploit.
B. File a claim against the organization ' s cyber insurance policy may be handled separately, but it is not the main risk management follow-up from the review.
D. Notify customers affected by the attack may be necessary operationally or legally, but the question asks what the risk team should do next as a result of the post-mortem review.
Exact Extracts supporting the answer:
“After a security incident the first step toward yielding an actionable plan that effectively mitigates the risk is root cause analysis.”
“The BEST way to verify that critical production servers are using up-to-date antivirus signature files is to Check a sample of servers.”
“The BEST way for an incident response team to identify the source of a malware attack to reduce the likelihood of recurrence is through Root cause analysis.”
“Risk scenarios enable the risk assessment process because they help estimate the frequency and impact of risk.”
“An emerging risk should be added to the risk register by the risk practitioner when the activity that triggers the risk initiates.”
These extracts support that once a new exploit pattern is identified, the organization should incorporate it into future risk analysis through updated risk events or scenarios.
===========
QUESTION NO: 116 [Risk Response and Mitigation]
Which of the following is the MOST effective way to help ensure a risk treatment plan remains on track?
A. Assigning sufficient resources to implement the plan
B. Requiring approval by the second line of defense
C. Adopting an Agile project management approach
D. Documenting risk treatment procedures for relevant stakeholders
Answer: A
The correct answer is A because a risk treatment plan is most likely to remain on track when sufficient resources are assigned to implement it. Even a well-designed treatment plan will fail if there are not enough people, budget, time, or technical capability to execute the required actions.
The other options are less effective:
B. Requiring approval by the second line of defense may provide oversight, but it does not keep execution on track.
C. Adopting an Agile project management approach may help delivery in some cases, but it is not the primary factor.
D. Documenting risk treatment procedures for relevant stakeholders is useful, but documentation alone does not ensure execution.
Exact Extracts supporting the answer:
“The most important information to include in a risk treatment plan that already has an appropriate resolution and a date for completion is responsible personnel.”
“The greatest benefit of implementing a risk treatment plan is to reduce the impact and likelihood of risk occurrence.”
“Risk treatment plans are necessary to describe how the chosen treatment options will be implemented.”
“In the event that available resources for risk treatment are not sufficient the risk treatment plan should define the priorities across all treatments to assist in resource allocation.”
“A risk treatment plan should primarily specify the responsibility for implementing the chosen risk treatment.”
These extracts support that implementation success depends heavily on responsibility and resource allocation. Therefore, the most effective way to keep the plan on track is assigning sufficient resources .
===========
QUESTION NO: 117 [Risk Response and Mitigation]
In the context of business continuity management, which of the following does the maximum allowable downtime represent?
A. The maximum time required to recover all critical systems to full operational capacity after a disaster
B. The maximum data loss an organization can tolerate during a disaster
C. The maximum length of time that a business can be disrupted before significant harm occurs
D. The maximum time required to initiate the disaster recovery plan (DRP)
Answer: C
The correct answer is C because maximum allowable downtime refers to the longest period a business process can remain unavailable before unacceptable damage occurs to the organization. It is a business-driven continuity threshold tied to process criticality and disruption impact.
The other options are incorrect:
A. The maximum time required to recover all critical systems to full operational capacity after a disaster is closer to a recovery objective, not maximum allowable downtime.
B. The maximum data loss an organization can tolerate during a disaster describes recovery point objective (RPO), not downtime.
D. The maximum time required to initiate the disaster recovery plan (DRP) is not what maximum allowable downtime means.
Exact Extracts supporting the answer:
“A business impact analysis is primarily used to evaluate the impact of disruption on an enterprise’s ability to operate over time.”
“The objective of a business impact analysis is best described as the identification of time-sensitive critical business functions and interdependencies.”
“The main outcome of a business impact analysis (BIA) is the criticality of business processes.”
“The most useful process in developing a series of recovery time objectives is business impact analysis.”
These extracts support that continuity downtime thresholds are defined by business impact and process criticality. Therefore, the correct answer is C , not D.
===========
QUESTION NO: 118 [Risk Response and Mitigation]
Which of the following is MOST important to consider when developing mitigation measures for a risk treatment plan?
A. Risk register ratings
B. Control implementation plan
C. Supplier capabilities
D. Cost-benefit analysis
Answer: D
The correct answer is D because the most important consideration when developing mitigation measures for a risk treatment plan is cost-benefit analysis . In CRISC, mitigation options should be selected based on whether the expected reduction in risk justifies the cost of implementing and operating the control or response.
The other options are less important as the primary consideration:
A. Risk register ratings are useful inputs, but they do not by themselves determine which mitigation is appropriate.
B. Control implementation plan comes after deciding what mitigation is justified.
C. Supplier capabilities may matter in some situations, but not as the main decision factor across treatment planning.
Exact Extracts supporting the answer:
“To best help finalize the risk treatment plan a cost-benefit analysis should be used.”
“The best help for an enterprise to select an appropriate risk response is an analysis of control costs and benefits.”
“The cost of mitigating a risk should not exceed the expected benefit to be derived.”
“The most important activity in determining the risk mitigation strategy is performing a cost-benefit analysis related to risk acceptance.”
“The MAIN reason a cost-benefit analysis in risk response planning is performed is to identify the right controls to address risks at acceptable levels within the budget.”
These extracts directly support that cost-benefit analysis is the most important consideration when developing mitigation measures for a risk treatment plan.
A company has recently acquired a customer relationship management (CRM) application from a certified software vendor. Which of the following will BE ST help lo prevent technical vulnerabilities from being exploded?
implement code reviews and Quality assurance on a regular basis
Verity me software agreement indemnifies the company from losses
Review the source coda and error reporting of the application
Update the software with the latest patches and updates
The best way to prevent technical vulnerabilities from being exploited is to update the software with the latest patches and updates. Patches and updates are software modifications that fix the known bugs, errors, or flaws in the software. They also improve the performance, functionality, and security of the software. By updating the software with the latest patches and updates, the company can reduce the exposure and likelihood of the technical vulnerabilities, and protect the software from potential attacks or exploits. The other options are not as effective as updating the software with the latest patches and updates, as they are related to the quality assurance, legal protection, or error handling of the software, not the prevention or mitigation of the technical vulnerabilities. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.3: IT Risk Response Implementation, page 145.
Which of the following would be a risk practitioner ' s GREATEST concern with the use of a vulnerability scanning tool?
Increased time to remediate vulnerabilities
Inaccurate reporting of results
Increased number of vulnerabilities
Network performance degradation
The greatest concern for a risk practitioner with the use of a vulnerability scanning tool is the inaccurate reporting of results. A vulnerability scanning tool is a software that scans the network or system for known vulnerabilities and generates a report of the findings. However, the tool may produce false positives (reporting vulnerabilities that do not exist) or false negatives (missing vulnerabilities that do exist). This can lead to incorrect risk assessment, ineffective risk response, and wasted resources. Increased time to remediate vulnerabilities, increased number of vulnerabilities, and network performance degradation are other possible concerns, but they are not as critical as the inaccurate reporting of results. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 7; CRISC Review Manual, 6th Edition, page 202.
An organization uses a vendor to destroy hard drives. Which of the following would BEST reduce the risk of data leakage?
Require the vendor to degauss the hard drives
Implement an encryption policy for the hard drives.
Require confirmation of destruction from the IT manager.
Use an accredited vendor to dispose of the hard drives.
Data leakage is the unauthorized or accidental disclosure of sensitive or confidential data to unauthorized parties. Data leakage can cause serious damages or losses to the organization, such as data breaches, fines, lawsuits, reputational harm, or loss of customer trust. Data leakage can occur due to various reasons, such as human errors, malicious attacks, or inadequate controls1.
An organization that uses a vendor to destroy hard drives faces a risk of data leakage, as the vendor may not properly or securely destroy the hard drives, or may access or misuse the data stored on them. The best way to reduce this risk is to use an accredited vendor to dispose of the hard drives, because it means that the vendor:
Has been certified or verified by a reputable or recognized authority or organization, such as ISACA, NAID, or R2, to provide hard drive destruction services
Follows the industry standards and best practices for hard drive destruction, such as NIST 800-88 or DoD 5220.22-M, and ensures the compliance with the legal and regulatory requirements, such as HIPAA, PCI DSS, or GDPR
Provides a secure and transparent process for hard drive destruction, such as using a specialized shredder, issuing a certificate of destruction, or allowing the customer to witness the destruction
Maintains a high level of professionalism and integrity, and does not compromise the confidentiality or security of the customer’s data234
The other options are not the best ways to reduce the risk of data leakage, but rather some of the steps or aspects of hard drive destruction. Require the vendor to degauss the hard drives is a step that can help to erase the data on the hard drives by using a strong magnetic field. However,degaussing may not be effective or reliable for some types of hard drives, such as solid state drives (SSDs), and it may not prevent the vendor from accessing or misusing the data before degaussing5. Implement an encryption policy for the hard drives is an aspect that can help to protect the data on the hard drives by using a cryptographic algorithm to make it unreadable without a key. However, encryption may not be sufficient or applicable for some types of data, such as metadata, and it may not prevent the vendor from accessing or misusing the key or the encrypted data6. Require confirmation of destruction from the IT manager is a step that can help to verify that the hard drives have been destroyed by the vendor, and to document the process and the outcome. However, confirmation of destruction may not be accurate or authentic, and it may not prevent the vendor from accessing or misusing the data before destruction7. References =
Data Leakage - ISACA
Hard Drive Shredding Services | Hard Drive Destruction & Disposal
Hard Drive Shredding and Destruction Service | CompuCycle
Electronic Destruction & Recycling | Shred Nations
Degaussing - ISACA
Encryption - ISACA
Certificate of Destruction - ISACA
[CRISC Review Manual, 7th Edition]
The GREATEST benefit of introducing continuous monitoring to an IT control environment is that it:
Enables the collection of benchmarking data.
Helps to obtain buy-in for future IT investments.
Enables timely detection of emerging risk.
Identifies stakeholders involved in the process.
The correct answer is C because continuous monitoring is intended to detect changes in the risk and control environment quickly enough for management to respond. The uploaded CRISC notes state that “the most significant benefit of implementing a continuous risk management process” is that it captures changes to the enterprise risk profile, and that a main purpose of continuous monitoring is detecting changes to the enterprise’s risk environment.
A, B, and D may be secondary benefits, but they are not the greatest benefit. Benchmarking, investment support, and stakeholder identification do not provide the same direct risk-management value as timely detection of emerging risk.
===========
A risk practitioner has been tasked with conducting a risk identification workshop with stakeholders to compile an IT risk profile. Which of the following would be MOST helpful in the brainstorming phase of this exercise?
List of issues and events from the risk register.
Internal audit reports with adverse findings.
IT control assessment results and trends.
Key risk indicators (KRIs) outside of appetite.
The BEST answer is A because a risk register is the direct repository of identified risk, issues, scenarios, impact, probability, mitigation action, and ownership. For a brainstorming workshop to compile an IT risk profile, previous issues and events from the risk register provide the most relevant starting point for identifying and discussing risk scenarios. The uploaded CRISC notes state that the risk register includes “risk scenario, date, description, impact, probability, risk score, mitigation action and owner,” and that preparation of a risk register begins in the risk identification process. They also state that the risk register is maintained as a repository of identified risk for decision-making.
ISACA’s CRISC outline places Risk Events , Risk Scenario Development and Evaluation , and Risk Register under Domain 2: Risk Assessment, supporting that this is a risk identification/risk assessment activity.
B, C, and D are useful inputs, but they are narrower. Audit findings and control assessment results focus mainly on control weaknesses, while KRIs outside appetite indicate monitored risk conditions. The risk register is broader and more directly aligned to brainstorming an IT risk profile.
===========
A zero-day vulnerability has been discovered in a globally used brand of hardware server that allows hackers to gain
access to affected IT systems. Which of the following is MOST likely to change as a result of this situation?
Control effectiveness
Risk appetite
Risk likelihood
Key risk indicator (KRI)
The most likely factor to change as a result of a zero-day vulnerability being discovered in a globally used brand of hardware server that allows hackers to gain access to affected IT systems is the risk likelihood. Risk likelihood is the probability or frequency of a risk event occurring, or the possibility of a risk event occurring within a given time period. Risk likelihood is one of the key dimensions of risk analysis, along with the risk impact. Risk likelihood helps to determine the severity and priority of the risk, and to select the most appropriate and effective risk response. Risk likelihood also helps to evaluate the cost-benefit and trade-off of the risk response, and to measure the residual risk and the risk performance. The risk likelihood is likely to change as a result of a zero-day vulnerability, because a zero-day vulnerability is a security flaw that has been discovered but not yet patched by the vendor, which means that it can be exploited by hackers before the affected systems can be updated or protected. A zero-day vulnerability increases the risk likelihood, because it creates a window of opportunity for hackers to launch attacks that could compromise the affected systems, and because it may not be detected or prevented by the existing security controls or measures. The other options are not as likely to change as the risk likelihood, although they may also be affected or influenced by the zero-day vulnerability. Control effectiveness, risk appetite, and key risk indicator (KRI) are all factors that could change as a result of a zero-day vulnerability, but they are not the most likely factor to change. Control effectiveness is the extent to which the risk controls or responses achieve the intended risk objectives or outcomes. Control effectiveness could change as a result of a zero-day vulnerability, because the existing controls may not be able to detect or prevent the exploitation of the vulnerability, or because new or additional controls may be needed to address the vulnerability. However, control effectiveness is not the most likely factor to change, because it depends on the type and level of the controls that are already in place or that can be implemented, and because it may not change until the vulnerability is actually exploited or the risk response is executed. Risk appetite is the amount and type of risk that the organization is willing to accept or pursue in order to achieve its objectives. Risk appetite could change as a result of a zero-day vulnerability, because the vulnerability could affect the organization’s objectives or operations, and because the organization may need to adjust its risk tolerance or threshold to cope with the vulnerability. However, risk appetite is not the most likely factor to change, because it is a strategic and long-term decision that is driven by the organization’s mission, vision, values, and strategy, and because it may not change until the vulnerability is resolved or the risk impact is realized. Key risk indicator (KRI) is a metric that measures thelikelihood and impact of risks, and helps monitor and prioritize the most critical risks. KRI could change as a result of a zero-day vulnerability, because the vulnerability could increase the likelihood and impact of the risks, and because the organization may need to update or revise its KRI to reflect the current risk situation. However, KRI is not the most likely factor to change,because it is a monitoring and reporting tool that is derived from the risk analysis and response, and because it may not change until the vulnerability is exploited or the risk response is implemented. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-25.
Which of the following would be MOST helpful to an information security management team when allocating resources to mitigate exposures?
Relevant risk case studies
Internal audit findings
Risk assessment results
Penetration testing results
The most helpful factor for an information security management team when allocating resources to mitigate exposures is the risk assessment results. The risk assessment results provide a comprehensive and objective analysis of the risks facing the enterprise, including their likelihood, impact, and root causes. The risk assessment results also help to identify the gaps and weaknesses in the existing controls, and to prioritize the risks based on their severity and urgency. The risk assessment results enable the information security management team toallocate the resources in a cost-effective and risk-based manner, and to implement the most appropriate risk responses to reduce the exposures to an acceptable level. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.1.1, page 1751
When reviewing management ' s IT control self-assessments, a risk practitioner noted an ineffective control that links to several low residual risk scenarios. What should be the NEXT course of action?
Assess management ' s risk tolerance.
Recommend management accept the low-risk scenarios.
Propose mitigating controls
Re-evaluate the risk scenarios associated with the control
IT control self-assessments are techniques that involve identifying and evaluating the effectiveness and efficiency of the IT controls that are designed and implemented to mitigate the IT risks, by the managers and staff within the organization12.
An ineffective control is a control that does not achieve its intended objective or purpose, or does not operate as designed or expected34.
A low residual risk scenario is a situation or occurrence that has a low likelihood and impact of affecting the organization’s objectives, performance, or value creation, after considering the existing controls and their effectiveness56.
The next course of action when reviewing management’s IT control self-assessments and noting an ineffective control that links to several low residual risk scenarios is to recommend management accept the low-risk scenarios, which is a risk response strategy that involves acknowledging and tolerating the level of risk exposure, and not taking any further action to reduce or eliminate it78.
Recommending management accept the low-risk scenarios is the next course of action because it is the most cost-effective and reasonable option, given that the level of risk exposure is low andacceptable, and the cost and effort of implementing or improving the control may outweigh the potential benefits or value78.
Recommending management accept the low-risk scenarios is also the next course of action because it is consistent with the risk management process and objectives, which are to identifyand address the risks that may affect the achievement of the organization’s goals and the delivery of value to the stakeholders, and to optimize the balance between risk and reward78.
The other options are not the next course of action, but rather possible alternatives or steps that may be considered or followed in different circumstances or scenarios. For example:
Assessing management’s risk tolerance is a step that involves determining and communicating the acceptable or tolerable level of risk exposure for the organization or its business units, based on the organization’s risk appetite, criteria, and objectives78. However, this stepis not the next course of action because it is usually done before or during the risk assessment process, and not after noting an ineffective control that links to several low residual risk scenarios78.
Proposing mitigating controls is a course of action that involves suggesting or recommending additional or alternative controls that can reduce or eliminate the level of risk exposure, and improve the effectiveness and efficiency of the risk management process78. However, this course of action is not the next course of action because it is not necessary or appropriate for low residual risk scenarios, as the cost and effort of implementing or improving the controls may outweigh the potential benefits or value78.
Re-evaluating the risk scenarios associated with the control is a course of action that involves revising and updating the likelihood and impact of the risk scenarios, and the level of risk exposure or tolerance for the organization, based on the current or changed conditions or factors that influence the risk landscape78. However, this course of action is not the next course of action because it is not required or relevant for low residual risk scenarios, as the level of risk exposure is already low and acceptable, and the ineffective control does not significantly affect the risk assessment78. References =
1: Control Self Assessments - PwC1
2: Control self-assessment - Wikipedia2
3: Ineffective Controls: What They Are and How to Identify Them3
4: Ineffective Controls: What They Are and How to Identify Them4
5: Residual Risk - Definition and Examples5
6: Residual Risk: Definition, Formula & Management6
7: Risk IT Framework, ISACA, 2009
8: IT Risk Management Framework, University of Toronto, 2017
Which of the following proposed benefits is MOST likely to influence senior management approval to reallocate budget for a new security initiative?
Reduction in the number of incidents
Reduction in inherent risk
Reduction in residual risk
Reduction in the number of known vulnerabilities
The proposed benefit that is most likely to influence senior management approval to reallocate budget for a new security initiative is the reduction in residual risk, as it indicates the expected value and outcome of the initiative in terms of reducing the risk exposure and impact to the level that is aligned with the risk tolerance and appetite of the organization. The other options are not the most likely benefits, as they may not reflect the actual or optimal risk reduction, or may not be relevant or measurable for the senior management, respectively. References = CRISC Review Manual, 7th Edition, page 111.
Which of We following is the MOST effective control to address the risk associated with compromising data privacy within the cloud?
Establish baseline security configurations with the cloud service provider.
Require the cloud prowler 10 disclose past data privacy breaches.
Ensure the cloud service provider performs an annual risk assessment.
Specify cloud service provider liability for data privacy breaches in the contract
Specifying cloud service provider liability for data privacy breaches in the contract is the most effective control to address the risk associated with compromising data privacy within the cloud, because it establishes the roles and responsibilities of the cloud service provider and the customer in case of a data breach, and defines the compensation or remediation measures that the cloud service provider should provide. This control also creates an incentive for the cloud service provider to implement adequate security measures to protect the customer’s data and comply with the relevant laws and regulations. The other options are not the most effective controls, although they may also be helpful in reducing the risk of data privacy breaches. Establishing baseline security configurations with the cloud service provider, requiring the cloud service provider to disclose past data privacy breaches, and ensuring the cloud service provider performs an annual risk assessment are examples of preventive or detective controls that aim to reduce the likelihood or impact of a data breach, but they do not address the accountability or liability of the cloud service provider in case of a data breach. References = CRISC: Certified in Risk & Information Systems Control Sample Questions
Which of the following provides the BEST assurance of the effectiveness of vendor security controls?
Review vendor control self-assessments (CSA).
Review vendor service level agreement (SLA) metrics.
Require independent control assessments.
Obtain vendor references from existing customers.
The best way to provide assurance of the effectiveness of vendor security controls is to require independent control assessments. Independent control assessments are evaluations of thevendor’s security controls by a third-party auditor or assessor, such as an external auditor, a certification body, or a testing laboratory. Independent control assessments provide an objective and unbiased opinion on the adequacy and performance of the vendor’s security controls, as well as the compliance with relevant standards and regulations. Independent control assessments can also provide evidence and assurance to the customers of the vendor’s security posture and capabilities. Reviewing vendor control self-assessments (CSA), vendor service level agreement(SLA) metrics, or vendor references from existing customers are not as reliable or credible as independent control assessments, because they may be biased, incomplete, or outdated.
Of the following, whose input is ESSENTIAL when developing risk scenarios for the implementation of a third-party mobile application that stores customer data?
Information security manager
IT vendor manager
Business process owner
IT compliance manager
An organization learns of a new ransomware attack affecting organizations worldwide. Which of the following should be done FIRST to reduce the likelihood of infection from the attack?
Identify systems that are vulnerable to being exploited by the attack.
Confirm with the antivirus solution vendor whether the next update will detect the attack.
Verify the data backup process and confirm which backups are the most recent ones available.
Obtain approval for funding to purchase a cyber insurance plan.
The first step to reduce the likelihood of infection from the attack is to identify systems that are vulnerable to being exploited by the attack. This would help the organization to assess the scope and severity of the risk, and to prioritize the systems that need immediate protection. Identifying systems that are vulnerable to being exploited by the attack would also help the organization to apply the appropriate patches, updates, or configurations to prevent or mitigate the attack, and to isolate or disconnect the systems that are already infected or compromised. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.2, page 60123
Which of the following is the PRIMARY objective of engaging key stakeholders in the IT risk assessment process?
Reducing the time required for risk analysis
Increasing the quality of analysis
Building a risk aware culture
Ensuring proper budget allocation for risk remediation
The correct answer isBbecause engaging key stakeholders in the IT risk assessment process primarily improves thequality of analysis. Stakeholders provide business context, operational knowledge, and understanding of risk impacts, dependencies, and priorities. This leads to more accurate and relevant risk assessment results.
The other options are less appropriate:
A. Reducing the time required for risk analysisis not the primary objective.
C. Building a risk aware cultureis a valuable secondary benefit, but not the main reason for engagement in the assessment process.
D. Ensuring proper budget allocation for risk remediationmay result later, but not the primary objective of stakeholder involvement.
Exact Extracts supporting the answer:
“To ensure the overall effectiveness of a risk management program it is essential to have the participation of relevant stakeholders.”
“An interdisciplinary team within the enterprise offers the best perspective on risk management to employees and stakeholders.”
“The BEST approach when developing risk scenarios for an enterprise is to use both the top-down and the bottom-up approach because they have different perspectives.”
“The PRIMARY result of a risk assessment process is input for risk-aware decisions.”
These extracts show that stakeholder engagement is primarily valuable because it improves the completeness, relevance, and quality of risk analysis.
===========
What can be determined from the risk scenario chart?
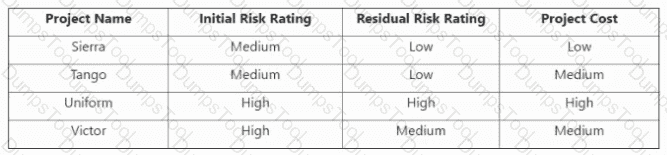
Relative positions on the risk map
Risk treatment options
Capability of enterprise to implement
The multiple risk factors addressed by a chosen response
The risk scenario chart shows the initial and residual risk ratings, and the project cost, for four projects named Sierra, Tango, Uniform, and Victor. The initial risk rating is the level of risk before applying any controls or mitigation measures, while the residual risk rating is the level of risk after applying the controls or measures. The project cost is the amount of resources required to implement the project. These three factors can be used to determine the relative positions of the projects on a risk map, which is a graphical tool for displaying the risks based on their impact and likelihood. The risk map can help to prioritize and compare the risks, and to select the most appropriate risk response strategy. The other options are not the best answers, as they are not directly shown or derived from the risk scenario chart. The risk treatment options are the possible actions that can be taken to address the risks, such as accept, avoid, mitigate, or transfer. The capability of enterprise to implement is the ability of the organization to execute the risk response plan,considering the available resources, skills, and constraints. The multiple risk factors addressed by a chosen response are the various elements that contribute to or affect the risk, such as the threat sources, events, vulnerabilities, assets, and impacts. These factors are not explicitly stated or measured in the risk scenario chart, and may require further analysis or information. References = How to Write Strong Risk Scenarios and Statements - ISACA; Identifying the Right Risk Scenarios to Measure with FAIR; How to write good risk scenarios and statements
What should be the PRIMARY objective for a risk practitioner performing a post-implementation review of an IT risk mitigation project?
Documenting project lessons learned
Validating the risk mitigation project has been completed
Confirming that the project budget was not exceeded
Verifying that the risk level has been lowered
A post-implementation review (PIR) is a process to evaluate whether the objectives of the project were met and whether the project delivered the expected benefits and outcomes1. The primary objective of a risk practitioner performing a PIR of an IT risk mitigation project is to verify that the risk level has been lowered as a result of the project implementation2. This can be done by comparing the actual risk level with theexpected risk level, assessing the effectiveness and efficiency of the risk mitigation controls, and identifying any residual or emergingrisks3. Documenting project lessons learned, validating the project completion, and confirming the project budget are important aspects of a PIR, but they are not the primary objective for a risk practitioner, as they do not directly measure the impact of the project on the risk level4. References = Risk and Information Systems Control Study Manual, Chapter 5: Risk Response and Mitigation, Section 5.4: Post-Implementation Review, pp. 239-241.
An IT risk threat analysis is BEST used to establish
risk scenarios
risk maps
risk appetite
risk ownership.
An IT risk threat analysis is best used to establish risk scenarios. A risk scenario is a description of a possible event or situation that may affect the achievement of the IT objectives. A riskscenario consists of three elements: a threat, a vulnerability, and an impact. A threat is a potential cause of an unwanted incident. A vulnerability is a weakness or flaw that can be exploited by a threat. An impact is the consequence or effect of the incident on the IT objectives. An IT risk threat analysis is a technique that identifies and evaluates the threats that may pose a risk to the IT assets and processes. An IT risk threat analysis can help to establish risk scenarios by providing the information and context for the threat element of the risk scenario. The other options are not as directly related to an IT risk threat analysis, as they are related to the outcomes, measures, or responsibilities of the IT risk management process, not the inputs or sources of the IT risk scenarios. References = Risk and Information Systems Control Study Manual, Chapter 1: IT Risk Identification, Section 1.3: IT Risk Scenarios, page 23.
A risk practitioner can use an organization ' s problem management process to anticipate potential risk within IT systems by:
conducting regular user satisfaction surveys to gather feedback on system performance.
continuously monitoring system metrics to identify performance issues.
analyzing incident trends to identify underlying issues that could lead to system failures.
implementing security patches and updates to prevent vulnerabilities from being exploited.
The correct answer isCbecause problem management helps anticipate potential risk byanalyzing incident trends to identify underlying issuesbefore they lead to more serious failures. Problem management is concerned with identifying recurring causes and systemic weaknesses, which makes it useful for anticipating future IT risk.
The other options are less accurate:
A. conducting regular user satisfaction surveysprovides feedback, but does not directly anticipate system risk.
B. continuously monitoring system metricsis useful, but that is more aligned with operational monitoring than problem management.
D. implementing security patches and updatesis a treatment activity, not the predictive use of problem management.
Exact Extracts supporting the answer:
“To determine the factors responsible for a loss event a risk professional should use cause-and-effect analysis.”
“After a security incident the first step toward yielding an actionable plan that effectively mitigates the risk is root cause analysis.”
“The risk register is the best tool for identifying changes in an enterprise’s risk profile.”
“The main purpose of continuous monitoring is detecting changes to the enterprise’s risk environment.”
These extracts support that identifying root causes and recurring incident patterns is the best way to anticipate future IT system risk.
===========
Who should be responsible for strategic decisions on risk management?
Chief information officer (CIO)
Executive management team
Audit committee
Business process owner
Strategic decisions on risk management are the decisions that involve setting the direction, objectives, and priorities for risk management within an organization, as well as aligning them with the organization’s overall strategy, vision, and mission1. Strategic decisions on riskmanagement also involve defining the organization’s risk appetite and tolerance, which are the amount and level of risk that the organization is willing and able to accept to achieve its goals2. The responsibility for strategic decisions on risk management should belong to the executive management team, which is the group of senior leaders who have the authority and accountability for the organization’s performance and governance3. The executive management team has the best understanding of the organization’s strategic context, environment, and stakeholders, and can make informed and balanced decisions that consider the benefits and costsof risk-taking4. The executive management team also has the ability and responsibility to communicate and cascade the strategic decisions on risk management to the rest of the organization, and to monitor and evaluate their implementation and outcomes5. The chief information officer (CIO), the audit committee, and the business process owner are not the best choices for being responsible for strategic decisions on risk management, as they do not have the same level of authority and accountability as the executive management team. The CIO is the senior leader who oversees the organization’s information andtechnology strategy, resources, and systems6. The CIO may be involved in providing input and feedback to the executive management team on the strategic decisions on risk management, especially those related to IT risk, but they do not have the final say or the overall responsibility for them. The audit committee is a subcommittee of the board of directors that oversees the organization’s financial reporting, internal controls, and external audits7. The audit committee may be involved in reviewing and approving the strategic decisions on risk management, as well as ensuring their compliance with the relevant laws and standards, but they do not have the authority or the expertise to make or implement them. The business process owner is the person who has the authority and accountability for a business process that supports or enables the organization’s objectives and functions. The business process owner may be involved in executing and reporting on the strategic decisions on risk management, as well as identifying and mitigating the risks related to their business process, but they do not have the perspective or the influence to make or communicate them. References = 1: Strategic Risk Management: Complete Overview (With Examples)2: [Risk Appetite and Tolerance - ISACA] 3: [Senior Management - Definition, Roles andResponsibilities] 4: Stanford Strategic Decision and Risk Management | Stanford Online5: A 7-Step Process for Strategic Risk Management — RiskOptics - Reciprocity6: [Chief Information Officer (CIO) - Gartner ITGlossary] 7: [Audit Committee - Overview, Functions, and Responsibilities] : [Business Process Owner - Gartner IT Glossary] : [Business Process Owner - Roles and Responsibilities] : [Risk and Information Systems Control Study Manual, Chapter 1: IT Risk Identification, Section 1.1: IT Risk Concepts, pp. 17-19.]
Which of the following is MOST important when developing key risk indicators (KRIs)?
Alignment with regulatory requirements
Availability of qualitative data
Properly set thresholds
Alignment with industry benchmarks
The most important factor when developing key risk indicators (KRIs) is to properly set thresholds, which are the predefined values or ranges that indicate the acceptable or unacceptable level of risk1. Thresholds can help to:
Trigger alerts or actions when the risk level exceeds or falls below the threshold, and enable timely and appropriate risk responses2.
Measure and monitor the performance and effectiveness of the risk responses, and ensure that the residual risk is within the risk appetite and tolerance3.
Communicate and report the risk status and performance to the stakeholders, and facilitate the decision-making and accountability for the risk management4.
The other factors are not the most important when developing KRIs, because:
Alignment with regulatory requirements is a necessary but not sufficient factor when developing KRIs, as it ensures that the KRIs comply with the applicable laws, rules, or standards that govern the organization’s activities and operations5. However, alignment with regulatory requirements does not guarantee that the KRIs are relevant and useful for the organization’s specific risk profile and objectives.
Availability of qualitative data is a desirable but not essential factor when developing KRIs, as it provides additional information or insights that may not be captured by quantitative data, such as opinions, perceptions, or feedback. However, availability of qualitative data does not ensure that the KRIs are reliable and consistent, as qualitative data may be subjective and difficult to measure and compare.
Alignment with industry benchmarks is a useful but not critical factor when developing KRIs, as it provides a reference or a standard for comparing the organization’s risk level and performance with its peers or competitors. However, alignment with industry benchmarks does not ensure that the KRIs are suitable and feasible for the organization’s specific context and capabilities.
References =
Threshold - CIO Wiki
Risk Thresholds: How to Set Them and When to Use Them - ProjectManager.com
Risk Appetite and Tolerance - CIO Wiki
Risk Reporting - CIO Wiki
Regulatory Compliance - CIO Wiki
[Regulatory Risk - CIO Wiki]
[Qualitative Data - CIO Wiki
During which phase of the system development life cycle (SDLC) should information security requirements for the implementation of a new IT system be defined?
Monitoring
Development
Implementation
Initiation
Information security requirements should be defined during theInitiationphase of the SDLC. This ensures that security is integrated into the design from the beginning, minimizing vulnerabilities and aligning security measures with business requirements. Early identification of security needs reduces rework and costs associated with later stages.
An organization is concerned that its employees may be unintentionally disclosing data through the use of social media sites. Which of the following will MOST effectively mitigate tins risk?
Requiring the use of virtual private networks (VPNs)
Establishing a data classification policy
Conducting user awareness training
Requiring employee agreement of the acceptable use policy
The most effective way to mitigate the risk of unintentional data disclosure through the use of social media sites is to conduct user awareness training. User awareness training is a process of educating and informing the users about the security policies, procedures, and practices that are relevant and applicable to their roles and responsibilities. User awareness training can help to increase the knowledge, understanding, and compliance of the users regarding the data protection and privacy requirements, and the potential risks and consequences of data disclosure through social media sites. User awareness training can also help to influence the behavior, attitude, and culture of the users toward data security and privacy. The other options are not as effective as conducting user awareness training, as they are related to the technical, procedural, or contractual measures to mitigate the risk, not the human or behavioral measures to mitigate the risk. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.3: IT Risk Response Implementation, page 145.
when developing IT risk scenarios associated with a new line of business, which of the following would be MOST helpful to review?
Organizational threats
Resource allocation plan
Competitor analysis
Cost-benefit analysis
Which of the following is the MOST effective way to mitigate identified risk scenarios?
Assign ownership of the risk response plan
Provide awareness in early detection of risk.
Perform periodic audits on identified risk.
areas Document the risk tolerance of the organization.
A risk response plan is a document that outlines the actions to be taken to address the identified risk scenarios. A risk response plan should include the objectives, scope, roles and responsibilities, resources, timelines, and metrics for each risk response. Assigning ownership of the risk response plan is the most effective way to mitigate identified risk scenarios, as it ensures accountability, clarity, and communication among the stakeholders involved in the risk management process. Assigning ownership also helps to monitor and evaluate the progress and effectiveness of the risk response plan, and to make adjustments as needed. References =Riskand Information Systems Control Study Manual, Chapter 3: Risk Response and Mitigation, Section 3.3: Risk Response Plan, p. 152-155.
Which of the following should a risk practitioner do FIRST when an organization decides to use a cloud service?
Review the vendor selection process and vetting criteria.
Assess whether use of service falls within risk tolerance thresholds.
Establish service level agreements (SLAs) with the vendor.
Check the contract for appropriate security risk and control provisions.
According to the CRISC EXAM TOPIC 2 LONG Flashcards, the first thing that a risk practitioner should do when an organization decides to use a cloud service is to review the vendor selection process and vetting criteria. This is because the vendor selection process and vetting criteria are essential steps to ensure that the cloud service provider meets the organization’s requirements and expectations, and that the risks associated with the cloud service are identified and managed. By reviewing the vendor selection process and vetting criteria, the risk practitioner can evaluate the quality, reliability, security, and compliance of the cloud service provider, and determine if the cloud service is suitable and beneficial for the organization. The risk practitioner can also identify any gaps or weaknesses in the vendor selection process and vetting criteria, and recommend improvements or alternatives accordingly. References = CRISC EXAM TOPIC 2 LONG Flashcards
The MAIN purpose of having a documented risk profile is to:
comply with external and internal requirements.
enable well-informed decision making.
prioritize investment projects.
keep the risk register up-to-date.
According to the Risk Management Essentials, a risk profile is established to enhance senior management’s analysis and decision making related to priority setting and resource allocation. A risk profile is a description of a set of risks that an organization faces, and it helps to make the risks visible and understandable. By having a documented risk profile, an organization can identify the nature and level of the threats, assess the likelihood and impact of the risks, evaluate the effectiveness of the controls, and determine the risk appetite and tolerance. This information can help the organization to make well-informed decisions on how to manage the risks and achieve its objectives. References = Risk Management Essentials, Risk Profile: Definition, Importance for Individuals & Companies
Which of the following attributes of a key risk indicator (KRI) is MOST important?
Repeatable
Automated
Quantitative
Qualitative
A key risk indicator (KRI) is a metric that helps organizations monitor and assess potential risks that may impact their operations, objectives, or performance. A good KRI should have certain characteristics that make it effective for risk management. One of these characteristics is repeatability, which means that the KRI can be measured consistently over time and across different situations. A repeatable KRI ensures that the risk data is reliable, comparable, and meaningful, and that the risk trends and patterns can be identified and analyzed. A repeatable KRI also supports the decision-making process by providing timely and accurate information on the risk level and status. Therefore, repeatability is the most important attribute of a KRI. References = Risk IT Framework, ISACA, 2022, p. 441
When reporting risk assessment results to senior management, which of the following is MOST important to include to enable risk-based decision making?
Risk action plans and associated owners
Recent audit and self-assessment results
Potential losses compared to treatment cost
A list of assets exposed to the highest risk
When reporting risk assessment results to senior management, the most important information to include to enable risk-based decision making is the potential losses compared to treatment cost. This information helps to quantify the impact and likelihood of the risks, and to evaluate the cost and benefit of the risk responses. This information also helps to prioritize and allocate resources for the risk management program, and to align the risk management program with the enterprise’s objectives, strategy, and risk appetite. The other options are not as important as the potential losses compared to treatment cost, as they provide different types of information for the risk management process:
Risk action plans and associated owners are the documents that specify the actions to be taken to address the identified risks, the resources required, the timelines, the owners, and the expected outcomes. This information helps to implement and monitor the risk management program, and to assign the authority and accountability for the risk management activities.
Recent audit and self-assessment results are the outcomes of the independent and objective examination of the risk management program, such as by internal or external auditors, or by the risk owners or practitioners themselves. This information helps to provide assurance and feedback on the effectiveness and efficiency of the risk management program, and to identify the gaps or weaknesses that need to be addressed.
A list of assets exposed to the highest risk are the resources that have the most value for the enterprise, such as hardware, software, data, or services, and that are affected by or contribute to the highest risks. This information helps to identify and protect the critical assets of theenterprise, and to reduce the exposure and impact of the risks to the assets. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.3.1.1, pp. 58-59.
Which of the following BEST enables a risk practitioner to focus on risk factors that could potentially affect the results of an IT initiative?
Prioritizing threats and controls
Assessing trends in quantitative risk analysis results
Measuring and reporting qualitative risk trends
Conducting stakeholder surveys
Prioritizing threats and controls helps tofocus resources and mitigationon high-risk elements that directly impact project objectives. This enhances decision-making and project alignment with business goals.
Which of the following would BEST help an enterprise define and communicate its risk appetite?
Gap analysis
Risk assessment
Heat map
Risk register
The best way to help an enterprise define and communicate its risk appetite is to use a risk register, which is a document that records and summarizes the key information and data about the identified risks and the risk responses1. A risk register can help to:
Define the risk appetite, which is the amount and type of risk that the enterprise is willing to accept or pursue in order to achieve its objectives2. The risk register can include the risk appetite statement, which is a clear and concise expression of the enterprise’s risk preferences and boundaries3.
Communicate the risk appetite, which is the process of sharing and informing the risk appetite to the relevant stakeholders, such as the board, the management, the employees, or the customers4. The risk register can be used as a communication tool, which can provide a consistent and transparent view of the enterprise’s risk profile and performance5.
The other options are not the best ways to help an enterprise define and communicate its risk appetite, because:
Gap analysis is a technique that compares the current state and the desired state of a process, system, or organization, and identifies the gaps or differences between them6. Gap analysis can help to assess the alignment or misalignment of the enterprise’s risk appetite with its risk level, but it does not help to define or communicate the risk appetite itself.
Risk assessment is a process that estimates the probability and impact of the risks, and prioritizes the risks based on their significance and urgency. Risk assessment can help to identify andanalyze the risks that may affect the enterprise’s objectives, but it does not help to define or communicate the risk appetite itself.
Heat map is a graphical representation that uses colors to indicate the level or intensity of a variable, such as risk. Heat map can help to visualize and compare the risks based on their probability and impact, but it does not help to define or communicate the risk appetite itself.
References =
Risk Register - CIO Wiki
Risk Appetite - CIO Wiki
Risk Appetite Statement - CIO Wiki
Risk Communication - CIO Wiki
Risk Reporting - CIO Wiki
Gap Analysis - CIO Wiki
[Risk Assessment - CIO Wiki]
[Heat Map - CIO Wiki]
[Risk and Information Systems Control documents and learning resources by ISACA]
Which of the following is the PRIMARY role of the second line when an IT risk management framework is adopted?
Overseeing the execution of framework requirements
Implementing the framework requirements
Advising industry standard framework organizations
Auditing the execution of framework requirements
When confirming whether implemented controls are operating effectively, which of the following is MOST important to review?
Results of benchmarking studies
Results of risk assessments
Number of emergency change requests
Maturity model
The number of emergency change requests is the most important factor to review when confirming whether implemented controls are operating effectively, as it indicates the frequency and severity of incidents or issues that require urgent changes to the controls, and may reflect the control deficiencies or failures. The results of benchmarking studies, the results of risk assessments, and the maturity model are not the most important factors, as they are more related to the comparison, evaluation, or improvement of the controls, respectively, rather than the confirmation of the control effectiveness. References = CRISC Review Manual, 7th Edition, page 154.
Which of the following would be MOST effective in monitoring changes in an organization ' s IT risk environment?
Lagging indicators
Risk mitigation plans
Industry regulatory reports
Risk inventory
The risk inventory contains a current and historical record of identified risks and their statuses. Monitoring this inventory reveals emerging risks, shifts in severity, and whether mitigation is effective. It supports trend analysis and continuous improvement.
Which of the following should be management ' s PRIMARY consideration when approving risk response action plans?
Ability of the action plans to address multiple risk scenarios
Ease of implementing the risk treatment solution
Changes in residual risk after implementing the plans
Prioritization for implementing the action plans
The management’s primary consideration when approving risk response action plans should be the changes in residual risk after implementing the plans. Residual risk is the level of risk that remains after the implementation of risk responses1. It indicates the degree of exposure or uncertainty that the organization still faces, and the potential impact or consequences of the risk events. The management should evaluate the effectiveness and adequacy of the risk responses, and decide whether the residual risk is acceptable or not2. The management should also compare the residual risk with the risk appetite, which is the amount and type of risk that the organization is willing to accept or pursue in order to achieve its objectives3. The management should ensure that the residual risk is aligned with the risk appetite, and that the risk responses are consistent and proportional to the risk level4.
The other options are not the primary consideration when approving risk response action plans, because:
Ability of the action plans to address multiple risk scenarios is a desirable but not essential criterion for approving risk response action plans. Risk scenarios are hypothetical situations that describe how a risk event could occur and what the consequences could be5. They can help to understand and communicate the nature and impact of the risks, and to design and evaluate the risk responses6. However, not all risk scenarios are equally likely or relevant, and some risk scenarios may be too complex or improbable to address. Therefore, the ability of the action plansto address multiple risk scenarios is not the primary consideration, but rather a secondary or supplementary one.
Ease of implementing the risk treatment solution is a practical but not critical criterion for approving risk response action plans. Risk treatment is the process of selecting and applying appropriate measures to modify the risk7. It can involve different strategies, such as avoid, reduce, transfer, or accept the risk8. The ease of implementing the risk treatment solution depends on various factors, such as the availability of resources, the feasibility of the solution, or the cooperation of the stakeholders. However, the ease of implementation is not the primary consideration, but rather a supporting or facilitating one.
Prioritization for implementing the action plans is a useful but not vital criterion for approving risk response action plans. Prioritization is the process of ranking the action plans according to their importance, urgency, or impact. It can help to allocate the resources, schedule the activities, and monitor the progress of the action plans. However, prioritization is not the primary consideration, but rather a subsequent or follow-up one.
References =
Residual Risk - CIO Wiki
What is Residual Risk? - Definition from Techopedia
Risk Appetite - CIO Wiki
Risk Appetite: What It Is and Why It Matters - Gartner
Risk Scenarios Toolkit - ISACA
Risk Scenarios Starter Pack - ISACA
Risk Treatment - CIO Wiki
Risk Treatment Plan - CIO Wiki
[Prioritization - CIO Wiki]
Which of the following is the PRIMARY reason to perform periodic vendor risk assessments?
To provide input to the organization ' s risk appetite
To monitor the vendor ' s control effectiveness
To verify the vendor ' s ongoing financial viability
To assess the vendor ' s risk mitigation plans
The primary reason to perform periodic vendor risk assessments is to monitor the vendor’s control effectiveness. A vendor risk assessment is a process of evaluating the risks associated with outsourcing a service or function to a third-party vendor. The assessment should be performed periodically to ensure that the vendor is complying with the contractual obligations, service level agreements, and security standards, and that the vendor’s controls are operating effectively to mitigate the risks. Providing input to the organization’s risk appetite, verifying the vendor’s ongoing financial viability, and assessing the vendor’s risk mitigation plans are otherpossible reasons, but they are not as important as monitoring the vendor’s control effectiveness. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 11; CRISC Review Manual, 6th Edition, page 144.
Average time to contain security incidents
Percentage of systems being monitored
Number of false positives reported
Number of personnel dedicated to security monitoring
The average time to contain security incidents directly reflects how quickly and effectively an organization can respond to cybersecurity threats, which is a critical measure of the program’s effectiveness. Other options like percentage of systems monitored or number of personnel indicate resources or scope but do not measure outcome or effectiveness. False positives may indicate detection issues but are less tied to program effectiveness than incident containment time.
The FIRST step for a startup company when developing a disaster recovery plan (DRP) should be to identify:
Current vulnerabilities
Recovery time objectives (RTOs)
Critical business processes
A suitable alternate site
Thefoundationof any DRP is identifying whichbusiness processes are criticalto the organization’s operations and survival.
CRISC guidance:
“The initial step in disaster recovery and business continuity planning is identifying and prioritizing critical business processes and the resources required to support them.”
From there, RTOs and recovery strategies are developed.
Hence,C. Critical business processesis correct.
CRISC Reference:Domain 3 – Risk Response and Mitigation, Topic: Business Impact and Continuity Planning.
The PRIMARY reason for communicating risk assessment results to data owners is to enable the:
design of appropriate controls.
industry benchmarking of controls.
prioritization of response efforts.
classification of information assets.
Understanding the Question:
The question focuses on the primary reason for communicating risk assessment results to data owners.
Analyzing the Options:
A. Design of appropriate controls:This is important but not the primary reason for communication.
B. Industry benchmarking of controls:This is secondary to the main goal of communicating risk.
C. Prioritization of response efforts:This enables data owners to allocate resources and address the most critical risks first.
D. Classification of information assets:This is typically part of the initial risk assessment process, not the main communication goal.
Communication of Risk Assessment Results:Ensuring data owners understand the results of risk assessments allows them to make informed decisions on where to focus their efforts.
Prioritization:Data owners can prioritize their actions based on the assessed risk levels, ensuring that resources are allocated efficiently to mitigate the most significant risks.
Which of the following tasks should be completed prior to creating a disaster recovery plan (DRP)?
Conducting a business impact analysis (BIA)
Identifying the recovery response team
Procuring a recovery site
Assigning sensitivity levels to data
According to the CRISC Review Manual, conducting a business impact analysis (BIA) is the task that should be completed prior to creating a disaster recovery plan (DRP), because it helps to identify the critical business processes and resources, and their dependencies, that need to be recovered in the event of a disaster. The BIA also helps to determine the recovery timeobjectives (RTOs) and recovery point objectives (RPOs) for each business process and resource, which are the key inputs for the DRP. The other options are not the tasks that should be completed prior to creating a DRP, as they are part of the DRP itself. Identifying the recovery response team is the task of defining the roles and responsibilities of the personnel involved in the recovery process. Procuring a recovery site is the task of selecting and acquiring an alternative location where the business operations can be resumed. Assigning sensitivity levels to data is the task of classifying the data based on its importance and protection requirements. References = CRISC Review Manual, 7th Edition, Chapter 5, Section 5.2.1, page 237.
An organization wants to assess the maturity of its internal control environment. The FIRST step should be to:
validate control process execution.
determine if controls are effective.
identify key process owners.
conduct a baseline assessment.
A baseline assessment is the first step in assessing the maturity of an organization’s internal control environment. A baseline assessment is a comprehensive evaluation of the current state of the internal control structure, processes, and activities across the organization. A baseline assessment helps to identify the strengths and weaknesses of the existing internal controls, as well as the gaps and opportunities for improvement. A baseline assessment also provides a reference point for measuring the progress and effectiveness of the internal control improvement initiatives. The other options are not the first steps in assessing the maturity of an internal control environment, although they may be part of the subsequent steps. Validating control process execution is a technique to verify that the internal control activities are performed as designed and intended. Determining if controls are effective is a process to evaluate the adequacy and efficiency of the internal controls in achieving the desired outcomes and mitigating the risks. Identifying key process owners is a task to assign the roles and responsibilities for the internal control design, implementation, and monitoring to the appropriate individuals or groupswithin theorganization. References = CRISC Review Manual, pages 153-1541; CRISC Review Questions, Answers & Explanations Manual, page 742
Which of the following criteria associated with key risk indicators (KRIs) BEST enables effective risk monitoring?
Approval by senior management
Low cost of development and maintenance
Sensitivity to changes in risk levels
Use of industry risk data sources
Key risk indicators (KRIs) are metrics that help organizations monitor and assess potential risks that may impact their operations, financial health, or overall performance1. KRIs should have certain characteristics that make them effective for risk monitoring, such as:
Ability to measure the right thing (e.g., supports the decisions that need to be made)
Quantifiable (e.g., damages in dollars of profit loss)
Capability to be measured precisely and accurately
Relevant (measuring the right thing associated with decisions)2
Among the four options given, only option C (sensitivity to changes in risk levels) best enables effective risk monitoring. This is because KRIs should be able to capture the changes in risk levels over time and alert organizations to emerging or escalating risks3. A high sensitivity to changes in risk levels indicates that theKRI is responsive and timely, and can help organizations take preventive or corrective actions before the risks become too severe.
References = Key Risk Indicators: A Practical Guide, Key Risk Indicators: Examples & Definitions, Key Risk Indicators - Wikipedia
Which of the following BEST protects organizational data within a production cloud environment?
Data encryption
Continuous log monitoring
Right to audit
Data obfuscation
Data encryption is the best method to protect organizational data within a production cloud environment, as it ensures the confidentiality, integrity, and availability of the data. Data encryption is the process oftransforming data into an unreadable format using a secret key or algorithm, so that only authorized parties can access and decrypt the data. Data encryption can protect data at rest (stored in the cloud) and data in transit (transferred over the network) from unauthorized access, modification, or deletion by malicious actors or accidental errors. Data encryption can also help organizations comply with legal, regulatory, and contractual requirements for data protection and privacy, such as GDPR, CCPA, and PCI DSS.
Which of the following should be the MOST important consideration when determining controls necessary for a highly critical information system?
The number of threats to the system
The organization ' s available budget
The number of vulnerabilities to the system
The level of acceptable risk to the organization
Determining Controls:
Acceptable Risk Level: The level of acceptable risk to the organization is the most important consideration because it directly influences the type and extent of controls implemented. Controls must be designed to keep risk within acceptable levels.
Risk Management Strategy: Aligning controls with the organization ' s risk appetite ensures that resources are used effectively and that critical information systems are adequately protected.
Comparison with Other Options:
Number of Threats: Important for understanding risk exposure but secondary to determining acceptable risk levels.
Available Budget: Budget constraints are important but should not compromise the implementation of necessary controls.
Number of Vulnerabilities: Identifying vulnerabilities is part of the risk assessment process, but controls are prioritized based on the acceptable risk level.
Best Practices:
Risk Assessment: Conduct thorough risk assessments to understand the potential impact of threats and vulnerabilities.
Control Effectiveness: Implement controls that are both cost-effective and capable of reducing risk to acceptable levels.
Continuous Monitoring: Regularly monitor and review controls to ensure they remain effective and aligned with the organization ' s risk tolerance.
An organization has just implemented changes to close an identified vulnerability that impacted a critical business process. What should be the NEXT course of action?
Redesign the heat map.
Review the risk tolerance.
Perform a business impact analysis (BIA)
Update the risk register.
According to the CRISC Review Manual1, the risk register is a tool that records the results of risk identification, analysis, evaluation, and treatment. It should be updated whenever there is a change in the risk profile, such as when a vulnerability is closed or a new threat is identified. Updating the risk register allows the organization to monitor the current status of risks and the effectiveness of risk responses. Therefore, the next course of action after implementing changes to close an identifiedvulnerability is to update the risk register with the new information. References = CRISC Review Manual1, page 191.
While reviewing a contract of a cloud services vendor, it was discovered that the vendor refuses to accept liability for a sensitive data breach. Which of the following controls will BES reduce the risk associated with such a data breach?
Ensuring the vendor does not know the encryption key
Engaging a third party to validate operational controls
Using the same cloud vendor as a competitor
Using field-level encryption with a vendor supplied key
Encryption is a technique that transforms data into an unreadable format using a secret key, so that only authorized parties can access and decrypt the data. Encryption can help to protectsensitive data from unauthorized access or disclosure, especially when the data is stored or transmitted in the cloud1.
Ensuring the vendor does not know the encryption key is a control that will best reduce the risk associated with a data breach, because it can help to:
Prevent the vendor from accessing or disclosing the sensitive data, intentionally or unintentionally
Limit the exposure or impact of the data breach, even if the vendor’s systems or networks are compromised by hackers or malicious insiders
Maintain the confidentiality and integrity of the sensitive data, regardless of the vendor’s liability or responsibility
Enhance the trust and confidence of the customers and stakeholders, who may be concerned about the vendor’s refusal to accept liability for a data breach23
The other options are not as effective as ensuring the vendor does not know the encryption key for reducing the risk associated with a data breach. Engaging a third party to validate operational controls is a control that can help to verify and improve the vendor’s security practices and processes, but it does not guarantee that the vendor will prevent or respond to a data breach adequately or timely. Using the same cloud vendor as a competitor is not a control, but rather a business decision that may increase the risk associated with a data breach, as the vendor may have access to or disclose the sensitive data of both parties, or may favor one party over the other. Using field-level encryption with a vendor supplied key is a control that can help to encrypt specific fields or columns of data, such as names, addresses, or credit card numbers, but it does not prevent the vendor from accessing or disclosing the data, as the vendor has the encryption key4. References =
Encryption - ISACA
Cloud Encryption: Using Data Encryption in The Cloud
Cloud Encryption: Why You Need It and How to Do It Right
Field-Level Encryption - ISACA
[CRISC Review Manual, 7th Edition]
Which of the following is the GREATEST concern when an organization uses a managed security service provider as a firewall administrator?
Exposure of log data
Lack of governance
Increased number of firewall rules
Lack of agreed-upon standards
A managed security service provider (MSSP) is a third-party entity that offers network security services to an organization, such as firewall operation, administration, monitoring, and maintenance1. A firewall is a device or software that controls the incoming and outgoing network traffic based on predefined rules2. A firewall administrator is a person or entity that manages and maintains the firewall configuration, rules, and policies3. When an organizationuses an MSSP as a firewall administrator, the greatest concern is the exposure of log data, because log data contains sensitive and valuable information about the organization’s network activity, such as source and destination IP addresses, ports, protocols, timestamps, and user identities4. If the log data is not protected properly by the MSSP, it could be accessed, modified, or stolen by unauthorized parties, such as hackers, competitors, or regulators, which could result in data breaches, compliance violations, reputational damage, or legal liabilities for the organization5. The other options are not as concerning as the exposure of log data, because they do not pose a direct and immediate threat to the organization’s data security and privacy, but rather affect the quality and efficiency of the firewall management, as explained below:
B. Lack of governance is a concern when an organization uses an MSSP as a firewall administrator, because it could lead to misalignment or inconsistency between the organization’s and the MSSP’s objectives, policies, and standards for firewall management. However, this concern can be mitigated by establishing a clear and comprehensive service level agreement (SLA) with the MSSP,which defines the roles, responsibilities, expectations, and performance indicators for the firewall management service6.
C. Increased number of firewall rules is a concern when an organization uses an MSSP as a firewall administrator, because it could create complexity, confusion, or duplication in the firewall configuration, which could affect the firewall performance and security. However, this concern can be mitigated by conducting regular firewall audits and reviews with the MSSP, which can help to rationalize, optimize, and update the firewall rules, and to ensure that they are relevant, effective, and efficient for the organization’s network environment.
D. Lack of agreed-upon standards is a concern when an organization uses an MSSP as a firewall administrator, because it could result in gaps or weaknesses in the firewall design and implementation, which could compromise the firewall functionality and security. However, this concern can be mitigated by adopting and following industry best practices, norms, and expectations for firewall management, such as the National Institute of Standards and Technology (NIST) guidelines, the Center for Internet Security (CIS) benchmarks, or the Payment Card Industry Data Security Standard (PCI DSS) requirements . References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 115. What Is A Managed Security Service Provider (MSSP)? - Fortinet, What is a Firewall? - Definition from Techopedia, Firewall Administrator Job Description - Betterteam, What is a Firewall Log? - Definition from Techopedia, Firewall Log Management: Why It’s Important and How to Do It Right, How to Write a Service Level Agreement (SLA) for an MSSP, [Firewall Auditing: BestPractices for Security and Compliance], [Guidelines on Firewalls and Firewall Policy | CSRC] , [CIS Firewall Benchmark - CIS], [PCI DSS and Firewalls - PCI Security Standards Council]
Which process is MOST effective to determine relevance of threats for risk scenarios?
Vulnerability assessment
Business impact analysis (BIA)
Penetration testing
Root cause analysis
A vulnerability assessment is a process that identifies and quantifies vulnerabilities in a system. It is the most effective process to determine the relevance of threats for risk scenarios as it helps in identifying potential security threats and vulnerabilities, quantifying the seriousness of each, and prioritizing techniques to mitigate attack and protect IT resources1.
References
2Identifying and Estimating Cybersecurity Risk for Enterprise Risk Management
3Threat Modeling Process | OWASP Foundation
1Threat modeling explained: A process for anticipating cyber attacks
4Hazard Identification and Risk Assessment: A Guide - SafetyCulture
5How to Write Strong Risk Scenarios and Statements - ISACA
A large organization recently restructured the IT department and has decided to outsource certain functions. What action should the control owners in the IT department take?
Conduct risk classification for associated IT controls.
Determine whether risk responses still effectively address risk.
Perform vulnerability and threat assessments.
Analyze and update IT control assessments.
According to the ISACA Risk and Information Systems Control study guide and handbook, the control owners in the IT department should determine whether risk responses still effectively address risk after a restructuring and outsourcing of certain functions. This is because the restructuring and outsourcing may have changed the risk profile, the control environment, and the control activities of the IT department. The control owners should review the existing risk responses and evaluate if they are still appropriate, adequate, and efficient in mitigating the risks associated with the outsourced functions. The control owners should also monitor the performance and compliance of the service providers and ensure that the contractual obligations and service level agreements are met12
1: ISACA Risk and Information Systems Control Study Guide, 4th Edition, page 33 2: ISACA Risk and Information Systems Control Handbook, 1st Edition, page 25
Which of the following offers the SIMPLEST overview of changes in an organization ' s risk profile?
A risk roadmap
A balanced scorecard
A heat map
The risk register
A heat map is a graphical representation of the organization’s risk profile that shows the relative level of risk for each risk category or event. A heat map uses colors, shapes, or symbols to indicate the magnitude and likelihood of each risk, as well as its trend and status. A heat map offers the simplest overview of changes in the organization’s risk profile, as it allows the risk decision-makers to quickly identify the most significant risks, theareas of improvement or deterioration, and the gaps or overlaps in risk management. A heat map can also be used to communicate the risk profile to senior management and other stakeholders in a clear and concise manner. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.3: IT Risk Assessment Methods and Techniques, Page 77; Future Risks: How organizations see changes in risk management - Aon.
Which of the following is the MOST important consideration when sharing risk management updates with executive management?
Including trend analysis of risk metrics
Using an aggregated view of organizational risk
Relying on key risk indicator (KRI) data
Ensuring relevance to organizational goals
The most important consideration when sharing risk management updates with executive management is ensuring relevance to organizational goals. This means that the risk information presented should align with the strategic objectives and priorities of the organization, and demonstrate how risk management supports the achievement of those goals. Executive management is responsible for setting the direction and vision of the organization, and therefore needs to understand how risk management contributes to the value creation and protection of the organization. By ensuring relevance to organizational goals, risk management updates can help executive management make informed decisions, allocate resources, and communicate with stakeholders.
Some of the ways to ensure relevance to organizational goals are:
Linking risk management updates to the organization’s mission, vision, values, and strategy
Highlighting the key risks and opportunities that affect the organization’s performance and competitiveness
Providing clear and concise risk reports that focus on the most critical and material risks
Using a common risk language and framework that is understood by executive management
Providing actionable recommendations and solutions to address the identified risks
Aligning risk management updates with the organization’s reporting cycle and governance structure
References =
The Importance of Integrating Risk Management with Strategy
Four steps for managing risk at the CEO level
5 Key Principles of Successful Risk Management
An organization has updated its acceptable use policy to mitigate the risk of employees disclosing confidential information. Which of the following is the BEST way to reinforce the effectiveness of this policy?
Communicate sanctions for policy violations to all staff.
Obtain signed acceptance of the new policy from employees.
Train all staff on relevant information security best practices.
Implement data loss prevention (DLP) within the corporate network.
Train all staff on relevant information security best practices, because it helps to increase the awareness and understanding of the employees regarding the acceptable use policy and its purpose, and to improve their skills and knowledge on how to protect and handle confidential information. An acceptable use policy is a document that outlines the standards and expectations for the proper usage of the organization’s IT resources, such as systems, applications, networks, or devices, and the consequences of non-compliance. Confidential information is information that is sensitive or proprietary, and may cause harm or damage to the organizationor its stakeholders if disclosed or compromised, such as trade secrets, customer data, or financial records. Training all staff on relevant information security best practices is the best way to reinforce the effectiveness of the policy, as it helps to ensure that the employees are aware of and comply with the policy, and that they adopt the appropriate behaviors and techniques to prevent or mitigate the risk of disclosing confidential information.
Communicating sanctions for policy violations to all staff, obtaining signed acceptance of the new policy from employees, and implementing data loss prevention (DLP) within the corporate network are all possible ways to reinforce the effectiveness of the policy, but they are not the best way, as they do not directly address the awareness and understanding of the employees regarding the policy and its purpose, and they may not be sufficient or effective to prevent or mitigate the risk of disclosing confidential information.
An organization has restructured its business processes, and the business continuity plan (BCP) needs to be revised accordingly. Which of the following should be identified FIRST?
Variances in recovery times
Ownership assignment for controls
New potentially disruptive scenarios
Contractual changes with customers
When an organization restructures its business processes, the first step in revising the BCP is to identify new potentially disruptive scenarios that may affect the continuity of the critical functions and processes. This can be done by conducting a risk assessment or a business impact analysis (BIA) to determine the likelihood and impact of various threats and vulnerabilities onthe organization’s objectives and operations. By identifying new potentially disruptive scenarios, the organization can then update its recovery strategies, objectives, and plans accordingly.
An organization is reviewing a contract for a Software as a Service (SaaS) sales application with a 99.9% uptime service level agreement (SLA). Which of the following BEST describes ownership of availability risk?
The risk is shared by both organizations.
The liability for the risk is owned by the cloud provider.
The risk is transferred to the cloud provider.
The liability for the risk is owned by the sales department.
Even with SLAs in place, both parties must manage aspects of availability risk. The provider manages infrastructure, while the organization is responsible for business impact.
In addition to the risk register, what should a risk practitioner review to develop an understanding of the organization ' s risk profile?
The control catalog
The asset profile
Business objectives
Key risk indicators (KRls)
In addition to the risk register, which is a tool to document and monitor the risks that affect the organization, a risk practitioner should review the business objectives of the organization to develop an understanding of its risk profile. The risk profile is a description of the set of risks that the organization faces in relation to its goals and strategies. By reviewing the business objectives, the risk practitioner can identify the sources, drivers, and consequences of the risks, as well as the alignment, prioritization, and tolerance of the risks. The business objectives also provide the context and criteria for evaluating and managing the risks. The other options are not the best choices to review for developing an understandingof the organization’s risk profile, as they do not capture the full scope and nature of the risks. The control catalog is a list of the existing controls that are implemented to mitigate the risks, but it does not reflect the effectiveness, efficiency, or sufficiency of the controls. The asset profile is a description of the resources and capabilities that the organization possesses or relies on, but it does not indicate the value, vulnerability, or interdependency of the assets. The key risk indicators (KRIs) are metrics that measure the level and trend of the risks, but they do not explain the causes, impacts, orresponses to the risks. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.2, Page 49.
Which of the following should a risk practitioner do NEXT after learning that Internet of Things (loT) devices installed in the production environment lack appropriate security controls for
sensitive data?
Assess the threat and associated impact.
Evaluate risk appetite and tolerance levels
Recommend device management controls
Enable role-based access control.
Assessing the threat and associated impact is the next thing that a risk practitioner should do after learning that Internet of Things (IoT) devices installed in the production environment lack appropriate security controls for sensitive data. This is because assessing the threat and associated impact can help determine the level and nature of the risk posed by the IoT devices, as well as the potential consequences and costs of a security breach or incident. Assessing the threat and associated impact can also provide the basis for further risk analysis and response steps, such as evaluating risk appetite and tolerance levels, recommending device management controls, or enabling role-based access control. According to the CRISC Review Manual 2022, assessing the threat and associated impact is one of the key steps in the IT risk assessment process1. According to the web search results, assessing the threat and associated impact is a common and recommended practice for addressing the security risks of IoT devices
An organization must make a choice among multiple options to respond to a risk. The stakeholders cannot agree and decide to postpone the decision. Which of the following risk responses has the organization adopted?
Transfer
Mitigation
Avoidance
Acceptance
Risk avoidance is a type of risk response that involves eliminating the risk entirely by not engaging in the activity that causes the risk or changing the conditions that create the risk1. Riskavoidance is usually applied when the potential impact or likelihood of the risk is high or unacceptable, and when the benefits of avoiding the risk outweigh the costs or losses of doing so2.
In this case, the organization has adopted risk avoidance as its risk response, because it has decided to postpone the decision that could trigger the risk. By delaying the decision, the organization is avoiding therisk of making a wrong or unfavorable choice among the multiple options. However, this may not be the best or most effective risk response, as it could also result in missed opportunities, wasted resources, or increased uncertainty3. The organization shouldconsider the trade-offs and consequences of avoiding the risk, and explore other possible risk responses that could reduce or transfer the risk.
The other options are not the risk responses that the organization has adopted. Risk transfer means shifting the responsibility or burden of the risk to another party, such as a vendor or an insurer2. The organization has not transferred the risk to anyone else, but rather avoided it by postponing the decision. Risk mitigation means implementing controls or safeguards to minimize the negative effects of the risk2. The organization has not mitigated the risk by reducing its impact or likelihood, but rather avoided it by delaying the decision. Risk acceptance means acknowledging the risk and its consequences without taking any action to address it2. The organization has not accepted the risk by tolerating its potential outcomes, but rather avoided it by postponing the decision. References =
10 Risk Mitigation techniques you need to know - Stakeholdermap.com
Risk Response Strategies: Types & Examples (+ Free Template)
[CRISC Review Manual, 7th Edition]
Which of the following is the MOST effective way to reduce potential losses due to ongoing expense fraud?
Implement user access controls
Perform regular internal audits
Develop and communicate fraud prevention policies
Conduct fraud prevention awareness training.
Developing and communicating fraud prevention policies is the most effective way to reduce potential losses due to ongoing expense fraud because it creates a culture of integrity and accountability, sets clear expectations and consequences for employees, and deters fraudulent behavior. Implementing user access controls, performing regular internal audits, and conducting fraud prevention awareness training are also important controls, but they are more reactive and detective than preventive. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.2, page 4-26.
An organization has been experiencing an increasing number of spear phishing attacks Which of the following would be the MOST effective way to mitigate the risk associated with these attacks?
Update firewall configuration
Require strong password complexity
implement a security awareness program
Implement two-factor authentication
A spear phishing attack is a type of cyberattack that targets a specific individual or organization with a fraudulent email that appears to be from a trusted source, and attempts to trick the recipient into clicking amalicious link, opening a malicious attachment, or providing sensitive information. A spear phishing attack can compromise the security, confidentiality, integrity, or availability of the information systems and data of the individual or organization. The most effective way to mitigate the risk associated with spear phishing attacks is to implement a security awareness program, which is a program that educates and trains the employees and stakeholders of the organization about the security policies, procedures, and best practices, and the potential threats and risks that may affect the organization. A security awareness program can help to prevent or reduce the success of spear phishing attacks, as it can increase the knowledge and skills of the employees and stakeholders to recognize and avoid the fraudulent emails, and to report and respond to any suspicious or malicious activities. References = CRISC Review Manual, 7th Edition, page 181.
Who is the MOST appropriate owner for newly identified IT risk?
The manager responsible for IT operations that will support the risk mitigation efforts
The individual with authority to commit organizational resources to mitigate the risk
A project manager capable of prioritizing the risk remediation efforts
The individual with the most IT risk-related subject matter knowledge
According to the CRISC Review Manual, the risk owner is the person who has the authority and accountability to manage a specific risk and its associated controls1. The risk owner is also responsible for ensuring that the risk is within the acceptable level and that the risk response is effective and efficient2. Therefore, the most appropriate owner for a newly identified IT risk is the individual who has the authority to commit organizational resources to mitigate the risk, asthey have the most interest and influence on the risk and its impact on the business objectives. The other options are not the most appropriate owners for a newly identified IT risk, as they may not have the authority or the accountability to manage the risk. The manager responsible for IT operations that will support the risk mitigation efforts may have the operational responsibility or the oversight of the risk management activities, but they may not have the authority to allocate the resources or approve the risk response. A project manager capable of prioritizing the risk remediation efforts may have the project management skills or the knowledge of the risk management process, but they may not have the accountability or the ownership of the risk or its outcomes. The individual with the most IT risk-related subject matter knowledge may have the technical expertise or the understanding of the risk and its causes, but they may not have the decision-making power or the responsibility to manage the risk or its controls. References = CRISC Review Manual, pages 32-331; CRISC Review Questions, Answers & Explanations Manual, page 822
Which of the following is the MOST important update for keeping the risk register current?
Modifying organizational structures when lines of business merge
Adding new risk assessment results annually
Retiring risk scenarios that have been avoided
Changing risk owners due to employee turnover
Understanding the Question:
The question asks what the most important update for keeping the risk register current is.
Analyzing the Options:
A. Modifying organizational structures when lines of business merge:Reflects significant changes in the organization that impact risk profiles.
B. Adding new risk assessment results annually:Important but periodic.
C. Retiring risk scenarios that have been avoided:Necessary but not as impactful as major organizational changes.
D. Changing risk owners due to employee turnover:Important but secondary to major structural changes.
Organizational Changes:When lines of business merge, it can significantly alter the risk landscape, introducing new risks and changing the impact and likelihood of existing ones. Updating the risk register to reflect these changes is crucial for accurate risk management.
Impact on Risk Profiles:Mergers and acquisitions can affect every aspect of an organization, from operational processes to regulatory compliance, making it essential to update the risk register accordingly.
An organization is analyzing the risk of shadow IT usage. Which of the following is the MOST important input into the assessment?
Business benefits of shadow IT
Application-related expresses
Classification of the data
Volume of data
The most important input into the assessment of the risk of shadow IT usage is the classification of the data that is being processed, stored, or transmitted by the unauthorized applications or devices. This determines the level of confidentiality, integrity, and availability that is required for the data and the potential impact of a breach or loss. Business benefits of shadow IT, application-related expenses, and volume of data are less important inputs that may affect the risk analysis, but not as much as the data classification. References = Risk IT Framework, 2nd Edition, page 28; CRISC Review Manual, 6th Edition, page 98.
An organization has an approved bring your own device (BYOD) policy. Which of the following would BEST mitigate the security risk associated with the inappropriate use of enterprise applications on the devices?
Periodically review application on BYOD devices
Include BYOD in organizational awareness programs
Implement BYOD mobile device management (MDM) controls.
Enable a remote wee capability for BYOD devices
The best way to mitigate the security risk associated with the inappropriate use of enterprise applications on the BYOD devices is to implement BYOD mobile device management (MDM) controls. MDM controls are software tools or services that allow the organization to remotely manage, monitor, and secure the BYOD devices and the enterprise applications and data on them. MDM controls can help to enforce security policies, restrict unauthorized access, encrypt sensitive data, wipe data in case of loss or theft, and update or patch applications. The other options are not as effective as implementing MDM controls, as they are related to the review, awareness, or recovery of the BYOD devices and applications, not the prevention or protection of the security risk. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.3: IT Risk Response Implementation, page 145.
Which of the following should be the FIRST consideration when a business unit wants to use personal information for a purpose other than for which it was originally collected?
Informed consent
Cross border controls
Business impact analysis (BIA)
Data breach protection
According to the GDPR, personal data shall be collected for specified, explicit and legitimate purposes and not further processed in a manner that is incompatible with those purposes1. This means that a business unit can only use personal information for a different purpose if it has obtained the consent of the data subject, or if it has a clear legal basis or obligation to do so2. Therefore, informed consent should be the first consideration when a business unit wants to use personal information for a purpose other than for which it was originally collected.
References = GDPR Article 5 (1) (b) and Article 6 (4)1, ICO Principle (b): Purpose limitation2
A company has located its computer center on a moderate earthquake fault. Which of the following is the MOST important consideration when establishing a contingency plan and an alternate processing site?
The alternative site is a hot site with equipment ready to resume processing immediately.
The contingency plan provides for backup media to be taken to the alternative site.
The contingency plan for high priority applications does not involve a shared cold site.
The alternative site does not reside on the same fault to matter how the distance apart.
A contingency plan is a set of actions and procedures that aim to ensure the continuity of critical business functions in the event of a disruption or disaster. An alternate processing site is a location where the organization can resume its information systems operations in case the primary site is unavailable or damaged. The most important consideration when establishing a contingency plan and an alternate processing site for a company located on a moderate earthquake fault is to ensure that the alternative site does not reside on the same fault, no matter how far apart they are. This is because an earthquake can affect a large area along the fault line, and potentially damage both the primary and the alternative site, rendering them unusable. By choosing an alternative site that is not on the same fault, the company can reduce the risk of losing both sites, and increase the likelihood of restoring its operations quickly and effectively. The other options are not as important as the alternative site location, because they do not address the main threat of an earthquake, but rather focus on specific or partial aspects of the contingency plan, as explained below:
A. The alternative site is a hot site with equipment ready to resume processing immediately is a consideration that relates to the availability and readiness of the alternative site, but it does not ensure that the site is safe and secure from an earthquake. A hot site is a type of alternative site that has the necessary hardware, software, and network components to resume the information systems operations with minimal or no downtime. However, if the hot site is on the same fault asthe primary site, it may not be accessible or functional after an earthquake, and the company may lose both sites and the data stored on them.
B. The contingency plan provides for backup media to be taken to the alternative site is a consideration that relates to the integrity and recoverability of the data, but it does not ensure that the site is safe and secure from an earthquake. Backup media are devices or systems that store copies of the data and information that are essential for the organization’s operations. Taking backup media to the alternative site can help the company to restore its data and resume its operations in case the primary site is damaged or destroyed. However, if the alternative site is on the same fault as the primary site, it may not be accessible or functional after an earthquake, and the company may lose both sites and the backup media.
C. The contingency plan for high priority applications does not involve a shared cold site is a consideration that relates to the performance and reliability of the alternative site, but it does not ensure that the site is safe and secure from an earthquake. A shared cold site is a type of alternative site that has the necessary space and infrastructure to accommodate the information systems operations, but does not have the hardware, software, or network components installed. A shared cold site is shared by multiple organizations, and may not be available or suitable for the company’s high priority applications, which require more resources and customization. However, if the alternative site is on the same fault as the primary site, it may not be accessible or functional after an earthquake, and the company may lose both sites and the ability to resume its high priority applications. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 115. How to conduct a contingency planning process - IFRC, CP-4(2): Alternate Processing Site - CSF Tools - Identity Digital, Information System Contingency Planning Guidance - ISACA
When an organization is having new software implemented under contract, which of the following is key to controlling escalating costs?
Risk management
Change management
Problem management
Quality management
The key to controlling escalating costs when an organization is having new software implemented under contract is change management, which is the process of identifying, evaluating, approving, and implementing changes to the project scope, schedule, budget, or quality1. Change management can help to control escalating costs by:
Establishing a clear and agreed-upon baseline for the project deliverables, requirements, and expectations, and ensuring that they are aligned with the contract terms and conditions2.
Defining and enforcing a formal and consistent change control process, which includes the roles and responsibilities, the criteria and methods, and the documentation and communication of the changes3.
Assessing and prioritizing the proposed changes, and determining their impact and feasibility, and their alignment with the project objectives and constraints4.
Obtaining the approval and authorization of the relevant stakeholders, such as the project sponsor, the project manager, the contractor, or the customer, before implementing the changes5.
Monitoring and measuring the performance and outcome of the changes, and ensuring that they are delivered within the agreed scope, schedule, budget, and quality6.
References =
Change Management - CIO Wiki
Project Scope Management - CIO Wiki
Change Control - CIO Wiki
Change Impact Analysis - CIO Wiki
Change Approval - CIO Wiki
Change Evaluation - CIO Wiki
Which of the following is the GREATEST risk to an organization when using a public AI system to process credit card transactions?
Potential exposure of sensitive information
Use of financial data to train the AI model
Noncompliance with security standards
AI hallucinations and bias
The correct answer isAbecause the greatest risk when using apublic AI systemto process credit card transactions is thepotential exposure of sensitive information. Credit card data is highly sensitive, and use of a public AI platform can introduce serious confidentiality, privacy, and data handling concerns. Exposure of that data can lead to fraud, regulatory issues, contractual violations, and significant business impact.
The other options are important, but not the greatest primary risk:
B. Use of financial data to train the AI modelis a specific form of data misuse, but it falls within the broader and more critical risk of sensitive information exposure.
C. Noncompliance with security standardsis also significant, but it is often a consequence of exposing or improperly handling sensitive payment data.
D. AI hallucinations and biasare important AI risks, but they are not the primary concern in payment card processing.
Exact Extracts supporting the answer:
“The MOST important consideration when transmitting personal information across networks is ensuring the privacy of the personal information.”
“The data security control that BEST protects the confidentiality of data stored on backup media in transit to a third-party storage facility is encryption.”
“The MOST significant risk associated with handling credit card data through a web application is failure to store credit card data in a secure area segregated from the demilitarized zone.”
“To determine the level of protection required for securing personally identifiable information a risk practitioner should PRIMARILY consider the sensitivity property of the information.”
These extracts support that the primary concern with payment-card-related processing is protecting the confidentiality of sensitive data. Therefore, the greatest risk is thepotential exposure of sensitive information.
===========
What is the PRIMARY role of the application owner when changes are being introduced into an existing environment?
Determining possible losses due to downtime during the changes
Updating control procedures and documentation
Approving the proposed changes based on impact analysis
Notifying owners of affected systems after the changes are implemented
The application owner must formally approve changes after reviewing impact—per ISACA ' s change management and governance frameworks that assign control over operational fallouts to functional owners .
A risk practitioner has observed that risk owners have approved a high number of exceptions to the information security policy. Which of the following should be the risk practitioner ' s GREATEST concern?
Security policies are being reviewed infrequently.
Controls are not operating efficiently.
Vulnerabilities are not being mitigated
Aggregate risk is approaching the tolerance threshold
An exception to the information security policy is a permission to continue operating a system, service, or product that cannot comply with the established information security standards and requirements1. A risk owner is a person or entity that has the authority and accountability for a risk and its management2. A risk practitioner is a person or entity that has the knowledge and skills to perform risk management activities3. A high number of exceptions to the information security policy indicates that there are many systems, services, or products that do not meet the expected level of security and pose potential risks to the organization. The risk practitioner’s greatest concern should be that the aggregate risk, which is the total amount of risk that the organization faces from all sources, is approaching the tolerance threshold, which is the limit beyond which the organization does not want to tolerate the risk4. If the aggregate risk isapproaching the tolerance threshold, it means that the organization is exposed to a high level of risk that may exceed its risk appetite, which is the amount of risk that the organization is willing to accept to achieve its objectives5. This may result in negative consequences for the organization, such as breaches, losses, damages, or reputational harm. Therefore, the risk practitioner should monitor and report the aggregate risk level and the tolerance threshold, and advise the risk owners and the management on the appropriate risk responses and actions to reduce the aggregate risk to an acceptable level. Security policies are being reviewed infrequently, controls are not operating efficiently, and vulnerabilities are not being mitigated are not the risk practitioner’s greatest concern, as they are not directly related to the aggregate risk level and the tolerance threshold. Security policies are being reviewed infrequently is a condition that indicates that the organization’s security policies are not updated or revised regularly to reflect the changes and updates in the security environment and the security requirements6. This may affect the relevance and effectiveness of the security policies, but it does not necessarilyincrease the aggregate risk level or the tolerance threshold. Controls are not operating efficiently is a condition thatindicates that the organization’s controls, which are the measures or actions taken to manage or mitigate the risks, are not performing well or optimally7. This may affect the quality and performance of the controls, but it does not necessarily increase the aggregate risk level or the tolerance threshold. Vulnerabilities are not being mitigated is a condition that indicates that the organization’s vulnerabilities, which are the weaknesses or gaps that may be exploited by the threats, are not being addressed or reduced8. This may increase the likelihood or impact of the risks, but it does not necessarily increase the aggregate risk level or the tolerance threshold. References = 1: IT/Information Security Exception Request Process2: [Risk Ownership - Risk Management] 3: [Risk Practitioner - ISACA] 4: Risk Threshold: Definition, Meaning & Example - PM Study Circle5: Risk Appetite vs Risk Tolerance vs Risk Threshold - projectcubicle6: [Security Policy Review and Update - SANS Institute] 7: [Control Effectiveness and Efficiency - ISACA] 8: [Vulnerability Management - ISACA] : [Risk andInformation Systems Control Study Manual, Chapter 1: IT Risk Identification, Section 1.1: IT Risk Concepts, pp. 17-19.] : [Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.1: Risk Identification, pp. 57-59.] : [Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.2: Risk Monitoring, pp. 189-191.] : [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.1: Control Design, pp. 233-235.] : [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.2: Control Implementation, pp. 243-245.] : [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.3: Control Monitoring and Maintenance, pp. 251-253.]
Which of the following is the ULTIMATE objective of utilizing key control indicators (KCIs) in the risk management process?
To provide insight into the effectiveness of the internal control environment
To provide a basis for determining the criticality of risk mitigation controls
To provide benchmarks for assessing control design effectiveness against industry peers
To provide early warning signs of a potential change in risk level
The ultimate objective of utilizing key control indicators (KCIs) in the risk management process is to provide early warning signs of a potential change in risk level, as they indicate the performance and adequacy of the controls, and alert the stakeholders to any control gaps or deficiencies that may affect the risk exposure and impact. The other options are not the ultimate objectives, as they are more related to the insight, basis, or benchmark of the risk managementprocess, respectively, rather than the early warning sign of the risk management process. References = CRISC Review Manual, 7th Edition, page 110.
Continuous monitoring of key risk indicators (KRIs) will:
ensure that risk will not exceed the defined risk appetite of the organization.
provide an early warning so that proactive action can be taken.
provide a snapshot of the risk profile.
ensure that risk tolerance and risk appetite are aligned.
Continuous monitoring of key risk indicators (KRIs) will provide an early warning so that proactive action can be taken, because it helps to detect and measure the changes or trends in the risk level or performance, and to alert the risk owners and stakeholders when the risk exceeds the predefined thresholds or targets. A KRI is a metric or indicator that helps to monitor and evaluate the likelihood or impact of a risk, or the effectiveness or efficiency of a control. A KRI can be quantitative or qualitative, and can be derived from internal or external sources. Continuous monitoring is a process of collecting and analyzing data on a regular or real-time basis, to provide timely and relevant information for decision making or action taking. Continuous monitoring of KRIs will provide an early warning, as it helps to identify and address the risk issues or incidents before they escalate or cause significant damage or disruption. Ensuring that risk will not exceed the defined risk appetite of the organization, providing a snapshot of the risk profile, and ensuring that risk tolerance and risk appetite are aligned are all possible outcomes of continuous monitoring of KRIs, but they are not the best answer, as they do not reflect the main purpose and benefit of continuous monitoring of KRIs, which is to provide an early warning. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.2, page 97
Which of the following is the MOST critical element to maximize the potential for a successful security implementation?
The organization ' s knowledge
Ease of implementation
The organization ' s culture
industry-leading security tools
According to the CRISC Review Manual, the organization’s culture is the most critical element to maximize the potential for a successful security implementation, because it influences the behavior, attitude, and perception of the stakeholders towards security. The organization’s culture includes the values, beliefs, norms, and practices that are shared by the members of the organization. A positive and supportive culture can foster the awareness, commitment, and collaboration of the stakeholders in achieving the security objectives and complying with the security policies and standards. The other options are not the most critical elements, as they are less influential or less challenging than the organization’s culture. The organization’s knowledge is the collective understanding and expertise of the organization regardingsecurity, which can be enhanced through training and education. Ease of implementation is the degree of difficulty and complexity of implementing security, which can be reduced by using appropriate methods and tools. Industry-leading security tools are the best-in-class solutions and technologies that can provide effective and efficient security, which can be acquired through market research and evaluation. References = CRISC Review Manual, 7th Edition, Chapter 1, Section 1.3.1, page 32.
Which stakeholder is MOST important to include when defining a risk profile during me selection process for a new third party application?
The third-party risk manager
The application vendor
The business process owner
The information security manager
A risk profile is a summary of the nature and level of risk that an organization faces. It includes information such as the sources, causes, and consequences of the risks, their likelihood and impact, their interrelationships and dependencies, and their alignment with the risk appetite and tolerance. A risk profile is influenced by various factors, such as the organization’s objectives, strategies, activities, processes, resources, capabilities, culture, etc. When defining a risk profile during the selection process for a new third party application, the stakeholder that is most important to include is the business process owner, who is the person who has the authority and responsibility for the design, execution, and performance of a business process. The business process owner can provide valuable input and insight into the requirements, expectations, and dependencies of the business process that will use the new third party application, and the potential risks and opportunities that may arise from the selection of the application. The business process owner can also help to prioritize and address the risks, and ensure that the risk profile is aligned with the business objectives and strategies. References = 5
A migration from an in-house developed system to an external cloud-based solution is affecting a previously rated key risk scenario related to payroll processing. Which part of the risk register should be updated FIRST?
Payroll system risk factors
Payroll system risk mitigation plans
Payroll process owner
Payroll administrative controls
Payroll system risk mitigation plans are the actions that are taken to reduce or eliminate the risk associated with payroll processing. When a migration from an in-house developed system to an external cloud-based solution is affecting a previously rated key risk scenario related to payroll processing, the first part of the risk register that should be updated is the payroll system risk mitigation plans. This is because the migration may introduce new risks or change the existing risks, and the risk mitigation plans may need to be revised or replaced accordingly. Updating the payroll system risk mitigation plans can help ensure that the risk level is acceptable and the payroll process is secure and reliable. According to the CRISC Review Manual 2022, one of the key risk treatment techniques is to update the risk action plan, which is a document that outlines the risk mitigation plans1. According to the CRISC Review Questions, Answers & Explanations Manual 2022, updating the risk mitigation plans is the correct answer to this question2.
Payroll system risk factors, payroll process owner, and payroll administrative controls are not the first part of the risk register that should be updated when a migration is affecting a key risk scenario. Payroll system risk factors are the sources or causes of risk, such as threats, vulnerabilities, or uncertainties. Payroll process owner is the person who is responsible for the payroll process and its outcomes. Payroll administrative controls are the policies, procedures, or guidelines that govern the payroll process. These parts of the risk register may also need to be updated, but they are not as urgent or critical as the risk mitigation plans. Updating the risk factors, process owner, and administrative controls can help identify, assess, and monitor the risk, but they do not directly address the risk response. The risk response is the most important part of the risk management process, as it determines how the risk is handled and controlled.
A global organization has implemented an application that does not address all privacy requirements across multiple jurisdictions. Which of the following risk responses has the organization adopted with regard to privacy requirements?
Risk avoidance
Risk transfer
Risk mitigation
Risk acceptance
The global organization has adopted risk acceptance as the risk response with regard to privacy requirements, as it has decided to continue with the implementation of the application that does not address all privacy requirements across multiple jurisdictions, and bear the potential consequences of noncompliance. Risk avoidance, risk transfer, and risk mitigation are not the risk responses adopted by the organization, as they would involve avoiding, sharing, or reducing the risk of noncompliance with privacy requirements, respectively. References = CRISC Review Manual, 7th Edition, page 111.
Which of the following should be the PRIMARY recipient of reports showing the
progress of a current IT risk mitigation project?
Senior management
Project manager
Project sponsor
IT risk manager
A project sponsor is the person or group who provides the financial, political, or organizational support for a project, and who has the authority to approve or reject the project’s objectives, scope, budget, schedule, and deliverables.
The primary recipient of reports showing the progress of a current IT risk mitigation project should be the project sponsor, because they are ultimately responsible for the success or failure of the project, and they need to be informed of the project’s status, issues, risks, and achievements on a regular basis.
The other options are not the primary recipients of reports showing the progress of a current IT risk mitigation project. They are either secondary or not essential for project reporting.
The references for this answer are:
Risk IT Framework, page 21
Information Technology & Security, page 15
Risk Scenarios Starter Pack, page 13
Which of the following BEST provides an early warning that network access of terminated employees is not being revoked in accordance with the service level agreement (SLA)?
Updating multi-factor authentication
Monitoring key access control performance indicators
Analyzing access control logs for suspicious activity
Revising the service level agreement (SLA)
According to the CRISC Review Manual (Digital Version), monitoring key access control performance indicators is the best way to provide an early warning that network access of terminated employees is not being revoked in accordance with the service level agreement (SLA), as it measures the effectiveness and efficiency of the access control process and its alignment with the SLA objectives and requirements. The SLA is a contract that defines the expectations and responsibilities of the service provider and the service recipient in terms of the quality, availability, and scope of the service. Monitoring key access control performance indicators helps to:
Evaluate the extent to which the access control process has met the SLA targets and standards
Identify and report any deviations, errors, or breaches in the access control process and its compliance with the SLA
Recommend and implement corrective actions or improvement measures to address the issues or findings in the access control process
Communicate and coordinate the monitoring results and recommendations with the relevant stakeholders, such as the service provider, the service recipient, and the senior management
References = CRISC Review Manual (Digital Version), Chapter 4: IT Risk Monitoring and Reporting, Section 4.1: IT Risk Monitoring, pp. 217-2181
Which of the following is the GREATEST concern when establishing key risk indicators (KRIs)?
High percentage of lagging indicators
Nonexistent benchmark analysis
Incomplete documentation for KRI monitoring
Ineffective methods to assess risk
The greatest concern when establishing key risk indicators (KRIs) is using ineffective methods to assess risk. KRIs are metrics that measure the likelihood and impact of risks, and help monitor and prioritize the most critical risks. To establish effective KRIs, the risk assessment methods should be reliable, valid, consistent, and timely. Ineffective methods to assess risk could lead to inaccurate or misleading KRIs, which could result in poor risk management decisions and outcomes. The other options are not as significant as using ineffective methods to assess risk, although they may also affect the quality and usefulness of KRIs. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.4.1, page 4-36.
Which of the following is MOST important to include in a Software as a Service (SaaS) vendor agreement?
An annual contract review
A service level agreement (SLA)
A requirement to adopt an established risk management framework
A requirement to provide an independent audit report
A service level agreement (SLA) is a contract between a SaaS vendor and a customer that defines the quality and availability of the SaaS service, as well as the responsibilities and obligations of both parties. An SLA is most important to include in a SaaS vendor agreement because it sets the expectations and standards for the SaaS service, provides a mechanism for measuring and monitoring the serviceperformance, and establishes the remedies and penalties for service failures or breaches. An SLA can also help to mitigate the risks and liabilities associated with SaaS delivery, such as data security, privacy, compliance, and disaster recovery. The other options are not the most important to include in a SaaS vendor agreement, although they may be beneficial or desirable depending on the context and nature of the SaaS service. An annual contract review is a process of evaluating and revising the SaaS vendor agreement to reflect the changing needs and circumstances of the customer and the vendor, but it is not a mandatory or essential element of the agreement. A requirement to adopt an established risk managementframework is a way of ensuring that the SaaS vendor follows the best practices and standards for identifying, assessing, and mitigating the risks related to the SaaS service, but it is not a specific or measurable term of the agreement. A requirement to provide an independent audit report is a way of verifying and validating the SaaS vendor’s compliance with the SLA and other contractual obligations, but it is not a direct or primary component of the agreement. References = SaaS Agreements: Key Contractual Provisions, SaaS Agreement: Everything You Need to Know, Essential checklist for SaaS agreement negotiations, KeyClauses To Understand and Evaluate in SaaS Contracts, SaaS Reseller Agreement: Everything You Need to Know
Which of the following is the BEST indication that key risk indicators (KRIs) should be revised?
An increase in the number of risk threshold exceptions
An increase in the number of change events pending management review
A decrease in the number of key performance indicators (KPIs)
A decrease in the number of critical assets covered by risk thresholds
Risk threshold exceptions are instances when a KRI exceeds or falls below a predefined level or point that triggers an action or a warning. An increase in the number of risk threshold exceptions indicates that the KRIs are not reflecting the current risk exposure or environment accurately oreffectively. This may suggest that the KRIs are outdated, irrelevant, or poorly defined. Therefore, the KRIs should be revised to ensure that they are aligned with the organizational objectives, risk appetite, and risk management strategy.
References
•Key Risk Indicators: A Practical Guide | SafetyCulture
•Key Risk Indicators: Examples & Definitions - SolveXia
•Choosing and Using Key Risk Indicators - Institute of Risk Management
An organization has recently been experiencing frequent data corruption incidents. Implementing a file corruption detection tool as a risk response strategy will help to:
reduce the likelihood of future events
restore availability
reduce the impact of future events
address the root cause
Implementing a file corruption detection tool as a risk response strategy will help to reduce the impact of future events, as it will enable the organization to identify and correct the corrupted files before they cause further damage or loss. A file corruption detection tool is a software that scans and verifies the integrity and validity of the files, and alerts the users or administrators of any anomalies or errors. This helps to minimize the disruption and downtime caused by the data corruption incidents, and to preserve the quality and reliability of the data. Implementing a file corruption detection tool will not reduce the likelihood of future events, as it does not prevent or mitigate the causes or sources of the data corruption incidents. It will not restore availability, as it does not recover or restore the corrupted files, but only detects them. It will not address the root cause, as it does not analyze or eliminate the underlying factors that lead to the data corruption incidents. References = CRISC Certified in Risk and Information Systems Control – Question215; ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 215.
Which of the following describes the relationship between risk appetite and risk tolerance?
Risk appetite is completely independent of risk tolerance.
Risk tolerance is used to determine risk appetite.
Risk appetite and risk tolerance are synonymous.
Risk tolerance may exceed risk appetite.
Relationship between Risk Appetite and Risk Tolerance:
Risk Appetite: Defined as the amount of risk an organization is willing to accept in pursuit of its objectives. It is a broad measure that reflects the organization ' s strategy and goals.
Risk Tolerance: Refers to the acceptable level of variation in performance relative to achieving objectives. It is narrower and can sometimes exceed the risk appetite in specific situations where deviations are permissible.
Contextual Understanding:
Controlled Exceedance: Risk tolerance allows for occasional and controlled exceedance of the risk appetite, typically under specific conditions and for compelling business reasons.
Management Decisions: Decisions to exceed risk appetite should be carefully considered and documented, ensuring they do not threaten the overall risk capacity of the organization.
Comparison with Other Options:
Independent of Each Other: Incorrect, as risk tolerance is related to risk appetite.
Risk Tolerance Determines Risk Appetite: Incorrect, risk appetite is generally broader and set before determining risk tolerance.
Synonymous: Incorrect, they are distinct concepts with risk tolerance providing operational flexibility within the boundaries set by risk appetite.
Best Practices:
Clear Definitions: Clearly define and communicate the organization’s risk appetite and risk tolerance.
Regular Reviews: Regularly review and adjust risk appetite and tolerance to align with changes in business strategy and external environment.
Which of the following BEST indicates the efficiency of a process for granting access privileges?
Average time to grant access privileges
Number of changes in access granted to users
Average number of access privilege exceptions
Number and type of locked obsolete accounts
According to the CRISC Review Manual, the average time to grant access privileges is the best indicator of the efficiency of a process for granting access privileges, because it measures how quickly and effectively the process can respond to the access requests and meet the business needs. The average time to grant access privileges can be calculated by dividing the total time spent on granting access privileges by the number of access requests processed. The other options are not the best indicators of the efficiency of the process, because they measure other aspects of the process, such as the quality, the security, or the maintenance. The number of changes in access granted to users measures the quality of the process, as it indicates how wellthe process can align the access rights with the user roles and functions. The average number of access privilege exceptions measures the security of the process, as it indicates how often theprocess deviates from the established policies and standards. The number and type of locked obsolete accounts measures the maintenance of the process, as it indicates how well the process can remove the unnecessary or outdated accounts. References = CRISC Review Manual, 7th Edition, Chapter 4, Section 4.1.2, page 163
An organization has implemented a preventive control to lock user accounts after three unsuccessful login attempts. This practice has been proven to be unproductive, and a change in the control threshold value has been recommended. Who should authorize changing this threshold?
Risk owner
IT security manager
IT system owner
Control owner
According to the CRISC Review Manual, a control owner is the person who is accountable for ensuring that specific control activities are performed. The control owner is responsible for defining, implementing, monitoring, and improving the control. Therefore, the control ownershould authorize changing the control threshold value, as it is part of their role to ensure that the control is effective and efficient. The other options are not the correct answers, because they are not directly involved in the control activities. The risk owner is the person who is accountable for the risk and its associated mitigation actions. The IT security manager is the person who is responsible for overseeing the IT security function and ensuring that the IT security policy is enforced. The IT system owner is the person who is responsible for the operation andmaintenance of the IT system and its associated data. References = CRISC Review Manual, 7th Edition, Chapter 3, Section 3.1.2, page 108.
Within the three lines of defense model, the PRIMARY responsibility for ensuring risk mitigation controls are properly configured belongs with:
line management.
the IT risk function.
enterprise compliance.
internal audit.
In the three lines of defense model, the primary responsibility for ensuring risk mitigation controls are properly configured belongs to line management.
First Line of Defense:
Operational Management:Line management is part of the first line of defense and is responsible for managing risks and implementing controls in their day-to-day operations.
Direct Control:They have the most direct control over processes and are best positioned to ensure that risk mitigation controls are properly configured and functioning as intended.
Responsibilities:
Implementation and Monitoring:Line management is responsible for both implementing the controls and monitoring their effectiveness. They are on the front lines of risk management and are integral to maintaining control effectiveness.
Accountability:They are accountable for ensuring that controls are aligned with the organization ' s risk management policies and procedures.
An organization has experienced a cyber-attack that exposed customer personally identifiable information (Pll) and caused extended outages of network services. Which of the following stakeholders are MOST important to include in the cyber response team to determine response actions?
Security control owners based on control failures
Cyber risk remediation plan owners
Risk owners based on risk impact
Enterprise risk management (ERM) team
Risk owners based on risk impact are the most important stakeholders to include in the cyber response team, as they are responsible for the business outcomes affected by the cyber attack and can decide on the appropriate response actions. The other options are not the most important stakeholders to include in the cyber response team, although they may be involved in the process.
Which component of a software inventory BEST enables the identification and mitigation of known vulnerabilities?
Software version
Assigned software manager
Software support contract expiration
Software licensing information
The software version is the component of a software inventory that best enables the identification and mitigation of known vulnerabilities. The software version is the specific release or update of a software product that has a unique identifier, such as a number or a name. The software version indicates the features, functions, and security patches that are included in the software product. By knowing the software version, the organization can compare it with the latest available version and identify any missing or outdated security fixes. The organization can then mitigate the known vulnerabilities by updating or upgrading the software to the latest version. The other components of a software inventory, such as the assigned software manager, the software support contract expiration, and the software licensing information, are not as directly related tothe identification and mitigation of known vulnerabilities, although they may provide some contextual or administrative information. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.3.2, page 2-25.
Which of the following is the BEST way to determine the ongoing efficiency of control processes?
Perform annual risk assessments.
Interview process owners.
Review the risk register.
Analyze key performance indicators (KPIs).
Control processes are the procedures and activities that aim to ensure the effectiveness and efficiency of the organization’s operations, the reliability of its information, and the compliance with its policies and regulations12.
The ongoing efficiency of control processes is the degree to which the control processes achieve their intended results with minimum resources, costs, or waste34.
The best way to determine the ongoing efficiency of control processes is to analyze key performance indicators (KPIs), which are quantifiable measures of progress toward an intended result, such as a strategic objective or a desired outcome56.
Analyzing KPIs is the best way because it provides a systematic and consistent method of evaluating the performance of the control processes, and identifying the areas of improvement or optimization56.
Analyzing KPIs is also the best way because it enables the organization to monitor and report the efficiency of the control processes to the relevant stakeholders, and to take corrective or preventive actions when necessary56.
The other options are not the best way, but rather possible sources of information or inputs that may support or complement the analysis of KPIs. For example:
Performing annual risk assessments is a way to identify and evaluate the risks that may affect the organization’s objectives, and to determine the adequacy and effectiveness ofthe control processes in mitigating those risks12. However, this way is not the best because it is periodic rather than continuous, and may not capture the changes or trends in the efficiency of the control processes12.
Interviewing process owners is a way to collect and verify the information and feedback from the people who are responsible for designing, implementing, and operating the control processes12. However, this way is not the best because it is subjective and qualitative, and may not provide reliable or comparable data on the efficiency of the control processes12.
Reviewing the risk register is a way to examine and update the documentation and status of the risks and the control processes that are associated with them12. However, this way is not the best because it is descriptive rather than analytical, and may not measure or evaluate the efficiency of the control processes12. References =
1: Risk IT Framework, ISACA, 2009
2: IT Risk Management Framework, University of Toronto, 2017
3: The Control Process | Principles of Management4
4: Control Management: What it is + Why It’s Essential | Adobe Workfront5
5: What is a Key Performance Indicator (KPI)? Guide & Examples - Qlik1
6: What is a Key Performance Indicator (KPI)? - KPI.org2
Which of the following should a risk practitioner review FIRST when evaluating risk events associated with the organization ' s data flow model?
Results of data classification activities
Recent changes to enterprise architecture (EA)
High-level network diagrams
Notes from interviews with the data owners
Senior management has asked the risk practitioner for the overall residual risk level for a process that contains numerous risk scenarios. Which of the following should be provided?
The sum of residual risk levels for each scenario
The loss expectancy for aggregated risk scenarios
The highest loss expectancy among the risk scenarios
The average of anticipated residual risk levels
Residual risk is the remaining risk after the risk response has been implemented. Residual risk can be expressed as a combination of the probability and impact of the risk scenario, or as a single value such as loss expectancy. Residual risk can be compared with the inherent risk, which is the risk level before considering the existing controls or responses, to evaluate the risk reduction and value creation of the risk response. Senior management has asked the risk practitioner for the overall residual risk level for a process that contains numerous risk scenarios. The best way to provide this information is to calculate the average of anticipated residual risklevels for each risk scenario, and to present it as a single value or a range. This can help to provide a comprehensive and consistent view of the residual risk exposure and performance of the process, as well as to align it with the organization’s risk appetite and tolerance. The sum of residual risk levels for each scenario, the loss expectancy for aggregated risk scenarios, or the highest loss expectancy among the risk scenarios are not the best ways to provide the overall residual risk level, as they may overestimate or underestimate the risk exposure and performance of the process, and may not reflect the actual risk reduction and value creation of the risk response. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.2, p. 108-109
Changes in which of the following would MOST likely cause a risk practitioner to adjust the risk impact rating in the risk register?
Control effectiveness
Risk appetite
Control costs
Risk tolerance
Control effectiveness directly influences risk severity—stronger controls reduce impact, weaker ones increase it. ISACA guidelines specify that ongoing impact ratings should reflect updated control performance assessments.
A risk heat map is MOST commonly used as part of an IT risk analysis to facilitate risk:
communication
identification.
treatment.
assessment.
A risk heat map is a tool that shows the likelihood and impact of different risks on a matrix, using colors to indicate the level of risk. A risk heat map is most commonly used as part of an IT risk analysis to facilitate risk assessment, which is the process of estimating the probability and consequences of the risks, and comparing them against the risk criteria1. A risk heat map can help to visualize, communicate, and prioritize the risks, as well as to evaluate the effectiveness of the risk response actions2. The other options are not the best choices for describing the purpose of a risk heat map, as they are either less specific or less relevant than risk assessment. Risk communication is the process of sharing and exchanging information about the risks among the stakeholders3. A risk heat map can support risk communication by providing a clear and concise representation of the risks, but it is not the main objective of the tool. Riskidentification is the process of finding, recognizing, and describing the risks that may affect the organization4. A risk heat map can help to identify the risks by categorizing them into different domains or sources, but it is not the primary function of the tool. Risk treatment is the process of selecting and implementing the appropriate measures to modify the risk5. A risk heat map can help to guide the risk treatment by showing the risk ratings and thresholds, but it is not the core purpose of the tool. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.1, Page 47.
Due to a change in business processes, an identified risk scenario no longer requires mitigation. Which of the following is the MOST important reason the risk should remain in the risk register?
To support regulatory requirements
To prevent the risk scenario in the current environment
To monitor for potential changes to the risk scenario
To track historical risk assessment results
A risk register is a document that records and tracks the identified risks, their causes, impacts, likelihood, responses, and status. A risk register can help manage and communicate risks throughout the risk management process. A risk register should be updated regularly to reflect the current state of risks and their responses. Due to a change in business processes, an identified risk scenario may no longer require mitigation, as the risk level may have decreased or the risk may have been eliminated. However, the risk should remain in the risk register, as the most important reason is to monitor for potential changes to the risk scenario. This means keeping track of the internal and external factors that may affect the risk scenario, such as new threats, vulnerabilities, opportunities, or controls. Monitoring for potential changes to the risk scenario can help identify and respond to any emerging or reoccurring risks, and ensure that therisk register is accurate and complete. References = Risk and Information Systems Control Study Manual, Chapter 1: IT Risk Identification, Section 1.3: Risk Register, p. 41-43.
Conduct frequent internal audits of IT systems.
Review information from threat intelligence sources.
Define a comprehensive set of key risk indicators (KRIs).
Document thorough IT risk scenarios in the risk register.
The identification of advanced persistent threats (APTs) is best supported by timely and relevant external information. Reviewing information from threat intelligence sources enables the organization to detect emerging threats quickly and accurately, reducing the mean time to identify APTs. While internal audits and KRIs are important, they typically focus on internal controls and risk monitoring rather than external threat detection. Thorough documentation of risk scenarios supports risk assessment but does not directly reduce detection time. Therefore, leveraging threat intelligence is the most effective approach for early identification of sophisticated threats.
A risk assessment has identified that an organization may not be in compliance with industry regulations. The BEST course of action would be to:
conduct a gap analysis against compliance criteria.
identify necessary controls to ensure compliance.
modify internal assurance activities to include control validation.
collaborate with management to meet compliance requirements.
According to the CRISC Review Manual (Digital Version), the best course of action when a risk assessment has identified that an organization may not be in compliance with industry regulations is to conduct a gap analysis against compliance criteria, which is a method of comparing the current state of compliance with the desired or required state of compliance. Conducting a gap analysis against compliance criteria helps to:
Identify and evaluate the differences or discrepancies between the compliance requirements and the actual compliance practices and capabilities
Assess the impact and severity of the compliance gaps on the organization’s objectives and performance
Prioritize the compliance gaps based on their urgency and importance
Develop and implement appropriate actions or measures to close or reduce the compliance gaps
Monitor and measure the effectiveness and efficiency of the actions or measures taken to address the compliance gaps
References = CRISC Review Manual (Digital Version), Chapter 1: IT Risk Identification, Section 1.5: IT Risk Identification Methods and Techniques, pp. 34-351
Which of the following is the PRIMARY risk management responsibility of the second line of defense?
Monitoring risk responses
Applying risk treatments
Providing assurance of control effectiveness
Implementing internal controls
The primary risk management responsibility of the second line of defense is to monitor the risk responses. The second line of defense is the function that oversees and supports the risk management activities of the first line of defense, which is the function that owns and manages the risks. The second line of defense includes the risk management, compliance, and quality assurance functions, among others. The second line of defense is responsible for monitoring the risk responses, which are the actions taken to address the risks, such as avoiding, transferring, mitigating, or accepting the risks. The second line of defense monitors the risk responses to ensure that they are implemented effectively and efficiently, that they achieve the desired outcomes, and that they are aligned with the risk appetite and tolerance of the organization. The second line of defense also provides guidance, advice, and feedback to the first line of defense on the risk responses, and reports the results and issues to the senior management and the board. Applying risk treatments, providing assurance of control effectiveness, and implementing internal controls are not the primary risk management responsibilities of the second line of defense, as they are either the responsibilities of the first line of defense or the third line ofdefense, which is the function that provides independent assurance of the risk management activities, such as the internal audit function. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 36.
Establishing and organizational code of conduct is an example of which type of control?
Preventive
Directive
Detective
Compensating
According to the CRISC Review Manual (Digital Version), establishing an organizational code of conduct is an example of a directive control, which is a type of control that guides or steers the behavior of individuals or processes to achieve desired outcomes. A directive control aims toinfluence or encourage compliance with the organization’s policies, standards, procedures, and guidelines. A directive control can also communicate the organization’s values, ethics, and expectations to its stakeholders. A directive control can take various forms, such as:
Codes of conduct or ethics
Policies or manuals
Training or awareness programs
Job descriptions or roles and responsibilities
Performance appraisals or incentives
Supervision or oversight
References = CRISC Review Manual (Digital Version), Chapter 2: IT Risk Assessment, Section 2.4: IT Risk Scenarios, pp. 105-1061
Which of the following will BEST ensure that controls adequately support business goals and objectives?
Using the risk management process
Enforcing strict disciplinary procedures in case of noncompliance
Reviewing results of the annual company external audit
Adopting internationally accepted controls
Using the risk management process will best ensure that controls adequately support business goals and objectives, as it involves identifying, assessing, responding, and monitoring the risks that may affect the achievement of the business goals and objectives, and designing and implementing controls to mitigate those risks. Enforcing strict disciplinary procedures in case of noncompliance, reviewing results of the annual company external audit, and adopting internationally accepted controls are also good practices, but they are not the best, as they do not necessarily align the controls with the business goals and objectives. References = CRISC Review Manual, 7th Edition, page 146.
A risk practitioner has been notified of a social engineering attack using artificial intelligence (Al) technology to impersonate senior management personnel. Which of the following would BEST mitigate the impact of such attacks?
Training and awareness of employees for increased vigilance
Increased monitoring of executive accounts
Subscription to data breach monitoring sites
Suspension and takedown of malicious domains or accounts
Understanding the Question:
The question is about mitigating the impact of social engineering attacks that use AI technology to impersonate senior management personnel.
Analyzing the Options:
A. Training and awareness of employees for increased vigilance:This is the most proactive approach. Educating employees about the risks and signs of social engineering attacks enhances their ability to recognize and respond appropriately to such threats.
B. Increased monitoring of executive accounts:Useful but reactive; it doesn ' t prevent initial attempts.
C. Subscription to data breach monitoring sites:Helps detect breaches but doesn’t directly mitigate impersonation attacks.
D. Suspension and takedown of malicious domains or accounts:Reactive measure and might not be immediate or comprehensive.
Importance of Training:Employees are often the first line of defense against social engineering attacks. Regular training ensures they are aware of the tactics used in such attacks, including those leveraging AI, and how to respond effectively.
Proactive Measure:Training increases vigilance and the likelihood of early detection, reducing the potential impact of the attack.
Which of the following is MOST important for ensuring anonymous reporting of non-compliant activity?
Implementing homomorphic encryption.
Establishing an employee feedback channel.
Establishing a dedicated compliance function.
Implementing an incentive program.
The correct answer is B because anonymous reporting requires a reporting channel through which employees can raise concerns or report non-compliant activity without being personally identified. ISACA’s Code of Professional Ethics includes reporting obligations and states that anyone who witnesses a member violation can report it through the ethics complaint process.
The uploaded CRISC notes emphasize that a risk-aware culture escalates issues when suspicious activity is noticed and that failure to internally report a successful attack is a major concern.
A is too technical and unrelated to employee reporting. C may support compliance oversight, but it does not ensure anonymous reporting. D may encourage reporting, but incentives do not provide anonymity.
===========
An organization delegates its data processing to the internal IT team to manage information through its applications. Which of the following is the role of the internal IT team in this situation?
Data controllers
Data processors
Data custodians
Data owners
Data processing is the activity of collecting, organizing, transforming, and analyzing data to produce useful information for decision making or other purposes12.
The role of the internal IT team in this situation is data processors, which are the people or entities that process data on behalf of the data controllers, who are the people or entities that determine the purposes and means of the data processing34.
Data processors are the role of the internal IT team because they are responsible for managing information through the applications that are used by the organization, and they act under the instructions and authority of the organization, which is the data controller34.
Data processors are also the role of the internal IT team because they have to comply with the data protection laws and regulations that apply to the data processing, and they have to ensure the security and confidentiality of the data34.
The other options are not the role of the internal IT team, but rather possible roles or terms that are related to data processing. For example:
Data custodians are the people or entities that have physical or logical control over the data, and they are responsible for implementing and maintaining the technical and administrative safeguards to protect the data56. However, this role is not the role of theinternal IT team because it is a subset or function of the data processor role, and it does not reflect the full scope of the data processing activities that the internal IT team performs56.
Data owners are the people or entities that have legal rights or authority over the data, and they are responsible for defining and enforcing the policies and rules for the data access, use, and quality . However, this role is not the role of the internal IT team because it is a different or separate role from the data processor role, and it does not reflect the relationship or agreement between the organization and the internal IT team . References =
1: Data Processing - Wikipedia1
2: Data Processing: Definition, Steps, and Types2
3: Data Controller vs Data Processor: What’s the Difference?3
4: Data controller vs data processor: What are the differences and responsibilities?4
5: Data Custodian - Wikipedia5
6: Data Custodian: Definition, Role & Responsibilities6
Data Owner - Wikipedia
Data Owner: Definition, Role & Responsibilities
Which of the following would be a risk practitioner ' s MOST important action upon learning that an IT control has failed?
Implement a replacement control.
Adjust residual risk rating.
Escalate to senior management.
Review compensating controls.
Upon discovering that an IT control has failed, the risk practitioner ' s most important action is to review compensating controls. This involves assessing whether other existing controls can mitigate the risk associated with the failed control. Evaluating compensating controls helps determine the immediate impact of the control failure and guides decisions on necessary remediation steps.
Which of the following BEST helps to balance the costs and benefits of managing IT risk?
Prioritizing risk responses
Evaluating risk based on frequency and probability
Considering risk factors that can be quantified
Managing the risk by using controls
Prioritizing risk responses helps to balance the costs and benefits of managing IT risk by ensuring that the most significant risks are addressed first and that the resources allocated to risk management are used efficiently and effectively. Evaluating risk based on frequency and probability is a part of risk analysis, not risk response. Considering risk factors that can be quantified is also a part of risk analysis, and it does not necessarily capture all the relevant aspects of risk. Managing the risk by using controls is a possible risk response, but it does not guarantee that the costs and benefits of risk management are balanced, as some controls may be too expensive or ineffective for the level of risk they mitigate. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk Response, page 145.
An organization has outsourced its lease payment process to a service provider who lacks evidence of compliance with a necessary regulatory standard. Which risk treatment was adopted by the organization?
Acceptance
Transfer
Mitigation
Avoidance
According to the ERM - Step 3 - Risk Treatment article, risk transfer is a risk treatment option that involves passing ownership and/or liability of a risk to a third party, such as an insurance company, a contractor, or a supplier. Risk transfer is usually adopted when the organization does not have the capability or the resources to manage the risk internally, or when the cost of transferring the risk is lower than the cost of retaining the risk. In this case, the organization has outsourced its lease payment process to a service provider who lacks evidence of compliance with a necessary regulatory standard. This means that the organization has transferred the risk ofnon-compliance to the service provider, who is now responsible for ensuring that the lease payment process meets the regulatory requirements. Therefore, the answer is B. Transfer. References = ERM - Step 3 - Risk Treatment
Which of the following is the MOST essential factor for managing risk in a highly dynamic environment?
Ongoing sharing of information among industry peers
Obtaining support from senior leadership
Adhering to industry-recognized risk management standards
Implementing detection and response measures
There is no definitive answer to this question, as different factors may be more or less important depending on the context and the nature of the risk. However, based on some web search results, one possible factor that could be considered essential for managing risk in a highly dynamic environment is D. Implementing detection and response measures.
Detection and response measures are the practices and procedures that enable an organization to identify and mitigate any potential or actual cybersecurity events that could compromise its network, systems, data, or assets. Detection and response measures can help an organization to reduce the impact and duration of a cyberattack, as well as to learn from the incident and improve its security posture and resilience. Detection and response measures can also help an organization to comply with regulatory and legal requirements, as well as to maintain its reputation and trust among its stakeholders.
Some examples of detection and response measures include:
•Using threat intelligence, user behavior analytics, and attacker behavior analytics to monitor and analyze the network activity and identify any anomalies or signs of compromise 12
•Implementing security continuous monitoring, intrusion detection and prevention systems, and antivirus and antimalware software to detect and block malicious traffic and malware 3
•Establishing incident response plans, teams, and tools to contain, eradicate, and recover from a cyberattack, as well as to communicate and coordinate with internal and external parties 45
•Conducting regular audits, assessments, and tests to evaluate the effectiveness of the detection and response measures and to identify any gaps or weaknesses 6
Therefore, implementing detection and response measures could be seen as an essential factor for managing risk in a highly dynamic environment, as it can help an organization to protect its critical assets and functions, and to respond quickly and effectively to any emerging or evolving threats.
A systems interruption has been traced to a personal USB device plugged into the corporate network by an IT employee who bypassed internal control procedures. Of the following, who should be accountable?
Business continuity manager (BCM)
Human resources manager (HRM)
Chief risk officer (CRO)
Chief information officer (CIO)
A systems interruption caused by a personal USB device plugged into the corporate network by an IT employee who bypassed internal control procedures is a serious breach of information security and IT risk management. The person who should be accountable for this incident is the chief information officer (CIO), who is responsible for overseeing the IT function and ensuring compliance with IT policies and standards. The CIO should also ensure that appropriate corrective and preventive actions are taken to prevent such incidents from recurring and to mitigate the impact of the systems interruption on the business operations and objectives. The CIO should also report the incident to the senior management and the board of directors, and communicate with the relevant stakeholders about the incident and the actions taken. References = Risk IT Framework, ISACA, 2022, p. 181
Management has required information security awareness training to reduce the risk associated with credential compromise. What is the BEST way to assess the effectiveness of the training?
Conduct social engineering testing.
Audit security awareness training materials.
Administer an end-of-training quiz.
Perform a vulnerability assessment.
Conducting social engineering testing is the best way to assess the effectiveness of the security awareness training, as it helps to measure and evaluate the actual behavior and response of the employees to simulated real-world attacks that exploit human vulnerabilities. Social engineering testing is a type of security testing that involves performing authorized and ethical hacking activities on the employees to manipulate them into revealing sensitive information, such as credentials, or performing malicious actions, suchas clicking on a phishing link or opening a malicious attachment. Social engineering testing can help to assess the effectiveness of the security awareness training by providing the following benefits:
It tests the employees’ knowledge and skills in recognizing and resisting social engineering attacks, such as phishing, vishing, baiting, or impersonation.
It identifies and measures the strengths and weaknesses of the employees’ security awareness and behavior, and the impact and severity of their actions on the security posture and risk exposure of the organization.
It provides feedback and learning opportunities for the employees to improve their security awareness and behavior, and to reinforce the key concepts and practices taught in the training.
It communicates and reports the results and findings of the testing to the management and the stakeholders, and supports the development and implementation of corrective or preventive actions.
The other options are not the best ways to assess the effectiveness of the security awareness training. Auditing security awareness training materials is a good practice to ensure that the training content is accurate, relevant, and up-to-date, but it does not measure or evaluate the employees’ security awareness and behavior. Administering an end-of-training quiz is a useful method to test the employees’ comprehension and retention of the training content, but it does not reflect or simulate the employees’ security awareness and behavior in real-world situations. Performing a vulnerability assessment is an important step to identify and analyze the potential vulnerabilities in the systems and software, but it does not assess or address the human vulnerabilities or the employees’ security awareness and behavior. References = 3 ways to assess the effectiveness of security awareness training …, IT Risk Resources | ISACA, Measuring the Effectiveness of Security Awareness Training - Hut Six
A bank has outsourced its statement printing function to an external service provider. Which of the following is the MOST critical requirement to include in the contract?
Monitoring of service costs
Provision of internal audit reports
Notification of sub-contracting arrangements
Confidentiality of customer data
The MOST critical requirement to include in the contract is the confidentiality of customer data, because it is a legal and ethical obligation of the bank to protect the privacy and security of its customers’ personal and financial information. Outsourcing the statement printing function to an external service provider exposes the customer data to potential unauthorized access, disclosure, or misuse by the service provider or its sub-contractors. Therefore, the contract should specify the terms and conditions for the handling, storage, and disposal of the customer data, as well as the penalties for any breach of confidentiality. The other options are not as critical as the confidentiality of customer data, because:
Option A: Monitoring of service costs is an important requirement to ensure that the service provider delivers the statement printing function within the agreed budget and scope, but it is not as critical as the confidentiality of customer data, which has legal and reputational implications for the bank.
Option B: Provision of internal audit reports is a useful requirement to verify that the service provider complies with the internal and external standards and regulations for the statement printing function, but it is not as critical as the confidentiality of customer data, which is a core value of the bank and its customers.
Option C: Notification of sub-contracting arrangements is a relevant requirement to ensure that the service provider does not delegate the statement printing function to another party without the bank’s consent and oversight, but it is not as critical as the confidentiality of customer data, which is the primary responsibility of the bank and its service provider. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 197.
Which of the following BEST enables the timely detection of changes in the security control environment?
Control self-assessment (CSA)
Log analysis
Security control reviews
Random sampling checks
Understanding the Question:
The question asks which method best enables timely detection of changes in the security control environment.
Analyzing the Options:
A. Control self-assessment (CSA):Allows for continuous monitoring and quick detection of any changes or deficiencies in controls.
B. Log analysis:Useful for detecting security incidents but not as comprehensive as CSA for overall control environment changes.
C. Security control reviews:Typically periodic and might not be as timely.
D. Random sampling checks:Not as systematic or comprehensive as CSA.
Control Self-Assessment (CSA):CSA involves regular, structured evaluations by internal staff to ensure controls are working effectively. It promotes early detection of issues by those directly responsible for the controls.
Timeliness:CSA is an ongoing process, making it more timely in identifying changes compared to periodic reviews or random checks.
Which of the following is the GREATEST concern when using artificial intelligence (AI) language models?
The model could be hacked or exploited.
The model could be used to generate inaccurate content.
Staff could become overly reliant on the model.
It could lead to biased recommendations.
Biased recommendations from AI models pose significant risks to decision-making and organizational ethics. Such biases can propagate systemic issues and impact regulatory compliance, emphasizing the need for robust controls in AI development and deployment underEmerging Technology Risks.
An organization is implementing encryption for data at rest to reduce the risk associated with unauthorized access. Which of the following MUST be considered to assess the residual risk?
Data retention requirements
Data destruction requirements
Cloud storage architecture
Key management
The most important factor to consider when assessing the residual risk of implementing encryption for data at rest is the key management. Key management is the process of generating, storing, distributing, using, and destroying the cryptographic keys that are used to encrypt anddecrypt the data. Key management is essential for ensuring the security, availability, and integrity of the encrypted data, as well as for complying with the legal and regulatory requirements. Poor key management could result in the loss, theft, compromise, or corruption of the keys, which could lead to unauthorized access, data breach, data loss, or data recovery failure. Therefore, key management must be considered to assess the residual risk, which is the risk that remains after the risk treatment, such as encryption, is applied. Data retention requirements, data destruction requirements, and cloud storage architecture are not as important as key management, as they do not directly affect the encryption and decryption of the data, and they may not introduce significant residual risk. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 217.
During a review of the asset life cycle process, a risk practitioner identified several unreturned and unencrypted laptops belonging to former employees. Which of the following is the GREATEST concern with this finding?
Insufficient laptops for existing employees
Abuse of leavers ' account privileges
Unauthorized access to organizational data
Financial cost of replacing the laptops
The greatest concern with finding unreturned and unencrypted laptops belonging to former employees is the risk of unauthorized access to organizational data. The laptops may containsensitive or confidential information that could be compromised if they fall into the wrong hands. This could result in data breaches, reputational damage, legal liabilities, or regulatory penalties for the organization. Therefore, it is important to have proper controls in place to ensure that the laptops are returned, wiped, or encrypted when the employees leave the organization.
A control owner responsible for the access management process has developed a machine learning model to automatically identify excessive access privileges. What is the risk practitioner ' s BEST course of action?
Review the design of the machine learning model against control objectives.
Adopt the machine learning model as a replacement for current manual access reviews.
Ensure the model assists in meeting regulatory requirements for access controls.
Discourage the use of emerging technologies in key processes.
The risk practitioner’s best course of action is to review the design of the machine learning model against the control objectives, because this will help to evaluate the suitability, effectiveness, and reliability of the model as a control measure. A machine learning model is a type of artificial intelligence that can learn from data and make predictions or decisions based on the data. A machine learning model can be used to automate or enhance the access management process, such as by identifying excessive access privileges, detecting unauthorized access, or recommending access rights. However, a machine learning model also introduces new risks and challenges, such as data quality, model accuracy, model bias, model explainability, model security, and model governance. Therefore, the risk practitioner should review the design of the machine learning model against the control objectives, which are the specific goals or outcomes that the control is intended to achieve. The control objectives can be derived from the IT riskmanagement strategy, the IT governance framework, the IT policies and standards, and the regulatory requirements. The review of the machine learning model should cover the following aspects: - The data sources and inputs: The risk practitioner should verify that the data used to train and test the machine learning model is relevant, complete, accurate, consistent, and representative of the access management process and the access rights. The risk practitioner should also check that the data is collected, stored, processed, and transmitted in a secure and compliant manner, and that the data privacy and confidentiality are protected. - The model algorithms and outputs: The risk practitioner should validate that the model algorithms are appropriate, robust, and transparent for the access management process and the control objectives. The risk practitioner should also evaluate that the model outputs are accurate, reliable, and interpretable, and that they provide meaningful and actionable insights orrecommendations for the access management process and the control objectives. - The model performance and monitoring: The riskpractitioner should measure and monitor the model performance and effectiveness against the control objectives and the predefined metrics and indicators. The risk practitioner should also ensure that the model is updated and maintained regularly to reflect the changes in the access management process and the access rights, and that the model is audited and reviewed periodically to ensure its compliance and quality. By reviewing the design of the machine learning model against the control objectives, the risk practitioner can ensure that the model is fit for purpose and adds value to the access management process and the control objectives. The risk practitioner can also identify and mitigate any potential risks or issues that may arise from the use of the machine learning model as a control measure. References = Risk and Information Systems Control Study Manual, Chapter 3: Risk Response and Mitigation, Section 3.3: Control Design and Implementation, pp. 124-1271, Manage roles in your workspace - Azure Machine Learning2, Dataset Inference: Ownership Resolution in Machine Learning3
Which of the following is the ULTIMATE objective of utilizing key control indicators (KCIs) in the risk management process?
To provide a basis for determining the criticality of risk mitigation controls
To provide early warning signs of a potential change in risk level
To provide benchmarks for assessing control design effectiveness against industry peers
To provide insight into the effectiveness of the intemnal control environment
Key control indicators (KCIs) are metrics that measure the performance of a control in reducing the causes, consequences, or likelihood of a risk. They help to evaluate the adequacy and efficiency of the internal control environment, which is the set of policies, procedures, and practices that support the achievement of organizational objectives and the management of risks. By monitoring KCIs, organizations can identify and address any gaps or weaknesses in their internal controls and ensure that they are operating as intended.
References
•ISACA CRISC Review Manual, 7th Edition, Domain 3: Risk Response, Section 3.2.2: Control Design and Implementation
•KRI Framework for Operational Risk Management | Workiva
•What is the difference between key risk indicators and key control indicators?
Which of the following is the GREATEST risk of relying on artificial intelligence (Al) within heuristic security systems?
Al may result in less reliance on human intervention.
Malicious activity may inadvertently be classified as normal during baselining.
Risk assessments of heuristic security systems are more difficult.
Predefined patterns of malicious activity may quickly become outdated.
AI in Heuristic Security Systems:
Heuristic security systems use artificial intelligence (AI) to identify and respond to potential threats by learning from data patterns and behaviors.
Risk of Misclassification:
During the baselining process, AI systems establish what is considered normal behavior. If malicious activity is present during this period, it may be incorrectly classified as normal.
This misclassification can lead to undetected security breaches, as the system will not recognize these activities as threats in the future.
Impact of Misclassification:
Misclassified malicious activities can lead to significant security risks, allowing attackers to operate undetected within the system.
It undermines the effectiveness of the heuristic system, reducing its ability to protect the organization from real threats.
Comparing Other Risks:
Less Reliance on Human Intervention:This is a general concern but does not directly impact the accuracy of threat detection.
Difficulty in Risk Assessments:While a challenge, it is not the greatest risk compared to misclassification of malicious activity.
Outdated Patterns:While a concern, the primary risk lies in initial misclassification during baselining.
References:
The CRISC Review Manual discusses the challenges of AI in security systems, particularly the risk of misclassification during the learning phase (CRISC Review Manual, Chapter 4: Information Technology and Security, Section 4.7.4 Artificial Intelligence) .
An organization ' s decision to remain noncompliant with certain laws or regulations is MOST likely influenced by:
The region in which the organization operates.
Established business culture.
Risk appetite set by senior management.
Identified business process controls.
Risk appetite determined by senior management reflects the enterprise ' s willingness to accept certain levels of risk, including noncompliance. This decision underscores the strategic trade-offs made in risk management, a key element inGovernance and Risk Policy Alignment.
Which of the following is the PRIMARY purpose of analyzing control effectiveness during risk analysis?
To enable a control cost-benefit analysis
To evaluate the risk impact
To determine the likelihood of occurrence
To determine the current risk level
During risk analysis, CRISC distinguishes between inherent risk (without controls) and residual or current risk (with controls). Analyzingcontrol effectiveness—both in design and operation—is central to determining thecurrent risk level. Effective controls reduce either the likelihood of occurrence, the impact, or both. The assessment of their strength, coverage, and reliability allows the practitioner to adjust the initial inherent risk estimate down to a realistic residual risk figure and compare this to appetite and tolerance. Cost-benefit analysis of controls is a later step in risk response decision-making. Impact evaluation depends more on the nature of assets and processes than on controls. Likelihood is influenced by controls, but the primary purpose of control effectiveness analysis is to calculate the updated (residual) risk level, not just likelihood independently.
An organization’s expense claim system allows users to split large transactions into smaller ones to bypass limits. What should the risk practitioner do?
Conduct an audit to determine the frequency of occurrence
Update the probability in the risk register
Create a noncompliance risk scenario
Weigh compliance against the cost-benefit
This behavior representsintentional circumvention of control, requiring formal documentation and assessment as anoncompliance risk scenario.
CRISC principle:
“When control circumvention occurs, the risk practitioner should document the event as a noncompliance risk scenario to evaluate its impact and treatment.”
The other options—auditing, probability updates, or cost analysis—may follow, but the first step isformal recognitionof the risk within the risk register via a new scenario.
CRISC Reference:Domain 2 – IT Risk Assessment, Topic: Scenario Development and Control Evaluation.
Which of the following is the MOST useful information for prioritizing risk mitigation?
Cost of risk mitigation
Asset criticality
Acceptable risk level
Business impact assessment
Business Impact Assessment (BIA):
BIA identifies and evaluates the potential effects of interruptions to critical business operations. It helps determine the priority of risk mitigation efforts based on the potential impact on business functions.
BIA provides detailed information on which processes and systems are most critical to the organization ' s operations and their respective impact levels.
Prioritizing Risk Mitigation:
The results of a BIA guide decision-makers in prioritizing which risks to address first based on their potential to disrupt critical business operations.
Risks that could cause significant operational, financial, or reputational damage are prioritized higher.
Comparing Other Factors:
Cost of Risk Mitigation:Important but secondary to understanding the impact on business operations.
Asset Criticality:Relevant but typically part of the BIA process.
Acceptable Risk Level:Defines the threshold but does not prioritize specific risks.
References:
The CRISC Review Manual discusses how BIA facilitates risk prioritization by identifying critical processes and their impacts (CRISC Review Manual, Chapter 2: IT Risk Assessment, Section 2.7 Business Impact Analysis).
An organization maintains independent departmental risk registers that are not automatically aggregated. Which of the following is the GREATEST concern?
Management may be unable to accurately evaluate the risk profile.
Resources may be inefficiently allocated.
The same risk factor may be identified in multiple areas.
Multiple risk treatment efforts may be initiated to treat a given risk.
The greatest concern of maintaining independent departmental risk registers that are not automatically aggregated is that management may be unable to accurately evaluate the risk profile. The risk profile is the overall view of the risks that the organization faces and their impact on the organization’s objectives. It helps management to prioritize and allocate resources for risk management and to align the risk appetite and strategy. If the departmental risk registers are not aggregated, management may not have a complete and consistent picture of the risks across the organization. They may miss some important risks, overestimate or underestimate some risks, or have conflicting or redundant risk information. This may lead to poor risk management decisions and outcomes. The other options are also concerns, but they are not ascritical as the inability to evaluate the risk profile. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.2: IT Risk Analysis, page 63.
Which of the following is the BEST way to promote adherence to the risk tolerance level set by management?
Defining expectations in the enterprise risk policy
Increasing organizational resources to mitigate risks
Communicating external audit results
Avoiding risks that could materialize into substantial losses
According to the Risk Appetite vs. Risk Tolerance: What is the Difference? article, risk tolerance is the acceptable level of variation that an organization is willing to accept around a specific objective. Risk tolerance is usually expressed as a range or a limit, and it helps to guide the decision making and risk taking of the organization. The best way to promote adherence to the risk tolerance level set by management is to define the expectations in the enterprise risk policy, which is a document that establishes the organization’s risk management framework, principles, and objectives. By defining the expectations in the enterprise risk policy, the organization can communicate the risk tolerance level to all the relevant stakeholders, and ensure that they understand and follow the risk management guidelines and standards. This can help to create aconsistent and coherent risk culture across the organization, and to avoid any deviations or violations of the risk tolerance level. References = Risk Appetite vs. Risk Tolerance: What is the Difference?
Which of the following will BEST help an organization select a recovery strategy for critical systems?
Review the business impact analysis.
Create a business continuity plan.
Analyze previous disaster recovery reports.
Conduct a root cause analysis.
According to the CRISC Review Manual (Digital Version), reviewing the business impact analysis (BIA) will best help an organization select a recovery strategy for critical systems, as it provides an assessment of the potential impact and consequences of a disruption to the organization’s critical business functions and processes. Reviewing the BIA helps to:
Identify and prioritize the critical systems and their dependencies that support the critical business functions and processes
Estimate the maximum tolerable downtime (MTD) and the recovery time objective (RTO) for each critical system
Evaluate the feasibility and cost-effectiveness of various recovery strategies and options for each critical system
Select the most appropriate recovery strategy and option for each critical system based on the organization’s objectives and requirements
Develop and implement the recovery plan and procedures for each critical system
References = CRISC Review Manual (Digital Version), Chapter 3: IT Risk Response, Section 3.3: Risk Response Options, pp. 174-1751
Which of the following is MOST important to review when evaluating the ongoing effectiveness of the IT risk register?
The costs associated with mitigation options
The status of identified risk scenarios
The cost-benefit analysis of each risk response
The timeframes for risk response actions
The status of identified risk scenarios, because it helps to monitor and track the current level and direction of the IT risks, and to determine whether the risk responses and controls are adequate and effective. An IT riskregister is a document that records and tracks the key IT risks that an organization faces, along with their likelihood, impact, and response strategies. An IT risk scenario is a hypothetical situation or event that describes the source, cause, consequence, and impact of an IT risk. The status of identified risk scenarios is the most important factor, as it reflects the actual and potential outcomes of the IT risks, and the performance and progress of the risk management process. The costs associated with mitigation options, the cost-benefit analysis of each risk response, and the timeframes for risk response actions are all possible factors to review when evaluating the ongoing effectiveness of the IT risk register, but they are not the most important factor, as they do not directly measure and report the status of the IT risk scenarios.
Which of the following is the PRIMARY risk management responsibility of the third line of defense?
Providing assurance of the effectiveness of risk management activities
Providing guidance on the design of effective controls
Providing advisory services on enterprise risk management (ERM)
Providing benchmarking on other organizations ' risk management programs
Which of the following should be the PRIMARY concern when changes to firewall rules do not follow change management requirements?
Potential audit findings
Insufficient risk governance
Potential business impact
Inaccurate documentation
Unapproved changes to firewall rules can lead tocritical security vulnerabilitiesordisruptions to business services, representing adirect impact on the business. This is more critical than documentation or governance concerns.
An effective control environment is BEST indicated by controls that:
minimize senior management ' s risk tolerance.
manage risk within the organization ' s risk appetite.
reduce the thresholds of key risk indicators (KRIs).
are cost-effective to implement
According to the CRISC Review Manual (Digital Version), an effective control environment is best indicated by controls that manage risk within the organization’s risk appetite, as this reflects the alignment of thecontrol objectives and activities with the organization’s strategic goals and risk preferences. The risk appetite is the amount and type of risk that the organization is willing to accept in pursuit of its objectives. Managing risk within the organization’s risk appetite helps to:
Balance the potential benefits and costs of risk-taking and risk response
Optimize the use of the organization’s resources and capabilities
Enhance the value and performance of the organization
Foster a risk-aware culture that supports the organization’s vision and mission
References = CRISC Review Manual (Digital Version), Chapter 2: IT Risk Assessment, Section 2.3: IT Risk Assessment Process, pp. 93-941
An organization recently implemented an extensive risk awareness program after a cybersecurity incident. Which of the following is MOST likely to be affected by the implementation of the program?
Inherent risk
Risk appetite
Threat landscape
Residual risk
Residual risk is the level of risk remaining after controls and mitigation are applied. An effective awareness program reduces the likelihood of incidents (e.g., phishing, human error), thereby lowering residual risk. Inherent risk remains unchanged, as it is independent of controls.
Which of the following sources is MOST relevant to reference when updating security awareness training materials?
Risk management framework
Risk register
Global security standards
Recent security incidents reported by competitors
The most relevant source to reference when updating security awareness training materials is the recent security incidents reported by competitors. This can help to illustrate the real-world threats and consequences of poor security practices, and to motivate the employees to follow the security policies and procedures. Risk management framework, risk register, and global security standards are other sources that may be useful, but they are not as relevant as the recent security incidents. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 9; CRISC Review Manual, 6th Edition, page 214.
Which of the following is the BEST control for a large organization to implement to effectively mitigate risk related to fraudulent transactions?
Segregation of duties
Monetary approval limits
Clear roles and responsibilities
Password policies
Segregation of duties is a key control for preventing and detecting fraudulent transactions, especially in a large organization where there are many employees and transactions involved. Segregation of duties means that no single person has the authority or ability to initiate, approve, execute, and record a transaction without the involvement or oversight of another person. This reduces the opportunity and incentive for fraud, as well as the risk of errors or omissions. Segregation of duties also facilitates the detection of fraud by creating an audit trail and increasing the likelihood of whistleblowing.
The other options are not as effective as segregation of duties for mitigating risk related to fraudulent transactions. Monetary approval limits (B) are useful for controlling the amount and frequency of transactions, but they do not prevent unauthorized or fraudulent transactions from occurring. Clear roles and responsibilities © are important for defining the expectations and accountabilities of employees, but they do not ensure that employees comply with them or that their actions are monitored and verified. Password policies (D) are essential for securing access to systems and data, but they do not prevent fraudsters from exploiting weak or compromised passwords or from using legitimate passwords for fraudulent purposes.
A risk action plan has been changed during the risk mitigation effort. Which of the following is MOST important for the risk practitioner to verify?
Impact of the change on inherent risk
Approval for the change by the risk owner
Business rationale for the change
Risk to the mitigation effort due to the change
Risk owner approval ensures accountability and alignment of the changes with the enterprise’s risk management strategy. It reflects adherence to the principles ofRisk Ownership and Governance, critical for maintaining control over mitigation activities.
Which of the following can be affected by the cost of risk mitigation alternatives?
Risk appetite
Risk factors
Risk tolerance
Current risk rating
When the cost of mitigating a risk exceeds the benefit,organizations may adjust their risk toleranceto accept a higher level of risk. Thus, financial feasibility influences how much risk the organization is willing to accept.
A business manager wants to leverage an existing approved vendor solution from another area within the organization. Which of the following is the risk practitioner ' s BEST course of action?
Recommend allowing the new usage based on prior approval.
Request a new third-party review.
Request revalidation of the original use case.
Assess the risk associated with the new use case.
A risk practitioner’s best course of action when a business manager wants to leverage an existing approved vendor solution from another area within the organization is to assess the risk associated with the new use case. This is because the new use case may introduce different or additional risks that were not considered or addressed in the original approval. For example, the new use case may involve different data types, volumes, or sensitivities; different business processes, functions, or objectives; different regulatory or contractual requirements; or different technical or operational dependencies. Therefore, the risk practitioner should perform a vendor risk assessment (VRA) to identify, evaluate, and mitigate the potential risks of the new use case and ensure that the vendor solution meets the organization’s riskappetite and tolerance12. Recommending allowing the new usage based on prior approval is not the best course of action, as it may overlook or underestimate the risks of the new use case and expose the organization to unacceptable levels of risk. Requesting a new third-party review is not the best course of action,as it may be unnecessary or redundant if the vendor solution has already been reviewed and approved for another use case within the organization. Requesting revalidation of the original use case is not the best course of action, as it may not address the specific risks of the new use case and may also delay or disrupt the existing use case. References = Risk and Information SystemsControl Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.2: Risk Monitoring, pp. 189-191.
Which of the following is the MOST effective way to validate organizational awareness of cybersecurity risk?
Conducting security awareness training
Updating the information security policy
Implementing mock phishing exercises
Requiring two-factor authentication
Implementing mock phishing exercises is the most effective way to validate organizational awareness of cybersecurity risk, because it helps to measure and test the knowledge and behavior of the employees regarding the detection and prevention of phishing attacks, which are one of the most common and dangerous forms of cybersecurity risk. A phishing attack is a fraudulent attempt to obtain sensitive or confidential information, such as usernames, passwords, or credit card details, by impersonating a legitimate or trusted entity, such as a bank, a government agency, or a colleague, through email, phone, or other communication channels. A mock phishing exercise is a simulated phishing attack that is conducted by the organization or a thirdparty to assess the level of awareness and readiness of the employees to recognize and respond to phishing attacks, and to provide feedback and training to improve their skills andknowledge. Implementing mock phishing exercises is the most effective way, as it helps to validate the actual and practical awareness of cybersecurity risk, and to identify and address the gaps or weaknesses in the employees’ awareness and behavior. Conducting security awareness training, updating the information security policy, and requiring two-factor authentication are all useful ways to enhance organizational awareness of cybersecurity risk, but they are not the most effective way, as they do not directly validate the awareness and behavior of the employees regarding phishing attacks. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.2, page 158
Which of the following would be of MOST concern to a risk practitioner reviewing risk action plans for documented IT risk scenarios?
Individuals outside IT are managing action plans for the risk scenarios.
Target dates for completion are missing from some action plans.
Senior management approved multiple changes to several action plans.
Many action plans were discontinued after senior management accepted the risk.
The most concerning factor for a risk practitioner reviewing risk action plans for documented IT risk scenarios is that many action plans were discontinued after senior management accepted the risk. Risk action plans are documents that define the roles, responsibilities, procedures, and resources for implementing the risk responses and strategies for the IT risk scenarios. Risk action plans help to reduce, transfer, avoid, or accept the IT risks, and to monitor and report on the IT risk performance and improvement. Discontinuing risk action plans after senior management accepted the risk is a major concern, because it may indicate that the risk acceptance decision was not based on a proper risk analysisor evaluation, or that the risk acceptance decision was not communicated or coordinated with the relevant stakeholders, such as the board, management, business units, and IT functions. Discontinuing risk action plans after senior management accepted the risk may also create challenges or risks for the organization, such as compliance, legal, reputational, or operational risks, or conflicts or inconsistencies with the organization’s risk appetite, risk objectives, or risk policies. The other options are not as concerning as discontinuing risk action plans after senior management accepted the risk, although they may also pose some difficulties or limitations for the risk management process. Individuals outside IT managing action plans for the risk scenarios, target dates for completion missing from some action plans, and senior management approving multiple changes to several action plans are all factors that could affect the quality and timeliness of the risk management process, but they donot necessarily indicate a lack of risk management accountability or oversight. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.4.1, page 4-32.
In order to determining a risk is under-controlled the risk practitioner will need to
understand the risk tolerance
monitor and evaluate IT performance
identify risk management best practices
determine the sufficiency of the IT risk budget
To determine if a risk is under-controlled, the risk practitioner will need to understand the risk tolerance. Risk tolerance is the acceptable or allowable level of variation or deviation from the expected or desired outcomes or objectives. Risk tolerance reflects the amount and type of risk that the organization is willing and able to take. A risk is under-controlled when the risk exposure exceeds the risk tolerance, meaning that the organization is taking on more risk than it can handle or afford. Therefore, the risk practitioner will need to understand the risk tolerance to compare it with the risk exposure and identify the gap or difference. The other options are not as relevant as understanding the risk tolerance, as they are related to the monitoring, identification, or determination of the risk or the IT performance, not the comparison or evaluation of therisk. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.4: IT Risk Response, page 87.
A risk practitioner is involved in a comprehensive overhaul of the organizational risk management program. Which of the following should be reviewed FIRST to help identify relevant IT risk scenarios?
Technology threats
IT assets
Security vulnerabilities
IT risk register
IT assets are the resources that support the organization’s business processes and objectives, such as hardware, software, data, and information. IT assets are the primary targets of IT risk, as they may be exposed to threats, vulnerabilities, and control deficiencies that could compromise their confidentiality, integrity, availability, or value. Therefore, identifying and classifying IT assets is the first step in developing relevant IT risk scenarios, as it helps to determine the scope, boundaries, and dependencies of the IT risk environment.
The other options are not the first things to review for identifying IT risk scenarios. Technology threats (A) are the potential sources of harm or damage to IT assets, such as natural disasters, cyberattacks, human errors, or sabotage. Technology threats are important to consider, but they are not the starting point for IT risk scenarios, as they depend on the context and characteristics of the IT assets. Security vulnerabilities © are the weaknesses or flaws in IT assets or controls that could be exploited by threats, such as outdated software, misconfigured systems, or insufficient encryption. Security vulnerabilities are also important to identify, but they are not the first thing to review, as they are specific to the IT assets and their configurations. IT risk register (D) is a document that records and tracks the identified IT risks, their analysis, evaluation, and response. IT risk register is a result of the IT risk assessment process, not an input to it.
Which of the following is the PRIMARY consideration when determining the impact to an organization after the discovery of malware on an endpoint device?
Availability of patches and security updates.
Asset criticality and sensitivity.
Currency of the incident response plan.
Currency of anti-malware signatures.
The BEST answer is B because impact is determined by what the affected asset means to the organization. If the endpoint stores sensitive information, supports a critical business process, or has privileged access, the organizational impact is higher. The uploaded CRISC notes support this by stating that the criticality of business processes is a main outcome of business impact analysis, risk assessments identify risk with the highest business impact, and infrastructure criticality can be quantified based on dependencies.
ISACA’s risk assessment guidance states that asset criticality should be determined in terms of impact on business or system objectives, and that impact is the magnitude of harm from a risk scenario affecting confidentiality, integrity, or availability.
A and D relate to vulnerability remediation and preventive/detective control strength, not the primary impact determination. C affects response readiness, but the impact depends first on the criticality and sensitivity of the compromised endpoint and its data.
===========
Which of the following should be determined FIRST when a new security vulnerability is made public?
Whether the affected technology is used within the organization
Whether the affected technology is Internet-facing
What mitigating controls are currently in place
How pervasive the vulnerability is within the organization
When a new security vulnerability is made public, the first step is to determine whether the affected technology is used within the organization. This will help to assess the impact and exposure of the vulnerability on the organization’s assets, processes, and objectives. If the affected technology is not used within the organization, then the vulnerability does not pose a direct threat and no further action is required. However, if the affected technology is used within the organization, then the next steps are to identify the systems and components that are vulnerable, evaluate the severity and likelihood of the vulnerability being exploited, and implement appropriate mitigating controls or remediation actions. References = Risk and Information Systems Control Study Manual, Chapter 5, Section 5.3.2.1, p. 240-241
Which of the following is the GREATEST risk associated with the use of data analytics?
Distributed data sources
Manual data extraction
Incorrect data selection
Excessive data volume
According to the CRISC Review Manual1, data selection is the process of choosing the appropriate data sources and variables for data analysis. Data selection is the most critical step in data analytics, as it determines the quality and validity of the results and insights derived from the analysis. Incorrect data selection is the greatest risk associated with the use of data analytics, as it can lead to inaccurate, incomplete, irrelevant, or biased outcomes that can adversely affectthe decision making and performance of the organization. Incorrect data selection can also cause legal, regulatory, ethical, or reputational issues for the organization, if the data used for analysis is not authorized, reliable, or compliant. References = CRISC Review Manual1, page 255.
Which of the following is the MOST appropriate key performance indicator (KPI) to measure change management performance?
Percentage of changes implemented successfully
Percentage of rejected change requests
Number of after-hours emergency changes
Number of change control requests
Thepercentage of successfully implemented changesdirectly reflects the effectiveness and stability of the change management process. It measures whether changes achieve intended results without disruption.
To drive effective risk management, it is MOST important that an organization ' s policy framework is:
Approved by relevant stakeholders.
Aligned to the functional business structure.
Included in employee onboarding materials.
Mapped to an industry-standard framework.
Policies must reflect the actual structure and processes of the business to be enforceable and effective. Alignment ensures that policies are understood, applicable, and tailored to how the business operates.
The BEST metric to monitor the risk associated with changes deployed to production is the percentage of:
changes due to emergencies.
changes that cause incidents.
changes not requiring user acceptance testing.
personnel that have rights to make changes in production.
Changes deployed to production are those that affect the functionality, performance, or security of the system in a way that is visible or accessible to the end users1. These changes can introduce new risks or vulnerabilities, such as errors, bugs, compatibility issues, or unauthorized access2. Therefore, it is important to monitor the risk associated with these changes and measure how often they cause incidents in production.
One metric that can be used to monitor this risk is the percentage of changes that cause incidents in production. This metric indicates how effective the change management process is and how well the organization can prevent or mitigate potential problems caused by changes3. A high percentage of incidents indicates a high level of risk and a need for improvement in the change management process.
References = IT Change Management for SOC: Process and Best Practices, Determining and Managing Risk when Deploying Code, 6 Deployment Risks and How To Mitigate Them
The PRIMARY purpose of IT control status reporting is to:
ensure compliance with IT governance strategy.
assist internal audit in evaluating and initiating remediation efforts.
benchmark IT controls with Industry standards.
facilitate the comparison of the current and desired states.
IT control status reporting is the process of collecting and analyzing data about the effectiveness and efficiency of IT controls. IT controls are the policies, procedures, and practices that ensure the confidentiality, integrity, and availability of IT resources and information. IT control status reporting helps to monitor the performance of IT controls against the predefined objectives and criteria, and to identify any gaps or issues that need to be addressed. IT control status reporting also provides information to the stakeholders about the current status and progress of IT control implementation and improvement.
The primary purpose of IT control status reporting is to facilitate the comparison of the current and desired states of IT controls. This means that IT control status reporting helps to evaluate the gap between the actual and expected performance of IT controls, and to determine the actions and resources needed to close the gap. IT control status reporting also helps to align the IT controls with the business goals and strategies, and to ensure that the IT controls are delivering value to the organization. By comparing the current and desired states of IT controls, IT control status reporting enables continuous improvement and optimization of IT control processes and outcomes.
The other options are not the primary purpose of IT control status reporting, but rather some of the benefits or outcomes of it. IT control status reporting can help to ensure compliance with IT governance strategy,but it is not the main reason for doing it. IT governance is the framework that defines the roles, responsibilities, and relationships among the stakeholders involved in ITdecision making and oversight. IT control status reporting can support IT governance by providing relevant and reliable information to the stakeholders, and by demonstrating the accountability and transparency of IT control activities. However, IT control status reporting is not the same as IT governance, and it is not the only way to ensure compliance with IT governance strategy.
IT control status reporting can also assist internal audit in evaluating and initiating remediation efforts, but it is not the main objective of it. Internal audit is an independent and objective assurance and consulting activity that evaluates the adequacy and effectiveness of IT controls, and provides recommendations for improvement. IT control status reporting can provide input and evidence to the internal audit process, and help to identify the areas of IT control that need further review or testing. IT control status reporting can also help to monitor and track the implementation of the audit findings and recommendations, and to verify the results of the remediation efforts. However, IT control status reporting is not the same as internal audit, and it is not the only source of information for internal audit.
Finally, IT control status reporting can benchmark IT controls with industry standards, but it is not the main goal of it. Industry standards are the best practices or guidelines that define the minimum requirements or expectations for IT control performance and quality. IT control status reporting can help to compare the IT controls with the industry standards, and to identify the areas of IT control that need to be enhanced or updated. IT control status reporting can also help to demonstrate the compliance or conformance of IT controls with the industry standards, and to provide assurance to the external parties or regulators. However, IT control status reporting is not the same as industry standards, and it is not the only way to benchmark IT controls. References =
Service Reporting in ITIL: Process, Objectives and Examples - KnowledgeHut
Anatomy of an effective status report - Project Management Institute
How to Create a Project Status Report [Template & Examples]
Communicating Document Control Progress on a Project
[CRISC Review Manual, 7th Edition]
Which of the following is MOST important for effective communication of a risk profile to relevant stakeholders?
Emphasizing risk in the risk profile that is related to critical business activities
Customizing the presentation of the risk profile to the intended audience
Including details of risk with high deviation from the risk appetite
Providing information on the efficiency of controls for risk mitigation
Customizing the risk profile presentation ensures that stakeholders receive information in a format and context relevant to their roles. Tailored communication improves understanding, aligns risk discussions with decision-making needs, and ensures the stakeholders are equipped to act on the information effectively.
Which of the following is the MOST important responsibility of a business process owner to enable effective IT risk management?
Delivering risk reports in a timely manner
Escalating risk to senior management
Prioritizing risk for appropriate response
Collecting and analyzing risk data
Which of the following is MOST important to consider when determining key performance indicators (KPIs) for a process?
Historical trends in process-related incidents
Known problems with the process
Success criteria for the process
Alignment with established industry frameworks
For no apparent reason, the time required to complete daily processing for a legacy application is approaching a risk threshold. Which of the following activities should be performed FIRST?
Temporarily increase the risk threshold.
Suspend processing to investigate the problem.
Initiate a feasibility study for a new application.
Conduct a root-cause analysis.
The first activity that should be performed when the time required to complete daily processing for a legacy application is approaching a risk threshold is to conduct a root-cause analysis. This will help to identify the source of the problem and the factors that are contributing to the increased processing time. By conducting a root-cause analysis, the enterprise can determine the most appropriate and effective solution to address the problem and prevent it from recurring. Temporarily increasing the risk threshold, suspending processing to investigate the problem, and initiating a feasibility study for a new application are not the first activities that should be performed, as they may not resolve the underlying issue and may introduce additional risks or costs. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.2.1.2, page 193.
An organization ' s internal audit department is considering the implementation of robotics process automation (RPA) to automate certain continuous auditing tasks. Who would own the risk associated with ineffective design of the software bots?
Lead auditor
Project manager
Chief audit executive (CAE)
Chief information officer (CIO)
Robotics process automation (RPA) is the use of software robots to perform repetitive, rules-based tasks that interact with multiple applications. RPA can help internal audit departments automate certain continuous auditing tasks, such as data extraction, validation, analysis, and reporting. RPA can improve the efficiency, quality, and coverage of internal audit activities, and provide greater insight and value to the business. However, RPA also involves certain risks, such as errors, failures, security breaches, or compliance issues, that need to be identified, assessed, and managed. The risk associated with ineffective design of the software bots is the possibility and impact of the bots not functioning as intended, or producing inaccurate or unreliable results. The risk owner of this risk is the person or entity who has the authority and responsibility for managing the risk. The risk owner should be able to define the risk appetite, assess the risk level, select and implement the risk response, monitor and report the risk status, and ensure the risk alignment with the project objectives and strategy. The risk owner of the risk associated with ineffective design of the software bots is the project manager, who is the person in charge of planning, executing, monitoring, and closing the RPA project. The project manager understands the project scope, requirements, budget, timeline, and deliverables, and the potential consequences of ineffective design of the software bots. The project manager also has the resources and incentives to address the risk effectively and efficiently. Therefore, the project manager is the most appropriate risk owner of the risk associated with ineffective design of thesoftware bots. References = Robotic Process Automation for Internal Audit, p. 3-4, Adopting robotic process automation in Internal Audit, Robotic Process Automation (RPA) – Internal Audit Use and Risks.
To enable effective risk governance, it is MOST important for senior management to:
Ensure the IT governance framework is up to date.
Communicate the risk management strategy across the organization.
Gain a clear understanding of business risk and related ownership.
Ensure security policies and procedures are documented.
Which of the following is a responsibility of the second line of defense in the three lines of defense model?
Performing duties independently to provide assurance
Alerting operational management to emerging issues
Implementing corrective actions to address deficiencies
Owning risk scenarios and bearing the consequences of loss
The second line (risk management, compliance) provides oversight and support to the first line (operations). It monitors risk-related activities, issues alerts, and helps ensure controls are properly designed and implemented, but does not own the risk.
An organization has granted a vendor access to its data in order to analyze customer behavior. Which of the following would be the MOST effective control to mitigate the risk of customer data leakage?
Enforce criminal background checks.
Mask customer data fields.
Require vendor to sign a confidentiality agreement.
Restrict access to customer data on a " need to know ' ' basis.
According to the Hierarchy of Controls, the most effective way to prevent and control hazards is to eliminate them or substitute them with safer alternatives. In this case, the hazard is the potential leakage of customer data by the vendor. Therefore, the most effective control would be to eliminate or substitute the customer data with masked or anonymized data fields. This would prevent the vendor from accessing or disclosing any sensitive or identifiable information about the customers. Masking customer data fields is an example of an engineering control, which reduces or prevents hazards from coming into contact with workers or third parties. References = Hierarchy of Controls, 5 Risk Control Measures In The Workplace
Following an acquisition, the acquiring company ' s risk practitioner has been asked to update the organization ' s IT risk profile What is the MOST important information to review from the acquired company to facilitate this task?
Internal and external audit reports
Risk disclosures in financial statements
Risk assessment and risk register
Business objectives and strategies
The most important information to review from the acquired company to facilitate the task of updating the organization’s IT risk profile is the risk assessment and risk register. The risk assessment is a process of identifying, analyzing, and evaluating the IT risks of the acquiredcompany. The risk register is a document that records the details of the IT risks, such as their sources, causes, consequences, likelihood, impact, and responses. By reviewing the risk assessment and risk register, the risk practitioner can gain a comprehensive and accurate understanding of the IT risk profile of the acquired company, and integrate it with the IT risk profile of the acquiring organization. Internal and external audit reports, risk disclosures in financial statements, and business objectives and strategies are other possible sources of information, but they are not as important as the risk assessment and risk register. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 11; CRISC Review Manual, 6th Edition, page 144.
An organization is adopting block chain for a new financial system. Which of the following should be the GREATEST concern for a risk practitioner evaluating the system ' s production readiness?
Limited organizational knowledge of the underlying technology
Lack of commercial software support
Varying costs related to implementation and maintenance
Slow adoption of the technology across the financial industry
The greatest concern for a risk practitioner when an organization is adopting blockchain for a new financial system is the limited organizational knowledge of the underlying technology. Blockchain is a distributed ledger technology that enables secure and transparent transactions among multiple parties without the need for intermediaries or central authorities. Blockchain technology has many potential benefits for the financial sector, such as reducing costs, increasing efficiency, enhancing security, and improving trust. However, blockchain technology also poses many challenges and risks for the organization, such as technical complexity, interoperability issues, regulatory uncertainty, and cultural resistance. The limited organizational knowledge of the underlying technology is the greatest concern, because it affects the ability and readiness of the organization to adopt, implement, use, and maintain the blockchain system effectively and securely. The limited organizational knowledge could also result in poor decision-making, inadequate governance, insufficient training, and increased vulnerability to errors, fraud, or attacks. The other options are not as concerning as the limited organizational knowledge, although they may also pose some difficulties or limitations for the blockchain adoption. Lack of commercial software support, varying costs related to implementation and maintenance, and slow adoption of the technology across the financial industry are all factors that could affect the feasibility and sustainability of the blockchain system, but they do not directly affect the capability and maturity of the organization. References = 5
What are the MOST important criteria to consider when developing a data classification scheme to facilitate risk assessment and the prioritization of risk mitigation activities?
Mitigation and control value
Volume and scope of data generated daily
Business criticality and sensitivity
Recovery point objective (RPO) and recovery time objective (RTO)
Data classification is the process of organizing data in groups based on their attributes and characteristics, and then assigning class labels that describe a set of attributes that hold true for the corresponding data sets1. Data classification helps an organization understand the value of its data, determine whether the data is at risk, and implement controls to mitigate risks1. Data classification also helps an organization comply with relevant industry-specific regulatory mandates such as SOX, HIPAA, PCI DSS, and GDPR1.
The most important criteria to consider when developing a data classification scheme are the business criticality and sensitivity of the data2. Business criticality refers to the impact of data loss or compromise on the organization’s operations, reputation, and objectives2. Sensitivityrefers to the level of confidentiality, integrity, and availability required for the data2. Data that is highly critical and sensitive should be classified and protected accordingly, as it poses the highest risk to the organization if mishandled or breached2.
Some of the best practices for data classification are3:
Inventory your data: Identify all data assets within your organization.
Define data categories: Create a classification scheme that suits your organization’s needs.
Assign responsibility: Designate individuals or teams responsible for data classification.
Implement classification tools: Invest in tools and technologies that facilitate data classification.
Educate and train: Raise awareness and provide guidance on data classification policies and procedures.
Review and audit: Monitor and evaluate the effectiveness and compliance of data classification.
References = What is Data Classification? | Best Practices & Data Types | Imperva, What Is Data Classification? The 5 Step Process & Best Practices for Classifying Data | Splunk, Top 10 Best Practices for Securing Your Database - 2023
The FIRST task when developing a business continuity plan should be to:
determine data backup and recovery availability at an alternate site.
identify critical business functions and resources.
define roles and responsibilities for implementation.
identify recovery time objectives (RTOs) for critical business applications.
A business continuity plan (BCP) is a system of prevention and recovery from potential threats to a company. The plan ensures that personnel and assets are protected and are able to function quickly in the event of a disaster1. The first task when developing a BCP should be to identify critical business functions and resources, because this will help to determine the scope, objectives, and priorities of the plan. Critical business functions and resources are those that are essential for the continuity of the company’s operations, and that would cause significant disruption or damage if they were interrupted or lost. By identifying critical business functions and resources, the company can focus its efforts and resources on protecting and restoring them, and minimizing the impact of a disaster. The other options are not the first task when developing a BCP, because they depend on the identification of critical business functions and resources, as explained below:
A. Determine data backup and recovery availability at an alternate site is a task that relates to the recovery strategy of the BCP, which aims to restore the data and information systems that support the critical business functions and resources. However, this task cannot be performed without first identifying which data and information systems are critical, and what level of availability and recovery they require.
C. Define roles and responsibilities for implementation is a task that relates to the organization and governance of the BCP, which aims to assign and communicate the duties and expectations of the personnel involved in the plan. However, this task cannot be performed without first identifying which personnel are critical, and what functions and resources they are responsible for.
D. Identify recovery time objectives (RTOs) for critical business applications is a task that relates to the analysis and evaluation of the BCP, which aims to measure the acceptable downtime and recovery speed of the critical business functions and resources. However, this task cannot be performed without first identifying which business applications are critical, and what impact and likelihood they have. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 115. What Is a Business Continuity Plan (BCP), and How Does It Work?, Business continuity plan (BCP) in 8 steps, with templates | BDC.ca, How Develop a Business Continuity Plan - Invenio IT, Business Continuity Planning | Ready.gov, Develop a Robust Business Continuity Plan | Wrike
Which of the following BEST helps to identify significant events that could impact an organization?
Control analysis
Vulnerability analysis
Scenario analysis
Heat map analysis
Scenario analysis is the best method to identify significant events that could impact an organization. Scenario analysis is the process of creating and evaluating hypothetical situations or scenarios that represent plausible outcomes of various events or actions. Scenario analysis helps to anticipate and prepare for potential risks and opportunities, as well as to test the robustness and resilience of the organization’s strategies and plans. Control analysis, vulnerability analysis, and heat map analysis are not as effective as scenario analysis, because they focus on the existing or current state of the organization, rather than the future or alternative states. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 4-13.
While reviewing an organization ' s monthly change management metrics, a risk practitioner notes that the number of emergency changes has increased substantially Which of the following would be the BEST approach for the risk practitioner to take?
Temporarily suspend emergency changes.
Document the control deficiency in the risk register.
Conduct a root cause analysis.
Continue monitoring change management metrics.
According to the CRISC Review Manual, a root cause analysis is a technique that identifies the underlying causes of an event or a problem. It helps to determine the most effective actions to prevent or mitigate the recurrence of the event or problem. A root cause analysis is the best approach for the risk practitioner to take in this scenario, because it will help to understand why the number of emergency changes has increased substantially and what can be done to address the issue. The other options are not the best approaches, because they do not address the underlying causes of the problem. Temporarily suspending emergency changes may disrupt the business operations and create more risks. Documenting the control deficiency in the risk register is a passive action that does not resolve the problem. Continuing monitoring change management metrics is an ongoing activity that does not provide any insight into the problem. References = CRISC Review Manual, 7th Edition, Chapter 3, Section 3.2.4, page 130.
The MOST effective approach to prioritize risk scenarios is by:
assessing impact to the strategic plan.
aligning with industry best practices.
soliciting input from risk management experts.
evaluating the cost of risk response.
The most effective approach to prioritize risk scenarios is by assessing the impact to the strategic plan, because this will help to align the risk management process with the organization’s vision, mission, and goals. The strategic plan is the document that defines the organization’s direction, priorities, and objectives, and guides the allocation of resources and efforts. By assessing theimpact to the strategic plan, the organization can determine which risk scenarios pose the greatest threat or opportunity to the achievement of the strategic objectives, and prioritize them accordingly. The other options are not as effective as assessing the impact to the strategic plan, because they do not directly relate to the organization’s specific context, needs, and expectations, as explained below:
B. Aligning with industry best practices is an approach that involves following the standards, norms, and expectations for risk management that are established and followed by the peers or competitors in the same industry or sector. Aligning with industry best practices can help to benchmark and compare the organization’s risk management performance and maturity, and identify areas for improvement or innovation. However, this approach is not as effective as assessing the impact to the strategic plan, because it does not account for the organization’s unique and customized risk scenarios, which may differ from the industry average or standard.
C. Soliciting input from risk management experts is an approach that involves seeking advice, guidance, or feedback from the professionals or specialists who have the knowledge, experience, or skills in risk management. Soliciting input from risk management experts can help to enhance the quality and validity of the risk analysis and evaluation, and provide insights and recommendations for risk mitigation. However, this approach is not as effective as assessing the impact to the strategic plan, because it does not reflect the organization’s risk appetite, preferences, and expectations, which may differ from the risk management experts’ opinions or perspectives.
D. Evaluating the cost of risk response is an approach that involves estimating the resources and efforts required to implement the risk response strategies, such as avoiding, reducing, transferring, or accepting the risk. Evaluating the cost of risk response can help to optimize the risk management efficiency and effectiveness, and balance the potential benefits and costs of taking risks. However, this approach is not as effective as assessing the impact to the strategic plan, because it does not consider the potential consequences and outcomes of the risk scenarios, which may affect the organization’s performance and reputation. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.3.1, page 45. The Ultimate Guide to Risk Prioritization - Hyperproof, Risk Prioritization: What Is It? [2021 Guide & Matrix] - ERM Software, What is Risk Prioritization | Centraleyes, Scenario Planning in Risk Management: Why It is Needed - SmartCompliance
Which of the following is the BEST measure of the effectiveness of an employee deprovisioning process?
Number of days taken to remove access after staff separation dates
Number of days taken for IT to remove access after receipt of HR instructions
Number of termination requests processed per reporting period
Number of days taken for HR to provide instructions to IT after staff separation dates
The effectiveness of an employee deprovisioning process can be measured by the number of days taken to remove access after staff separation dates, as this indicates how quickly and completely the organisation can revoke the privileges of former employees and reduce the risk of unauthorized access or data leakage. The number of days taken for IT to remove access after receipt of HR instructions is a measure of the efficiency of the IT department, but not the overall process. The number of termination requests processed per reporting period is a measure of the volume of the process, but not the quality or timeliness. The number of days taken for HR to provide instructions to IT after staff separation dates is a measure of the performance of the HR department, but not the entire process. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk Response, page 152.
After entering a large number of low-risk scenarios into the risk register, it is MOST important for the risk practitioner to:
prepare a follow-up risk assessment.
recommend acceptance of the risk scenarios.
reconfirm risk tolerance levels.
analyze changes to aggregate risk.
After entering a large number of low-risk scenarios into the risk register, it is most important for the risk practitioner to analyze changes to aggregate risk. Aggregate risk is the total amount and type of risk that the organization faces or accepts, considering all the individual and interrelated risk scenarios. Aggregate risk helps to measure and monitor the organization’s risk profile, riskappetite, and risk performance, and to support the risk decision-making and reporting processes. Analyzing changes to aggregate risk is important after entering a large number of low-risk scenarios, because even though the individual risk scenarios may have low likelihood or impact, they may still have a significant cumulative or combined effect on the organization’s objectives or operations. Analyzing changes to aggregate risk also helps to identify and prioritize the most critical or relevant risk scenarios, and to select the most appropriate and effective risk responses and strategies. The other options are not as important as analyzing changes to aggregate risk, although they may be part of or derived from the risk analysis process. Preparing a follow-up risk assessment, recommending acceptance of the risk scenarios, and reconfirming risk tolerance levels are all activities that can help to implement or update the risk management process, but they are not the most important after entering a large number of low-risk scenarios. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-25.
A maturity model is MOST useful to an organization when it:
benchmarks against other organizations
defines a qualitative measure of risk
provides a reference for progress
provides risk metrics.
A maturity model is a framework that describes the stages or levels of development and improvement of a certain domain, such as a process, a function, or an organization. A maturity model is most useful to an organization when it provides a reference for progress, meaning that it helps the organization to assess its current state, identify its strengths and weaknesses, set its goals and objectives, and measure itsperformance and improvement over time. A maturity model can also help the organization to compare itself with best practices and standards, but benchmarking against other organizations is not its primary purpose. A maturity model can also help the organization to manage its risks, but defining a qualitative measure of risk or providingrisk metrics is not its main function. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.2.1, p. 118-119
Which of the following should be done FIRST upon learning that the organization will be affected by a new regulation in its industry?
Transfer the risk.
Perform a gap analysis.
Determine risk appetite for the new regulation.
Implement specific monitoring controls.
A gap analysis is the process of comparing the current state of the organization’s compliance with the new regulation and the desired state of compliance. It helps to identify the gaps or deficiencies that need to be addressed and prioritize the actions to close them. Performing a gap analysis is the first step to understand the impact of the new regulation and plan the appropriate risk response.
References
•ISACA CRISC Review Manual, 7th Edition, Domain 2: IT Risk Assessment, Section 2.2.3: Gap Analysis
•Regulatory Change: Future of Risk in the Digital Era | Deloitte US
•Gap Analysis: What It Is and How to Perform One | The Blueprint
Which of the following approaches BEST identifies information systems control deficiencies?
Countermeasures analysis
Best practice assessment
Gap analysis
Risk assessment
A gap analysis is the best approach to identify information systems control deficiencies, as it helps to compare and evaluate the current and desired states of the information systems and their controls, and to identify and prioritize the gaps or weaknesses that need to be addressed. A gap analysis is a process of assessing and measuring the difference between the actual and expected performance or outcomes of a system or a process, such as an information system or a control process. A gap analysis can help to identify information systems control deficiencies by providing the following benefits:
It enables a data-driven and evidence-based approach to information systems control assessment and improvement, rather than relying on subjective or qualitative judgments.
It facilitates a consistent and standardized way of measuring and communicating information systems control performance and quality across the organization and to the external stakeholders.
It supports the alignment of information systems and their controls with the organizational strategy and objectives, and helps to evaluate the achievement of the desired outcomes.
It helps to identify and prioritize the root causes and contributing factors of information systems control deficiencies, and to develop and implement appropriate strategies and actions to address them.
It provides feedback and learning opportunities for the information systems and their controls, and helps to foster a culture of continuous improvement and innovation.
The other options are not the best approaches to identify information systems control deficiencies. Countermeasures analysis is a method of identifying and evaluating the potential countermeasures or solutions to mitigate or eliminate a specific threat or risk, but it does not directly address the information systems control deficiencies. Best practice assessment is a method of comparing and benchmarking the information systems and their controls against the industry standards or best practices, but it does not provide a comprehensive or customized analysis of the information systems control deficiencies. Risk assessment is a method ofidentifying and analyzing the potential risks and their impacts on the information systems and their objectives, but it does not measure or evaluate the information systems control performance or quality. References = Gap Analysis: A Practical Guide | Smartsheet, IT Risk Resources | ISACA, How to Perform a Gap Analysis: Step-By-Step Guide & Template
Which of the following is the MOST important consideration when selecting key risk indicators (KRIs) to monitor risk trends over time?
Ongoing availability of data
Ability to aggregate data
Ability to predict trends
Availability of automated reporting systems
Ongoing availability of data is the most important consideration when selecting key risk indicators (KRIs) to monitor risk trends over time, as it ensures that the KRIs can provide timely and reliable information on the current and future risk status and performance. KRIs are metrics that measure the level of risk exposureand the effectiveness of risk response strategies, and they should be aligned with the enterprise’s risk appetite and objectives. Ongoing availability ofdatameans that the data sources and collection methods for the KRIs are consistent, accessible, and sustainable, and that the data quality and integrity are maintained and verified. Ability to aggregate data, ability to predict trends, and availability of automated reporting systems are not the most important considerations, as they do not affect the validity and usefulness of the KRIs, but rather the presentation and analysis of the KRI data. References = CRISC Certified in Risk and Information Systems Control – Question213; ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 213.
Which of the following is the PRIMARY concern related to using pseudonymization for the protection of an organization’s processed privacy data?
Authorized users can access personal data.
Updates to privacy data content are not allowed.
Individual data subjects can be re-identified.
Other information about the data subject can be revealed.
Pseudonymizationreplaces identifying fields in a data record with artificial identifiers or pseudonyms. However, unlike full anonymization,re-identification remains possibleif the pseudonym can be matched with external or hidden reference data.
CRISC and privacy-risk guidance (aligned with GDPR principles) emphasize that:
“The primary concern when using pseudonymization as a privacy safeguard is the potential for re-identification of individual data subjects.”
Pseudonymized data can still be linked back to individuals if the mapping key or auxiliary datasets are compromised.
True anonymization eliminates any reasonable means of re-identification, but pseudonymization does not.
Therefore, while pseudonymization reduces exposure, it doesnot fully eliminateprivacy risk.
Options A, B, and D are not inherent to pseudonymization:
Authorized access and update restrictions are policy issues, not intrinsic to pseudonymization.
Other information disclosure (D) could occur through inference but is secondary to direct re-identification.
Hence,C. Individual data subjects can be re-identifiedis the correct and verified answer as per CRISC and GDPR-aligned data protection practices.
Which of the following would MOST likely require a risk practitioner to update the risk register?
An alert being reported by the security operations center.
Development of a project schedule for implementing a risk response
Completion of a project for implementing a new control
Engagement of a third party to conduct a vulnerability scan
The completion of a project for implementing a new control would most likely require a risk practitioner to update the risk register. The risk register is a document that records the identified risks, their analysis, and their responses. The completion of a project for implementing a new control means that a risk response has been executed and a new control has been established. This may affect the likelihood and/or impact of the related risks, and the residual risk level. Therefore, the risk practitioner should update the risk register to reflect the current status and outcome of the risk response and the new control. The other options are not as likely to require a risk practitioner to update the risk register, as they are related to the reporting, planning, or assessment of the risks or the controls, not the implementation or completion of the risk response or the new control. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.4: IT Risk Response, page 87.
Which of the following BEST facilities the alignment of IT risk management with enterprise risk management (ERM)?
Adopting qualitative enterprise risk assessment methods
Linking IT risk scenarios to technology objectives
linking IT risk scenarios to enterprise strategy
Adopting quantitative enterprise risk assessment methods
The best way to facilitate the alignment of IT risk management with enterprise risk management (ERM) is to link IT risk scenarios to enterprise strategy, because this ensures that the IT risks are considered in the context of the enterprise’s mission, vision, and goals. Linking IT risk scenarios to enterprise strategy also helps to prioritize the IT risks based on their impact and relevance to the enterprise’s objectives, and to select the appropriate risk responses and resources. The other options are not the best ways to facilitate the alignment of IT risk management with ERM, because they do not address the integration or alignment of the IT and enterprise perspectives. Adopting qualitative or quantitative enterprise risk assessment methods, and linking IT risk scenarios to technology objectives are examples of techniques or tools that can be used to perform IT risk management or ERM, but they do not ensure the alignment or consistency of the two processes. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.2.3, p. 22.
A peer review of a risk assessment finds that a relevant threat community was not included. Mitigation of the risk will require substantial changes to a software application. Which of the following is the BEST course of action?
Ask the business to make a budget request to remediate the problem.
Build a business case to remediate the fix.
Research the types of attacks the threat can present.
Determine the impact of the missing threat.
Determining the impact of the missing threat is the best course of action for a peer review of a risk assessment, as it helps to assess the potential consequences and severity of the threat on the information system and the business objectives. Determining the impact of the missing threat is a process of estimating and quantifying the possible harm or loss that could result from the occurrence of the threat event, such as data breach, system failure, or service disruption. Determining the impact of the missing threat can help to:
Identify and prioritize the critical assets, processes, and functions that could be affected by the threat
Evaluate and measure the extent and magnitude of the damage or disruption caused by the threat
Analyze and compare the current and residual risk levels and control effectiveness
Develop and implement appropriate risk response and mitigation strategies and actions
Communicate and report the risk exposure and status to the relevant stakeholders
Determining the impact of the missing threat is an essential step to ensure the completeness and accuracy of the risk assessment and to improve the quality and reliability of the risk management and control processes.
The other options are not the best courses of action for a peer review of a risk assessment. Asking the business to make a budget request to remediate the problem is a possible action to allocate the resources and costs for the risk mitigation, but it does not address the root cause or the severity of the problem. Building a business case to remediate the fix is a possible action to justify and support the risk mitigation, but it does not provide a clear and comprehensive analysis of the problem. Researching the types of attacks the threat can present is a possible action to understand and anticipate the threat scenarios andtechniques, but it does not evaluate the actual or potential impact of the threat. References = Risk Assessment and Analysis Methods: Qualitative and Quantitative, IT Risk Resources | ISACA, Peer Review Assessment Framework
Which of the following is MOST important to consider when assessing the likelihood that a recently discovered software vulnerability will be exploited?
The skill level required of a threat actor
The amount of personally identifiable information (PH) disclosed
The ability to detect and trace the threat action
The amount of data that might be exposed by a threat action
When assessing the likelihood that a recently discovered software vulnerability will be exploited, the most important consideration is the skill level required of a threat actor. Here ' s an explanation:
Skill Level of Threat Actors:
The skill level required to exploit a vulnerability determines how accessible the exploit is to potential attackers.
If a vulnerability requires advanced technical skills to exploit, it is less likely to be targeted by less sophisticated attackers.
Conversely, if the exploit can be easily executed with minimal skills, it increases the likelihood of widespread exploitation.
Factors Influencing Likelihood of Exploitation:
Availability of Exploit Tools:If automated tools or scripts are available to exploit the vulnerability, even less skilled attackers can take advantage of it.
Publication of Exploit Details:If the vulnerability and its exploitation method are widely published, it becomes more accessible to a broader range of attackers.
Assessment of Likelihood:
Security teams assess the skill level required by analyzing whether the exploit is straightforward or complex.
They also consider the presence of exploit kits in the wild that could lower the barrier to entry for potential attackers.
Comparison with Other Factors:
Amount of PII Disclosed:While important, it relates more to the impact rather than the likelihood of exploitation.
Ability to Detect and Trace:This is crucial for response but does not directly influence the likelihood of exploitation.
Amount of Data Exposed:Similar to PII, this factor pertains to the impact rather than the likelihood of exploitation.
An organization recently implemented an automated interface for uploading payment files to its banking system to replace manual processing. Which of the following elements of the risk register is MOST appropriate for the risk practitioner to update to reflect the improved control?
Risk scenarios
Risk ownership
Risk impact
Risk likelihood
Updating the risk likelihood in the risk register is appropriate when an improved control, such as an automated interface, is implemented. This change affects the probability of the risk occurring, thus reflecting the enhanced control environment.
Which of the following is the MOST important objective of embedding risk management practices into the initiation phase of the project management life cycle?
To deliver projects on time and on budget
To assess inherent risk
To include project risk in the enterprise-wide IT risk profit.
To assess risk throughout the project
The most important objective of embedding risk management practices into the initiation phase of the project management life cycle is to assess inherent risk. Inherent risk is the risk that exists before any controls or mitigations are applied. By assessing inherent risk in the initiation phase, the project team can identify the potential sources, causes, and impacts of risk that may affect the project objectives, scope, and deliverables. Assessing inherent risk in the initiation phase also helps to prioritize the risks, determine the risk appetite and tolerance, and plan the risk responses. Delivering projects on time and on budget, including project risk in the enterprise-wide IT risk profile, and assessing risk throughout the project are important objectives of risk management,but they are not the most important objective of embedding risk management practices into the initiation phase. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.1.1, page 511
1: ISACA Certified in Risk and Information Systems Control (CRISC®) Exam Guide, Answer to Question 658.
Which of the following is the GREATEST concern associated with insufficient focus on addressing blockchain interoperability in the SDLC?
Limited blockchain adoption and support
Reduced transaction speed and system responsiveness
Reduced network integrity and availability
Limited integration with external systems and blockchains
Limited integration with external systems and blockchainsis the greatest concern. Without considering interoperability during the SDLC, the system may not be able to connect seamlessly with partners or external networks, hindering business goals and limiting the blockchain’s benefits.
===========
Which of the following is the BEST indicator of the effectiveness of IT risk management processes?
Percentage of business users completing risk training
Percentage of high-risk scenarios for which risk action plans have been developed
Number of key risk indicators (KRIs) defined
Time between when IT risk scenarios are identified and the enterprise ' s response
IT risk management is the process of identifying, assessing, and mitigating the risks related to the use of information technology (IT) in the organization. IT risk management aims to ensure the confidentiality, integrity, and availability of IT resources and information, and to support the IT governance and strategy of the organization1.
The best indicator of the effectiveness of IT risk management processes is the time between when IT risk scenarios are identified and the enterprise’s response. This indicator can help to measure how quickly and efficiently the organization can detect and respond to the IT risks, and how well the organization can prevent or minimize the negative impacts of the IT risks. The time between when IT risk scenarios are identified and the enterprise’s response can include:
The time taken to identify and report the IT risk scenarios, using various methods and sources, such as risk assessments, audits, monitoring, alerts, or incidents
The time taken to analyze and evaluate the IT risk scenarios, using various tools and techniques, such as risk matrices, risk registers, risk indicators, or risk models
The time taken to select and implement the IT risk responses, using various strategies and controls, such as avoidance, mitigation, transfer, or acceptance
The time taken to review and improve the IT risk management processes, using various feedback and learning mechanisms, such as lessons learned, best practices, or benchmarks23
The other options are not the best indicators of the effectiveness of IT risk management processes, but rather some of the inputs or outputs of IT risk management processes. Percentage of business users completing risk training is an indicator of the awareness and competence of the IT users and providers, which can affect the IT risk management performance, but it does not measure the IT risk management processes directly. Percentage of high-risk scenarios for which risk action plans have been developed is an indicator of the completeness and coverage of the IT risk management activities, which can affect the IT risk management outcomes, but it does not measure the IT risk management processes directly. Number of key risk indicators (KRIs) defined is an indicator of the scope and complexity of the IT risk management objectives, whichcan affect the IT risk management resources and capabilities, but it does not measure the IT risk management processes directly. References =
IT Risk Management - ISACA
Risk Management Process - ISACA
Risk Response - ISACA
[CRISC Review Manual, 7th Edition]
The cost of maintaining a control has grown to exceed the potential loss. Which of the following BEST describes this situation?
Insufficient risk tolerance
Optimized control management
Effective risk management
Over-controlled environment
The situation where the cost of maintaining a control has grown to exceed the potential loss is best described as an over-controlled environment, as it indicates that the control is not cost-effective and may be unnecessary or excessive. Insufficient risk tolerance, optimized control management, and effective risk management are not the best descriptions, as they do not reflect the imbalance between the control cost and the potential loss. References = CRISC Review Manual, 7th Edition, page 149.
When of the following is the MOST significant exposure when an application uses individual user accounts to access the underlying database?
Users may share accounts with business system analyst
Application may not capture a complete audit trail.
Users may be able to circumvent application controls.
Multiple connects to the database are used and slow the process
The risk of users circumventing application controls is the most significant exposure when an application uses individual user accounts to access the underlying database. This is because users may have direct access to the data and bypass the validation, authorization, and logging mechanisms that are implemented at the application level. Users may also be able to modify or delete data without proper authorization or audit trail. The other options are less significant exposures, as they do not directly affect the integrity or confidentiality of the data. References = Risk IT Framework, ISACA, 2009, page 35; CRISC Review Manual, 6th Edition, ISACA, 2015, page 214.
Which of the following scenarios represents a threat?
Connecting a laptop to a free, open, wireless access point (hotspot)
Visitors not signing in as per policy
Storing corporate data in unencrypted form on a laptop
A virus transmitted on a USB thumb drive
A virus transmitted on a USB thumb drive is a scenario that represents a threat, as it involves a malicious or harmful event that could compromise the confidentiality, integrity, or availability of an information system. A virus is a type of malware that can infect and damage files, programs, or devices by replicating itself and spreading to other systems or networks. A USB thumb drive is a portable storage device that can be used to transfer data between computers or devices. Avirus transmitted on a USB thumb drive can occur when a user inserts an infected USB thumb drive into a computer or device, or when a user downloads or copies an infected file from a USB thumb drive to a computer or device. A virus transmitted on a USB thumb drive can pose a serious risk to the information system, as it can corrupt or delete data, disrupt or degrade performance, steal or leak information, or allow unauthorized access or control.
The other options are not scenarios that represent a threat, but rather vulnerabilities or weaknesses that could increase the likelihood or impact of a threat. Connecting a laptop to a free, open, wireless access point (hotspot) is a vulnerability, as it exposes the laptop to potential eavesdropping, interception, or manipulation by malicious actors on the same network. Visitorsnot signing in as per policy is a vulnerability, as it creates a gap in the physical security and access control of the premises, and could allow unauthorized or malicious visitors to enter or access sensitive areas or assets. Storing corporate data in unencrypted form on a laptop is a vulnerability, as it reduces the protection and security of the data, and could enable unauthorized or malicious access, disclosure, or modification of the data in case of loss, theft, or compromise of the laptop. References = What is a Computer Virus? | McAfee, What is a USB Flash Drive? | Kingston Technology, Threats, Vulnerabilities, and Exploits – oh my!
What is the BEST course of action when the business impact of a risk event is rated high, but the likelihood of risk materialization has decreased?
Adjust risk tolerance thresholds.
Adjust the associated key risk indicator (KRI).
Further mitigate the risk.
Accept the risk if within tolerance.
The correct answer isDbecause even though thebusiness impact remains high, thelikelihood has decreased, so the overall risk may now fall within acceptable tolerance. In CRISC, the appropriate course of action is to compare the resulting risk level against appetite and tolerance. If the residual exposure is now acceptable, the organization may accept the risk.
The other options are less appropriate:
A. Adjust risk tolerance thresholdsshould not be done simply because one risk has changed.
B. Adjust the associated key risk indicator (KRI)may be considered later if monitoring needs refinement, but it is not the primary action.
C. Further mitigate the riskmay be unnecessary if the risk is already within tolerance.
Exact Extracts supporting the answer:
“It is most important to reduce risk to a level that the enterprise is willing to accept when defining risk management strategies.”
“Residual risk is best reflected as risk remaining after the implementation of new or enhanced controls.”
“Acceptable risk for an enterprise is achieved when residual risk is within tolerance levels.”
“The risk treatment plan should be developed when risk levels exceed risk appetite or tolerance.”
These extracts support that the decision should be based on whether the remaining risk is within tolerance. If it is, the best course is toaccept the risk.
Which of the following is the MOST effective way to help ensure future risk levels do not exceed the organization ' s risk appetite?
Establishing a series of key risk indicators (KRIs).
Adding risk triggers to entries in the risk register.
Implementing key performance indicators (KPIs).
Developing contingency plans for key processes.
KRIs provide predictive metrics to monitor changes in risk levels, enabling timely interventions to maintain risks within the organization ' s appetite. This aligns with theRisk Monitoring and Reportingframework, which emphasizes proactive identification of risk thresholds.
Which of The following is the MOST comprehensive input to the risk assessment process specific to the effects of system downtime?
Business continuity plan (BCP) testing results
Recovery lime objective (RTO)
Business impact analysis (BIA)
results Recovery point objective (RPO)
The most comprehensive input to the risk assessment process specific to the effects of system downtime is the business impact analysis (BIA). The BIA is a process of analyzing the potential impacts of disruptive events on the business processes, functions, and resources. The BIA identifies the criticality, dependencies, recovery priorities, and recovery objectives of the business processes, and quantifies the financial and non-financial impacts of system downtime. The BIA provides valuable information for the risk assessment process, as it helps to evaluate the likelihood and impact of the risks, and to determine the appropriate risk responses. Business continuity plan (BCP) testing results, recovery time objective (RTO), and recovery point objective (RPO) are not as comprehensive as the BIA, as they are derived from the BIA and focus on specific aspects of the business continuity and recovery strategies. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 130.
Risk mitigation is MOST effective when which of the following is optimized?
Operational risk
Residual risk
Inherent risk
Regulatory risk
Risk mitigation is most effective when the residual risk is optimized, as it means that the risk exposure and impact have been reduced to the level that is aligned with the risk tolerance and appetite of the organization, and that the risk response is cost-effective and optimal. The other options are not the factors that determine the effectiveness of risk mitigation, as they are more related to the types or sources of risk, respectively, rather than the level or outcome of risk. References = CRISC Review Manual, 7th Edition, page 111.
In which of the following scenarios would a risk practitioner be required to provide the MOST justification for a risk assessment?
Modeling a threat-based risk event
Calculating mean time between failures (MTBF)
Using a semi-quantitative approach
Calculating adjusted loss expectancy (ALE)
Threat-based risk event modeling often involves significant expert judgment: choosing plausible threats, estimating their capability, attack paths, and motivations, and modeling multi-step attack scenarios. According to CRISC, such modeling demands strong justification and documented rationale because assumptions and inputs may be challenged by stakeholders and auditors. Semi-quantitative approaches and ALE calculations also require explanation, but they are generally based on standardized scales, historical data, or accepted formulas. MTBF is an engineering reliability metric, usually based on vendor data or operational history, requiring limited justification from a risk perspective. Threat-based modeling, however, drives critical decisions about controls and investment, and because it can be sensitive to subjective inputs, risk practitioners must carefully justify scenario selection, likelihood estimates, and impact assumptions to maintain credibility and enable informed governance decisions.
An organization is conducting a review of emerging risk. Which of the following is the BEST input for this exercise?
Audit reports
Industry benchmarks
Financial forecasts
Annual threat reports
The best input for conducting a review of emerging risk is the annual threat reports. Emerging risk is the risk that arises from new or evolving sources, or from existing sources that have not been previously considered or recognized. Emerging risk may have significant impact on the organization’s objectives, strategies, operations, or reputation, and may require new or different risk responses. Annual threat reports are the reports that provide information and analysis on the current and future trends, developments, and challenges in the threat landscape, such as cyberattacks, natural disasters, geopolitical conflicts, or pandemics. Annual threat reports can help to identify and assess the emerging risk, as they can provide insights into the sources, drivers, indicators, and scenarios of the emerging risk, as well as the potential impact and likelihood of the emerging risk. Annual threat reports can also help to benchmark and compare the organization’s risk exposure and preparedness with the industry and the peers, and to prioritize and respond to the emerging risk. Audit reports, industry benchmarks, and financial forecasts are not as useful as annual threat reports, as they do not focus on the emerging risk, and may not capture the latest or future changes in the threat landscape. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 50.
Changes in which of the following are MOST likely to trigger the need to reassess inherent risk?
Risk tolerance
Regulatory requirements
Key risk indicators (KRIs)
Industry benchmarks
Inherent risk reflects exposure before controls. Whenregulatory requirementschange, they can alter compliance obligations, legal exposure, and the baseline inherent risk of processes.
ISACA’s CRISC framework specifies:
“Significant changes to regulatory or legal environments are triggers for reassessing inherent and residual risk.”
A(risk tolerance) affects acceptance, not inherent risk itself.
C(KRIs) andD(benchmarks) measure and compare risk but do not trigger reassessment directly.
Hence,Bis correct.
CRISC Reference:Domain 2 – IT Risk Assessment, Topic: Risk Triggers and Environmental Changes.
Which of the following roles is PRIMARILY accountable for risk associated with business information protection?
Control owner
Data owner
System owner
Application owner
The data owner is responsible for ensuring that information is appropriately classified and protected. They are accountable for defining access controls and ensuring compliance with data protection policies, making them primarily accountable for risks associated with business information protection.
An organization uses one centralized single sign-on (SSO) control to cover many applications. Which of the following is the BEST course of action when a new application is added to the environment after testing of the SSO control has been completed?
Initiate a retest of the full control
Retest the control using the new application as the only sample.
Review the corresponding change control documentation
Re-evaluate the control during (he next assessment
The best course of action when a new application is added to the environment after testing of the SSO control has been completed is to initiate a retest of the full control, as it may reveal any new issues or gaps that the new application may introduce to the SSO control, and ensure that the control remains effective and adequate. Retesting the control using the new application as the only sample, reviewing the corresponding change control documentation, and re-evaluating the control during the next assessment are not the best courses of action, as they may not provide sufficient assurance, evidence, or timeliness of the control testing, respectively. References = CRISC Review Manual, 7th Edition, page 154.
Which of the following would be MOST useful to management when allocating resources to mitigate risk to the organization?
Risk assessments
Control self-assessments (CSAs)
Risk-based audits
Vulnerability analysis
Risk assessmentsprovide a prioritized view of potential threats, their likelihood, and impact. This enables management tofocus resourceson high-priority risks, ensuring cost-effective mitigation aligned with organizational goals.
Which of the following BEST enables the integration of IT risk management across an organization?
Enterprise risk management (ERM) framework
Enterprise-wide risk awareness training
Robust risk reporting practices
Risk management policies
Understanding the Question:
The question asks what best enables the integration of IT risk management across an organization.
Analyzing the Options:
A. Enterprise risk management (ERM) framework:Provides a comprehensive approach to integrating risk management across the entire organization.
B. Enterprise-wide risk awareness training:Important for education but doesn ' t ensure integration.
C. Robust risk reporting practices:Crucial for communication but not integration.
D. Risk management policies:Necessary but need to be part of an overall framework for effective integration.
ERM Framework:An ERM framework ensures that risk management practices are standardized and integrated throughout the organization. It aligns risk management with business objectives, ensuring that IT risk is considered within the broader context of enterprise risk.
Comprehensive Approach:ERM covers all aspects of risk, including IT, and facilitates a unified approach to managing risk across all departments and levels.
Risk acceptance of an exception to a security control would MOST likely be justified when:
automation cannot be applied to the control
business benefits exceed the loss exposure.
the end-user license agreement has expired.
the control is difficult to enforce in practice.
The most likely justification for risk acceptance of an exception to a security control is when the business benefits exceed the loss exposure. Risk acceptance is a risk response strategy that involves acknowledging and tolerating the risk, without taking any action to reduce or transfer the risk. An exception to a security control is a deviation or non-compliance from the established security policy or standard, due to a valid business reason or circumstance. Risk acceptance of an exception to a security control may be justified when the business benefits exceed the loss exposure, which means that the value or advantage of the exception outweighs the potential cost or harm of the risk. For example, an exception to a security control may enable faster or easier access to the system or data, which may improve the productivity, efficiency, or satisfaction of the users or customers, and generate more revenue or profit for the business. The business benefits of the exception may exceed the loss exposure of the risk, which may be low or negligible, or may be mitigated by other controls or factors. Therefore, risk acceptance of an exception to a security control may be a reasonable and rational decision, based on the cost-benefit analysis of the exception and the risk. Automation cannot be applied to the control, the end-user license agreement has expired, and the control is difficult to enforce in practice are not the most likely justifications for risk acceptance of an exception to a security control, as they are either irrelevant or insufficient reasons, and they do not consider the business benefits or the loss exposure of the exception and the risk. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 50.
Which of the following is the BEST way for an organization to enable risk treatment decisions?
Allocate sufficient funds for risk remediation.
Promote risk and security awareness.
Establish clear accountability for risk.
Develop comprehensive policies and standards.
Establishing clear accountability for risk is the best way for an organization to enable risk treatment decisions, as it ensures that the risk owners and stakeholders have the authority and responsibility to manage and mitigate the risks that they are assigned to. Establishing clear accountability for risk also facilitates communication and collaboration among the risk owners and stakeholders, and enables them to monitor and report the risk status and performance. Establishing clear accountability for risk also supports the risk governance and culture of the organization, and aligns the risk management process with the organization’s strategy and objectives. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question 250. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 250. CRISC Sample Questions 2024, Question 250. CRISC by Isaca Actual Free Exam Q & As, Question 9.
It is MOST important for a risk practitioner to have an awareness of an organization s processes in order to:
perform a business impact analysis.
identify potential sources of risk.
establish risk guidelines.
understand control design.
It is most important for a risk practitioner to have an awareness of an organization’s processes in order to identify potential sources of risk, as this enables the risk practitioner to understand the objectives, activities, resources, dependencies, and outputs of the processes, and how they may be affected by internal or external factors that create uncertainty or variability. Identifying potential sources of risk is the first step in the risk identification process, which aims to find, recognize, and describe the risks that could affect the achievement of the organization’s goals. The other options are not the most important reasons for a risk practitioner to have an awareness of an organization’s processes, although they may be related or beneficial aspects of it. Performing a business impact analysis is a part of the risk analysis process, which aims to understand the nature and extent of the risks and their consequences on the organization’s objectives and functions. Establishing risk guidelines is a part of the risk governance process, which aims to define and communicate the risk management principles, policies, and roles across the organization. Understanding control design is a part of the risk response process, which aims to select and implement the appropriate actions to modify the risk level or achieve the risk objectives. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Identification, page 47.
Which of the following is the BEST indication of an enhanced risk-aware culture?
Users have read and agreed to comply with security policies.
Risk issues are openly discussed within the organization.
Scores have improved on risk awareness quizzes.
There is a decrease in the number of reported incidents.
A strong risk-aware culture is reflected by transparent communication about risks. Open discussions signify employee engagement and ownership of risk-related issues.
Which of the following BEST supports the integration of IT risk management into an organization ' s strategic planning?
Clearly defined organizational goals and objectives
Incentive plans that reward employees based on IT risk metrics
Regular organization-wide risk awareness training
A comprehensive and documented IT risk management plan
A comprehensive and documented IT risk management plan provides a structured approach to identifying, assessing, and mitigating IT risks. Integrating this plan into the organization ' s strategic planning ensures that IT risk considerations are aligned with business objectives and are factored into decision-making processes at the strategic level.
Which of the following activities is PRIMARILY the responsibility of senior management?
Bottom-up identification of emerging risks
Categorization of risk scenarios against a standard taxonomy
Prioritization of risk scenarios based on severity
Review of external loss data
The primary responsibility of senior management in risk management is to prioritize the risk scenarios based on severity. Risk scenarios are hypothetical events or situations that could affect the achievement of the objectives. Risk severity is a measure of the overall level of risk, based on the combination of the probability and impact of the risk scenario. Prioritizing the risk scenarios based on severity is the primary responsibility of senior management, because it helps to allocate the resources and actions to the most critical and urgent risks, and to align the risk management process with the organizational strategy and risk appetite. Senior management also has the authority and accountability to make the final decisions and approve the risk response plans for the prioritized risks. The other options are not the primary responsibility of senior management, although they may be involved or consulted in these activities. Bottom-up identification of emerging risks is a process of identifying and reporting the new or changing risks that may arise from the operational or tactical level of the organization. This is usually the responsibility of the risk owners or the risk practitioners, who have the knowledge and experience of the specific functions and processes. Categorization of risk scenarios against a standard taxonomy is a process of classifying and organizing the risk scenarios into predefined categories or groups, based on their nature, source, or impact. This is usually the responsibility of the risk analysts or the risk coordinators, who have the skills and tools to perform the risk analysis and assessment. Review of external loss data is a process of collecting and analyzing the data and information on the losses or incidents that occurred in other organizations or industries, due to similar or related risks. This is usually the responsibility of the risk researchers or the risk consultants, who have the access and expertise to obtain and interpret the external data and information. References = The Role of Executive Management in ERM - Corporate Compliance Insights, Guidelines on Risk Management Practices – Board and Senior Management, Risk Manager Job Description [+2023 TEMPLATE] - Workable
An IT risk practitioner is evaluating an organization ' s change management controls over the last six months. The GREATEST concern would be an increase in:
rolled back changes below management ' s thresholds.
change-related exceptions per month.
the average implementation time for changes.
number of user stories approved for implementation.
= Change management is the process of planning, implementing, and monitoring changes to IT systems, services, or infrastructure in a controlled and coordinated manner1. Change management controls are the policies, procedures, and tools that ensure changes are authorized, documented, tested, and reviewed before they are deployed to the production environment2.
Change-related exceptions are the deviations or violations from the established change management controls, such as unauthorized, untested, or failed changes3. Change-related exceptions pose a high risk to theorganization, as they can cause system instability, performance degradation, security breaches, data loss, or compliance issues3.
An increase in change-related exceptions per month would be the greatest concern for an IT risk practitioner, as it indicates a lack of effectiveness, efficiency, or compliance of the change management process and controls. An increase in change-related exceptions per month could result from:
Poor change planning, prioritization, or scheduling
Insufficient change approval, review, or communication
Inadequate change testing, validation, or verification
Lack of change monitoring, reporting, or auditing
Low change awareness, training, or support
An IT risk practitioner should investigate the root causes of the increase in change-related exceptions per month, and recommend corrective and preventive actions to improve the change management process and controls, such as:
Aligning the change management process with the organization’s goals, strategies, and risk appetite
Implementing a standardized and consistent change management methodology, such as ITIL or COBIT
Defining clear roles and responsibilities for change management stakeholders, such as change owners, change managers, change advisory boards, change implementers, and change users
Establishing clear and measurable criteria and thresholds for change authorization, classification, and evaluation
Leveraging tools and technologies to automate and streamline the change management process and controls, such as change management software, configuration management databases, or change management dashboards
Enhancing the change management culture and capabilities, such as change management awareness, training, support, or feedback
The other options are not as concerning as an increase in change-related exceptions per month, because they do not directly imply a risk to the organization’s IT systems, services, or infrastructure. Rolled backchanges below management’s thresholds, which are the changes that are reversed or undone due to errors, defects, or issues, may indicate a need for improvement in the change testing, validation, or verification processes, but they do not necessarily cause harm or damage to the production environment, as long as they are within the acceptable limits set bythe management. The average implementation time for changes, which is the duration of the change deployment process, may affect the organization’s agility, efficiency, or productivity, but it does not necessarily compromise the quality, security, or reliability of the changes, as long as they are implemented according to the change management controls. The number of user stories approved for implementation, which are the requirements or features that are expressed from the perspective of the end users, may reflect the organization’s demand, innovation, or customer satisfaction, but it does not necessarily increase the risk of the changes, as long as they are managed and controlled by the change management process.
References = What is Change Management? | ITIL | AXELOS, Change Management Controls: Definition, Types, and Best Practices, Change Management Exceptions: Definition, Causes, and Impacts, ITIL Change Management: Best Practices & Processes - BMC Software, COBIT 2019: Change Enablement
Who is responsible for IT security controls that are outsourced to an external service provider?
Organization ' s information security manager
Organization ' s risk function
Service provider ' s IT management
Service provider ' s information security manager
The organization’s information security manager is responsible for IT security controls that are outsourced to an external service provider. The information security manager is accountable for ensuring that the security policies and standards of the organization are followed by the service provider, and that the security objectives and requirements are met. The information security manager is also responsible for monitoring and evaluating the security performance and compliance of the service provider, and for managing the security risks and incidents that may arise from the outsourcing arrangement. The organization’s risk function, the service provider’s IT management, and the service provider’s information security manager are not responsible for IT security controls that are outsourced, as they have different roles and responsibilities in the outsourcing process. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 5, Section 5.2.1.2, page 2461
1: ISACA Certified in Risk and Information Systems Control (CRISC®) Exam Guide, Answer to Question 651.
Which of the following is the PRIMARY objective of aggregating the impact of IT risk scenarios and reflecting the results in the enterprise risk register?
To ensure IT risk appetite is communicated across the organization
To ensure IT risk impact can be compared to the IT risk appetite
To ensure IT risk ownership is assigned at the appropriate organizational level
To ensure IT risk scenarios are consistently assessed within the organization
The primary objective of aggregating the impact of IT risk scenarios and reflecting the results in the enterprise risk register is to ensure IT risk impact can be compared to the IT risk appetite, as it enables the organization to measure and evaluate the overall level and exposure of the IT risk, and to align and prioritize the IT risk response and strategy with the organizational objectives and regulations. The other options are not the primary objectives, as they are more related to the communication, assignment, or assessment of the IT risk scenarios, respectively, rather than the aggregation or reflection of the IT risk scenarios. References = CRISC Review Manual, 7th Edition, page 109.
An organization has operations in a location that regularly experiences severe weather events. Which of the following would BEST help to mitigate the risk to operations?
Prepare a cost-benefit analysis to evaluate relocation.
Prepare a disaster recovery plan (DRP).
Conduct a business impact analysis (BIA) for an alternate location.
Develop a business continuity plan (BCP).
The best way to mitigate the risk to operations caused by severe weather events is to develop a business continuity plan (BCP). A BCP is a document that describes the procedures and resources needed to ensure the continuity of the organization’s critical functions and processes in the event of a disruption or disaster. A BCP helps to identify the recovery objectives, strategies, and priorities, as well as the roles and responsibilities of the recovery team members. A BCP also helps to prepare and test the recovery capabilities and resources, such as alternate locations, backup systems, and communication channels. The other options are not as effective as developing a BCP, although they may be part of the BCP process or outcomes. Preparing a cost-benefit analysis to evaluate relocation, preparing a disaster recovery plan (DRP), and conducting a business impact analysis (BIA) for an alternate location are all activities that can help to develop or implement a BCP, but they are not the best way to mitigate the risk to operations. References = Risk and Information Systems Control Study Manual, Chapter 5, Section 5.2.1, page 5-9.
Deviation from a mitigation action plan ' s completion date should be determined by which of the following?
Change management as determined by a change control board
Benchmarking analysis with similar completed projects
Project governance criteria as determined by the project office
The risk owner as determined by risk management processes
Deviation from a mitigation action plan’s completion date should be determined by the risk owner as determined by risk management processes, because the risk owner is the person or entity who has the accountability and authority to manage the risk and its associated mitigation actions. The risk owner should monitor and report the progress and status of the mitigation action plan, and determine if there is any deviation from the expected completion date, based on the risk management processes and criteria. The other options are not the ones who should determine the deviation, because:
Option A: Change management as determined by a change control board is a process that ensures that any changes to the project scope, schedule, cost, or quality are controlled and approved, but it does not determine the deviation from the mitigation action plan’s completion date, which is a risk management activity.
Option B: Benchmarking analysis with similar completed projects is a technique that compares the performance and practices of the current project with those of similar or successful projects, but it does not determine the deviation from the mitigation action plan’s completion date, which is a risk management activity.
Option C: Project governance criteria as determined by the project office is a set of rules and standards that define the roles, responsibilities, and authority of the project stakeholders, but it does notdetermine the deviation from the mitigation action plan’s completion date, which is a risk management activity. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 122.
An organization ' s business gap analysis reveals the need for a robust IT risk strategy. Which of the following should be the risk practitioner ' s PRIMARY consideration when participating in development of the new strategy?
Scale of technology
Risk indicators
Risk culture
Proposed risk budget
The risk practitioner’s primary consideration when participating in development of a new IT risk strategy should be the risk culture of the organization. Risk culture is the set of values, beliefs, attitudes, and behaviors that shape how the organization perceives, manages, and responds to risks. Risk culture influences the organization’s risk appetite, risk objectives, risk policies, risk processes, and risk performance. The risk practitioner should consider the risk culture whendeveloping a new IT risk strategy, because it helps to align the IT risk strategy with the organization’s mission, vision, values, and strategy, and to ensure that the IT risk strategy is supported and accepted by the organization’s stakeholders, such as the board, management, employees, customers, regulators, etc. The risk practitioner should also consider the risk culture when developing a new IT risk strategy, because it helps to identify and addressany gaps, issues, or challenges that may affect the implementation and effectiveness of the IT risk strategy, such as lack of awareness, communication, coordination, or accountability. The other options are not the primary consideration for the risk practitioner, although they may be related to the IT risk strategy. Scale of technology, risk indicators, and proposed risk budget are all factors that could affect the feasibility and sustainability of the IT risk strategy, but they do not necessarily reflector influence the organization’s risk culture. References = Risk and Information Systems Control Study Manual, Chapter 1, Section 1.2.1, page 1-9.
it was determined that replication of a critical database used by two business units failed. Which of the following should be of GREATEST concern1?
The underutilization of the replicated Iink
The cost of recovering the data
The lack of integrity of data
The loss of data confidentiality
The lack of integrity of data is the greatest concern when replication of a critical database used by two business units failed. Data integrity means that the data is accurate, complete, consistent, and reliable. If the replication failed, it means that the data in the primary and secondary databases may not be synchronized and may have discrepancies or errors. This could affect the quality and reliability of the data and the business processes that depend on it. The other options are not as concerning as the lack of integrity of data, as they are related to the efficiency, cost, or confidentiality of the data, which are less critical than the accuracy and reliability of the data. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.2: Key Performance Indicators, page 183.
An organization is unable to implement a multi-factor authentication requirement until the next fiscal year due to budget constraints. Consequently, a policy exception must be submitted. Which of the following is MOST important to include in the analysis of the exception?
Sections of the policy that may justify not implementing the requirement
Risk associated with the inability to implement the requirement
Budget justification to implement the new requirement during the current year
Industry best practices with respect to implementation of the proposed control
The most important factor to include in the analysis of the policy exception is the risk associated with the inability to implement the multi-factor authentication requirement. A policy exception is a temporary orpermanent deviation from the established policies or standards of the organization, due to various reasons, such as budget constraints, technical limitations, or business needs. A policy exception must be submitted and approved by the appropriate authority, and it must include a clear and comprehensive analysis of the rationale, impact, and mitigation of the exception. The risk associated with the inability to implement the multi-factor authentication requirement is the most important factor to include in the analysis, because it evaluates the probability and severity of potential threats or incidents that could exploit the lack of multi-factor authentication, such as unauthorized access, data breach, or identity theft. The risk analysis also helps to justify the need and urgency of the policy exception, and to propose alternative or compensating controls to reduce or transfer the risk, such as password policies, access restrictions, or encryption. The other options are not the most important factor, although they may be relevant or supportive to the policy exception analysis. Sections of the policy that may justify not implementing the requirement are the clauses or provisions in the policy that allow or enable the policy exception, such as exemptions, waivers, or variances. These sections can help to validate the legitimacy and feasibility of the policy exception, but they do not assess the risk or the impact of the exception. Budget justification to implement the new requirement during the current year is the explanation and evidence of the financial resources and constraints that affect the implementation of the multi-factor authentication requirement. This justification can help to demonstrate the cost-benefit and return on investment of the requirement, but it does not measure the risk or the mitigation of the exception. Industry best practices with respect to implementation of the proposed control are the proven methods and standards that are adopted by the leading organizations in a specific field or sector for implementing the multi-factor authentication requirement. These best practices can help to benchmark and improve the quality and effectiveness of the requirement, but they do not quantify the risk or the impact of the exception. References = Policy Exception Management - ISACA, Multi-Factor Authentication Policy - University of Arkansas, Common Conditional Access policy: Require MFA for all users
Which of the following is the MOST important key performance indicator (KPI) to monitor the effectiveness of disaster recovery processes?
Percentage of IT systems recovered within the mean time to restore (MTTR) during the disaster recovery test
Percentage of issues arising from the disaster recovery test resolved on time
Percentage of IT systems included in the disaster recovery test scope
Percentage of IT systems meeting the recovery time objective (RTO) during the disaster recovery test
The most important key performance indicator (KPI) to monitor the effectiveness of disaster recovery processes is the percentage of IT systems meeting the recovery time objective (RTO) during the disaster recovery test. The RTO is the maximum acceptable time that a system orprocess can be unavailable after a disruption. The disaster recovery test is a simulation of a disaster scenario to evaluate the readiness and capability of the organization to restore its critical functions and systems. By measuring the percentage ofIT systems meeting the RTO during the test, the organization can assess how well the disaster recovery processes meet the predefined objectives and standards. Percentage of IT systems recovered within the mean time to restore (MTTR), percentage of issues arising from the disaster recovery test resolved on time, and percentage of IT systems included in the disaster recovery test scope are other possible KPIs, but they are not as important as the percentage of IT systems meeting the RTO. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 12; CRISC Review Manual, 6th Edition, page 215.
The MAIN reason for prioritizing IT risk responses is to enable an organization to:
determine the risk appetite.
determine the budget.
define key performance indicators (KPIs).
optimize resource utilization.
Optimizing resource utilization is the main reason for prioritizing IT risk responses, as it helps to allocate resources to the most critical and urgent risks. The other options are not the main reasons for prioritizing IT risk responses, although they may be related to the process.
Which of the following BEST promotes commitment to controls?
Assigning control ownership
Assigning appropriate resources
Assigning a quality control review
Performing regular independent control reviews
Commitment to controls is the degree to which the organization and its stakeholders support and adhere to the controls that are designed and implemented to manage or mitigate the risks1. Commitment to controls is essential for ensuring the effectiveness and efficiency of the controls, as well as the achievement of the organization’s objectives and strategies2. The best way to promote commitment to controls is to assign control ownership, which is the process ofidentifying and assigning the person or entity that has the authority and accountability for a control and its management3. By assigning control ownership, the organization can ensure that the controls are properly and promptly designed, implemented, monitored, and maintained, and that the issues or gaps in the controls are identified andresolved4. Assigning control ownership also helps to establish and communicate the roles and responsibilities of the control owners and the other stakeholders, and to enforce the accountability and performance of the control owners5. Assigning appropriate resources, assigning a quality control review, and performing regular independent control reviews are not the best ways to promote commitment to controls, as they donot provide the same level of authority and accountability as assigning control ownership. Assigning appropriate resources is the process of allocating and providing the necessary funds, staff, equipment, or technology that are required to support or enable the controls. Assigning appropriate resources can enhance the quality and performance of the controls, but it does not ensure that the controls are managed or maintained by a specific person or entity. Assigning a quality control review is the process of conducting and documenting a systematic and objective examination and evaluation of the controls, to ensure that they meet the established standards and requirements. Assigning a quality control review can improve the reliability and compliance of the controls, but it does not ensure that the controls are owned or operated by a specific person or entity. Performing regular independent control reviews is the process of performing and reporting an independent and impartial assessment and verification of the controls, to provide assurance and advice on the adequacy and effectiveness of the controls. Performing regular independent control reviews can provide feedback and recommendations for the controls, but it does notensure that the controls are implemented or improved by a specific person or entity. References = 1: Commitment Controls - IMF2: 17 COSO Principles of Effective Internal Control | Weaver3: [Control Ownership - ISACA] 4: [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.1: Control Design, pp. 233-235.] 5: [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.2: Control Implementation, pp. 243-245.] : Resource Allocation - an overview | ScienceDirect Topics : Quality Control Review - an overview | ScienceDirect Topics : IT Risk Resources | ISACA : [Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.1: Risk Identification, pp. 57-59.] : [Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.2: Risk Monitoring, pp. 189-191.] : [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.3: Control Monitoring and Maintenance, pp. 251-253.]
Which of the following is a risk practitioner ' s BEST recommendation to address an organization ' s need to secure multiple systems with limited IT resources?
Apply available security patches.
Schedule a penetration test.
Conduct a business impact analysis (BIA)
Perform a vulnerability analysis.
The best recommendation to address an organization’s need to secure multiple systems with limited IT resources is to perform a vulnerability analysis. A vulnerability analysis is a process of identifying, assessing, and prioritizing the weaknesses or flaws in the systems that could be exploited by threats or risks. A vulnerability analysis helps to determine the level and nature of the exposure and impact of the systems, and to select and implement the appropriate security controls or mitigations. Performing a vulnerability analysis is the best recommendation, as it helps to optimize the use of the limited IT resources, by focusing on the most critical or significant vulnerabilities, and by applying the most effective or efficient security solutions.Performing a vulnerability analysis also helps to improve the security posture and performance of the systems, and to reduce the likelihood and consequences of security incidents or breaches. Applying available security patches, scheduling a penetration test, and conducting a business impact analysis (BIA) are not the best recommendations, as they are either the outputs or the inputs of the vulnerability analysis process, and they do not address the primary need of securing the systems with limited IT resources. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 217.
When creating a separate IT risk register for a large organization, which of the following is MOST important to consider with regard to the existing corporate risk ' register?
Leveraging business risk professionals
Relying on generic IT risk scenarios
Describing IT risk in business terms
Using a common risk taxonomy
Using a common risk taxonomy is the most important factor to consider when creating a separate IT risk register for a large organization with regard to the existing corporate risk register, as it ensures consistency, clarity, and alignment of the IT risk identification, classification, and reporting with the corporate risk management framework and strategy. Leveraging business risk professionals, relying on generic IT risk scenarios, and describing IT risk in business terms are not the most important factors, as they are more related to the resources, inputs, or outputs of the IT risk register, respectively, rather than the structure or format of the IT risk register. References = CRISC Review Manual, 7th Edition, page 100.
When reporting to senior management on changes in trends related to IT risk, which of the following is MOST important?
Materiality
Confidentiality
Maturity
Transparency
The most important factor when reporting to senior management on changes in trends related to IT risk is materiality. Materiality is the extent to which the information reported is significant, relevant, and useful for decision-making purposes. Materiality helps to prioritize the most important risks and communicate them effectively to senior management12
1: Integrating KRIs and KPIs for Effective Technology Risk Management - ISACA 2: CRISC Review Manual, 7th Edition, page 271
Which of the following BEST enables effective IT control implementation?
Key risk indicators (KRIs)
Documented procedures
Information security policies
Information security standards
Documented procedures are the best way to enable effective IT control implementation. Documented procedures are the specific actions or steps that are performed to achieve the IT control objectives and mitigate the IT risks. Documented procedures provide clear guidance, consistency, and accountability for the IT control activities. Documented procedures also help to monitor and evaluate the effectiveness and efficiency of the IT controls, and to identify and address any gaps or weaknesses. The other options are not as effective as documented procedures, although they may support or complement the IT control implementation. Key risk indicators (KRIs) are metrics that measure the likelihood and impact of IT risks, but they do not specify how to implement the IT controls. Information security policies and standards are high-level statements that define the IT security goals and requirements, but they do not detail how to implement the IT controls. References = Risk and Information Systems Control Study Manual, Chapter 1, Section 1.3.2, page 1-15.
Which of the following is the PRIMARY advantage of aligning generic risk scenarios with business objectives?
It establishes where controls should be implemented.
It ensures relevance to the organization.
It quantifies the materiality of any losses that may occur.
It provides better estimates of the impact of current threats.
By aligning risk scenarios with business objectives, risk practitioners can accurately measure the potential loss (materiality) based on business value. This enhances prioritization and allows for risk treatment to be directed toward what impacts the organization’s mission and goals the most.
Which of the following is a crucial component of a key risk indicator (KRI) to ensure appropriate action is taken to mitigate risk?
Management intervention
Risk appetite
Board commentary
Escalation triggers
The best answer is D. Escalation triggers. Escalation triggers are predefined thresholds or conditions that indicate when a key risk indicator (KRI) has reached a critical level that requires immediate attention or action. Escalation triggers can be based on quantitative or qualitative measures, such as percentages, scores, ratings, or colors. Escalation triggers can help to ensure appropriate action is taken to mitigate risk, because they provide clear and timely signals that alert the risk owners, managers, and other stakeholders of the need to review and revise the risk response plan, or to implement additional or alternative controls. Escalation triggers can also help to communicate and report the risk status and the risk response actions to the senior management and the board, and to obtain their support and approval, if needed. The otheroptions are not the best answer, although they may be related or influential to the KRI and the risk mitigation. Management intervention is a part of the risk response process, which involves the actions and decisions taken by the management to address the risk, such as approving, implementing, or monitoring the controls. Management intervention can help to mitigate risk, but it is not a component of the KRI, rather it is a consequence or a result of the escalation triggers. Risk appetite is the amount and type of risk that an organization is willing to accept or pursue in order to achieve its objectives. Risk appetite can help to define and align the KRI and the escalation triggers with the organizational strategy and culture, but it is not a component of the KRI, rather it is a factor or a driver of the KRI. Board commentary is a part of the risk reporting process, which involves the feedback and guidance provided by the board on the risk management process and performance. Board commentary can help to improve and enhance the KRI and the risk mitigation, but it is not a component of the KRI, rather it is a source or a resource of the KRI. References = Key Risk Indicators: A Practical Guide | SafetyCulture, KRI Framework for Operational Risk Management | Workiva
Which of the following is the MOST important reason to validate that risk responses have been executed as outlined in the risk response plan ' '
To ensure completion of the risk assessment cycle
To ensure controls arc operating effectively
To ensure residual risk Is at an acceptable level
To ensure control costs do not exceed benefits
The most important reason to validate that risk responses have been executed as outlined in the risk response plan is to ensure that the residual risk is at an acceptable level. Residual risk is the risk that remains after applying a risk response. The risk response plan is the document thatdescribes the actions and resources needed to address the risk. Validating the risk response execution is the process of verifying that the risk response actions have been performed as planned, and that they have achieved the desired results. Validating the risk response execution helps to measure and monitor the residual risk, and to ensure that it is within the risk tolerance of the organization and its stakeholders. The other reasons are not as important as ensuring that the residual risk is at an acceptable level, although they may be secondary benefits or outcomes of validating the risk response execution. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-23.
An organization has outsourced its ERP application to an external SaaS provider. Which of the following provides the MOST useful information to identify risk scenarios involving data loss?
Data classification schemes
Industry data breach reports
Data storage locations
Data flow documentation
Data flow documentation provides insight into how and where data moves, stored, or processed. It helps identify vulnerable points in the data lifecycle where data loss can occur.
Which of the following should be done FIRST when a new risk scenario has been identified
Estimate the residual risk.
Establish key risk indicators (KRIs).
Design control improvements.
Identify the risk owner.
•A risk owner is the person or entity that has the authority and responsibility to manage a specific risk1. The risk owner is accountable for the implementation and effectiveness of the risk response strategy and the risk treatment plan2.
•Identifying the risk owner is the first step when a new risk scenario has been identified, because the risk owner is the key stakeholder who will be involved in the subsequent steps of the risk management process, such as risk analysis, risk evaluation, risk treatment, and risk monitoring2.
•Identifying the risk owner also helps to clarify the roles and responsibilities of different parties involved in the risk management process, such as the risk manager, the risk analyst, the risk committee, and the risk auditor3. This can improve the communication, coordination, and collaboration among the risk management team and ensure that the risk is managed effectively and efficiently.
•Estimating the residual risk (option A) is not the first step when a new risk scenario has been identified, because the residual risk is the risk that remains after the risk treatment plan has been implemented2. Therefore, estimating the residual risk requires prior steps such as risk analysis, risk evaluation, and risk treatment.
•Establishing key risk indicators (KRIs) (option B) is not the first step when a new risk scenario has been identified, because KRIs are metrics or data points that provide early warning signals or information about the level or trend of a risk4. Therefore, establishing KRIs requires prior steps such as risk identification, risk analysis, and risk evaluation.
•Designing control improvements (option C) is not the first step when a new risk scenario has been identified, because control improvements are part of the risk treatment plan, which is the set of actions and resources needed to implement the chosen risk response strategy2. Therefore,designing control improvements requires prior steps such as risk analysis, risk evaluation, and risk response selection.
References =
•Risk Owner - Institute of Internal Auditors
•Risk Treatment Plan - ISACA
•Risk Management Roles and Responsibilities - 360factors
•Key Risk Indicators: A Practical Guide | SafetyCulture
Which of the following MUST be updated to maintain an IT risk register?
Expected frequency and potential impact
Risk tolerance
Enterprise-wide IT risk assessment
Risk appetite
An IT risk register is a document that records and tracks the significant IT risks that an organization faces across its various functions, processes, and activities. An IT risk register can help to provide a comprehensive and consistent view of the organization’s IT risk profile, and to support the decision making and reporting of the IT risk management function1.
One of the data that must be updated to maintain an IT risk register is the expected frequency and potential impact of each IT risk. The expected frequency is the probability or likelihood of the IT risk occurring, based on historical data, statistical analysis, expert judgment, or other methods. The potential impact is the magnitude or severity of the consequences or outcomes of the IT risk, measured in terms of cost, time, quality, reputation, or other criteria2.
Updating the expected frequency and potential impact of each IT risk is essential for maintaining an IT risk register, because it can help to:
Evaluate and prioritize the IT risks based on their risk level, which is calculated by multiplying the frequency and impact
Monitor and track the changes or trends in the IT risk exposure and performance over time
Identify and implement the appropriate risk response strategies and controls, based on the risk level and the risk appetite and tolerance of the organization
Report and communicate the IT risk status and progress to the stakeholders, using risk indicators, dashboards, or matrices3
The other options are not the data that must be updated to maintain an IT risk register, but rather the data that are used as inputs or outputs of the IT risk management process. Risk tolerance is the acceptable variation in the outcomes related to specific objectives or risks. Risk tolerance is used to measure the IT risk analysis and to guide the IT risk response. Enterprise-wide IT risk assessment is a process that identifies, analyzes, and evaluates the IT risks across theorganization. Enterprise-wide IT risk assessment is used topopulate the IT risk register and to inform the IT risk response. Risk appetite is the amount and type of risk that an organization is willing to accept in order to achieve its objectives. Risk appetite is used to guide the IT risk analysis and to align the IT risk response. References =
Risk Register - ISACA
Risk Analysis - ISACA
Risk Register 2021-2022 - UNECE
[How To Conduct Business Impact Analysis in 8 Easy Steps - G2]
[Risk Appetite and Risk Tolerance - ISACA]
[Enterprise Risk Assessment - ISACA]
[CRISC Review Manual, 7th Edition]
Which of the following is the BEST indication of an effective risk management program?
Risk action plans are approved by senior management.
Residual risk is within the organizational risk appetite
Mitigating controls are designed and implemented.
Risk is recorded and tracked in the risk register
An effective risk management program is a systematic and consistent process of identifying, analyzing, evaluating, treating, monitoring, and communicating risks that may affect the achievement of the organization’s objectives12.
The best indication of an effective risk management program is that the residual risk, which is the risk remaining after risk treatment, is within the organizational risk appetite, which is the amount and type of risk that the organization is willing to accept in pursuit of its objectives12.
This indicates that the organization has successfully implemented appropriate risk responses that align with its risk strategy and criteria, and that the organization is able to balance the potential benefits and costs of taking risks12.
The other options are not the best indication, but rather components or outcomes of an effective risk management program. For example:
Risk action plans are approved by senior management is an outcome of an effective risk management program that demonstrates the commitment and accountability of the leadership for risk management12.
Mitigating controls are designed and implemented is a component of an effective risk management program that involves reducing the likelihood or impact of a risk event12.
Risk is recorded and tracked in the risk register is a component of an effective risk management program that involves documenting and updating the risk information and status12. References =
1: Risk IT Framework, ISACA, 2009
2: IT Risk Management Framework, University of Toronto, 2017
Which of the following should be the GREATEST concern for an organization that uses open source software applications?
Lack of organizational policy regarding open source software
Lack of reliability associated with the use of open source software
Lack of monitoring over installation of open source software in the organization
Lack of professional support for open source software
Lack of organizational policy regarding open source software should be the greatest concern for an organization that uses open source software applications, as it may expose the organization to legal, security, and operational risks. Open source software is software that is freely available and can be modified and distributed by anyone, subject to certain conditions and licenses. An organizational policy regarding open source software should define the criteria and procedures for selecting, acquiring, using, and maintaining open source software, as well as the roles and responsibilities of the stakeholders involved. Lack of reliability, lack of monitoring, and lack of professional support are not the greatest concerns, as they can be addressed by implementing quality assurance, configuration management, and community engagement practices for open source software. References = CRISC by Isaca Actual Free Exam Q & As, question 214; CRISC: Certified in Risk & Information Systems Control Sample Questions, question 214.
Which of the following BEST enables a risk practitioner to enhance understanding of risk among stakeholders?
Key risk indicators (KRIs)
Risk scenarios
Business impact analysis (BIA)
Threat analysis
Risk scenarios are descriptions of possible events or situations that could cause or affect a risk. Risk scenarios can help a risk practitioner to enhance understanding of risk among stakeholders, as they can illustrate the causes, consequences, and impacts of the risk in a clear and realistic way. Risk scenarios can also facilitate communication and collaboration among stakeholders, as they can provide a common language and framework for risk identification, analysis, and response. Risk scenarios can also support decision-making and prioritization, as they can show the likelihood and severity of the risk outcomes. References = Most Asked CRISC Exam Questions and Answers. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 237.
Which of the following methods is the BEST way to measure the effectiveness of automated information security controls prior to going live?
Testing in a non-production environment
Performing a security control review
Reviewing the security audit report
Conducting a risk assessment
Automated information security controls are controls that are implemented or executed by software or hardware, without human intervention, to protect the confidentiality, integrity, and availability of information and systems1. Examples of automated information security controls include firewalls, antivirus software, encryption, authentication, and logging2. The effectiveness of automated information security controls refers to how well they achieve their intended objectives and outcomes, such as preventing, detecting, or responding to security threats or incidents3. The best way to measure the effectiveness of automatedinformation security controls prior to going live is to test them in a non-production environment, which is an environment thatsimulates the production environment, but does not contain real or sensitive data orsystems4. Testing in a non-production environment allows the organization to verify the proper and consistent configuration, functionality, and performance of the automated information security controls, without affecting the normal operations or risking the exposure of the data or systems5. Testing in a non-production environment also enables the organization to identify andresolve any issues or gaps in the automated information security controls, and to evaluate their compatibility and interoperability with other systems or controls6. Performing a security control review, reviewing the security audit report, and conducting a risk assessment are not the best ways to measure the effectiveness of automated information security controls prior to going live, as they do not provide direct and timely information on the configuration, functionality, and performance of the automated information security controls. Performing a security control review is a process that involves checking and verifying that the organization’s security controls are up to date, relevant, and effective7. A security control review can help to identify and address any issues or gaps in the security controls, but it does not show the actual behavior and results of the automated information security controls in a realistic environment. Reviewing the security audit report is a process that involves reading and analyzing the findings and recommendations of an independent examination and evaluation of the organization’s security controls8. A security audit report can help to provide assurance and advice on the adequacy and effectiveness of the security controls, but it does not show the current and dynamic status and performance of the automated information security controls in a changing environment. Conducting a risk assessment is a process that involves identifying, analyzing, and evaluating the risks and their potential impacts on the organization’s objectives and performance. A risk assessment can help to anticipate and prepare for the risks that may affect the organization’s security, but it does not show the actual impact and outcome of the automated information security controls in a specific scenario. References = 1: Automation Support for Security Control Assessments - NIST2: Automated Security Control Assessment: When Self-Awareness Matters3: Technology Control Automation: Improving Efficiency, Reducing … - ISACA4: [What is a Non-Production Environment? | Definition and FAQs] 5: [Why You Need a Non-Production Environment - Plutora] 6: [Testing Automated Security Controls - SANS Institute] 7: A brief guide to assessing risks and controls | ACCA Global8: IT Risk Resources | ISACA : [Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.1: Risk Identification, pp. 57-59.]
Which of the following is the MOST important reason for an organization to regularly assess the design of key risk indicators (KRIs)?
Increasing process failures could impact a key objective.
Tolerance levels change as strategies evolve.
System enhancements could bypass the change control process.
Data required for risk reporting changes with industry trends.
As strategies evolve, so do the acceptable risk thresholds (tolerances). Regular KRI reassessment ensures alignment with the current risk appetite and supports timely, risk-informed decisions.
When testing the security of an IT system, il is MOST important to ensure that;
tests are conducted after business hours.
operators are unaware of the test.
external experts execute the test.
agreement is obtained from stakeholders.
According to the CRISC Review Manual1, stakeholders are the individuals or groups that have an interest or stake in the outcome of the IT system and its risks. Stakeholders include the system owners, users, operators, developers, managers, auditors, regulators, and customers. It is most important to ensure that agreement is obtained from stakeholders when testing the security of an IT system, as this helps to define the scope, objectives, and expectations of the test, and to obtain the necessary authorization, support, and resources for the test. Agreement from stakeholders also helps to avoid any conflicts, disruptions, or misunderstandings that may arise during or after the test, and to ensure the validity and acceptance of the test results and recommendations. References = CRISC Review Manual1, page 198, 224.
The MOST essential content to include in an IT risk awareness program is how to:
define the IT risk framework for the organization
populate risk register entries and build a risk profile for management reporting
comply with the organization ' s IT risk and information security policies
prioritize IT-related actions by considering risk appetite and risk tolerance
An IT risk awareness program shouldprimarily ensure that employees and stakeholders understand and comply with the organization ' s risk and information security policies. ISACA highlights that an awareness program must reinforce policy understanding to drive compliant and secure behavior across the organization.
===========
Which of the following BEST enables effective risk reporting to the board of directors?
Presenting case studies of breaches from other similar organizations
Mapping risk scenarios to findings identified by internal audit
Communicating in terms that correlate to corporate objectives and business value
Reporting key metrics that indicate the efficiency and effectiveness of risk governance
Effective risk reporting to the board of directors requires communication that aligns with the organization ' s strategic goals and business value. By correlating risk information to corporate objectives, the board can better understand the implications of risks on the organization ' s performance and make informed decisions. This approach ensures that risk discussions are relevant and meaningful at the executive level.
As part of an aggressive new marketing strategy, an organization has decided to implement an emerging technology in a critical business system. Which of the following is the BEST course of action to address the risk associated with this new technology?
Update the risk tolerance and appetite
Identify technical solutions
Obtain senior management support
Re-evaluate the risk and existing controls
When adopting new technology, the first step is toreassess risks and control effectivenessbecause the technology may introduce new vulnerabilities or alter existing risk profiles.
CRISC guidance:
“Significant changes to business or technology environments should trigger a re-evaluation of existing risk scenarios and control effectiveness to identify new or residual risk.”
Updating appetite or seeking support follows after reassessment.
Hence,Dis correct.
CRISC Reference:Domain 2 – IT Risk Assessment, Topic: Emerging Technology Risk.
Which of the following is MOST helpful in identifying loss magnitude during risk analysis of a new system?
Recovery time objective (RTO)
Cost-benefit analysis
Business impact analysis (BIA)
Cyber insurance coverage
Business impact analysis (BIA) is the most helpful tool in identifying loss magnitude during risk analysis of a new system, as it involves estimating the potential financial and operational losses resulting from the disruption or degradation of the system. Recovery time objective (RTO), cost-benefit analysis, and cyber insurance coverage are not the most helpful tools, as they are more related to the recovery, evaluation, andtransfer of the risk, respectively, rather than the identification of the loss magnitude. References = CRISC Review Manual, 7th Edition, page 108.
During a risk assessment, a risk practitioner learns that an IT risk factor is adequately mitigated by compensating controls in an associated business process. Which of the following would enable the MOST effective management of the residual risk?
Schedule periodic reviews of the compensating controls ' effectiveness.
Report the use of compensating controls to senior management.
Recommend additional IT controls to further reduce residual risk.
Request that ownership of the compensating controls is reassigned to IT
A compensating control is a control that is implemented to reduce the risk exposure when the primary control is not feasible or cost-effective. A compensating control may not directly address the root cause of the risk, but it can provide an alternative or supplementary way of mitigating the risk. A residual risk is the risk that remains after the risk response has been implemented. A residual risk can be accepted, monitored, or further reduced depending on the risk tolerance and appetite of the organization. During a risk assessment, a risk practitioner is a person who is responsible for identifying and analyzing the potential sources and consequences of risk events. When a risk practitioner learns that an IT risk factor is adequately mitigated by compensating controls in an associated business process, the action that would enable the most effective management of the residual risk is to schedule periodic reviews of the compensating controls’ effectiveness, which means to measure and evaluate the performance and compliance of the compensating controls on a regular basis. By scheduling periodic reviews of the compensating controls’ effectiveness, the risk practitioner can ensure that the compensating controls are stilloperating as intended, and that they are delivering the expected results. The risk practitioner can also identify any gaps or weaknesses in the compensating controls, and recommend any improvements or adjustments as needed. References = CRISC Review Manual, 7th Edition, page 177.
IT management has deployed a major update to reduce the risk of system compromise. What is the BEST way to validate the effectiveness of this control?
Conduct social engineering testing.
Perform penetration testing.
Run vulnerability scans.
Review mean time to apply critical patches.
The correct answer is B because penetration testing validates whether the implemented control actually resists realistic compromise attempts. The uploaded CRISC notes state that penetration testing offers the greatest level of assurance regarding the effectiveness of implemented security controls and that penetration testing is the best way to ensure network security against external attacks.
ISACA also states that control testing demonstrates whether controls are mitigating risk as intended, including assessing network security and testing controls designed to prevent or detect unauthorized access, data breaches, and system failures. ISACA further explains that penetration testing evaluates vulnerabilities and supports effective risk response decisions.
C, vulnerability scanning, is useful for identifying known vulnerabilities, and it may be appropriate for validating a patching program. However, the question asks for the BEST way to validate effectiveness of a major update intended to reduce system compromise, making penetration testing stronger. A is too narrow because social engineering tests people rather than the technical control. D is only a metric and does not validate whether the update reduced compromise risk.
Which of the following should be considered when selecting a risk response?
Risk scenarios analysis
Risk response costs
Risk factor awareness
Risk factor identification
When selecting a risk response, the following should be considered:
B. Risk response costs
It’s important to evaluate the costs associated with implementing a risk response to ensure that they are justified by the benefits of mitigating the risk. This helps in making cost-effective decisions that align with the organization’s risk management objectives.
Which of the following BEST enables detection of ethical violations committed by employees?
Transaction log monitoring
Access control attestation
Periodic job rotation
Whistleblower program
Whistleblower Program:
Definition: A whistleblower program allows employees to report unethical or illegal activities within the organization anonymously.
Detection of Ethical Violations: Employees are often in the best position to observe unethical behavior. A well-structured whistleblower program encourages them to report such behavior without fear of retaliation.
Anonymity and Protection: Providing anonymity and protection to whistleblowers increases the likelihood that employees will report violations, thus enabling the organization to detect and address ethical issues more effectively.
Comparison with Other Options:
Transaction Log Monitoring: While useful for detecting anomalies and potential fraud, it is not specifically focused on ethical violations and may not capture all types of unethical behavior.
Access Control Attestation: This ensures that users have the correct access permissions but does not directly detect unethical behavior.
Periodic Job Rotation: This can help prevent fraud by reducing the risk of collusion and providing fresh perspectives on processes, but it does not directly detect ethical violations.
Best Practices:
Clear Reporting Channels: Ensure that the whistleblower program has clear and accessible reporting channels.
Training and Awareness: Regularly train employees on the importance of reporting unethical behavior and the protections offered by the whistleblower program.
Follow-up and Action: Ensure that reports are investigated thoroughly and appropriate actions are taken to address verified violations.
Which of the following is the PRIMARY reason to use administrative controls in conjunction with technical controls?
To gain stakeholder support for the implementation of controls
To comply with industry best practices by balancing multiple types of controls
To improve the effectiveness of controls that mitigate risk
To address multiple risk scenarios mitigated by technical controls
Administrative controls, such as policies, procedures, and training, complement technical controls by addressing the human and organizational aspects of risk management. Using bothtypes of controls together enhances the overall effectiveness of the risk mitigation strategy, ensuring that technical measures are supported by appropriate governance and user behavior.
During a recent security framework review, it was discovered that the marketing department implemented a non-fungible token asset program. This was done without following established risk procedures. Which of the following should the risk practitioner do FIRST?
Report the infraction.
Perform a risk assessment.
Conduct risk awareness training.
Discontinue the process.
Perform a Risk Assessment:
Immediate Action: The first step when discovering a non-compliant implementation is to understand the potential risks it poses to the organization. This involves identifying threats, vulnerabilities, and potential impacts of the non-fungible token (NFT) asset program.
Risk Identification and Evaluation: Assess the new program’s impact on the organization’s risk profile. Determine if it introduces significant security, compliance, or operational risks.
Documentation and Reporting: Document the findings and present them to senior management along with recommendations for mitigation or further action.
Comparison with Other Options:
Report the Infraction: Reporting is necessary but should follow the risk assessment to provide a clear understanding of the implications and necessary mitigations.
Conduct Risk Awareness Training: Training is preventive and should be part of a long-term strategy, not the immediate response to a specific incident.
Discontinue the Process: Discontinuing the process may be a necessary step after assessing the risk, but the assessment must come first to justify such an action.
Best Practices:
Comprehensive Risk Assessment: Ensure that the risk assessment covers all aspects, including financial, reputational, and regulatory risks.
Stakeholder Involvement: Involve relevant stakeholders in the assessment process to gather diverse perspectives and ensure a thorough evaluation.
Actionable Recommendations: Provide clear, actionable recommendations based on the risk assessment findings.
Which of the following is MOST helpful in identifying new risk exposures due to changes in the business environment?
Standard operating procedures
SWOT analysis
Industry benchmarking
Control gap analysis
New risk exposures due to changes in the business environment are the possibilities and impacts of new or emerging threats or opportunities that may affect the organization’s objectives, performance, or value creation, as a result of changes in the internal or external factors that influence the organization’s operations, such as technology, competition, regulation, or customer behavior12.
The most helpful tool in identifying new risk exposures due to changes in the business environment is a SWOT analysis, which is a technique that involves identifying and analyzing the strengths, weaknesses, opportunities, and threats (SWOT) that are relevant to the organization’s situation, goals, and capabilities34.
A SWOT analysis is the most helpful tool because it helps the organization to scan and assess the business environment, and to identify and prioritize the new or emerging risk exposures that may arise from the changes in the environment34.
A SWOT analysis is also the most helpful tool because it helps the organization to align and adapt its strategy and actions to the changes in the environment, and to leverage its strengths and opportunities, and mitigate its weaknesses and threats34.
The other options are not the most helpful tools, but rather possible sources or inputs that may be used in a SWOT analysis. For example:
Standard operating procedures are documents that describe the routine tasks and processes that are performed by the organization, and the policies and standards that govern them56. However, these documents are not the most helpful tools because they may not reflect or capture the changes in the business environment, and they may need to be revised or updated to address the new or emerging risk exposures56.
Industry benchmarking is a technique that involves comparing and contrasting the performance and practices of the organization with those of the similar or leadingorganizations in the same or related industry, and identifying the gaps or opportunities for improvement78. However, this technique is not the most helpful tool because it may not provide a comprehensive or holistic view of the business environment, and it may not align with the organization’s specific situation, goals, or capabilities78.
Control gap analysis is a technique that involves assessing and evaluating the adequacy and effectiveness of the controls that are designed and implemented to mitigate the risks, and identifying and addressing the areas or aspects that need to be improved or added . However, this technique is not the most helpful tool because it is reactive rather than proactive, and it may not identify or anticipate the new or emerging risk exposures that may result from the changes in the business environment . References =
1: Risk IT Framework, ISACA, 2009
2: IT Risk Management Framework, University of Toronto, 2017
3: SWOT Analysis - ISACA1
4: SWOT Analysis: What It Is and When to Use It2
5: Standard Operating Procedure - Wikipedia3
6: How to Write Effective Standard Operating Procedures (SOP)4
7: Benchmarking - Wikipedia5
8: Benchmarking: Definition, Types, Process, Advantages & Examples6
Control Gap Analysis - ISACA7
Control Gap Analysis: A Step-by-Step Guide8
A risk practitioner has been made aware of a problem in an IT system that was missed during a routine risk assessment. Which of the following is the practitioner ' s BEST course of action?
Record the problem as a new issue in the risk management system
Record a new issue but backdate it to the original risk assessment date
Report the vulnerability to the asset owner ' s manager
Document the issue during the next risk assessment
Thebest practiceis torecord the problem immediately as a new issuein the risk management system. ISACA emphasizes maintaining an up-to-date risk register to ensure emerging issues are tracked and addressed in a timely manner.
===========
Which of the following is the MOST important data attribute of key risk indicators (KRIs)?
The data is measurable.
The data is calculated continuously.
The data is relevant.
The data is automatically produced.
Key risk indicators (KRIs) are metrics that provide information about the level of exposure to a specific risk or a group of risks.
The most important data attribute of KRIs is that the data is relevant. This means that the data reflects the current state of the risk, the potential impact of the risk, and the effectiveness of the risk response. Relevant data helps to monitor and measure the risk performance and to make informed decisions about risk management.
The other options are not the most important data attributes of KRIs. They are either secondary or not essential for KRIs.
The references for this answer are:
Risk IT Framework, page 15
Information Technology & Security, page 9
Risk Scenarios Starter Pack, page 7
Which of the following is the BEST control to prevent unauthorized access to an organization ' s critical assets?
Data loss prevention (DLP)
Intrusion detection system (IDS)
Multi-factor authentication (MFA)
Intrusion prevention system (IPS)
Which of the following is the BEST indication that an organization ' s IT asset life cycle is poorly managed?
Increased hardware maintenance costs
Sensitive data found on discarded devices
Lack of asset labeling
Inadequate employee training
The correct answer isBbecause findingsensitive data on discarded devicesis the clearest indication that the IT asset life cycle is poorly managed. This points to failure in end-of-life handling, media sanitization, disposal controls, ownership accountability, and policy enforcement. It is a direct indicator of life cycle control breakdown with significant security and compliance consequences.
The other options are less conclusive:
A. Increased hardware maintenance costsmay indicate inefficiency, but not necessarily poor life cycle control.
C. Lack of asset labelingis a weakness, but less severe and less direct than improper disposal of sensitive data.
D. Inadequate employee trainingmay contribute to problems, but it is not the strongest indicator by itself.
Exact Extracts supporting the answer:
“When data are no longer needed by a particular process they should be handled according to policy.”
“Information that is no longer required to support the main purpose of the enterprise from an information security perspective should be managed under the retention policy.”
“The data security control that BEST protects the confidentiality of data stored on backup media in transit to a third-party storage facility is encryption.”
“The BEST safeguard against a data breach is security awareness training.”
These extracts support that assets and the data on them must be handled according to policy throughout the life cycle, especially when no longer needed. Sensitive data remaining on discarded devices is therefore the strongest indication of poor asset life cycle management.
===========
Which of the following would MOST likely result in updates to an IT risk appetite statement?
External audit findings
Feedback from focus groups
Self-assessment reports
Changes in senior management
An IT risk appetite statement is a document that expresses the amount and type of IT risk that an organization is willing to accept or pursue in order to achieve its objectives. An IT risk appetite statement can help guide the IT risk management process, by setting the boundaries, criteria, andtargets for IT risk identification, assessment, response, and reporting. An IT risk appetite statement should be aligned with the organization’s overall risk appetite and strategy, and should be reviewed and updated periodically to reflect the changes in the internal and external environment. One of the factors that would most likely result in updates to an IT risk appetite statement is changes in senior management. Senior management is the group of executives who have the authority and responsibility for the strategic direction and performance of the organization. Changes in senior management can affect the IT risk appetite statement, as they may introduce new perspectives, priorities, expectations, or preferences for IT risk taking or avoidance. Changes in senior management can also affect the IT risk appetite statement, as they may require new or revised IT objectives, goals, or initiatives, which may entail different levelsor types of IT risk. Therefore, changes in senior management should trigger a review and update of the IT risk appetite statement, to ensure that it is consistent and compatible with the new leadership and direction of the organization. References = Organisations must define their IT risk appetite and tolerance, Risk Appetite Statements - Institute of Risk Management, Develop Your Technology Risk Appetite - Gartner.
Following the implementation of an Internet of Things (loT) solution, a risk practitioner identifies new risk factors with impact to existing controls. Which of the following is MOST important to include in a report to stakeholders?
Identified vulnerabilities
Business managers ' concerns
Changes to residual risk
Risk strategies of peer organizations
Which of the following is the BEST course of action to help reduce the probability of an incident recurring?
Perform a risk assessment.
Perform root cause analysis.
Initiate disciplinary action.
Update the incident response plan.
An incident is an unplanned event that disrupts or degrades the normal operation or performance of an IT service, system, or network1. An incident can cause various negative impacts, such as service outages, data losses, security breaches, or customer dissatisfaction2. An incident can recur if the underlying cause or problem of the incident is not properly identified and resolved3.
The best course of action to help reduce the probability of an incident recurring is to perform root cause analysis. Root cause analysis is a systematic process of finding and eliminating the fundamental cause or problem that led to the incident4. Root cause analysis can help to:
Prevent or minimize the recurrence of the incident by addressing the source of the problem, not just the symptoms or effects
Identify and implement corrective or preventive actions that can effectively resolve or mitigate the problem
Learn from the incident and improve the IT service, system, or network quality and reliability
Enhance the incident management and problem management processes and capabilities5
References = What is an Incident?, Incident Management - Wikipedia, Problem Management - Wikipedia, Root Cause Analysis - Wikipedia, Root Cause Analysis: A Guide for Business Leaders
An organization uses an automated vulnerability scanner to identify potential vulnerabilities on various enterprise systems. Who is accountable for ensuring the vulnerabilities are mitigated?
Data owners
Information security manager
System administrators
System owners
System ownershold ultimate accountability for managing risks associated with their systems, including vulnerability mitigation.
ISACA CRISC defines:
“The system owner is responsible for ensuring that security controls are implemented and that vulnerabilities identified in their systems are addressed.”
System administrators perform mitigation activities, but accountability (oversight and confirmation) remains with thesystem owner.
A: Data owners focus on data classification.
B: InfoSec managers oversee policy, not execution.
C: Admins implement controls but don’t own the risk.
Dis correct becauseownership equates to accountability.
CRISC Reference:Domain 1 – IT Risk Governance, Topic: Roles and Responsibilities in Risk Management.
An organization uses a web application hosted by a cloud service that is populated by data sent to the vendor via email on a monthly basis. Which of the following should be the FIRST consideration when analyzing the risk associated with the application?
Whether the service provider ' s data center is located in the same country
Whether the data sent by email has been encrypted
Whether the data has been appropriately classified
Whether the service provider contract allows right of onsite audit
Data classification is the process of assigning labels or categories to data based on its sensitivity, value, and criticality to the organization. Data classification is the first consideration when analyzing the risk associated with the web application hosted by a cloud service, as it determines the level of protection and controls required for the data. Data classification can help the organization to comply with legal, regulatory, and contractual obligations, such as GDPR,CCPA, and PCI DSS, and to prevent data breaches, leaks, or losses. Data classification can also help the organization to evaluate the suitability and trustworthiness of the cloud service provider, and to negotiate the terms and conditions of the service level agreement (SLA).
An organization is moving its critical assets to the cloud. Which of the following is the MOST important key performance indicator (KPI) to include in the service level agreement (SLA)?
Percentage of standard supplier uptime
Average time to respond to incidents
Number of assets included in recovery processes
Number of key applications hosted
When moving critical assets to the cloud, the most important KPI to include in the SLA is the percentage of standard supplier uptime, which measures the availability and reliability of the cloud service provider. This KPI indicates how often the cloud service is operational and accessible, and how well it meets the agreed service level objectives. A high percentage of standard supplier uptime means that the cloud service provider can deliver the expected performance and functionality of the critical assets, and minimize the risk of service disruptions, downtime, or data loss. The percentage of standard supplier uptime should be aligned with the organization’s business continuity and disaster recovery requirements, and should be monitored and reported regularly by the cloud service provider. The SLA should also specify the compensation or remediation actions in case of any breach of the agreed percentage of standard supplier uptime.
When determining which control deficiencies are most significant, which of the following would provide the MOST useful information?
Risk analysis results
Exception handling policy
Vulnerability assessment results
Benchmarking assessments
A control deficiency is a weakness or flaw in the design or implementation of a control that reduces its effectiveness or efficiency in achieving its intended objective or mitigating the risk that it is designed to address. A control deficiency may be caused by various factors, such as human error, system failure, process inefficiency, resource limitation, etc.
When determining which control deficiencies are most significant, the most useful information would be the risk analysis results, which are the outcomes or outputs of the risk analysis process that measures and compares the likelihood and impact of various risk scenarios, and prioritizes them based on their significance and urgency. The risk analysis results can help to determine which control deficiencies are most significant by providing the following information:
The level and priority of the risks that are associated with the control deficiencies, and the potential consequences or impacts that they may cause for the organization if they materialize.
The gap or difference between the current and desired level of risk, and the extent or degree to which the control deficiencies contribute to or affect the gap or difference.
The cost-benefit or feasibility analysis of the possible actions or plans to address or correct the control deficiencies, and the expected or desired outcomes or benefits that they may provide for the organization.
The other options are not the most useful information when determining which control deficiencies are most significant, because they do not provide the same level of detail and insight that the risk analysis results provide, and they may not be relevant or actionable for the organization.
An exception handling policy is a policy that defines and describes the procedures and guidelines for dealing with the situations or circumstances that deviate from the normal or expected operation or functionality of a control, and that may require special or alternative actions or measures to address or resolve them. An exception handling policy can provide useful information on how to handle or manage the control deficiencies, but it is not the most usefulinformation when determining which control deficiencies are most significant, because it does not indicate the level and priority of the risks that are associated with the control deficiencies, and the potential consequences or impacts that they may cause for the organization.
A vulnerability assessment is an assessment that identifies and evaluates the weaknesses or flaws in the organization’s assets, processes, or systems that can be exploited or compromised by the threats or sources of harm that may affect the organization’s objectives or operations. A vulnerability assessment can provide useful information on the existence and severity of the control deficiencies, but it is not the most useful information when determining which control deficiencies are most significant, because it does not indicate the likelihood and impact of the risk scenarios that are associated with the control deficiencies, and the potential consequences or impacts that they may cause for the organization.
A benchmarking assessment is an assessment that compares and contrasts the organization’s performance, practices, or processes with those of other organizations or industry standards, and identifies the strengths, weaknesses, opportunities, or threats that may affect the organization’s objectives or operations. A benchmarking assessment can provide useful information on the best practices or improvement areas for the organization, but it is not the most useful information when determining which control deficiencies are most significant, because it does not indicate the level and priority of the risks that are associatedwith the control deficiencies, and the potential consequences or impacts that they may cause for the organization. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 176
CRISC Practice Quiz and Exam Prep
Which of the following is the BEST method to ensure a terminated employee ' s access to IT systems is revoked upon departure from the organization?
Login attempts are reconciled to a list of terminated employees.
A list of terminated employees is generated for reconciliation against current IT access.
A process to remove employee access during the exit interview is implemented.
The human resources (HR) system automatically revokes system access.
The best method to ensure a terminated employee’s access to IT systems is revoked upon departure from the organization is to have the human resources (HR) system automatically revoke system access, which is a process that involves integrating the HR system with the IT system, and triggering the removal of access rights for the employee as soon as the termination is recorded in the HR system12.
This method is the best because it provides the most timely, accurate, and consistent way of revoking access, and reduces the risk of human error, oversight, or delay that may occur in manual or semi-automated processes12.
This method is also the best because it enhances the security and compliance of the organization, and prevents the terminated employee from accessing or compromising the IT systems or data after departure12.
The other options are not the best methods, but rather alternative or supplementary methods that may have some limitations or drawbacks. For example:
Login attempts are reconciled to a list of terminated employees is a method that involves monitoring and verifying the login activities of the IT systems, and comparing them with a list of terminated employees to identify and block any unauthorized access attempts34. However, this method is not the best because it is reactive rather than proactive, and may not prevent the terminated employee from accessing the IT systems before the reconciliation is done34.
A list of terminated employees is generated for reconciliation against current IT access is a method that involves creating and maintaining a list of terminated employees, and checking it against the current IT access rights to identify and remove any access that is no longer needed34. However, this method is not the best because it is manual and labor-intensive, and may introduce errors or inconsistencies in the list or the access rights34.
A process to remove employee access during the exit interview is implemented is a method that involves conducting an exit interview with the terminated employee, and revoking the employee’s access to the IT systems during or immediately after the interview34. However, this method is not the best because it depends on the availability and cooperation of the terminated employee, and may not cover all the IT systems or access rights that the employee had34. References =
1: IT Involvement in Employee Termination, A Checklist3
2: Best Practices to Ensure Departing Employees Retain No Access5
3: User Termination Best Practices - IT Security - Spiceworks2
4: IT Security for Employee Termination - Policies, Checklists, Templates - Endsight1
Which of the following is a drawback in the use of quantitative risk analysis?
It assigns numeric values to exposures of assets.
It requires more resources than other methods
It produces the results in numeric form.
It is based on impact analysis of information assets.
The drawback in the use of quantitative risk analysis is that it requires more resources than other methods. Quantitative risk analysis is a method of risk analysis that assigns numeric values to the exposures of assets, the impact and likelihood of risk events, and the cost and benefit of risk responses. Quantitative risk analysis can provide more precise and objective results, and support the risk-based decision making process. However, quantitative risk analysis also requires more resources than other methods, such as data, time, expertise, and tools, to collect, validate, and analyze the quantitative information, and to perform the complex calculations and simulations. Quantitative risk analysis may also be limited by the availability, reliability, and accuracy of thedata, and the assumptions and models used. Assigning numeric values to exposures of assets, producing the results in numeric form, and being based on impact analysis of information assets are not drawbacks, but characteristics of quantitative risk analysis. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 49.
Which of the following is the MOST significant benefit of using quantitative risk analysis instead of qualitative risk analysis?
Minimized time to completion
Decreased structure
Minimized subjectivity
Decreased cost
Quantitative risk analysis provides numerical values for likelihood and impact, thereby reducing subjectivity. It enables risk practitioners to perform cost-benefit analysis and make data-driven decisions. Though time-consuming, its objectivity is its major advantage over qualitative methods.
An organization has completed a project to implement encryption on all databases that host customer data. Which of the following elements of the risk register should be updated the reflect this change?
Risk likelihood
Inherent risk
Risk appetite
Risk tolerance
The risk likelihood is the element of the risk register that should be updated to reflect the change of implementing encryption on all databases that host customer data. The risk likelihood is the probability or frequency of a risk event occurring, and it is one of the factors that determine the risk level and priority. By implementing encryption, the organization reduces the risk likelihood of unauthorized access, disclosure, or breach of the customer data, as encryption protects the data from being read or modified by anyone who does not have the decryption key. Therefore, the risk likelihood should be updated to reflect the lower probability of the risk event after applying the encryption control. The other options are not the elements that should be updated, as they are either not affected by or not related to the change of implementing encryption. The inherent risk is the level of risk before applying any controls or mitigation measures, and it does not change after implementing encryption. The risk appetite is the amount of risk that the organization is willing to accept in pursuit of its objectives, and it is not influenced by the change ofimplementing encryption. The risk tolerance is the acceptable variation between the risk thresholds and thebusiness objectives, and it is not determined by the change of implementing encryption. References = Risk Register: A Project Manager’s Guide with Examples [2023] • Asana; Risk Assessment in Project Management | PMI; Risk Assessment Process: Definition, Steps, and Examples; Risk Assessment - an overview | ScienceDirect Topics
Which of the following is MOST helpful in developing key risk indicator (KRl) thresholds?
Loss expectancy information
Control performance predictions
IT service level agreements (SLAs)
Remediation activity progress
Key risk indicator (KRI): A metric that measures the level of risk exposure or the likelihood of a risk event1.
KRI threshold: A predefined value or range that triggers an alert or action when the KRI reaches or exceeds it2.
Loss expectancy: The estimated amount of loss that an organization may incur due to a risk event3.
The most helpful thing in developing KRI thresholds is loss expectancy information. Loss expectancy information provides an estimate of the potential or expected impact of a risk event on the organization’s operations, reputation, or objectives. Loss expectancy information can help an organization to:
Quantify and prioritize the risks that pose the greatest threat to the organization
Determine the acceptable level of risk exposure or tolerance for each risk
Set the appropriate value or range for the KRI threshold that reflects the risk appetite and the risk mitigation strategy
Monitor and measure the performance and effectiveness of the risk management process and controls
Loss expectancy information can be derived from various sources, such as historical data, statistical analysis, expert judgment, or simulation models3.
The other options are not as helpful as loss expectancy information in developing KRI thresholds, because they do not directly address the potential or expected impact of a risk event.Control performance predictions, which are the forecasts or estimates of how well the risk management controls will perform in preventing, detecting, or mitigating risks, may help to evaluate the adequacy and efficiency of the risk management process and controls, but they do not provide a clear and quantifiable measure of the risk impact. IT service level agreements (SLAs), which are the contracts or agreements that define the quality and availability of IT services, may help to establish the standards and expectations for IT service delivery and performance, but they do not provide a comprehensive and current view of the risk exposure or likelihood. Remediation activity progress, which is the status or outcome of the actions taken to address and resolve a risk event, may help to monitor and report the effectiveness and compliance of the risk management process and controls, but it is usually done after the risk event has occurred and resolved, not before.
References = Key Risk Indicators: Definition, Examples, and Best Practices, KRI Framework for Operational Risk Management | Workiva, Loss Expectancy: Definition, Calculation, and Examples
An organization wants to transfer risk by purchasing cyber insurance. Which of the following would be MOST important for the risk practitioner to communicate to senior management for contract negotiation purposes?
Most recent IT audit report results
Replacement cost of IT assets
Current annualized loss expectancy report
Cyber insurance industry benchmarking report
The most important information for the risk practitioner to communicate to senior management for contract negotiation purposes when the organization wants to transfer risk by purchasing cyber insurance is the current annualized loss expectancy report, as it provides an estimate of the potential financial loss or impact that theorganization may incur due to a cyber risk event in a given year, and helps to determine the optimal coverage and premium of the cyber insurance. The other options are not the most important information, as they are more related to the audit, asset, or industry aspects of the cyber risk, respectively, rather than the financial aspect of the cyber risk. References = CRISC Review Manual, 7th Edition, page 111.
Which of the following is the BEST reason to use qualitative measures to express residual risk levels related to emerging threats?
Qualitative measures require less ongoing monitoring.
Qualitative measures are better aligned to regulatory requirements.
Qualitative measures are better able to incorporate expert judgment.
Qualitative measures are easier to update.
Qualitative measures are methods of expressing risk levels using descriptive terms, such as high, medium, or low, based on subjective criteria, such as likelihood, impact, or severity. Qualitative measures are often used to identify and prioritize risks, and to communicate risk information to stakeholders1.
Residual risk is the level of risk that remains after the risk response has been implemented. Residual risk reflects the effectiveness and efficiency of the risk response, and the need for further action or monitoring2.
Emerging threats are new or evolving sources or causes of risk that have the potential to adversely affect the organization’s objectives, assets, or operations. Emerging threats are oftencharacterized by uncertainty, complexity, and ambiguity, and may require innovative or adaptive risk responses3.
The best reason to use qualitative measures to express residual risk levels related to emerging threats is that qualitative measures are better able to incorporate expert judgment. Expert judgment is the opinion or advice of a person or a group of people who have specialized knowledge, skills, or experience in a particular domain or field. Expert judgment can help to:
Provide insights and perspectives on the nature and characteristics of the emerging threats, and their possible causes and consequences
Assess the likelihood and impact of the emerging threats, and their interactions and dependencies with other risks
Evaluate the suitability and effectiveness of the risk responses, and their alignment with the organization’s risk appetite and tolerance
Identify and recommend the best practices and lessons learned for managing the emerging threats, and for improving the risk management process45
Qualitative measures are better able to incorporate expert judgment than quantitative measures, which are methods of expressing risk levels using numerical or measurable values, such as percentages, probabilities, or monetary amounts. Quantitative measures are often used to estimate and analyze risks, and to support risk decision making1. However, quantitative measures may not be suitable or feasible for expressing residual risk levels related to emerging threats, because:
Quantitative measures require reliable and sufficient data and information, which may not be available or accessible for the emerging threats
Quantitative measures rely on mathematical models and techniques, which may not be able to capture or reflect the complexity and uncertainty of the emerging threats
Quantitative measures may create a false sense of precision or accuracy, which may not be justified or warranted for the emerging threats
Quantitative measures may be influenced or manipulated by biases or assumptions, which may not be valid or appropriate for the emerging threats67
Therefore, qualitative measures are better able to incorporate expert judgment, which can enhance the understanding and management of the residual risk levels related to emerging threats.
The other options are not the best reasons to use qualitative measures to express residual risk levels related to emerging threats, but rather some of the advantages or disadvantages of qualitative measures. Qualitative measures require less ongoing monitoring than quantitative measures, because they are simpler and easier to apply and update. However, this does not mean that qualitative measures can eliminate or reduce the need for monitoring, which is an essential part of the risk management process. Qualitative measures are better aligned to regulatory requirements than quantitative measures, because they are more consistent and comparable across different domains and contexts. However, this does not mean that qualitative measures can satisfy or comply with all the regulatory requirements, which may vary depending on theindustry or sector. Qualitative measures are easier to update than quantitative measures, because they do not depend on complex calculations or formulas. However, this does not mean that qualitative measures can always reflect the current or accurate risk levels, which may change over time or due to external factors. References =
Qualitative Risk Analysis vs. Quantitative Risk Analysis - ISACA
Residual Risk - ISACA
Emerging Threats - ISACA
Expert Judgment - ISACA
Expert Judgment in Project Management: Narrowing the Theory-Practice Gap
Quantitative Risk Analysis - ISACA
Quantitative Risk Analysis: A Critical Review
[CRISC Review Manual, 7th Edition]
Which of the following is MOST important to the effectiveness of key performance indicators (KPIs)?
Management approval
Annual review
Relevance
Automation
The most important factor to the effectiveness of key performance indicators (KPIs) is relevance. KPIs are metrics that measure the achievement of the objectives or the performance of the processes. Relevance means that the KPIs are aligned with and support the strategic goals and priorities of the organization, and that they reflect the current and desired state of the outcomes or outputs. Relevance also means that the KPIs are meaningful and useful for the decision makers and stakeholders, and that they provide clear and actionable information for improvement or optimization. The other options are not as important as relevance, as they arerelated to the approval, review, or automation of the KPIs, not the quality or value of the KPIs. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.2: Key Performance Indicators, page 183.
Which of the following is the BEST risk management approach for the strategic IT planning process?
Key performance indicators (KPIs) are established to track IT strategic initiatives.
The IT strategic plan is reviewed by the chief information security officer (CISO) and enterprise risk management (ERM).
The IT strategic plan is developed from the organization-wide risk management plan.
Risk scenarios associated with IT strategic initiatives are identified and assessed.
Identifying and assessing the risk scenarios associated with IT strategic initiatives is the best risk management approach for the strategic IT planning process, because it helps to understand and evaluate the potential or actual threats or opportunities that may affect the achievement or implementation of the IT strategic initiatives, and to determine the appropriate risk responses and controls. A risk scenario is a hypothetical situation or event that describes the source, cause, consequence, and impact of a risk. A risk scenario can be positive or negative, depending on whether it represents an opportunity or a threat. An IT strategic initiative is a project or program that supports or enables the IT strategy, which is a plan that defines how IT supports and aligns with the organization’s vision, mission, and strategy. The strategic IT planning process is a process of developing, implementing, and monitoring the IT strategy and its associated IT strategic initiatives. Identifying and assessing the risk scenarios is the best risk management approach, as it helps to anticipate and prepare for the potential or actual outcomes of the IT strategic initiatives, and to optimize the risk-reward balance and the value delivery of IT. Establishing key performance indicators (KPIs) to track IT strategic initiatives, reviewing the IT strategic plan by the chief information security officer (CISO) and enterprise risk management (ERM), and developing the IT strategic plan from the organization-wide risk management plan are all possible risk management approaches for the strategic IT planning process, but they are not the best approach, as they do not directly address the identification and assessment of the risk scenarios associated with IT strategic initiatives. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.1.1, page 37
Which of the following would be MOST helpful to a risk practitioner when preparing a summary of current IT risk for senior management review?
Changes in risk mitigation plans
Resolution status of audit findings
Areas of elevated risk
Industry risk management benchmarks
Senior management requireshigh-level, decision-relevantinformation. CRISC guidance states that the most valuable elements to communicate areareas of elevated risk, because these represent conditions that may exceed risk appetite or require immediate action. Changes in mitigation plans and audit findings are important operational details but do not provide a clear picture of current exposure. Industry benchmarks offer context but do not describe the organization’s actual risk posture. Highlighting elevated risks helps executives prioritize resources, make treatment decisions, and determine whether escalations are required.
Which of the following is the MOST important consideration when determining whether to accept residual risk after security controls have been implemented on a critical system?
Cost versus benefit of additional mitigating controls
Annualized loss expectancy (ALE) for the system
Frequency of business impact
Cost of the Information control system
Residual risk is the risk that remains after security controls have been implemented on a system. Residual risk can be accepted, transferred, avoided, or further mitigated. The most important consideration when deciding whether to accept residual risk is the cost versus benefit of additional mitigating controls. This means comparing the potential impact of the residual risk with the cost and effectiveness of implementing more controls to reduce it. If the cost of additional controls outweighs the benefit of reducing the residual risk, then it may be acceptableto accept the residual risk. However, if the benefit of additional controls exceeds the cost, then it may be advisable to implement more controls to lower the residual risk to an acceptable level. References = Risk and Information Systems Control Study Manual, Chapter 3: Risk Response and Mitigation, Section 3.4: Risk Response Selection, p. 156-157.
The PRIMARY reason to have risk owners assigned to entries in the risk register is to ensure:
risk is treated appropriately
mitigating actions are prioritized
risk entries are regularly updated
risk exposure is minimized.
The primary reason to have risk owners assigned to entries in the risk register is to ensure that risk is treated appropriately, as risk owners are responsible for implementing the risk response strategies and monitoring the risk status and outcomes. Risk owners are also accountable for the risk and its impact on the enterprise’s objectives and operations. Having risk owners assigned to entries in the risk register helps to clarify the roles and responsibilities, improve the communication and coordination, and enhance the effectiveness and efficiency of the risk management process. Mitigating actions are prioritized, risk entries are regularly updated, and risk exposure is minimized are not the primary reasons to have risk owners assigned to entries in the risk register, but rather the results or benefits of having risk owners assigned to entries in the risk register. References = CRISC by Isaca Actual Free Exam Q & As, question 206; CRISC: Certified in Risk & Information Systems Control Sample Questions, question 206.
Which of the following is the FIRST step in risk assessment?
Review risk governance
Asset identification
Identify risk factors
Inherent risk identification
The first step in risk assessment is asset identification, which is the process of identifying and documenting the assets that are relevant and valuable to the organization, such as people, information, systems, processes, or infrastructure1. Asset identification can help to:
Establish the scope and boundaries of the risk assessment, and ensure that all the assets within the scope are considered and covered2.
Determine the criticality and priority of the assets, and assign them appropriate values or ratings based on their importance and contribution to the organization’s objectives3.
Identify the potential threats and vulnerabilities that may affect the assets, and assess their likelihood and impact on the assets4.
The other options are not the first step in risk assessment, because:
Review risk governance is not the first step, but rather a prerequisite or a foundation for risk assessment. Risk governance is the system of principles, policies, roles, and responsibilities that guide and oversee the risk management activities and initiatives of the organization5. Reviewing risk governance can help to ensure that the risk assessment is aligned with the organization’sriskstrategy, culture, and appetite, and that the risk assessment process is consistent, effective, and efficient6.
Identify risk factors is not the first step, but rather a subsequent or a parallel step to asset identification. Risk factors are the elements or conditions that influence or contribute to the occurrence or outcome of a risk event7. Identifying risk factors can help to understand the causes and sources of the risks, and to analyze and evaluate the risks based on their probability and severity.
Inherent risk identification is not the first step, but rather a later or a dependent step on asset identification and risk factor identification. Inherent risk is the level of risk that exists before the implementation of risk responses. Identifying inherent risk can help to measure the exposure or uncertainty of the assets, and to determine the need and extent of the risk responses.
References =
Risk Governance - CIO Wiki
Risk Governance Framework - CIO Wiki
Asset Identification - CIO Wiki
Asset Identification and Valuation - ISACA
Asset Criticality - CIO Wiki
Threat and Vulnerability Assessment - CIO Wiki
Risk Factor - CIO Wiki
[Risk Factor Analysis - CIO Wiki]
[Inherent Risk - CIO Wiki]
[Inherent Risk Assessment - CIO Wiki]
[Risk Assessment - CIO Wiki]
Which of the following is the MOST important reason to communicate risk assessments to senior management?
To ensure actions can be taken to align assessment results to risk appetite
To ensure key risk indicator (KRI) thresholds can be adjusted for tolerance
To ensure awareness of risk and controls is shared with key decision makers
To ensure the maturity of the assessment program can be validated
Communicating risk assessments to senior management is crucial for ensuring that key decision-makers are aware of the organization ' s risk landscape. This awareness enables informed decision-making regarding risk responses, resource allocation, and strategic planning. It also fosters a risk-aware culture throughout the organization.
The PRIMARY reason to implement a formalized risk taxonomy is to:
reduce subjectivity in risk management.
comply with regulatory requirements.
demonstrate best industry practice.
improve visibility of overall risk exposure.
The primary reason to implement a formalized risk taxonomy is to reduce subjectivity in risk management, as it provides a common and consistent language and structure for identifying, classifying, and reporting risks, and facilitates the comparison and aggregation of risks across the organization. The other options are not the primary reasons, as they are more related to the outcomes, benefits, or drivers of risk management, respectively, rather than the reason for risk management. References = CRISC Review Manual, 7th Edition, page 100.
An organization ' s financial analysis department uses an in-house forecasting application for business projections. Who is responsible for defining access roles to protect the sensitive data within this application?
IT risk manager
IT system owner
Information security manager
Business owner
According to the Data Roles and Responsibilities article, the business owner is the person who has authority over the business process that is supported by the data. The business owner is responsible for defining the access roles to protect the sensitive data within the application, as well as approving the access requests and ensuring the compliance with the data policies andstandards. The business owner may delegate this responsibility to a data steward, who is a person who acts on behalf of the business owner to manage the data quality, security, and usage. Therefore, the answer is D. Business owner. References = Data Roles and Responsibilities
Which of the following is MOST important to determine when assessing the potential risk exposure of a loss event involving personal data?
The cost associated with incident response activitiesThe composition and number of records in the information asset
The maximum levels of applicable regulatory fines
The length of time between identification and containment of the incident
When assessing the potential risk exposure of a loss event involving personal data, the most important factor to determine is the composition and number of records in the information asset. The composition refers to the type and sensitivity of the personal data, such as name, address, phone number, email, social security number, health information, financial information, etc. The number of records refers to the quantity and scope of the personal data that is affected by the loss event. The composition and number of records in the information asset determine the severity and impact of the loss event, as they indicate the extent of the harm and damage that can be caused to the data subjects, the organization, and other stakeholders.The composition and number of records in the information asset also influence the cost of the incident responseactivities, the level of the regulatory fines, and the duration of the incident containment and recovery. References = CRISC Review Manual, 7th Edition, page 159.
Which of the following is the MOST important consideration when selecting either a qualitative or quantitative risk analysis?
Expertise in both methodologies
Maturity of the risk management program
Time available for risk analysis
Resources available for data analysis
The most important consideration when selecting either a qualitative or quantitative risk analysis is the time available for risk analysis, as this affects the level of detail and accuracy that can be achieved in the risk assessment process. Qualitative risk analysis is a method that uses subjective judgments and ratings to measure and prioritize the risks based on their likelihood and impact, as well as other factors such as urgency, velocity, and persistence. Qualitative risk analysis is usually faster and simpler than quantitative risk analysis, but it may also be less precise and consistent. Quantitative risk analysis is a method that uses numerical data and mathematicalmodels to measure and prioritize the risks based on theirprobability and magnitude, as well as other factors such as frequency, duration, and correlation. Quantitative risk analysis is usually more complex and time-consuming than qualitative risk analysis, but it may also provide more objective and reliable results. The other options are not the most important considerations when selecting either a qualitative or quantitative risk analysis, although they may have some influence or relevance. Expertise in both methodologies is desirable, but it does not determine the choice of the risk analysis method, as it depends on the availability and suitability of the experts for the specific risk context and objectives. Maturity of the risk management program is important, but it does not dictate the choice of the risk analysis method, as it depends on the level of integration and alignment of the risk management activities with the enterprise’s strategy and goals. Resources available for data analysis are relevant, but they do not decide the choice of the risk analysis method, as they depend on the quality and availability of the data sources and tools for the risk assessment process. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Assessment, page 81.ST
An organization has decided to postpone the assessment and treatment of several risk scenarios because stakeholders are unavailable. As a result of this decision, the risk associated with these new entries has been;
mitigated
deferred
accepted.
transferred
The result of postponing the assessment and treatment of several risk scenarios is that the risk associated with these new entries has been accepted. Risk acceptance is a risk response strategy that involves acknowledging the existence of a risk and deciding not to take any action to reduce its likelihood or impact. By postponing the assessment and treatment of the risk scenarios, the organization is implicitly accepting the risk and its consequences. Risk mitigation, deferral, and transfer are other possible risk response strategies, but they are not applicable in this case. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 9; CRISC Review Manual, 6th Edition, page 137.
An organization ' s Internet-facing server was successfully attacked because the server did not have the latest security patches. The risk associated with poor patch management had been documented in the risk register and accepted. Who should be accountable for any related losses to the organization?
Risk owner
IT risk manager
Server administrator
Risk practitioner
The risk owner is the person who should be accountable for any related losses to the organization, because they are the person who has the authority and responsibility to manage the risk and its associated controls.The risk owner is also the person who accepts the risk and its residual level, and who monitors and reports on the risk status and performance. The IT risk manager, the server administrator, and the risk practitioner are all involved in the riskmanagement process, but they are not the person who should be accountable for the risk and its outcomes, as they do not have the ultimate decision-making power and accountability for therisk. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.1.1, page 79
Which of the following provides the MOST insight regarding an organization ' s risk culture?
Awareness training participation rate
Risk assessment results
Senior management interviews
Risk management framework
Risk culture reflects how leadership and staff actually perceive, discuss, and act on risk. CRISC emphasizes tone at the top, decision-making behavior, openness to reporting issues, and integration of risk considerations into strategic choices as key indicators of culture.Senior management interviewsreveal these aspects directly—how leaders prioritize risk, how they respond to bad news, and whether risk considerations are embedded in planning and performance expectations. Training participation rates show awareness activity but not necessarily attitudes or behavior change. Risk assessment results are more about the organization’s risk profile than underlying culture. A documented risk management framework is a formal structure; it may be well designed but not actually lived. Interviews with senior leadership provide qualitative but rich insight into whether the framework and policies are truly influencing behavior.
Which organizational role should be accountable for ensuring information assets are appropriately classified?
Data protection officer
Chief information officer (CIO)
Information asset custodian
Information asset owner
The organizational role that should be accountable for ensuring information assets are appropriately classified is the information asset owner, as they have the authority and responsibility to define the classification, retention, and disposal requirements for the information assets they own, and to manage the risk and controls related to the information assets. The other options are not the correct roles, as they have different roles and responsibilities related to the protection, governance, or maintenance of the information assets, respectively, rather than the classification of the information assets. References = CRISC Review Manual, 7th Edition, page 154.
Which of the following is the MOST important course of action for a risk practitioner when reviewing the results of control performance monitoring?
Evaluate changes to the organization ' s risk profile.
Validate whether the controls effectively mitigate risk.
Confirm controls achieve regulatory compliance.
Analyze appropriateness of key performance indicators (KPIs).
The most important course of action for a risk practitioner when reviewing the results of control performance monitoring is to validate whether the controls effectively mitigate risk, as it involves verifying and testing the adequacy and performance of the controls, and identifying any control gaps or deficiencies that may affect the risk level and response. The other options are not the most important courses of action, as they are more related to the evaluation, confirmation, or analysis of the risk profile, compliance, or indicators, respectively, rather than the validation of the control effectiveness. References = CRISC Review Manual, 7th Edition, page 154.
A penetration testing team discovered an ineffectively designed access control. Who is responsible for ensuring the control design gap is remediated?
Control owner
Risk owner
IT security manager
Control operator
Role of the Control Owner:
The control owner is responsible for the design, implementation, and maintenance of a specific control.
They have detailed knowledge of the control’s purpose, its intended functionality, and its operational context within the organization.
Responsibility for Remediation:
When a penetration testing team discovers an ineffectively designed access control, it is the control owner’s responsibility to ensure the design gap is remediated.
The control owner must assess the findings, determine the root cause of the ineffectiveness, and take necessary actions to redesign or enhance the control to address the identified weaknesses.
Steps to Remediate Control Design Gap:
Assess the Findings:Understand the specific issues identified by the penetration testing team.
Redesign the Control:Modify the control design to address the identified gaps and ensure it meets security requirements.
Implement Changes:Apply the redesigned control and test its effectiveness.
Continuous Monitoring:Regularly review the control to ensure it remains effective over time.
Comparing Other Roles:
Risk Owner:Manages overall risk but does not directly handle control design.
IT Security Manager:Oversees the security posture but delegates specific control responsibilities to control owners.
Control Operator:Operates the control but is not responsible for its design or remediation.
References:
The CRISC Review Manual emphasizes the control owner ' s responsibility in maintaining and improving control effectiveness (CRISC Review Manual, Chapter 3: Risk Response and Mitigation, Section 3.7 Control Design and Selection).
During testing, a risk practitioner finds the IT department ' s recovery time objective (RTO) for a key system does not align with the enterprise ' s business continuity plan (BCP). Which of the following should be done NEXT?
Report the gap to senior management
Consult with the IT department to update the RTO
Complete a risk exception form.
Consult with the business owner to update the BCP
According to the CRISC Review Manual (Digital Version), the next course of action when a risk practitioner finds the IT department’s recovery time objective (RTO) for a key system does not align with the enterprise’s business continuity plan (BCP) is to consult with the IT department to update the RTO. The RTO is the maximum acceptable time that an application, computer, network, or system can be down after an unexpected disaster, failure, or comparable event takes place. The RTO should be aligned with the BCP, which is a set of policies, procedures, and resources that enable the organization to continue or resume its critical business functions in the event of a disruption. Consulting with the IT department to update the RTO helps to:
Ensure that the RTO reflects the current business requirements and expectations for the availability and recovery of the key system
Evaluate the feasibility and cost-effectiveness of achieving the RTO with the existing IT resources and capabilities
Identify and implement the necessary changes or improvements in the IT infrastructure, processes, and controls to meet the RTO
Test and validate the RTO and the IT recovery procedures and verify their compatibility and consistency with the BCP
Communicate and coordinate the RTO and the IT recovery plan with the relevant stakeholders, such as the business owner, the risk owner, and the senior management
References = CRISC Review Manual (Digital Version), Chapter 3: IT Risk Response, Section 3.3: Risk Response Options, pp. 174-1751
Which of the following is the GREATEST concern associated with the use of artificial intelligence (AI) language models?
The model could be hacked or exploited.
The model could be used to generate inaccurate content.
Staff could become overly reliant on the model.
It could lead to biased recommendations.
Biased recommendations from AI models can perpetuate or exacerbate organizational risks, especially in decision-making processes, regulatory compliance, and ethical standards. Addressing such concerns is vital under theEmerging Technology Risksdomain in risk management.
A risk practitioner notes control design changes when comparing risk response to a previously approved action plan. Which of the following is MOST important for the practitioner to confirm?
Appropriate approvals for the control changes
The reason the action plan was modified
The risk owner ' s approval of the revised action plan
The effectiveness of the resulting control
The MOST important aspect for the risk practitioner to confirm is:
A. Appropriate approvals for the control changes
Ensuring that the control design changes have the appropriate approvals is crucial. This confirms that the changes are recognized and sanctioned by the necessary authority within the organization, aligning with governance practices and maintaining the integrity of the risk management process.
Which of the following BEST facilitates the development of relevant risk scenarios?
Perform quantitative risk analysis of historical data.
Adopt an industry-recognized risk framework.
Use qualitative risk assessment methodologies.
Conduct brainstorming sessions with key stakeholders.
Brainstorming sessions with key stakeholders are the best way to facilitate the development of relevant risk scenarios, as they can generate diverse and creative ideas, perspectives, and insights about the potential risks and their impact on the organization’s objectives and operations. Brainstorming sessions can also foster collaboration, communication, and engagement among the stakeholders, and help to identify and prioritize the most significant and realistic risk scenarios. Brainstorming sessions can be guided by an industry-recognized risk framework, such as ISACA’s Risk IT, and supported by qualitative or quantitative risk assessment methodologies, but they are not sufficient by themselves to develop relevant risk scenarios.
An assessment of information security controls has identified ineffective controls. Which of the following should be the risk practitioner ' s FIRST course of action?
Determine whether the impact is outside the risk appetite.
Request a formal acceptance of risk from senior management.
Report the ineffective control for inclusion in the next audit report.
Deploy a compensating control to address the identified deficiencies.
The risk practitioner’s first course of action when an assessment of information security controls has identified ineffective controls should be A. Determine whether the impact is outside the risk appetite1
According to the CRISC Review Manual, risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Risk appetite reflects the organization’s risk culture, strategy, and values2
When an assessment of information security controls has identified ineffective controls, it means that the controls are not providing the expected level of protection or assurance for the information assets or processes. This may result in increased exposure or vulnerability to threats, or reduced ability to achieve objectives. Therefore, the risk practitioner should first determine whether the impact of the ineffective controls is outside the risk appetite, as this would indicate the need for urgent action or escalation3
The other options are not the first course of action when an assessment of information security controls has identified ineffective controls, because:
•B. Requesting a formal acceptance of risk from senior management may be appropriate if the impact of the ineffective controls is within the risk appetite, and the organization decides to accept the risk as it is. However, this should not be the first course of action, as it may not address the root cause of the ineffective controls, or the potential consequences or opportunities for improvement4
•C. Reporting the ineffective control for inclusion in the next audit report may be part of the risk communication and reporting process, but it should not be the first course of action, as it may delay the resolution or mitigation of the issue, or the implementation of corrective actions. Moreover, the next audit report may not be timely or relevant for the decision-makers or stakeholders who need to be informed of the ineffective controls5
•D. Deploying a compensating control to address the identified deficiencies may be a possible risk response option, but it should not be the first course of action, as it may require further analysis, evaluation, and approval. Moreover, deploying a compensating control may not be the most effective or efficient solution, as it may introduce additional complexity, cost, or risk.
1: CRISC Review Questions, Answers & Explanations Database, Question ID: 100003 2: CRISC Review Manual, 7th Edition, page 28 3: CRISC Review Manual, 7th Edition, page 223 4: CRISC Review Manual, 7th Edition, page 224 5: CRISC Review Manual, 7th Edition, page 225 : CRISC Review Manual, 7th Edition, page 226
During an acquisition, which of the following would provide the MOST useful input to the parent company ' s risk practitioner when developing risk scenarios for the post-acquisition phase?
Risk management framework adopted by each company
Risk registers of both companies
IT balanced scorecard of each company
Most recent internal audit findings from both companies
The most useful input to the parent company’s risk practitioner when developing risk scenarios for the post-acquisition phase is the risk registers of both companies. The risk register is a document that records the details of the risks, such as their sources, causes, consequences, likelihood, impact, and responses. By reviewing the risk registers of both companies, the risk practitioner can identify the existing and potential risks that may affect the post-acquisition integration, performance, and value. The risk management framework, the IT balancedscorecard, and the most recent internal audit findings are other possible inputs, but they are not as useful as the risk registers. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 11; CRISC Review Manual, 6th Edition, page 144.
Which of the following is the MOST important consideration when developing risk strategies?
Organization ' s industry sector
Long-term organizational goals
Concerns of the business process owners
History of risk events
Risk strategies are the plans and actions that an organization adopts to manage its risks and to achieve its objectives. Risk strategies should be aligned with the organization’s vision, mission, values, and culture, as well as its internal and external environment. The most important consideration when developing risk strategies is the long-term organizational goals, meaning that the risk strategies should support and enable the organization to pursue and attain its desired future state and outcomes. The long-term organizational goals should guide the risk identification, assessment, response, and monitoring processes, as well as the risk appetite and tolerance levels. The long-term organizational goals should also be communicated and cascaded throughout the organization to ensure the risk awareness and engagement of all stakeholders. References = Risk and Information Systems Control Study Manual, Chapter 1, Section 1.3.2, p. 27-28
Which of the following is MOST important when conducting a post-implementation review as part of the system development life cycle (SDLC)?
Verifying that project objectives are met
Identifying project cost overruns
Leveraging an independent review team
Reviewing the project initiation risk matrix
The most important activity when conducting a post-implementation review as part of the system development life cycle (SDLC) is to verify that the project objectives are met. The project objectives are the specific and measurable outcomes that the project aims to achieve. By verifying that the project objectives are met, the post-implementation review can evaluate the success and value of the project, and identify the lessons learned and best practices for future projects. Identifying project cost overruns, leveraging an independent review team, and reviewing the project initiation risk matrix are other possible activities, but they are not as important as verifying that the project objectives are met. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 4; CRISC Review Manual, 6th Edition, page 153.
Which of the following would BEST help to determine the inherent risk associated with a cloud service provider?
Cloud access security broker (CASB).
Cloud service configuration.
Cloud service attestation.
Cloud service level agreement (SLA).
The correct answer is D because inherent risk is assessed before considering additional controls. For a cloud service provider, the SLA helps define the nature of the service, expected availability, responsibilities, dependencies, and service commitments. These elements help determine the exposure created by using the provider. The uploaded CRISC notes support this by stating that the greatest risk when engaging a cloud provider is an ambiguous SLA and that SLAs address threats such as financial losses from service interruption.
A CASB is a security tool/control used to track cloud use, reveal noncompliance, and help secure data, so it is more relevant to monitoring or mitigation than determining inherent risk. ISACA describes CASBs as tools for tracking authorized/unauthorized cloud application use, revealing possible regulatory noncompliance, and helping secure cloud data.
C, cloud service attestation, is useful for assurance over the provider’s control environment, but that relates more to control assurance/current or residual risk than inherent risk. ISACA notes that third-party risk management may involve evidence such as SOC reports, ISO 27001, and other attestation reports, but these are used as evidence of controls and compliance.
===========
Which of the following risk impacts should be the PRIMARY consideration for determining recovery priorities in a disaster recovery situation?
Data security
Recovery costs
Business disruption
Recovery resource availability
The primary consideration for determining recovery priorities in a disaster recovery situation is the impact of business disruption on the organization’s mission, objectives, and stakeholders. Business disruption can result in loss of revenue, reputation, customer satisfaction, market share, and competitive advantage. Therefore, the recovery priorities should be based on the criticality of the business processes and functions that support the organization’s value proposition and strategic goals. Data security (A), recovery costs (B), and recovery resource availability (D) are important factors, but they are secondary to the impact of business disruption. Data security should be ensured throughout the recovery process, but it does not determine the recovery order. Recovery costs should be balanced with the benefits of restoring the business operations, but they do not reflect the urgency of the recovery. Recovery resource availability should be assessed and allocated according to the recovery priorities, but it does not define the recovery sequence. (Risk and Information Systems Control Review Questions, Answers & Explanations Manual, 5th Edition, page 982)
A failure in an organization s IT system build process has resulted in several computers on the network missing the corporate endpoint detection and response (EDR) software. Which of the following should be the risk practitioner’s IMMEDIATE concern?
Multiple corporate build images exist.
The process documentation was not updated.
The IT build process was not followed.
Threats are not being detected.
Which of the following is the BEST control to minimize the risk associated with scope creep in software development?
An established process for project change management
Retention of test data and results for review purposes
Business managements review of functional requirements
Segregation between development, test, and production
The best control to minimize the risk associated with scope creep in software development is an established process for project change management. Scope creep is the uncontrolled expansion of the project scope due to changes in requirements, specifications, or expectations. A project change management process can help to prevent or reduce scope creep by defining the procedures for requesting, reviewing, approving, and implementing changes in the project. Retention of test data and results, business management review of functional requirements, and segregation between development, test, and production are other possible controls, but they are not as effective as a project change management process. References = ISACA Certified in Riskand Information Systems Control (CRISC) Certification Exam Question and Answers, question 11; CRISC Review Manual, 6th Edition, page 144.
Which of the following is the MAIN benefit to an organization using key risk indicators (KRIs)?
KRIs provide an early warning that a risk threshold is about to be reached.
KRIs signal that a change in the control environment has occurred.
KRIs provide a basis to set the risk appetite for an organization.
KRIs assist in the preparation of the organization ' s risk profile.
The main benefit of using key risk indicators (KRIs) for an organization is that they provide an early warning that a risk threshold is about to be reached. KRIs are metrics that measure the likelihood and impact of risks, and help monitor and prioritize the most critical risks. KRIs also help to trigger timely and appropriate risk responses, before the risk becomes unmanageable orunacceptable. The other options are not the main benefit of using KRIs, although they may be secondary benefits or outcomes. KRIs signal that a change in the control environment has occurred, provide a basis to set the risk appetite for an organization, and assist in the preparation of the organization’s risk profile. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.4.1, page 4-36.
Which of the following will BEST ensure that information security risk factors are mitigated when developing in-house applications?
Identify information security controls in the requirements analysis
Identify key risk indicators (KRIs) as process output.
Design key performance indicators (KPIs) for security in system specifications.
Include information security control specifications in business cases.
Information security risk factors are the sources of uncertainty that may affect the confidentiality, integrity, or availability of information assets within an organization. Information security risk factors can include threats, vulnerabilities, or impacts that may compromise the security of information assets. Information security risk factors should be mitigated when developing in-house applications, which are software applications that are designed, developed, and maintained by the organization itself, rather than by external vendors or providers. Mitigating information security risk factors when developing in-house applications canhelp prevent or reduce the occurrence or consequences of security incidents, such as data breaches, cyberattacks, unauthorized access, or data loss. The best way to ensure that information security risk factors are mitigated when developing in-house applications is to identify information security controls in the requirements analysis. The requirements analysis is the stage of the system development life cycle (SDLC) where the business needs and expectations of the application are defined and documented. The requirements analysis should include the functional and non-functional requirements of the application, such as the features, functions, performance, quality, reliability, and security of the application. Identifying information security controls in the requirements analysis can help ensure that the security requirements of the application are clearly specified and agreed upon by the stakeholders, and that they are aligned with the organization’s security policies, standards, and regulations. Identifying information security controls in the requirements analysis can also help ensure that the security requirements are integrated into the design, development, testing, and deployment of the application, and that they are verified and validated throughout the SDLC. Identifying information security controls in the requirements analysis can also help ensure that the security requirements are traceable, measurable, and manageable, and that they can be monitored and reviewed for effectiveness and efficiency. References = THE SYSTEM DEVELOPMENT LIFE CYCLE (SDLC), p. 2-3, System Development Life Cycle - GeeksforGeeks, 7.3: Systems Development Life Cycle - Engineering LibreTexts, What Is SDLC? 7 Phases of System Development Life Cycle - Intetics.
An organization has procured a managed hosting service and just discovered the location is likely to be flooded every 20 years. Of the following, who should be notified of this new information FIRST.
The risk owner who also owns the business service enabled by this infrastructure
The data center manager who is also employed under the managed hosting services contract
The site manager who is required to provide annual risk assessments under the contract
The chief information officer (CIO) who is responsible for the hosted services
The risk owner is the person who has the authority and accountability to manage a specific risk and its associated controls. The risk owner is also responsible for ensuring that the risk is within the acceptable level and that the risk response is effective and efficient. In this case, the risk owner is also the owner of the business service that depends on the managed hosting service. Therefore, the risk owner should be notified of the new information about the flood risk first, as they have the most interest and influence on the risk and its impact on the business objectives. The risk owner can then decide on the appropriate actions to take, such as reviewing the contract terms, requesting additional controls, or changing the service provider. The other options are not the correct answers because they are not the primary stakeholders of the risk and its consequences. The data center manager is an employee of the managed hosting service provider, not the organization that procured the service. The data center manager may not have the authority or the incentive to address the flood risk or inform the organization. The site manager is also an employee of the managed hosting service provider, and their role is to conduct annual risk assessments under the contract. The site manager may not be aware of the new information or have the responsibility to communicate it to the organization. The CIO is the senior executive who oversees the IT strategy and operations of the organization. The CIO may have a general interest in the managed hosting service and its risks, but they are not the direct owner or managerof the specific risk or the business service that relies on the service. References = CRISC Review Manual, pages 32-331; CRISC Review Questions, Answers & Explanations Manual, page 702
Controls should be defined during the design phase of system development because:
it is more cost-effective to determine controls in the early design phase.
structured analysis techniques exclude identification of controls.
structured programming techniques require that controls be designed before coding begins.
technical specifications are defined during this phase.
Controls are the mechanisms or procedures that ensure the security, reliability, and quality of an IT system or process. Controls can be preventive, detective, or corrective, and can be implemented at various levels, such as physical, logical, administrative, or technical. Controls should be defined during the design phase of system development because it is more cost-effective to determine controls in the early design phase. The design phase is the stage where the system requirements are translated into a detailed technical plan, which includes the system architecture, database structure, user interface, and system components. The design phase also defines the system objectives, goals, and performance criteria. Defining controls during the design phase can help ensure that the controls are aligned with the system requirements and objectives, and that they are integrated into the system design from the start. Defining controls during the design phase can also help avoid or reduce the costs and risks associated with implementing controls later in the development or operation phases, such as rework, delays, errors, failures, or breaches. References = THE SYSTEM DEVELOPMENT LIFE CYCLE (SDLC), p. 2-3, System Development LifeCycle - GeeksforGeeks, 7.3: Systems Development Life Cycle - Engineering LibreTexts, What Is SDLC? 7 Phases of System Development Life Cycle - Intetics.
A new risk practitioner finds that decisions for implementing risk response plans are not being made. Which of the following would MOST likely explain this situation?
Risk ownership is not being assigned properly.
The organization has a high level of risk appetite.
Risk management procedures are outdated.
The organization ' s risk awareness program is ineffective.
Which of the following is the BEST method to mitigate the risk of an unauthorized employee viewing confidential data in a database ' '
Implement role-based access control
Implement a data masking process
Include sanctions in nondisclosure agreements (NDAs)
Install a data loss prevention (DLP) tool
Implementing a data masking process is the best method to mitigate the risk of an unauthorized employee viewing confidential data in a database. Data masking is the process of replacing sensitive data with fictitious but realistic data, such as changing names, addresses, phone numbers, etc. Data masking protects the privacy and confidentiality of the data, while still allowing for testing, analysis, or training purposes. Implementing role-based access control, including sanctions in NDAs, and installing a DLP tool are also useful methods to reduce the risk of data exposure, but they are not as effective as data masking, which prevents the data from being accessed in the first place. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.1, page 3-21.
Which of the following BEST informs decision-makers about the value of a notice and consent control for the collection of personal information?
A comparison of the costs of notice and consent control options
Examples of regulatory fines incurred by industry peers for noncompliance
A report of critical controls showing the importance of notice and consent
A cost-benefit analysis of the control versus probable legal action
A cost-benefit analysis of the control versus probable legal action is the best way to inform decision-makers about the value of a notice and consent control for the collection of personal information, as it quantifies the potential benefits and costs of implementing the control and compares them with the potential consequences of not implementing the control. This helps the decision-makers to evaluate the trade-offs and the return on investment of the control.
A comparison of the costs of notice and consent control options is not sufficient to inform decision-makers about the value of the control, as it does not consider the benefits or the risks of the control.
Examples of regulatory fines incurred by industry peers for noncompliance are not the best way to inform decision-makers about the value of the control, as they are based on historical data and may not reflect the current or future situation of the enterprise.
A report of critical controls showing the importance of notice and consent is not the best way to inform decision-makers about the value of the control, as it does not provide any quantitative or comparative data to support the decision. References = CRISC Review Manual, 7th Edition, ISACA, 2020, page 140-1411
Which of the following resources is MOST helpful when creating a manageable set of IT risk scenarios?
Results of current and past risk assessments
Organizational strategy and objectives
Lessons learned from materialized risk scenarios
Internal and external audit findings
According to the CRISC Review Manual1, lessons learned from materialized risk scenarios are the insights and knowledge gained from analyzing the causes, impacts, and responses of actual risk events that occurred in the past. Lessons learned from materialized risk scenarios are the most helpful resource when creating a manageable set of IT risk scenarios, as they help to identify and prioritize the most relevant and realistic risks that could affect the organization’s objectives, processes, and resources. Lessons learned from materialized risk scenarios also helpto improve the risk management practices and capabilities, and to avoid repeating the same mistakes or gaps in the future. References = CRISC Review Manual1, page 206.
Which of the following is MOST helpful when prioritizing action plans for identified risk?
Comparing risk rating against appetite
Obtaining input from business units
Determining cost of controls to mitigate risk
Ranking the risk based on likelihood of occurrence
Comparing risk rating against appetite is the most helpful criterion when prioritizing action plans for identified risk, as it helps to determine the urgency and importance of addressing the risk. Risk rating is the level of risk after considering the likelihood and impact of a risk event, and risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. By comparing risk rating against appetite, an organization can identify which risks are above, within, or below its tolerance level, and prioritize the action plans accordingly. Risks that are above the appetite level should be treated with the highest priority, as they pose asignificant threat to the organization’s objectives and performance. Risks that are within the appetite level should be monitored and controlled regularly, as they are acceptable but still require attention. Risks that are below the appetite level should be reviewed periodically, as they are negligible or insignificant.
Which of the following BEST enables the selection of appropriate risk treatment in the event of a disaster?
Business impact analysis (BIA)
Risk scenario analysis
Failover procedures
Risk treatment plan
Thebusiness impact analysis (BIA)identifies critical services, acceptable downtime limits, and the business consequences of disruptions. CRISC emphasizes that the BIA is the foundation for deciding risk treatment strategies because it defines what must be restored first and to what level. Scenario analysis identifies risks but does not determine business priorities. Failover procedures are themselves a treatment, not a method for selecting treatments. A risk treatment plan documents chosen actions but depends entirely on the BIA to inform those decisions. Therefore, the BIA is the key input enabling proper treatment selection during disasters.
TESTED 17 Oct 2026
Copyright © 2014-2026 DumpsTool. All Rights Reserved