Weekend Sale - Special 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 75onlydt

Cilium-Associate Questions and Answers

Question # 6

Which statement about Cilium's identity-based security model is correct?

A.

An endpoint identity Is identified by labels and is tied to a single namespace.

B.

Security is based on the identity of a pod, which is derived through labels.

C.

By using an IP-address security model, identities can be shared between pods.

D.

Cilium enforces security based on IP addresses as it provides better scalability and flexibility.

Full Access
Question # 7

Which statement is true of both the Ingress Controller and Gateway API?

A.

It provides portable Layer 7 north-south routing logic for Kubernetes workloads.

B.

Its routing logic can be restricted to a single namespace.

C.

It is role-oriented, with some resources for administrators and others for users.

D.

Its features are commonly extended by using resource annotations.

Full Access
Question # 8

If you are required to block ingress traffic from external IPs for all pods in your cluster, which of the following network policies would be the best fit?

A.

CiliumNetworkPolicy

B.

CiliumGlobalPolicy

C.

NetworkPolicy

D.

CiliumClusterWideNetworkPolicy

Full Access
Question # 9

Which command is used to enable logging at the debug log level of Cilium agents7

A.

cilium log level --set=debug

B.

cilium logging.level=debug

C.

cilium config set debug true

D.

cilium logging debug

Full Access
Question # 10

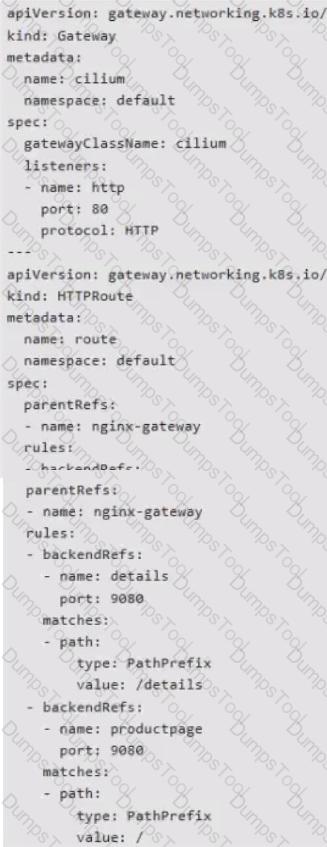
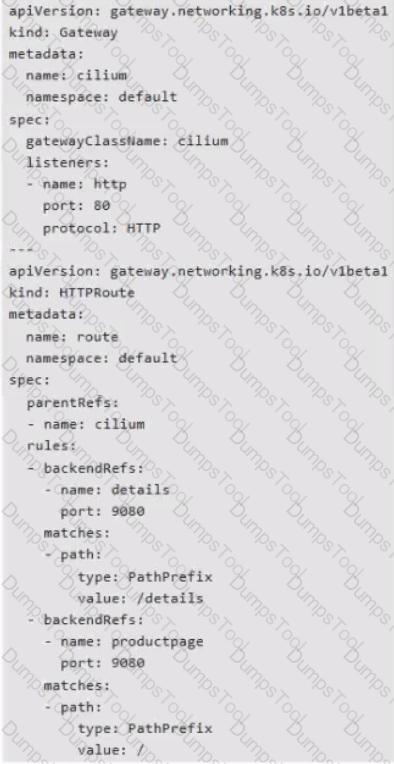
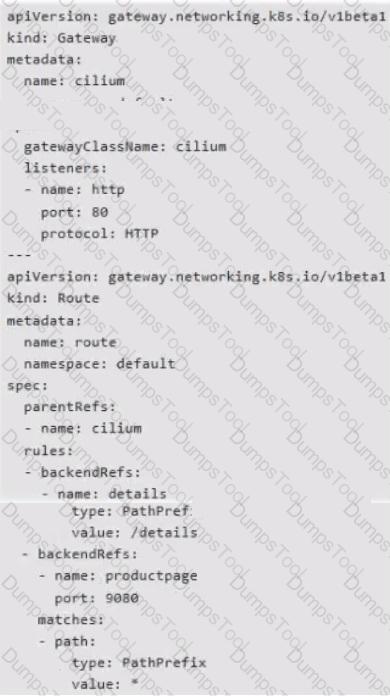
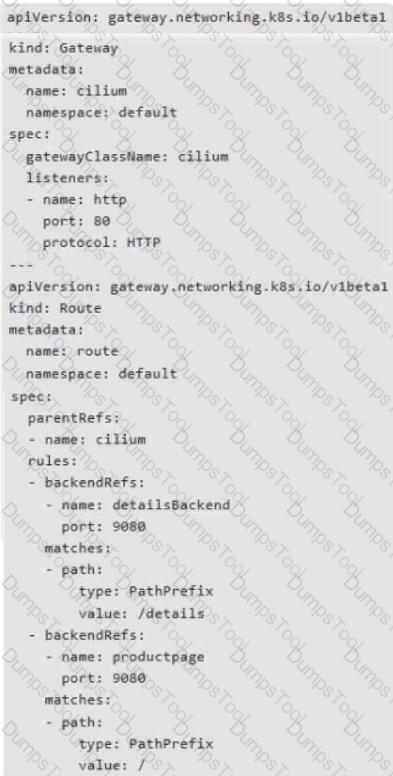
This an Ingress configuration. What is the equivalent Gateway API configuration?
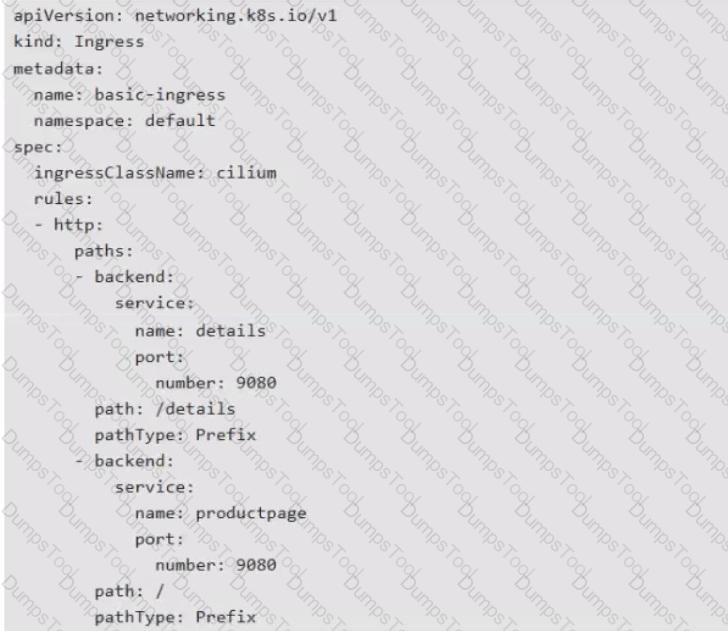
Question # 10

Question 19 source Ingress

A)

Question # 10

Question 19 option A

B)

Question # 10

Question 19 option B

C)

Question # 10

Question 19 option C

D)

Question # 10

Question 19 option D

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Full Access
Question # 11

What is the default policy enforcement behavior?

A.

If any rule selects an Endpoint and the rule has an ingress section, the Endpoint goes Into default deny at egress. f any rule selects an Endpoint and the rule has an egress section, the Endpoint goes into default deny at ingress.

B.

If any rule selects an Endpoint and the rule has an ingress section, the Endpoint goes Into default allow at egress, f any rule selects an Endpoint and the rule has an egress section, the Endpoint goes into default allow at ingress.

C.

If any rule selects an Endpoint and the rule has an ingress section, the Endpoint goes Into default allow at Ingress, f any rule selects an Endpoint and the rule has an egress section, the Endpoint goes into default allow at egress.

D.

If any rule selects an Endpoint and the rule has an ingress section, the Endpoint goes into default deny at ingress. f any rule selects an Endpoint and the rule has an egress section, the Endpoint goes into default deny at egress.

Full Access
Question # 12

The application team would like to observe egress traffic with application level information for workloads running in a Cilium based Kubernetes Cluster Which features would offer this without the need for additional tooling?

A.

Cilium Load Balancing

B.

Fluentd and Grafana

C.

Kubernetes Network Policies

D.

Hubble Ul and CLI

Full Access
Question # 13

What is the purpose of the 12 Announcements" feature?

A.

To support Layer 2 multicast traffic within Kubernetes.

B.

To make services visible and reachable on the local area network.

C.

To provide DNS-based service discovery within the cluster.

D.

To enforce Layer 2-based network security policies.

Full Access
Question # 14

Which proxy does Cilium use to enforce HTTP and other Layer 7 (L7) policies specified in network policies for the cluster?

A.

HAProxy

B.

Squid

C.

Linkerd2-proxy

D.

Envoy

Full Access
Question # 15

Which one of the following statements accurately describes the identity-based network security model used by Cilium?

A.

Security is based on the identity of a pod, which Is derived through its IP address. This identity cannot be shared between pods.

B.

Security is based on the identity of a pod, which is derived through annotations. This Identity can be shared between pods.

C.

Security is based on the identity of a pod, which is derived through labels. This identity can be shared between pods.

D.

Security is based on the identity of a pod. The security ID is manually set by the operator and cannot be shared between pods.

Full Access
Question # 16

You are tasked to install Cilium and enable transparent encryption in a cluster in which the following conditions applies:

� Internal cluster traffic is IPv6-only

� The current cluster is running on 5001 nodes

� The cluster is planned to connect to another cluster which has 5001 nodes through Cluster Mesh

What are your recommendations regarding transparent encryption?

A.

Enable the wireguard transparent encryption.

B.

Enable the IPSec transparent encryption.

C.

Clusters have too many nodes for transparent encryption.

D.

Transparent encryption requires an IPv4-only network.

Full Access
Question # 17

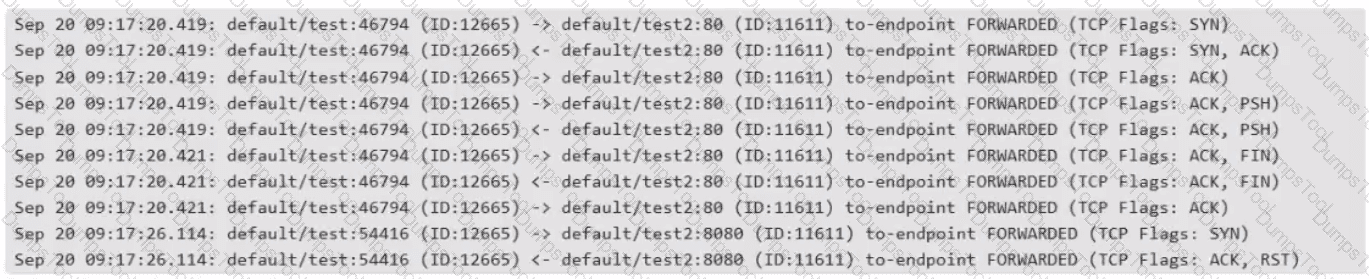
We observed Hubble output:

Question # 17

Question 7 Hubble flow exhibit

Explain what may have happened:

A.

On test pod (default namespace), someone launched commands:

curl 19.244.0.191 #Output: Failed

curl 16.244.0.191:8680 #Output: Succeeded

B.

On test2 pod (default namespace), someone launched commands:

curl 16.244.0.143 #Output: Failed curl 10.244.0.143:8080 #Output: Succeeded

C.

On test2 pod (default namespace), someone launched commands:

curl 10.244.0.143 #Output: Succeeded curl 10.244.0.143:8080 #Output: Failed

D.

On test pod (default namespace), someone launched commands: curl 16.244.0.191 #Output: Succeeded curl ie.244.0.191:8080 #Output: Failed

Full Access
Question # 18

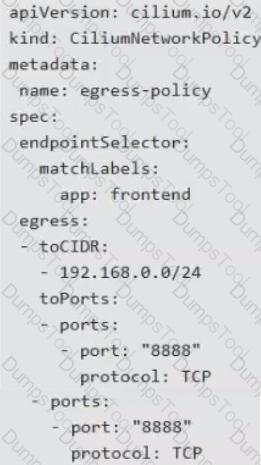
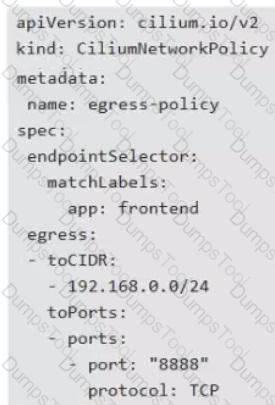
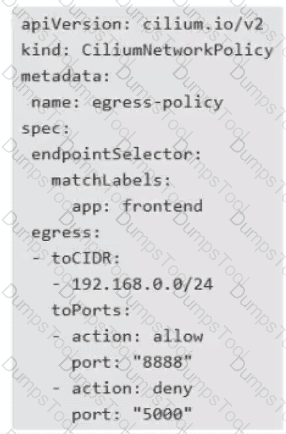
You are creating a Cilium network policy for pods with the label app: frontend . The policy should allow all pods with that label to communicate with destinations inside 192.168.e.e/24 and using TCP on port 8888.

For example:

� Traffic to 192.168.9.23:8888 should be allowed

� Traffic to 192.168.10.5:8888 should be denied.

� Traffic to 192.168.9.12:5606 should be denied.

Which of the following policies is correct?

A)
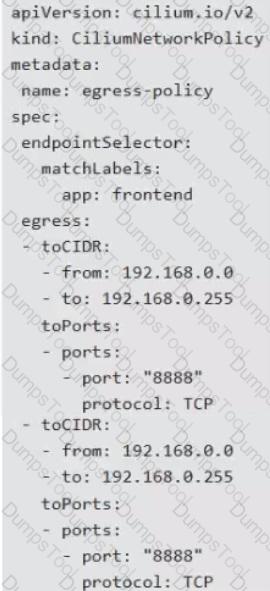
Question # 18

Option A

B)

Question # 18

Option B

C)

Question # 18

Option C

D)

Question # 18

Option D

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Full Access