dumpstool logo

A client connected to an AOS-CX switch has been assigned Role1. Role1 has the following port-access classes and policy associated with it:
```text
class ip class1
10 match tcp any any eq 22
20 ignore tcp any 10.10.4.0/23 eq 443
30 match ip any 10.10.4.0/23
class ip class2
10 match any any eq 67
20 match ip any 10.10.4.0/22
port-access policy policy1
10 class ip class1 action drop
20 class ip class2
```
The client sends two packets:
1: HTTPS to 10.10.5.5
2: DNS to 10.10.6.6
What occurs?
An HPE Aruba Networking Mobility Controller is configured with the following commands:
`aaa rfc-3576-server 10.1.2.3 key mysecretkey & ^%!7531 replay-protection window-duration 300`
Later, this output is displayed:
`(host)#show aaa rfc-3576-server statistics`
`RADIUS RFC 3576 Statistics - 10.1.2.3`
`Disconnect Requests: 2534 | Disconnect Accepts: 2534 | Disconnect Rejects: 0`
`No Secret: 0 | No Session ID: 0 | Bad Authenticator: 0 | Invalid Request: 0`
`Packets Dropped: 1431 | Unknown service: 0`
`CoA Requests: 2453 | CoA Accepts: 1022 | CoA Rejects: 0 | No permission: 0`
What should be investigated?
Refer to the exhibit.
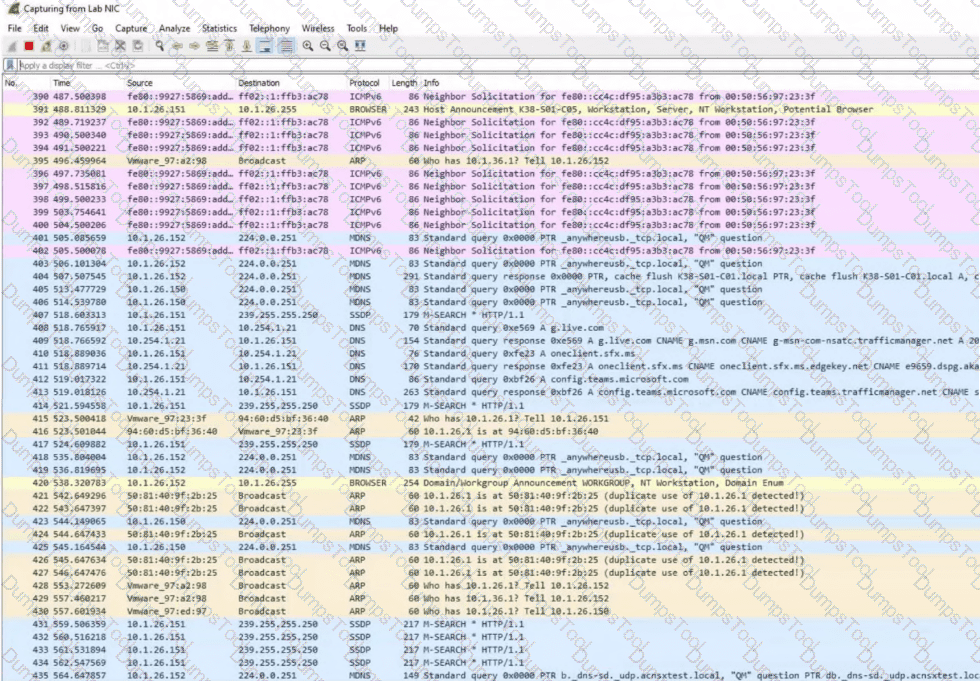
Frame 421: 50:81:40:9f:2b:25 - > Broadcast ARP 60 10.1.26.1 is at 50:81:40:9f:2b:25 (duplicate use of 10.1.26.1 detected!)
Frame 422: 50:81:40:9f:2b:25 - > Broadcast ARP 60 10.1.26.1 is at 50:81:40:9f:2b:25 (duplicate use of 10.1.26.1 detected!)
Frame 424: 50:81:40:9f:2b:25 - > Broadcast ARP 60 10.1.26.1 is at 50:81:40:9f:2b:25 (duplicate use of 10.1.26.1 detected!)
Which device should be documented as potentially malicious and requiring further investigation?
A customer has an AOS-10 architecture that includes HPE Aruba Networking APs. The customer recently enabled WIDS at the high level on the APs. Administrators see several "ad hoc using valid SSID" events.
What should you explain?
A company wants its AOS-CX switches to obtain certificates from ClearPass Onboard and use those certificates to implement RadSec with ClearPass Policy Manager (CPPM).
ClearPass Onboard has a CA with EST enabled and this EST URL: `[https://cp1.acnsxtest.com/.well-known/est/ca:2](https://cp1.acnsxtest.com/.well-known/est/ca:2)`
ClearPass Guest has an account whose username is `switchcorp123`. (Assume CPPM also has a valid service to authenticate users who access the EST application.)
CPPM has a network-device account for the switches with RadSec enabled. The RadSec settings validate by CN or SAN using this regex: `switchcorp123`
ClearPass has these certificates:
* HTTPS certificate signed by DigiCert
* RadSec certificate signed by DigiCert
* RADIUS/EAP certificate signed by MyDomainCA
This configuration is on the AOS-CX switches:
```text
crypto pki est-profile est1
url https://clearpass1.acnsxtest.com/.well-known/est/ca:2
username switchcorp123
password plaintext %FY212h & zaTk
vrf default
exit
crypto pki certificate cert1
subject switchcorp123
enroll est-profile onboard
crypto pki application radsec-client certificate cert1
```
The switches’ TA-profile list includes DigiCert.
Assume you have obtained the correct password associated with the indicated username. What error or errors are present?
Refer to the exhibit.
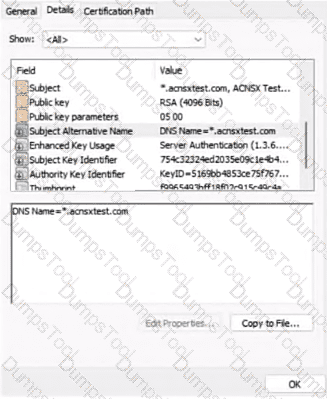
Field: Subject
Value: .acnsxtest.com, ACNSX Test...
Field: Subject Alternative Name
Value: DNS Name=.acnsxtest.com
Field: Enhanced Key Usage
Value: Server Authentication (1.3.6.1.5.5.7.3.1)
You have received this certificate to install on an HPE Aruba Networking ClearPass server for RADIUS/EAP and RadSec use. What is one issue?
You are helping a developer create a custom NAE script for an AOS-CX switch. What information might you need to provide so the developer can define the parameters correctly?
A customer uses an AOS-10 architecture managed by HPE Aruba Networking Central. HPE Aruba Networking infrastructure devices authenticate clients to an HPE Aruba Networking ClearPass cluster.
In HPE Aruba Networking Central, you are reviewing network traffic flows for a wireless IoT device categorized as "Raspberry Pi" clients. You observe SSH traffic. You then examine several additional wireless IoT clients and find that they are also sending SSH.
Refer to the scenario.
You need a fast way to find a list of all IoT clients that have used SSH.
What step can you take?
How does HPE Aruba Networking Central secure site-to-site connections between AOS-10 gateways?
A customer operates an HPE Aruba Networking ClearPass cluster. The customer has AOS-CX switches that use 802.1X authentication with HPE Aruba Networking ClearPass Policy Manager (CPPM).
The switches use local port-access policies. The customer wants to begin tunneling wired clients that pass only user authentication to an HPE Aruba Networking gateway cluster. The gateway cluster must assign these clients the eth-internet role. The gateway must also assign the clients to VLAN 20.
The intended enforcement policy and profiles are shown below:
* Policy: `written-exam-3`
* Profile: `written-exam-b`
The gateway cluster contains two gateways with the following IP addresses:
Gateway 1: VLAN 4085 (system IP) = 10.20.4.21 | VLAN 20 (users) = 10.20.20.1 | VLAN 4094 (WAN) = 198.51.100.14
Gateway 2: VLAN 4085 (system IP) = 10.20.4.22 | VLAN 20 (users) = 10.20.20.2 | VLAN 4094 (WAN) = 198.51.100.12 | VRRP on VLAN 20 = 10.20.20.254
The customer needs high availability for tunnels between the switches and the gateway cluster. If one gateway fails, the other gateway must take over its tunnels. The switch must also be able to discover the gateway cluster even if one gateway in the cluster is unavailable.
Refer to the scenario. Assume that `myzone` is the name used for the UBT zone.
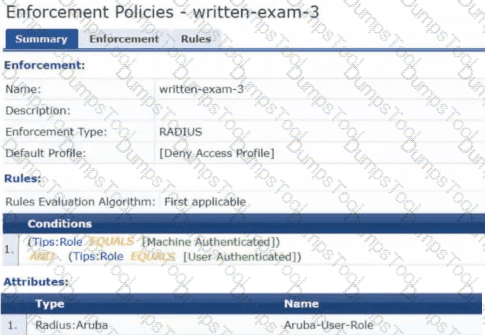
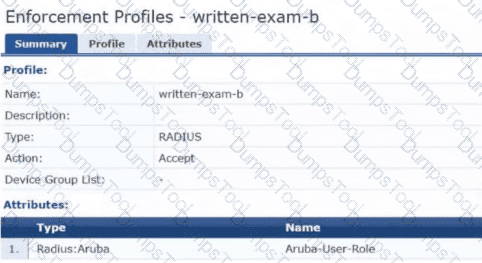
Which option is a valid minimal configuration for the AOS-CX port-access roles?
An organization wants an AOS-CX switch to trigger an alert when its RADIUS server (cp.acnsxtest.local) rejects an unusual number of client authentication requests each hour. After discussions with other HPE Aruba Networking administrators, you still do not know how many rejections are normal or unusual. You expect the value might differ on every switch.
You are helping the developer understand how to create an NAE script for this use case.
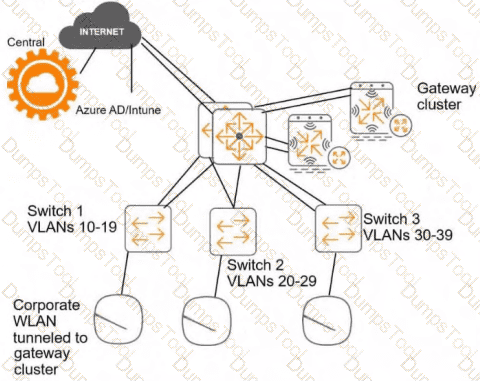
Refer to the scenario.
The developer explains that they intend to define the rule with logic like this: `monitor > value`
However, the developer asks what value to include.
What should you recommend?
A financial institution must authenticate managers of HPE Aruba Networking Mobility Controllers (MCs) and HPE Aruba Networking Mobility Conductors through ClearPass Policy Manager (CPPM). The institution’s security policies require strong encryption for manager-authentication communications between the HPE Aruba Networking devices and CPPM.
What is a valid solution?
You want to use HPE Aruba Networking ClearPass Device Insight tags as conditions in CPPM role-mapping or enforcement-policy rules.
Which guidelines should you follow?
Introduction to the customer
You are assisting a company with adding HPE Aruba Networking ClearPass to its network, which uses HPE Aruba Networking infrastructure devices.
The company already has a Windows domain and Windows CA. The Windows CA issues certificates to domain computers, domain users, and servers such as domain controllers.
ClearPass cluster IP addressing and hostnames
A customer's ClearPass cluster uses these IP addresses:
Publisher = 10.47.47.5
Subscriber 1 = 10.47.47.6
Subscriber 2 = 10.47.47.7
Virtual IP with Subscriber 1 and Subscriber 2 = 10.47.47.8
The customer's DNS server contains these entries:
cp.acnsxtest.com = 10.47.47.5
cps1.acnsxtest.com = 10.47.47.6
cps2.acnsxtest.com = 10.47.47.7
radius.acnsxtest.com = 10.47.47.8
onboard.acnsxtest.com = 10.47.47.8
Refer to the scenario.
The Onboard CA uses the settings shown in the exhibits below.
* CA Name: Onboard CA, CA ID: 2
* Common Name: ClearPass Intune Certificate Authority
Microsoft Entra ID (Azure AD) administrators need assistance configuring the app registration for integration with ClearPass Onboard.
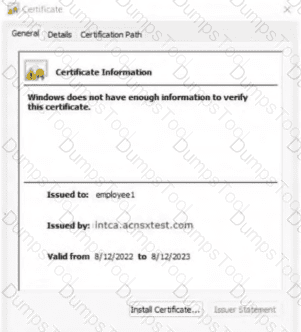
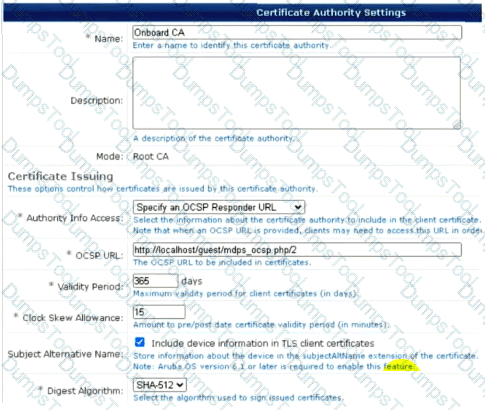
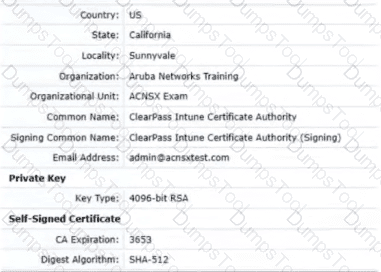
Which URL should you tell them to use?
A company uses an HPE Aruba Networking EdgeConnect SD-Branch solution. The customer wants to integrate the solution with HPE Aruba Networking SSE.
What is one step that must be completed in HPE Aruba Networking SSE and is not automated as part of the typical setup?
Introduction to the customer
You are assisting a company with adding HPE Aruba Networking ClearPass to its network, which uses HPE Aruba Networking network-infrastructure devices.
The company already has a Windows domain and Windows CA. The Windows CA issues certificates to domain computers, domain users, and servers such as domain controllers.
ClearPass cluster IP addressing and hostnames
Publisher = 10.47.47.5
Subscriber 1 = 10.47.47.6
Subscriber 2 = 10.47.47.7
Virtual IP with Subscriber 1 and Subscriber 2 = 10.47.47.8
Refer to the scenario.
You created a role-mapping policy as displayed in the exhibits below.
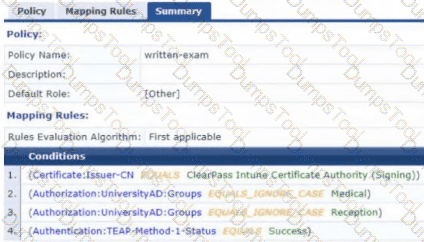
Policy Name: written-exam
Rules Evaluation Algorithm: First applicable
Conditions:
1. (Certificate:Issuer-CN EQUALS ClearPass Intune Certificate Authority (Signing))
2. (Authorization:UniversityAD:Groups EQUALS_IGNORE_CASE Medical)
3. (Authorization:UniversityAD:Groups EQUALS_IGNORE_CASE Reception)
4. (Authentication:TEAP-Method-1-Status EQUALS Success)
What one change must you make to this policy?
A hospital has an AOS-10 architecture managed by HPE Aruba Networking Central. The customer has deployed a pair of HPE Aruba Networking 9000 Series gateways with Security licenses at each clinic. The gateways implement IDS/IPS in IDS mode.
The Security Dashboard shows several recent events with the same signature, as shown below:
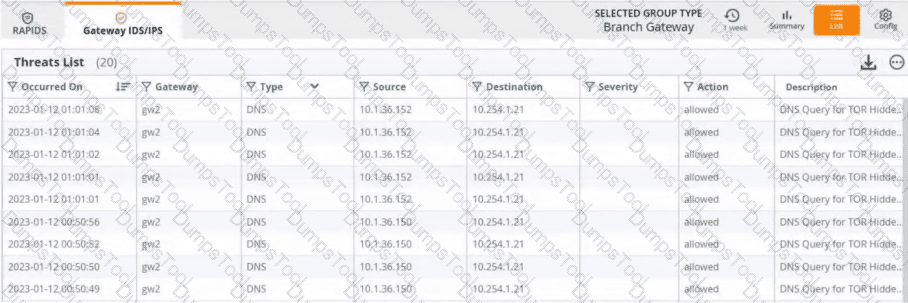
Occurred On: 2023-01-12 | Gateway: gw2 | Type: DNS | Source: 10.1.36.152 | Destination: 10.254.1.21 | Action: allowed | Description: DNS Query for TOR Hidden...
Refer to the scenario.
You have learned that nurse call stations are the source of the events. What can you conclude?

TESTED 21 Nov 2026