Halloween Sale - Special 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 75onlydt

HPE7-A08 Questions and Answers

Question # 6

You have configured 802.1X and MAC authentication in an office environment. During testing, you noticed that devices that don’t support 802.1X take a few minutes to receive an IP address. What can you do to improve the connection time for these devices while maintaining a secure configuration?

A.

Disable 802.1X on ports connecting to devices that don’t support it.

B.

Increase the 802.1X EAPOL timeout value on all ports.

C.

Configure auth-precedence to MAC, then 802.1X authentication.

D.

Decrease the MAC auth start value on all ports.

Full Access
Question # 7

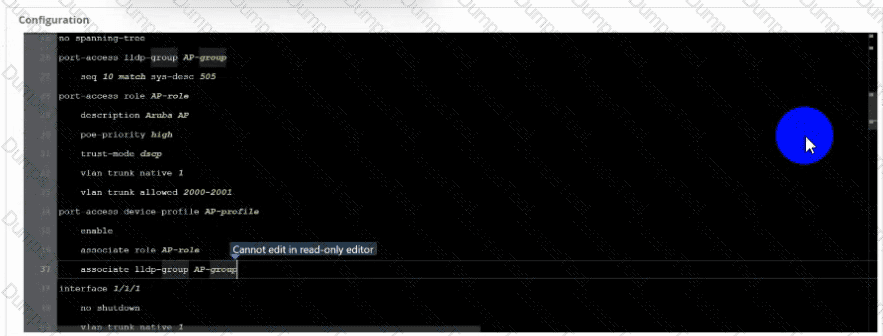
Which two configuration tasks must be performed when creating a device profile for an AP? (Select two.)

A.

Associate a role

B.

Associate a QoS policy

C.

Associate an LLDP group

D.

Associate a VLAN

E.

Associate an ACL

Full Access
Question # 8

You must enable HTTPS access to an HPE Aruba Networking CX 8100 for an SVI 100 created after default settings. How do you meet this requirement?

A.

Use the command https-server vrf mgmt to allow HTTPS access.

B.

The HTTPS server is accessible by default.

C.

The HTTPS server is accessible only from mgmt VRF.

D.

Use the command https-server vrf default to allow HTTPS access.

Full Access
Question # 9

You are troubleshooting a performance issue with a VSX LAG and have run the following troubleshooting commands:
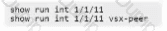
Question # 9

Which troubleshooting methodology does this exemplify?

A.

Follow the path

B.

Top-down/Bottom-up

C.

Replace configuration

D.

Spot the difference

Full Access
Question # 10

Refer to the exhibit.

Question # 10

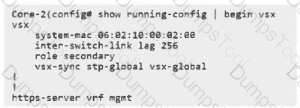
The NTP server is configured on the Primary VSX switch, however, the Secondary switch does not display the NTP configuration in the running configuration. How can the VSX configuration be changed to have the same config on both nodes?

A.

On the primary switch, add vsx-sync ntp under VSX configuration.

B.

On the secondary switch, add vsx-sync ntp under VSX configuration.

C.

On the secondary switch, add vsx-sync time under VSX configuration.

D.

On the primary switch, add vsx-sync time under VSX configuration.

Full Access
Question # 11

A recent routing change has caused an outage to one of your customer’s branch sites. You are about to run the command below:

copy checkpoint 20240722 running-config

Which troubleshooting methodology does this exemplify?

A.

Replace configuration

B.

Top-down/Bottom-up

C.

Spot the difference

D.

Divide and conquer

Full Access
Question # 12

Which switch configuration is required to implement Dynamic User Roles (DUR)?

A.

Install the CPPM HTTPS certificates root certificate.

B.

Configure the http://.well-known/aruba/clearpass/https-root.pem URL.

C.

Install the CPPM internal CA self-signed certificate.

D.

Install the TA cert of the CPPM RADIUS certificate.

Full Access
Question # 13

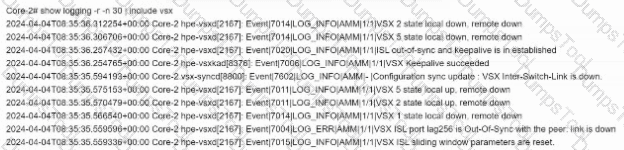
Your network monitoring system has issued a critical alert indicating that the ISL between two VSX core switches is down. What can you determine from the log output below?
Question # 13

A.

Core-2 has disabled its VSX LAG interfaces.

B.

Keepalive packets are being dropped.

C.

Both switches are forwarding traffic over VSX LAGs.

D.

Downstream switches are not able to forward traffic.

Full Access
Question # 14

What should you configure for an interface connected to a device you cannot trust to assign DSCP markings? (Select two.)

A.

Configure " qos trust cos "

B.

Apply a classifier-based policy to the interface to assign a Local Priority value

C.

Apply a dscp-map to the interface to assign a Local Priority value

D.

Configure Weighted Fair Queuing

E.

Configure " qos trust none "

Full Access
Question # 15

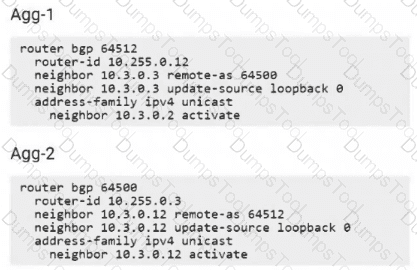
A junior engineer has configured eBGP between two CX switches (Agg-1 and Agg-2) using the configuration below, and tells you that the neighbors are in the ‘Active’ state.
Question # 15

What can you tell them?

A.

When configuring eBGP the AS numbers must match.

B.

The eBGP multi-hop feature must be configured.

C.

Peering using loopback addresses is not supported.

D.

The BGP peers are advertising and learning routes.

Full Access
Question # 16

An eBGP configuration is set up from HPE Aruba Networking CX 6300 to two peers. Both peers advertise the 10.200.0.0/23 subnet with the default configuration. What configuration implementation would prefer this route using peer A over B?

A.

Define a route-map with set local-preference 200 and bind it to peer B BGP import configuration.

B.

Define a route-map with set metric 200 and bind it to peer A BGP import configuration.

C.

Define a route-map with set local-preference 200 and bind it to peer A BGP import configuration.

D.

Define a route-map with set metric 200 and bind it to peer B BGP import configuration.

Full Access
Question # 17

When configuring a multicast solution on HPE Aruba Networking CX switches, what needs to be configured on the core switch to enable L3 multicast routing locally?

A.

IGMP on SVI

B.

IGMP on VLAN

C.

IGMP-snooping on VLAN

D.

IGMP-snooping on SVI

Full Access
Question # 18

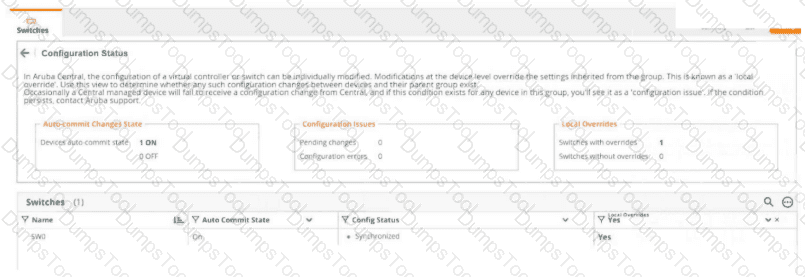
Refer to the exhibit:

Question # 18

Based on the output, which statement is true?

A.

The switch is currently managed by local CLI overrides.

B.

The switch has a configuration pushed that has changed the default settings.

C.

The switch is set to auto checkpoint creation for auto-rollback, if configuration push fails.

D.

The switch requires a commit configuration, once the change is pushed.

Full Access
Question # 19

Refer to the exhibit:

Question # 19

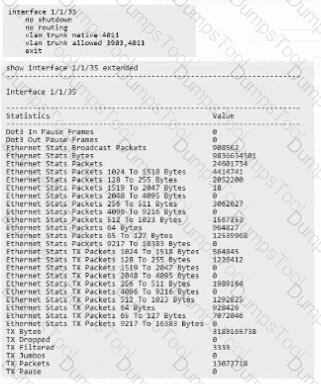
The interface is configured on an HPE Aruba Networking CX 8320 for a VMware server NIC, and the server admin reports that VMware vMotion traffic on VLAN 3903 fails, but the server can ping other ports with default settings.

What must be done to correct the issue based on the provided interface status and configuration?

A.

Configure jumbo on VLAN 3903

B.

Configure jumbo on interface 1/1/36

C.

Configure MTU 9198 on interface 1/1/36

D.

Configure MTU 9198 on VLAN 3903

Full Access
Question # 20

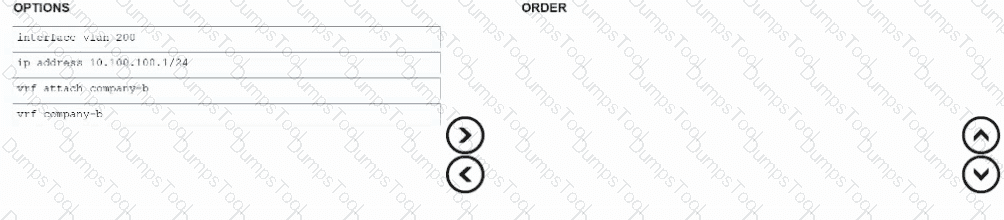
Company A has an existing HPE Aruba Networking CX 8325 VSX. It has acquired Company B and must merge its networks onto the same VSX switch configuration as Company A. Both Company A and Company B share the same 10.100.100.1/21 subnet.

What is the correct order for creating a configuration allowing overlapping networks in the setup?
Question # 20

Full Access
Question # 21

Refer to the exhibit:

Question # 21

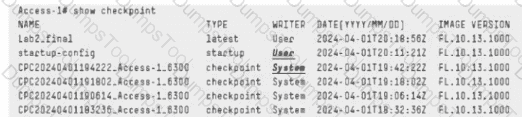
The current startup configuration on the HPE Aruba Networking CX 6300 switch no longer includes a device profile that was created on the previous day. Based on the exhibit, how can you validate if the configuration was removed without changing the current configuration?

A.

Use show checkpoint to see the changes created between the available checkpoints.

B.

Use checkpoint diff to check for differences between the startup-config and available checkpoints.

C.

Use copy startup-config checkpoint < checkpoint-name > to see the changes created between the available checkpoints.

D.

Use checkpoint rollback to see the changes created between the available checkpoints.

Full Access
Question # 22

You are deploying CX 6300 switches and AP-615 access points at a hospital providing connectivity to critical medical devices. Which feature should you enable on the switch to provide the highest uptime for the Wi-Fi network? (Choose two.)

A.

Fast РоЕ

B.

Quick PoE

C.

Uninterruptable PoE

D.

Always-on PoE

Full Access
Question # 23

Refer to the exhibit:

Question # 23

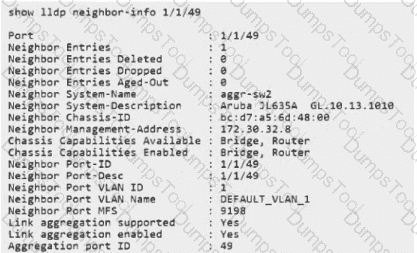
The neighbor switch is configured with the following IP interfaces:

mgmt: 172.30.32.8

loopback 0: 10.255.255.2

vlan 5: 192.168.5.2

How can you change the advertised management IP information to appear as the VLAN 5 IP?
A.

Under interface vlan 5, issue command: lldp management-address

B.

Issue in global context command: lldp management-address vlan 5

C.

Under lldp context: lldp management-address 192.168.5.2

D.

Issue in global context command: lldp management-ipv4-address vlan 5

Full Access
Question # 24

Question # 24

You are about to make a change to the HPE Aruba Networking CX switch in HPE Aruba Networking Central and are encountering the condition displayed above. What needs to be done to make a change to the switch with multi-edit?
A.

Select configuration status and enable edit config

B.

Enable edit config mode using the gear icon

C.

Override state

D.

Select the device in multi-edit and enable edit config mode

Full Access
Question # 25

Question # 25

Refer to the exhibit for an HPE Aruba Networking CX 6300M VSF:

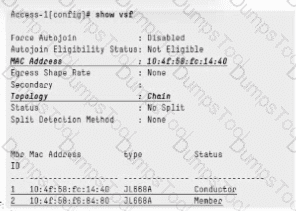
What VSF configuration is required for the stack configuration to work and avoid split-brain?

A.

vsf start-auto-stacking

B.

vsf secondary-member 2

C.

vsf conductor-member 2

D.

vsl split-detect mgrep

Full Access
Question # 26

An Aruba CX B100 VSX has the following state for LACP:

2024-06-08T19:48:34.713434+03:00 VSX1 lacpd[837]: Event|1321|LOG_INFO|AMM|1/1|LAG 253 State change for interface 1/1/25:3: Actor state: ALFNCD, Partner state: ASFNCD

2024-06-06T19:48:34.675496+03:00 VSX1 lacpd[837]: Event|1308|LOG_INFO|AMM|1/1|LACP rate set to slow for LAG 253

What can be observed based on the output?

A.

The LAG 253 has a mismatching configuration with a peer

B.

The global LACP rate has been configured for LACP ports

C.

The LAG 253 has been negotiated automatically with peer timeout values

D.

The local LAG 253 has a matching LACP configuration with peer

Full Access
Question # 27

A database administrator has reported intermittent connectivity issues with a SQL server hosted in the data center and has provided you with the source and destination IP addresses. Which troubleshooting methodology would be the most suitable to start with?

A.

Follow the path

B.

Divide and conquer

C.

Spot the difference

D.

Top-down/Bottom-up

Full Access
Question # 28

After configuring IGMP snooping on a Layer 2 VLAN, multicast applications are no longer working. Which additional configuration step is required?

A.

Enable IGMP snooping on the Layer 3 interface for the VLAN.

B.

Enable IGMP on the Layer 3 interface for the VLAN.

C.

Enable PIM-SM on the Layer 3 interface for the VLAN.

D.

Enable PIM-DM on the Layer 3 interface for the VLAN.

Full Access
Question # 29

How would you describe the firmware upgrade process for an HPE Aruba Networking VSX cluster?

A.

After the upgrade, the vsx-syned process can resume synchronization even if the switches are in a different firmware version

B.

After the upgrade, the vsx-syned process will continue synchronization, once vsx-upgrade commit is issued

C.

During the upgrade, the vsx-syned process will stop synchronization while the software versions are mismatched

D.

During the upgrade, the vsx-syned process will continue synchronization while the software versions are mismatched

Full Access
Question # 30

You are reviewing the configuration of a VSX lag and have noticed the command lacp fallback. Why might this have been configured?

A.

To allow operation with active or passive LACP.

B.

To support devices that require PXE Boot.

C.

For backwards compatibility with LACP v1.

D.

For operation using a single partner LACP interface.

Full Access
Question # 31

Which HPE Aruba Networking ClearPass configuration is required to implement DUR?

A.

Enable the RadSec service

B.

Create an admin user role

C.

Import RADIUS dictionary attributes

D.

Configure an HTTPS certificate

Full Access
Question # 32

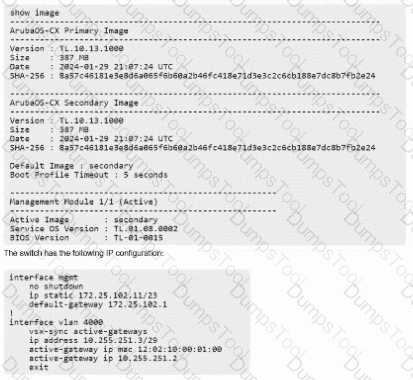
The HPE Aruba Networking CX 8320 VSX configuration is running the current software:
Question # 32

How do you upgrade the VSX cluster with the least amount of downtime from a remote server 172.25.101.10 reachable from 172.25.102.11?

A.

vsx update-software scp://172.25.101.10/image vrf mgmt

B.

vsx update-software scp://172.25.101.10/image primary

C.

vsx update-software tftp://172.25.101.10/image vrf mgmt

D.

vsx update-software tftp://172.25.101.10/image primary

Full Access
Question # 33

You are implementing a design where the campus network should be in an isolated spanning tree topology from the data centre network. The core switches are connected by a single Layer-2 interface carrying multiple VLANs.

When you examine the switches, you discover that the campus core sees the data centre core as the root bridge.

What configuration can you apply to the campus-to-data centre core link to resolve the issue?

A.

Root guard

B.

BPDU filter

C.

Admin edge

D.

BPDU guard

Full Access
Question # 34

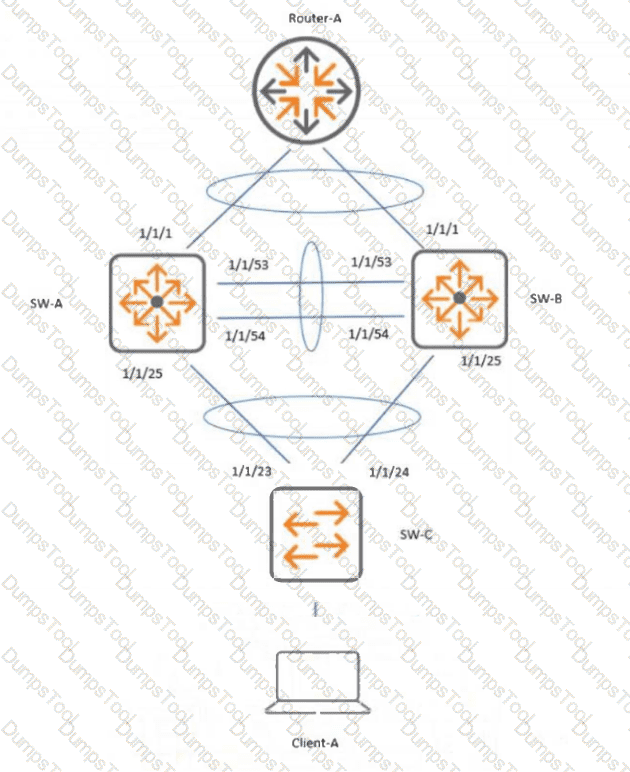
Refer to the exhibit.

Question # 34

Interfaces 1/1/53 and 1/1/54 were accidentally disconnected from Switch-A, the primary VSX member. Client A is experiencing network disruptions with network connections to Router-A.

What needs to be done to prevent user traffic disruption in this scenario?

A.

Configure VSX shutdown on-split on SW-B.

B.

Configure keepalive VLAN on upstream lag.

C.

Configure VSX shutdown on-split on SW-A.

D.

Configure keepalive using mgmt ports between SW-A and SW-B.

Full Access
Question # 35

In an attempt to clear the switch configuration, you’ve issued the command erase all zeroize. What is the result of this task?

A.

The switch clears all user credentials and retains the running configuration.

B.

The switch restores the factory-installed AOS-CX image to the switch.

C.

The switch runs a secure erase task, deleting the startup-config, and retains admin credential password.

D.

The switch runs a secure erase task, deleting all customer data, and may run up to an hour.

Full Access
Question # 36

You need to find which change was made to the HPE Aruba Networking CX switch from the GUI. Which option can you use?

A.

Use checkpoint diff to compare running-config with stored saved-config revisions

B.

Use show checkpoint diff to compare running-config with stored checkpoints

C.

Use show checkpoint diff to compare running-config with stored saved-config revisions

D.

Use checkpoint diff to compare running-config with stored checkpoints

Full Access
Question # 37

Your customer’s CISO would like to deploy colorless ports across the network. Which will you need to configure to meet this requirement?

A.

Port-security

B.

MAC Auth

C.

Sticky MAC

D.

Virtual MAC

Full Access
Question # 38

After enabling 802.1X authentication on all switch ports connected to AOS10 access points, users joining SSIDs in bridge mode no longer receive an IP address. Users of tunnel mode SSIDs are unaffected. What should be done to resolve the issue?

A.

Enable device auth-mode for the assigned AP role.

B.

Increase the client-limit value on all ports to 99.

C.

Enable MAC authentication on all switch ports.

D.

Configure 802.1X on all client devices.

Full Access
Question # 39

Refer to the exhibit from an HPE Aruba Networking CX6000:
Question # 39

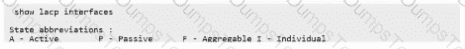
Two CX 6000 switches are configured with the same configuration for LAG 1. What needs to be done to remove the LACP block state?

A.

On one of the switches, change the LACP mode to passive

B.

Change the LACP mode from passive to active on one of the switches

C.

Change the LACP mode from passive to static on one of the switches

D.

On both of the switches, change the LACP timeout to short

Full Access
Question # 40

Your customer requires encrypting and authenticating Ethernet frames between all APs and CX switches. Which solution should you recommend?

A.

MACSec

B.

MAC-TLS

C.

MAC Auth

D.

Sticky MAC

Full Access
Question # 41

A customer has set global qos trust dscp on an HPE Aruba Networking CX 6300 VSF configuration, which replaced the existing HPE Aruba Networking 5406R VSF. After the change, a video streaming service connected to ports 1/1/20 and 2/1/20, bound to LAG 20, no longer maps to the CoS priority queue mappings used in the old configuration.

What configuration change would enable priority trust on DSCP by default and on traffic that requires CoS?

A.

Bashint 1/1/20, 2/1/20qos trust none!int lag 20qos trust cos

B.

qos trust dscp, cos

C.

Bashint 1/1/20, 2/1/20qos trust cos

D.

Bashint lag 20qos trust cos

Full Access
Question # 42

You are remotely connected to an HPE Aruba Networking CX 6200F switch using SSH to change the Control Plane ACL, allowing only defined subnets to access the switch. Which AOS-CX command allows you to roll back your change if the ACL change is wrongly formed and you can no longer log in to the switch?

A.

Use the checkpoint commit command after you commit the change.

B.

Use the checkpoint auto command before you commit the change.

C.

Use the checkpoint auto command after you commit the change.

D.

Use the checkpoint commit command before you commit the change.

Full Access
Question # 43

You need to configure BGP on an HPE Aruba Networking switch using AS 65010. What is required when establishing peering with neighboring devices using eBGP AS 65100?

A.

Use of peer AS 65001

B.

Use of route-reflector

C.

Use of directory connected peer

D.

Use of address-family ipv4 internal

Full Access
Question # 44

Your customer’s CX switches are managed in HPE Aruba Networking Central. They have recently connected some new AP-615 access points and want to be notified if the switches have any capacity issues. Which alerts should you enable? (Choose two.)

A.

Switch Uplink Port Usage

B.

Switch Link Status Change

C.

Switch Port Tx Rate

D.

Switch PoE Utilization

E.

Switch Port Rx Rate

Full Access
Question # 45

You are troubleshooting a complex routing issue after a recent change. Your customer has just called and reported that the issue now impacts all users. What should you do next?

A.

Restore the last-known working configuration.

B.

Ask the customer to send logs from each user.

C.

Explain to the customer what the issue is.

D.

Collect a show tech and log a case with TAC.

Full Access
Question # 46

What will help prevent false positives with ARP inspection?

A.

Enable ARP inspection trust for interface 1/1/20.

B.

Enable ARP inspection trust for MAC F4-6D-3F-24-76-51 at the VLAN interface context.

C.

Enable ARP inspection trust 10.100.100.10 at VLAN interface level context.

D.

Enable ARP inspection trust IP 10.100.100.10 MAC F4-6D-3F-24-76-51 in the global context.

Full Access
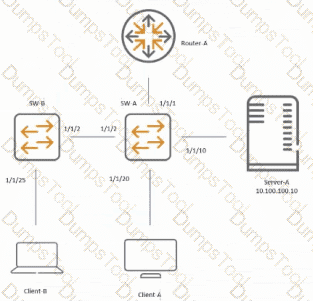
Question # 47

Refer to the exhibit:

Question # 47

SW-A is the Layer 3 gateway for:

Server-A in VLAN 100, subnet 10.100.100.0/24

Client-A in VLAN 20, subnet 10.100.20.0/24

Client-B in VLAN 30, subnet 10.100.30.0/24

What must be done to prevent rogue DHCP servers in VLAN 30 on SW-B?

A.

Enable dhcpv4-snooping trust 10.100.100.10 on VLAN 30

B.

Enable dhcpv4-snooping authorized-server 10.100.100.10 on VLAN 30

C.

Enable snooping globally and on VLAN 30

D.

Enable dhcpv4-snooping globally and on interface VLAN 30

Full Access
Question # 48

You have added a switch with existing configuration to an existing group in HPE Aruba Networking Central but the configuration is not synchronizing. What could cause this?
A.

Only switches with factory default config can be added to a group with existing config.

B.

HPE Aruba networking Central has not been enabled on the local switch configuration.

C.

The switch is configured in a VSX pair, which HPE Aruba Networking Central does not support.

D.

The switch is still pending authorization on the organization settings page.

Full Access