dumpstool logo
You want to protect OT devices that are not updated against known vulnerabilities so you apply virtual patching to the firewall policies. What must you check to confirm that the OT devices are virtually patched? (Choose one answer)
Refer to the exhibits.
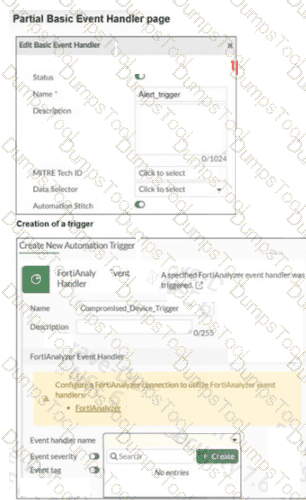
A partial Basic Event Handler page on FortiAnalyzer and the creation of a trigger in a FortiGate device are shown. To improve the protection of your OT network, you want to automate the handling of compromised devices notified through FortiAnalyzer. You have configured an event handler named Alert_trigger as shown in the exhibit. When you create the trigger on the FortiGate device, the Event handler name field does not provide the Alert_trigger option. What two actions must you perform to make the Alert_trigger option available? (Choose two answers)
Refer to the exhibit.
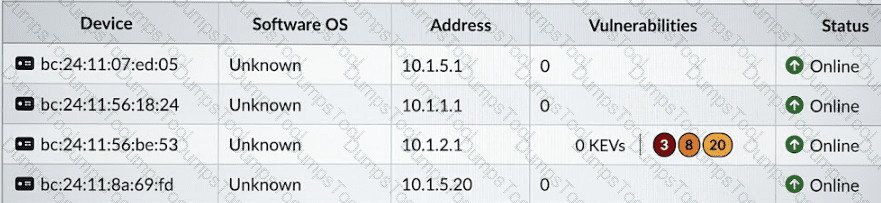
Which statement about this partial Asset Identity List page is correct? (Choose one answer)
You want FortiAnalyzer to trigger an automation stitch on a FortiGate device automatically. What must you configure on FortiAnalyzer to enable direct communication with FortiGate? (Choose one answer)
Refer to the exhibit.
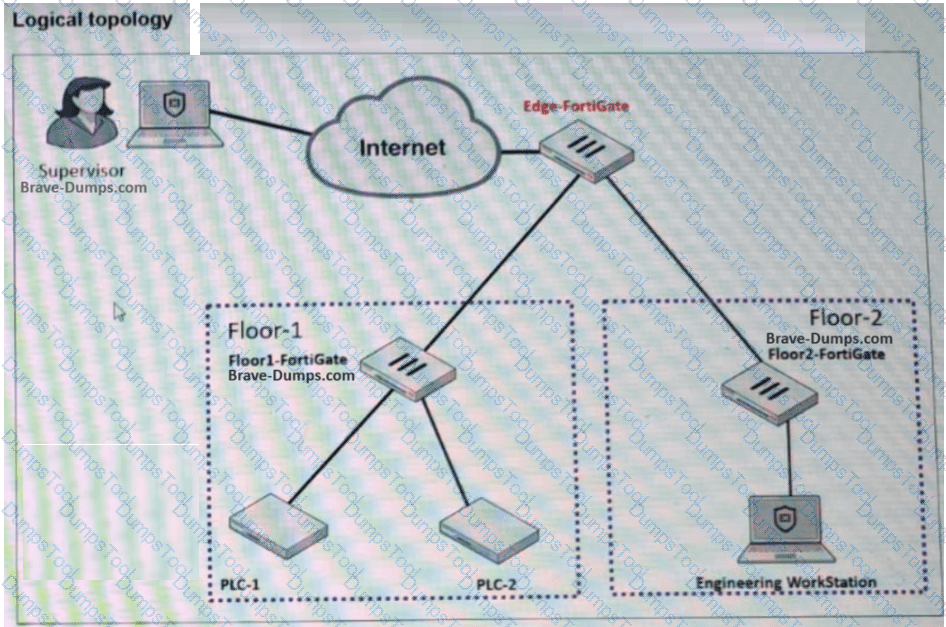
A partial OT network is shown. You want to provide the supervisor with secure remote access. Which two features can you implement on Edge-FortiGate ? (Choose two answers)
Refer to the exhibit.
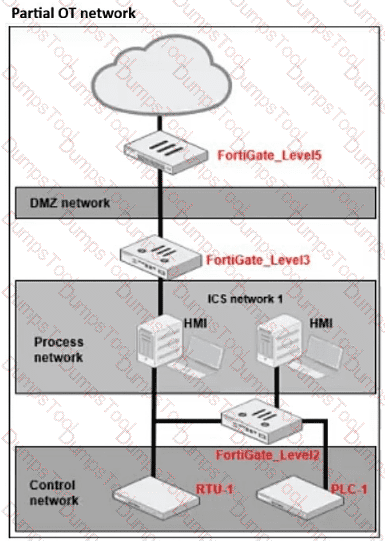
A partial OT network is shown.
PLC-1 has a known critical vulnerability, but you cannot update it.
What must you configure to protect PLC-1?
Refer to the exhibit.
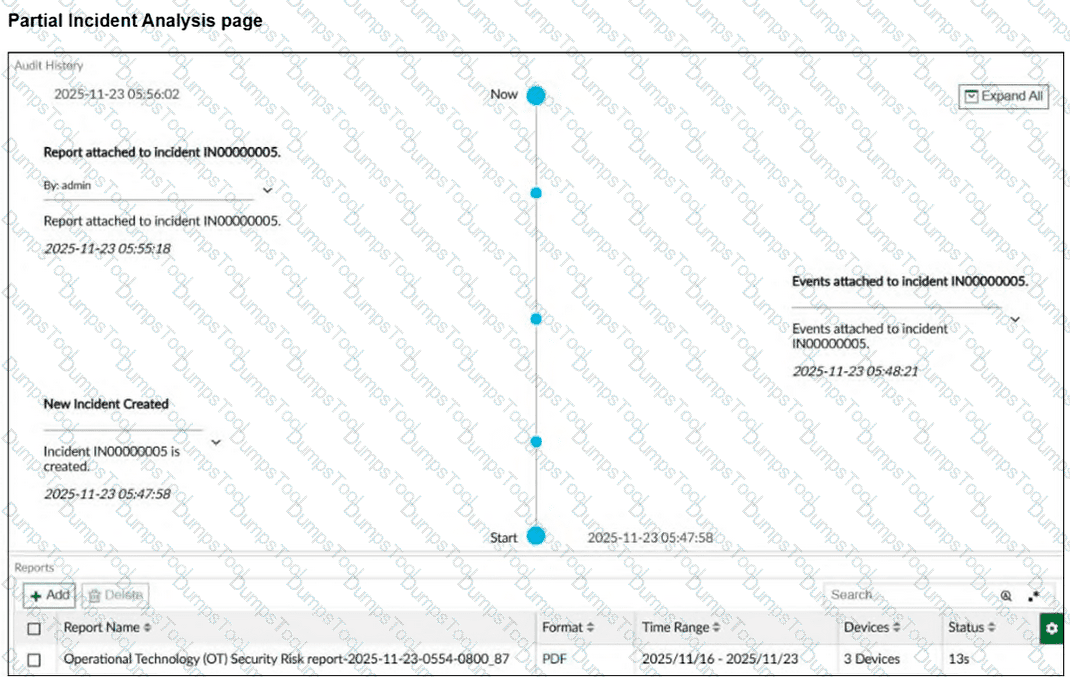
A partial Incident Analysis page is shown. How was the 360-Degree Security Review OT report attached to the incident? (Choose one answer)
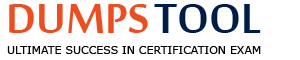
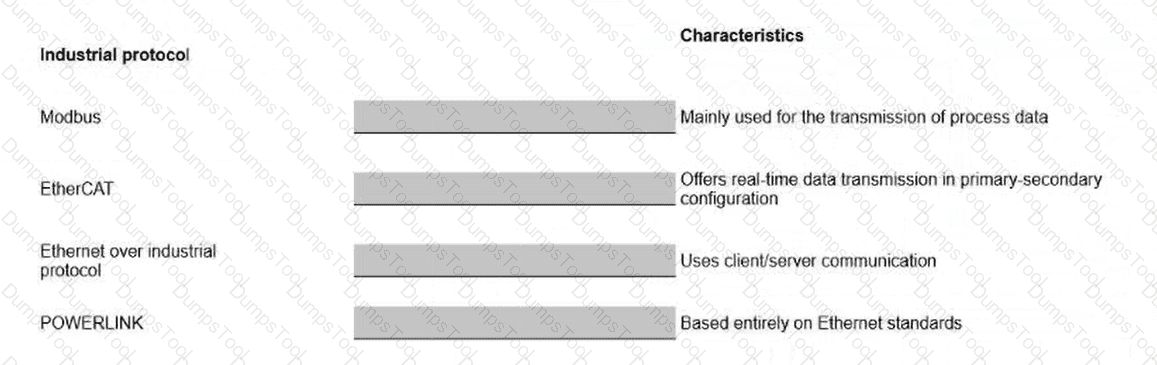
Match each industrial protocol to its corresponding characteristics.
Select each OT industrial protocol in the column on the left and drag and drop it into the blank space next to its corresponding characteristic in the column on the right. You must match all four industrial protocols to their characteristics in the work area.
Refer to the exhibit.
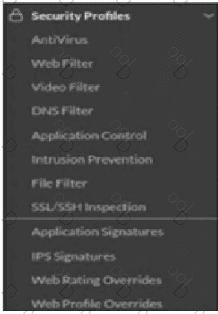
The OT devices behind the ruggedized FortiGate have vulnerabilities and you want to apply a virtual patching profile in the firewall policy. Why is Virtual Patching not available in the Security Profiles section? (Choose one answer)
Refer to the exhibit.
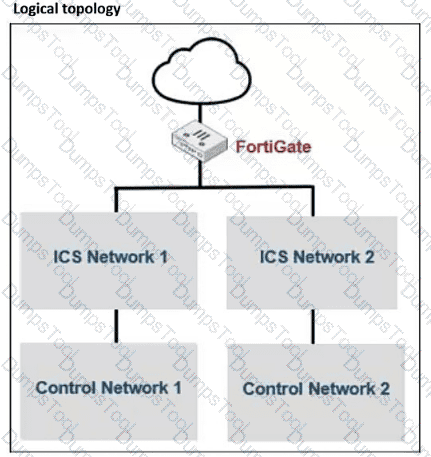
A partial OT network is shown.
The OT network is divided into two main networks with a FortiGate device operating in NAT mode.
How can you further segment network 1 from network 2?
What is the main OT component for monitoring and controlling industrial processes? (Choose one answer)
TESTED 06 Oct 2026