dumpstool logo
An engineer must deploy a high-availability that includes two Cisco Secure Firewall Threat Defense devices configured as cluster. The deployment must have a mechanism that protects synchronization between cluster members Which action must the engineer take to meet the requirements?
Which CLI command is used to control special handling of ClientHello messages?
Which policy rule is included in the deployment of a local DMZ during the initial deployment of a Cisco NGFW through the Cisco FMC GUI?
A software development company hosts the website http:dev.company.com for contractors to share code for projects they are working on with internal developers. The web server is on premises and is protected by a Cisco Secure Firewall Threat Defense appliance. The network administrator is worried about someone trying to transmit infected files to internal users via this site. Which type of policy must be able associated with an access control policy to enable Cisco Secure Firewall Malware Defense to detect and block malware?
An analyst is reviewing the Cisco FMC reports for the week. They notice that some peer-to-peer applications are being used on the network and they must identify which poses the greatest risk to the environment. Which report gives the analyst this information?
An engineer is working on a LAN switch and has noticed that its network connection to the mime Cisco IPS has gone down Upon troubleshooting it is determined that the switch is working as expected What must have been implemented for this failure to occur?
An engineer is implementing clustering in Cisco Secure Firewall Management Center. The configuration must ensure that the cluster has a designated control node with more resources than the other nodes. What must the engineer set for the priority value of that node?
Which action should be taken after editing an object that is used inside an access control policy?
An engineer is deploying a Cisco Secure Firewall Management Center appliance. The company must send data to Cisco Secure Network Analytics appliances. Which two actions must the engineer take? (Choose two.)
An organization has a Cisco IPS running in inline mode and is inspecting traffic for malicious activity. When traffic is received by the Cisco IRS, if it is not dropped, how does the traffic get to its destination?
An engineer runs the command restore remote-manager-backup location 2.2.2.2 admin /Volume/home/admin FTD408566513.zip on a Cisco FMC. After connecting to the repository, the Cisco FTD device is unable to accept the backup file. What is the reason for this failure?
While integrating Cisco Umbrella with Cisco Threat Response, a network security engineer wants to automatically push blocking of domains from the Cisco Threat Response interface to Cisco Umbrella. Which API meets this requirement?
An engineer is implementing a new Cisco Secure Firewall. The firewall must filler traffic between the three subnets:
• LAN 192.168.101.0724
• DMZ 192.168 200.0/24
• WAN 10.0.0.0/30
Which firewall mode must the engineer implement?
An organization is configuring a new Cisco Firepower High Availability deployment. Which actionmust be taken to ensure that failover is as seamless as possible to end users?
An engineer is troubleshooting an intermittent connectivity issue on a Cisco Secure Firewall Threat Defense appliance and must collect 24 hours ' worth of data. The engineer started a packet capture. Whenever it stopsprematurely during this time period. The engineer notices that the packet capture butter size is set to the default of 32 MB Which butter S170 is the maximum that the engineer must sot to able the packet capture to run successfully?
Upon detecting a flagrant threat on an endpoint, which two technologies instruct Cisco Identity Services Engine to contain the infected endpoint either manually or automatically? (Choose two.)
A security engineer must configure a Cisco Secure Firewall Threat Defense device to inspect only executable files. A lightweight method of detecting whether a file is an executable must be used. Which configuration for Malware Cloud Lookup must be selected in Cisco Secure Firewall Management Center?
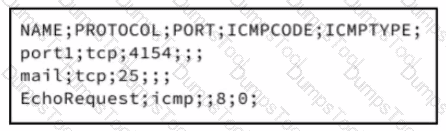
An engineer must import three port objects into the Cisco Secure Firewall Management Center by using a CSV file. Which file content must be imported to meet the requirement?
A)
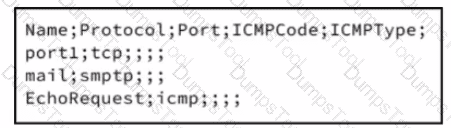
B)
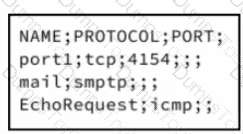
C)
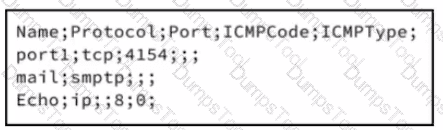
D)
Which two OSPF routing features are configured in Cisco FMC and propagated to Cisco FTD? (Choosetwo.)
An engineer is configuring URL filtering tor a Cisco Secure Firewall Threat Defense device in Cisco Secure Firewall Management Centre. Use ' s must receive a warning when they access
..wwww badaduitsito com with the option of continuing to the website if they choose to No other websites should he blocked. Which two actions must the engineer take to moot these requirements?
An organization has seen a lot of traffic congestion on their links going out to the internet There is a Cisco Firepower device that processes all of the traffic going to the internet prior to leaving the enterprise. How is the congestion alleviated so that legitimate business traffic reaches the destination?
Network traffic coining from an organization ' s CEO must never be denied. Which access control policy configuration option should be used if the deployment engineer is not permitted to create a rule to allow all traffic?
What is a benefit of implementing Integrated Routing and Bridging (IRB) on a Cisco Secure Firewall device?
With Cisco Firepower Threat Defense software, which interface mode must be configured to passively receive traffic that passes through the appliance?
When an engineer captures traffic on a Cisco FTD to troubleshoot a connectivity problem, they receive a large amount of output data in the GUI tool. The engineer found that viewing the Captures this way is time-consuming and difficult lo son and filter. Which file type must the engineer export the data in so that it can be reviewed using a tool built for this type of analysis?
An engineer is configuring Cisco Secure Firewall Threat Defense managed by a Secure Firewall Management Center appliance. The company wants remote access VPN users to be reachable from the inside network. What must the engineer configure to meet the requirements?
An engineer must deny ICMP traffic to the networks of separate departments that use Cisco Secure Firewall Management Center. The engineer must use the same object on the relevant device for each network. What must be configured in Secure Firewall Management Center?
An engineer installs a Cisco FTD device and wants to inspect traffic within the same subnet passing through a firewall and inspect traffic destined to the internet.
Which configuration will meet this requirement?
A security engineer must create an access list object in Cisco Secure Firewall Management Center to allow traffic to IP address 10.236.131.1 but block traffic to IP address 10.236.131.0/24. Which access control entries must the engineer create?
A)
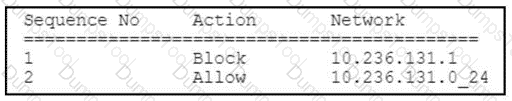
B)
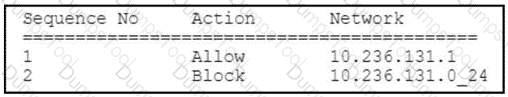
C)
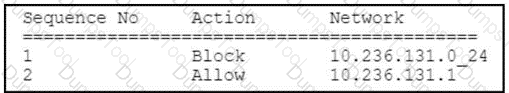
D)
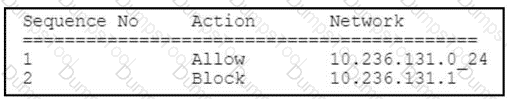
A network administrator is configuring an instance of Cisco Secure Firewall Threat Defense, which is registered to Cisco Secure Firewall Management Center, to prevent internal users from downloading executable files from the internet. What must be created and configured by the administrator to meet the requirement?
An administrator configures a Cisco Secure Firewall Threat Defense device in transparent mode. To configure the BVI (Bridge Virtual Interface), the administrator must:
Add a bridge-group interface
Configure a bridge-group ID
Configure the bridge-group interface description
Add bridge-group member interfaces
How must the engineer perform these actions?
A security engineer must deploy a Cisco FTD appliance as a bump in the wire to detect intrusion events without disrupting the flow of network traffic. Which two features must be configured to accomplish the task? (Choose two.)
When packet capture is used on a Cisco Secure Firewall Threat Defense device and the packet flow is wailing on the malware query, which Snort verdict appears?
A network administrator notices that inspection has been interrupted on all non-managed interfaces of a device. What is the cause of this?
An engineer must export a packet capture from Cisco Secure Firewall Management Center to assist in troubleshooting an issue an a Secure Firewall Threat Defense device. When the engineer navigates to URL for Secure Firewall Management Center at:
.. < FMC IP > /capture/CAP/pcap/sample.pcap
An engineer receives a 403: Forbidden error instead of being provided with the PCAP file. Which action resolves the issue?
An administrator must fix a network problem whereby traffic from the inside network to a webserver is not getting through an instance of Cisco Secure Firewall Threat Defense. Which command must the administrator use to capture packets to the webserver that are dropped by Secure Firewall Throat Defense and resold the issue?
An engineer defines a new rule while configuring an Access Control Policy. After deploying the policy, the rule is not working as expected and the hit counters associated with the rule are showing zero. What is causing this error?
An engineer must create an access control policy on a Cisco Secure Firewall Threat Defense device. The company has a contact center that utilizes VoIP heavily, and it is critical that this traffic is not …. by performance issues after deploying the access control policy Which access control Action rule must be configured to handle the VoIP traffic?
A security administrator must configure Cisco Secure Firewall Management Center so that certain intrusion rules are active only during specified times. Which action must the administrator take?
A network engineer is implementing high availability between two Cisco Secure Firewall Threat Defense devices. The engineer already checked the model, version, and number of interfaces Which two configurations must the engineer match next to meet the requirement? (Choose two.)
A network administrator is concerned about (he high number of malware files affecting users ' machines. What must be done within the access control policy in Cisco FMC to address this concern?
Users report that Cisco Duo 2FA fails when they attempt to connect to the VPN on a Cisco Secure Firewall Threat Defense (FTD) device IT staff have VPN profiles that do not require multifactor authentication and they can connect to the VPN without any issues When viewing the VPN troubleshooting log in Cisco Secure Firewall Management Centre (FMC), the network administrator sees an error in the Cisco Duo AAA server has been marked as tailed. What is the root cause of the Issue?
An engineer Is configuring a Cisco FTD device to place on the Finance VLAN to provide additional protection tor company financial data. The device must be deployed without requiring any changes on the end user workstations, which currently use DHCP lo obtain an IP address. How must the engineer deploy the device to meet this requirement?
A Cisco FTD has two physical interfaces assigned to a BVI. Each interface is connected to a different VLAN on the same switch. Which firewall mode is the Cisco FTD set up to support?
What is a limitation to consider when running a dynamic routing protocol on a Cisco FTD device in IRB mode?
An engineer must investigate a connectivity issue and decides to use the packet capture feature on Cisco FTD. The goal is to see the real packet going through the Cisco FTD device and see the Snort detection actions as a part of the output. After the capture-traffic command is issued, only the packets are displayed. Which action resolves this issue?
A security engineer needs to configure a network discovery policy on a Cisco FMC appliance and prevent excessive network discovery events from overloading the FMC database? Which action must be taken to accomplish this task?
An engineer must configure a SPAN to monitor traffic by using a Cisco Secure IPS device in passive mode. The Cisco Secure IPS interface Gi0/1 is connected to Cisco Catalyst Switch interface Gi0/3. Which SPAN configuration meets the requirement?
A)
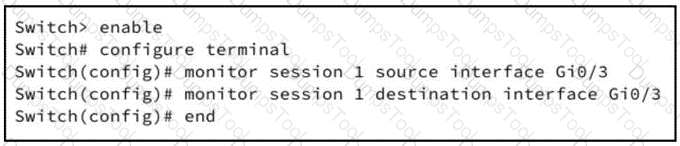
B)
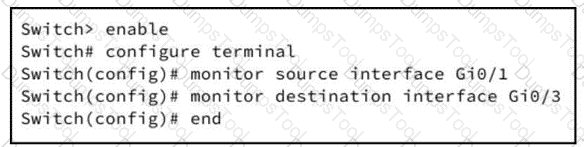
C)
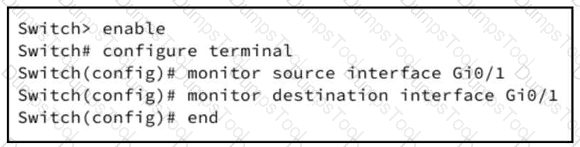
D)
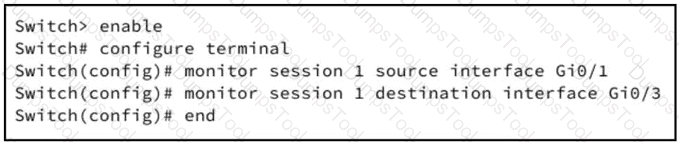
An engineer is troubleshooting connectivity to the DNS servers from hosts behind a new Cisco FTD device. The hosts cannot send DNS queries to servers in the DMZ. Which action should the engineer take to troubleshoot this issue using the real DNS packets?
An engineer must configure an ERSPAN passive interface on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. These configurations have been performed already:
Configure the passive interface.
Configure the ERSPAN IP address.
Which two additional settings must be configured to complete the configuration? (Choose two.)
A security analyst must provide detailed statics about high-bandwidth applications on a Cisco Secure Firewall Threat Defense device. The organization is approaching its peak season, so network downtime must be minimized. Which report template must the security analyst use?
An engineer attempts to pull the configuration for a Cisco FTD sensor to review with Cisco TAC but does not have direct access to the CU for the device. The CLl for the device is managed by Cisco FMC to which the engineer has access. Which action in Cisco FMC grants access to the CLl for the device?
Network users are experiencing Intermittent issues with internet access. An engineer ident med mat the issue Is being caused by NAT exhaustion. How must the engineer change the dynamic NAT configuration to provide internet access for more users without running out of resources?
What is the maximum bit size that Cisco FMC supports for HTTPS certificates?
An engineer must configure a passive interface on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. These configurations have been performed already:
•Set the interface mode to Passive.
•Configure the MTU.
•Set the speed and duplex. Which action completes the configuration?
Refer to the exhibit.
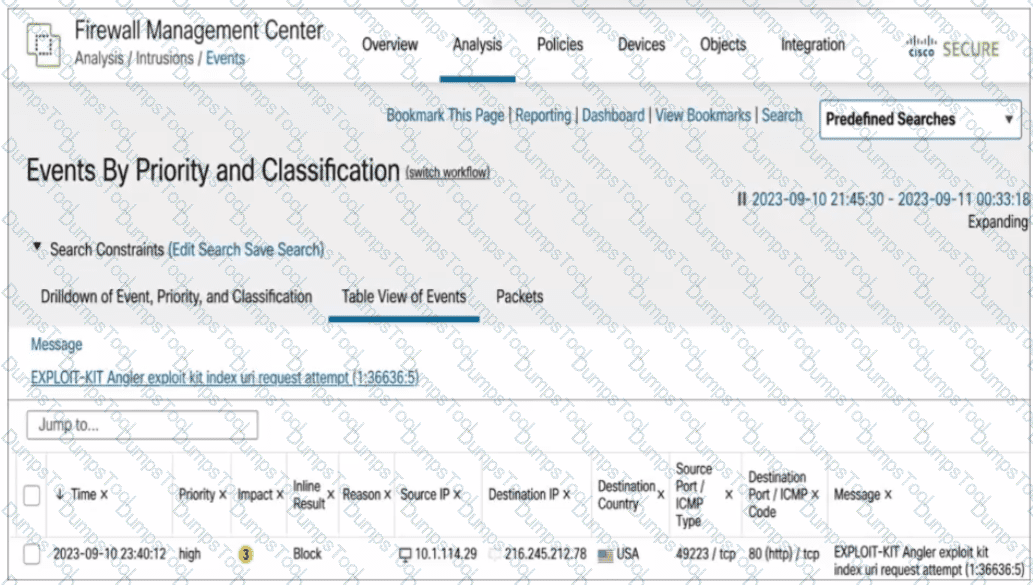
An engineer is analyzing an event in Cisco Secure Firewall Management Center Considering this log entry, which specific security threat is observed?
Which default action setting in a Cisco FTD Access Control Policy allows all traffic from an undefined application to pass without Snort Inspection?
An administrator is configuring their transparent Cisco FTD device to receive ERSPAN traffic from multiple switches on a passive port, but the Cisco FTD is not processing the traffic. What is the problem?
Which license type is required on Cisco ISE to integrate with Cisco FMC pxGrid?
An engineer wants to perform a packet capture on the Cisco FTD to confirm that the host using IP address 192 168.100.100 has the MAC address of 0042 7734.103 to help troubleshoot aconnectivity issue What is the correct tcpdump command syntax to ensure that the MAC address appears in the packet capture output?
An engineer is monitoring network traffic from their sales and product development departments, which are on two separate networks What must be configured in order to maintain data privacy for both departments?
A mid-sized company is experiencing higher network bandwidth utilization due to a recent acquisition The network operations team is asked to scale up their one Cisco FTD appliance deployment to higher capacities due to the increased network bandwidth. Which design option should be used to accomplish this goal?
What is the maximum SHA level of filtering that Threat Intelligence Director supports?
Which two routing options are valid with Cisco Firepower Threat Defense? (Choose two.)
Which language searches and analyzes data within Splunk for threat detection?
An engineer must integrate a third-party security intelligence feed with Cisco Secure Firewall Management Center. Secure Firewall Management Center is running Version 6.2.3 and has 8
GB of memory. Which two actions must be taken to implement Threat Intelligence Director? (Choose two.)
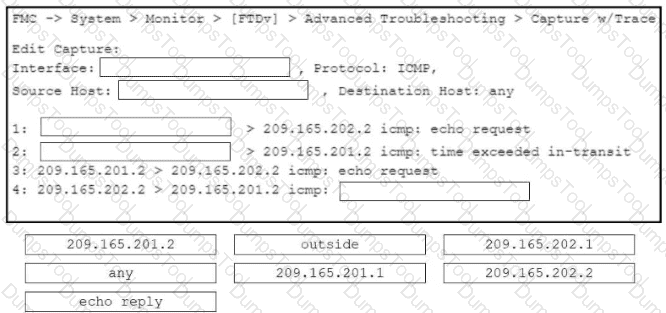
Refer to the exhibit.
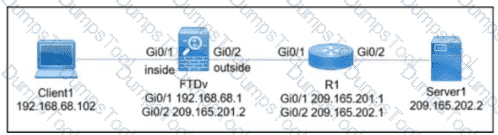
A user on a computer named Client1 is performing a traceroute to IP address 209.165.202.2. Drag and drop the appropriate values onto the fields in the Capture w/Trace configuration and captured-packet output. Not all options are used.
An engineer is configuring a Cisco Secure Firewall Threat Defense device to operate in transparent mode between two switch stacks. VLAN 10 is used for in-band management on both switch stacks. Which two actions are required on the device to inspect traffic between the switch stacks without interrupting network traffic? (Choose two.)
A security engineer is deploying a Cisco Secure Firewall Threat Defense device through Cisco Secure Firewall Management Center. The Threat license is installed, the Encrypted Visibility Engine is enabled in the access control policy Decryption policy is configured with the Decrypt - Resign action to inspect outbound TLS/SSL traffic. Users report that a banking applications repeatedly fails to load. The engineer confirms the endpoint performs certificate pinning to validate the server certificate. Engineer must allow the traffic to pass while all other outbound traffic continues to be inspected. The engineer created a rule that matches banking category and placed the rule above Decrypt - Resign policy. Which decryption rule action must be configured to meet the requirement?
Refer to the exhibit.
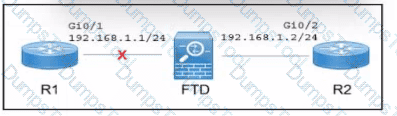
A Cisco Secure Firewall Threat Defense (FTD) device is deployed in inline mode with an inline set. The network engineer wants router R2 to remove the directly connected route M 68.1.0/24 from its routing table when the cable between routed R1 and the Secure FTD device Is disconnected. Which action must the engineer take?
1
An administrator is adding a new URL-based category feed to the Cisco FMC for use within the policies. The intelligence source does not use STIX. but instead uses a .txt file format. Which action ensures that regular updates are provided?
A network administrator is migrating from a Cisco ASA to a Cisco FTD.
EIGRP is configured on the Cisco ASA but it is not available in the Cisco FMC.
Which action must the administrator take to enable this feature on the Cisco FTD?
A network administrator is trying to configure Active Directory authentication for VPN authentication to a Cisco Secure Firewall Threat Defence instance that is registered with Cisco Secure Firewall Management Center. Which system settings must be configured first in Secure Firewall Management Center to accomplish the goal?
Network users experience issues when accessing a server on a different network segment. An engineer investigates the issue by performing packet capture on Cisco Secure Firewall Threat Defense. The engineer expects more data and suspects that not all the traffic was collected during a 15-minute can’t captured session. Which action must the engineer take to resolve the issue?
Which process should be checked when troubleshooting registration issues between Cisco FMC and managed devices to verify that secure communication is occurring?
An engineer must deploy a Cisco FTD device. Management wants to examine traffic without requiring network changes that will disrupt end users. Corporate security policy requires the separation of management traffic from data traffic and the use of SSH over Telnet for remote administration. How must the device be deployed to meet these requirements?
A network administrator wants to configure a Cisco Secure Firewall Threat Defense instance managed by Cisco Secure Firewall Management Center to block traffic to known cryptomning networks. Which system settings must the administrator configure in Secure Firewall Management Center to meet the requirement?
A Cisco FTD device is running in transparent firewall mode with a VTEP bridge group member ingress interface What must be considered by an engineer tasked with specifying a destination MAC address for a packet trace?
An engineer is investigating connectivity problems on Cisco Firepower that is using service group tags. Specific devices are not being tagged correctly, which is preventing clients from using the proper policies when going through the firewall How is this issue resolved?
How many report templates does the Cisco Firepower Management Center support?
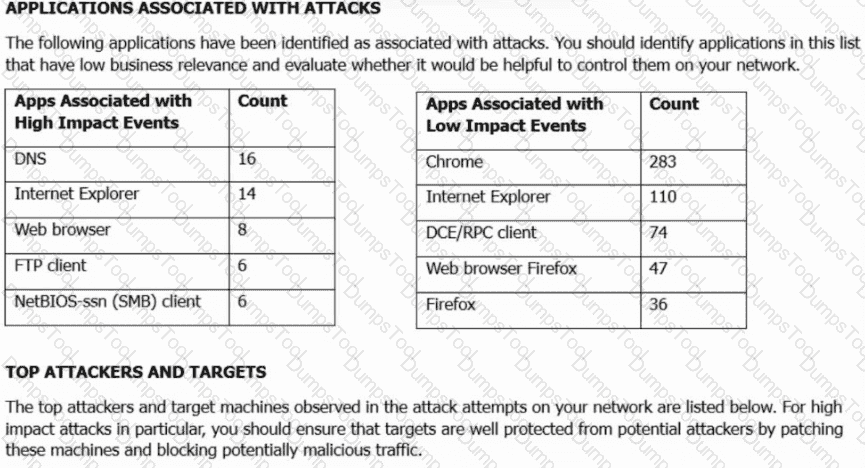
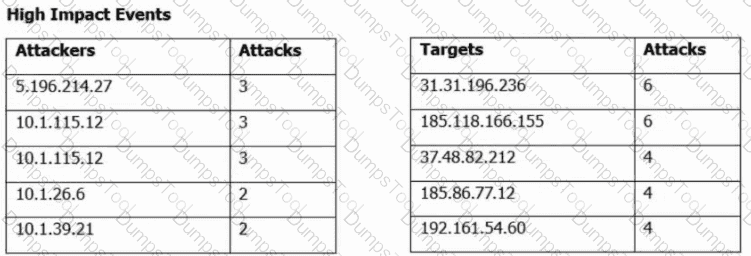
Refer to the exhibit. A security engineer must improve security in an organization and is producing a risk mitigation strategy to present to management for approval. Which action must the security engineer take based on this Attacks Risk Report?
Which two considerations must be made when deleting and re-adding devices while managing them via Cisco FMC (Choose two).
Refer to the exhibit.
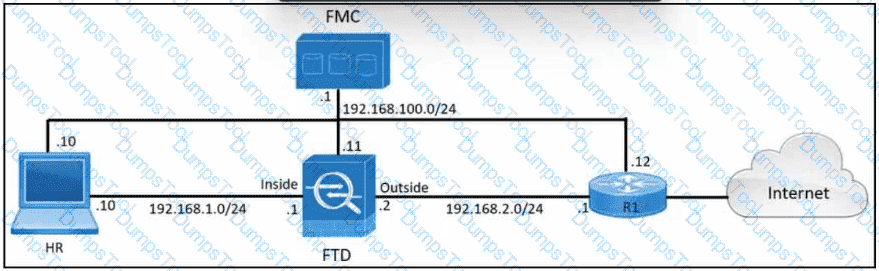
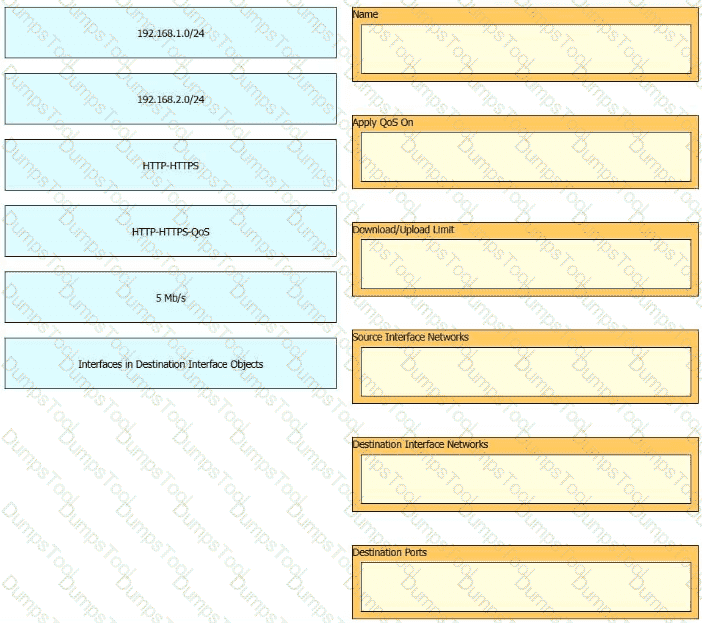
An engineer must create a QoS policy in Cisco Secure Firewall Management Center to limit HTTP and HTTPS traffic originating from users in the HR department. The download and upload limits for HTTP and HTTPS traffic must both be set to 5 Mb/s. Drag and drop the values onto the corresponding QoS rule settings.
An administrator is attempting to add a new FTD device to their FMC behind a NAT device with a NAT ID of NAT001 and a password of Cisco0420l06525. The private IP address of the FMC server is 192.168.45.45. which is being translated to the public IP address of 209.165.200.225/27. Which command set must be used in order to accomplish this task?
An administrator is optimizing the Cisco FTD rules to improve network performance, and wants to bypass inspection for certain traffic types to reduce the load on the Cisco FTD. Which policy must be configured to accomplish this goal?
An engineer is configuring a second Cisco FMC as a standby device but is unable to register with the active unit. What is causing this issue?
An engineer must configure an inline set on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. The inline set must make a copy of each packet before analyzing the packet and block any connections that do not complete the three-way handshake. These configurations have been performed already:
Select and enable the interfaces that will be added to the inline set.
Configure the speed and duplex.
Configure the inline set and add the interfaces to the inline set.
Which action completes the task?
Which two features of Cisco AMP for Endpoints allow for an uploaded file to be blocked? (Choose two.)
An engineer is configuring Cisco FMC and wants to limit the time allowed for processing packets through the interface However if the time is exceeded the configuration must allow packets to bypass detection What must be configured on the Cisco FMC to accomplish this task?
An engineer has been tasked with providing disaster recovery for an organization ' s primary Cisco FMC. What must be done on the primary and secondary Cisco FMCs to ensure that a copy of the original corporate policy is available if the primary Cisco FMC fails?
An organization recently implemented a transparent Cisco FTD in their network.
They must ensure that the device does not respond to insecure SSL/TLS protocols.
Which action accomplishes the task?
An engineer is building a new access control policy using Cisco FMC. The policy must inspect a unique IPS policy as well as log rule matching. Which action must be taken to meet these requirements?
Which Cisco FMC report gives the analyst information about the ports and protocols that are related to the configured sensitive network for analysis?
A network administrator cannot select the link to be used for failover when configuring an active/passive HA Cisco FTD pair.
Which configuration must be changed before setting up the high availability pair?
A network administrator is trying to configure an access rule to allow access to a specific banking site over HTTPS. Which method must the administrator use to meet the requirement?
A security engineer must create a Network Operations Center dashboard to display detailed information about the events collected by Secure Firewall Management Center. A Custom Analysis widget must be configured to display how many intrusion events of each type occurred by using the Intrusion Events table, with the data aggregated by Event Count. Which field must be configured to create the widget?
An engainermust add DNS-specific rules to me Cisco FTD intrusion policy. The engineer wants to use the rules currently in the Cisco FTD Snort database that are not already enabled but does not want to enable more than are needed. Which action meets these requirements?
Which action should you take when Cisco Threat Response notifies you that AMP has identified a file as malware?
Refer to the exhibit.
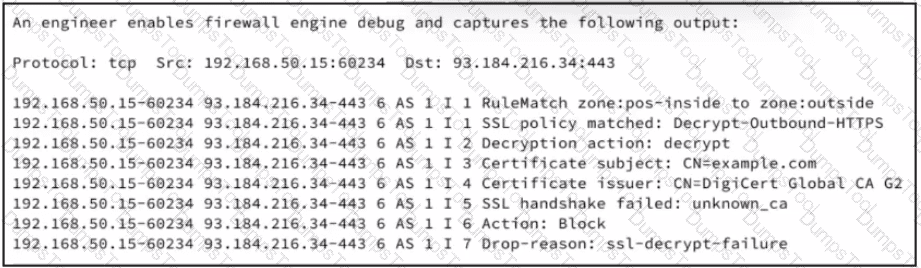
Security engineer is investigating an issue where outbound HTTPS traffic from an endpoint using network 192.168.50.0/24 is being blocked. The Cisco Secure Firewall Threat Defense is configured with a TLS decryption policy applied to all outbound web traffic. An engineer enables firewall engine debug and captures the output. Which action must be performed to resolve the issue?
An engineer must implement static route tracking on a Cisco Secure Firewall Threat Defense appliance. Static route and IP SLA operation has already been configured. Static route must be removed from the routing table if the tracked object is unreachable. Which action must the engineer take next to meet the requirement?
Which Firepower feature allows users to configure bridges in routed mode and enables devices to perform Layer 2 switching between interfaces?
Which type of certificate must be exported from Cisco ISE to integrate Cisco Secure Firewall Management Center with pxGrid?
Refer to the exhibit.
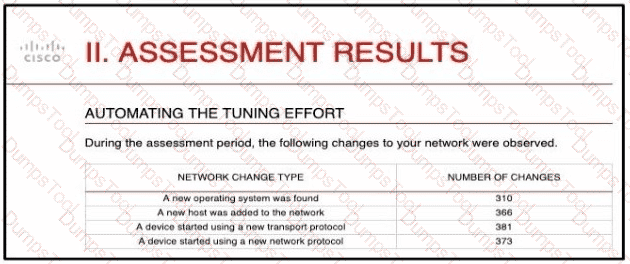
And engineer is analyzing the Attacks Risk Report and finds that there are over 300 instances of new operating systems being seen on the network How is the Firepower configuration updated to protect these new operating systems?
Refer to the exhibit.
What must be done to fix access to this website while preventing the same communication to all other websites?
A security engineer is configuring an Access Control Policy for multiple branch locations. These locations share a common rule set and utilize a network object called INSIDE_NET which contains the locally significant internal network subnets at each location. Which technique will retain the policy consistency at each location but allow only the locally significant network subnet within the applicable rules?
An organization wants to secure traffic from their branch office to the headquarter building using Cisco Firepower devices, They want to ensure that their Cisco Firepower devices are not wasting resources on inspecting the VPN traffic. What must be done to meet these requirements?
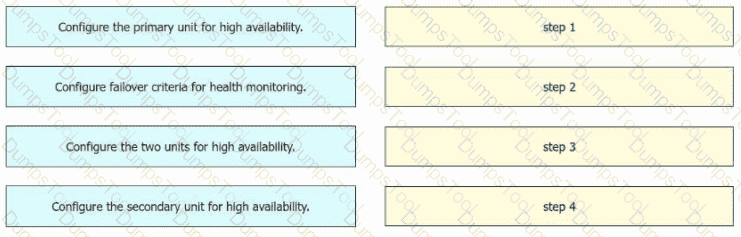
An engineer must configure high availability on two Cisco Secure Firewall Threat Defense appliances. Drag and drop the configuration steps from the left into the sequence on the right.
A network administrator configured an access control rule named WEB05405_SRV06798_ALLOW that allows any source on the Internet to reach the public IP address of a web server on port 8080. The administrator also configured a NAT policy that translates the public IP address to the internal web server IP address. During testing, the web server is not reachable from the Internet on port 8080. Which configuration must the administrator apply to resolve the issue?
An engineer must configure a SPAN session to monitor traffic by using a Cisco Secure IPS device in passive mode. Cisco Secure IPS interface Gi0/1 is connected to Cisco Catalyst switch interface Gi0/3. Which SPAN configuration meets the requirement?
An engineer is configuring a cisco FTD appliance in IPS-only mode and needs to utilize fail-to-wire interfaces. Which interface mode should be used to meet these requirements?
A network administrator is implementing an active/passive high availability Cisco FTD pair.
When adding the high availability pair, the administrator cannot select the secondary peer.
What is the cause?
A network security engineer must export packet captures from the Cisco FMC web browser while troubleshooting an issue. When navigating to the address https:// < FMC IP > /capture/CAPI/pcap/test.pcap. an error 403: Forbidden is given instead of the PCAP file. Which action must the engineer take to resolve this issue?
Refer to the exhibit.
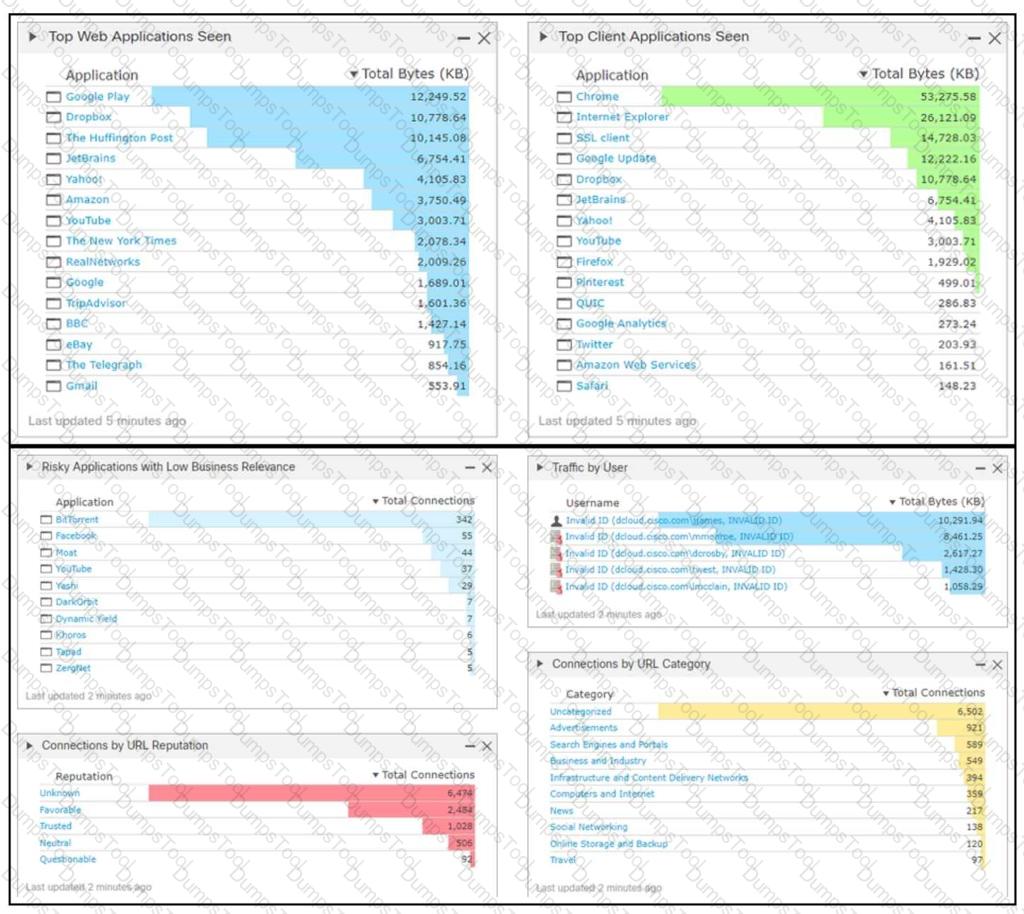
An engineer analyzes a Cisco Firepower Management Center dashboard. Which action must the engineer take to decrease the application usage risk?
An engineermustconfigure a Cisco FMC dashboard in a multidomain deployment Which action must the engineer take to edit a report template from an ancestor domain?
A network administrator is deploying a new Cisco Secure Firewall Threat Defense (FTD) firewall After Cisco Secure FTD is deployed, inside clients nave intermittent connectivity to each other. When … the packet capture on the Secure FTD firewall, the administrator sees that Secure FID is responding to all the AW requests on the inside network. Which action must the network administrator e to resolve the issue ' '
A network engineer must configure an existing firewall to have a NAT configuration. The now configuration must support more than two interlaces per context. The firewall has previously boon operating transparent mode. The Cisco Secure Firewall Throat Defense (FTD) device has been deregistered from Cisco Secure Firewall Management Center (FMC). Which set of configuration actions must the network engineer take next to meet the requirements?
An engineer is tasked with deploying an internal perimeter firewall that will support multiple DMZs Each DMZ has a unique private IP subnet range. How is this requirement satisfied?
Which two packet captures does the FTD LINA engine support? (Choose two.)
An analyst is investigating a potentially compromised endpoint within the network and pulls a host report for the endpoint in question to collect metrics and documentation. What information should be taken from this report for the investigation?
An engineer is configuring a Cisco Secure Firewall Threat Defence device managed by Cisco Secure Firewall Management Centre. The device must have SSH enabled and the accessible from the inside interface for remote administration. Which type of policy must the engineer configure to accomplish this?
An engineer is restoring a Cisco FTD configuration from a remote backup using the command restore remote-manager-backup location 1.1.1.1 admin /volume/home/admin BACKUP_Cisc394602314.zip on a Cisco FMG. After connecting to the repository, an error occurred that prevents the FTD device from accepting the backup file. What is the problem?
Refer to the exhibit.
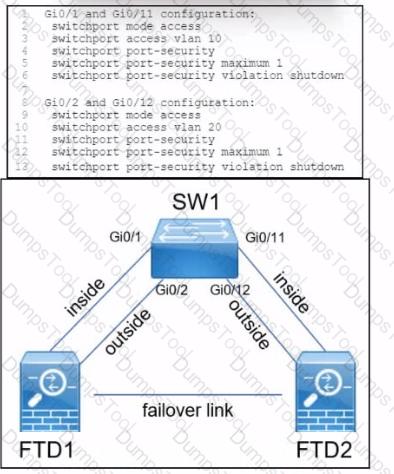
A company is deploying a pair of Cisco Secure Firewall Threat defence devices named FTD1 and FTD2. FTD1 and FTD2 have been configured as an active/standby pair with a failover link but without a stateful link. What must be implemented next to ensure that users on the internal network still communicate with outside devices if FTD1 fails?
What is a method used by Cisco Rapid Threat Containment to contain the threat in the network?
Which two dynamic routing protocols are supported in Firepower Threat Defense without using FlexConfig? (Choose two.)
Refer to the exhibit.
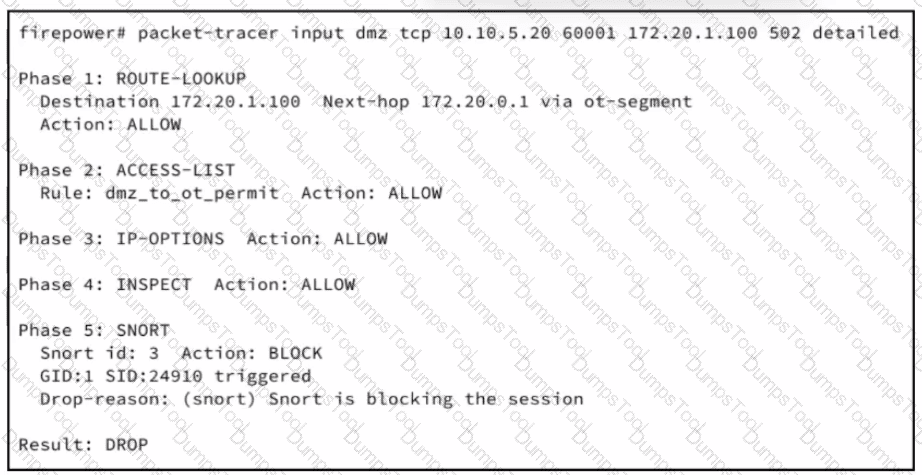
At a manufacturing facility, a historian server 10.10.5.20 in the OT DMZ is intermittently unable to reach a remote PLC at 172.20.1.100 on TCP 502 Modbus. A security engineer runs packet-tracer on Cisco Secure Firewall Threat Defence and captures the output. The access policy is verified as correct. Which action must be performed to resolve the issue?
TESTED 07 Nov 2026


