dumpstool logo
212-89 Question Includes: Single Choice Questions: 354, Fill in the Blanks: 2,
A multinational corporation with a diverse computing environment experiences a sophisticated malware attack targeting its endpoint devices. The malware is designed to evade traditional antivirus solutions and establish a persistent backdoor for data exfiltration. This incident underscores the complex landscape of endpoint security and the evolving threat vectors. In this context, what is the most critical reason for establishing a robust endpoint security incident handling and response capability?
Rachel, a first responder, finds a smartphone in an executive’s office that is powered ON and actively displaying a messaging app with potentially incriminating information. She avoids locking the screen or turning off the device, photographs the current display, and collects its charging cable. She then safely packages the device and ensures it is kept charged during transport. What principle is Rachel applying in her evidence handling approach?
A logistics company relying heavily on cloud-based inventory management discovered unauthorized activity initiated by a third-party contractor. The investigation revealed that the contractor ' s login was reused across multiple departments and lacked any tracking mechanism or role-specific restrictions to limit its scope. What cloud security best practice should be implemented to prevent such violations?
An employee at a pharmaceutical company loses their organization-issued mobile device while attending an international conference. The device contained access to corporate email, cloud storage apps, and internal communication tools. Upon being informed, the company’s incident response team attempts to take control of the device and protect sensitive data. However, they quickly discover that no centralized management setup or security controls had been established on the device, preventing them from locking the system or removing its stored information. Which preparation step would have enabled containment in this situation?
Smith employs various malware detection techniques to thoroughly examine the
network and its systems for suspicious and malicious malware files. Among all
techniques, which one involves analyzing the memory dumps or binary codes for the
traces of malware?
Customers Passed
ECCouncil 212-89
Average Score In Real
Exam At Testing Centre
Questions came word by
word from this dump
DumpsTool Practice Questions provide you with the ultimate pathway to achieve your targeted ECCouncil Exam 212-89 IT certification. The innovative questions with their interactive and to the point content make your learning of the syllabus far easier than you could ever imagine.
DumpsTool Practice Questions are information-packed and prove to be the best supportive study material for all exam candidates. They have been designed especially keeping in view your actual exam requirements. Hence they prove to be the best individual support and guidance to ace exam in first go!
ECCouncil ECIH 212-89 PDF file of Practice Questions is easily downloadable on all devices and systems. This you can continue your studies as per your convenience and preferred schedule. Where as testing engine can be downloaded and install to any windows based machine.
DumpsTool Practice Questions ensure your exam success with 100% money back guarantee. There virtually no possibility of losing ECCouncil ECIH 212-89 Exam, if you grasp the information contained in the questions.
DumpsTool professional guidance is always available to its worthy clients on all issues related to exam and DumpsTool products. Feel free to contact us at your own preferred time. Your queries will be responded with prompt response.
DumpsTool tires its level best to entertain its clients with the most affordable products. They are never a burden on your budget. The prices are far less than the vendor tutorials, online coaching and study material. With their lower price, the advantage of DumpsTool 212-89 EC Council Certified Incident Handler (ECIH v3) Practice Questions is enormous and unmatched!
The EC-Council 212-89 exam, also known as the Certified Incident Handler (ECIH v3) exam, validates a candidate’s ability to effectively manage and respond to cybersecurity incidents. It focuses on structured incident response processes, malware handling, email security, network-level incidents, and application-level threats.
The 212-89 exam is ideal for cybersecurity professionals such as SOC analysts, incident responders, forensic investigators, and IT security managers. It is recommended for individuals with at least one year of experience in cybersecurity or IT security.
Key domains include:
Incident Handling & Response Process
First Response procedures
Malware Incident Handling
Email Security Incidents
Network-Level Incidents
Application-Level Incidents
The exam consists of 100 multiple-choice questions to be completed in 180 minutes. The passing score is 70%.
The official ECCouncil 212-89 exam fee is $449 USD, though training providers may offer bundled packages with discounts.
On average, candidates spend 6 to 8 weeks preparing, depending on prior experience. Using 212-89 practice questions and PDF guides accelerates readiness.
Yes, Dumpstool provides a money-back guarantee under specific conditions. If a candidate fails the ECIH exam after preparing with our 212-89 study materials, they can apply for a refund by following the terms and providing valid proof of failure.
Yes, we frequently offers discounts on our 212-89 study materials, making it affordable for students and professionals. These discounted packages include complete access to 212-89 PDF questions and testing engine.

 Irene J.posted on 21-Sep-2026
Thanks dumpstool.com for opening the doors of success for me. I will remain always grateful to you for reviving my professional life. The 212-89 exam was a ditto copy of what I learnt in your given pdf. EC Council Certified Incident Handler (ECIH v3) certificate enhanced my CV.
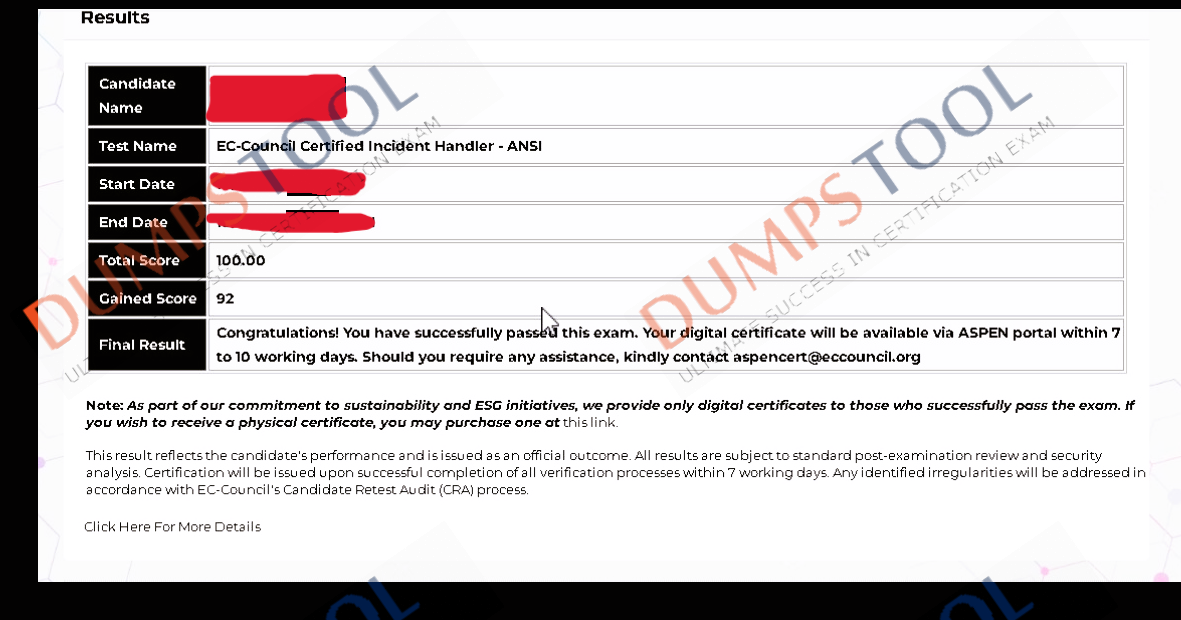
Fresh exam score sheets highlighting the real-world success rate of our platform's training.
TESTED 15 Oct 2026