Weekend Sale - Special 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 75onlydt

GH-600 Questions and Answers

Question # 6

You need to resolve the scoping issue associated to agent1.

What should you do?

A.

To the profile of agent1, add a custom instruction specifying that the agent must NOT access billing-service or infra-terraform.

B.

Add a permissions block to the agent1 workflow in product-api.

C.

Create a fine-grained personal access token (PAT) scoped to product-api and store the PAT as a GitHub Actions secret for agent1 to use.

D.

Create a ruleset for billing-service and infra-terraform that blocks push access from the github-actions bot account.

Full Access
Question # 7

Before App1 is upgraded, you need to verify each individual upgrade step and whether all tests have passed.

Which file should you use?

A.

< project > /.mcp/agent.md

B.

< project > /.github/plan.md

C.

< project > /.github/upgrades/{scenarioId}/assessment.md

D.

< project > /.github/upgrades/{scenarioId}/tasks.md

Full Access
Question # 8

You need to provide access to the API key of MCP1. The solution must meet the security requirements.

What should you do?

A.

Store the API key as a secret in the Copilot environment of product-api by using a name prefix of COPILOT_MCP_, and then reference the variable name in the mcp.json configuration.

B.

In the product-api repository settings, add the API key directly to the .mcp/server.json file by using a plaintext apiKey field.

C.

Store the API key as a GitHub Codespaces user secret scoped to product-api.

D.

In product-api, add the API key as a GitHub Actions encrypted secret and reference the secret by using ${{ secrets.KEY }} in the workflow YAML of agent1.

Full Access
Question # 9

You have multiple GitHub Copilot coding agents that run tasks concurrently.

You live stream the session log output and see the following.

• agent execution (ID 987654321)

Run ./scripts/agent-run.sh

--------------------------------

[agent] Starting task: Clean up infra configs

[agent] Executing step: Remove unused files

rm -rf /infra

Error: Command blocked by policy

Reason: destructive_operation_detected

[agent] Escalating to human review...

X Run agent task

X Process completed with exit code 1

X agent-execution failed

What is a possible cause of the error?

A.

a preToolUse hook

B.

a postToolUse hook

C.

a Copilot firewall policy

D.

a GitHub app installation policy

Full Access
Question # 10

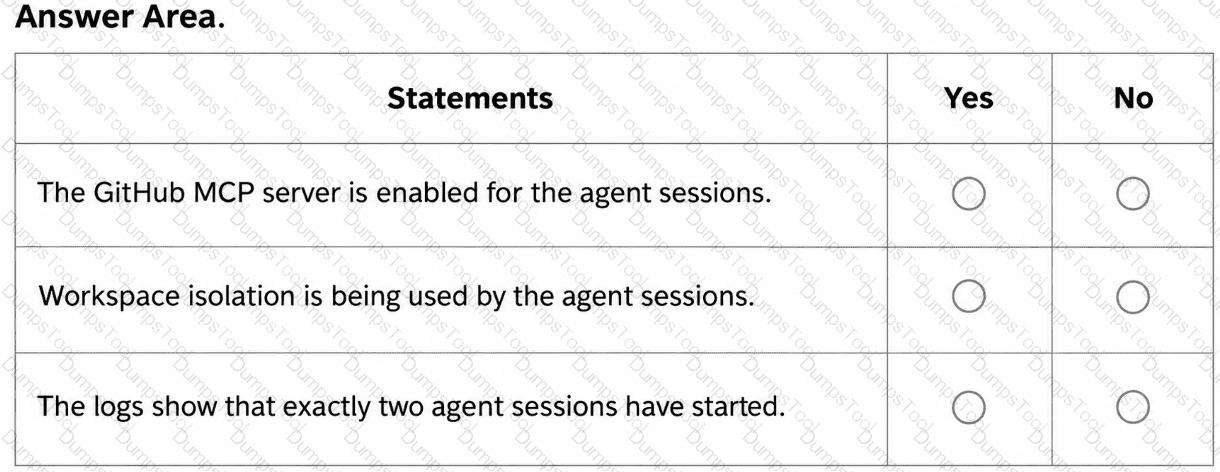
You are evaluating the logs of the multi-agent workflow in repo2.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.

NOTE: Each correct selection is worth one point.
Question # 10

Full Access
Question # 11

You have a GitHub repository that uses the GitHub Copilot coding agent to run agent plans for assigned issues.

You discover that some issues contain ambiguous implementation steps.

You need to reduce the likelihood that Copilot executes plans based on ambiguous implementation steps.

What should you do?

A.

Add comments to the issues after assigning the issues to the agent.

B.

Add acceptance criteria and directions to the issues before assigning the issues to the agent.

C.

Add a copilot-setup-steps.yml file to preinstall dependencies in the agent environment.

D.

Mention @copilot in a pull request comment to request changes after the plan runs.

Full Access
Question # 12

You need to configure agent1 to support the planned changes.

What should you do?

A.

Add Use all available tools to the instructions in the agent configuration.

B.

Add the mcp-servers property to the agent configuration.

C.

In the agent configuration, replace line 05 with the following: tools: []

D.

Add Use all available tools to the .github/copilot-instructions.md file.

E.

Delete line 05 from the agent configuration.

Full Access
Question # 13

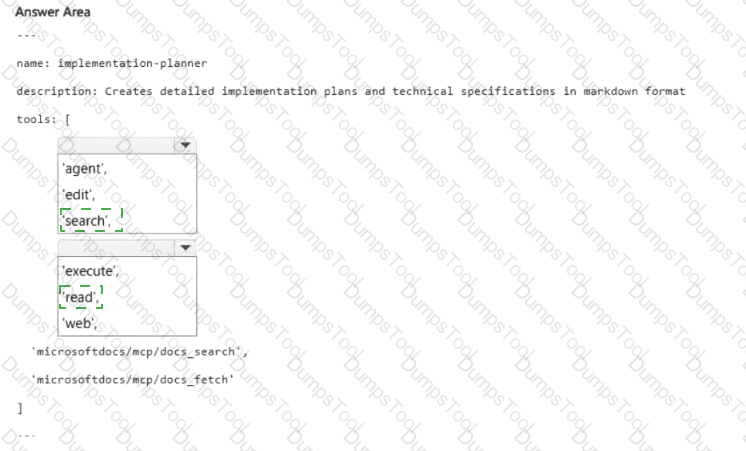
You need to implement agent2 to meet the technical requirements.

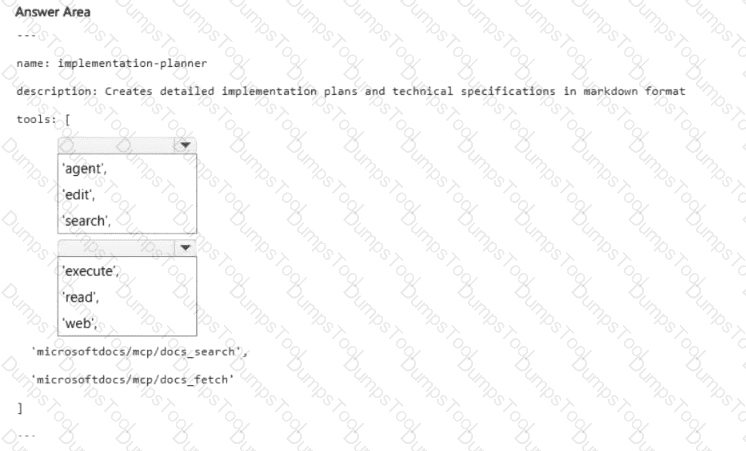
How should you complete the YAML configuration? To answer, select the appropriate options in the answer area.

NOTE: Each correct selection is worth one point.

HOTSPOT

name: implementation-planner

description: Creates detailed implementation plans and technical specifications in markdown format

tools: [

< Dropdown 1 > ,

< Dropdown 2 > ,

' microsoftdocs/mcp/docs_search ' ,

' microsoftdocs/mcp/docs_fetch '

]

The accompanying image includes empty dropdown controls and recreated practice alternatives.
Question # 13

Full Access
Question # 14

You need to troubleshoot the issue reported by Dev1.

What should you review?

A.

The GitHub Actions usage metrics of repo1.

B.

The agent session log in the Agents panel.

C.

The GitHub Actions runner log for the session job.

D.

The GITHUB_TOKEN permissions block in the agent1 workflow.

Full Access
Question # 15

While upgrading App1, the agent identifies 47 issues, including a security vulnerability, and 46 API incompatibilities across different projects.

Which two actions are unsafe to delegate to the agent and require human involvement? Each correct answer presents a complete solution.

NOTE: Each correct selection is worth one point.

A.

Generate the assessment.md file.

B.

Approve all Git commits.

C.

Validate whether the tasks.md file exists.

D.

Validate the assessment.md file for accuracy.

E.

Review the plan.md file for dependencies.

Full Access
Question # 16

You need to enable Copilot memory to support the planned changes.

What should you configure?
A.

The personal Copilot settings of each developer

B.

The Copilot settings of each repository

C.

The agent profile of agent1

D.

The Copilot settings of the organization

Full Access