Pre-Winter Sale - Special 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 70dumps

NSE7_CDS_AR-7.6 Questions and Answers

Question # 6

An administrator is trying to implement FortiCNP with Microsoft Azure Security integration. However, FortiCNP is not able to extract any cloud integration data from Azure; therefore, real-time cloud security monitoring is not possible.

What is causing this issue?

A.

The organization is using a free Azure AD license.

B.

The Azure account doesn ' t have the global administrator role.

C.

The administrator enabled the wrong defender plan for servers.

D.

The FortiCNP account in Azure has the Storage Blob Data Reader role.

Full Access
Question # 7

An administrator is looking for a solution that can provide insight into users and data stored in major SaaS applications in the multicloud environment. Which product should the administrator deploy to have secure access to SaaS applications? (Choose one answer)

A.

FortiSandbox

B.

FortiCASB

C.

FortiWeb

D.

FortiSIEM

Full Access
Question # 8

An administrator decides to use the Use managed identity option on the FortiGate SDN connector with Microsoft Azure. However, the SDN connector is failing on the connection.

What must the administrator do to correct this issue?

A.

Make sure to add the Client secret on FortiGate side of the configuration.

B.

Make sure to add the Tenant ID on FortiGate side of the configuration.

C.

Make sure to enable the system assigned managed identity on Azure.

D.

Make sure to set the type to system managed identity on FortiGate SDN connector settings.

Full Access
Question # 9

Refer to the exhibit.

Question # 9

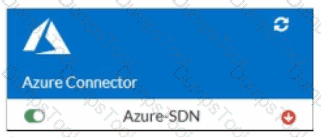
You are troubleshooting a Microsoft Azure SDN connector issue on your FortiGate VM in Azure.

Which command can you use to examine details about API calls sent by the connector?

A.

diag debug application cloud-connector -1

B.

diag test application azd 1

C.

diag debug application azd -1

D.

get system sdn-connector

Full Access
Question # 10

You are using Ansible to modify the configuration of several FortiGate VMs. What is the minimum number of files you need to create, and in which file should you configure the target FortiGate IP addresses?

A.

One playbook file for each target and the required tasks, and one inventory file.

B.

One .yaml file with the targets IP addresses, and one playbook file with the tasks.

C.

One inventory file for each target device, and one playbook file.

D.

One text file for all target devices, and one playbook file.

Full Access
Question # 11

Refer to the exhibit.

Question # 11

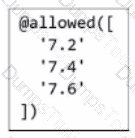
What is the purpose of this section of an Azure Bicep file?

A.

To restrict which FortiOS versions are accepted for deployment

B.

To indicate the correct FortiOS upgrade path after deployment

C.

To add a comment with the permitted FortiOS versions that can be deployed

D.

To document the FortiOS versions in the resulting topology

Full Access
Question # 12

Refer to the exhibit.

Question # 12

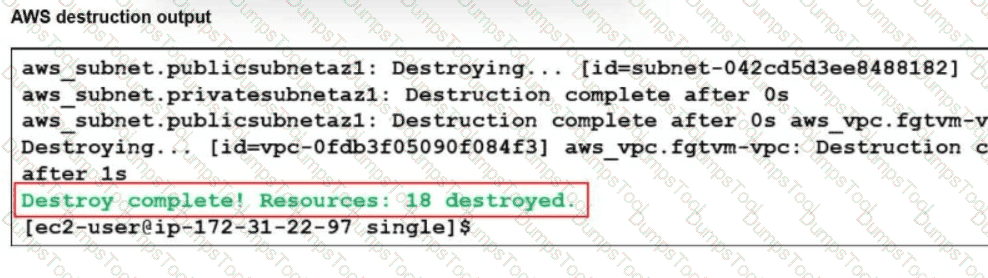
An administrator deployed a FortiGate-VM in a high availability (HA) (active/passive) architecture in Amazon Web Services (AWS) using Terraform for testing purposes. At the same time, the administrator deployed a single Linux server using AWS Marketplace.

Which two options are available for the administrator to delete all the resources created in this test? (Choose two.)

A.

The administrator must manually delete the Linux server.

B.

Use the terraform destroy all command.

C.

Use the terraform destroy command.

D.

Use the terraform validate command.

Full Access
Question # 13

Refer to the exhibit.

Question # 13

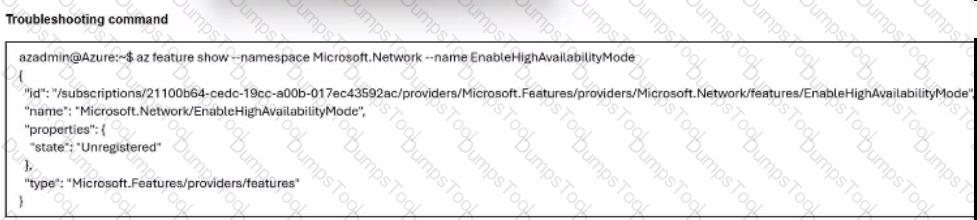
A managed security service provider (MSSP) administration team is trying to deploy a new HA cluster in Azure to filter traffic to and from a client that is also using Azure. However, every deployment attempt fails, and only some of the resources are deployed successfully. While troubleshooting this issue, the team runs the command shown in the exhibit.

What are the implications of the output of the command?

A.

The team will not be able to deploy an A-P FortiGate HA cluster with Azure gateway load balancer.

B.

The team will not be able to deploy an A-P FortiGate HA cluster with Azure load balancer.

C.

The team will not be able to deploy an active-passive (A-P) FortiGate high availability (HA) cluster with SDN connector.

D.

The team will not be able to deploy an active-active (A-P) FortiGate HA cluster with Azure load balancer.

Full Access
Question # 14

A Network security administrator is searching for a solution to secure traffic going in and out of the container infrastructure.

In which two ways can Fortinet container security help secure container infrastructures? (Choose two.)

A.

FortiGate NGFW can inspect north-south container traffic with label aware policies.

B.

FortiGate NGFW and FortiWeb can be used to secure container traffic.

C.

FortiGate NGFW can connect to the worker nodes and protect the containers.

D.

FortiGate NGFW can be placed between each application container for north-south traffic inspection.

Full Access
Question # 15

Refer to the exhibit.

Question # 15

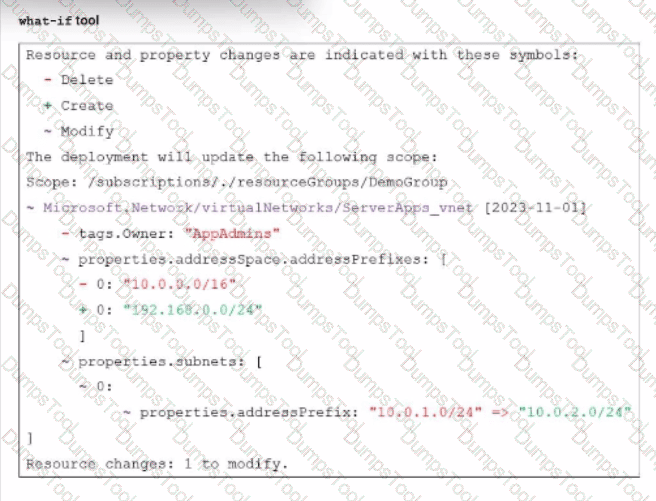
An administrator used the what-if tool to preview changes to an Azure Bicep file.

What will happen if the administrator decides to apply these changes in Azure?

A.

Subnet 10.0.1.0/24 will replace subnet 10.0.2.0/24.

B.

This deployment will fail and no changes will be applied.

C.

A new subnet will be added to ServerApps.

D.

The ServerApps VNet will be renamed.

Full Access
Question # 16

As part of your organization ' s monitoring plan, you have been tasked with obtaining and analyzing detailed information about the traffic sourced at one of your FortiGate EC2 instances.

What can you do to achieve this goal?

A.

Use AWS CloudTrail to capture and then examine traffic from the EC2 instance.

B.

Create a virtual public cloud (VPC) flow log at the network interface level for the EC2 instance.

C.

Add the EC2 instance as a target in CloudWatch to collect its traffic logs.

D.

Configure a network access analyzer scope with the EC2 instance as a match finding.

Full Access
Question # 17

An administrator is configuring a software-defined network (SDN) connector in FortiWeb to dynamically obtain information about existing objects in an Amazon Elastic Kubernetes Service (EKS) cluster.

Which AWS policy should the administrator attach to a user to achieve this goal?

A.

AmazonEKSConnectorServiceRolePolicy

B.

AmazonEKSComputePolicy

C.

AmazonEKSServicePolicy

D.

AmazonEKSClusterPolicy

Full Access
Question # 18

Refer to the exhibit.

Question # 18

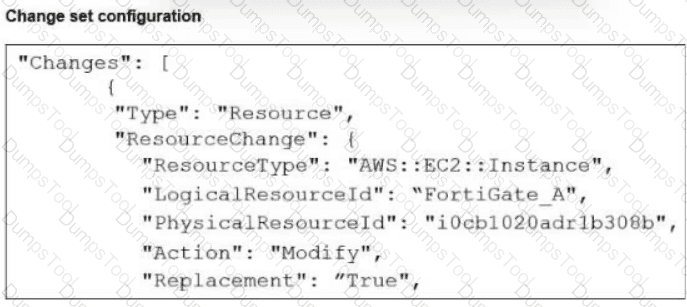
An AWS administrator created a change set to examine the effects of proposed changes to the current infrastructure.

Based only on the output shown in the exhibit, what will happen if the administrator applies these changes?

A.

The resulting FortiGate instance will lose its current local users.

B.

The deployment will take place without any service interruption.

C.

The PhysicalResourceId will remain the same.

D.

CloudFormation will roll back the current stack before updating it.

Full Access
Question # 19

What is the main advantage of using SD-WAN Transit Gateway Connect over traditional SD-WAN?

A.

You can use BGP over IPsec for maximum throughput.

B.

You can combine it with IPsec to achieve higher bandwidth.

C.

It eliminates the use of ECMP.

D.

You can use GRE-based tunnel attachments.

Full Access
Question # 20

You have onboarded the organization’s Microsoft Azure account on FortiCNAPP using the automated configuration approach. However, FortiCNAPP does not appear to be receiving any workload scanning data. How can you remedy this? (Choose one answer)
A.

Add a new Azure App Registration.

B.

Add a service principal in the Azure Cloud Shell.

C.

Add a FortiCNAPP threat policy to monitor Azure workloads.

D.

Add the appropriate integration type using the guided configuration.

Full Access