Weekend Sale - Special 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 75onlydt

NSE5_FSW_AD-7.6 Questions and Answers

Question # 6

Which statement about the quarantine VLAN on FortiSwitch is true?

A.

Quarantine VLAN has no DHCP server

B.

Users who fail 802.1X authentication can be placed on the quarantine VLAN.

C.

It is only used for quarantined devices if global setting is set to quarantine by VLAN.

D.

FortiSwitch can block devices without configuring quarantine VLAN to be part of the allowed VLANs.

Full Access
Question # 7

(Full question statement start from here)

How does enabling an IGMP snooping proxy on FortiSwitch help reduce the number of IGMP reports processed by the IGMP querier? (Choose one answer)

A.

By converting IGMP reports into broadcast packets to reach all VLAN members

B.

By converting IGMP traffic to unicast

C.

By suppressing duplicate IGMP reports within the VLAN

D.

By forwarding IGMP reports only when the first member joins and the last member leaves

Full Access
Question # 8

Refer to the exhibit.

Question # 8

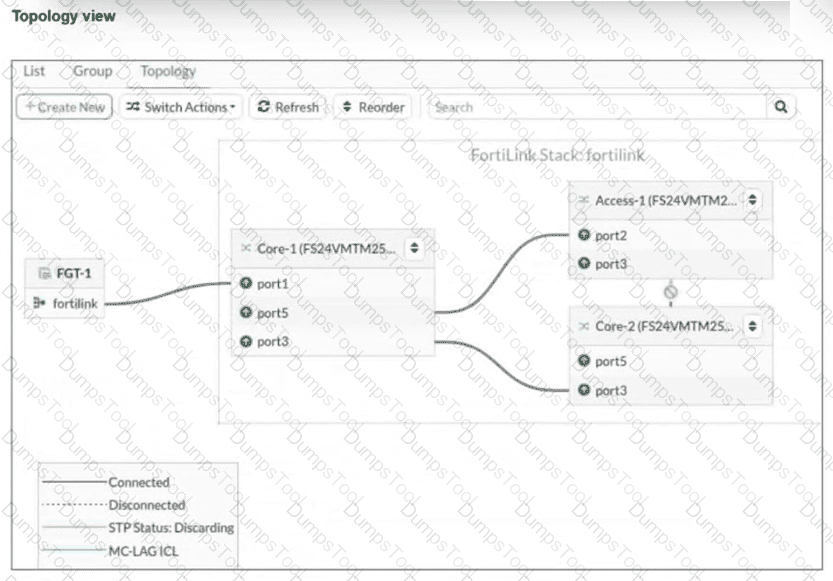
You just connected three FortiSwitch devices:Core-1,Core-2, andAccess-1. Core-1 and Core-2 both connect to Access-1 for redundancy. All switches are managed by FortiGate, which uses port4 as the FortiLink interface. After you enable the uplink ports on Core-2, you notice that port3 on Access-1 enters the Discarding STP state. What is the most likely cause of this behavior? (Choose one answer)

A.

Bridge Protocol Data Unit (BPDU) Guard is enabled, which shuts down the port after it receives BPDUs.

B.

Access-1 is not authorized by FortiGate.

C.

Core-2 has the lowest bridge priority.

D.

FortiGate is not running Spanning Tree Protocol (STP) on the FortiLink interface.

Full Access
Question # 9

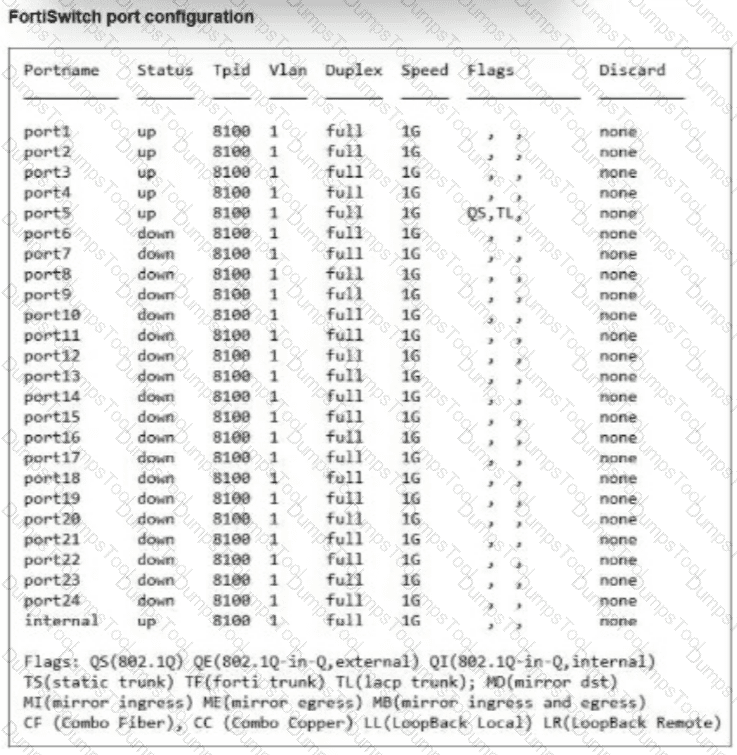
Exhibit.

port24 is the only uplink port connected to the network where access to FortiSwitch management services is possible. However, FortiSwitch is still not accessible on the management interface. Which two actions should you take to fix the issue and access FortiSwitch? (Choose two.)

A.

You must add port24 native VLAN as an allowed VLAN on internal.

B.

You must add VLAN ID 200 to the allowed VLANS on internal.

C.

You must allow VLAN ID 4094 on port24, if management traffic is tagged.

D.

You should use VLAN ID 4094 as the native VLAN on port24.

Full Access
Question # 10

What is the role of a device that is simultaneously functioning as both the distribution and core in the hierarchy network model?

A.

POE with high density FortiSwitch

B.

FortiGate managing FortiSwitch

C.

FortiSwitch functioning as standalone

D.

HA backup FortiGate managing FortiSwitch

Full Access
Question # 11

What happens when a routed VLAN interface (RVI) is configured on a FortiSwitch port or trunk? (Choose one answer)

A.

VLAN 1 is automatically assigned for management.

B.

The port becomes a layer 3 interface with VLAN 4095 assigned automatically.1

C.

All VLANs on the port are terminated in a trunk by default.

D.

The port becomes a layer 3 interface and assigned to VLAN 1.

Full Access
Question # 12

Which interfaces on FortiSwitch send out FortiLink discovery frames by default in order to detect a FortiGate with an enabled FortiLink interface?

A.

All ports have auto-discovery enabled by default.

B.

No ports are enabled by default for auto-discovery. This must be configured under config switch interface.

C.

The ports with auto-discovery enabled by default are dependent upon the FortiSwitch model.

D.

The last four switch ports on FortiSwitch have auto-discovery enabled by default.

Full Access
Question # 13

What are two reasons why time synchronization between FortiGate and its managed FortiSwitch is critical in switch management? (Choose two.)

A.

FortiSwitch does not retain its time after a reboot, which gets reset after each reboot.

B.

FortiSwitch will not be able to become an NTP server for downstream devices.

C.

FortiSwitch cannot complete the DTLS handshake used in the CAPWAP tunnel.

D.

FortiSwitch will not allow other FortiSwitch devices in the chain be discovered by FortiGate.

Full Access
Question # 14

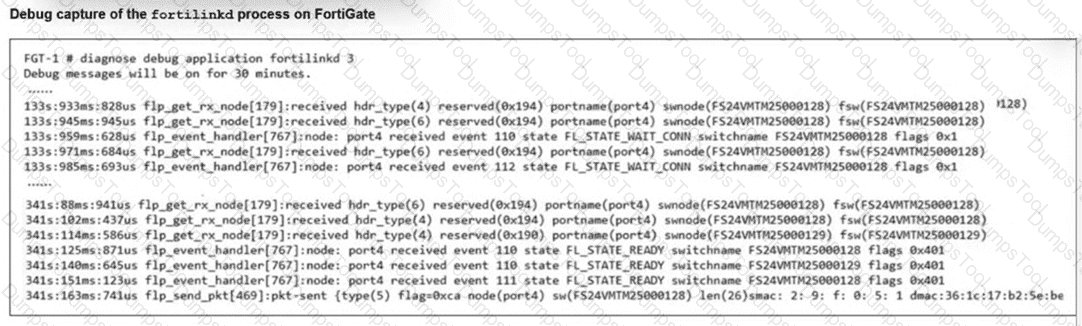
Refer to the exhibit.

Question # 14

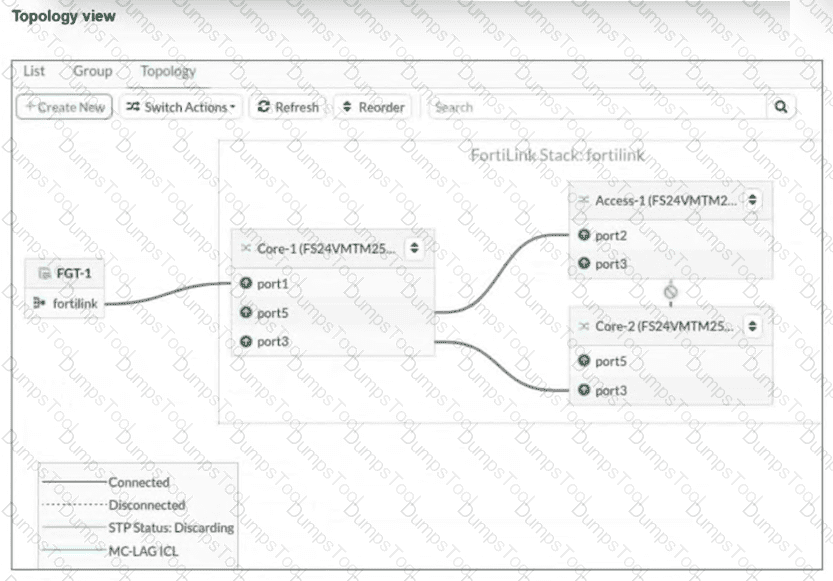
You just connected three FortiSwitch devices:Core-1,Core-2, andAccess-1. Core-1 and Core-2 both connect to Access-1 for redundancy. All switches are managed by FortiGate, which uses port4 as the FortiLink interface. After you enable the uplink ports on Core-2, you notice that port3 on Access-1 enters the Discarding STP state. What is the most likely cause of this behavior? (Choose one answer)

A.

Bridge Protocol Data Unit (BPDU) Guard is enabled, which shuts down the port after it receives BPDUs.

B.

Access-1 is not authorized by FortiGate.

C.

Core-2 has the lowest bridge priority.

D.

FortiGate is not running Spanning Tree Protocol (STP) on the FortiLink interface.

Full Access
Question # 15

How does FortiSwitch perform actions on ingress and egress traffic using the access control list (ACL)?

A.

Only high-end FortiSwitch models support ACL.

B.

ACL can be used only at the prelookup stage in the traffic processing pipeline.

C.

Classifiers enable matching traffic based only on the VLAN ID.

D.

FortiSwitch checks ACL policies only from top to bottom.

Full Access
Question # 16

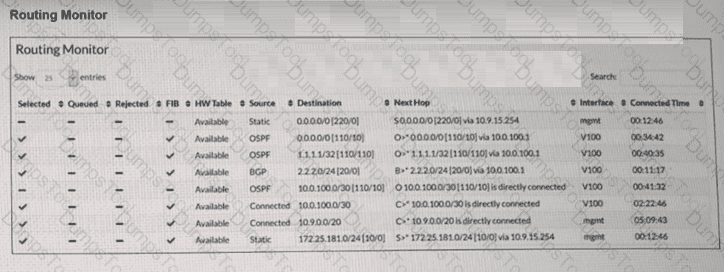
Refer to the exhibit.

Question # 16

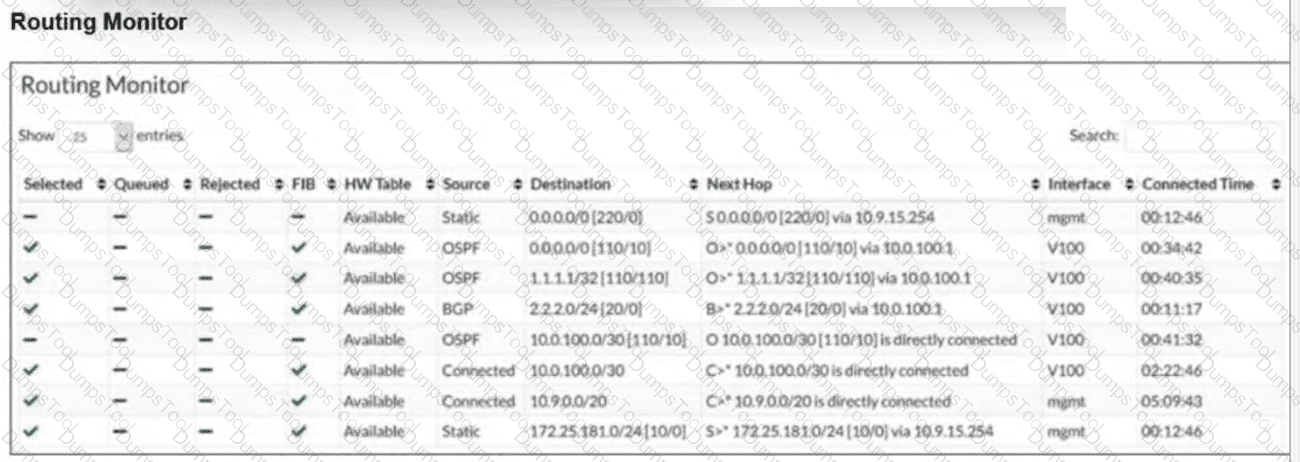
and an OSPF route with destination 0.0.0.0/0 [110/10]. The OSPF route is marked with a checkmark in the FIB column, while the Static route has a dash.]

The routing monitor displays multiple route entries, but only some are installed in the forwarding information base (FIB). After analyzing the two route entries with the destination 0.0.0.0/0, which statement correctly describe why one of these routes is not installed in the FIB? (Choose one answer)

A.

The OSPF route has a higher metric, making it less preferred than the static route.

B.

The interface V100 for the OSPF route is down, preventing its installation.

C.

The OSPF route with a lower administrative distance is preferred over the static route.

D.

The two routes have identical destination prefixes, causing a conflict where only one is selected.

Full Access
Question # 17

What type of multimode transceiver can be used to split a 40G port?

A.

QSFP+ transceiver

B.

SFP transceiver

C.

QSFP transceiver

D.

SFP+ transceiver

Full Access
Question # 18

Which statement about the configuration of VLANs on a managed FortiSwitch port is true?

A.

Untagged VLANs must be part of the allowed VLANs: ingress and egress.

B.

FortiSwitch VLAN interfaces are created only when FortiSwitch is managed by Forti-Gate.

C.

The native VLAN is implicitly part of the allowed VLAN on the port.

D.

Allowed VLANS expand the collision domain to the port.

Full Access
Question # 19

On supported FortiSwitch models, which access control list (ACL) stage is recommended for applying actions before the switch performs any layer 2 or layer 3 processing? (Choose one answer)

A.

Ingress

B.

Forwarding

C.

Egress

D.

Prelookup

Full Access
Question # 20

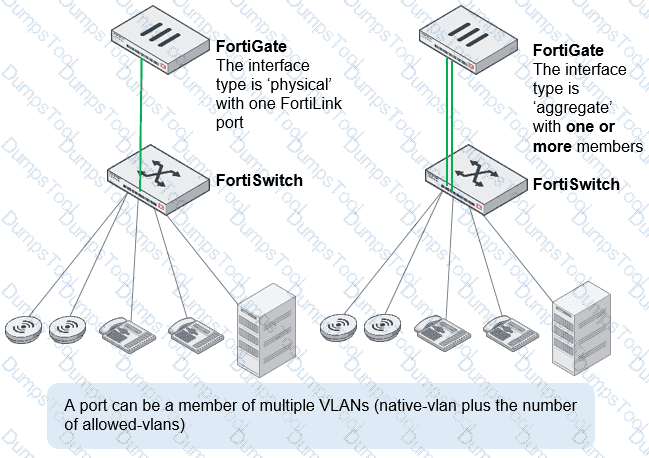
Refer to the exhibit.

Question # 20

You have just authorized a new FortiSwitch on your FortiGate, and it appears online in the GUI. To verify that FortiLink connectivity is healthy, what should you check next? (Choose one answer)

A.

Check that the switch automatically disables all unused ports.

B.

Look for FortiLink heartbeat messages sent from FortiSwitch to FortiGate every few seconds and confirm FortiGate acknowledges them.

C.

Verify that FortiGate has pushed a new firmware image to FortiSwitch immediately.

D.

Ensure the FortiSwitch is automatically sending log events to FortiAnalyzer.

Full Access
Question # 21

What can an administrator do to maintain a FortiGate-compatible FortiSwitch configuration when changing the management mode from standalone to FortiLinK?

A.

Use a migration tool based on Python script to convert the configuration.

B.

Enable the FortiLink setting on FortiSwitch before the authorization process.

C.

FortiGate automatically saves the existing FortiSwitch configuration during the FortiLink management process.

D.

Register FortiSwitch to FortiSwitch Cloud to save a copy before managing with FortiGate.

Full Access
Question # 22

(Full question statement start from here)

When you change FortiSwitch management mode fromstandalonetomanaged, what happens to the existing standalone configuration? (Choose one answer)

A.

FortiSwitch registers to FortiSwitch Cloud to save a copy before managing with FortiGate.

B.

FortiSwitch merges the existing standalone configuration with the default FortiLink configuration.

C.

FortiSwitch saves the standalone configuration and changes to the default FortiLink configuration.

D.

FortiGate automatically saves the existing FortiSwitch configuration during the FortiLink management process.

Full Access
Question # 23

(Full question statement start from here)

You are deploying a FortiSwitch virtual stack in a network that contains Cisco devices. You want the Cisco devices toautomatically discover the FortiSwitch devices and exchange device information. Which two protocols must be enabled on the FortiSwitch devices to achieve this? (Choose two answers)

A.

Unidirectional Link Detection

B.

Cisco Discovery Protocol

C.

Link Layer Discovery Protocol

D.

LLDP – Media Endpoint Discovery

Full Access
Question # 24

Refer to the exhibit.

Question # 24

You run the command diagnose switch physical-ports summary on FortiSwitch.

Based on exhibit, what does the output indicate to about the FortiSwitch mode? (Choose one answer)

A.

FortiSwitch is configured as access ports.

B.

FortiSwitch is configured as a layer 3 router.

C.

FortiSwitch is in standalone mode.

D.

FortiSwitch is operating in managed mode.

Full Access
Question # 25

You are deploying a new FortiSwitch device in a branch office and you want it to be automatically detected and managed by FortiGate. Which FortiSwitch feature enables automatic detection during deployment? (Choose one answer)

A.

Zero-touch deployment

B.

Auto-discovery

C.

Link Layer Discovery Protocol (LLDP)

D.

FortiLink heartbeat

Full Access
Question # 26

Refer to the exhibit.

Question # 26

Two routes in the routing monitor are marked as available but are not installed in the forwarding information base (FIB). Which statement correctly explains why the routes have this status? (Choose one answer)

A.

They are excluded from the FIB because a more preferred route exists for the same destination.

B.

They are unavailable due to invalid next-hop addresses.

C.

They are not included in the FIB due to route-policy filtering.

D.

They are installed in the FIB but cannot be offloaded to hardware.

Full Access
Question # 27

Which statement about using MAC, IP, and protocol-based VLANs on FortiSwitch is true?

A.

lt is a scalable and secure solution in comparison to other Layer 2 security measures.

B.

FortiSwitch uses only the Ethernet type to assign traffic to VLANs.

C.

It provides benefits that can be obtained when using 802.1X authentication.

D.

Endpoints are required to use the same FortiSwitch port to remain members of the VLAN.

Full Access
Question # 28

(Full question statement start from here)

Refer to the exhibit.
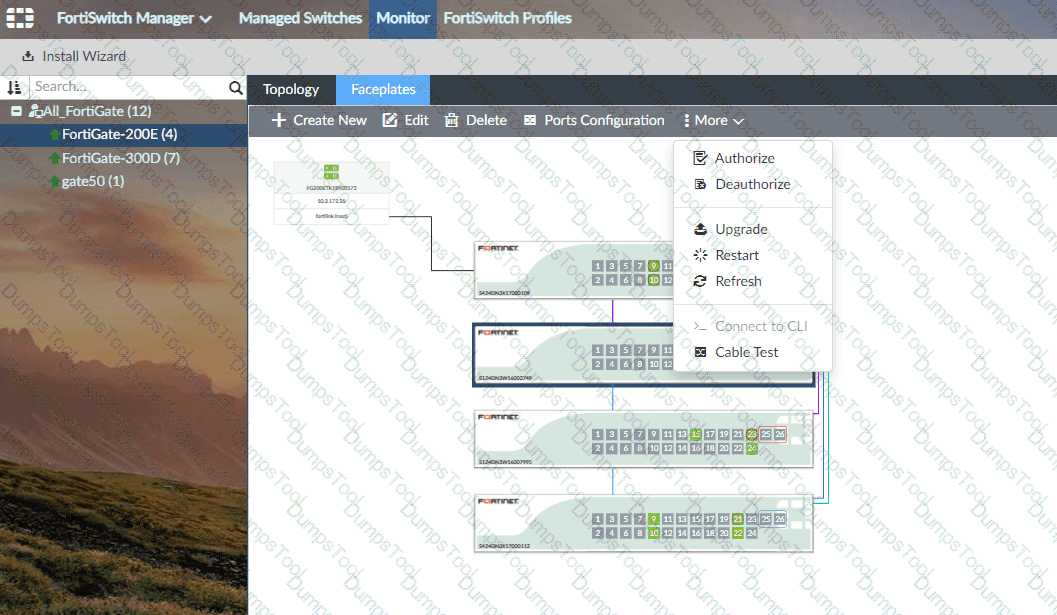
Question # 28

Question # 28

Question # 28

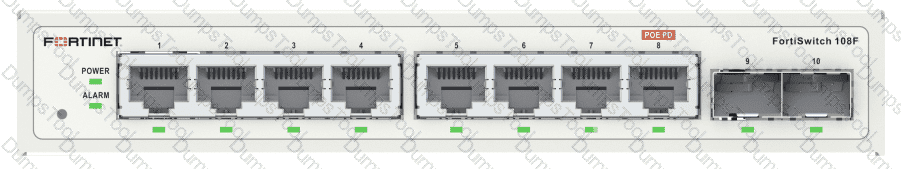
Which information does FortiGate use to generate the port details in the FortiSwitch Faceplates view? (Choose one answer)

A.

The FortiSwitch model

B.

The Cisco Discovery Protocol (CDP) advertisements from FortiSwitch

C.

The LLDP advertisements received from the FortiSwitch

D.

The FortiLink discovery frames sent by FortiSwitch

Full Access
Question # 29

Which is a requirement to enable SNMP v2c on a managed FortiSwitch?

A.

Create an SNMP user to use for authentication and encryption.

B.

Specify an SNMP host to send traps to.

C.

Enable an SNMP v3 to handle traps messages with SNMP hosts.

D.

Configure SNMP agent and communities.

Full Access
Question # 30

An administrator needs to deploy managed FortiSwitch devices in a remote location where multiple VLANs must be utilized to segment devices. No Layer 3 switch or router is present. The the only WAN connectivity is the router provided by the ISP connected to the public internet.

Which two items will the administrator need to use? (Choose two.)

A.

A FortiSwitch interface connected to the ISP router configured with fortilink-13-mode enabled.

B.

FortiSwitch and FortiGate devices configured with VXLAN interfaces.

C.

FortiSwitch devices configured with NAT disabled.

D.

FortiSwitch devices that have the required internal hardware for this configuration.

E.

FortiSwitch and FortiGate devices configured with IPsec interfaces.

Full Access
Question # 31

Which statement about the IGMP snooping querier when enabled on a VLAN is true?

A.

Active multicast receiver entries are aging on each IGMP query sent on the VLAN

B.

IGMP reports on the VLAN are forwarded to all switch ports.

C.

The setting can only be enabled using the FortiSwitch CLI.

D.

All other indirectly connected switches will be unable to get IGMP multicast traffic.

Full Access
Question # 32

Refer to the exhibit.

Question # 32

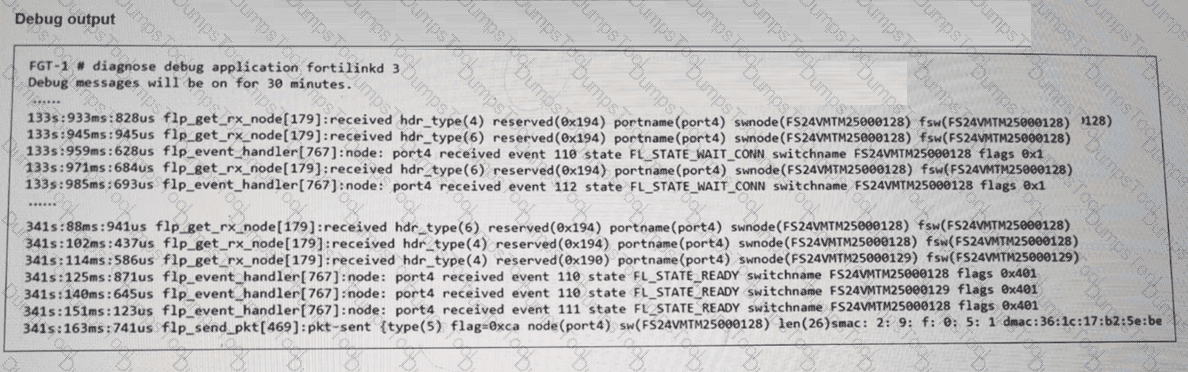
A periodic heartbeat message sent from a managed FortiSwitch and corresponding acknowledgments from FortiGate is shown. What does this behavior indicate? (Choose one answer)

A.

The FortiLink connection between FortiGate and FortiSwitch is healthy and active.

B.

FortiGate is unable to establish a FortiLink session with FortiSwitch.

C.

FortiSwitch is expecting an authorization from FortiGate.

D.

FortiSwitch has not been authorized yet.

Full Access
Question # 33

How does FortiGate handle configuration of flow tracking sampling if you export the settings to a managed FortiSwitch stack with sampling mode set to perimeter is true?

A.

FortiGate configures FortiSwitch to perform ingress sampling on all switch interfaces.

B.

FortiGate configures FortiSwitch to perform ingress sampling on all switch interfaces, except ICL and ISL interfaces.

C.

FortiGate configures and enables flow sampling on FortiSwitch but does not change existing sampling settings of interfaces.

D.

FortiGate configures and enables egress sampling on all management interfaces.

Full Access
Question # 34

Which two requirements must be met before FortiGate can manage a FortiSwitch stack? (Choose two answers)
A.

The latest FortiOS and FortiSwitchOS versions must be running.

B.

The switch controller feature must be enabled.

C.

All existing FortiLink interfaces must be disabled.

D.

The FortiSwitchOS version must be compatible with FortiOS.

Full Access