dumpstool logo

Several employees report that the company intranet website is no longer accepting their login credentials.
You attempt to access the site using its URL and notice several misspellings on the webpage. However, when you access the site directly using its IP address, it functions normally.
What should you do?
Which two private IPv4 addresses would be blocked on the Internet to prevent security and performance issues? (Choose two.)
Note: You will receive partial credit for each correct selection.
Which wireless encryption technology requires AES to secure home wireless networks?
Which security measure can prevent unauthorized devices from automatically connecting to a corporate network through unused switch ports?
An employee accidentally sends an email containing sensitive corporate information to an external email address.
Which type of threat does this scenario describe?
Your supervisor suspects that someone is attempting to gain access to a Windows computer by guessing user account IDs and passwords. The supervisor asks you to use the Windows Event Viewer security logs to verify the attempts.
Which two audit policy events provide information to determine whether someone is using invalid credentials to attempt to log in to the computer? (Choose 2.)
Note: You will receive partial credit for each correct selection.
Several employees complain that the company intranet site is no longer accepting their login information. You attempt to connect using the URL and notice some misspellings on the site. When you connect using the IP address, the site functions normally.
What should you do?
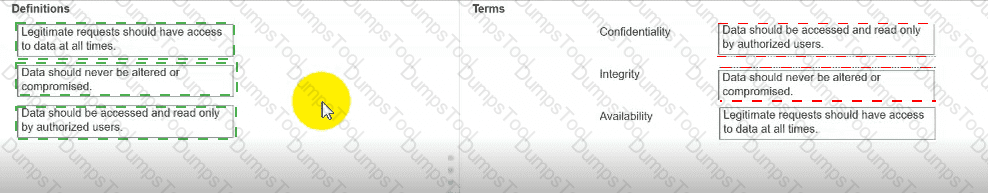
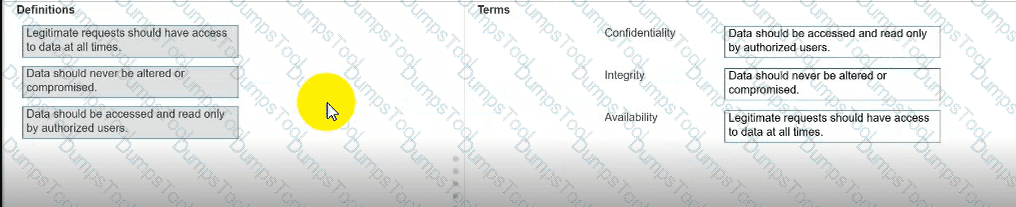
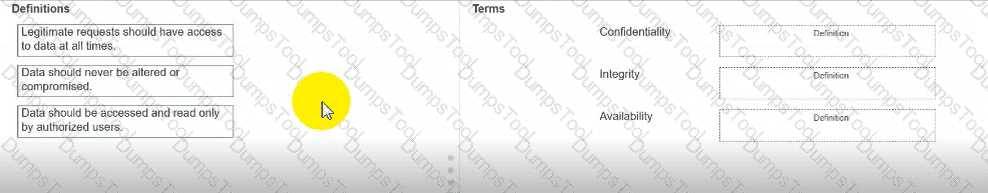
Move each definition from the list on the left to the correct CIA Triad term on the right.
Note: You will receive partial credit for each correct answer.
A security assessment reveals that a system administrator accessed files outside normal working hours. The assessment identifies the commands executed and records how long the administrator was connected to the system.
Which AAA component does this represent?
A client cannot connect to the corporate web server. You discover a large number of half-open TCP connections to the server.
What should you do?
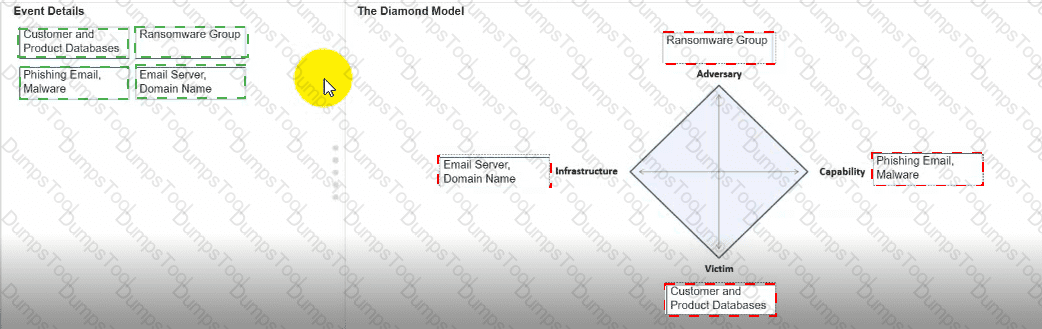
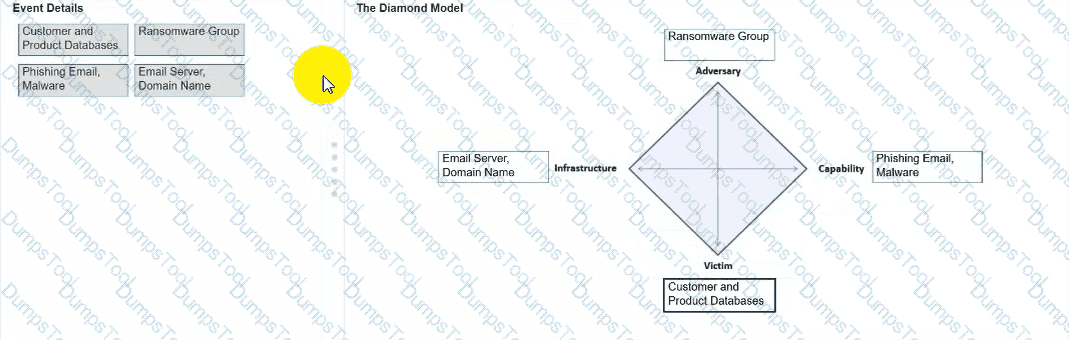
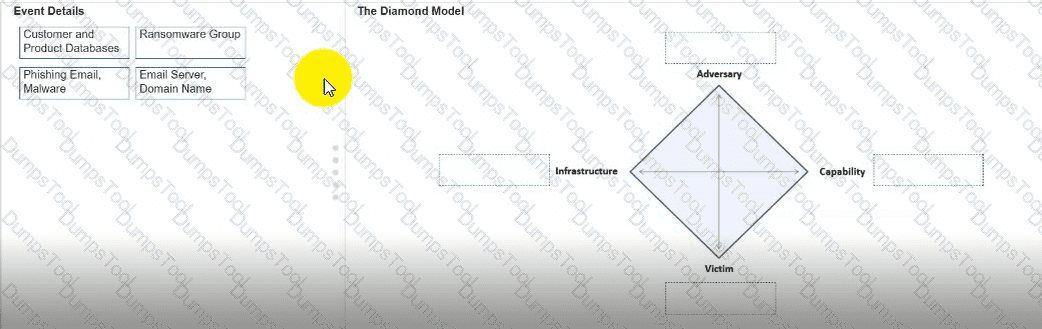
You need to diagram an intrusion event by using the Diamond Model.
Move each event detail from the list on the left to the correct location in the diagram on the right.
Note: You will receive partial credit for each correct response.

TESTED 22 Nov 2026