Pre-Winter Sale - Special 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 70dumps

CCAR-P Questions and Answers

Question # 6

A document analysis service processes legal filings averaging 80,000 tokens each. Each filing is queried by attorneys an average of 14 times during a case. The current architecture sends the full filing on every query. The CFO has asked you to reduce per-query costs while preserving response quality. The security officer requires that filing contents not be stored outside Fabrikam ' s tenancy.

Which optimization approach should you recommend?

A.

Summarize each filing once at intake and run all subsequent queries against the summary.

B.

Cache the filing as the prompt prefix for reuse across the 14 queries per case.

C.

Index filings in a vector store and retrieve only the relevant passages per query.

D.

Move the workload to a smaller Claude model to reduce the per-token cost paid.

Full Access
Question # 7

Engineering leadership wants to roll out Claude Skills to 280 developers across 14 teams. Skills will encode internal coding standards, code-review checklists, and incident-postmortem templates. Leadership has asked how to govern Skill authorship so that Skills remain trustworthy without bottlenecking on a single central team.

Which governance model should you recommend?

A.

Per-developer authorship across the 280 engineers with no team-level coordination required.

B.

Centralized authorship by a single platform team responsible for every Skill produced.

C.

Fully decentralized authorship across the 14 teams with no review before publication.

D.

Federated authorship across the 14 teams with a central review and publication gate.

Full Access
Question # 8

You are building an ethics review checklist for deployments supported by artificial intelligence (AI). Which two checks belong on the list? (Select two.) Each correct answer presents a complete solution.

A.

Confirm that vendor licensing terms permit the planned production use of the model.

B.

Confirm that high-impact decisions retain human accountability rather than being attributed to the model.

C.

Restrict the ethics review to outputs that exceed a defined model-confidence threshold.

D.

Confirm that latency and throughput targets are met across the supported user populations.

E.

Verify that outputs do not rely on generalizations about people that the underlying data does not support.

Full Access
Question # 9

You are reviewing a peer’s draft architecture decision record (ADR). The ADR states the decision and the technical detail but does not state the alternatives considered or the trade-offs accepted.

Which response is most appropriate?

A.

Delete the ADR entirely and rely on the engineering team’s collective memory to reconstruct the decision context, alternatives, and trade-offs during future audits or onboarding.

B.

Ask the author to add the alternatives considered and the trade-offs accepted before publishing the ADR.

C.

Approve the ADR as written on the grounds that the decision itself is documented, accepting that reviewers and future maintainers will lack the context to evaluate or revisit it.

D.

Replace the ADR with a different decision unrelated to the one drafted.

Full Access
Question # 10

The compliance team has authored a regulatory disclosure procedure that must be applied identically across customer service, sales, and onboarding workflows. The procedure changes when regulators issue updates, currently four to six times per year. You are designing how the procedure will be packaged for use by Claude across all three workflows.

Which two design decisions should you include? (Select two.)

Each correct answer presents part of the solution.

A.

Package the procedure as a Claude Skill owned directly by the compliance team.

B.

Embed the procedure text into each workflow’s system prompt at integration time.

C.

Store the procedure in a shared retrieval corpus accessed by all three workflows.

D.

Have each workflow team rewrite the procedure for its own context.

E.

Reference the same Claude Skill from all three workflow integrations.

Full Access
Question # 11

You are diagnosing a Claude Code session whose subagent uses 50,000 tokens of context before the engineer types a single message.

Which root cause is most likely?

A.

The developer ' s keyboard layout or input-method configuration is the cause of the elevated context consumption, introducing extra tokens before the engineer types any message.

B.

Many MCP servers are configured, each contributing tool definitions to the context budget; Tool Search is not enabled, so all definitions load upfront.

C.

The model has internal personal preferences or default behaviors that silently consume large portions of context budget before any user message is processed, independent of tool configuration.

D.

The font rendering or display-scaling settings of the IDE are converting visual output into additional context tokens, causing the high pre-session context consumption.

Full Access
Question # 12

You are listing characteristics of robust guardrail design for an enterprise deployment.

Which two characteristics belong on the list? (Select two.)

Each correct answer presents a complete solution.

A.

Centralized log retention for guardrail violations with quarterly review by the security team.

B.

Per-role tool allow-lists enforced at the orchestration layer before any tool call executes.

C.

User feedback channels that route reported guardrail failures into the product backlog for triage.

D.

Periodic refresh of the system prompt wording to keep refusal language current and clear.

E.

Adversarial-input coverage in the evaluation set with regression tracking on guardrail performance.

Full Access
Question # 13

A senior architect is preparing briefing materials on a new retrieval architecture. The executive sponsor has requested a summary of the architectural decision. Which framing is most appropriate for that audience?

A.

Technical alternatives evaluated, implementation implications, and component-level consequences.

B.

Business outcomes achieved, trade-offs accepted, and high-level risks acknowledged.

C.

Capabilities delivered, scope implications, and feature-level dependencies on the roadmap.

D.

Threat model, control mappings, residual-risk acceptance, and audit traceability.

Full Access
Question # 14

You are running a discovery engagement for a new Claude-based capability and must complete the requirements-gathering steps before validating with stakeholders.

Which two steps must be completed BEFORE validating the captured requirements with stakeholders? (Select two.)

Each correct answer presents part of the solution.

A.

Produce architecture decision records that capture the rationale for major design choices.

B.

Capture the business goals, success criteria, and the in-scope user population for the engagement.

C.

Document the consolidated requirements with traceability to the source stakeholder for each item.

D.

Schedule the rollout milestones and dependencies with engineering and product partners.

E.

Identify the non-functional constraints covering latency, cost, audit, data sensitivity, and regulatory needs.

Full Access
Question # 15

You are designing a test strategy for a Claude-based pipeline that handles sensitive financial data.

Which two test types should be prioritized to cover both safety under attack and cross-component correctness? (Select two.)

A.

Adversarial tests using prompt-injection and malformed-input cases.

B.

Regression tests against a stable reference set of previously known-good outputs.

C.

Smoke tests that verify core paths after each deployment.

D.

Integration tests that verify end-to-end pipeline behavior across all components.

E.

Unit tests targeting only individual prompt-template rendering logic.

Full Access
Question # 16

You are reviewing a peer’s draft system prompt that contains contradictory instructions: one section says never to speculate beyond the supplied source, while another says to confidently fill in any gaps.

Which response is most appropriate?

A.

Add a priority instruction directing the model to evaluate all instructions and apply whichever appears most contextually appropriate on each request.

B.

Remove or rewrite the gap-filling instruction so the prompt consistently constrains the model to source-supported content.

C.

Increase temperature so output randomness masks the contradiction.

D.

Keep both instructions and rely on the model to decide which one to follow on each request.

Full Access
Question # 17

You are defining an SLA for a Claude-based assistant.

Which SLA definition is most operationally meaningful?

A.

A target tied to a stakeholder sentiment measure such as “the team feels satisfied,” which cannot be measured objectively or used to trigger a documented breach response.

B.

A measurable target with a defined metric, threshold, evaluation window, and consequence for breach—for example, “p95 per-request latency under 800 ms over a 28-day window.”

C.

A qualitative commitment such as “the system will be fast and reliable,” which names no metric, threshold, or evaluation window.

D.

A target that names the metric and threshold but omits the evaluation window and breach consequence, leaving compliance periods and remediation triggers undefined.

Full Access
Question # 18

You are defining when to introduce a project subagent versus relying on Claude Code ' s general capabilities.

Which scenario most directly justifies a dedicated subagent?

A.

The team has a recurring specialized task, such as database schema review, that requires a focused system prompt, narrow tool permissions, and a specific model selection across many sessions.

B.

The team has a one-time ad hoc question that will not recur and does not require a focused system prompt, narrow tool permissions, or dedicated model selection.

C.

The team has no recurring specialized tasks and uses Claude Code only for isolated general-purpose work that does not justify a dedicated system prompt or tool scope.

D.

The team wants every Claude Code interaction to use the same generic system prompt with no task-specific specialization, narrow tool permissions, or dedicated model selection.

Full Access
Question # 19

You are identifying the highest-impact optimization for a deployment whose token cost is dominated by a long, repeated system prompt and a large retrieved context per request.

Which optimization most directly targets the dominant cost driver?

A.

Increase retrieval depth on every request to maximize recall, worsening the dominant cost driver by adding more retrieved tokens per request rather than reducing them.

B.

Add additional repeated content to the system prompt to give the model more guidance.

C.

Move the long, repeated system prompt into a cacheable prefix and trim retrieved context to the spans relevant to each query.

D.

Switch every request to the heaviest available model to maximize output quality, accepting that higher per-request inference cost compounds rather than addresses the dominant cost driver.

Full Access
Question # 20

You are defining where human review must remain in a planned automated pipeline. Which placement reflects sound human-in-the-loop design?

A.

Place a human reviewer only after the irreversible action has already executed, making the review a post-hoc audit rather than a meaningful pre-action check or approval gate.

B.

Place a human reviewer between the model’s output and any high-impact, irreversible action, with explicit criteria for what the reviewer must check before approval.

C.

Place a human reviewer in the loop for a randomly selected sample of requests, without defining criteria for what the reviewer should check or which output categories require mandatory review.

D.

Remove all human review steps from the pipeline to maximize throughput, accepting that high-impact and irreversible actions will be taken without any human approval or oversight.

Full Access
Question # 21

You are integrating human review into a high-volume classification pipeline where reviewing every output is infeasible.

Which sampling strategy best balances throughput with quality oversight?

A.

No sampling, relying entirely on user complaints to reveal quality and safety problems after they affect users.

B.

Risk-stratified sampling that reviews all low-confidence and high-impact outputs and a smaller random sample of high-confidence routine outputs.

C.

Inverse sampling that reviews only high-confidence routine outputs and skips low-confidence and high-impact outputs.

D.

Universal review of every output regardless of confidence or throughput impact.

Full Access
Question # 22

You are a solution architect designing a Claude-based assistant with access to 60 internal tools across multiple business domains. Loading every tool definition on every request increases token usage and time to first response.

Which design pattern best addresses this issue without sacrificing capability breadth?

A.

Apply progressive tool discovery so a curated initial subset is exposed and additional tools are loaded on demand based on the task.

B.

Use a separate model call to summarize all 60 tool definitions before each user turn.

C.

Increase the maximum context length and load all 60 tool definitions on every request, accepting the higher token cost and latency as necessary for full capability.

D.

Hard-code a fixed set of five tools per request to reduce token usage, regardless of whether those tools are relevant to the current task.

Full Access
Question # 23

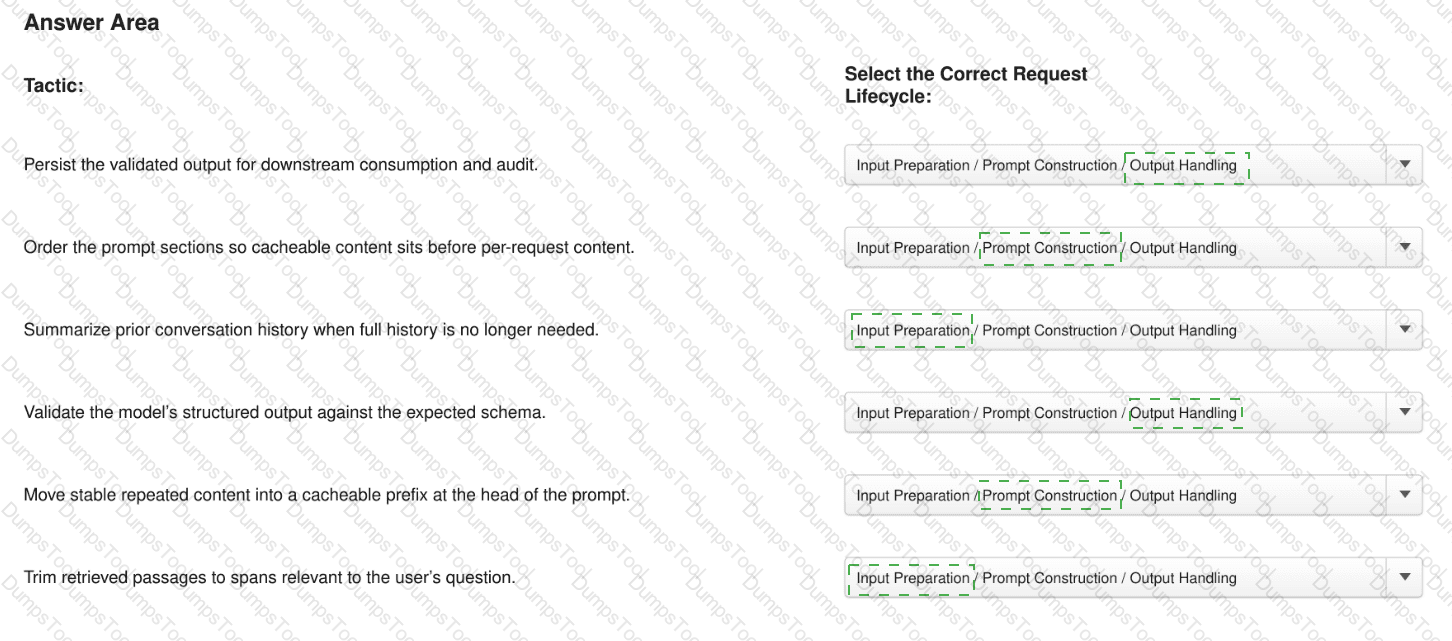
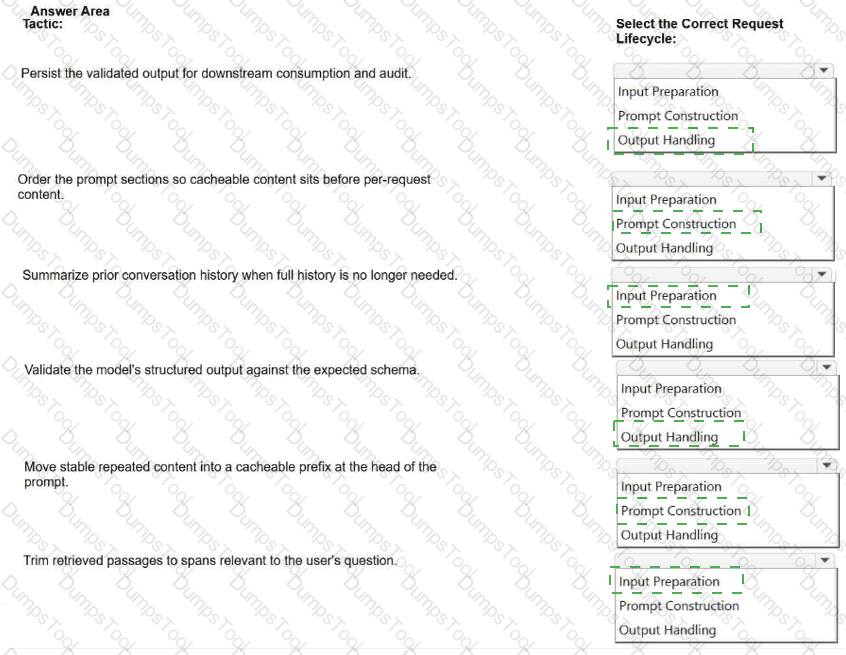
You are classifying token-management tactics by where each tactic applies in the request lifecycle: “Input Preparation,” “Prompt Construction,” or “Output Handling.”
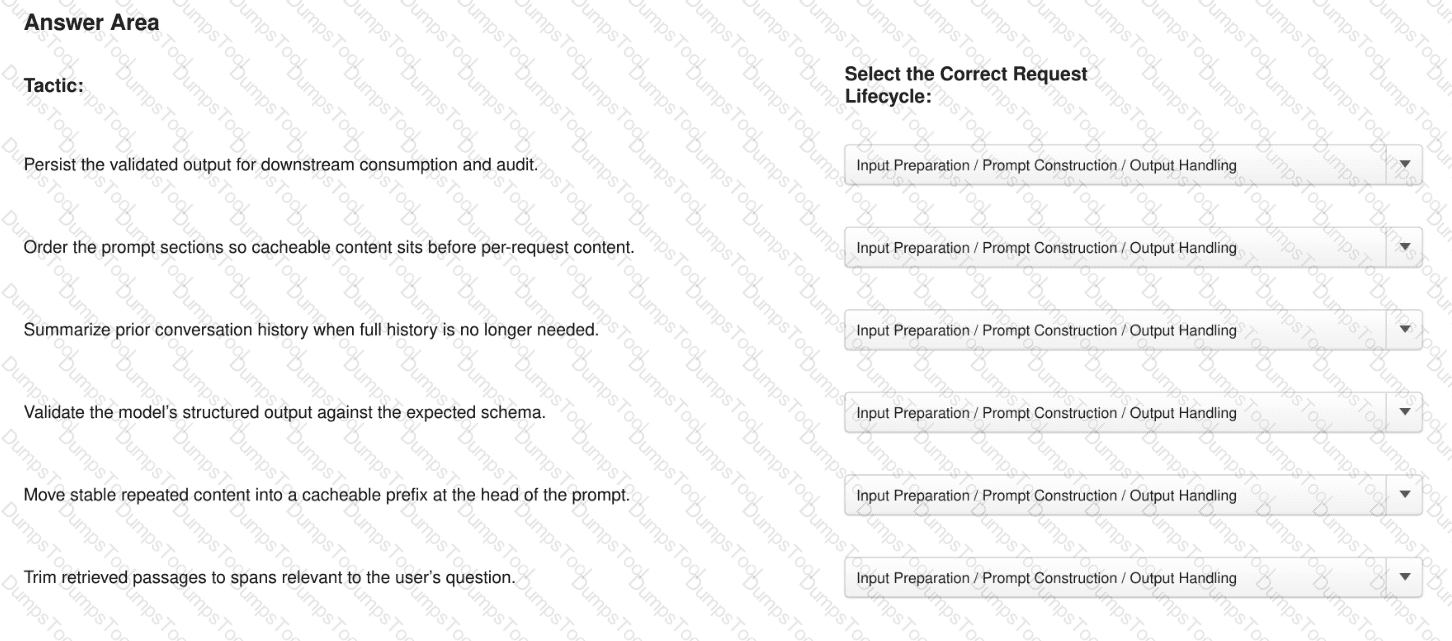
Question # 23

Full Access
Question # 24

An engineer inadvertently commits an API key to the repository by placing it in .claude/settings.json.

Which configuration design principle was violated?

A.

Project-scope configuration should always override user-scope configuration.

B.

Managed configuration must be applied before project-scope configuration is read.

C.

Credentials must be resolved at runtime from a secret store and never stored in version-controlled files.

D.

MCP server definitions must reside in environment variables to prevent scope conflicts.

Full Access
Question # 25

A platform team operates a self-hosted multi-agent system on Kubernetes that orchestrates seven specialized agents for invoice processing. The team spends approximately 40 percent of engineering capacity on infrastructure maintenance, message bus reliability, and agent state recovery. The CFO has asked you to evaluate moving to managed agent infrastructure to reclaim engineering capacity. The security officer requires that all customer financial data remain within an approved network boundary.

Which factor should most heavily influence your recommendation?

A.

Whether the current seven agents map cleanly to the patterns supported by managed agents.

B.

Whether managed agents reduce per-invoice token costs across the existing processing volume.

C.

Whether managed agents support the current bus topology used by the platform team.

D.

Whether managed agent data handling satisfies the network boundary required by security.

Full Access
Question # 26

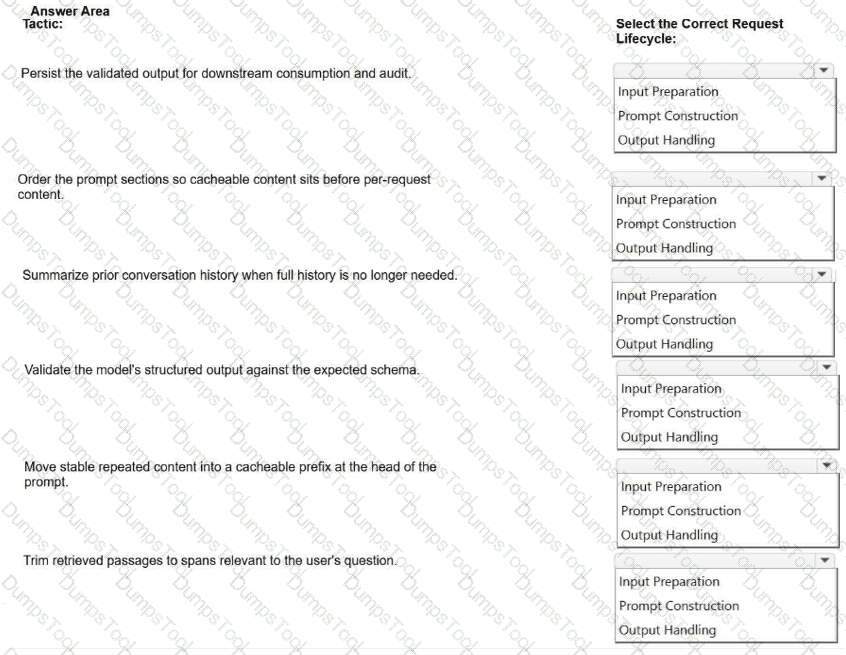
You are classifying token-management tactics by where in the request lifecycle each tactic applies.

For each tactic, select where in the request lifecycle it applies: Input Preparation , Prompt Construction , or Output Handling .
Question # 26

Full Access
Question # 27

A Claude Architect is reviewing a post-deployment performance report for an AI-assisted legal-document summarization system. The report includes these observations:

Average summarization time decreased from 47 minutes to 6 minutes per document.

Associates spend less time on summaries, but overall billable output has not measurably changed.

Infrastructure costs increased by 22% because redundant retry logic generated additional API calls.

Some summaries require attorney correction, adding an average of 8 minutes of review per document.

Which analysis correctly attributes each observation to the appropriate business-value pillar?

A.

Observations 1 and 2 both indicate efficiency gains; Observation 3 is a solution-cost issue; Observation 4 is a performance-SLA issue.

B.

Observation 1 is a transformation outcome; Observation 2 is an efficiency gain; Observation 3 is a performance-SLA degradation; Observation 4 is a solution-cost issue.

C.

Observations 1 and 4 together indicate a net performance-SLA improvement; Observation 2 is a transformation gap; Observation 3 is a productivity drain from over-engineering.

D.

Observation 1 indicates an efficiency gain; Observation 2 shows that productivity has not yet been realized; Observation 3 is a solution-cost issue; Observation 4 is an efficiency loss that partially offsets Observation 1.

Full Access
Question # 28

You are selecting a protocol for a single low-latency stateless tool call from a Claude-based assistant to an internal pricing service that already exposes a stable HTTP API.

Which integration mechanism is the most appropriate?

A.

A direct API call to the existing endpoint with the appropriate scoped credentials.

B.

A long-lived stateful session protocol for a stateless single-call interaction.

C.

A bespoke streaming protocol layered over an unrelated asynchronous message bus.

D.

An agent-to-agent handoff that introduces another Claude-based agent in front of the pricing service.

Full Access
Question # 29

You are reviewing instrumentation in a multi-agent system.

Which two findings constitute valid observability gaps in the instrumentation? (Select two.)

Each correct answer presents a complete solution.

A.

Trace spans for each agent step are exported to the shared distributed-tracing backend.

B.

Latency and token usage on every span are emitted to the central metrics pipeline.

C.

Tool-call payloads and outcomes are recorded with redaction applied to known sensitive fields.

D.

Model identity and version on each turn are not recorded with the turn artifacts.

E.

Request-scoped correlation identifiers do not propagate across agent and tool calls.

Full Access
Question # 30

A customer support team has proposed delegating customer refund decisions to a Claude-driven workflow with no human review for refunds under 50 USD. The team ' s reasoning is that small refunds are low-risk and human review would erase the efficiency gain.

Which Delegation-competency principle should guide your response?

A.

Delegation should always include human review on every decision the workflow produces.

B.

Delegation scope should reflect the type of risk involved, not the transaction size alone.

C.

Delegation scope should be set primarily by maximizing efficiency gains across the workflow.

D.

Delegation should be avoided entirely wherever financial transactions occur in the workflow.

Full Access
Question # 31

You are an architect supporting the iteration phase of a deployed Claude-based system.

Which activity most directly fits this phase?

A.

Rebuild the entire system architecture from scratch at the start of every iteration cycle regardless of what production telemetry, evaluations, and stakeholder feedback indicate is needed.

B.

Stop measuring production outcomes once the deployment has successfully launched, treating the go-live milestone as the end of the evaluation and iteration cycle.

C.

Discard the evaluation framework and reference set once the deployment is in production, accepting that future iterations will have no structured basis for measuring the impact of changes.

D.

Review production telemetry, sampled output evaluations, and stakeholder feedback to identify the highest-impact change for the next cycle, then plan the change against the evaluation framework.

Full Access
Question # 32

A Claude architect is implementing safety controls for a customer-facing advice assistant that must never provide regulated investment recommendations.

Which two guardrail implementations most directly enforce this constraint? (Select two.)

A.

Increase response temperature to introduce variability that reduces the likelihood of specific recommendations.

B.

Add an output classifier that detects and blocks responses containing regulated investment-recommendation language.

C.

Limit session length to reduce the volume of queries processed per user per day.

D.

Log all user queries to a SIEM for post-hoc compliance review.

E.

Define explicit out-of-scope categories in the system prompt with fixed refusal phrasing for investment advice requests.

Full Access
Question # 33

You are selecting a pattern for a compliance Q & A assistant that must answer policy questions with citations to the authoritative internal source set. Latency, cost, and audit predictability are prioritized.

Which pattern is the best fit?

A.

Augmented LLM with retrieval-augmented generation over the indexed authoritative corpus and citation rendering on each answer.

B.

Multi-agent orchestration with a planner, researcher, and writer agent for every query.

C.

A pure agent loop with open web-browsing tools to surface the most current policy information, without constraining retrieval to the authoritative internal corpus.

D.

A static prompt with the entire policy corpus concatenated into every request.

Full Access
Question # 34

You are explaining the precedence of Claude Code configuration scopes to the team.

Which precedence ordering, from highest to lowest, is correct?

A.

Local → managed → user → command-line arguments → project

B.

Project → user → managed → local → command-line arguments

C.

Managed → command-line arguments → local → project → user

D.

User → project → local → command-line arguments → managed

Full Access
Question # 35

During an architectural review, the security team identifies a risk that adversarial content injected into retrieved documents could manipulate the model’s behavior.

Which mitigation most directly addresses this threat?

A.

Treat all retrieved content as untrusted input and apply input classifiers with output validation.

B.

Require citations for each claim and constrain responses to source-supported content.

C.

Restrict outbound tool calls to an approved destination allow-list.

D.

Score outputs against a stable adversarial evaluation set on each model-version change.

Full Access
Question # 36

You are choosing the level of detail for an implementation guide. The audience is a delivery team that will build the deployment.

Which guidance composition best serves them?

A.

Component responsibilities, contracts between components, sequence diagrams of the dominant flows, configuration parameters with defaults, and operational runbooks.

B.

Component responsibilities and interface contracts only, without sequence diagrams of the dominant flows, configuration parameters with defaults, or runbooks to guide operational tasks.

C.

An architecture overview and sequence diagrams for the dominant flows, without interface contracts, configuration-parameter tables, or operational runbooks for the delivery team to follow.

D.

An architecture overview and a list of known limitations, without component-level diagrams, interface contracts, configuration parameters, or operational runbooks to support implementation.

Full Access
Question # 37

You are a platform architect designing an internal Claude-based assistant that serves both finance analysts and external auditors. Each population must access only documents permitted by its role.

Where should role-based access control be enforced in the pipeline?

A.

Inside the system prompt as a natural-language instruction for Claude to ignore unauthorized documents.

B.

At the retrieval layer, before any role-restricted content reaches the prompt-construction step or the model.

C.

Nowhere in the pipeline; rely on the model’s general refusal behavior to reject unauthorized document access without any enforced access control.

D.

After the response is generated, by post-filtering content that should not have been retrieved.

Full Access
Question # 38

You are reviewing an integration specification for security gaps.

Which two findings constitute valid security gaps in the specification? (Select two.)

Each correct answer presents a complete solution.
A.

Tool calls execute server-side under a least-privilege service principal scoped to the requested action.

B.

Service credentials are placed in the prompt context, where they can leak into logs and traces.

C.

Role-based access control is enforced only at the response-rendering layer after the model accesses restricted data.

D.

Per-user OAuth tokens are exchanged with scope-restricted permissions and refreshed within the active session.

E.

Tool inputs and outputs are encrypted in transit using transport-layer security between services.

Full Access